[EXP] Enterprise Management Control-Plane Compromise Through Authentication Bypass and Privileged Execution
Report Type: Exploit / EXP
Threat Category: Network-Management Control-Plane Compromise
Assessment Date: June 24, 2026
Most recent amendment Date: October 07, 2026
Primary Impact Domain: Network Infrastructure Trust and Control-Plane Integrity
Secondary Impact Domains: Remote Access, Firewall Policy, Routing, DNS, Wireless Operations, Recorder Infrastructure, Storage Access, Administrator Trust, Configuration Integrity, Business Continuity
Affected Asset Class: UniFi OS Server Deployments, UniFi Consoles, Cloud Gateways, Dream Machines, Cloud Keys, Gateways, Controllers, Recorders, Storage Appliances, Management Interfaces, and Downstream Managed Network Devices
Threat Objective Classification: Authentication Bypass, Protected Functionality Access, Update or Package Abuse, Command Injection, Privileged Execution, Administrator or API-Token Manipulation, Configuration Exposure, and Downstream Network-Control Impac
Published by: CyberDax LLC
Author: Edward “Tony” Dolley
Role: Founder / Principal Threat Researcher, CyberDax LLC
Publication Date: June 24, 2026
Publication Type: Cybersecurity Research Report / White Paper
BLUF
UniFi OS control-plane compromise through authentication bypass and command injection creates material business risk because adversaries may move from unauthenticated management-plane access to protected UniFi OS functionality, package-update abuse, command execution, sudo-assisted root-level activity, and downstream network-infrastructure manipulation without needing a conventional user-compromise path. The core risk is whether vulnerable or exposed UniFi OS Server deployments, consoles, gateways, controllers, cloud keys, recorders, storage appliances, or management interfaces can still be trusted after exploit-path activity that may affect firewall policy, routing, VPN access, DNS behavior, wireless configuration, device adoption, administrator accounts, configuration exports, backup workflows, surveillance infrastructure, storage access, or managed-device trust. Immediate executive action is required to validate UniFi OS asset inventory, fixed-version deployment, KEV-driven remediation, management-plane exposure, administrator baselines, update-package activity, root-context evidence, downstream configuration integrity, and the organization’s ability to distinguish approved UniFi administration from control-plane compromise behavior.
Executive Risk Translation
UniFi OS exploitation shifts the business risk from a patch-management issue to uncertainty over whether network-management infrastructure, administrative trust paths, and downstream network controls can still be relied on. If authentication-gateway behavior, traversal-like request activity, update-package endpoints, command execution, sudo activity, administrator-state changes, and network-device configuration changes cannot be tied to reliable time-sequenced evidence, leadership may need to assume that affected UniFi OS systems, managed gateways, firewall rules, VPN access, DNS settings, wireless networks, device-adoption workflows, recorder infrastructure, storage functions, and associated management credentials were exposed until proven otherwise. That response can expand into emergency remediation, management-plane isolation, root-compromise investigation, configuration rollback, firewall and VPN review, DNS and wireless validation, administrator and API-token review, backup and configuration-export scoping, downstream infrastructure assurance, legal and regulatory assessment, cyber-insurance coordination, executive reporting, and business-continuity planning for network-dependent operations.
S3 — Why This Matters Now
· UniFi OS can sit in a privileged network-management position supporting gateways, routing, firewall policy, VPN access, DNS behavior, wireless configuration, device adoption, network video recorders, storage appliances, controller functions, and administrator workflows.
· CISA KEV treatment and active exploitation reporting elevate the issue beyond theoretical vulnerability exposure because leadership must assume vulnerable internet-reachable or poorly controlled UniFi OS deployments may already be targeted.
· The exploit path is materially different from routine vulnerability management because authentication bypass and traversal-like access can enable access to protected functionality before command injection and privileged execution occur.
· Successful exploitation can create uncertainty over whether the organization still trusts the management plane that controls network access, segmentation, firewall policy, wireless access, VPN paths, device trust, recorder behavior, and storage workflows.
· The highest-risk condition occurs when suspicious UniFi OS management-plane access is followed by update-package activity, unexpected child processes, sudo commands, root-context execution, administrator changes, API token activity, device adoption, configuration changes, outbound communication, or downstream network-control activity.
· UniFi OS environments can make malicious activity difficult to classify because legitimate firmware updates, package operations, controller upgrades, device adoption, backups, gateway changes, VPN changes, DNS changes, wireless changes, vendor support, monitoring, security testing, and incident response may resemble suspicious behavior when viewed in isolation.
· Missing UniFi OS logs, reverse-proxy logs, endpoint process telemetry, sudo telemetry, package-management logs, administrator audit records, downstream configuration telemetry, exposure records, or change-management context can force broader investigation because the organization cannot quickly prove whether exploitation moved into privileged control or infrastructure modification.
· Response requires coordination across executive leadership, network engineering, firewall owners, wireless teams, identity teams, SOC, incident response, infrastructure owners, surveillance or physical-security owners where applicable, storage owners, legal, compliance, cyber insurance, communications, and business-continuity teams because compromise may affect both digital operations and network-control trust.
S4 — Key Judgments
· UniFi OS authentication bypass, path traversal, and command injection should be treated as a network-management control-plane trust risk, not only as a vulnerable-server finding, patch ticket, scanner result, or isolated web application issue.
· The primary enterprise risk is reduced ability to determine whether a vulnerable UniFi OS deployment was used to gain unauthorized management-plane access, execute commands, escalate privileges, modify administrator state, export configuration data, change network controls, or affect downstream managed devices.
· Suspicious management-plane access followed by update-endpoint activity, command execution, sudo usage, root-context behavior, administrator-state changes, configuration changes, outbound communication, or downstream management activity is the strongest executive risk signal.
· A vulnerable UniFi OS version, exposed management interface, scanner hit, isolated denied request, single web error, ordinary update check, or routine administrator action should not be treated as confirmed compromise without supporting exploit-path and follow-on evidence.
· Business exposure increases sharply when affected UniFi OS systems manage gateways, firewall policy, routing, VPN access, DNS behavior, wireless networks, device adoption, network video recorders, storage appliances, remote sites, critical business locations, regulated environments, customer-facing operations, or privileged management networks.
· Incomplete telemetry increases cost because the organization may need to reconstruct management-plane access, update-package activity, package-management events, process execution, sudo activity, administrator changes, configuration changes, outbound communication, internal scanning, device enumeration, and downstream network-control activity across multiple systems.
· The most damaging outcome occurs when UniFi OS compromise results in confirmed or suspected root-level access, unauthorized firewall or VPN changes, DNS manipulation, wireless trust changes, device-adoption abuse, configuration export, credential exposure, backup tampering, monitoring disruption, downstream network-control impact, incomplete containment, legal and regulatory review, cyber-insurance scrutiny, customer or workforce disruption, or board-level concern about infrastructure control-plane resilience.
S5 — Executive Risk Summary
Business Risk
UniFi OS control-plane compromise can weaken the organization’s ability to trust network-management infrastructure, administrative access paths, firewall and routing controls, VPN configuration, DNS behavior, wireless networks, device adoption, recorder functions, storage access, and managed-device state. Risk increases when affected deployments administer critical sites, remote offices, customer-facing locations, regulated environments, production networks, executive facilities, surveillance infrastructure, backup networks, wireless access, privileged management networks, or segmentation boundaries. The business impact is not limited to a vulnerable server or patch exception; it can expand into uncertainty about whether adversaries accessed protected management functions, executed commands, escalated to root, changed administrators, modified firewall or VPN policy, altered DNS or wireless settings, exported configuration data, weakened logging or monitoring, staged tools, or retained control after apparent remediation.
Technical Cause
The risk is driven by a UniFi OS exploit chain involving improper access control, traversal-like access behavior, and improper input validation that can allow unauthorized access to protected functionality and command injection against affected UniFi OS Server deployments. Technical exposure becomes material when vulnerable UniFi OS systems are reachable from untrusted networks, exposed through public management interfaces, accessible through broad VPN paths, weakly segmented from internal systems, or insufficiently monitored across web, reverse-proxy, firewall, process, sudo, package-management, administrator, and configuration-change telemetry. The highest-risk technical condition is an exploit-path sequence where suspicious management-plane access reaches update or package functionality, spawns unexpected service-context processes, uses sudo or root-context execution, modifies administrator or device state, communicates outbound, or changes downstream gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, or managed-device configuration.
Threat Posture
The threat posture is elevated because UniFi OS may function as a trusted administrative layer for network infrastructure and site connectivity. Exploitation may bypass traditional endpoint-focused or identity-only controls because the adversary can target the management plane directly, abuse protected backend functionality, and produce effects through legitimate-looking update, package, administrator, or configuration workflows. The posture becomes critical when vulnerable systems are internet-exposed, manage high-value network segments, control remote access, support wireless authentication paths, administer cameras or storage appliances, sit inside privileged management networks, or lack sufficient logging to prove whether control-plane trust remained intact.
Executive Decision Requirement
Executives must require measurable assurance that UniFi OS assets are inventoried, exposed management interfaces are identified, fixed versions are deployed, KEV-driven remediation is complete, vulnerable systems are assessed for pre-patch compromise, approved management paths are documented, administrator sources are baselined, update and package activity is reviewable, command execution and sudo activity are visible where technically available, downstream configuration changes are auditable, and SOC teams can rapidly distinguish approved UniFi administration from exploitation behavior. Leadership should also require evidence that network, firewall, wireless, identity, infrastructure, incident response, legal, compliance, cyber-insurance, communications, and business-continuity stakeholders can support defensible decisions if UniFi OS control-plane compromise is suspected.
S6 — Executive Cost Summary
UniFi OS control-plane compromise creates financial exposure because the organization must determine whether a trusted network-management platform was used to execute commands, alter infrastructure controls, change administrator state, export configuration data, affect device trust, or manipulate downstream network behavior. The cost profile is different from a routine patching event because the intrusion path may involve authentication bypass, traversal-like access, package-update command injection, sudo-assisted root-level activity, and management-plane control over infrastructure that supports connectivity, segmentation, remote access, DNS, wireless operations, device onboarding, surveillance, storage, and operational continuity. Response cost is driven by the work required to validate UniFi OS exposure, confirm fixed-version deployment, reconstruct management-plane requests, review update and package activity, inspect system and sudo logs where available, identify unexpected service-context child processes, validate administrator and API-token changes, review gateway and firewall policies, confirm routing and VPN integrity, inspect DNS and wireless changes, assess device adoption, validate recorder and storage configuration, review outbound communication, and prove that downstream network-control behavior was not maliciously changed.
Cost increases materially when UniFi OS asset inventory is incomplete, public exposure is unclear, reverse-proxy or firewall logs lack request-path detail, appliance deployments do not expose process or sudo telemetry, administrator audit records are limited, downstream configuration telemetry is missing, change-management records are weak, or network teams cannot rapidly distinguish approved maintenance from suspicious control-plane activity. In those conditions, leadership may need to fund broader assurance work across network engineering, firewall administration, wireless operations, identity, infrastructure, SOC, incident response, legal, compliance, cyber insurance, communications, physical security where recorder systems are involved, storage owners, and business-continuity teams. The highest-cost cases occur when suspected or confirmed compromise affects gateways, firewalls, VPN paths, DNS controls, wireless access, segmentation boundaries, executive or regulated sites, surveillance infrastructure, storage appliances, remote-site connectivity, or critical management networks, especially when root-level compromise, configuration manipulation, credential exposure, outage risk, customer impact, or formal notification analysis cannot be ruled out quickly.
Low Impact Scenario
Rapid investigation confirms vulnerable or exposed UniFi OS activity without evidence of successful command execution, sudo activity, root-context behavior, administrator-state change, configuration export, downstream network-control change, suspicious outbound communication, persistence, credential access, or continued activity after remediation. Activity may involve KEV-driven emergency patching, suspicious scanning, abnormal management-plane requests, denied requests, blocked access, or limited update-endpoint probing, but UniFi OS logs, reverse-proxy logs, firewall records, system logs where available, administrator audit records, configuration records, network telemetry, and change-management evidence support a failed, contained, or non-impacting event. Response is limited to emergency update validation, exposure reduction, targeted log review, management-interface access review, administrator baseline validation, limited firewall and VPN policy confirmation, short-term monitoring, and executive assurance that network-control trust was not materially affected. Estimated impact $450K - $2.8M.
Moderate Impact Scenario
Confirmed or strongly suspected UniFi OS exploit-path activity affects one or more systems that manage business-relevant gateways, network devices, VPN access, DNS behavior, wireless networks, recorder infrastructure, storage appliances, or remote-site connectivity. The organization cannot immediately determine whether authentication bypass, traversal-like access, or update-package command injection led to command execution, sudo usage, root-context activity, administrator changes, API token activity, configuration export, device-adoption changes, outbound communication, or downstream network-control modification. Response requires management-plane investigation, fixed-version validation, exposed-interface review, reverse-proxy and firewall reconstruction, endpoint or system telemetry review where available, administrator and token review, gateway and firewall policy review, routing and VPN validation, DNS and wireless configuration review, backup and configuration-export scoping, downstream device assurance, legal and compliance review, cyber-insurance coordination, executive reporting, and strengthened monitoring for post-remediation activity. Estimated impact $3.5M - $18M.
High Impact Scenario
UniFi OS exploitation becomes an enterprise-impact event when suspected or confirmed compromise results in root-level control, unauthorized administrator creation, firewall or routing modification, VPN exposure changes, DNS manipulation, wireless trust changes, device-adoption abuse, configuration export, credential exposure, backup tampering, monitoring disruption, recorder or storage compromise, remote-site outage, segmentation weakening, or uncertainty over multiple network-dependent business workflows. The organization may need to assume that network-management trust, downstream infrastructure configuration, and privileged control-plane paths were exposed until telemetry and configuration evidence prove otherwise. Response may require emergency isolation of management interfaces, broad UniFi OS remediation, root-compromise forensics, gateway and firewall rollback, VPN and DNS review, wireless revalidation, administrator credential rotation, API token revocation, configuration restore, device readoption review, network segmentation validation, surveillance and storage assurance, outage coordination, legal and privacy notification analysis, cyber-insurance engagement, customer or workforce communications planning, executive and board reporting, and formal validation that network-control trust can safely resume. Estimated impact $22M - $95M+.
S6A — Key Cost Drivers
· Number and criticality of affected UniFi OS systems, including UniFi OS Server deployments, consoles, cloud gateways, dream machines, cloud keys, gateways, recorders, storage appliances, controller hosts, exposed management interfaces, and remote-site controllers.
· Whether affected systems manage gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless networks, device adoption, recorder infrastructure, storage access, network segmentation, privileged management networks, or business-critical locations.
· Whether response must reconstruct authentication-bypass behavior, traversal-like request activity, update-endpoint access, package-management activity, command execution, sudo usage, root-context process behavior, administrator changes, API token activity, configuration changes, outbound communication, or downstream management activity.
· Availability and retention of UniFi OS logs, reverse-proxy logs, firewall records, secure access logs, NDR telemetry, DNS logs, endpoint process telemetry, sudo logs, package-management logs, administrator audit records, configuration-change records, change-management records, and incident-response records.
· Whether appliance deployments expose enough system, process, file, package, sudo, and persistence telemetry to confirm or refute command execution and root-level compromise.
· Scope of downstream infrastructure requiring review, including gateways, firewalls, VPN systems, routers, switches, access points, DNS services, wireless networks, cameras, recorders, storage systems, backup paths, monitoring systems, and management interfaces.
· Ability to distinguish approved firmware updates, package operations, controller upgrades, backups, device adoption, gateway changes, wireless changes, VPN changes, DNS changes, vendor support, security testing, monitoring, vulnerability management, and incident-response actions from suspicious exploit-path activity.
· Need to rotate or review UniFi administrator accounts, local users, API tokens, SSH access, VPN credentials, management credentials, backup credentials, device-adoption trust, service accounts, and privileged network-management access.
· Whether configuration review requires validation across firewall rules, routing tables, VPN policies, DNS forwarding, wireless SSIDs, access policies, segmentation boundaries, device-adoption records, recorder settings, storage configuration, backup exports, and management-plane permissions.
· Business disruption caused by emergency patching, management-interface isolation, remote-access restrictions, firewall or VPN rollback, wireless changes, device readoption, segmentation review, network downtime, help desk surge, administrator lockouts, monitoring gaps, or delayed site operations.
· Legal, privacy, regulatory, cyber-insurance, communications, customer, workforce, partner, executive, or board-level obligations triggered by suspected infrastructure-control compromise, regulated-network exposure, service disruption, physical-security system impact, configuration export, credential exposure, or inability to prove non-compromise.
S6B — Compliance and Risk Context

Figure 1
UniFi OS exploitation can create compliance and governance exposure when vulnerable management-plane systems support regulated environments, customer-facing connectivity, workforce access, physical-security infrastructure, remote-site operations, sensitive network segments, or systems that enforce access controls for protected data. Compliance exposure should be driven by local evidence of unauthorized control-plane access, command execution, root-level activity, administrator changes, configuration export, firewall or VPN manipulation, DNS changes, wireless trust changes, recorder or storage exposure, credential access, downstream device modification, service disruption, or inability to validate containment. KEV status, vulnerable version state, or internet exposure should increase remediation urgency, but they should not by themselves be treated as proof of reportable compromise without environment-specific evidence.
Compliance Exposure Indicator
High
Risk Register Entry
Risk Title
UniFi OS Control-Plane Compromise and Network Infrastructure Trust Exposure
Risk Description
Adversaries may exploit UniFi OS authentication bypass, path traversal, update-package abuse, command injection, or privileged execution behavior to move from network access into management-plane compromise, root-context activity, administrator-state changes, configuration export, device-adoption manipulation, or downstream network-control changes. This may increase business interruption, remote-site exposure, firewall and VPN trust uncertainty, DNS or wireless manipulation risk, recorder or storage exposure, credential-review requirements, legal and compliance review, cyber-insurance scrutiny, customer or workforce impact analysis, public trust loss, and board-level concern around network-management resilience. Compliance exposure should be driven by local evidence of unauthorized configuration change, credential exposure, regulated-network impact, service disruption, sensitive system access, recorder or storage exposure, or incomplete containment, not by vulnerable version state or KEV listing alone.
Likelihood
High
Impact
Severe
Risk Rating
Critical
Annualized Risk Exposure
Estimated $3.5M - $20M+ for materially exposed enterprise environments with vulnerable UniFi OS Server deployments, public or broadly reachable management interfaces, critical gateway or firewall dependency, VPN or wireless control-plane reliance, incomplete UniFi OS logging, limited endpoint or sudo telemetry, weak administrator baselines, incomplete downstream configuration records, or inconsistent change-management evidence. Exposure may exceed $22M - $95M+ where UniFi OS exploitation results in confirmed or suspected root-level compromise, unauthorized administrator creation, firewall or VPN manipulation, DNS or wireless changes, configuration export, credential exposure, recorder or storage compromise, remote-site disruption, segmentation weakening, customer or workforce impact, cyber-insurance review, legal escalation, communications response, or board-level reporting.
S7 — Risk Drivers
· UniFi OS may concentrate gateway administration, firewall policy, routing, VPN access, DNS behavior, wireless configuration, device adoption, recorder infrastructure, storage access, and controller workflows in a single trusted management plane.
· Authentication bypass and traversal-like request behavior can create access to protected functionality before normal administrator identity controls or endpoint-focused detections provide reliable warning.
· Package-update and command-injection behavior can turn management-plane access into privileged execution risk, especially when sudo activity, root-context execution, service modification, or package-management activity cannot be fully reconstructed.
· Internet-exposed or broadly reachable management interfaces increase urgency because opportunistic scanning and active exploitation can reach vulnerable systems without requiring a valid administrator account.
· Successful remediation requires more than applying a fixed version when pre-patch compromise cannot be ruled out; organizations must also validate logs, administrator state, configuration integrity, downstream device state, and post-remediation activity.
· Business exposure increases when affected UniFi OS systems control executive sites, branch offices, regulated environments, production networks, wireless access, VPN access, customer-facing locations, surveillance systems, storage appliances, or privileged management networks.
· Missing UniFi OS logs, reverse-proxy request details, endpoint process telemetry, sudo logs, package-management records, administrator audit events, downstream configuration logs, exposure records, or change-management context can increase investigation scope and cost.
· Legitimate workflows such as firmware updates, package operations, controller upgrades, backups, device adoption, gateway changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, monitoring, security testing, and incident response can increase false positives when not baselined.
· Limited ability to rapidly isolate management interfaces, validate fixed versions, inspect root-level activity, review administrator changes, audit firewall and VPN policy, confirm DNS and wireless integrity, and validate downstream device configuration can extend operational disruption.
· Configuration export, credential exposure, firewall weakening, VPN exposure changes, DNS manipulation, wireless trust changes, device-adoption abuse, recorder or storage compromise, and incomplete containment can transform a vulnerability response into legal, regulatory, communications, cyber-insurance, customer, workforce, executive, and board-level exposure.
S8 — Bottom Line for Executives
UniFi OS authentication bypass, path traversal, and command injection should be treated as a high-priority network-management control-plane risk because exploitation can turn a vulnerable management platform into a pathway for privileged execution, infrastructure manipulation, and downstream network-control uncertainty. The executive question is not only whether a UniFi OS system was vulnerable, exposed, scanned, or patched; it is whether the organization can prove that suspicious management-plane activity did not lead to command execution, sudo-assisted root activity, administrator changes, configuration export, firewall or VPN modification, DNS or wireless changes, device-adoption abuse, outbound communication, or continued activity after remediation. Response must focus on validating UniFi OS inventory, applying fixed versions, reducing management exposure, reconstructing exploit-path activity, reviewing privileged and configuration changes, validating downstream network controls, and restoring confidence that infrastructure management can be trusted.
S9 — Board-Level Takeaway
UniFi OS control-plane compromise turns network-infrastructure security into a board-level resilience, trust, and governance issue. The risk is not simply that a critical CVE exists, a management interface was exposed, a scanner observed a vulnerable version, or a patch had to be deployed; it is the possibility that adversaries used a trusted management platform to reach root-level execution, alter network controls, weaken remote access, manipulate DNS or wireless behavior, affect managed devices, expose configuration data, or undermine confidence in the infrastructure layer that supports business operations. Leadership should require evidence that KEV-driven remediation, management-plane exposure control, UniFi OS telemetry, administrator governance, configuration auditing, firewall and VPN validation, DNS and wireless review, downstream device assurance, incident response, legal readiness, cyber-insurance coordination, and business-continuity planning can support rapid, defensible decisions when UniFi OS exploitation is suspected.
S10 — Threat Overview
UniFi OS control-plane compromise through authentication bypass and command injection describes adversary behavior in which vulnerable UniFi OS Server deployments may be accessed through management-plane exploit paths that bypass expected authentication controls, reach protected functionality, interact with update or package mechanisms, and enable command execution that may run with elevated or root-level impact. The behavior is most relevant when suspicious UniFi OS management-plane access aligns with traversal-like request activity, update-endpoint interaction, package-management behavior, unexpected service-context child processes, sudo activity, root-context execution, administrator-state changes, configuration export, outbound communication, device enumeration, or downstream network-control changes.
· This is not only a vulnerable-version, exposed-interface, scanner-output, single-CVE, proof-of-concept, single-request, patch-ticket, web-error, or ordinary update-management model.
· The core threat behavior is movement from UniFi OS management-plane access into protected service functionality, update-package abuse, command execution, privileged activity, administrator-state manipulation, configuration exposure, or downstream network-control impact.
· The primary risk is reduced ability to determine whether UniFi OS activity remained approved administration or crossed into unauthorized control-plane access, command execution, root-level compromise, configuration manipulation, credential exposure, device-adoption abuse, or network-infrastructure modification.
· UniFi OS logs, reverse-proxy logs, firewall telemetry, secure access logs, network-flow telemetry, DNS telemetry, system logs, sudo logs, package-management logs, process telemetry, administrator audit records, configuration-change records, exposure records, change-management records, and incident-response records may be incomplete or difficult to reconcile during active investigation.
· The behavior can create uncertainty around network-management trust, gateway policy integrity, firewall and routing control, VPN access, DNS behavior, wireless configuration, recorder infrastructure, storage access, administrator access, backup or configuration exports, device adoption, remote-site operations, and business continuity.
· Public reporting, KEV status, vendor advisories, and technical analysis should support the relevance and urgency of the behavior class but should not narrow the report into a CVE-only, exploit-string-only, actor-only, scanner-only, or internet-exposure-only report.
S11 — Threat Classification and Type
Threat Type
UniFi OS control-plane compromise and network-management infrastructure exposure.
Threat Sub-Type
Authentication bypass, path traversal, protected endpoint access, update-package abuse, command injection, sudo-assisted privileged execution, root-context compromise, management-plane trust collapse, administrator-state manipulation, configuration exposure, device-adoption abuse, outbound follow-on behavior, and downstream network-control modification.
Operational Classification
Network-management control-plane compromise, remote command execution pathway, and downstream infrastructure-trust exposure.
Primary Function
Exploit vulnerable UniFi OS management-plane functionality to move from unauthorized or unauthenticated access into protected service interaction, update or package abuse, command execution, privileged system activity, administrator or configuration manipulation, and potential downstream modification of gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, or managed-device controls, creating uncertainty around infrastructure integrity, containment completeness, and operational trust.
S12 — Campaign or Activity Overview
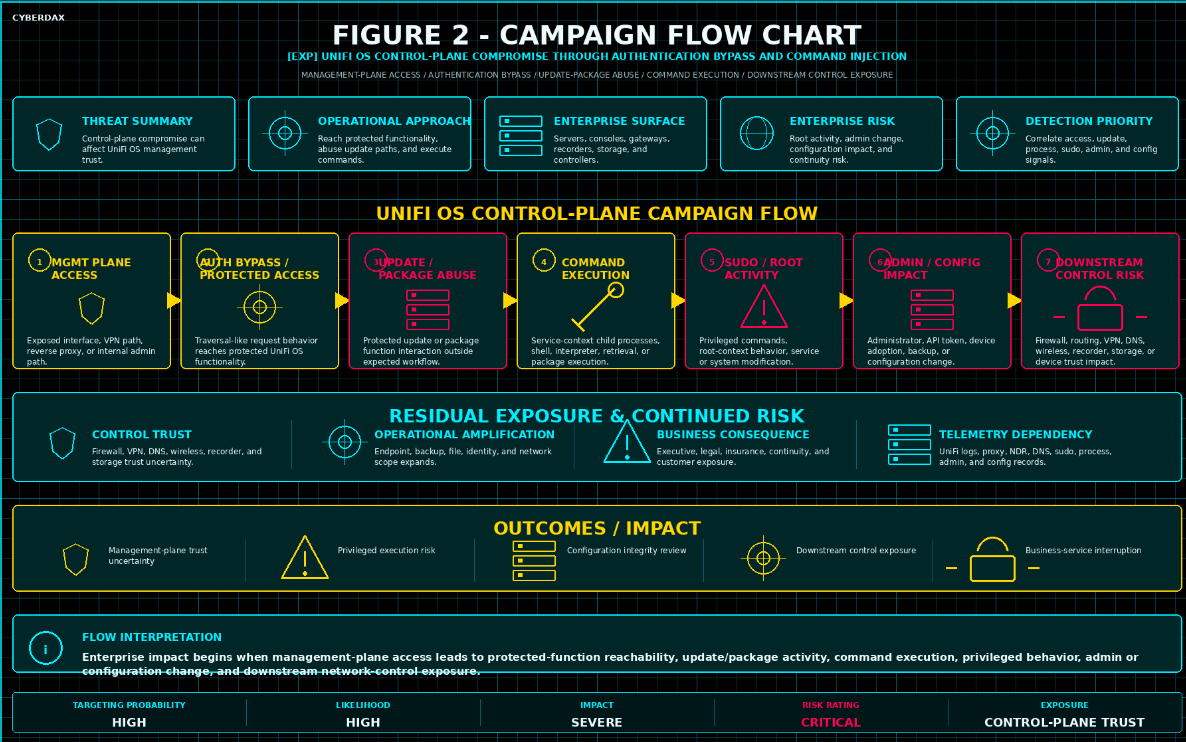
Figure 2
UniFi OS control-plane compromise activity model showing management-plane exposure, authentication bypass, traversal-like access behavior, improper access-control reachability, protected update or package endpoint interaction, command injection, sudo-assisted or root-context execution, administrator or configuration change, and downstream network-control exposure.
This report assesses UniFi OS control-plane compromise through authentication bypass, improper access control, and command injection as a durable exploit-path behavior class rather than a single CVE-only vulnerability entry or proof-of-concept event. The activity pattern involves adversaries attempting to reach protected UniFi OS or related UniFi management functionality through management-plane access paths, abuse exposed application or update-related behavior, execute commands, escalate operational control, and potentially affect the network infrastructure managed by the affected UniFi environment.
· The activity is best understood as a network-management control-plane threat rather than a simple patching event, exposed-service finding, scanner alert, web application issue, or isolated UniFi administration anomaly.
· Adversaries may target UniFi OS Server deployments, UniFi Connect Application deployments, consoles, gateways, cloud keys, dream machines, controller hosts, exposed management interfaces, network video recorders, storage appliances, and management paths that provide access to downstream infrastructure functions.
· The behavior may involve suspicious source access, unfamiliar internet or VPN ingress, traversal-style request behavior, improper access-control reachability, application or update-endpoint access, package-management activity, service instability, unexpected process execution, sudo usage, root-context activity, or abnormal administrator and configuration events.
· The activity may remain limited to scanning, blocked access, failed exploitation, abnormal requests, or emergency remediation, or it may progress into command injection, command execution, root-level activity, administrator manipulation, configuration export, outbound communication, internal scanning, device enumeration, and downstream network-control modification.
· The activity becomes highest risk when affected UniFi OS or related UniFi management systems manage gateways, firewalls, VPN access, DNS behavior, wireless infrastructure, segmentation boundaries, remote sites, customer-facing locations, regulated environments, recorder infrastructure, storage appliances, or privileged management networks.
· CVE identifiers, exploit-chain reporting, KEV status, public technical analysis, and vendor advisory details may increase urgency, but they should enrich the report rather than replace local behavior-led evidence of management-plane exploitation, improper access-control abuse, privileged execution, configuration change, or downstream infrastructure impact.
S13 — Targets and Exposure Surface
· The exposure surface includes UniFi OS Server deployments, UniFi Connect Application deployments, UniFi consoles, cloud gateways, dream machines, cloud keys, gateways, network application controllers, exposed management interfaces, update and package-management paths, administrator sessions, API tokens, device-adoption workflows, backup and configuration functions, recorder infrastructure, storage appliances, downstream managed devices, public Wi-Fi gateways, connected guest users, and network-control functions tied to gateway, firewall, routing, VPN, DNS, and wireless operations.
· UniFi OS, UniFi Connect, and related UniFi management interfaces, internet-reachable administration paths, VPN-accessible administration paths, reverse-proxy destinations, secure access paths, internal management interfaces, and controller administration endpoints.
· UniFi OS Server deployments, UniFi Connect Application deployments, controller hosts, supporting Linux hosts, consoles, cloud gateways, dream machines, cloud keys, gateways, recorders, storage appliances, and management-plane services.
· Check Point Security Management and Multi-Domain Management deployments, SmartConsole administration paths, internet-reachable Management Servers, application-login-token workflows, Trusted Clients restrictions, administrative authentication controls, security-policy and configuration-management functions, and downstream gateways, firewalls, VPN services, network objects, and managed security infrastructure whose trust or operation may be affected by unauthorized full-administrator access.
· Cisco IOS XE deployments operating in autonomous or controller-managed modes, internet-reachable or internally accessible device-management services, web-based and API-accessible administration paths, network-device configuration functions, privileged operating-system services, and downstream routing, switching, segmentation, VPN, and network-control infrastructure that may be affected by unauthorized command or argument injection.
· Fortinet FortiMail deployments and associated email-security-appliance infrastructure, including internet-reachable or internally accessible HTTP and HTTPS interfaces, administrative and management paths, mail-processing services, appliance filesystem and configuration paths, privileged server-side processing contexts, administrator functions, security policies, mail-system data, and downstream email-security dependencies whose confidentiality, integrity, availability, or administrative trust may be affected through unauthenticated path traversal and arbitrary file write.
· Tenable Security Center deployments, authenticated web and management interfaces, low-privilege user sessions, report-creation and report-rendering workflows, report jobs, trusted server-side rendering or processing functions, service-account execution contexts, administrative functions, vulnerability-management data, scanner and repository relationships, and downstream security-management infrastructure whose trust or operation may be affected when crafted report input reaches server-side processing and results in arbitrary execution under the Security Center service account.
· TrueConf Server deployments, internet-reachable or internally accessible web and management interfaces, administrative and application-service paths, authentication and authorization controls, server-side request-processing functions, privileged service contexts, configuration and collaboration-service functions, and downstream communications or infrastructure whose trust or operation may be affected by unauthorized access to protected functionality or server-side code execution.
· HP Advance deployments and associated enterprise print-workflow infrastructure, including administrative and management interfaces, print-management services, workflow-processing functions, authenticated service contexts, file-processing and file-write paths, application services, configuration functions, and downstream enterprise printing resources whose trust or operation may be affected through compromised management or application-processing paths.
· Dell ObjectScale deployments and associated storage-management and control-plane infrastructure, including administrative and management interfaces, cluster-management functions, controller and service endpoints, privileged server-side processing contexts, object-storage configuration and management workflows, serialization and deserialization processing paths, and downstream storage resources whose trust or operation may be affected through compromised management or server-side processing.
· CISA Malcolm deployments before v26.06.0, including internet-reachable or internally accessible web and management interfaces, reverse-proxy paths, identity-provider integrations, analyst interfaces, authenticated and unauthenticated application routes, containerized services, backend search and analytics services, file-transfer and archive-processing workflows, administrative interfaces, security-monitoring data stores, configuration paths, and supporting infrastructure whose confidentiality, integrity, or administrative trust may be affected by unauthorized access or code execution.
· Malcolm analyst identities, authenticated sessions, cookies, application roles, RBAC state, proxy trust relationships, identity-provider relationships, certificate-validation settings, application signing secrets, administrator credentials, and bundled service credentials whose misuse or unsafe configuration may permit session hijacking, authentication bypass, authorization bypass, role escalation, or access to protected administrative functions.
· Malcolm file-transfer, upload, archive-processing, filename-handling, record-management, backend query, tagging, and configuration workflows that may permit command execution, arbitrary file writes, record fabrication or modification, unauthorized writes in read-only deployments, unauthorized access to internal services, or modification of security-monitoring evidence.
· Malcolm containerized application services, backend data services, reverse proxies, identity-provider connections, administrative components, and supporting service relationships that may be affected when attacker-controlled input reaches privileged processing paths or when compromised application components use elevated service credentials.
· Malcolm deployments using sample or inherited configuration containing default administrator passwords, default cookie-signing secrets, insufficiently protected credential material, disabled certificate verification, or other insecure deployment settings that weaken application, proxy, identity, or administrative trust boundaries.
· Malcolm security-monitoring records, stored events, session records, tags, configuration objects, uploaded data, and related evidence repositories whose integrity may be affected through vulnerable write, archive, backend, read-only, or record-modification paths.
· Logsign SIEM versions 6.4.101 through versions before 6.4.117; a default-credential weakness that may permit unauthenticated administrative access; low-privilege authenticated path traversal; low-privilege authenticated network-reachable code injection; affected files, configuration, credentials, administrator state, connectors, ingestion, alerting, logging, and security records; and consequential security-monitoring and evidence-integrity effects.
· UTMStack SIEM and security-management deployments, including internet-reachable or internally accessible administrative and API surfaces, identity-provider integrations, asset-group and network-scan search functions, backend database and query-processing paths, password-reset workflows, PDF and reporting services, internal-key authentication and trust paths, STOMP command WebSocket communications, connected-agent relationships, configuration and security-rule functions, security records, credentials and sensitive information, internal-service and cloud-metadata reachability, and downstream managed endpoints whose confidentiality, integrity, administrative trust, or execution state may be affected through unauthorized access, authorization failure, injection, server-side request forgery, privileged API misuse, sensitive-record access, or management-plane command delivery.
· SUSE Rancher Manager deployments, including internet-reachable or internally accessible Rancher management interfaces, public and authenticated API routes, public UI settings, login-page processing, local administrator bootstrap credentials, administrator sessions, browser session state, public API session tokens, identity-provider and OIDC-backed authentication relationships, cluster-management functions, RBAC state, secrets, configuration objects, and downstream Kubernetes or managed-cluster resources whose confidentiality, integrity, administrative trust, or access control may be affected through unauthorized public-setting modification, administrator-session exposure, or continued use of a captured session token after logout.
· Cloud Foundry deployments using UAA for identity and access management, including UAA authentication and OAuth endpoints, OAuth clients, access-token and client-credentials grant workflows, OIDC identity-provider integrations, self-UAA OIDC configurations, browser authentication and session-establishment paths, shadow-account mappings, group memberships, client authorities, administrative scopes, and downstream Cloud Foundry platform resources whose authentication, authorization, or administrative trust may be affected through unauthorized session establishment or privilege-bearing token issuance.
· SailPoint IdentityIQ deployments, including internet-reachable or internally accessible web and administrative interfaces, web-service APIs, identity-governance workflows, authentication and authorization controls, identity and account objects, role and entitlement state, workflow-processing functions, privileged application-service contexts, connectors, credentials, configuration data, and downstream enterprise systems whose trust or operation may be affected when unauthenticated web-service API content reaches vulnerable server-side processing and results in remote code execution.
· FreePBX deployments and associated PBX and unified-communications management infrastructure, including FreePBX Administrator Control Panel interfaces, authenticated administrative sessions, module-management and configuration paths, sound-language upload and conversion workflows, Superfecta configuration and source-processing paths, GraphQL and API-accessible management functions where deployed, file-upload and file-conversion paths, PHP and web-server processing contexts, Asterisk service contexts, telephony configuration, credentials, call-control functions, and downstream communications services whose confidentiality, integrity, availability, or administrative trust may be affected through arbitrary file write, unsafe server-side file inclusion, code execution, or operating-system command execution.
· FreeIPA deployments, identity-management servers, LDAP-accessible directory services, Kerberos services, 389 Directory Server dependencies, administrative web and API paths, enrollment and identity-management interfaces, host and service principal workflows, group and privilege-management functions, OTP and authentication workflows, identity-provider configuration functions, and downstream systems that rely on FreeIPA for centralized authentication, authorization, host trust, service trust, or privileged identity decisions.
· FreeIPA environments where anonymous or otherwise insufficiently restricted LDAP interaction, self-service identity or OTP functionality, directory authorization state, stale or improperly retained authentication context, principal creation, group membership, privilege assignment, or Kerberos identity issuance may combine to produce unauthorized privileged identity state or administrative control.
· FreeIPA identity-provider configuration and federation-management paths, authenticated low-privilege user sessions, template or parameter-processing functions, environment-variable handling, external identity-provider definitions, authentication-broker relationships, and service memory or resource state that may be affected when attacker-controlled configuration values reach privileged server-side processing before intended authorization or validation decisions are enforced.
· 389 Directory Server instances supporting FreeIPA or adjacent enterprise identity infrastructure, LDAP bind and SASL authentication paths, directory-manager or equivalent privileged identities, directory authorization state, group and role membership, object creation and modification activity, password and OTP objects, service and host principals, replication relationships, Kerberos-integrated identity state, and downstream systems that consume directory-backed authorization decisions.
· Kerberos realms, KDC services, ticket-granting workflows, attacker-created or attacker-controlled principals, administrative group membership, privileged service principals, host principals, ticket issuance, authentication events, authorization decisions, and downstream services that trust resulting Kerberos identities.
· Enterprise identity objects including users, groups, hosts, services, roles, privileges, HBAC rules, sudo rules, OTP tokens, service accounts, administrator accounts, directory-manager identities, Kerberos principals, IdP definitions, authentication templates, and trust relationships whose creation, modification, misuse, or compromise may expand access beyond the initial management-plane interaction.
· IBM Guardium Data Protection 12.2-family deployments and associated enterprise database-security and security-management control-plane infrastructure, including Central Manager, Collector, Guardium Installation Manager, appliance-management functions, administrative interfaces, REST interfaces, PESI functions, SNMP functions, import workflows, update and patch-management paths, privileged server-side or SUID-wrapper execution contexts, process and service activity, files, credentials, databases, certificates, administrator identities, network configuration, monitored-database relationships, compliance functions, and downstream data-security dependencies whose confidentiality, integrity, availability, or administrative trust may be affected through compromised Guardium management or appliance-processing paths.
· kcp multi-tenant management-control-plane deployments, including front-proxy and shard topology, authenticated tenant paths, caller-supplied X-Remote-* identity handling, delegated identity and scope, system privilege state, workspace and RBAC state, secrets, APIExports, APIBindings, LogicalClusters, configuration activity, and downstream resources whose authorization or confidentiality may be affected when improperly trusted identity information crosses front-proxy, shard, or workspace trust boundaries. Remediation-state validation should identify affected deployments and confirm migration to fixed releases 0.31.4, 0.32.2, or later applicable fixed releases.
· Brocade Fabric OS deployments and associated Fibre Channel switching and fabric-management infrastructure, including REST API, WebTools and web-management interfaces, administrative CLI paths, local and federated authentication, AAA, RADIUS, LDAP, TACACS+, and SSO relationships, RBAC and account-management functions, Virtual Fabric authorization boundaries, zoning and zone-management functions, firmware-management and firmware-download workflows, configuration upload and download functions, certificate-management functions, SNMP management, switch-to-switch management relationships, fabric synchronization, inter-switch administrative communications, privileged operating-system and management-service contexts, and downstream storage-fabric resources whose confidentiality, integrity, availability, access control, or administrative trust may be affected through authentication bypass, authorization failure, command injection, privilege escalation, session manipulation, or unauthorized administrative control.
· Kiteworks Core deployments and associated secure file-transfer and content-exchange control-plane infrastructure, including administrative interfaces, delegated administrator identities, administrative roles and permissions, administrative import workflows, integration configuration, privileged integration credentials, secure file-transfer functions, managed content, connectors, external service relationships, and downstream enterprise systems or data whose confidentiality, integrity, access control, or administrative trust may be affected through unauthorized privilege expansion.
· Public Wi-Fi gateways, guest wireless networks, connected users, DNS resolver or forwarding functions, SSIDs, access points, and user traffic that may be redirected through unauthorized DNS changes to attacker-controlled credential-harvesting infrastructure.
· Update endpoints, package-management functions, application-update workflows, package retrieval behavior, update-triggered service activity, UniFi Connect application service paths, and maintenance workflows that may become relevant during exploit-path investigation.
· Administrator accounts, local users, API tokens, administrative sessions, SSH access where present, device-adoption workflows, backup actions, configuration exports, service settings, application permissions, management permissions, directory privileges, Kerberos principals, identity-group memberships, OTP state, identity-provider configuration, analyst sessions, application roles, RBAC assignments, proxy trust state, application signing secrets, privileged service credentials, Cloud Foundry UAA user identities, OAuth clients, user access tokens, client-credentials grants, OAuth client authorities, OIDC identity-provider configuration, self-UAA OIDC relationships, browser login state, shadow-account mappings, shadow-account group memberships, UAA administrative scopes, Brocade Fabric OS administrator and management identities, REST API and WebTools sessions, CLI administrative sessions, RBAC roles and permissions, AAA state, RADIUS, LDAP, TACACS+, and SSO authentication relationships, Virtual Fabric authorization state, switch and fabric administrative relationships, and privileged management credentials.
· Authenticated Tenable Security Center users, user roles and privilege assignments, report definitions, report-generation requests, report jobs, rendering processes, parent and child process relationships, service-account activity, file creation or modification, outbound network activity, administrative-state changes, and downstream security-platform actions associated with suspected report-rendering abuse.
· Rancher asset and version inventory, public and authenticated API exposure, public UI settings, administrator and bootstrap-account state, browser and public API session-token state, logout and session-revocation behavior, identity-provider and OIDC configuration, authentication and authorization records, cluster-management activity, RBAC changes, secret and configuration access, downstream cluster activity, and remediation-state evidence required to distinguish vulnerable-product presence or legitimate administration from unauthorized public-setting modification, administrator-session exposure, post-logout token reuse, or consequential management-plane activity.
· SailPoint IdentityIQ asset and version inventory, reachable web and web-service API paths, authentication and authorization state, identity-governance and workflow activity, application and service process telemetry, identity, role, entitlement, connector and configuration state, filesystem or process changes where observable, network behavior, and remediation-state evidence required to distinguish vulnerable-product presence or legitimate IdentityIQ administration from unauthorized server-side execution or consequential identity-governance compromise.
· FreePBX asset and version inventory, installed module and module-version state, Administrator Control Panel exposure, authenticated-user and administrative-session context, sound-language upload and conversion activity, Superfecta configuration and source-processing activity, GraphQL and other management API activity where deployed, file creation and modification, PHP and web-server process activity, Asterisk service and child-process activity, operating-system command execution, telephony configuration changes, network behavior, and remediation-state evidence required to distinguish vulnerable-product presence or legitimate PBX administration from arbitrary file write, unsafe file inclusion, PHP execution, operating-system command execution, or downstream communications effects.
· FreeIPA authenticated-user and administrator activity, LDAP request and bind telemetry, Kerberos authentication and ticket activity, identity and group changes, OTP enrollment and self-service operations, principal creation, role and privilege assignment, directory-object modification, IdP configuration changes, environment-variable or template-processing errors, process-memory or resource anomalies, and downstream authentication or authorization events associated with suspected identity-control-plane abuse.
· 389 Directory Server authentication, authorization, bind, group-membership, privileged-directory, replication, object-modification, and error telemetry required to distinguish ordinary directory administration from stale-identity reuse, authentication-state confusion, unauthorized privileged binding, attacker-created directory objects, or consequential identity and access changes.
· Brocade Fabric OS authentication, administrator and account-management activity, REST API requests, WebTools and web-management activity, CLI command execution, AAA and external-authentication events, RADIUS, LDAP, TACACS+, and SSO interactions, RBAC decisions and privilege changes, zoning and Virtual Fabric changes, configuration upload and download activity, firmware-management operations, certificate-management activity, SNMP administration, switch and fabric management sessions, inter-switch administrative communications, fabric-synchronization activity, privileged process or command execution, configuration changes, and downstream fabric-state changes required to distinguish legitimate switch administration from authentication bypass, authorization bypass, privilege escalation, command injection, session abuse, unauthorized administrative actions, or consequential control-plane compromise.
· Cloud Foundry UAA authentication, OAuth-token issuance, client-credentials grant, OIDC login and callback, OAuth-client configuration, client-authority, user and service identity, shadow-account, group-membership, session, administrative-scope, and downstream platform-access telemetry required to identify unauthorized session creation, anomalous privilege-bearing token issuance, unexpected identity or group mapping, or consequential Cloud Foundry control-plane activity.
· Gateway policy, firewall rules, routing configuration, VPN access, DNS behavior, DNS-forwarding configuration, wireless configuration, SSID security, device trust, network segmentation, recorder behavior, storage access, managed-device configuration, identity policy, directory authorization state, Kerberos trust, privileged-group membership, centralized authentication dependencies, management-platform role state, proxy trust, security-monitoring data integrity, Brocade Fabric OS switch and fabric configuration, zoning and zone-management state, Virtual Fabric configuration and authorization boundaries, switch-account and RBAC state, AAA configuration, firmware and configuration-management state, certificate-management state, SNMP configuration, fabric synchronization relationships, and inter-switch administrative trust.
· Endpoint, process, file, sudo, system, package-management, and persistence telemetry for self-hosted UniFi OS Server deployments, UniFi Connect Application deployments, controller hosts, appliance environments, FreeIPA servers, 389 Directory Server hosts, KDC systems, or identity-management infrastructure that expose host-level visibility.
· Tenable Security Center asset and version inventory, authenticated-user and role telemetry, report and job activity, report-rendering process telemetry, parent and child process telemetry, service-account execution telemetry, file and network telemetry, administrative-state records, and downstream security-platform activity required to distinguish vulnerable-product presence or legitimate report generation from suspicious server-side execution and post-exploitation behavior.
· Malcolm asset and version inventory, including identification of deployments before v26.06.0, externally or internally reachable interfaces, reverse-proxy configuration, identity-provider configuration, certificate-validation state, deployment mode, read-only configuration, enabled services, containerized components, analyst and administrator roles, application-secret provenance, bundled administrative interfaces, backend service relationships, and security-monitoring data stores.
· Logsign SIEM asset and version inventory, including identification of deployments running versions 6.4.101 through versions before 6.4.117; externally or internally reachable application and management paths; administrator and low-privilege user identities; authentication and authorization state; default-credential exposure; request and path activity; file and configuration access; parent and child process activity; credential or secret access; administrator-state changes; connector and ingestion activity; alerting and logging behavior; security-record modification or degradation; outbound network activity; and remediation-state evidence required to distinguish vulnerable-product presence or legitimate administration from unauthorized administrative access, path traversal, code execution, or consequential security-monitoring and evidence-integrity effects.
· UTMStack asset and version inventory, including identification of affected deployments and corrected-version state; externally or internally reachable administrative interfaces and APIs; authenticated identity and role context; internal-key state and provenance; identity-provider configuration; STOMP command-WebSocket activity; connected-agent identity and command telemetry; asset-group, network-scan, database, and query-processing activity; password-reset request and response activity; PDF and reporting requests; credential, sensitive-record, configuration, and security-rule access; internal-service or cloud-metadata network activity; managed-endpoint process and command telemetry; downstream managed-system state; and remediation-state and incident-response evidence required to distinguish vulnerable-product presence or legitimate administration from unauthorized database access, server-side request forgery, authorization failure, privileged API misuse, account enumeration, sensitive-record exposure, or management-control-plane command delivery to connected agents.
· Cloud Foundry UAA and cf-deployment asset and version inventory, OAuth-client configuration, enabled grant types, client-authority state, user and client token issuance, OIDC identity-provider configuration, self-UAA OIDC relationships, browser authentication and session activity, shadow-account creation and mapping, group-membership state, administrative-scope assignment, authentication and authorization records, token-endpoint activity, change-management evidence, and remediation-state validation required to distinguish vulnerable-product presence or legitimate Cloud Foundry identity administration from unauthorized session establishment, privilege-bearing token issuance, or consequential platform access.
· FreeIPA, 389 Directory Server, and Kerberos asset and version inventory, enabled-service state, anonymous LDAP exposure, authentication-method configuration, OTP configuration, directory and Kerberos trust relationships, user and group state, administrator membership, service and host principal state, IdP configuration, environment-variable and template-processing context, process and memory telemetry, authentication and authorization logs, and downstream identity-consumer activity required to distinguish vulnerable-product presence or ordinary identity administration from unauthorized privilege creation, authentication bypass, information disclosure, or denial-of-service behavior.
· Brocade Fabric OS asset and version inventory, including affected switch and platform identification, REST API and WebTools exposure, web-management and CLI reachability, enabled authentication methods, AAA configuration, RADIUS, LDAP, TACACS+, and SSO relationships, administrator and service accounts, RBAC roles and permissions, Virtual Fabric configuration, zoning state, firmware and configuration-management state, certificate-management configuration, SNMP management state, switch-to-switch and fabric relationships, management-session records, privileged-command and process telemetry, applicable change-management evidence, and remediation-state validation required to distinguish vulnerable-product presence or legitimate switch administration from unauthorized management access, authentication or authorization bypass, privilege escalation, command injection, session manipulation, arbitrary administrative action, or consequential fabric-control compromise.
· HP Advance and Dell ObjectScale asset and version inventory, including identification of deployed HP Advance print-workflow services, Dell ObjectScale storage-management and control-plane components, exposed or internally reachable management interfaces, enabled management services, authenticated service contexts, print-workflow and file-processing paths, ObjectScale cluster-management and server-side processing paths, administrative configuration state, and available application, process, file, authentication, and management telemetry required to distinguish vulnerable-product presence or ordinary administrative activity from suspicious privileged processing, unauthorized file activity, or server-side execution.
· Fortinet FortiMail asset and version inventory, including identification of affected FortiMail deployments, externally or internally reachable HTTP and HTTPS interfaces, administrative and management paths, mail-processing and appliance-service context, request and path activity, filesystem and file-write activity, configuration state, administrator activity, process and service behavior where available, network communication, email-security policy and mail-system state, change-management evidence, incident-response findings, and remediation-state validation required to distinguish vulnerable-product presence or legitimate FortiMail administration from unauthenticated path traversal, arbitrary file write, or consequential appliance compromise.
· IBM Guardium Data Protection and kcp asset and version inventory, including Guardium 12.2-family deployment and appliance-role state; Central Manager, Collector, and Guardium Installation Manager relationships; kcp front-proxy, shard, tenant, and workspace topology; exposed or internally reachable interfaces; authenticated access paths; privileged identity, role, and authorization state; Guardium management, process, file, credential, database, certificate, update, patch, network, and downstream dependency telemetry; kcp authentication, request, identity-header, delegated-identity, workspace, RBAC, secret-access, configuration, audit, and downstream access telemetry; applicable change-management evidence; and remediation-state validation required to distinguish vulnerable-product presence or legitimate administration from suspicious control-plane behavior and to confirm deployment of applicable vendor-fixed releases.
· Network-flow, firewall, DNS, reverse-proxy, secure access, load-balancer, NDR, LDAP, Kerberos, proxy, identity-provider, and application telemetry that can support management-plane access review, outbound communication analysis, UniFi Connect application access review, public Wi-Fi traffic scoping, DNS-redirection investigation, Malcolm proxy and backend-service interaction review, Logsign SIEM application and management-path review, UTMStack administrative-interface and API review, identity-provider activity analysis, STOMP command-WebSocket and connected-agent communication review, internal-key and privileged-API investigation, database and query-activity analysis, password-reset activity review, PDF/reporting request review, internal-service and cloud-metadata access analysis, managed-endpoint command correlation, FortiMail HTTP and HTTPS request-path, appliance, filesystem, configuration, mail-processing, administrator, and network-activity review, suspicious request and path activity analysis, process-to-network correlation, connector and ingestion activity review, alerting and logging degradation analysis, security-record and evidence-integrity review, Rancher API, session-token, identity-provider, and management-plane interaction review, IdentityIQ web-service and identity-governance activity review, FreePBX administrative, module, API, file-processing, process, and communications-management review, FreeIPA and directory-service reachability analysis, identity-control-plane interaction review, Cloud Foundry UAA OAuth-token-endpoint, OIDC-login-callback, OAuth-client, token-issuance, identity-provider, session, and administrative-scope activity review, Brocade Fabric OS REST API, WebTools and web-management, CLI, authentication, AAA, RADIUS, LDAP, TACACS+, SSO, RBAC, account-management, configuration-transfer, firmware-management, certificate-management, zoning, Virtual Fabric, fabric-synchronization, inter-switch management, administrative-session, and privileged-command activity review, HP Advance print-workflow and management-path review, Dell ObjectScale management and control-plane interaction review, and downstream management or authentication activity scoping.
· Change-management records, maintenance windows, update records, device-onboarding records, network-change tickets, firewall-policy records, VPN-change records, wireless-change records, DNS-change records, UniFi Connect application update records, Tenable Security Center upgrade and maintenance records, report-generation baselines, Malcolm upgrade and configuration records, Logsign SIEM upgrade and remediation records, UTMStack upgrade and remediation records, administrative and API configuration changes, identity-provider configuration changes, internal-key rotation or trust-state changes, connected-agent and STOMP configuration changes, reporting-service changes, database or query-related configuration changes, security-rule changes, Rancher upgrade, authentication, identity-provider, session-management, and cluster-administration records, SailPoint IdentityIQ upgrade, patch, API, connector, workflow, role, entitlement, and configuration records, FreePBX upgrade, module-update, administrative, telephony-configuration, API, and maintenance records, configuration changes, administrator-account and credential changes, connector and ingestion changes, alerting and logging configuration changes, proxy and identity-provider changes, certificate-validation changes, administrator or application-secret rotation records, deployment-mode changes, FreeIPA and 389 Directory Server upgrade records, identity-policy changes, group-membership changes, Kerberos configuration changes, OTP-policy changes, IdP configuration changes, Cloud Foundry UAA and cf-deployment upgrade records, OAuth-client configuration and grant-type changes, OAuth-client authority changes, OIDC identity-provider and self-UAA configuration changes, shadow-account and group-membership changes, UAA session or token-policy changes, Brocade Fabric OS upgrade and remediation records, firmware-management and firmware-download records, REST API and WebTools configuration changes, administrator-account, RBAC, AAA, RADIUS, LDAP, TACACS+, and SSO configuration changes, configuration-upload and configuration-download activity, zoning and Virtual Fabric changes, certificate-management changes, SNMP configuration changes, fabric-synchronization changes, and switch or fabric administrative changes, HP Advance upgrade and configuration records, Dell ObjectScale upgrade and storage-management configuration records, approved administrative activity, vendor-support records, security-testing records, and incident-response records.
Environments with exposed management interfaces, incomplete UniFi OS or UniFi Connect inventory, incomplete Tenable Security Center asset or version inventory, incomplete Malcolm asset or version inventory, incomplete Logsign SIEM asset, version, authentication, request-path, process, file, configuration, credential, administrator-state, connector, ingestion, alerting, logging, security-record, network, change-management, or remediation-state visibility, incomplete UTMStack asset, version, administrative-interface, API, authentication, role, internal-key, identity-provider, STOMP command-WebSocket, connected-agent, database-query, password-reset, PDF-reporting, credential, sensitive-record, configuration, security-rule, internal-service, cloud-metadata, managed-endpoint, network, change-management, incident-response, or remediation-state visibility, incomplete Rancher asset, version, API, public-setting, session-token, identity-provider, OIDC, RBAC, cluster-management, change-management, or remediation-state visibility, incomplete SailPoint IdentityIQ asset, version, web-service API, authentication, authorization, workflow, identity, role, entitlement, connector, process, network, change-management, or remediation-state visibility, incomplete FreePBX asset, version, module, administrative-session, file-processing, PHP, web-server, Asterisk, API, telephony-configuration, network, change-management, or remediation-state visibility, incomplete FreeIPA or 389 Directory Server inventory, incomplete HP Advance asset or version inventory, incomplete Dell ObjectScale asset or version inventory, incomplete FortiMail asset, version, HTTP or HTTPS interface, request-path, filesystem, file-write, configuration, mail-processing, administrator, process, service, network, change-management, incident-response, or remediation-state visibility, incomplete IBM Guardium Data Protection or kcp asset, version, topology, interface, telemetry, change-management, or remediation-state visibility, incomplete Cloud Foundry UAA or cf-deployment asset, version, OAuth-client, grant-type, client-authority, access-token, token-issuance, OIDC identity-provider, self-UAA configuration, browser-session, shadow-account, group-membership, authentication, change-management, or remediation-state visibility, incomplete Brocade Fabric OS asset, version, REST API, WebTools, web-management, CLI, authentication, AAA, RADIUS, LDAP, TACACS+, SSO, RBAC, administrative-session, account-management, configuration-transfer, firmware-management, certificate-management, zoning, Virtual Fabric, fabric-synchronization, inter-switch management, privileged-command, network, change-management, or remediation-state visibility, weak administrator or authenticated-user source baselines, broad VPN administration paths, anonymously reachable or insufficiently restricted LDAP services, weak directory authorization controls, incomplete Kerberos or privileged-group visibility, limited request-path logging, limited report or job visibility, missing service-account or parent-child process visibility, limited Malcolm analyst-session, RBAC, proxy, identity-provider, certificate-validation, container, backend-service, record-integrity, or secret-configuration visibility, missing directory bind or authorization telemetry, missing identity-change or Kerberos-principal telemetry, missing IdP configuration or template-processing visibility, limited HP Advance print-workflow, file-processing, file-write, service-context, or management telemetry, limited Dell ObjectScale cluster-management, control-plane, server-side processing, deserialization, or management telemetry, appliance-only telemetry, weak configuration monitoring, weak DNS-change monitoring, limited visibility into public Wi-Fi traffic, inability to associate affected users or endpoints with suspicious authentication activity, short log retention, or incomplete change-management discipline.
S14 — Sectors / Countries Affected
Sectors Affected
· Small and midsize businesses using UniFi OS for gateway, firewall, wireless, routing, VPN, recorder, storage, or network-management functions.
· Managed service providers, IT service providers, and distributed support organizations administering multiple customer environments or remote sites.
· Education, campus, and research environments with broad wireless networks, distributed sites, or decentralized infrastructure administration.
· Retail, hospitality, logistics, branch-office, and distributed enterprises using UniFi OS for site connectivity, wireless access, remote management, or security-camera infrastructure.
· Healthcare, professional services, legal, financial services, and regulated organizations where network access, surveillance, wireless connectivity, or site operations support sensitive workflows.
· Manufacturing, industrial support, utilities, energy, transportation, and critical infrastructure-adjacent organizations using UniFi OS in business networks, branch networks, remote sites, or operational support environments.
· Local government, public-sector, nonprofit, and community-service organizations with limited infrastructure staff, exposed management interfaces, or high dependence on remote administration.
· Organizations using UniFi OS to manage gateways, firewalls, VPN paths, DNS behavior, wireless networks, device adoption, recorders, storage appliances, segmentation boundaries, or privileged management networks.
Countries Affected
· Global.
· Exposure is not limited to a single country or region because UniFi OS is deployed across small business, enterprise, education, public-sector, retail, hospitality, healthcare, professional services, branch-office, and distributed network environments.
· Countries with high UniFi OS adoption, broad internet-exposed management surfaces, MSP-administered networks, distributed branch operations, or limited infrastructure monitoring may face elevated operational exposure.
· Country-specific impact should be assessed by UniFi OS dependency, exposed management paths, affected device roles, fixed-version deployment, downstream network-control scope, telemetry maturity, change-management quality, and local evidence of exploitation rather than geography alone.
S15 — Adversary Capability Profiling
Capability Level
Moderate to High
Technical Sophistication
Adversaries require enough technical capability to identify reachable UniFi OS management surfaces, understand the authentication-gateway bypass path, chain traversal-like access behavior into protected functionality, interact with update or package mechanisms, and translate command execution into meaningful host or infrastructure impact. Lower-complexity activity may involve scanning, opportunistic exploitation, use of public detection or exploit knowledge, basic command execution, or limited system access. Higher-capability activity may involve selective targeting of exposed management interfaces, careful timing around maintenance windows, controlled command execution, root-context activity, administrator or API-token manipulation, configuration export, network-device enumeration, downstream configuration changes, and post-remediation persistence or re-entry attempts.
Infrastructure Maturity
Moderate
Infrastructure maturity varies by activity pattern. Lower-maturity activity may rely on direct internet scanning, hosting-provider infrastructure, commodity VPNs, simple request automation, public proof-of-concept adaptation, or basic follow-on commands. Higher-maturity activity may use rotating source infrastructure, residential proxies, compromised internal hosts, cloud-hosted infrastructure, VPN ingress paths, staged tool retrieval, delayed follow-on behavior, and operational timing designed to blend with firmware updates, package operations, network maintenance, vendor support, monitoring, or administrator troubleshooting.
Operational Scale
Single exposed UniFi OS asset to multi-site network-management exposure
Operational scale ranges from activity against one vulnerable UniFi OS Server or management interface to broader exposure when compromised systems manage multiple gateways, firewalls, VPN paths, DNS settings, wireless networks, recorders, storage appliances, remote sites, or downstream network devices. Within one organization, scale can expand from one management-plane event to site-level network-control review, administrator and API-token review, configuration-integrity validation, device-adoption assurance, remote-access review, and business-continuity decisions for network-dependent operations.
Escalation Likelihood
Moderate to High
Escalation likelihood is moderate to high when suspicious UniFi OS management-plane activity is followed by update-endpoint access, package-management behavior, command execution, sudo usage, root-context activity, administrator changes, API token activity, configuration export, device-adoption changes, outbound communication, internal scanning, device enumeration, or downstream gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, or managed-device changes. Escalation likelihood increases when affected systems are internet-exposed, control remote-site connectivity, administer firewall or VPN policy, support wireless access, operate inside privileged management networks, or lack telemetry needed to prove containment.
S16 — Targeting Probability Assessment
Overall Targeting Probability
High
Targeting Drivers
· UniFi OS deployments may manage gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, controller, and device-adoption functions that provide high operational value if compromised.
· Public exploitation context and KEV treatment increase urgency because vulnerable systems with reachable management paths may be targeted before normal patch cycles complete.
· Authentication bypass and traversal-like access behavior can reduce reliance on stolen credentials, user interaction, or conventional phishing success.
· Command injection and privileged execution potential increase attacker value because the management platform may provide a pathway to root-level control and downstream infrastructure manipulation.
· Exposed management interfaces, broad VPN administration paths, weak segmentation, incomplete asset inventories, limited request-path logging, and appliance-only telemetry can make exploitation harder to detect and prove.
· Downstream configuration impact has high pressure value because firewall rules, VPN access, DNS behavior, wireless trust, routing, device adoption, recorder infrastructure, storage access, and segmentation boundaries may affect business continuity and security assurance.
· Adversaries benefit from environments where firmware updates, package operations, controller upgrades, backups, device adoption, gateway changes, wireless changes, VPN changes, DNS changes, vendor support, monitoring, security testing, and incident response are not well documented or baselined.
· Targeting probability should be assessed through UniFi OS exposure, affected device role, management-plane reachability, fixed-version deployment, telemetry coverage, administrator baseline quality, downstream configuration visibility, and local evidence of exploit-path behavior rather than CVE identifiers or scanner findings alone.
Most Likely Targets
· Internet-exposed or broadly reachable UniFi OS Server deployments, UniFi OS consoles, cloud gateways, dream machines, cloud keys, gateways, controller hosts, and management interfaces.
· UniFi OS systems controlling gateways, firewalls, routing, VPN access, DNS behavior, wireless networks, segmentation boundaries, remote sites, and customer-facing or business-critical locations.
· Administrator accounts, API tokens, local users, SSH access where present, device-adoption workflows, backup functions, configuration-export paths, and management permissions.
· Network devices, access points, switches, gateways, firewalls, VPN systems, DNS services, recorder infrastructure, storage appliances, monitoring systems, and other downstream management targets.
· MSP-administered networks, distributed branch environments, education campuses, retail and hospitality sites, healthcare offices, professional services networks, public-sector environments, and organizations with limited infrastructure telemetry.
· Organizations with exposed management paths, incomplete UniFi OS inventory, delayed fixed-version deployment, weak administrator baselines, limited UniFi OS logging, incomplete downstream configuration telemetry, broad remote administration, or inconsistent change-management records.
S17 — MITRE ATT&CK Chain Flow Mapping
Stage 1: Management-Plane Exploit Path Access
The adversary targets a vulnerable UniFi OS management interface or administration path and attempts to move through the exposed application surface into protected functionality. This stage should be mapped only when telemetry supports management-plane exploit-path activity, not merely vulnerable version state or scanner output.
· T1190 Exploit Public-Facing Application.
Stage 2: Command Execution Through UniFi OS Service Context
The adversary executes commands through the affected UniFi OS service path, package-update context, or application service context. This stage should be mapped when process, command-line, system, package-management, or incident-response evidence supports command execution.
· T1059 Command and Scripting Interpreter.
· T1059.004 Command and Scripting Interpreter: Unix Shell.
Stage 3: Privileged or Root-Context Activity
The adversary obtains or attempts to obtain elevated execution through sudo-assisted behavior, root-context process activity, service modification, or privileged command execution. This stage should be mapped only when sudo, effective-user, process, system, or incident-response evidence supports privilege escalation or privileged activity.
· T1068 Exploitation for Privilege Escalation.
Stage 4: Downstream Network Service Discovery
The adversary enumerates network devices, management interfaces, internal services, or adjacent infrastructure after suspected UniFi OS compromise. This stage should be mapped only when network telemetry, UniFi OS logs, endpoint telemetry, or incident-response evidence supports internal scanning, device enumeration, management-interface discovery, or downstream infrastructure reconnaissance.
· T1046 Network Service Discovery.
S18 — Attack Path Narrative (Signal-Aligned Execution Flow)
UniFi OS control-plane compromise through authentication bypass and command injection begins when an adversary targets a vulnerable UniFi OS management interface or administration path and attempts to move through the exposed management-plane surface into protected functionality. The attacker’s objective is to convert management-plane reachability into unauthorized protected endpoint access, update or package-related abuse, command execution, privileged or root-context activity, administrator or configuration manipulation, and potential downstream network-control impact. The attack path is defined by management-plane exploit-path access, protected functionality reachability, command execution, privileged activity, administrator or configuration change, and downstream infrastructure discovery or control-plane impact. Rogue administrator creation, persistence, configuration export, credential exposure, internal scanning, or downstream network modification should be treated as conditional amplification unless supporting telemetry confirms those behaviors.
Stage 1: Management-Plane Exposure and Exploit-Path Access
The adversary targets a vulnerable UniFi OS management interface, exposed administration path, VPN-accessible management path, reverse-proxy destination, or internal management interface. Observable evidence may include suspicious source access, unfamiliar internet infrastructure, unusual VPN ingress, hosting-provider sources, residential proxy sources, newly observed internal hosts, traversal-like request behavior, authentication-gateway anomalies, repeated path variation, abnormal request ordering, update-endpoint probing, or response anomalies. This stage is not sufficient by itself to establish compromise because exposed management interfaces, scanning, vulnerability assessment, security testing, monitoring, vendor support, and ordinary denied requests may produce similar signals. This stage becomes material when suspicious management-plane access aligns with exploit-path request behavior, protected path access, update or package activity, service instability, administrator anomalies, or downstream follow-on activity.
Stage 2: Protected UniFi OS Functionality Reachability
The adversary reaches protected UniFi OS functionality after authentication-bypass or traversal-like access behavior. The relevant signal is not simply that the system is vulnerable or exposed; it is evidence that activity reached management-plane functions, update paths, package-related behavior, application-update workflows, protected API paths, administrative functions, or other UniFi OS service areas that should normally require authorized access. This stage changes the event from exposure into suspected exploitation. It becomes materially significant when protected functionality access occurs near suspicious source context, repeated exploit-path requests, abnormal response behavior, update-endpoint interaction, package-management activity, administrator-state anomalies, or service instability.
Stage 3: Command Execution Through UniFi OS Service Context
The adversary attempts to execute commands through the affected UniFi OS service path, update-package context, package-management mechanism, or application service context. Observable evidence may include unexpected child processes from UniFi OS service contexts, shell execution, interpreter execution, command chaining, package-manager execution, file retrieval, archive extraction, network utility execution, service restart behavior, or process execution from temporary, application-writable, update, package, or staging paths. This stage is the primary technical pivot because it moves the incident from management-plane access into host execution. It should not be assumed from request activity alone; it becomes materially significant when process, system, endpoint, package-management, sudo, network, or incident-response evidence supports command execution.
Stage 4: Privileged or Root-Context Activity
The adversary obtains or attempts to obtain elevated control through sudo-assisted execution, root-context process activity, privileged command execution, service modification, package-script activity, permission changes, local user changes, SSH configuration changes, or other system-level actions. This stage increases business risk because UniFi OS may operate as a trusted management layer for gateways, firewalls, VPN paths, DNS behavior, wireless networks, recorders, storage appliances, and managed devices. Privileged or root-context activity should not be inferred from management-plane access alone. It becomes materially significant when sudo logs, effective-user context, process telemetry, system logs, file telemetry, package-management logs, service-change records, or incident-response evidence support privileged execution or system-level modification.
Stage 5: Administrator, Configuration, and Device-Trust Impact
The adversary may attempt to manipulate administrator accounts, API tokens, local users, administrative sessions, SSH access, device-adoption workflows, backup functions, configuration exports, gateway policy, firewall rules, routing, VPN settings, DNS behavior, wireless configuration, recorder settings, storage access, or managed-device trust. This stage creates control-plane uncertainty because authorized-looking management actions may be difficult to separate from adversary-driven changes without administrator audit records, configuration-change logs, change-management context, and incident-response validation. It becomes high risk when administrator or configuration changes occur near exploit-path activity, command execution, sudo activity, suspicious source access, outbound communication, internal scanning, or maintenance mismatch.
Stage 6: Downstream Network Discovery and Control-Plane Expansion
The adversary may use the compromised UniFi OS system, related management host, or recently active source system to enumerate network devices, discover internal services, access additional management interfaces, probe adjacent infrastructure, or move toward broader control-plane impact. Observable evidence may include internal scanning, device enumeration, management-interface discovery, SNMP activity, SSH access, web-admin access, API probing, access to gateways, switches, firewalls, VPN systems, DNS services, wireless infrastructure, recorder systems, storage appliances, backup systems, monitoring systems, or other high-value management targets. This stage should remain conditional unless network telemetry, UniFi OS logs, endpoint telemetry, administrator records, configuration records, or incident-response evidence supports downstream reconnaissance or infrastructure impact.
S19 — Attack Chain Risk Amplification Summary
UniFi OS control-plane compromise amplifies risk because it targets a platform that may concentrate gateway administration, firewall policy, routing, VPN access, DNS behavior, wireless configuration, device adoption, recorder infrastructure, storage access, controller workflows, and privileged network-management trust. The chain becomes materially more dangerous when suspicious management-plane exploit-path activity is followed by protected functionality access, update or package activity, command execution, sudo or root-context behavior, administrator changes, configuration export, outbound communication, internal scanning, device enumeration, or downstream network-control changes.
· Broad UniFi OS dependency increases exposure because the platform may support site connectivity, remote access, wireless access, segmentation, firewall policy, DNS behavior, recorder infrastructure, storage access, device adoption, and network operations.
· Internet-exposed or broadly reachable management interfaces increase risk because adversaries may target vulnerable systems without requiring stolen credentials, user interaction, or conventional phishing success.
· Authentication-bypass behavior increases concern when suspicious source access aligns with traversal-like request activity, protected path reachability, update-endpoint access, package-management behavior, service instability, or administrator anomalies.
· Command execution becomes materially significant when UniFi OS service contexts spawn shells, interpreters, package managers, network utilities, file-retrieval tools, archive utilities, service-management tools, or other unexpected child processes.
· Sudo-assisted or root-context activity amplifies risk because it may allow modification of services, users, permissions, update behavior, SSH settings, package components, logs, or other host-level controls.
· Administrator-state changes increase concern when newly created, rarely used, unfamiliar, API-token-based, or unusual-source administrative activity occurs near exploit-path behavior or command-execution evidence.
· Configuration changes amplify business impact when they affect gateway policy, firewall rules, routing, VPN access, DNS settings, wireless configuration, device adoption, recorder behavior, storage access, segmentation boundaries, or managed-device trust.
· Outbound communication increases concern when UniFi OS systems or related management hosts contact rare, newly observed, low-reputation, unusual ASN, unexpected geographic, tunnel-like, or role-inconsistent destinations after suspected exploit-path activity.
· Internal scanning, device enumeration, management-interface discovery, SNMP activity, SSH access, web-admin access, or API probing increases risk when it follows suspected UniFi OS compromise or originates from a source tied to abnormal management-plane access.
· Business exposure increases when affected systems support executive sites, remote offices, regulated environments, customer-facing locations, production networks, wireless access, VPN access, surveillance infrastructure, storage appliances, privileged management networks, or critical segmentation boundaries.
· Incomplete UniFi OS logging, reverse-proxy request detail, endpoint process telemetry, sudo logs, package-management records, administrator audit events, downstream configuration logs, exposure records, or change-management context can force broader validation because the organization cannot quickly prove whether control-plane trust remained intact.
· Response burden increases because teams must validate UniFi OS exposure, fixed-version deployment, pre-patch compromise possibility, management-plane access, update and package behavior, command execution, privileged activity, administrator state, configuration integrity, downstream network controls, legal obligations, business impact, and executive assurance.
S20 — Tactics, Techniques, and Procedures

Figure 3
UniFi OS control-plane compromise attack-chain model showing management-plane exposure, authentication bypass, protected functionality reachability, update or package abuse, command execution, sudo-assisted or root-context activity, administrator and configuration impact, and downstream network-control exposure.
Management-Plane Exposure and Access
Adversaries may target internet-reachable UniFi OS management interfaces, VPN-accessible administration paths, reverse-proxy destinations, secure access paths, or internal management interfaces. Activity may appear as scanning, suspicious source access, repeated management requests, unfamiliar geographies, suspicious ASNs, hosting-provider sources, residential proxy sources, newly observed internal hosts, unmanaged systems, or sources outside approved administrator baselines. This behavior becomes risk-relevant when management-plane access aligns with exploit-path request behavior, protected functionality reachability, update-endpoint activity, administrator anomalies, or downstream follow-on behavior.
Authentication Bypass and Traversal-Like Request Behavior
Adversaries may attempt to bypass expected authentication controls or use traversal-like request behavior to reach protected UniFi OS functionality. Relevant activity may include authentication-gateway anomalies, encoded path variations, unexpected file-access paths, request-normalization mismatches, repeated path variation, abnormal request ordering, or unusual response-code patterns. This behavior should be evaluated against approved vulnerability scanning, exposure assessment, security testing, monitoring, and incident-response activity before being treated as suspected exploitation.
Protected Update or Package Function Interaction
Adversaries may interact with update endpoints, package-management paths, application-update workflows, package retrieval behavior, or update-triggered service activity after reaching protected functionality. This activity becomes high risk when it occurs outside approved maintenance windows, follows suspicious management-plane access, triggers service instability, aligns with package-management errors, or precedes command execution, file retrieval, archive extraction, outbound communication, administrator changes, or configuration changes.
Command Execution From UniFi OS Service Contexts
Adversaries may execute commands through UniFi OS web, application, controller, update, package-management, or service-wrapper contexts. Relevant behavior may include unexpected child processes, shell execution, interpreter execution, command chaining, file retrieval, archive extraction, package-manager execution, network utility execution, service-management commands, or execution from temporary, application-writable, update, package, or staging paths. This activity becomes high risk when service-context execution follows suspicious management-plane or update-path activity and lacks an approved maintenance explanation.
Sudo-Assisted or Root-Context Activity
Adversaries may attempt privileged execution through sudo usage, root-context process activity, permission changes, service modification, package-script behavior, local user changes, SSH configuration changes, or other system-level actions. This behavior is operationally significant because privileged activity can affect the integrity of the UniFi OS host, service configuration, update behavior, logging, administrator access, and downstream control-plane trust. It becomes high risk when sudo or root-context evidence aligns with exploit-path activity, command execution, suspicious file activity, outbound communication, administrator changes, or configuration manipulation.
Administrator, API Token, and Session Manipulation
Adversaries may create, modify, or misuse administrator accounts, API tokens, local users, administrative sessions, SSH access, or management permissions. This behavior becomes high risk when newly created, rarely used, unusual-source, or API-token-based administrative activity occurs near suspicious management-plane access, command execution, sudo activity, update-package behavior, outbound communication, or configuration change. Administrator changes should be validated against approved maintenance, incident response, vendor support, device onboarding, and change-management records.
Configuration Export and Management Data Access
Adversaries may attempt to access or export UniFi OS configuration data, backups, stored management data, device configuration, network settings, credential material, or administrative artifacts. This behavior becomes materially significant when backup export, configuration export, sensitive file access, credential access, or unusual file activity follows exploit-path behavior, command execution, privileged activity, or suspicious administrator use. Configuration and backup access should be evaluated against approved backup jobs, migrations, vendor support, recovery operations, and incident-response workflows.
Downstream Network-Control Manipulation
Adversaries may modify or abuse gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless settings, device-adoption workflows, recorder behavior, storage access, segmentation boundaries, or managed-device trust. This behavior is high impact because it may affect connectivity, remote access, monitoring visibility, physical-security infrastructure, storage availability, customer-facing operations, or network segmentation. It becomes highest risk when downstream changes occur near exploit-path activity, command execution, administrator anomalies, suspicious source access, outbound communication, or lack of approved change records.
Outbound Communication and Tool Staging
Adversaries may cause UniFi OS systems, controller hosts, or related management systems to contact newly observed, rare, low-reputation, unusual ASN, unexpected geographic, tunnel-like, or role-inconsistent destinations. Activity may involve file retrieval, package-repository access, HTTP or HTTPS communication, DNS queries, SSH traffic, tunnel-like protocols, abnormal byte volume, or process-network connections. This behavior should be evaluated against approved vendor services, update destinations, monitoring tools, backup systems, remote-management platforms, security testing, and incident-response infrastructure before being treated as malicious.
Internal Discovery and Management-Interface Reconnaissance
Adversaries may enumerate network devices, discover internal services, access additional management interfaces, probe adjacent infrastructure, or identify gateways, switches, access points, firewalls, VPN systems, DNS services, recorder systems, storage systems, backup systems, monitoring systems, or high-value management targets. This behavior becomes risk-relevant when it follows suspected UniFi OS compromise, originates from a compromised UniFi OS system or related source, or aligns with command execution, outbound communication, administrator changes, or downstream configuration activity.
Operational Blending With UniFi Administration Workflows
Adversaries may attempt to blend malicious behavior into normal UniFi OS activity such as firmware updates, package operations, controller upgrades, backups, device adoption, gateway changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, monitoring, vulnerability management, security testing, administrator troubleshooting, or incident-response actions. This blending is effective because legitimate UniFi OS operations may involve management-plane access, update activity, package behavior, service restarts, administrator changes, configuration changes, outbound communication, and downstream device management.
S20A — Adversary Tradecraft Summary
UniFi OS control-plane compromise targets the trust relationship between management-plane access, protected UniFi OS functionality, update or package mechanisms, command execution, privileged system behavior, administrator state, configuration integrity, and downstream network-control authority. The adversary objective is to convert vulnerable UniFi OS exposure into control-plane uncertainty, privileged execution, infrastructure manipulation, or downstream network-impact potential while blending into normal administration and maintenance workflows.
· The core tradecraft pattern is suspicious UniFi OS management-plane access followed by protected functionality reachability, update or package activity, command execution, sudo or root-context behavior, administrator-state change, configuration change, outbound communication, internal scanning, device enumeration, or downstream network-control activity.
· The behavior is not dependent on a single CVE identifier, proof-of-concept name, request string, user agent, source IP, file hash, tool name, malware family, actor attribution, or static IOC.
· Adversaries may use exposed management interfaces, authentication-bypass paths, traversal-like request behavior, update endpoints, package mechanisms, shell execution, sudo-assisted activity, root-context execution, administrator changes, configuration export, device enumeration, and downstream management access.
· The strongest operational risk occurs when suspicious activity affects UniFi OS systems that manage gateways, firewalls, routing, VPN access, DNS behavior, wireless networks, segmentation boundaries, remote sites, customer-facing locations, regulated environments, surveillance infrastructure, storage appliances, or privileged management networks.
· Detection requires visibility into the management-plane behavior that initiates the chain and the UniFi OS, process, sudo, package-management, network, administrator, configuration, change-management, and incident-response evidence that confirms or disproves impact.
· Response requires treating suspected UniFi OS exploitation as a network-management control-plane trust incident, not a routine patch ticket, isolated scanner finding, single denied request, ordinary update event, or standard administrator troubleshooting issue.
· The behavior remains durable because the adversary objective is to convert vulnerable network-management infrastructure into privileged control or infrastructure-trust uncertainty regardless of the specific CVE label, request variant, source infrastructure, tool name, or public exploit implementation used.
S21 — Detection Strategy Overview
Detection Philosophy
Detection for UniFi OS control-plane compromise through authentication bypass and command injection must prioritize management-plane exploit-path behavior, unauthorized control-plane state change, suspicious update-package activity, command execution from UniFi OS service contexts, sudo-assisted privilege escalation, and downstream network-infrastructure modification over vulnerability-state identification alone. The detection model should treat UniFi OS compromise as a durable network-management control-plane exposure pathway where exploitation may affect gateway administration, routing, firewall policy, VPN configuration, wireless-network settings, device adoption, administrator accounts, recorder infrastructure, storage appliances, or controller-managed network devices depending on the deployed UniFi OS role. Coverage should focus on suspicious management-plane requests, abnormal authentication-validation paths, traversal-like access behavior, update-endpoint abuse, unexpected child processes, privileged command execution, control-plane configuration change, and post-exploitation network behavior that occurs before, during, or after suspected UniFi OS compromise.
Primary Detection Anchors
· Abnormal UniFi OS management-plane requests involving authentication-validation paths, update endpoints, traversal-like path patterns, unexpected file-access paths, or request-normalization mismatches.
· Requests to UniFi OS management interfaces from unfamiliar source IPs, unusual geographies, suspicious ASNs, VPN ingress paths, newly observed internal hosts, unmanaged systems, or sources outside approved administration paths.
· UniFi OS update-package, package-management, or application-update activity occurring outside approved maintenance windows or from suspicious request contexts.
· Unexpected process creation, shell execution, package-manager execution, scripting activity, command chaining, or child-process behavior from UniFi OS, update, web, controller, or application service contexts.
· Sudo usage, privileged command execution, root-context process activity, or privilege-escalation indicators associated with UniFi OS application or update-service behavior.
· Creation, modification, or unexpected use of UniFi administrator accounts, API tokens, sessions, device adoption workflows, or management-plane configuration objects.
· Firewall, routing, VPN, DNS, wireless, device-management, recorder, storage, or gateway configuration changes occurring near suspicious management-plane or command-execution activity where those UniFi OS roles are deployed.
· Outbound communication, internal scanning, device enumeration, credential access, tool staging, or downstream network-control activity following suspected UniFi OS compromise.
Detection Prioritization Model
· Highest priority should be assigned to suspicious UniFi OS management-plane path activity followed by update-endpoint abuse, command execution, sudo activity, root-context process behavior, rogue administrator creation, control-plane configuration changes, or downstream infrastructure modification.
· High priority should be assigned to repeated authentication-validation, traversal-like, package-update, or exploit-path request patterns against UniFi OS from non-standard source systems, public ingress paths, newly observed sources, unmanaged hosts, VPN ingress ranges, or network segments outside approved administration paths.
· High priority should be assigned to UniFi OS process execution where web, application, update, package-management, or controller service contexts spawn shells, interpreters, package managers, network utilities, file-retrieval tools, archive utilities, or privileged commands without an approved maintenance workflow.
· Medium priority should be assigned to suspicious management-plane access, unusual administrative sessions, unexpected API activity, device-adoption changes, or configuration changes when supporting process, network, privilege, or change-management evidence is incomplete.
· Lower priority should be assigned to vulnerability scan results, exposed management interfaces, patch-state findings, isolated web errors, single denied requests, or update activity that aligns with vendor guidance, approved maintenance, known administrator systems, and validated change records.
Correlation Strategy (Strict Enforcement)
· Correlate UniFi OS management-plane access logs, reverse-proxy logs, web/application logs, update-service logs, system logs, authentication logs, administrator activity logs, endpoint telemetry, process telemetry, sudo logs, package-management logs, network-flow telemetry, DNS logs, firewall logs, and change-management records where available.
· Require temporal linkage between suspicious management-plane request behavior and downstream process execution, privileged command activity, control-plane configuration change, administrator-session anomaly, or network-infrastructure modification before escalating to suspected compromise.
· Treat vulnerable-state findings, scanner output, exposed UniFi management interfaces, and isolated web errors as exposure indicators, not compromise indicators.
· Do not attribute ordinary UniFi updates, package operations, backup jobs, device adoption, controller maintenance, gateway configuration changes, or administrator troubleshooting to exploitation unless suspicious source context, exploit-path behavior, or downstream control-plane behavior is also present.
· Prioritize correlation that captures authentication-gateway bypass indicators, traversal-like request patterns, update-endpoint misuse, command execution, sudo-assisted privilege escalation, rogue administration, outbound communication, and downstream device-control activity.
· Preserve separate analytic outcomes for exposure, attempted exploitation, suspected management-plane compromise, suspected root-level compromise, downstream network-control impact, and confirmed post-exploitation activity.
Telemetry Prioritization
· UniFi OS management-plane access logs.
· UniFi OS web, application, controller, and update-service logs where available.
· UniFi OS system logs, authentication logs, sudo logs, package-management logs, and process telemetry where available.
· Endpoint or server telemetry for self-hosted UniFi OS Server deployments.
· Network telemetry covering public ingress, reverse-proxy paths, firewall traffic, management-plane access, east-west device-control traffic, and outbound communication.
· DNS, proxy, firewall, and secure web gateway telemetry for outbound follow-on behavior.
· UniFi administrator activity, session, API, device adoption, and configuration-change logs where available.
· Gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, and managed-device configuration telemetry where those UniFi OS roles are deployed.
· Asset inventory and exposure-management data identifying UniFi OS servers, consoles, gateways, recorders, storage appliances, controller hosts, exposed management interfaces, firmware versions, and approved management paths.
· Change-management records for UniFi OS patching, firmware updates, controller upgrades, device adoption, backup, gateway configuration, firewall/routing changes, and administrative maintenance.
Detection Design Constraints
· Detection must distinguish exposed or vulnerable UniFi OS assets from active exploitation or post-exploitation behavior.
· Detection must avoid relying on public proof-of-concept names, static exploit strings, narrow request fragments, scanner output, or version state as the primary detection strategy.
· Detection must account for environments where UniFi appliance logs, full request bodies, endpoint process telemetry, sudo logs, package-management logs, or local shell visibility are unavailable.
· Detection must not assume that suspicious management-plane access alone represents successful command execution or root compromise.
· Detection must preserve operational separation between approved updates, administrator maintenance, device adoption, backup activity, firmware upgrades, gateway configuration changes, and unauthorized control-plane manipulation.
· Detection must use behavior-led correlation wherever possible instead of single-event alerting.
· Detection must avoid forcing endpoint-only, cloud-only, or YARA-based coverage where the relevant telemetry cannot observe the UniFi OS exploit path.
· Detection must preserve report scope around the durable UniFi OS control-plane compromise model rather than reducing the report to a single CVE, while still allowing applicable CVEs to be covered in vulnerability context, references, and behavioral coverage mapping.
Baseline and Deployment Requirements
· Establish a verified UniFi OS inventory covering UniFi OS Server deployments, cloud gateways, dream machines, cloud keys, network video recorders, storage appliances, gateway consoles, controller hosts, exposed management interfaces, firmware versions, and administrative access paths where applicable.
· Baseline approved administrator source IPs, VPN ingress ranges, jump hosts, privileged access workstations, remote-management tools, identity-provider paths, maintenance networks, vendor-support paths, and monitoring systems.
· Baseline normal UniFi management-plane request paths, administrative login patterns, API activity, update checks, package-management behavior, firmware-update timing, backup operations, and device-adoption workflows.
· Baseline normal process execution for self-hosted UniFi OS Server and observable appliance environments, including approved update processes, package managers, service restarts, backup jobs, and maintenance scripts.
· Baseline normal sudo usage, root-context activity, service-account behavior, shell execution, interpreter execution, file staging, archive extraction, and outbound communication from UniFi OS systems where host telemetry exists.
· Baseline normal gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, and managed-device configuration changes where those roles are present.
· Confirm SIEM field mappings preserve source IP, destination host, destination interface, request path, HTTP method, response status, user agent, administrator account, session ID, API token context, process lineage, command line, user context, sudo activity, package-management event, device identifier, configuration object, network segment, and change-window context.
· Ensure exceptions are tied to approved administrators, maintenance windows, update systems, device-adoption workflows, vendor support, monitoring, backup, vulnerability management, security testing, and incident response.
· Ensure exceptions do not suppress suspicious management-plane requests followed by command execution, sudo activity, unauthorized administrator changes, or downstream network-control changes.
Variant Resilience Requirements
· Detection must remain effective against modified exploit chains, altered request paths, changed user agents, renamed tools, different source infrastructure, delayed command execution, altered package-update behavior, and non-public exploit variants.
· Detection should prioritize abnormal management-plane paths, traversal-like request behavior, update-endpoint misuse, service-context child processes, sudo-assisted privilege escalation, root-context execution, administrator-state changes, and downstream control-plane modification.
· Detection must support both attempted-exploitation visibility and post-exploitation consequence visibility.
· Detection must remain useful when payload inspection is unavailable by correlating management-plane metadata, network telemetry, host telemetry, system logs, administrator activity, change records, and downstream configuration changes.
· Detection must account for adversaries staging activity from compromised internal hosts, VPN-connected systems, hosting providers, residential proxies, cloud infrastructure, or systems with partial administrative legitimacy.
· Detection must not depend on the presence of malware, a stable file artifact, a webshell, or known command-and-control infrastructure because successful control-plane compromise may initially present as command execution, administrative-state change, or configuration manipulation.
· Detection must support future related UniFi OS or network-management control-plane vulnerability coverage without requiring the report to be rewritten around a single CVE.
Operational Detection Model
· Treat suspicious UniFi OS management-plane exploit-path activity as a network-management control-plane incident candidate.
· Escalate when suspicious authentication-validation, traversal-like, update-endpoint, or exploit-path request activity is followed by unexpected process execution, sudo usage, root-context activity, administrator changes, device-adoption changes, configuration modification, outbound communication, or downstream network-control behavior.
· Use source reputation, administrator baseline, request path, device role, management-interface exposure, change window, process lineage, user context, sudo context, asset criticality, and downstream configuration impact to separate authorized maintenance from exploitation behavior.
· Route high-confidence detections to network infrastructure, identity, incident response, firewall, wireless, gateway, surveillance, storage, and platform owners according to the affected UniFi OS role because the primary risk is control-plane compromise rather than isolated host execution.
· Require incident triage to determine whether activity represents exposure, attempted exploitation, suspected management-plane compromise, suspected root compromise, unauthorized configuration change, or confirmed downstream network-control impact.
· Preserve escalation language that reflects confidence level and observed behavior rather than assuming full UniFi OS compromise from a single weak signal.
S22 — Primary Detection Signals
Primary Detection Signals
· Abnormal UniFi OS management-plane requests involving authentication-validation paths, update endpoints, traversal-like path behavior, unexpected file-access paths, request-normalization mismatches, or access patterns inconsistent with approved administrative use.
· Repeated access to UniFi OS management interfaces from unfamiliar source IPs, unusual geographies, suspicious ASNs, hosting providers, residential proxy ranges, VPN ingress paths, newly observed internal hosts, unmanaged systems, or sources outside approved administration paths.
· UniFi OS update-package, package-management, or application-update activity occurring outside approved maintenance windows, outside expected update workflows, or after abnormal management-plane request behavior.
· Unexpected child-process activity from UniFi OS web, application, controller, update, or package-management service contexts where host-level telemetry exists, including shell execution, interpreter execution, package-manager execution, command chaining, file retrieval, archive extraction, or script execution.
· Sudo usage, root-context process activity, privileged command execution, service modification, or privilege-escalation indicators associated with UniFi OS application, update, package-management, or controller service behavior.
· Creation, modification, or unexpected use of UniFi administrator accounts, API tokens, administrative sessions, device adoption workflows, backup functions, or management-plane configuration objects.
· Gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, or managed-device configuration changes occurring near exploit-path activity where those UniFi OS roles are deployed.
· Rare outbound communication, unfamiliar external destination access, internal scanning, device enumeration, credential access, tool staging, or downstream network-control behavior after suspected UniFi OS compromise activity.
Supporting Detection Signals
· HTTP response anomalies, repeated denied requests, redirect anomalies, authentication-validation failures, unusual response-size patterns, or abnormal management-plane status-code sequences near suspected UniFi OS exploit-path activity.
· Access to rarely used UniFi OS paths, update-related endpoints, package-management functions, backup-related paths, administrative API paths, device-adoption paths, or configuration endpoints by sources outside the approved administration baseline.
· User-agent anomalies, automation-like request timing, repeated requests with small path changes, unusual URL encoding, path canonicalization differences, or traversal-style request construction against UniFi OS management interfaces.
· New administrative sessions, administrative API activity, device-adoption activity, backup activity, or configuration activity following suspicious source access, failed authentication patterns, abnormal path behavior, or update-endpoint activity.
· UniFi OS service restarts, application errors, update-service instability, package-management errors, unexpected daemon behavior, or system-level fault events occurring near exploit-path request activity.
· File creation, file modification, temporary file use, archive extraction, script placement, unusual download activity, or execution from temporary, application, update, package, or user-writable paths where server-side or appliance telemetry exposes those signals.
· DNS, firewall, proxy, or network-flow events showing outbound connections from UniFi OS systems to newly observed, rare, low-reputation, geographically unusual, or role-inconsistent destinations.
· Change-management mismatch where UniFi OS updates, package operations, administrator changes, device adoption, backup operations, firmware activity, or configuration changes occur without a corresponding approved maintenance record.
Exploit Attempt and Instability Signals
· Bursts of UniFi OS management-plane requests involving authentication-validation paths, update endpoints, unexpected file paths, encoded path elements, repeated path variations, traversal-style construction, or unusual request ordering.
· Repeated attempts against exposed UniFi OS management interfaces from the same source, source network, ASN, hosting provider, residential proxy range, VPN path, or newly observed internal source.
· Management-plane request activity followed by HTTP 5xx errors, application errors, update-service errors, package-management failures, service restarts, process crashes, or abnormal system instability.
· Update-endpoint or package-management activity followed by shell execution, interpreter execution, network utility execution, file retrieval, archive extraction, command chaining, sudo usage, or root-context process activity.
· Authentication, session, administrator-state, or API anomalies occurring shortly after abnormal path behavior, update-endpoint access, or management-plane request bursts.
· Similar exploit-path request patterns observed across multiple UniFi OS assets, management interfaces, gateways, consoles, controllers, or exposed administration paths.
· Internal scanning, device enumeration, network discovery, service discovery, or management-plane enumeration preceding suspicious UniFi OS access or following suspected compromise.
· Logging gaps, service interruptions, unexpected restart behavior, administrative-console errors, monitoring visibility reduction, or unexplained telemetry loss near suspected UniFi OS exploit-path activity.
Outbound Communication Signals
· Outbound communication from a UniFi OS system to unfamiliar external infrastructure before or after exploit-path request behavior, update-endpoint activity, or command-execution evidence.
· Newly observed DNS queries, rare domains, rare IP destinations, unusual ASNs, low-reputation destinations, unexpected geographic destinations, or traffic patterns inconsistent with the deployed UniFi OS role.
· HTTP, HTTPS, DNS, SSH, SMB, tunnel-like traffic, unexpected package-repository access, unusual file retrieval, or abnormal byte volume from UniFi OS systems after suspected exploit-path activity.
· External communication from a UniFi OS appliance, server, gateway, recorder, storage appliance, or controller host that does not align with approved update services, monitoring tools, backup destinations, vendor services, or administrator workflows.
· Outbound communication from an internal source host that recently generated abnormal UniFi OS management-plane access.
· Data staging, archive creation, backup export, configuration export, credential material access, or unusual outbound transfer behavior from UniFi OS systems or related management hosts after suspected compromise.
· Communication to newly observed external destinations followed by administrator changes, configuration changes, device-adoption activity, gateway policy changes, or downstream management activity.
Persistence and Post-Exploitation Signals (Conditional)
· Creation, modification, or unexpected use of UniFi administrator accounts, local users, API tokens, sessions, SSH access, remote-access settings, or other administrative access mechanisms.
· Modification of gateway, firewall, routing, VPN, DNS, wireless, device-adoption, recorder, storage, backup, or management-plane configuration where those UniFi OS roles are present.
· Unexpected enabling, disabling, or modification of services, startup behavior, scheduled jobs, package components, update settings, local users, SSH configuration, or remote-management pathways where host or appliance telemetry exposes those signals.
· Placement or execution of scripts, binaries, archives, temporary files, downloaded tools, or suspicious packages on self-hosted UniFi OS Server deployments or observable appliance environments.
· Credential access behavior, sensitive configuration access, backup export, administrator credential change, token misuse, or access to stored network, VPN, device, or management credentials where telemetry exists.
· Security-control weakening, log clearing, logging interruption, backup tampering, monitoring disruption, firewall policy weakening, DNS manipulation, VPN exposure changes, or defensive visibility reduction after suspected UniFi OS compromise.
· Administrative activity from newly created, rarely used, unfamiliar, or geographically unusual administrator identities following exploit-path activity or command-execution behavior.
Lateral Movement and Expansion Signals (Conditional)
· Access from a suspected UniFi OS system or related management host to internal network infrastructure, gateways, switches, access points, firewalls, VPN systems, identity infrastructure, backup systems, monitoring systems, or high-value business systems.
· Internal scanning, device enumeration, ARP or subnet discovery, service enumeration, management-plane discovery, SNMP activity, SSH access, SMB access, RDP access, web-admin access, or API probing after suspected UniFi OS exploit-path activity.
· Downstream configuration changes affecting gateway policy, firewall rules, routing, DNS forwarding, VPN access, wireless SSIDs, device adoption, network segmentation, recorder behavior, storage access, or managed-device trust where those roles are present.
· Administrative sessions, API activity, credential use, or configuration activity expanding from UniFi OS into adjacent network-management, security-management, identity, backup, or monitoring platforms.
· Lateral movement from an internal host that recently generated abnormal UniFi OS management-plane access, especially when the host also shows command execution, credential access, tool staging, rare outbound communication, or access to additional management interfaces.
· Reuse of administrator credentials, API tokens, SSH keys, session material, or management credentials across UniFi OS assets, network devices, or related infrastructure after suspected compromise.
· Cross-segment, cross-site, or cross-management-domain activity that does not align with normal network topology, approved administration paths, device-management workflows, or change records.
Signal Usage Constraints
· Do not treat patch state, vulnerability scan output, exposed management interfaces, or internet exposure as evidence of exploitation by itself.
· Do not treat isolated web errors, denied requests, ordinary update checks, single login failures, or single administrative actions as compromise indicators unless they correlate with suspicious source context, exploit-path behavior, or downstream control-plane activity.
· Do not escalate approved firmware updates, package operations, backups, device adoption, gateway changes, wireless changes, VPN changes, DNS changes, or administrator maintenance when the activity aligns with known administrators, approved systems, expected windows, and validated change records.
· Do not infer command execution or root compromise from management-plane request activity alone without supporting process, sudo, system, endpoint, network, configuration, or incident-response evidence.
· Do not rely on proof-of-concept names, static request fragments, tool names, scanner labels, user-agent strings, or known infrastructure as primary detection signals.
· Do not assume endpoint, sudo, package-management, local shell, or process telemetry exists for all UniFi OS appliance deployments; reduce confidence or keep logic in hunt mode when host-level visibility is unavailable.
· Do not treat downstream gateway, firewall, VPN, DNS, wireless, recorder, storage, or managed-device changes as UniFi compromise evidence unless they occur near suspicious UniFi OS access, exploit-path activity, administrator-state anomalies, or command-execution evidence.
· Do not infer actor attribution from exploit-path behavior, command execution, outbound communication, or configuration changes without incident-specific intelligence and validated evidence.
· Preserve separate analytic outcomes for exposure, attempted exploitation, suspected management-plane compromise, suspected root-level compromise, unauthorized configuration change, downstream network-control impact, and confirmed post-exploitation activity.
S23 — Telemetry Requirements
Endpoint and Process Execution Telemetry
· Endpoint and process telemetry should be collected from self-hosted UniFi OS Server deployments, controller hosts, supporting Linux hosts, management servers, and appliance environments that expose host-level telemetry.
· Process telemetry should capture process creation, parent-child process lineage, command-line execution, working directory, process user, process path, process hash, service context, interpreter execution, shell execution, package-manager activity, network utility execution, archive extraction, file retrieval, and service restart behavior.
· UniFi OS service-context execution should be monitored for unexpected child processes spawned by web, application, controller, update, package-management, backup, or appliance-management components.
· Process telemetry should identify execution from UniFi OS service accounts, application users, update-service contexts, package-management contexts, or root-context processes when those fields are exposed.
· Sudo telemetry, privileged command telemetry, and root-context execution telemetry should be collected from deployments that expose operating-system logs or equivalent appliance diagnostics.
· Endpoint telemetry should capture service modification, startup changes, scheduled jobs, package installation, package removal, local user changes, SSH configuration changes, and remote-management pathway changes where those signals are visible.
· Endpoint telemetry should support differentiation between approved maintenance, vendor-guided update activity, administrative troubleshooting, vulnerability management, incident response, and unauthorized command execution.
· Detection logic must not require endpoint or process telemetry as a universal prerequisite because many UniFi OS appliance deployments may not expose full host-level process visibility to the customer.
Memory and Execution Telemetry
· Memory and execution telemetry is useful where EDR, host security agents, operating-system telemetry, or appliance diagnostics provide runtime visibility.
· Memory telemetry should capture suspicious process injection, unusual module loading, unauthorized code execution, credential-access behavior, sensitive process access, and security-control interference when technically available.
· Execution telemetry should identify unusual interpreter use, shell activity, downloaded tooling execution, package script execution, privilege-escalation behavior, and process ancestry tied to UniFi OS service contexts.
· Runtime telemetry should increase confidence when management-plane exploit-path activity is followed by command execution, sudo activity, root-context execution, credential access, or suspicious outbound communication.
· Memory and execution telemetry should not be required to identify initial UniFi OS exploit-path activity because management-plane compromise may first appear through web logs, update-service behavior, system logs, administrator-state changes, or configuration changes.
· Environments without memory telemetry should preserve detection coverage through management-plane logs, network telemetry, system logs, package-management logs, administrator activity logs, and change-management correlation.
Crash and Fault Telemetry
· Crash and fault telemetry should capture UniFi OS application errors, web-service errors, controller errors, update-service errors, package-management failures, system faults, daemon restarts, service interruptions, abnormal reboot behavior, and administrative-console instability.
· HTTP 5xx response patterns, repeated application errors, request-handling failures, update-service faults, package-operation failures, and process crashes should be correlated with management-plane request activity rather than treated as compromise indicators by themselves.
· Fault telemetry should support triage of attempted exploitation, failed exploitation, exploit-adjacent instability, operational maintenance issues, and post-compromise disruption.
· UniFi OS system logs should be retained for service restarts, daemon failures, package events, authentication anomalies, sudo activity, local user changes, SSH changes, and other operating-system events when exposed to the customer.
· Appliance diagnostics, controller logs, reverse-proxy logs, web logs, and infrastructure monitoring should be combined when direct host fault telemetry is incomplete.
· Service instability should receive higher priority when preceded by abnormal management-plane requests or followed by command execution, privilege activity, administrator changes, configuration changes, outbound communication, or downstream control-plane behavior.
· Isolated faults, restarts, update failures, or administrative-console errors should remain low-confidence signals unless supported by suspicious source context, exploit-path behavior, or post-exploitation evidence.
File and Persistence Telemetry
· File telemetry should capture creation, modification, deletion, download, extraction, execution, and permission changes involving scripts, binaries, archives, temporary files, update packages, package scripts, backup files, configuration exports, and administrative tooling where visible.
· Persistence telemetry should capture service creation, service modification, scheduled job creation, startup modification, package installation, package modification, local user creation, SSH key changes, remote-access changes, and unauthorized management pathway changes when those signals are exposed.
· Self-hosted UniFi OS Server deployments should collect file and persistence telemetry from application directories, update directories, package-management paths, temporary directories, user-writable paths, backup locations, log locations, and administrative staging paths.
· Appliance environments should rely on UniFi OS logs, system diagnostics, configuration records, backup records, update records, and management-plane activity logs when direct file telemetry is unavailable.
· Sensitive configuration access, backup export, device configuration export, credential material access, API token exposure, or unusual access to stored network-management data should be treated as higher risk when correlated with exploit-path activity.
· File and persistence telemetry should not be required for initial exploit detection because UniFi OS compromise may produce command execution, configuration change, administrative-state change, or outbound behavior without durable file artifacts.
· File and persistence events should be correlated with management-plane access, process execution, sudo activity, administrator actions, outbound communication, and change-management records before being escalated as post-exploitation evidence.
Network and Outbound Communication Telemetry
· Network telemetry must capture source IP, destination IP, destination host, destination interface, destination port, protocol, application classification, request timing, connection frequency, directionality, byte volume, user agent when visible, and source network context for UniFi OS management-plane access.
· Web, reverse-proxy, load-balancer, firewall, and secure access telemetry should capture request path, HTTP method, response status, response size, user agent, source IP, destination interface, TLS termination context when available, session identifiers when available, and management-interface exposure path.
· Network telemetry should identify access from unfamiliar internet sources, unusual geographies, suspicious ASNs, hosting providers, residential proxy ranges, VPN ingress paths, newly observed internal hosts, unmanaged systems, and sources outside approved administration paths.
· Outbound telemetry should capture DNS, HTTP, HTTPS, SSH, SMB, tunnel-like protocols, package-repository access, file retrieval, unusual external destinations, abnormal byte volume, and traffic inconsistent with the deployed UniFi OS role.
· Internal network telemetry should capture device enumeration, service discovery, management-plane discovery, SNMP activity, SSH access, web-admin access, SMB access, RDP access, API probing, and access to adjacent network-management or security-management platforms after suspected UniFi OS compromise.
· Network telemetry should support differentiation between internet scanning, failed exploitation, suspicious management-plane activity, approved administration, vendor update behavior, and downstream control-plane impact.
· Network telemetry alone should not be treated as proof of command execution, root compromise, credential theft, or actor attribution without supporting host, system, administrator, configuration, or incident-response evidence.
Web and Application Telemetry (Conditional Availability)
· UniFi OS web and application telemetry should capture management-plane requests, authentication-validation behavior, administrative sessions, API activity, update-endpoint access, package-management activity, device-adoption workflows, backup actions, configuration changes, and application errors when exposed by the deployment.
· Web telemetry should preserve request path, normalized path, raw path when available, HTTP method, response status, response size, source IP, user agent, referrer when available, session context, administrator identity when available, and destination interface.
· Application telemetry should capture administrator login activity, session creation, session reuse, API token use, permission changes, backup activity, device adoption, firmware update actions, gateway policy changes, wireless changes, VPN changes, DNS changes, and role-specific configuration events.
· Update-service telemetry should capture update checks, package retrieval, package installation, package validation, update failures, package-management errors, and update-triggered service restarts.
· Authentication telemetry should capture successful and failed administrative access, unusual source context, unfamiliar device context, anomalous session timing, unusual API use, and authentication-state transitions where UniFi OS exposes those details.
· Web and application telemetry should enrich exploitation and post-exploitation triage, but it should not be used alone to confirm root compromise unless correlated with process, sudo, system, configuration, outbound, or incident-response evidence.
· Where UniFi OS application logs are limited, reverse-proxy logs, firewall logs, administrative audit logs, system diagnostics, and change-management records should be used to preserve management-plane visibility.
Telemetry Availability Requirements
· UniFi OS asset inventory must identify UniFi OS Server deployments, cloud gateways, dream machines, cloud keys, gateways, consoles, recorders, storage appliances, controller hosts, exposed management interfaces, firmware versions, and approved administration paths as applicable.
· Management-plane access telemetry must be available from UniFi OS logs, reverse proxies, firewalls, secure access services, load balancers, or other ingress-control points.
· Web or application telemetry should be available for management-plane requests, administrative access, update-endpoint activity, API activity, device adoption, and configuration changes when the platform exposes those logs.
· Network telemetry should cover internet ingress, VPN ingress, administrator access paths, management VLANs, controller-to-device communication, east-west management traffic, and outbound communication from UniFi OS assets.
· System, sudo, package-management, process, file, and persistence telemetry should be collected from self-hosted UniFi OS Server deployments and appliance environments that expose those signals.
· Administrator activity telemetry should capture administrative session creation, account changes, API token activity, permission changes, backup actions, device adoption, configuration changes, and role-specific management actions.
· Downstream configuration telemetry should be collected for gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, and managed-device changes when those UniFi OS roles are deployed.
· Change-management records must be available to validate approved updates, firmware upgrades, package operations, backups, device adoption, gateway changes, wireless changes, VPN changes, DNS changes, vendor support, security testing, and incident-response actions.
· Incident-response records, vulnerability management records, asset exposure records, and patch records should be available to separate exposure, attempted exploitation, suspected compromise, remediation, and post-remediation validation.
Telemetry Limitations and Gaps
· UniFi OS appliance deployments may not expose full endpoint, sudo, process, package-management, file, or memory telemetry to the customer, limiting direct confirmation of command execution or root-context behavior.
· Reverse-proxy, firewall, or secure access telemetry may preserve request metadata but not full request bodies, normalized paths, application context, session state, or update-service behavior.
· Web and application logs may not consistently expose the raw request path, normalized path, administrator session context, API token context, or internal service behavior needed for high-confidence exploit-path reconstruction.
· Network telemetry may identify suspicious access patterns, outbound communication, or downstream management activity but may not prove exploitation, command execution, credential access, or root compromise by itself.
· Missing administrator audit logs may reduce confidence when assessing account changes, API token use, session anomalies, device adoption, backup exports, or configuration changes.
· Missing downstream configuration telemetry may limit visibility into gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, or managed-device impact after suspected UniFi OS compromise.
· Incomplete asset inventory may make it difficult to distinguish UniFi OS servers, appliances, gateways, controllers, recorders, storage systems, management interfaces, approved administrators, and unmanaged sources.
· Missing change-management context may increase false positives around firmware updates, package operations, device adoption, backups, gateway changes, wireless changes, VPN changes, DNS changes, vendor support, security testing, and incident-response activity.
· Telemetry gaps should reduce confidence ratings, shift detections toward hunt mode, or increase investigation requirements rather than force unsupported compromise conclusions.
S24 — Detection Opportunities and Gaps

Figure 4
Detection Opportunities
· Abnormal UniFi OS management-plane request behavior provides an early opportunity to identify suspected exploit-path activity before confirmed command execution or root-level compromise.
· Authentication-validation anomalies, traversal-style request patterns, unusual path-normalization behavior, update-endpoint access, and unexpected file-access paths provide high-value signals when correlated with suspicious source context.
· UniFi OS update-package, package-management, and application-update activity provide strong detection opportunities when observed outside approved maintenance workflows or near abnormal management-plane request activity.
· Unexpected child-process execution from UniFi OS web, application, controller, update, package-management, or appliance-management contexts provides a high-value host-side detection opportunity where process telemetry exists.
· Sudo usage, privileged command execution, root-context activity, service modification, or package-script execution after exploit-path activity provides a strong escalation opportunity for suspected compromise.
· Administrator-state changes, API token activity, new administrative sessions, device-adoption activity, backup actions, and role-specific configuration changes provide durable control-plane detection anchors.
· Outbound communication from UniFi OS assets to rare, newly observed, low-reputation, geographically unusual, or role-inconsistent destinations provides useful post-exploitation scoping.
· Downstream gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, or managed-device changes provide high-value impact signals when those UniFi OS roles are deployed and activity is linked to suspected exploit-path behavior.
High-Value Correlation Opportunities
· Correlate abnormal UniFi OS management-plane request activity with update-endpoint activity, package-management behavior, application errors, update-service instability, or system faults within the same investigation window.
· Correlate suspicious source access with later administrator-session creation, API token use, administrator-account modification, permission change, device-adoption activity, backup export, or configuration change.
· Correlate update-package or package-management activity with process execution, shell activity, interpreter execution, file retrieval, archive extraction, sudo usage, root-context activity, or service modification where host telemetry exists.
· Correlate exposed management-interface access with reverse-proxy, firewall, secure access, load-balancer, VPN, source-reputation, ASN, geography, and approved-administration baselines.
· Correlate UniFi OS system faults, application errors, update-service errors, package failures, or service restarts with abnormal request activity and downstream administrator or configuration events.
· Correlate outbound DNS, proxy, firewall, and network-flow activity from UniFi OS systems with command-execution evidence, administrator-state changes, backup export activity, or configuration changes.
· Correlate downstream gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, or managed-device configuration changes with prior UniFi OS exploit-path activity, administrator anomalies, or command-execution evidence.
· Correlate activity from internal hosts that accessed UniFi OS abnormally with later lateral movement, credential access, tool staging, rare outbound communication, or access to additional management interfaces.
Detection Gaps
· UniFi OS appliance deployments may not expose full process, sudo, package-management, file, memory, or endpoint telemetry to the customer, limiting direct confirmation of command execution or root-context behavior.
· Web, reverse-proxy, firewall, or secure access telemetry may preserve request metadata but not raw request bodies, normalized paths, internal service routing, session state, or update-service context.
· Limited UniFi OS application logging may reduce visibility into authentication-validation behavior, API token use, administrator-session state, update-endpoint behavior, package-management activity, and device-adoption workflows.
· Network telemetry may identify suspicious ingress, outbound communication, or downstream management activity but cannot independently prove exploitation, command execution, credential access, or root compromise.
· Missing administrator audit logs may reduce confidence when assessing account creation, permission changes, API activity, backup exports, device adoption, or configuration changes.
· Missing downstream configuration telemetry may reduce visibility into gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, or managed-device impact after suspected UniFi OS compromise.
· Incomplete asset inventory may prevent reliable separation of UniFi OS servers, appliances, consoles, gateways, recorders, storage systems, controller hosts, approved administrators, and unmanaged sources.
· Missing change-management records may increase false positives around firmware updates, package operations, backups, device adoption, gateway changes, wireless changes, VPN changes, DNS changes, vendor support, security testing, and incident-response activity.
Operational Blind Spots
· Internet-exposed UniFi OS management interfaces may receive frequent scanning and probing, making it difficult to separate opportunistic exposure noise from exploit-path activity without request, source, timing, and follow-on context.
· Broad administrative access from many locations can weaken source-path baselines and make abnormal administrator behavior harder to distinguish from approved management.
· Environments without ingress logging may lose early exploit-path visibility before activity reaches system, administrator, or configuration logs.
· Appliance-only deployments may reveal administrator or configuration changes while concealing the underlying command-execution path.
· Environments without downstream configuration monitoring may fail to detect network-control impact after compromise.
· Short log-retention windows may prevent reconstruction of the sequence between management-plane access, update behavior, command execution, administrator changes, and downstream impact.
· Undocumented maintenance workflows may generate high false-positive volume around legitimate updates, device adoption, backup exports, firmware activity, and network configuration changes.
False Positive Control Requirements
· Validate whether the source IP, administrator identity, device, VPN path, jump host, privileged access workstation, or management network is approved for UniFi OS administration.
· Validate whether activity aligns with approved firmware updates, package operations, controller upgrades, device adoption, backup activity, gateway changes, wireless changes, VPN changes, DNS changes, vendor support, security testing, or incident-response actions.
· Validate whether management-plane request anomalies occurred near expected vulnerability scanning, exposure assessment, penetration testing, monitoring, or administrative troubleshooting.
· Validate whether update-endpoint or package-management activity aligns with vendor-guided updates, known maintenance windows, approved automation, or documented remediation activity.
· Validate whether child-process execution, sudo activity, service modification, or package-script activity is expected for the deployment type and maintenance window.
· Validate whether administrator-account changes, API token activity, session anomalies, backup exports, or configuration changes match approved change records and known administrators.
· Validate whether outbound communication aligns with approved update services, vendor services, monitoring tools, backup destinations, remote-management platforms, or incident-response workflows.
· Validate whether downstream network-device changes occurred near legitimate network maintenance, device replacement, site onboarding, firewall policy updates, VPN changes, wireless changes, or approved troubleshooting.
Hunt-to-Alert Promotion Criteria
· Promote to alert logic when abnormal UniFi OS management-plane request behavior repeatedly correlates with update-endpoint activity, package-management behavior, administrator-state change, configuration change, command-execution evidence, or outbound communication.
· Promote to alert logic when update-package or package-management activity is followed by unexpected child processes, shell execution, interpreter execution, file retrieval, archive extraction, sudo usage, root-context activity, or service modification.
· Promote to alert logic when UniFi administrator creation, API token activity, session anomalies, device-adoption changes, backup exports, or configuration changes occur near exploit-path request behavior or suspicious source access.
· Promote to alert logic when outbound communication from UniFi OS systems to rare, newly observed, low-reputation, geographically unusual, or role-inconsistent destinations follows exploit-path activity or command-execution evidence.
· Promote to alert logic when downstream gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, or managed-device changes occur near suspected UniFi OS compromise activity and are not explained by approved change records.
· Keep as hunt logic when signals are limited to patch state, scanner output, exposed management interfaces, isolated denied requests, isolated web errors, ordinary update checks, or uncorrelated administrative actions.
· Keep as hunt logic when required field mappings, asset inventory, administrator baselines, source-path baselines, telemetry joins, or change-management validation are insufficient for reliable alerting.
· Keep as hunt logic where appliance-only telemetry prevents confirmation of command execution or root-context behavior and no compensating administrator, network, configuration, or incident-response evidence exists.
Detection Engineering Gaps to Resolve Before S25 Deployment
· Confirm UniFi OS asset inventory, including servers, consoles, gateways, cloud keys, dream machines, recorders, storage appliances, controller hosts, exposed management interfaces, firmware versions, and approved administration paths.
· Confirm which deployments expose host-level telemetry, process telemetry, sudo logs, package-management logs, file telemetry, system logs, appliance diagnostics, administrator audit logs, and configuration-change logs.
· Confirm field mappings for source IP, destination host, destination interface, request path, HTTP method, response status, response size, user agent, administrator identity, session context, API token context, event timestamp, process lineage, command line, sudo activity, package event, configuration object, and change-window context.
· Confirm reverse-proxy, firewall, secure access, load-balancer, VPN, DNS, proxy, network-flow, endpoint, UniFi OS, change-management, and incident-response telemetry can be correlated within reliable time windows.
· Confirm approved administrator sources, VPN ranges, jump hosts, privileged access workstations, management networks, vendor-support paths, monitoring systems, update systems, and backup destinations.
· Confirm false-positive baselines for firmware updates, package operations, controller upgrades, device adoption, backups, gateway changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, security testing, and incident-response activity.
· Confirm downstream configuration telemetry for gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, and managed-device changes where those UniFi OS roles are deployed.
· Confirm SOC triage procedures for separating exposure, attempted exploitation, suspected management-plane compromise, suspected root-level compromise, unauthorized configuration change, downstream network-control impact, and confirmed post-exploitation activity.
· Confirm query-performance limits, lookup quality, enrichment reliability, exception handling, and hunt-to-alert thresholds before enabling production alerting.
S25 — Ultra-Tuned Detection Engineering Rules
NDR / Network Behavioral Analytics
Detection Viability Assessment
NDR / Network Behavioral Analytics has three rules for this EXP report.
· NDR / Network Behavioral Analytics is viable for detecting suspicious network behavior associated with UniFi OS control-plane compromise through authentication bypass and command injection, including abnormal management-plane access, exploit-path request behavior, update-endpoint interaction, suspicious source-path deviation, outbound communication, and downstream network-control activity.
· NDR / Network Behavioral Analytics is strongest where network-flow telemetry, web or reverse-proxy telemetry, firewall telemetry, secure access telemetry, DNS telemetry, management-interface exposure context, UniFi OS asset inventory, approved-administrator source baselines, source-reputation enrichment, and SIEM correlation can be combined.
· NDR / Network Behavioral Analytics can identify suspicious sequencing between abnormal source access, authentication-validation or traversal-style request behavior, update-endpoint activity, outbound communication, internal scanning, device enumeration, and downstream access to network-management infrastructure.
· NDR / Network Behavioral Analytics is not a standalone source for confirming successful command execution, sudo-assisted privilege escalation, root compromise, credential theft, administrator-account misuse, or actor attribution because network telemetry may not observe process lineage, sudo logs, package-management logs, local file activity, administrator intent, or internal UniFi OS service state.
· NDR / Network Behavioral Analytics detections must be correlated with UniFi OS logs, reverse-proxy logs, firewall logs, endpoint telemetry where available, system logs, administrator activity logs, configuration-change records, change-management records, and incident-response evidence before activity is classified as probable UniFi OS compromise.
· NDR / Network Behavioral Analytics detection content should be treated as high-value behavioral coverage for suspicious management-plane access, exploit-attempt scoping, outbound follow-on detection, downstream infrastructure-impact triage, and hunt-to-alert promotion, not direct CVE confirmation or standalone compromise confirmation.
· NDR / Network Behavioral Analytics rules should not generate high-confidence alerting from exposed management interfaces alone, patch state alone, vulnerability scan output alone, isolated denied requests alone, single web errors alone, ordinary update checks alone, or normal administrator access alone.
Rule
Suspicious UniFi OS Management-Plane Access With Exploit-Path Request Behavior
Rule Format
Vendor-neutral NDR behavioral analytics rule template suitable for network-flow telemetry, web telemetry, reverse-proxy telemetry, firewall telemetry, secure access telemetry, load-balancer telemetry, DNS enrichment, source-reputation enrichment, UniFi OS asset inventory, approved-administrator source baselines, management-interface exposure context, and SIEM correlation after UniFi OS asset validation, management-interface validation, request-field validation, source-baseline validation, timing-window tuning, and environment-specific allowlisting.
Detection Purpose
· Detect abnormal access to UniFi OS management interfaces involving authentication-validation paths, traversal-style request behavior, update endpoints, unexpected file-access paths, request-normalization mismatches, or access patterns inconsistent with approved administrative use.
· Identify sources that interact with UniFi OS management interfaces from unfamiliar internet locations, suspicious ASNs, hosting providers, residential proxy ranges, VPN ingress paths, newly observed internal hosts, unmanaged systems, or sources outside approved administration paths.
· Prioritize activity where suspicious source context aligns with exploit-path request behavior rather than treating internet exposure or routine scanning as compromise evidence.
· Support early escalation when abnormal management-plane access is followed by update-endpoint activity, administrator-state changes, configuration changes, outbound communication, or downstream network-control activity.
· Preserve separation between suspicious management-plane access and confirmed compromise by requiring supporting UniFi OS logs, administrator activity, process telemetry, system telemetry, configuration records, or incident-response evidence before classifying activity as probable compromise.
· This rule does not prove successful command execution, sudo-assisted escalation, root compromise, credential theft, administrator-account compromise, downstream infrastructure compromise, or actor attribution without supporting telemetry and investigation evidence.
Detection Logic
· Identify network, web, reverse-proxy, firewall, secure access, or load-balancer events targeting verified UniFi OS management interfaces.
· Prioritize request paths, normalized paths, raw paths, URI categories, or locally classified web events associated with authentication-validation behavior, traversal-style path construction, update-endpoint access, unexpected file-access paths, or request-normalization mismatch indicators.
· Prioritize sources that are unfamiliar, newly observed, internet-facing, hosting-provider-based, residential-proxy-based, VPN-ingress-based, unmanaged, or outside approved administrator source baselines.
· Increase confidence when repeated request attempts, path variations, encoded path elements, unusual request ordering, abnormal response-code patterns, or unusual response-size patterns occur within a locally defined investigation window.
· Increase confidence when abnormal management-plane access is followed by update-endpoint activity, administrator-session anomalies, API token activity, device-adoption activity, backup export activity, configuration changes, outbound communication, or downstream management activity.
· Increase confidence when the source later accesses additional management interfaces, network devices, VPN systems, firewall systems, identity infrastructure, backup systems, monitoring systems, or high-value internal systems.
· Reduce severity when request activity aligns with approved administrator access, vulnerability scanning, exposure assessment, monitoring, vendor support, penetration testing, security testing, incident response, or documented maintenance.
· Do not classify exposed UniFi OS management interfaces, patch state, scanner output, isolated denied requests, ordinary login failures, single web errors, or normal update checks as exploitation evidence by themselves.
· Do not treat network-visible exploit-path behavior as proof of command execution or root compromise without supporting system, endpoint, administrator, configuration, or incident-response evidence.
Required Telemetry
· Network-flow telemetry.
· Web telemetry where available.
· Reverse-proxy telemetry where available.
· Firewall telemetry.
· Secure access telemetry where available.
· Load-balancer telemetry where available.
· DNS telemetry where available.
· Source IP.
· Destination IP.
· Destination host.
· Destination interface.
· Destination port.
· Protocol.
· Application or service classification.
· Request path where available.
· Normalized request path where available.
· Raw request path where available.
· HTTP method where available.
· Response status where available.
· Response size where available.
· User agent where available.
· Session identifier where available.
· Request timestamp.
· Connection count.
· Connection frequency.
· Byte volume.
· Directionality.
· UniFi OS asset inventory.
· UniFi OS management-interface inventory.
· Approved administrator source inventory.
· VPN address pool inventory.
· Management network inventory.
· Jump-host inventory.
· Privileged access workstation inventory.
· Source-reputation enrichment.
· ASN enrichment.
· Geolocation enrichment.
· Newly observed source context.
· Change-management records.
· Approved vulnerability scanning records.
· Approved security testing records.
· Approved incident-response records.
Engineering Implementation Instructions
· Build UniFi OS asset groups covering UniFi OS Server deployments, consoles, cloud gateways, dream machines, cloud keys, gateways, recorders, storage appliances, controller hosts, exposed management interfaces, and management-plane IP addresses.
· Build management-interface groups covering externally exposed UniFi OS interfaces, internal administration interfaces, reverse-proxy destinations, secure access paths, VPN-accessible management paths, and controller administration paths.
· Build approved administrator source groups covering known administrator IPs, VPN ranges, jump hosts, privileged access workstations, management networks, monitoring systems, vendor-support paths, vulnerability management systems, security-testing systems, and incident-response systems.
· Build suspicious source groups covering unfamiliar internet sources, hosting providers, residential proxy ranges, unusual geographies, suspicious ASNs, newly observed internal hosts, unmanaged systems, non-administrative networks, and sources outside the approved administration baseline.
· Build exploit-path request groups for authentication-validation paths, traversal-style path construction, encoded path elements, unexpected file-access paths, update-endpoint access, request-normalization mismatch indicators, and locally observed UniFi OS management-plane anomalies.
· Build response-anomaly groups for repeated denied requests, redirect anomalies, HTTP 5xx patterns, unusual response sizes, abnormal status-code sequences, and request bursts near exploit-path activity.
· Build follow-on groups for update-endpoint activity, administrator-session anomalies, API token activity, administrator-account changes, backup export activity, device-adoption activity, configuration changes, outbound communication, and downstream management activity.
· Validate whether NDR, firewall, reverse-proxy, secure access, load-balancer, DNS, UniFi OS, change-management, and SIEM telemetry can reliably join on source IP, destination host, destination interface, request path, timestamp, session context, administrator context, asset role, and management-interface exposure path.
· Use short correlation windows for abnormal management-plane access, path variation, response anomalies, and update-endpoint activity.
· Use moderate correlation windows for administrator-state changes, configuration changes, outbound communication, device-adoption activity, backup export activity, or downstream management activity.
· Use longer correlation windows only when repeated source behavior, incident-response evidence, administrator evidence, configuration evidence, or downstream impact evidence supports delayed linkage.
· Add severity weighting for exploit-path request behavior, source novelty, hosting-provider source, residential-proxy source, suspicious ASN, unusual geography, VPN ingress source, repeated path variation, update-endpoint activity, administrator-state change, configuration change, and outbound follow-on behavior.
· Treat exploit-path request behavior as a confidence amplifier, not standalone proof of successful command execution, sudo activity, root compromise, or credential theft.
· Use approved administrator records, update records, vulnerability scanning records, security-testing records, vendor-support records, incident-response records, and change-management records as triage evidence.
· Validate all environment variables, asset groups, management-interface groups, approved source groups, suspicious source groups, request-path groups, response-anomaly groups, timing windows, enrichment fields, exception logic, parser behavior, join logic, and local schema mappings before production deployment.
· Do not enable alert mode until field availability, request-field quality, management-interface inventory, source baseline quality, false-positive rate, query performance, SOC triage workflow, enrichment availability, exception handling, and incident-response evidence requirements are validated.
DRI Assessment
DRI
8.5 / 10
· The rule is behaviorally anchored to abnormal UniFi OS management-plane access, exploit-path request behavior, source-path deviation, and follow-on control-plane activity rather than static CVE identifiers, proof-of-concept names, scanner labels, fixed user agents, IP addresses, hashes, or known infrastructure.
· The rule remains useful if an adversary changes tooling, source infrastructure, request pacing, user agent, path encoding, request ordering, or post-access timing.
· The score is supported by the durability of management-plane source deviation, authentication-validation anomalies, traversal-style request behavior, update-endpoint interaction, response anomalies, and downstream correlation.
· The score is constrained by incomplete request visibility, missing raw paths, limited reverse-proxy logging, weak source baselines, broad administrator access paths, and high internet scanning volume against exposed management interfaces.
· The rule is durable as an early exploit-path detector but should not be treated as standalone proof of command execution, root compromise, or actor attribution.
TCR Assessment
Operational TCR
7.5 / 10
Full-Telemetry TCR
8.5 / 10
· Operational confidence depends on reliable management-interface inventory, request-path visibility, reverse-proxy or firewall logging, source-reputation enrichment, administrator source baselines, and SIEM correlation quality.
· Operational confidence is reduced where exposed management interfaces receive heavy scanning, request paths are not logged, source baselines are weak, or approved administration paths are broad.
· Operational confidence is reduced where vulnerability scanning, exposure assessment, security testing, vendor support, or incident-response workflows generate similar request patterns.
· Full-telemetry confidence improves when abnormal access is enriched with UniFi OS logs, administrator audit logs, update-service logs, system logs, configuration-change records, endpoint telemetry where available, change-management records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support early escalation and scoping rather than standalone confirmation of exploit success or root compromise.
Limitations
· This rule detects suspicious UniFi OS management-plane access and exploit-path request behavior, not confirmed exploitation by itself.
· NDR may not observe process execution, sudo activity, root-context behavior, local file activity, package-script execution, administrator intent, or internal UniFi OS service behavior without enrichment.
· Internet scanning, vulnerability assessment, penetration testing, monitoring, vendor support, administrator troubleshooting, and incident-response activity may produce similar management-plane request patterns.
· Missing request paths, missing normalized paths, missing raw paths, weak source baselines, incomplete asset inventory, or limited reverse-proxy logging can reduce confidence.
· The rule may miss exploitation that originates from an approved administrator source, uses expected management paths, blends into normal access patterns, or occurs outside configured timing windows.
· The rule should not be used for actor attribution without incident-specific intelligence, validated behavioral correlation, or confirmed victim-environment evidence.
Detection Query Pattern
Vendor-neutral NDR query pattern for UniFi OS management-plane exploit-path access. This pattern requires target-platform syntax conversion, UniFi OS asset validation, management-interface validation, request-field validation, source-baseline validation, timing-window tuning, and environment-specific allowlisting before production deployment.
NetworkEvent AS UniFiManagementAccess
WHERE UniFiManagementAccess.DestinationAsset IN ASSET_GROUP (
"UniFi OS Servers",
"UniFi OS Consoles",
"UniFi Cloud Gateways",
"UniFi Dream Machines",
"UniFi Cloud Keys",
"UniFi Gateways",
"UniFi Recorders",
"UniFi Storage Appliances",
"UniFi Controller Hosts",
"UniFi Management Interfaces"
)
AND UniFiManagementAccess.DestinationService IN ANY (
"UNIFI_OS_MANAGEMENT",
"UNIFI_NETWORK_APPLICATION",
"UNIFI_CONSOLE_MANAGEMENT",
"UNIFI_GATEWAY_MANAGEMENT",
"UNIFI_CONTROLLER_MANAGEMENT",
"UNIFI_REVERSE_PROXY_MANAGEMENT"
)
AND (
UniFiManagementAccess.RequestPathCategory IN ANY (
"authentication_validation_path",
"traversal_style_path",
"encoded_path_variation",
"unexpected_file_access_path",
"update_endpoint_access",
"package_management_endpoint",
"request_normalization_mismatch"
)
OR UniFiManagementAccess.RequestPattern IN ANY (
"repeated_path_variation",
"abnormal_request_ordering",
"request_burst_to_management_interface",
"rare_management_path_access",
"path_not_in_administration_baseline"
)
OR UniFiManagementAccess.ResponsePattern IN ANY (
"repeated_denied_requests",
"redirect_anomaly",
"http_5xx_near_management_path_activity",
"unusual_response_size",
"abnormal_status_code_sequence"
)
)
AND UniFiManagementAccess.SourceAsset NOT IN ASSET_GROUP (
"Approved UniFi Administrators",
"Approved Administrative Jump Hosts",
"Approved Privileged Access Workstations",
"Approved Management Networks",
"Approved VPN Administration Ranges",
"Approved Monitoring Systems",
"Approved Vulnerability Management Systems",
"Approved Vendor Support Paths",
"Approved Security Testing Systems",
"Approved Incident Response Systems"
)
AND (
UniFiManagementAccess.SourceContext IN ANY (
"unfamiliar_internet_source",
"newly_observed_source",
"hosting_provider_source",
"residential_proxy_source",
"suspicious_asn",
"unusual_geography",
"vpn_ingress_source",
"unmanaged_internal_host",
"source_not_in_unifi_admin_baseline"
)
OR UniFiManagementAccess.ConnectionPattern IN ANY (
"repeated_management_interface_access",
"new_source_to_unifi_management_path",
"high_frequency_management_requests",
"multiple_unifi_assets_targeted",
"outside_normal_administration_window"
)
)
AND OPTIONAL_CONFIDENCE_INCREASE WITHIN ENV_UNIFI_FOLLOWON_WINDOW (
ManagementOrSecurityEvent AS UniFiFollowOn
WHERE UniFiFollowOn.Asset IN SAME_DESTINATION (
UniFiManagementAccess.DestinationAsset
)
AND UniFiFollowOn.EventPattern IN ANY (
"update_endpoint_activity",
"package_management_activity",
"administrator_session_anomaly",
"api_token_activity",
"administrator_account_change",
"device_adoption_activity",
"backup_export_activity",
"configuration_change",
"service_instability",
"system_fault"
)
)
AND OPTIONAL_CONFIDENCE_INCREASE WITHIN ENV_UNIFI_NETWORK_FOLLOWON_WINDOW (
NetworkEvent AS UniFiNetworkFollowOn
WHERE (
UniFiNetworkFollowOn.SourceAsset IN SAME_DESTINATION (
UniFiManagementAccess.DestinationAsset
)
OR UniFiNetworkFollowOn.SourceAsset IN SAME_SOURCE (
UniFiManagementAccess.SourceAsset
)
)
AND UniFiNetworkFollowOn.EventPattern IN ANY (
"rare_outbound_destination",
"new_external_destination",
"low_reputation_destination",
"unusual_asn_destination",
"tunnel_like_traffic",
"internal_scanning",
"device_enumeration",
"additional_management_interface_access",
"downstream_network_control_activity"
)
)
AND NOT ChangeContext IN ANY (
"approved_firmware_update",
"approved_package_operation",
"approved_controller_upgrade",
"approved_device_adoption",
"approved_backup_activity",
"approved_gateway_change",
"approved_wireless_change",
"approved_vpn_change",
"approved_dns_change",
"approved_vendor_support",
"approved_vulnerability_scan",
"approved_security_testing",
"approved_incident_response"
)
Rule
UniFi OS Update or Package Activity Followed by Suspicious Outbound or Downstream Management Behavior
Rule Format
Vendor-neutral NDR behavioral analytics rule template suitable for network-flow telemetry, DNS telemetry, firewall telemetry, proxy telemetry, web telemetry, reverse-proxy telemetry, package-update metadata where available, UniFi OS asset inventory, outbound baseline enrichment, downstream management-interface inventory, administrator source baselines, configuration-change enrichment, and SIEM correlation after update-path validation, outbound-destination validation, downstream management-path validation, timing-window tuning, and environment-specific allowlisting.
Detection Purpose
· Detect UniFi OS update-endpoint or package-management activity followed by suspicious outbound communication, internal scanning, device enumeration, additional management-interface access, or downstream network-control behavior.
· Identify cases where update or package activity becomes higher risk because it is followed by behavior consistent with operator staging, external callback, tool retrieval, device discovery, configuration manipulation, or movement toward adjacent management infrastructure.
· Prioritize outbound communication to newly observed, rare, low-reputation, geographically unusual, role-inconsistent, or unexpected destinations after update-endpoint or package-management activity.
· Prioritize downstream access to network devices, gateways, switches, access points, firewalls, VPN systems, identity infrastructure, backup systems, monitoring systems, or other management platforms after suspected UniFi OS exploit-path activity.
· Preserve separation between suspicious follow-on behavior and confirmed compromise by requiring supporting UniFi OS logs, administrator activity, process telemetry where available, configuration records, change-management records, or incident-response evidence.
· This rule does not prove successful command injection, root compromise, credential theft, data exfiltration, downstream infrastructure compromise, or actor attribution without supporting evidence.
Detection Logic
· Identify UniFi OS management-plane access involving update endpoints, package-management paths, update-service behavior, or locally classified update-related management events.
· Correlate update or package activity with outbound communication from the UniFi OS asset to newly observed, rare, low-reputation, unusual, role-inconsistent, or unexpected external destinations.
· Correlate update or package activity with internal scanning, device enumeration, management-plane discovery, SNMP activity, SSH access, web-admin access, API probing, or access to adjacent management platforms.
· Increase confidence when follow-on behavior occurs after abnormal source access, traversal-style request behavior, authentication-validation anomalies, response anomalies, or management-interface access from a non-standard source.
· Increase confidence when outbound or downstream behavior is accompanied by administrator-state changes, backup export activity, device-adoption changes, gateway policy changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, or managed-device configuration changes.
· Increase confidence when the same source that accessed UniFi OS abnormally later interacts with additional internal management interfaces or high-value systems.
· Reduce severity when outbound communication aligns with approved vendor update services, monitoring tools, backup destinations, remote-management services, vulnerability management, security testing, incident response, or documented maintenance.
· Do not classify outbound communication or downstream access as UniFi OS compromise without upstream UniFi OS exploit-path context or supporting administrator, configuration, host, or incident-response evidence.
· Do not treat update checks, package repository access, ordinary outbound communication, or normal network-device management as malicious by themselves.
Required Telemetry
· Network-flow telemetry.
· DNS telemetry.
· Firewall telemetry.
· Proxy telemetry where available.
· Web telemetry where available.
· Reverse-proxy telemetry where available.
· Secure access telemetry where available.
· UniFi OS update or package activity metadata where available.
· Source host.
· Destination host.
· Source IP.
· Destination IP.
· Destination port.
· Protocol.
· Application or service classification.
· Request path where available.
· Event timestamp.
· Session timing.
· Connection frequency.
· Byte volume.
· Directionality.
· External destination reputation where available.
· External destination first-seen context where available.
· ASN enrichment.
· Geolocation enrichment.
· UniFi OS asset inventory.
· Downstream network-device inventory.
· Management-interface inventory.
· Gateway inventory.
· Firewall inventory.
· VPN system inventory.
· Wireless infrastructure inventory.
· Recorder and storage inventory where applicable.
· Identity infrastructure inventory where available.
· Backup system inventory where available.
· Monitoring system inventory where available.
· Approved update destination records.
· Approved vendor service records.
· Approved backup destination records.
· Approved monitoring destination records.
· Approved administrator source records.
· Change-management records.
· Incident-response records.
Engineering Implementation Instructions
· Build UniFi OS asset groups covering all UniFi OS systems, exposed management interfaces, controller hosts, consoles, gateways, recorders, storage appliances, and management-plane destinations.
· Build update and package activity groups for update endpoints, package-management paths, package repository access, update-service behavior, update-triggered service activity, and locally observed UniFi OS update workflows.
· Build outbound-risk groups for newly observed external destinations, rare domains, rare IPs, low-reputation destinations, unusual ASNs, unexpected geographic destinations, tunnel-like traffic, abnormal byte volume, unusual package-repository access, and destinations inconsistent with the deployed UniFi OS role.
· Build downstream management groups covering gateways, switches, access points, firewalls, VPN systems, network-management platforms, security-management platforms, identity infrastructure, backup systems, monitoring systems, recorder systems, storage systems, and other high-value management interfaces.
· Build internal discovery groups for device enumeration, management-plane discovery, SNMP activity, SSH access, web-admin access, API probing, service discovery, and access to additional management interfaces.
· Build configuration follow-on groups for administrator changes, API token activity, backup exports, device adoption, gateway policy changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, and managed-device configuration changes.
· Validate whether NDR, DNS, firewall, proxy, reverse-proxy, secure access, UniFi OS, configuration, change-management, and SIEM telemetry can reliably join on source host, destination host, source IP, destination IP, timestamp, request path, asset role, administrator context, and change-window context.
· Use short correlation windows for update or package activity followed by immediate outbound communication, internal scanning, or management-interface access.
· Use moderate correlation windows for delayed downstream management activity, configuration changes, backup export activity, or repeated external communication.
· Use longer correlation windows only when repeated source behavior, incident-response evidence, configuration evidence, or administrator evidence supports delayed linkage.
· Add severity weighting for abnormal upstream source access, update-endpoint activity, rare outbound destinations, low-reputation destinations, internal management discovery, additional management-interface access, administrator-state changes, and downstream configuration changes.
· Treat outbound communication and downstream management behavior as confidence amplifiers, not standalone proof of command execution, root compromise, or data exfiltration.
· Use approved update records, vendor service records, backup records, monitoring records, administrator records, vulnerability management records, security-testing records, incident-response records, and change-management records as triage evidence.
· Validate all environment variables, UniFi OS asset groups, update activity groups, outbound-risk groups, downstream management groups, discovery groups, configuration follow-on groups, timing windows, enrichment fields, exception logic, parser behavior, join logic, and local schema mappings before production deployment.
· Do not enable alert mode until update-path validation, outbound baseline quality, downstream management inventory, false-positive rate, query performance, SOC triage workflow, enrichment availability, exception handling, and incident-response evidence requirements are validated.
DRI Assessment
DRI
8.0 / 10
· The rule is behaviorally anchored to UniFi OS update or package activity followed by outbound communication or downstream management behavior rather than static exploit strings, CVE identifiers, proof-of-concept names, file hashes, user agents, or known infrastructure.
· The rule remains useful if an adversary changes source infrastructure, outbound destination, command syntax, tool retrieval method, timing, downstream target order, or post-exploitation sequence.
· The score is supported by the durability of update-path interaction, rare outbound communication, management-plane discovery, downstream management access, and configuration follow-on behavior.
· The score is constrained by legitimate vendor update activity, monitoring traffic, backup traffic, administrator workflows, weak outbound baselines, limited destination reputation enrichment, and incomplete downstream management inventory.
· The rule is durable as a post-interaction scoping detector but should not be treated as standalone proof of command injection, root compromise, exfiltration, or actor attribution.
TCR Assessment
Operational TCR
7.0 / 10
Full-Telemetry TCR
8.5 / 10
· Operational confidence depends on reliable update-path visibility, outbound network telemetry, DNS or proxy coverage, destination reputation enrichment, downstream management inventory, source baselines, and SIEM correlation quality.
· Operational confidence is reduced where UniFi OS update behavior is poorly baselined, approved update destinations are not documented, or monitoring and backup tools commonly generate similar outbound activity.
· Operational confidence is reduced where internal management traffic is broad, management-interface inventories are incomplete, or downstream network-device administration is not well documented.
· Full-telemetry confidence improves when outbound and downstream behavior is enriched with UniFi OS logs, administrator activity logs, configuration-change records, endpoint telemetry where available, system logs, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support escalation and scoping rather than standalone confirmation of exploit success, root compromise, or data exfiltration.
Limitations
· This rule detects suspicious follow-on network behavior after UniFi OS update or package activity, not confirmed exploitation by itself.
· NDR may not observe local command execution, sudo activity, package-script execution, root-context behavior, administrator intent, or internal application state without enrichment.
· Approved vendor updates, monitoring tools, backup workflows, administrator actions, vulnerability management, security testing, incident response, and remote-management activity can produce similar outbound or downstream patterns.
· Missing DNS telemetry, proxy telemetry, destination reputation, downstream inventory, source baselines, or configuration records can reduce confidence.
· The rule may miss activity that uses approved destinations, blends into normal update traffic, avoids visible outbound communication, or remains within expected management paths.
· The rule should not be used for actor attribution without incident-specific intelligence, validated behavioral correlation, or confirmed victim-environment evidence.
Detection Query Pattern
Vendor-neutral NDR query pattern for UniFi OS update and downstream follow-on behavior. This pattern requires target-platform syntax conversion, update-path validation, outbound baseline validation, downstream management inventory validation, timing-window tuning, and environment-specific allowlisting before production deployment.
NetworkEvent AS UniFiUpdateOrPackageActivity
WHERE UniFiUpdateOrPackageActivity.DestinationAsset IN ASSET_GROUP (
"UniFi OS Servers",
"UniFi OS Consoles",
"UniFi Cloud Gateways",
"UniFi Dream Machines",
"UniFi Cloud Keys",
"UniFi Gateways",
"UniFi Recorders",
"UniFi Storage Appliances",
"UniFi Controller Hosts",
"UniFi Management Interfaces"
)
AND (
UniFiUpdateOrPackageActivity.RequestPathCategory IN ANY (
"update_endpoint_access",
"package_management_endpoint",
"package_repository_access",
"application_update_path",
"update_service_path"
)
OR UniFiUpdateOrPackageActivity.EventPattern IN ANY (
"update_service_activity",
"package_management_activity",
"update_triggered_service_activity",
"package_operation_near_management_request",
"update_activity_outside_maintenance_window"
)
)
AND EVENT_NEAR WITHIN ENV_UNIFI_OUTBOUND_FOLLOWON_WINDOW (
NetworkEvent AS UniFiOutboundFollowOn
WHERE UniFiOutboundFollowOn.SourceAsset IN SAME_DESTINATION (
UniFiUpdateOrPackageActivity.DestinationAsset
)
AND (
UniFiOutboundFollowOn.ExternalDestinationContext IN ANY (
"newly_observed_external_destination",
"rare_external_destination",
"low_reputation_destination",
"unusual_asn",
"unexpected_geography",
"destination_not_in_unifi_role_baseline",
"unexpected_package_repository",
"tunnel_like_protocol",
"abnormal_byte_volume"
)
OR UniFiOutboundFollowOn.ProtocolOrService IN ANY (
"HTTP",
"HTTPS",
"DNS",
"SSH",
"SMB_EGRESS",
"TUNNEL_LIKE_TRAFFIC",
"FILE_RETRIEVAL"
)
)
)
AND OPTIONAL_CONFIDENCE_INCREASE WITHIN ENV_UNIFI_DOWNSTREAM_WINDOW (
NetworkEvent AS DownstreamManagementActivity
WHERE (
DownstreamManagementActivity.SourceAsset IN SAME_DESTINATION (
UniFiUpdateOrPackageActivity.DestinationAsset
)
OR DownstreamManagementActivity.SourceAsset IN SAME_SOURCE (
UniFiUpdateOrPackageActivity.SourceAsset
)
)
AND (
DownstreamManagementActivity.DestinationAsset IN ASSET_GROUP (
"Gateways",
"Switches",
"Access Points",
"Firewalls",
"VPN Systems",
"Network Management Platforms",
"Security Management Platforms",
"Identity Infrastructure",
"Backup Systems",
"Monitoring Systems",
"Recorder Systems",
"Storage Systems",
"High Value Management Interfaces"
)
OR DownstreamManagementActivity.EventPattern IN ANY (
"device_enumeration",
"management_plane_discovery",
"snmp_activity",
"ssh_access",
"web_admin_access",
"api_probing",
"additional_management_interface_access",
"downstream_network_control_activity"
)
)
)
AND OPTIONAL_CONFIDENCE_INCREASE WITHIN ENV_UNIFI_CONFIGURATION_WINDOW (
ManagementOrConfigurationEvent AS UniFiConfigurationFollowOn
WHERE UniFiConfigurationFollowOn.Asset IN SAME_DESTINATION (
UniFiUpdateOrPackageActivity.DestinationAsset
)
AND UniFiConfigurationFollowOn.EventPattern IN ANY (
"administrator_account_change",
"api_token_activity",
"backup_export_activity",
"device_adoption_activity",
"gateway_policy_change",
"firewall_rule_change",
"routing_change",
"vpn_change",
"dns_change",
"wireless_change",
"recorder_change",
"storage_change",
"managed_device_configuration_change"
)
)
AND NOT ChangeContext IN ANY (
"approved_firmware_update",
"approved_package_operation",
"approved_controller_upgrade",
"approved_device_adoption",
"approved_backup_activity",
"approved_gateway_change",
"approved_firewall_change",
"approved_routing_change",
"approved_vpn_change",
"approved_dns_change",
"approved_wireless_change",
"approved_vendor_support",
"approved_monitoring_activity",
"approved_security_testing",
"approved_incident_response"
)
Rule
UniFi OS Exploit-Path Activity Followed by Downstream Network-Control Change
Rule Format
Vendor-neutral NDR behavioral analytics rule template suitable for network-flow telemetry, management-interface telemetry, firewall telemetry, DNS telemetry, reverse-proxy telemetry, UniFi OS asset inventory, downstream network-device inventory, configuration-change enrichment, administrator baseline enrichment, change-management records, and SIEM correlation after downstream asset validation, configuration-change validation, source-path validation, timing-window tuning, and environment-specific allowlisting.
Detection Purpose
· Detect suspected UniFi OS exploit-path activity followed by downstream network-control changes affecting gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless configuration, device adoption, recorder behavior, storage access, or managed-device trust where those roles are deployed.
· Identify cases where UniFi OS management-plane compromise may create operational risk through changes to network infrastructure, segmentation, access paths, remote access, traffic handling, or device trust.
· Prioritize downstream changes that occur near abnormal UniFi OS management-plane access, administrator-state anomalies, update-endpoint activity, outbound communication, or command-execution evidence from other telemetry sources.
· Support escalation when downstream changes are not explained by approved change records, known administrators, expected maintenance windows, device onboarding, incident response, or vendor support.
· Preserve separation between suspicious downstream changes and confirmed compromise by requiring linkage to UniFi OS exploit-path activity, administrator anomalies, configuration records, or incident-response evidence.
· This rule does not prove command execution, root compromise, credential theft, or actor attribution without supporting host, system, administrator, configuration, or incident-response evidence.
Detection Logic
· Identify abnormal UniFi OS management-plane access, exploit-path request behavior, update-endpoint activity, suspicious source access, or outbound follow-on behavior involving verified UniFi OS assets.
· Correlate suspected UniFi OS activity with downstream configuration changes affecting gateway policy, firewall rules, routing, VPN access, DNS settings, wireless settings, device adoption, recorder behavior, storage access, or managed-device trust.
· Prioritize changes involving remote access expansion, firewall weakening, new port exposure, VPN policy changes, route changes, DNS forwarding changes, wireless SSID or security changes, device adoption anomalies, backup export behavior, or configuration changes outside approved windows.
· Increase confidence when the downstream change is performed by a newly created administrator, rarely used administrator, unfamiliar source, unusual geography, suspicious ASN, API token, or administrative session created near suspected exploit-path activity.
· Increase confidence when downstream changes are followed by unusual outbound communication, internal scanning, additional management-interface access, access to high-value systems, or visibility reduction.
· Reduce severity when downstream changes align with approved network maintenance, device replacement, site onboarding, firmware updates, firewall policy changes, VPN changes, wireless changes, vendor support, security testing, incident response, or documented change-control activity.
· Do not classify downstream network-control changes as UniFi OS compromise without upstream UniFi OS exploit-path activity, administrator-state anomaly, suspicious source context, or incident-response validation.
· Do not treat legitimate network maintenance or expected device-adoption workflows as compromise indicators solely because UniFi OS is vulnerable or exposed.
Required Telemetry
· Network-flow telemetry.
· Firewall telemetry.
· DNS telemetry.
· Reverse-proxy telemetry where available.
· Web telemetry where available.
· Secure access telemetry where available.
· UniFi OS management-plane telemetry where available.
· Configuration-change telemetry where available.
· Administrator activity telemetry where available.
· Source host.
· Destination host.
· Source IP.
· Destination IP.
· Destination port.
· Protocol.
· Application or service classification.
· Request path where available.
· Event timestamp.
· Administrator identity where available.
· Session context where available.
· API token context where available.
· Configuration object.
· Configuration action.
· Change type.
· Device identifier.
· Device role.
· Network segment.
· UniFi OS asset inventory.
· Gateway inventory.
· Firewall inventory.
· Routing configuration inventory.
· VPN system inventory.
· DNS configuration inventory.
· Wireless infrastructure inventory.
· Recorder and storage inventory where applicable.
· Managed-device inventory.
· Approved administrator source inventory.
· Change-management records.
· Network maintenance records.
· Device onboarding records.
· Vendor-support records.
· Incident-response records.
Engineering Implementation Instructions
· Build UniFi OS upstream activity groups for abnormal management-plane request behavior, exploit-path request categories, update-endpoint activity, suspicious source access, response anomalies, outbound follow-on behavior, and administrator-state anomalies.
· Build downstream configuration groups for gateway policy changes, firewall rule changes, route changes, VPN changes, DNS changes, wireless changes, device-adoption changes, recorder changes, storage changes, and managed-device configuration changes.
· Build high-risk change groups for remote-access expansion, firewall weakening, new inbound exposure, segmentation changes, default route changes, DNS forwarding changes, VPN access changes, wireless security weakening, unexpected device adoption, backup export, and management-access expansion.
· Build administrator-risk groups for newly created administrators, rarely used administrators, unusual source geographies, suspicious ASNs, unfamiliar devices, API token use, session anomalies, and administrator activity outside approved windows.
· Build follow-on impact groups for unusual outbound communication, internal scanning, additional management-interface access, high-value system access, monitoring disruption, logging gaps, defensive visibility reduction, and downstream management activity.
· Validate whether NDR, firewall, DNS, reverse-proxy, secure access, UniFi OS, configuration, administrator audit, change-management, and SIEM telemetry can reliably join on UniFi OS asset, administrator identity, source IP, destination host, device identifier, configuration object, timestamp, and change-window context.
· Use short correlation windows for downstream changes occurring immediately after suspected UniFi OS exploit-path activity or administrator-state anomalies.
· Use moderate correlation windows for delayed configuration changes, device adoption, VPN changes, DNS changes, wireless changes, gateway policy changes, or managed-device changes.
· Use longer correlation windows only when repeated source behavior, administrator evidence, configuration evidence, or incident-response evidence supports delayed linkage.
· Add severity weighting for high-risk downstream change type, suspicious administrator context, abnormal source context, update-endpoint activity, outbound follow-on behavior, lack of change record, and impact on remote access, segmentation, firewall policy, VPN access, or managed-device trust.
· Treat downstream configuration changes as impact signals only when linked to UniFi OS exploit-path activity, administrator anomalies, suspicious source context, or incident-response evidence.
· Use approved change records, network maintenance records, device onboarding records, firewall policy records, VPN change records, wireless change records, vendor-support records, security-testing records, and incident-response records as triage evidence.
· Validate all environment variables, upstream activity groups, downstream configuration groups, high-risk change groups, administrator-risk groups, follow-on impact groups, timing windows, enrichment fields, exception logic, parser behavior, join logic, and local schema mappings before production deployment.
· Do not enable alert mode until downstream inventory, configuration telemetry, administrator context, change-record quality, false-positive rate, query performance, SOC triage workflow, enrichment availability, exception handling, and incident-response evidence requirements are validated.
DRI Assessment
DRI
8.0 / 10
· The rule is behaviorally anchored to UniFi OS exploit-path activity followed by downstream network-control change rather than static CVE identifiers, exploit strings, proof-of-concept names, scanner labels, file artifacts, or known infrastructure.
· The rule remains useful if an adversary changes tooling, source infrastructure, timing, administrator account, command syntax, outbound destination, or downstream target order.
· The score is supported by the durability of management-plane compromise followed by gateway, firewall, routing, VPN, DNS, wireless, device-adoption, recorder, storage, or managed-device configuration changes.
· The score is constrained by legitimate network maintenance, broad administrator workflows, incomplete configuration telemetry, weak change records, appliance-only visibility, and incomplete downstream inventory.
· The rule is durable as a downstream impact detector but should not be treated as standalone proof of command execution, root compromise, credential theft, or actor attribution.
TCR Assessment
Operational TCR
7.0 / 10
Full-Telemetry TCR
8.5 / 10
· Operational confidence depends on reliable UniFi OS upstream activity detection, downstream configuration telemetry, administrator context, change-management records, asset inventory, and SIEM correlation quality.
· Operational confidence is reduced where network teams perform frequent configuration changes, device onboarding is common, administrator sources are broad, or configuration-change records are incomplete.
· Operational confidence is reduced where downstream device inventories, gateway roles, firewall policy ownership, VPN workflows, DNS change records, wireless change records, recorder records, or storage records are poorly documented.
· Full-telemetry confidence improves when downstream changes are enriched with UniFi OS logs, administrator activity logs, endpoint telemetry where available, system logs, firewall logs, DNS logs, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support downstream impact triage and escalation rather than standalone confirmation of root compromise or actor attribution.
Limitations
· This rule detects suspicious downstream network-control changes after suspected UniFi OS exploit-path activity, not confirmed exploitation by itself.
· NDR may not observe administrator intent, local process execution, sudo activity, root-context behavior, package-script execution, or credential access without enrichment.
· Legitimate network maintenance, device onboarding, firewall policy updates, VPN changes, DNS changes, wireless changes, storage changes, vendor support, security testing, and incident response can produce similar downstream signals.
· Missing downstream configuration telemetry, incomplete administrator context, weak change records, broad administrator source paths, or incomplete asset inventory can reduce confidence.
· The rule may miss activity that does not produce observable downstream changes, uses approved administrators, aligns with normal maintenance windows, or occurs outside configured correlation windows.
· The rule should not be used for actor attribution without incident-specific intelligence, validated behavioral correlation, or confirmed victim-environment evidence.
Detection Query Pattern
Vendor-neutral NDR query pattern for UniFi OS downstream network-control change. This pattern requires target-platform syntax conversion, upstream UniFi OS activity validation, downstream configuration telemetry validation, administrator-context validation, timing-window tuning, and environment-specific allowlisting before production deployment.
NetworkEvent AS UniFiUpstreamExploitPathActivity
WHERE UniFiUpstreamExploitPathActivity.DestinationAsset IN ASSET_GROUP (
"UniFi OS Servers",
"UniFi OS Consoles",
"UniFi Cloud Gateways",
"UniFi Dream Machines",
"UniFi Cloud Keys",
"UniFi Gateways",
"UniFi Recorders",
"UniFi Storage Appliances",
"UniFi Controller Hosts",
"UniFi Management Interfaces"
)
AND (
UniFiUpstreamExploitPathActivity.RequestPathCategory IN ANY (
"authentication_validation_path",
"traversal_style_path",
"encoded_path_variation",
"unexpected_file_access_path",
"update_endpoint_access",
"package_management_endpoint",
"request_normalization_mismatch"
)
OR UniFiUpstreamExploitPathActivity.EventPattern IN ANY (
"abnormal_management_plane_access",
"exploit_path_request_behavior",
"update_endpoint_activity",
"response_anomaly_near_management_access",
"suspicious_source_to_unifi_management"
)
OR UniFiUpstreamExploitPathActivity.SourceContext IN ANY (
"unfamiliar_internet_source",
"hosting_provider_source",
"residential_proxy_source",
"suspicious_asn",
"unusual_geography",
"vpn_ingress_source",
"source_not_in_unifi_admin_baseline"
)
)
AND EVENT_NEAR WITHIN ENV_UNIFI_DOWNSTREAM_CHANGE_WINDOW (
ManagementOrConfigurationEvent AS DownstreamControlChange
WHERE DownstreamControlChange.RelatedUniFiAsset IN SAME_DESTINATION (
UniFiUpstreamExploitPathActivity.DestinationAsset
)
AND DownstreamControlChange.EventPattern IN ANY (
"gateway_policy_change",
"firewall_rule_change",
"routing_change",
"vpn_change",
"dns_change",
"wireless_change",
"device_adoption_activity",
"recorder_change",
"storage_change",
"managed_device_configuration_change",
"management_access_expansion",
"backup_export_activity"
)
AND DownstreamControlChange.ChangeRisk IN ANY (
"remote_access_expansion",
"firewall_policy_weakening",
"new_inbound_exposure",
"segmentation_change",
"default_route_change",
"dns_forwarding_change",
"vpn_access_change",
"wireless_security_change",
"unexpected_device_adoption",
"management_trust_change"
)
)
AND OPTIONAL_CONFIDENCE_INCREASE WITHIN ENV_UNIFI_ADMIN_CONTEXT_WINDOW (
ManagementOrSecurityEvent AS AdministratorRiskContext
WHERE AdministratorRiskContext.RelatedUniFiAsset IN SAME_DESTINATION (
UniFiUpstreamExploitPathActivity.DestinationAsset
)
AND AdministratorRiskContext.EventPattern IN ANY (
"new_administrator_created",
"rare_administrator_used",
"administrator_from_unusual_source",
"api_token_activity",
"session_anomaly",
"administrator_activity_outside_change_window",
"administrator_not_in_baseline"
)
)
AND OPTIONAL_CONFIDENCE_INCREASE WITHIN ENV_UNIFI_IMPACT_FOLLOWON_WINDOW (
NetworkOrSecurityEvent AS DownstreamImpactContext
WHERE DownstreamImpactContext.RelatedAsset IN SAME_DESTINATION (
DownstreamControlChange.TargetAsset
)
AND DownstreamImpactContext.EventPattern IN ANY (
"unusual_outbound_communication",
"internal_scanning",
"additional_management_interface_access",
"high_value_system_access",
"monitoring_disruption",
"logging_gap",
"defensive_visibility_reduction",
"downstream_management_activity"
)
)
AND NOT ChangeContext IN ANY (
"approved_network_maintenance",
"approved_device_onboarding",
"approved_firewall_policy_update",
"approved_routing_change",
"approved_vpn_change",
"approved_dns_change",
"approved_wireless_change",
"approved_recorder_change",
"approved_storage_change",
"approved_vendor_support",
"approved_security_testing",
"approved_incident_response"
)
SentinelOne
Detection Viability Assessment
SentinelOne has two rules for this EXP report.
· SentinelOne is viable for detecting UniFi OS control-plane compromise behavior only where UniFi OS runs on a self-hosted server, controller host, supporting Linux host, or appliance environment that exposes endpoint telemetry to SentinelOne.
· SentinelOne is strongest for detecting suspicious child-process execution, shell execution, interpreter execution, file retrieval, archive extraction, package-manager activity, sudo usage, root-context process behavior, service modification, persistence changes, and outbound process-network activity from UniFi OS service contexts.
· SentinelOne is not universal coverage for all UniFi OS appliances because many cloud gateways, consoles, recorders, storage appliances, and embedded UniFi OS environments may not support customer-managed endpoint-agent visibility.
· SentinelOne should be treated as direct host-behavior coverage for endpoint-visible UniFi OS deployments and as non-coverage for UniFi OS appliance deployments that do not expose process, command-line, file, sudo, or service telemetry.
· SentinelOne detections should be correlated with UniFi OS logs, web logs, reverse-proxy logs, firewall logs, NDR telemetry, DNS telemetry, administrator activity logs, configuration-change records, change-management records, and incident-response evidence.
· SentinelOne should not be used to infer UniFi OS compromise from unrelated Linux process anomalies unless the process lineage, asset role, service context, timing, and management-plane evidence support the UniFi OS exploit path.
· SentinelOne rules should not generate high-confidence alerting from ordinary package operations, approved updates, backup jobs, service restarts, administrator maintenance, vulnerability scanning, security testing, vendor support, or incident-response activity without suspicious service lineage, management-plane context, or maintenance mismatch.
Rule
UniFi OS Service Context Child Process and Privileged Execution Behavior
Rule Format
SentinelOne Deep Visibility hunting logic and STAR custom detection template for endpoint-visible UniFi OS Server, controller-host, or supporting Linux-host deployments after UniFi OS process-baseline validation, endpoint-agent validation, event-type validation, command-line field validation, parent-child process validation, sudo telemetry validation, timing-window tuning, and environment-specific allowlisting.
Detection Purpose
· Detect unexpected shell execution, interpreter execution, command chaining, file retrieval, archive extraction, package-manager execution, sudo usage, privileged command execution, or root-context process activity from UniFi OS web, application, controller, update, or package-management service contexts.
· Identify endpoint-visible behavior consistent with command execution following UniFi OS management-plane exploit-path activity.
· Prioritize cases where suspicious child-process activity occurs near abnormal management-plane access, traversal-style request behavior, authentication-validation anomalies, update-endpoint access, or suspicious source access.
· Support escalation when UniFi OS service-context execution is followed by file staging, outbound communication, service modification, local user change, SSH configuration change, scheduled job creation, or administrator-state anomalies.
· Preserve separation between suspicious process behavior and confirmed compromise by requiring process lineage, asset role, command-line context, source telemetry, change records, and incident-response validation.
· This rule does not apply to UniFi OS appliance deployments that do not expose endpoint process telemetry to SentinelOne or equivalent EDR tooling.
Detection Logic
· Identify endpoint events from verified UniFi OS Server, controller-host, or supporting Linux-host assets.
· Identify process creation where the parent process is a UniFi OS web, application, controller, update, package-management, Java, Node.js, Nginx, service-wrapper, or locally mapped UniFi OS service process.
· Prioritize child processes involving shells, interpreters, package managers, file-retrieval utilities, archive utilities, network utilities, scripting engines, service-management tools, user-management commands, SSH configuration commands, permission-changing commands, or sudo execution.
· Increase confidence when child-process execution occurs near abnormal UniFi OS management-plane access, update-endpoint activity, request-path anomalies, suspicious source access, or reverse-proxy management events.
· Increase confidence when process behavior includes command chaining, encoded command content, execution from temporary paths, execution from application-writable paths, unexpected package scripts, service modification, local user changes, SSH key changes, scheduled job creation, or outbound process-network activity.
· Increase confidence when the process runs as root, escalates through sudo, modifies services, changes permissions, writes executable files, or accesses sensitive UniFi OS configuration or backup material.
· Reduce severity when activity aligns with approved UniFi OS updates, package operations, controller upgrades, backup jobs, service restarts, vulnerability management, security testing, vendor support, incident response, or documented maintenance windows.
· Do not classify ordinary Linux administration or expected UniFi maintenance as exploitation without suspicious UniFi OS service lineage or management-plane correlation.
· Do not apply this rule to UniFi OS appliance deployments where endpoint telemetry is absent or unavailable to SentinelOne.
Required Telemetry
· SentinelOne endpoint telemetry.
· Deep Visibility process telemetry.
· Process creation events.
· Parent process name.
· Parent process path.
· Parent process command line.
· Child process name.
· Child process path.
· Child process command line.
· Process user.
· Effective user where available.
· Root-context execution indicator where available.
· Sudo execution events where available.
· Process hash where available.
· Working directory.
· File creation events.
· File modification events.
· Script creation events.
· Archive extraction events.
· Service modification events.
· Scheduled job events.
· Local user modification events.
· SSH configuration events where available.
· Process network connection events.
· DNS events where available.
· Endpoint hostname.
· Endpoint IP address.
· Asset role.
· UniFi OS asset inventory.
· UniFi OS service-process baseline.
· Approved maintenance window records.
· Approved update records.
· Approved package-operation records.
· Approved administrator activity records.
· Change-management records.
· UniFi OS management-plane logs where available.
· Reverse-proxy logs where available.
· Firewall or NDR correlation context where available.
Engineering Implementation Instructions
· Build a SentinelOne asset group for endpoint-visible UniFi OS Server deployments, controller hosts, supporting Linux hosts, and any appliance environment that exposes endpoint telemetry.
· Exclude UniFi OS appliances that do not expose SentinelOne endpoint telemetry from direct SentinelOne coverage claims.
· Build a UniFi OS service-process baseline covering locally observed UniFi OS application processes, controller processes, update-service processes, Java processes, Node.js processes, Nginx or reverse-proxy processes, package-management processes, service wrappers, and approved maintenance scripts.
· Build a suspicious child-process group covering shells, interpreters, package managers, file-retrieval utilities, archive utilities, network utilities, service-management commands, user-management commands, SSH configuration commands, permission-changing commands, and sudo execution.
· Build sensitive path groups covering UniFi OS application directories, update directories, package-management directories, temporary directories, user-writable paths, backup locations, configuration locations, log locations, and administrative staging paths.
· Build approved activity groups covering vendor-guided updates, package operations, controller upgrades, backup jobs, service restarts, administrator troubleshooting, vulnerability management, security testing, vendor support, and incident-response workflows.
· Correlate SentinelOne process events with UniFi OS management-plane logs, reverse-proxy logs, firewall logs, NDR telemetry, DNS telemetry, administrator activity, configuration changes, and change-management records when those sources are available.
· Use short correlation windows for management-plane activity followed by child-process execution, sudo usage, file retrieval, archive extraction, service modification, or outbound process-network activity.
· Use moderate correlation windows for delayed service changes, scheduled job creation, local user changes, SSH configuration changes, backup export behavior, or administrator-state changes.
· Add severity weighting for UniFi OS service lineage, suspicious child-process type, root-context execution, sudo usage, command chaining, temporary-path execution, file retrieval, archive extraction, service modification, unexpected outbound connection, and lack of approved change record.
· Treat process execution from UniFi OS service contexts as a high-confidence host signal only when asset role, process lineage, command behavior, telemetry quality, and maintenance context are validated.
· Validate all SentinelOne event types, Deep Visibility fields, STAR-compatible field mappings, process lineage fields, command-line visibility, file telemetry, user-context fields, network connection fields, asset groups, service-process baselines, suspicious child-process groups, timing windows, exception logic, and local schema mappings before production deployment.
· Do not enable STAR alert mode until endpoint coverage, process-lineage quality, command-line visibility, false-positive rate, query performance, SOC triage workflow, exception handling, and incident-response escalation requirements are validated.
DRI Assessment
DRI
8.7 / 10
· The rule is behaviorally anchored to UniFi OS service-context process lineage, suspicious child-process execution, privileged execution, and post-exploitation host behavior rather than static CVE identifiers, exploit strings, proof-of-concept names, hashes, IP addresses, user agents, or known infrastructure.
· The rule remains useful if an adversary changes command syntax, tool name, outbound destination, file name, staging path, request path, or execution timing.
· The score is supported by the durability of web or application service processes spawning shells, interpreters, package managers, file-retrieval utilities, sudo commands, service-management tools, or root-context processes.
· The score is constrained by environments without SentinelOne endpoint visibility, incomplete command-line capture, incomplete parent-child lineage, limited sudo telemetry, weak UniFi OS process baselines, and legitimate maintenance activity that can resemble suspicious process behavior.
· The rule is highly durable for endpoint-visible UniFi OS deployments but should not be treated as coverage for appliance-only deployments without host telemetry.
TCR Assessment
Operational TCR
7.8 / 10
Full-Telemetry TCR
8.8 / 10
· Operational confidence depends on SentinelOne agent coverage, Deep Visibility retention, process-lineage completeness, command-line visibility, asset-role accuracy, service-process baselines, and maintenance-window validation.
· Operational confidence is reduced where UniFi OS maintenance frequently spawns package managers, service-management tools, shell scripts, backup jobs, or update workflows from service contexts.
· Operational confidence is reduced where endpoint telemetry exists but cannot reliably capture sudo usage, effective user context, command-line arguments, or process-network activity.
· Full-telemetry confidence improves when SentinelOne process and file telemetry is enriched with UniFi OS logs, reverse-proxy logs, firewall logs, NDR telemetry, DNS telemetry, administrator activity, configuration changes, change-management records, and incident-response evidence.
· Even under full telemetry conditions, this rule should classify observed host behavior and escalation likelihood rather than infer actor attribution.
Limitations
· This rule applies only to endpoint-visible UniFi OS deployments and does not provide direct coverage for appliance deployments without SentinelOne telemetry.
· Legitimate updates, package operations, controller upgrades, backup jobs, service restarts, troubleshooting, vendor support, security testing, and incident response can produce similar child-process or privileged-execution behavior.
· Missing command-line capture, weak process lineage, incomplete sudo telemetry, limited file telemetry, or poor asset-role tagging can reduce confidence.
· The rule may miss activity that executes through expected maintenance scripts, uses approved parent-child patterns, avoids suspicious child processes, or occurs outside configured correlation windows.
· The rule should not be used to infer root compromise unless sudo, effective-user, root-context, system, or incident-response evidence supports that conclusion.
· The rule should not be used for actor attribution without incident-specific intelligence, validated behavioral correlation, or confirmed victim-environment evidence.
Detection Query Pattern
SentinelOne Deep Visibility / STAR logic template for endpoint-visible UniFi OS service-context child process and privileged execution behavior. This template requires SentinelOne tenant syntax validation, event-type validation, field-name validation, UniFi OS process-baseline validation, timing-window tuning, and environment-specific allowlisting before STAR promotion.
EndpointEvent AS UniFiServiceChildProcess
WHERE UniFiServiceChildProcess.EndpointName IN ASSET_GROUP (
"Endpoint Visible UniFi OS Servers",
"Endpoint Visible UniFi Controller Hosts",
"Endpoint Visible UniFi Supporting Linux Hosts"
)
AND UniFiServiceChildProcess.EventType IN ANY (
"Process Creation",
"Process Execution",
"Command Execution"
)
AND UniFiServiceChildProcess.ParentProcessName IN ANY (
"unifi",
"unifi-os",
"unifi-network",
"unifi-core",
"java",
"node",
"nginx",
"mongod",
"systemd",
"service-wrapper",
"update-service",
"package-manager"
)
AND UniFiServiceChildProcess.ChildProcessName IN ANY (
"sh",
"bash",
"dash",
"zsh",
"python",
"python3",
"perl",
"ruby",
"node",
"php",
"curl",
"wget",
"scp",
"ssh",
"nc",
"ncat",
"socat",
"tar",
"gzip",
"gunzip",
"unzip",
"dpkg",
"apt",
"apt-get",
"systemctl",
"service",
"chmod",
"chown",
"useradd",
"usermod",
"sudo"
)
AND (
UniFiServiceChildProcess.CommandLine HAS_ANY (
"curl ",
"wget ",
"bash -c",
"sh -c",
"/tmp/",
"/var/tmp/",
"/dev/shm/",
"chmod +x",
"base64",
"python -c",
"python3 -c",
"systemctl",
"service ",
"useradd",
"usermod",
"authorized_keys",
"sudo "
)
OR UniFiServiceChildProcess.ExecutionContext IN ANY (
"root_context",
"sudo_execution",
"unexpected_service_child_process",
"temporary_path_execution",
"application_writable_path_execution",
"package_script_execution"
)
)
AND OPTIONAL_CORRELATION WITHIN ENV_UNIFI_ENDPOINT_CORRELATION_WINDOW (
ManagementOrNetworkEvent AS UniFiManagementContext
WHERE UniFiManagementContext.RelatedAsset IN SAME_ENDPOINT (
UniFiServiceChildProcess.EndpointName
)
AND UniFiManagementContext.EventPattern IN ANY (
"abnormal_management_plane_access",
"authentication_validation_path",
"traversal_style_path",
"update_endpoint_activity",
"request_normalization_mismatch",
"suspicious_source_to_unifi_management"
)
)
AND OPTIONAL_CORRELATION WITHIN ENV_UNIFI_PROCESS_FOLLOWON_WINDOW (
EndpointEvent AS UniFiProcessFollowOn
WHERE UniFiProcessFollowOn.EndpointName IN SAME_ENDPOINT (
UniFiServiceChildProcess.EndpointName
)
AND UniFiProcessFollowOn.EventPattern IN ANY (
"file_retrieval",
"archive_extraction",
"service_modification",
"scheduled_job_creation",
"local_user_change",
"ssh_configuration_change",
"process_network_connection",
"root_context_activity"
)
)
AND NOT ChangeContext IN ANY (
"approved_unifi_update",
"approved_package_operation",
"approved_controller_upgrade",
"approved_backup_job",
"approved_service_restart",
"approved_administrator_troubleshooting",
"approved_vulnerability_management",
"approved_security_testing",
"approved_vendor_support",
"approved_incident_response"
)
Rule
UniFi OS Update Context File Staging and Persistence-Oriented Host Behavior
Rule Format
SentinelOne Deep Visibility hunting logic and STAR custom detection template for endpoint-visible UniFi OS Server, controller-host, or supporting Linux-host deployments after UniFi OS update-process validation, file-path validation, process-network validation, persistence-event validation, command-line field validation, timing-window tuning, and environment-specific allowlisting.
Detection Purpose
· Detect suspicious file staging, script placement, archive extraction, permission modification, service change, scheduled job creation, local user modification, SSH configuration change, or outbound process-network behavior occurring near UniFi OS update or package-management context.
· Identify cases where UniFi OS update-related behavior is followed by host activity consistent with command execution, tool staging, persistence preparation, unauthorized maintenance-path abuse, or post-exploitation setup.
· Prioritize cases where update-context host behavior occurs outside approved maintenance windows or near suspicious management-plane access.
· Support escalation when file staging or persistence-oriented behavior is followed by outbound communication, administrator-state changes, configuration changes, or downstream network-control activity.
· Preserve separation between suspicious host behavior and confirmed compromise by requiring process lineage, file path, user context, maintenance records, source context, and incident-response validation.
· This rule does not apply to UniFi OS appliance deployments that do not expose endpoint file, process, persistence, or network telemetry to SentinelOne or equivalent EDR tooling.
Detection Logic
· Identify endpoint-visible UniFi OS assets with update-service, package-management, application-update, or controller-upgrade process activity.
· Identify file creation, script placement, archive extraction, executable permission changes, service modification, scheduled job creation, local user modification, SSH configuration change, or process-network activity near update or package-management context.
· Prioritize activity involving temporary paths, application-writable paths, update directories, package directories, backup locations, configuration directories, log locations, administrative staging paths, or unusual executable content.
· Increase confidence when file staging or persistence-oriented behavior follows abnormal management-plane access, update-endpoint activity, traversal-style request behavior, suspicious source access, or response anomalies.
· Increase confidence when the process executes as root, uses sudo, changes permissions, modifies services, creates scheduled jobs, creates or modifies local users, alters SSH configuration, or initiates outbound communication to rare or newly observed destinations.
· Increase confidence when host behavior aligns with administrator-state changes, backup export activity, device-adoption changes, gateway policy changes, VPN changes, DNS changes, wireless changes, or downstream network-control behavior.
· Reduce severity when activity aligns with approved firmware updates, package operations, controller upgrades, backup jobs, service restarts, administrator troubleshooting, vulnerability management, security testing, vendor support, incident response, or documented maintenance.
· Do not treat ordinary update operations, package extraction, backup jobs, or service restarts as malicious without suspicious process lineage, file behavior, management-plane correlation, or maintenance mismatch.
· Do not apply this rule to appliance-only environments without SentinelOne endpoint telemetry.
Required Telemetry
· SentinelOne endpoint telemetry.
· Deep Visibility process telemetry.
· File creation events.
· File modification events.
· File permission events where available.
· Script creation events.
· Archive extraction events.
· Process creation events.
· Parent process name.
· Parent process path.
· Child process name.
· Child process path.
· Command line.
· Process user.
· Effective user where available.
· Sudo events where available.
· Service modification events.
· Scheduled job events.
· Local user modification events.
· SSH configuration events where available.
· Process network connection events.
· DNS events where available.
· Endpoint hostname.
· Endpoint IP address.
· Asset role.
· UniFi OS asset inventory.
· UniFi OS update-process baseline.
· UniFi OS file-path baseline.
· Approved maintenance window records.
· Approved update records.
· Approved package-operation records.
· Approved backup records.
· Approved service-restart records.
· Change-management records.
· UniFi OS management-plane logs where available.
· Reverse-proxy logs where available.
· Firewall or NDR correlation context where available.
Engineering Implementation Instructions
· Build a SentinelOne asset group for endpoint-visible UniFi OS Server deployments, controller hosts, supporting Linux hosts, and any appliance environment that exposes endpoint telemetry.
· Exclude UniFi OS appliances that do not expose SentinelOne endpoint telemetry from direct SentinelOne coverage claims.
· Build update-process groups covering UniFi OS update services, package managers, application-update processes, controller-upgrade processes, service restart processes, approved maintenance scripts, and locally observed update workflows.
· Build suspicious file-path groups covering temporary directories, application-writable paths, update directories, package-management paths, backup locations, configuration directories, log locations, administrative staging paths, and uncommon executable paths.
· Build persistence-event groups covering service creation, service modification, scheduled job creation, startup modification, local user creation, local user modification, SSH key changes, SSH configuration changes, permission changes, and unexpected remote-access changes.
· Build outbound process-network groups covering newly observed external destinations, rare domains, rare IP addresses, low-reputation destinations, unexpected ASNs, unusual geographies, tunnel-like traffic, unusual package repositories, and destinations inconsistent with the deployed UniFi OS role.
· Build approved activity groups covering vendor-guided updates, package operations, controller upgrades, backups, service restarts, administrator troubleshooting, vulnerability management, security testing, vendor support, and incident-response workflows.
· Correlate SentinelOne process, file, persistence, and network events with UniFi OS management-plane logs, reverse-proxy logs, firewall logs, NDR telemetry, DNS telemetry, administrator activity, configuration changes, and change-management records when available.
· Use short correlation windows for update activity followed by file creation, script placement, archive extraction, permission changes, service modification, sudo usage, or outbound process-network activity.
· Use moderate correlation windows for delayed scheduled job creation, local user modification, SSH configuration change, administrator-state change, backup export activity, or downstream network-control behavior.
· Add severity weighting for suspicious update lineage, temporary-path writes, application-writable path execution, executable permission changes, archive extraction, script placement, sudo usage, service modification, scheduled job creation, SSH changes, local user changes, rare outbound destination, and lack of approved change record.
· Treat file staging and persistence-oriented behavior near UniFi OS update context as high-value host evidence only when process lineage, file path, user context, maintenance context, and telemetry quality are validated.
· Validate all SentinelOne event types, Deep Visibility fields, STAR-compatible field mappings, file-event fields, process-lineage fields, command-line visibility, user-context fields, process-network fields, asset groups, update-process baselines, suspicious file-path groups, persistence-event groups, outbound groups, timing windows, exception logic, and local schema mappings before production deployment.
· Do not enable STAR alert mode until endpoint coverage, file telemetry quality, process-lineage quality, command-line visibility, user-context quality, false-positive rate, query performance, SOC triage workflow, exception handling, and incident-response escalation requirements are validated.
DRI Assessment
DRI
8.4 / 10
· The rule is behaviorally anchored to update-context file staging, permission modification, persistence-oriented changes, and process-network behavior rather than static CVE identifiers, exploit strings, proof-of-concept names, hashes, filenames, IP addresses, or known infrastructure.
· The rule remains useful if an adversary changes file names, staging paths, archive names, outbound destinations, script names, command syntax, timing, or persistence method.
· The score is supported by the durability of suspicious file staging, archive extraction, permission changes, service modification, scheduled job creation, SSH changes, local user changes, and outbound process-network behavior near UniFi OS update context.
· The score is constrained by legitimate update behavior, backup jobs, package extraction, service restarts, maintenance scripts, incomplete file telemetry, weak update baselines, and environments without SentinelOne endpoint visibility.
· The rule is durable for endpoint-visible UniFi OS deployments but should not be treated as coverage for appliance-only environments without host telemetry.
TCR Assessment
Operational TCR
7.4 / 10
Full-Telemetry TCR
8.6 / 10
· Operational confidence depends on SentinelOne endpoint coverage, Deep Visibility retention, file-event completeness, process-lineage quality, command-line visibility, user-context accuracy, update-process baselines, and maintenance-window validation.
· Operational confidence is reduced where UniFi OS updates regularly create files, extract archives, modify permissions, restart services, or run maintenance scripts from paths similar to suspicious staging locations.
· Operational confidence is reduced where file telemetry exists but cannot reliably capture archive extraction, permission changes, scheduled jobs, SSH configuration changes, or process-network events.
· Full-telemetry confidence improves when SentinelOne file, process, persistence, and network telemetry is enriched with UniFi OS logs, reverse-proxy logs, firewall logs, NDR telemetry, DNS telemetry, administrator activity, configuration changes, change-management records, and incident-response evidence.
· Even under full telemetry conditions, this rule should classify suspicious host behavior and escalation likelihood rather than infer actor attribution.
Limitations
· This rule applies only to endpoint-visible UniFi OS deployments and does not provide direct coverage for appliance deployments without SentinelOne telemetry.
· Legitimate updates, package operations, archive extraction, controller upgrades, backup jobs, service restarts, maintenance scripts, troubleshooting, vendor support, security testing, and incident response can produce similar file or persistence behavior.
· Missing file telemetry, incomplete command-line capture, weak process lineage, incomplete user context, missing sudo telemetry, or poor update-process baselines can reduce confidence.
· The rule may miss activity that uses approved update workflows, expected file paths, trusted maintenance scripts, memory-only execution, or delayed persistence outside configured correlation windows.
· The rule should not be used to infer root compromise unless sudo, effective-user, root-context, system, or incident-response evidence supports that conclusion.
· The rule should not be used for actor attribution without incident-specific intelligence, validated behavioral correlation, or confirmed victim-environment evidence.
Detection Query Pattern
SentinelOne Deep Visibility / STAR logic template for endpoint-visible UniFi OS update-context file staging and persistence-oriented host behavior. This template requires SentinelOne tenant syntax validation, event-type validation, field-name validation, UniFi OS update-process validation, file-path validation, timing-window tuning, and environment-specific allowlisting before STAR promotion.
EndpointEvent AS UniFiUpdateContextHostActivity
WHERE UniFiUpdateContextHostActivity.EndpointName IN ASSET_GROUP (
"Endpoint Visible UniFi OS Servers",
"Endpoint Visible UniFi Controller Hosts",
"Endpoint Visible UniFi Supporting Linux Hosts"
)
AND (
UniFiUpdateContextHostActivity.ParentProcessName IN ANY (
"unifi",
"unifi-os",
"unifi-network",
"unifi-core",
"java",
"node",
"nginx",
"systemd",
"service-wrapper",
"update-service",
"package-manager",
"apt",
"apt-get",
"dpkg"
)
OR UniFiUpdateContextHostActivity.EventPattern IN ANY (
"update_service_activity",
"package_management_activity",
"controller_upgrade_activity",
"update_triggered_service_activity"
)
)
AND UniFiUpdateContextHostActivity.EventType IN ANY (
"File Creation",
"File Modification",
"File Permission Change",
"Archive Extraction",
"Process Creation",
"Service Modification",
"Scheduled Job Creation",
"Local User Modification",
"SSH Configuration Change",
"Process Network Connection"
)
AND (
UniFiUpdateContextHostActivity.FilePath HAS_ANY (
"/tmp/",
"/var/tmp/",
"/dev/shm/",
"/var/lib/",
"/usr/lib/",
"/usr/local/",
"/opt/",
"/etc/systemd/",
"/etc/init.d/",
"/etc/cron",
"/root/.ssh/",
"/home/",
"/var/log/",
"/backup/",
"/config/"
)
OR UniFiUpdateContextHostActivity.CommandLine HAS_ANY (
"chmod +x",
"chown ",
"tar ",
"unzip ",
"curl ",
"wget ",
"systemctl",
"service ",
"crontab",
"authorized_keys",
"useradd",
"usermod",
"sudo "
)
OR UniFiUpdateContextHostActivity.EventPattern IN ANY (
"temporary_path_write",
"application_writable_path_write",
"archive_extraction",
"executable_permission_change",
"service_modification",
"scheduled_job_creation",
"local_user_change",
"ssh_configuration_change",
"rare_process_network_connection"
)
)
AND OPTIONAL_CORRELATION WITHIN ENV_UNIFI_ENDPOINT_CORRELATION_WINDOW (
ManagementOrNetworkEvent AS UniFiManagementContext
WHERE UniFiManagementContext.RelatedAsset IN SAME_ENDPOINT (
UniFiUpdateContextHostActivity.EndpointName
)
AND UniFiManagementContext.EventPattern IN ANY (
"abnormal_management_plane_access",
"update_endpoint_activity",
"traversal_style_path",
"authentication_validation_path",
"request_normalization_mismatch",
"suspicious_source_to_unifi_management"
)
)
AND OPTIONAL_CORRELATION WITHIN ENV_UNIFI_HOST_FOLLOWON_WINDOW (
EndpointEvent AS UniFiHostFollowOn
WHERE UniFiHostFollowOn.EndpointName IN SAME_ENDPOINT (
UniFiUpdateContextHostActivity.EndpointName
)
AND UniFiHostFollowOn.EventPattern IN ANY (
"root_context_activity",
"sudo_execution",
"outbound_process_network_connection",
"rare_external_destination",
"administrator_state_change",
"backup_export_activity",
"configuration_change",
"downstream_network_control_activity"
)
)
AND NOT ChangeContext IN ANY (
"approved_unifi_update",
"approved_package_operation",
"approved_controller_upgrade",
"approved_backup_job",
"approved_service_restart",
"approved_administrator_troubleshooting",
"approved_vulnerability_management",
"approved_security_testing",
"approved_vendor_support",
"approved_incident_response"
)
Splunk
Detection Viability Assessment
Splunk has three rules for this EXP report.
· Splunk is viable for detecting UniFi OS control-plane compromise behavior where UniFi OS management-plane logs, reverse-proxy logs, firewall logs, NDR telemetry, DNS telemetry, endpoint telemetry where available, administrator activity logs, configuration-change records, asset inventory, and change-management records are normalized or correlated into searchable datasets.
· Splunk is strongest for correlating abnormal UniFi OS management-plane access, suspicious source context, authentication-validation or traversal-style request behavior, update-endpoint activity, process or sudo evidence where available, outbound communication, administrator-state changes, and downstream network-control changes.
· Splunk can support both direct alerting and hunt-stage logic depending on field completeness, request-path visibility, endpoint telemetry availability, administrator-audit quality, asset inventory, lookup quality, and change-management integration.
· Splunk should not treat exposed management interfaces, scanner output, patch state, isolated denied requests, single web errors, ordinary update checks, or normal administrator access as exploitation evidence by themselves.
· Splunk detections must preserve separate analytic outcomes for exposure, attempted exploitation, suspected management-plane compromise, suspected root-level compromise, unauthorized configuration change, downstream network-control impact, and confirmed post-exploitation activity.
· Splunk rules should use local field mappings, accelerated data models or summary indexes where appropriate, lookup-driven enrichment, bounded time windows, approved-change suppression, and SOC triage fields before production alerting.
· Splunk should not infer command execution, sudo-assisted privilege escalation, root compromise, credential theft, data exfiltration, downstream compromise, or actor attribution without supporting host, system, administrator, configuration, or incident-response evidence.
Rule
UniFi OS Management-Plane Exploit-Path Access With Suspicious Source Context
Rule Format
Splunk SPL correlation search suitable for web, reverse-proxy, firewall, secure access, load-balancer, NDR, and DNS telemetry after local index validation, sourcetype validation, field normalization, UniFi OS asset lookup validation, approved administrator lookup validation, suspicious source enrichment validation, request-path field validation, timing-window tuning, and environment-specific allowlisting.
Detection Purpose
· Detect abnormal UniFi OS management-plane access involving authentication-validation paths, traversal-style request behavior, update endpoints, unexpected file-access paths, request-normalization mismatch indicators, or access patterns inconsistent with approved administration.
· Identify suspicious source context involving unfamiliar internet sources, newly observed sources, hosting providers, residential proxy ranges, suspicious ASNs, unusual geographies, VPN ingress paths, unmanaged internal hosts, or sources outside approved administrator baselines.
· Prioritize cases where request-path behavior and source-path deviation occur together rather than treating exposure or scanning as compromise evidence.
· Support early escalation when exploit-path request behavior is followed by update-endpoint activity, administrator-state changes, configuration changes, outbound communication, or downstream management activity.
· Preserve separation between suspicious management-plane access and confirmed compromise by requiring supporting UniFi OS, endpoint, system, administrator, configuration, or incident-response evidence before classifying activity as probable compromise.
· This rule does not prove successful command execution, sudo-assisted escalation, root compromise, credential theft, downstream infrastructure compromise, or actor attribution without supporting telemetry and investigation evidence.
Detection Logic
· Search normalized web, reverse-proxy, firewall, secure access, load-balancer, NDR, or DNS telemetry for activity targeting verified UniFi OS management interfaces.
· Match locally mapped request-path categories associated with authentication-validation behavior, traversal-style path construction, encoded path variation, update-endpoint access, package-management endpoints, unexpected file-access paths, or request-normalization mismatch indicators.
· Enrich events with UniFi OS asset inventory, approved administrator source baselines, VPN administration ranges, management networks, jump hosts, privileged access workstations, source reputation, ASN, geolocation, and newly observed source context.
· Increase confidence when repeated request attempts, path variations, unusual request ordering, HTTP 5xx patterns, abnormal response sizes, redirect anomalies, or abnormal status-code sequences occur within a bounded time window.
· Increase confidence when suspicious management-plane access is followed by update-endpoint activity, administrator-session anomalies, API token activity, administrator-account changes, backup export activity, device-adoption activity, configuration changes, outbound communication, or downstream management activity.
· Reduce severity when activity aligns with approved administration, vulnerability scanning, exposure assessment, monitoring, security testing, vendor support, incident response, or documented maintenance.
· Do not classify vulnerable-state findings, exposed interfaces, scanner labels, isolated denied requests, ordinary login failures, or single web errors as exploitation evidence by themselves.
· Do not treat network-visible exploit-path behavior as proof of command execution or root compromise without supporting host, administrator, configuration, or incident-response evidence.
Required Telemetry
· Splunk-indexed web telemetry.
· Reverse-proxy telemetry where available.
· Firewall telemetry.
· Secure access telemetry where available.
· Load-balancer telemetry where available.
· NDR telemetry where available.
· DNS telemetry where available.
· Source IP.
· Destination IP.
· Destination host.
· Destination interface.
· Destination port.
· Protocol.
· HTTP method where available.
· Request path where available.
· Normalized request path where available.
· Raw request path where available.
· Response status where available.
· Response size where available.
· User agent where available.
· Session identifier where available.
· Event timestamp.
· UniFi OS asset lookup.
· UniFi OS management-interface lookup.
· Approved administrator source lookup.
· VPN administration range lookup.
· Management network lookup.
· Jump-host lookup.
· Privileged access workstation lookup.
· Source-reputation enrichment.
· ASN enrichment.
· Geolocation enrichment.
· Newly observed source enrichment.
· Change-management lookup.
· Approved scanning and security-testing lookup.
· Incident-response exception lookup.
Engineering Implementation Instructions
· Validate Splunk indexes, sourcetypes, CIM mappings, local field names, timestamp consistency, request-path availability, response-code availability, source-IP normalization, destination-host normalization, and asset identifiers before deployment.
· Build or validate a unifi_os_assets lookup covering UniFi OS Server deployments, consoles, cloud gateways, dream machines, cloud keys, gateways, recorders, storage appliances, controller hosts, exposed management interfaces, and management-plane IP addresses.
· Build or validate a unifi_approved_admin_sources lookup covering administrator IPs, VPN ranges, jump hosts, privileged access workstations, management networks, monitoring systems, vendor-support paths, vulnerability management systems, security-testing systems, and incident-response systems.
· Build or validate a unifi_exploit_path_categories lookup mapping local request paths, normalized paths, raw paths, web classifications, and reverse-proxy classifications to authentication-validation paths, traversal-style paths, encoded path variations, update endpoints, package-management endpoints, unexpected file-access paths, and request-normalization mismatch indicators.
· Build or validate enrichment lookups for source reputation, ASN, geolocation, newly observed source context, approved change windows, approved scanning, approved maintenance, approved vendor support, and incident-response exceptions.
· Use summary indexing or accelerated datasets for high-volume web, firewall, reverse-proxy, and NDR telemetry when raw-event correlation would create unacceptable search cost.
· Use bounded time windows for request bursts, path variation, response anomalies, and source-baseline deviation.
· Use moderate follow-on windows for administrator-state changes, configuration changes, outbound communication, backup export activity, device-adoption activity, or downstream management activity.
· Avoid broad raw joins, unbounded subsearches, repeated mvexpand, and direct high-cardinality exclusion lists in production correlation searches.
· Use lookup-output flags such as is_unifi_asset, is_approved_admin_source, is_suspicious_source, is_exploit_path_category, is_approved_change, and is_security_testing to support efficient correlation and suppression.
· Validate false-positive baselines for vulnerability scanning, exposure assessment, administrator troubleshooting, vendor support, security testing, monitoring, firmware updates, package operations, and incident-response workflows.
· Do not enable alert mode until field coverage, lookup quality, enrichment reliability, query performance, alert volume, suppression logic, SOC triage fields, and incident-response escalation paths are validated.
DRI Assessment
DRI
8.6 / 10
· The rule is behaviorally anchored to UniFi OS management-plane exploit-path access, suspicious source context, request-path anomaly, and follow-on control-plane activity rather than static CVE identifiers, proof-of-concept names, scanner labels, fixed user agents, IP addresses, hashes, or actor infrastructure.
· The rule remains useful if an adversary changes request pacing, user agent, source infrastructure, path encoding, request ordering, or post-access timing.
· The score is supported by durable management-plane access anomalies, source-path deviation, request-normalization mismatch indicators, update-endpoint interaction, response anomalies, and follow-on correlation.
· The score is constrained by missing request paths, reverse-proxy normalization, incomplete source baselines, high internet scanning volume, weak asset inventories, and incomplete change-management data.
· The rule is durable as an early exploit-path detector but should not be treated as standalone proof of command execution, root compromise, or actor attribution.
TCR Assessment
Operational TCR
7.8 / 10
Full-Telemetry TCR
8.7 / 10
· Operational confidence depends on reliable request-path telemetry, UniFi OS asset lookup quality, approved administrator baseline quality, source enrichment, response-code visibility, and Splunk field normalization.
· Operational confidence is reduced where reverse proxies strip useful request details, exposed management interfaces receive heavy scanning, approved administrator paths are broad, or source reputation enrichment is unavailable.
· Operational confidence is reduced where vulnerability scanning, exposure assessment, monitoring, security testing, vendor support, or incident-response workflows generate similar request behavior.
· Full-telemetry confidence improves when Splunk correlates suspicious access with UniFi OS logs, administrator audit logs, update-service logs, endpoint telemetry where available, configuration-change records, NDR telemetry, DNS telemetry, change-management records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support escalation and scoping rather than standalone confirmation of exploit success or root compromise.
Limitations
· This rule detects suspicious UniFi OS management-plane access and exploit-path request behavior, not confirmed exploitation by itself.
· Missing raw request paths, normalized paths, response status, response size, user agent, or source enrichment can reduce confidence.
· Internet scanning, vulnerability assessment, penetration testing, monitoring, vendor support, administrator troubleshooting, and incident-response activity may produce similar management-plane request patterns.
· The rule may miss exploitation that originates from approved administrator sources, uses expected management paths, blends into normal access patterns, or occurs outside configured timing windows.
· The rule should not be used to infer command execution, root compromise, data exfiltration, or actor attribution without supporting evidence.
· The rule requires local Splunk field mapping, lookup validation, suppression validation, and query-performance testing before alert promotion.
Detection Query Pattern
Splunk SPL query pattern for UniFi OS management-plane exploit-path access with suspicious source context. This pattern requires local index, sourcetype, macro, lookup, field-name, and data-model validation before production deployment.
unifi_management_ingress_events
| eval src_ip=coalesce(src_ip, src, client_ip, c_ip), dest_ip=coalesce(dest_ip, dest, d_ip), dest_host=coalesce(dest_host, host, dvc, device_name), request_path=coalesce(uri_path, url_path, request_path, uri), http_method=coalesce(http_method, method), http_status=coalesce(status, http_status, response_code), user_agent=coalesce(user_agent, http_user_agent)
| lookup unifi_os_assets dest_ip AS dest_ip OUTPUT is_unifi_asset, unifi_asset_role, unifi_management_interface
| lookup unifi_approved_admin_sources src_ip AS src_ip OUTPUT is_approved_admin_source, approved_source_type
| lookup unifi_exploit_path_categories request_path AS request_path OUTPUT is_exploit_path_category, exploit_path_category
| lookup source_reputation src_ip AS src_ip OUTPUT source_reputation, source_asn, source_geo, is_hosting_provider, is_residential_proxy, is_suspicious_asn
| lookup unifi_change_context dest_ip AS dest_ip OUTPUT is_approved_change, change_type, change_window
| where is_unifi_asset="true"
| eval suspicious_source=if(is_approved_admin_source!="true" AND (is_hosting_provider="true" OR is_residential_proxy="true" OR is_suspicious_asn="true" OR source_reputation IN ("low","unknown") OR approved_source_type=""), 1, 0)
| eval response_anomaly=if(http_status>=500 OR http_status IN (401,403,404) OR isnull(http_status), 1, 0)
| bin time span=10m
| stats count AS requestcount dc(request_path) AS distinct_paths values(exploit_path_category) AS exploit_path_categories values(http_status) AS http_statuses values(user_agent) AS user_agents max(suspicious_source) AS suspicious_source max(response_anomaly) AS response_anomaly values(source_reputation) AS source_reputation values(source_asn) AS source_asn values(source_geo) AS source_geo values(unifi_asset_role) AS unifi_asset_role values(unifi_management_interface) AS unifi_management_interface values(is_approved_change) AS is_approved_change by time, srcip, dest_ip, dest_host
| eval repeated_variation=if(request_count>=ENV_UNIFI_REQUEST_THRESHOLD AND distinct_paths>=ENV_UNIFI_PATH_VARIATION_THRESHOLD, 1, 0)
| where exploit_path_categories!="" AND suspicious_source=1 AND (repeated_variation=1 OR response_anomaly=1 OR request_count>=ENV_UNIFI_REQUEST_THRESHOLD)
| where is_approved_change!="true"
| eval detection_outcome="Suspicious UniFi OS management-plane exploit-path access requiring correlation"
| eval confidence="Medium to High"
| table time, srcip, dest_ip, dest_host, unifi_asset_role, unifi_management_interface, request_count, distinct_paths, exploit_path_categories, http_statuses, user_agents, source_reputation, source_asn, source_geo, detection_outcome, confidence
Rule
UniFi OS Update or Package Activity Followed by Endpoint or Network Follow-On Behavior
Rule Format
Splunk SPL scheduled summary-correlation search suitable for UniFi OS web and application logs, update-service logs where available, package-management logs where available, endpoint telemetry where available, NDR telemetry, firewall telemetry, DNS telemetry, proxy telemetry, administrator activity logs, configuration-change records, and change-management records after local index validation, sourcetype validation, field normalization, lookup validation, summary-index validation, timing-window tuning, and environment-specific allowlisting.
Detection Purpose
· Detect UniFi OS update-endpoint, package-management, or application-update activity followed by suspicious endpoint, outbound, administrator, configuration, or downstream management behavior.
· Identify cases where update or package activity becomes higher risk because it is followed by shell execution, interpreter execution, file retrieval, archive extraction, sudo usage, root-context activity, outbound communication, administrator-state change, configuration change, or internal management access.
· Prioritize behavior where update context appears near abnormal management-plane access or suspicious source context.
· Support escalation when update/package activity links to process execution, outbound communication, backup export activity, device-adoption changes, gateway policy changes, VPN changes, DNS changes, wireless changes, or downstream network-control activity.
· Preserve separation between suspicious follow-on behavior and confirmed compromise by requiring supporting host, system, administrator, configuration, or incident-response evidence.
· This rule does not prove successful command injection, root compromise, credential theft, data exfiltration, downstream infrastructure compromise, or actor attribution without supporting evidence.
Detection Logic
· Identify UniFi OS update-endpoint, package-management, application-update, or update-service activity from verified UniFi OS assets and write normalized candidates to a scheduled summary dataset.
· Identify endpoint follow-on behavior where available, including shell execution, interpreter execution, package-manager execution, file retrieval, archive extraction, sudo usage, service modification, scheduled job creation, local user change, SSH configuration change, or root-context activity.
· Identify outbound or downstream follow-on behavior involving newly observed, rare, low-reputation, unusual, role-inconsistent, or unexpected destinations, internal scanning, device enumeration, additional management-interface access, or downstream management activity.
· Correlate update candidates with endpoint, outbound, administrator, configuration, and downstream candidates using bounded windows and shared UniFi OS asset identifiers.
· Increase confidence when update or package activity occurs after abnormal source access, traversal-style request behavior, authentication-validation anomalies, response anomalies, or management-plane access from a non-standard source.
· Reduce severity when activity aligns with approved firmware updates, package operations, controller upgrades, backup jobs, vendor support, monitoring, security testing, incident response, or documented maintenance.
· Do not treat ordinary update checks, vendor repository access, expected package operations, backup jobs, service restarts, or routine administrator maintenance as malicious by themselves.
· Do not infer root compromise or data exfiltration unless supporting process, sudo, effective-user, file, network, administrator, configuration, or incident-response evidence exists.
Required Telemetry
· Splunk-indexed UniFi OS management-plane logs where available.
· UniFi OS update-service logs where available.
· Package-management logs where available.
· Web or reverse-proxy telemetry.
· Endpoint process telemetry where available.
· Endpoint file telemetry where available.
· Sudo or effective-user telemetry where available.
· Firewall telemetry.
· NDR telemetry where available.
· DNS telemetry.
· Proxy telemetry where available.
· Administrator activity logs where available.
· Configuration-change logs where available.
· Change-management records.
· Source IP.
· Destination IP.
· Destination host.
· Asset role.
· Request path where available.
· Event timestamp.
· Process name where available.
· Parent process where available.
· Command line where available.
· Process user where available.
· Destination domain where available.
· External destination reputation where available.
· Configuration object where available.
· Change type where available.
· UniFi OS asset lookup.
· Approved update lookup.
· Approved destination lookup.
· Approved administrator lookup.
· Approved change lookup.
Engineering Implementation Instructions
· Validate Splunk indexes, sourcetypes, CIM mappings, endpoint field mappings, UniFi OS field mappings, network field mappings, administrator-audit field mappings, configuration-change field mappings, and timestamp normalization before deployment.
· Build or validate a unifi_update_activity macro or lookup that identifies update endpoints, package-management paths, package repository access, application-update paths, update-service events, and locally observed UniFi OS update workflows.
· Build or validate a unifi_host_followon_behavior macro or lookup covering shell execution, interpreter execution, file retrieval, archive extraction, package-manager execution, sudo usage, root-context activity, service modification, scheduled job creation, local user changes, SSH configuration changes, and outbound process-network activity.
· Build or validate a unifi_outbound_risk macro or lookup covering newly observed external destinations, rare domains, rare IP addresses, low-reputation destinations, unexpected ASNs, unusual geographies, tunnel-like traffic, unusual package repositories, and destinations inconsistent with the deployed UniFi OS role.
· Build or validate a unifi_config_followon macro or lookup covering administrator changes, API token activity, backup exports, device adoption, gateway policy changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, and managed-device configuration changes.
· Use scheduled candidate searches that write normalized update, endpoint-follow-on, network-follow-on, and configuration-follow-on events to a summary index before running production alert correlation.
· Use bounded windows between update candidates and follow-on candidates instead of broad raw-event correlation across high-volume datasets.
· Prefer accelerated datasets or scheduled intermediate searches for high-volume endpoint, web, firewall, DNS, NDR, and proxy telemetry.
· Avoid unbounded joins, broad raw-event appends, broad subsearch membership checks, repeated mvexpand, and literal high-cardinality exclusion lists.
· Use lookup-output flags for approved update windows, approved package operations, approved vendor destinations, approved monitoring destinations, approved backup destinations, approved administrator sources, approved security testing, and approved incident-response activity.
· Validate false-positive baselines for firmware updates, package operations, controller upgrades, backup jobs, service restarts, monitoring traffic, vendor support, vulnerability management, security testing, and incident-response workflows.
· Do not enable alert mode until endpoint coverage, update-path quality, outbound baseline quality, administrator-context quality, configuration telemetry, summary-index quality, query performance, false-positive rate, suppression behavior, SOC triage workflow, and incident-response escalation requirements are validated.
DRI Assessment
DRI
8.3 / 10
· The rule is behaviorally anchored to UniFi OS update or package activity followed by endpoint, outbound, administrator, configuration, or downstream behavior rather than static CVE identifiers, exploit strings, proof-of-concept names, hashes, IP addresses, user agents, or known infrastructure.
· The rule remains useful if an adversary changes command syntax, file names, outbound destinations, tool names, staging paths, timing, or downstream target order.
· The score is supported by durable update-path interaction followed by child-process behavior, file retrieval, archive extraction, sudo activity, outbound communication, administrator-state change, configuration changes, or downstream management activity.
· The score is constrained by legitimate update behavior, weak update baselines, incomplete endpoint telemetry, missing package logs, noisy outbound traffic, incomplete administrator logs, and incomplete configuration-change records.
· The rule is durable as a cross-telemetry follow-on detector but should not be treated as standalone proof of command injection, root compromise, data exfiltration, or actor attribution.
TCR Assessment
Operational TCR
7.5 / 10
Full-Telemetry TCR
8.8 / 10
· Operational confidence depends on UniFi OS update-path visibility, endpoint telemetry availability, process-lineage quality, command-line visibility, outbound telemetry, administrator logs, configuration telemetry, and change-management integration.
· Operational confidence is reduced where update behavior is poorly baselined, package logs are unavailable, endpoint visibility is absent, or approved update destinations are not documented.
· Operational confidence is reduced where monitoring tools, backup workflows, vendor services, vulnerability management, security testing, or incident response produce similar follow-on behavior.
· Full-telemetry confidence improves when Splunk correlates UniFi OS logs, endpoint process and file telemetry, sudo logs, firewall logs, DNS logs, NDR telemetry, administrator activity, configuration-change records, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support escalation and scoping rather than standalone confirmation of exploit success, root compromise, or data exfiltration.
Limitations
· This rule detects suspicious follow-on behavior after UniFi OS update or package activity, not confirmed exploitation by itself.
· Endpoint-specific portions apply only where process, command-line, sudo, file, or service telemetry exists.
· Approved vendor updates, monitoring tools, backup workflows, administrator actions, vulnerability management, security testing, incident response, and remote-management activity can produce similar follow-on patterns.
· Missing endpoint telemetry, DNS telemetry, proxy telemetry, destination reputation, administrator logs, configuration records, source baselines, or change records can reduce confidence.
· The rule may miss activity that uses approved destinations, expected update workflows, approved parent-child process patterns, or delayed follow-on activity outside configured correlation windows.
· The rule should not be used for actor attribution without incident-specific intelligence, validated behavioral correlation, or confirmed victim-environment evidence.
Detection Query Pattern
Splunk SPL summary-correlation pattern for UniFi OS update or package activity followed by endpoint or network follow-on behavior. This pattern assumes scheduled candidate searches populate unifi_update_activity_summary, unifi_endpoint_followon_summary, unifi_network_followon_summary, and unifi_config_followon_summary. Local index, sourcetype, macro, lookup, field-name, timing-window, summary-index, and data-model validation are required before production deployment.
index=summary source=unifi_update_activity_summary earliest=-ENV_UNIFI_UPDATE_LOOKBACK latest=now
| eval candidate_type="update_activity", unifi_asset=coalesce(unifi_asset, dest_host, host, dvc, device_name), update_time=_time
| lookup unifi_os_assets unifi_asset AS unifi_asset OUTPUT is_unifi_asset, unifi_asset_role
| lookup unifi_change_context unifi_asset AS unifi_asset OUTPUT is_approved_change, change_type, change_window
| where is_unifi_asset="true"
| fields update_time, unifi_asset, unifi_asset_role, src_ip, request_path, update_activity_type, event_type, is_approved_change
| append [
search index=summary source=unifi_endpoint_followon_summary earliest=-ENV_UNIFI_UPDATE_LOOKBACK latest=now
| eval candidate_type="endpoint_followon", unifi_asset=coalesce(unifi_asset, endpoint_name, dest_host, host, dvc, device_name), followon_time=_time
| lookup unifi_os_assets unifi_asset AS unifi_asset OUTPUT is_unifi_asset
| where is_unifi_asset="true"
| fields followon_time, unifi_asset, process_name, parent_process, command_line, process_user, host_followon_type, candidate_type
]
| append [
search index=summary source=unifi_network_followon_summary earliest=-ENV_UNIFI_UPDATE_LOOKBACK latest=now
| eval candidate_type="network_followon", unifi_asset=coalesce(unifi_asset, src_host, host, dvc, device_name), followon_time=_time
| lookup unifi_os_assets unifi_asset AS unifi_asset OUTPUT is_unifi_asset
| where is_unifi_asset="true"
| fields followon_time, unifi_asset, dest_ip, dest_domain, network_action, network_followon_type, candidate_type
]
| append [
search index=summary source=unifi_config_followon_summary earliest=-ENV_UNIFI_UPDATE_LOOKBACK latest=now
| eval candidate_type="config_followon", unifi_asset=coalesce(unifi_asset, related_unifi_asset, controller_host, host, dvc, device_name), followon_time=_time
| lookup unifi_os_assets unifi_asset AS unifi_asset OUTPUT is_unifi_asset
| where is_unifi_asset="true"
| fields followon_time, unifi_asset, administrator, config_object, change_type, config_followon_type, candidate_type
]
| eventstats min(update_time) AS first_update_time max(update_time) AS last_update_time values(update_activity_type) AS update_activity_types values(request_path) AS update_paths values(is_approved_change) AS approved_change_context by unifi_asset
| where isnotnull(first_update_time) AND isnotnull(followon_time)
| eval time_from_update=followon_time-first_update_time
| where time_from_update>=0 AND time_from_update<=ENV_UNIFI_UPDATE_FOLLOWON_WINDOW
| where approved_change_context!="true"
| stats values(update_activity_types) AS update_activity_types values(update_paths) AS update_paths values(process_name) AS process_names values(parent_process) AS parent_processes values(command_line) AS command_lines values(process_user) AS process_users values(dest_ip) AS dest_ips values(dest_domain) AS dest_domains values(network_action) AS network_actions values(administrator) AS administrators values(config_object) AS config_objects values(change_type) AS change_types values(host_followon_type) AS host_followon_types values(network_followon_type) AS network_followon_types values(config_followon_type) AS config_followon_types min(first_update_time) AS first_update_time min(followon_time) AS first_followon_time by unifi_asset
| eval detection_outcome="UniFi OS update or package activity followed by suspicious endpoint, network, or configuration behavior"
| eval confidence="Medium to High"
| table first_update_time, first_followon_time, unifi_asset, update_activity_types, update_paths, process_names, parent_processes, command_lines, process_users, dest_ips, dest_domains, network_actions, administrators, config_objects, change_types, host_followon_types, network_followon_types, config_followon_types, detection_outcome, confidence
Rule
UniFi OS Exploit-Path Activity Followed by Downstream Configuration Change
Rule Format
Splunk SPL scheduled summary-correlation search suitable for UniFi OS management-plane telemetry, web or reverse-proxy logs, firewall telemetry, NDR telemetry, administrator activity logs, configuration-change records, downstream device logs, and change-management records after local index validation, sourcetype validation, field normalization, configuration-event mapping, administrator-context mapping, lookup validation, summary-index validation, timing-window tuning, and environment-specific allowlisting.
Detection Purpose
· Detect suspected UniFi OS exploit-path activity followed by downstream configuration changes affecting gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless configuration, device adoption, recorder behavior, storage access, or managed-device trust.
· Identify cases where UniFi OS management-plane compromise may create operational risk through network-control changes, access-path expansion, segmentation changes, remote-access modification, traffic-handling changes, or device-trust manipulation.
· Prioritize downstream changes that occur near abnormal UniFi OS management-plane access, suspicious source context, update-endpoint activity, administrator-state anomalies, outbound communication, or endpoint evidence where available.
· Support escalation when downstream changes are not explained by approved change records, known administrators, expected maintenance windows, device onboarding, vendor support, security testing, or incident response.
· Preserve separation between suspicious downstream changes and confirmed compromise by requiring linkage to UniFi OS exploit-path activity, administrator anomalies, configuration evidence, or incident-response validation.
· This rule does not prove command execution, root compromise, credential theft, data exfiltration, downstream compromise, or actor attribution without supporting host, administrator, system, configuration, or incident-response evidence.
Detection Logic
· Identify abnormal UniFi OS management-plane access, exploit-path request behavior, update-endpoint activity, suspicious source context, or related endpoint/network follow-on behavior involving verified UniFi OS assets and write normalized upstream candidates to a scheduled summary dataset.
· Identify downstream configuration changes affecting gateway policy, firewall rules, routing, VPN access, DNS settings, wireless settings, device adoption, recorder behavior, storage access, or managed-device trust and write normalized downstream candidates to a scheduled summary dataset.
· Prioritize changes involving remote-access expansion, firewall weakening, new inbound exposure, segmentation changes, route changes, DNS forwarding changes, VPN access changes, wireless security changes, unexpected device adoption, backup export behavior, or management-access expansion.
· Correlate upstream UniFi OS candidates with downstream configuration candidates using bounded windows, shared UniFi OS asset identifiers, related controller identifiers, administrator context, and change-window context.
· Increase confidence when the downstream change is performed by a newly created administrator, rarely used administrator, unfamiliar source, unusual geography, suspicious ASN, API token, or administrative session created near suspected exploit-path activity.
· Increase confidence when downstream changes are followed by unusual outbound communication, internal scanning, additional management-interface access, high-value system access, monitoring disruption, logging gaps, or defensive visibility reduction.
· Reduce severity when downstream changes align with approved network maintenance, device replacement, site onboarding, firewall policy updates, VPN changes, DNS changes, wireless changes, vendor support, security testing, incident response, or documented change-control activity.
· Do not classify downstream network-control changes as UniFi OS compromise without upstream UniFi OS exploit-path activity, administrator-state anomaly, suspicious source context, or incident-response validation.
· Do not treat legitimate network maintenance or expected device-adoption workflows as compromise indicators solely because UniFi OS is vulnerable or exposed.
Required Telemetry
· Splunk-indexed UniFi OS management-plane telemetry where available.
· Web telemetry where available.
· Reverse-proxy telemetry where available.
· Firewall telemetry.
· NDR telemetry where available.
· Administrator activity logs where available.
· Configuration-change telemetry where available.
· Downstream network-device logs where available.
· DNS telemetry where available.
· Endpoint telemetry where available.
· Change-management records.
· Source IP.
· Destination IP.
· Destination host.
· Asset role.
· Request path where available.
· Event timestamp.
· Administrator identity where available.
· Session context where available.
· API token context where available.
· Configuration object.
· Configuration action.
· Change type.
· Device identifier.
· Device role.
· Network segment.
· UniFi OS asset lookup.
· Downstream device inventory lookup.
· Approved administrator lookup.
· Approved change lookup.
· High-risk change mapping.
· Incident-response exception lookup.
Engineering Implementation Instructions
· Validate Splunk indexes, sourcetypes, CIM mappings, local field names, timestamp consistency, configuration-event parsing, administrator-context parsing, downstream device identifiers, and change-record identifiers before deployment.
· Build or validate a unifi_upstream_suspicious_activity macro or scheduled summary search that identifies abnormal management-plane access, exploit-path request categories, update-endpoint activity, suspicious source context, response anomalies, endpoint follow-on behavior where available, and outbound follow-on behavior.
· Build or validate a unifi_downstream_config_changes macro or scheduled summary search covering gateway policy changes, firewall rule changes, route changes, VPN changes, DNS changes, wireless changes, device-adoption changes, recorder changes, storage changes, and managed-device configuration changes.
· Build or validate a unifi_high_risk_config_changes lookup for remote-access expansion, firewall weakening, new inbound exposure, segmentation change, default route change, DNS forwarding change, VPN access change, wireless security weakening, unexpected device adoption, backup export, and management-access expansion.
· Build or validate administrator-risk enrichment for newly created administrators, rarely used administrators, unusual source geographies, suspicious ASNs, unfamiliar devices, API token use, session anomalies, and administrator activity outside approved windows.
· Build or validate approved-change lookups for network maintenance, device onboarding, firewall policy updates, route changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, security testing, and incident response.
· Use scheduled intermediate searches, summary indexes, or accelerated datasets when raw upstream and downstream correlation is too expensive.
· Use bounded correlation windows for downstream changes occurring after suspected UniFi OS activity and separate immediate, moderate, and delayed follow-on windows.
· Avoid broad joins, unbounded subsearches, repeated mvexpand, broad raw-event appends, and high-cardinality raw exclusion lists.
· Use lookup-output flags for upstream UniFi OS activity, downstream configuration change, high-risk change type, administrator-risk context, approved change context, and incident-response exception context.
· Validate false-positive baselines for frequent network maintenance, firewall policy changes, VPN changes, DNS changes, wireless changes, device onboarding, storage changes, vendor support, security testing, and incident-response workflows.
· Do not enable alert mode until downstream inventory, configuration telemetry, administrator context, change-record quality, summary-index quality, false-positive rate, query performance, SOC triage workflow, enrichment availability, exception handling, and incident-response escalation paths are validated.
DRI Assessment
DRI
8.2 / 10
· The rule is behaviorally anchored to UniFi OS exploit-path activity followed by downstream configuration change rather than static CVE identifiers, exploit strings, proof-of-concept names, scanner labels, file artifacts, IP addresses, or known infrastructure.
· The rule remains useful if an adversary changes source infrastructure, request timing, administrator account, command syntax, outbound destination, downstream target order, or configuration-change sequence.
· The score is supported by the durability of suspected management-plane compromise followed by gateway, firewall, routing, VPN, DNS, wireless, device-adoption, recorder, storage, or managed-device configuration changes.
· The score is constrained by legitimate network maintenance, broad administrator workflows, incomplete configuration telemetry, weak change records, appliance-only visibility, and incomplete downstream inventory.
· The rule is durable as a downstream impact detector but should not be treated as standalone proof of command execution, root compromise, credential theft, or actor attribution.
TCR Assessment
Operational TCR
7.6 / 10
Full-Telemetry TCR
8.8 / 10
· Operational confidence depends on reliable upstream UniFi OS activity detection, downstream configuration telemetry, administrator context, change-management records, asset inventory, downstream inventory, and Splunk correlation quality.
· Operational confidence is reduced where network teams perform frequent configuration changes, device onboarding is common, administrator sources are broad, or configuration-change records are incomplete.
· Operational confidence is reduced where downstream device inventories, gateway roles, firewall policy ownership, VPN workflows, DNS change records, wireless change records, recorder records, or storage records are poorly documented.
· Full-telemetry confidence improves when Splunk correlates downstream changes with UniFi OS logs, administrator activity logs, endpoint telemetry where available, system logs, firewall logs, DNS logs, NDR telemetry, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support downstream impact triage and escalation rather than standalone confirmation of root compromise or actor attribution.
Limitations
· This rule detects suspicious downstream configuration changes after suspected UniFi OS exploit-path activity, not confirmed exploitation by itself.
· Legitimate network maintenance, device onboarding, firewall policy updates, VPN changes, DNS changes, wireless changes, storage changes, vendor support, security testing, and incident response can produce similar downstream signals.
· Missing downstream configuration telemetry, incomplete administrator context, weak change records, broad administrator source paths, or incomplete asset inventory can reduce confidence.
· The rule may miss activity that does not produce observable downstream changes, uses approved administrators, aligns with normal maintenance windows, or occurs outside configured correlation windows.
· The rule should not be used to infer command execution, root compromise, credential theft, or actor attribution without supporting host, system, administrator, configuration, or incident-response evidence.
· The rule requires local Splunk field mapping, lookup validation, suppression validation, summary-index validation, and query-performance testing before alert promotion.
Detection Query Pattern
Splunk SPL summary-correlation pattern for UniFi OS exploit-path activity followed by downstream configuration change. This pattern assumes scheduled candidate searches populate unifi_upstream_suspicious_activity_summary and unifi_downstream_config_change_summary. Local index, sourcetype, macro, lookup, field-name, timing-window, summary-index, and data-model validation are required before production deployment.
index=summary source=unifi_upstream_suspicious_activity_summary earliest=-ENV_UNIFI_DOWNSTREAM_LOOKBACK latest=now
| eval candidate_type="upstream_unifi_activity", unifi_asset=coalesce(unifi_asset, dest_host, host, dvc, device_name), upstream_time=_time
| lookup unifi_os_assets unifi_asset AS unifi_asset OUTPUT is_unifi_asset, unifi_asset_role
| lookup unifi_approved_admin_sources src_ip AS src_ip OUTPUT is_approved_admin_source, approved_source_type
| lookup source_reputation src_ip AS src_ip OUTPUT source_reputation, source_asn, source_geo, is_hosting_provider, is_residential_proxy, is_suspicious_asn
| where is_unifi_asset="true"
| eval upstream_suspicious=if(is_exploit_path_category="true" OR upstream_event_type IN ("abnormal_management_plane_access","update_endpoint_activity","suspicious_source_to_unifi_management") OR is_approved_admin_source!="true" OR is_hosting_provider="true" OR is_residential_proxy="true" OR is_suspicious_asn="true", 1, 0)
| where upstream_suspicious=1
| fields upstream_time, unifi_asset, unifi_asset_role, src_ip, request_path, exploit_path_category, upstream_event_type, administrator, source_reputation, source_asn, source_geo
| append [
search index=summary source=unifi_downstream_config_change_summary earliest=-ENV_UNIFI_DOWNSTREAM_LOOKBACK latest=now
| eval candidate_type="downstream_config_change", unifi_asset=coalesce(unifi_asset, related_unifi_asset, controller_host, host, dvc, device_name), downstream_change_time=_time
| lookup unifi_os_assets unifi_asset AS unifi_asset OUTPUT is_unifi_asset
| lookup unifi_downstream_inventory target_asset AS target_asset OUTPUT is_downstream_device, downstream_role
| lookup unifi_high_risk_config_changes change_type AS change_type OUTPUT is_high_risk_change, high_risk_change_type
| lookup unifi_change_context target_asset AS target_asset OUTPUT is_approved_change, approved_change_type, change_window
| where is_unifi_asset="true" AND is_downstream_device="true" AND is_high_risk_change="true"
| fields downstream_change_time, unifi_asset, target_asset, administrator, config_object, change_type, high_risk_change_type, downstream_role, is_approved_change, approved_change_type
]
| eventstats min(upstream_time) AS first_upstream_time values(request_path) AS upstream_paths values(exploit_path_category) AS exploit_path_categories values(upstream_event_type) AS upstream_event_types values(src_ip) AS upstream_sources values(source_asn) AS upstream_asns values(source_geo) AS upstream_geos by unifi_asset
| where isnotnull(first_upstream_time) AND isnotnull(downstream_change_time)
| eval time_from_upstream=downstream_change_time-first_upstream_time
| where time_from_upstream>=0 AND time_from_upstream<=ENV_UNIFI_DOWNSTREAM_CHANGE_WINDOW
| where is_approved_change!="true"
| stats values(upstream_event_types) AS upstream_event_types values(upstream_paths) AS upstream_paths values(exploit_path_categories) AS exploit_path_categories values(upstream_sources) AS upstream_sources values(upstream_asns) AS upstream_asns values(upstream_geos) AS upstream_geos values(target_asset) AS target_assets values(downstream_role) AS downstream_roles values(config_object) AS config_objects values(change_type) AS change_types values(high_risk_change_type) AS high_risk_change_types min(first_upstream_time) AS first_upstream_time min(downstream_change_time) AS first_downstream_change_time by unifi_asset
| eval detection_outcome="Suspected UniFi OS exploit-path activity followed by downstream configuration change"
| eval confidence="Medium to High"
| table first_upstream_time, first_downstream_change_time, unifi_asset, upstream_event_types, upstream_paths, exploit_path_categories, upstream_sources, upstream_asns, upstream_geos, target_assets, downstream_roles, config_objects, change_types, high_risk_change_types, detection_outcome, confidence
Elastic
Detection Viability Assessment
Elastic has three rules for this EXP report.
· Elastic is viable for detecting UniFi OS control-plane compromise behavior where UniFi OS management-plane logs, web or reverse-proxy logs, firewall logs, DNS logs, endpoint telemetry where available, administrator activity logs, configuration-change records, asset inventory, and change-management context are normalized into ECS-aligned or locally mapped data streams.
· Elastic is strongest when transforms, enrichment policies, value lists, exception lists, and bounded KQL or EQL logic can correlate suspicious UniFi OS management-plane access, exploit-path request behavior, update-endpoint activity, endpoint behavior where available, outbound communication, administrator-state changes, and downstream configuration activity.
· Elastic can support both detection rules and hunt logic depending on request-path visibility, ECS mapping quality, endpoint telemetry availability, administrator-audit quality, asset inventory, enrichment coverage, transform quality, and exception-list maturity.
· Elastic should not treat exposed management interfaces, scanner output, patch state, isolated denied requests, single web errors, ordinary update checks, or normal administrator access as exploitation evidence by themselves.
· Elastic detections must preserve separate analytic outcomes for exposure, attempted exploitation, suspected management-plane compromise, suspected root-level compromise, unauthorized configuration change, downstream network-control impact, and confirmed post-exploitation activity.
· Elastic rules should use ECS-compatible field mappings, local field aliases where needed, enrich processors or enrichment policies, transforms for high-volume correlation, value lists for approved sources and assets, exception lists for approved activity, and bounded sequence logic before production alerting.
· Elastic should not infer command execution, sudo-assisted privilege escalation, root compromise, credential theft, data exfiltration, downstream compromise, or actor attribution without supporting host, system, administrator, configuration, or incident-response evidence.
Rule
UniFi OS Management-Plane Exploit-Path Access With Suspicious Source Context
Rule Format
Elastic KQL and EQL detection rule template suitable for ECS-aligned web, reverse-proxy, firewall, secure access, load-balancer, DNS, and network telemetry after data-view validation, local index validation, ECS mapping validation, UniFi OS asset enrichment validation, approved administrator value-list validation, suspicious source enrichment validation, request-path field validation, exception-list validation, timing-window tuning, and environment-specific allowlisting.
Detection Purpose
· Detect abnormal UniFi OS management-plane access involving authentication-validation paths, traversal-style request behavior, update endpoints, unexpected file-access paths, request-normalization mismatch indicators, or access patterns inconsistent with approved administration.
· Identify suspicious source context involving unfamiliar internet sources, newly observed sources, hosting providers, residential proxy ranges, suspicious ASNs, unusual geographies, VPN ingress paths, unmanaged internal hosts, or sources outside approved administrator baselines.
· Prioritize cases where request-path behavior and source-path deviation occur together rather than treating exposure or scanning as compromise evidence.
· Support early escalation when exploit-path request behavior is followed by update-endpoint activity, administrator-state changes, configuration changes, outbound communication, or downstream management activity.
· Preserve separation between suspicious management-plane access and confirmed compromise by requiring supporting UniFi OS, endpoint, system, administrator, configuration, or incident-response evidence before classifying activity as probable compromise.
· This rule does not prove successful command execution, sudo-assisted escalation, root compromise, credential theft, downstream infrastructure compromise, or actor attribution without supporting telemetry and investigation evidence.
Detection Logic
· Search ECS-aligned or locally mapped web, reverse-proxy, firewall, secure access, load-balancer, DNS, or network events from data views containing UniFi OS management-plane ingress telemetry.
· Match locally maintained exploit-path categories for authentication-validation behavior, traversal-style path construction, encoded path variation, update-endpoint access, package-management endpoints, unexpected file-access paths, or request-normalization mismatch indicators.
· Enrich events with UniFi OS asset role, management-interface exposure context, approved administrator source status, source reputation, ASN, geolocation, VPN ingress context, newly observed source context, and approved change context.
· Increase confidence when repeated request attempts, path variations, unusual request ordering, HTTP 5xx patterns, abnormal response sizes, redirect anomalies, or abnormal status-code sequences occur within a bounded window.
· Increase confidence when suspicious management-plane access is followed by update-endpoint activity, administrator-session anomalies, API token activity, administrator-account changes, backup export activity, device-adoption activity, configuration changes, outbound communication, or downstream management activity.
· Reduce severity when activity aligns with approved administration, vulnerability scanning, exposure assessment, monitoring, security testing, vendor support, incident response, or documented maintenance.
· Do not classify vulnerable-state findings, exposed interfaces, scanner labels, isolated denied requests, ordinary login failures, or single web errors as exploitation evidence by themselves.
· Do not treat network-visible exploit-path behavior as proof of command execution or root compromise without supporting host, administrator, configuration, or incident-response evidence.
Required Telemetry
· ECS-aligned or locally mapped web telemetry.
· Reverse-proxy telemetry where available.
· Firewall telemetry.
· Secure access telemetry where available.
· Load-balancer telemetry where available.
· DNS telemetry where available.
· Network telemetry where available.
· source.ip.
· destination.ip.
· destination.domain or destination.address where available.
· host.name or observer.hostname.
· url.path where available.
· url.original where available.
· http.request.method where available.
· http.response.status_code where available.
· http.response.bytes where available.
· user_agent.original where available.
· event.action.
· event.category.
· event.dataset.
· event.outcome where available.
· event.created or @timestamp.
· UniFi OS asset enrichment.
· UniFi OS management-interface enrichment.
· Approved administrator source value list.
· VPN administration range value list.
· Management network value list.
· Jump-host and privileged access workstation value list.
· Source-reputation enrichment.
· ASN enrichment.
· Geolocation enrichment.
· Newly observed source enrichment.
· Approved change exception list.
· Approved scanning and security-testing exception list.
· Incident-response exception list.
Engineering Implementation Instructions
· Validate Elastic data views, indices, data streams, ECS mappings, local field aliases, ingest pipelines, event timestamp consistency, request-path availability, response-code availability, source-IP normalization, destination-host normalization, and asset identifiers before deployment.
· Build or validate a UniFi OS asset enrichment policy covering UniFi OS Server deployments, consoles, cloud gateways, dream machines, cloud keys, gateways, recorders, storage appliances, controller hosts, exposed management interfaces, and management-plane IP addresses.
· Build or validate approved administrator value lists covering administrator IPs, VPN ranges, jump hosts, privileged access workstations, management networks, monitoring systems, vendor-support paths, vulnerability management systems, security-testing systems, and incident-response systems.
· Build or validate exploit-path value lists or enrichment policies mapping local request paths, normalized paths, raw paths, web classifications, and reverse-proxy classifications to authentication-validation paths, traversal-style paths, encoded path variations, update endpoints, package-management endpoints, unexpected file-access paths, and request-normalization mismatch indicators.
· Build or validate enrichment for source reputation, ASN, geolocation, newly observed source context, approved change windows, approved scanning, approved maintenance, approved vendor support, and incident-response exceptions.
· Use transforms or precomputed correlation indices for high-volume web, firewall, reverse-proxy, DNS, and network telemetry where raw EQL correlation would create unacceptable search cost.
· Use bounded time windows for request bursts, path variation, response anomalies, and source-baseline deviation.
· Use moderate follow-on windows for administrator-state changes, configuration changes, outbound communication, backup export activity, device-adoption activity, or downstream management activity.
· Avoid broad cross-index EQL sequences over high-volume raw datasets unless a transform, event categorization, or pre-filtered candidate index constrains the search.
· Use exception lists for approved administrators, approved scanners, approved security testing, approved vendor support, approved maintenance, and incident-response activity.
· Validate false-positive baselines for vulnerability scanning, exposure assessment, administrator troubleshooting, vendor support, security testing, monitoring, firmware updates, package operations, and incident-response workflows.
· Do not enable alert mode until field coverage, enrichment quality, transform quality, exception-list quality, query performance, alert volume, SOC triage fields, and incident-response escalation paths are validated.
DRI Assessment
DRI
8.5 / 10
· The rule is behaviorally anchored to UniFi OS management-plane exploit-path access, suspicious source context, request-path anomaly, and follow-on control-plane activity rather than static CVE identifiers, proof-of-concept names, scanner labels, fixed user agents, IP addresses, hashes, or actor infrastructure.
· The rule remains useful if an adversary changes request pacing, user agent, source infrastructure, path encoding, request ordering, or post-access timing.
· The score is supported by durable management-plane access anomalies, source-path deviation, request-normalization mismatch indicators, update-endpoint interaction, response anomalies, and follow-on correlation.
· The score is constrained by missing request paths, reverse-proxy normalization, incomplete source baselines, high internet scanning volume, weak asset enrichment, and incomplete change-management data.
· The rule is durable as an early exploit-path detector but should not be treated as standalone proof of command execution, root compromise, or actor attribution.
TCR Assessment
Operational TCR
7.7 / 10
Full-Telemetry TCR
8.6 / 10
· Operational confidence depends on reliable request-path telemetry, UniFi OS asset enrichment, approved administrator value-list quality, source enrichment, response-code visibility, ECS mapping quality, and exception-list maturity.
· Operational confidence is reduced where reverse proxies strip useful request details, exposed management interfaces receive heavy scanning, approved administrator paths are broad, or source reputation enrichment is unavailable.
· Operational confidence is reduced where vulnerability scanning, exposure assessment, monitoring, security testing, vendor support, or incident-response workflows generate similar request behavior.
· Full-telemetry confidence improves when Elastic correlates suspicious access with UniFi OS logs, administrator audit logs, update-service logs, endpoint telemetry where available, configuration-change records, DNS telemetry, network telemetry, change-management records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support escalation and scoping rather than standalone confirmation of exploit success or root compromise.
Limitations
· This rule detects suspicious UniFi OS management-plane access and exploit-path request behavior, not confirmed exploitation by itself.
· Missing raw request paths, normalized paths, response status, response size, user agent, source enrichment, or asset enrichment can reduce confidence.
· Internet scanning, vulnerability assessment, penetration testing, monitoring, vendor support, administrator troubleshooting, and incident-response activity may produce similar management-plane request patterns.
· The rule may miss exploitation that originates from approved administrator sources, uses expected management paths, blends into normal access patterns, or occurs outside configured timing windows.
· The rule should not be used to infer command execution, root compromise, data exfiltration, or actor attribution without supporting evidence.
· The rule requires local Elastic data-view validation, ECS validation, enrichment validation, exception-list validation, transform validation, and query-performance testing before alert promotion.
Detection Query Pattern
Elastic KQL and EQL query pattern for UniFi OS management-plane exploit-path access with suspicious source context. Configure the Elastic rule data view to include ECS-aligned UniFi OS management ingress, web, reverse-proxy, firewall, secure-access, load-balancer, DNS, and network telemetry. Local ECS field, value-list, enrichment-policy, exception-list, threshold, transform, and timing-window validation are required before production deployment.
event.dataset : (
"nginx.access" or
"apache.access" or
"proxy.access" or
"firewall.traffic" or
"network.traffic" or
"secure_access.activity" or
"load_balancer.access"
)
and labels.is_unifi_asset : true
and (
labels.is_unifi_exploit_path_category : true or
labels.unifi_request_category : (
"authentication_validation_path" or
"traversal_style_path" or
"encoded_path_variation" or
"unexpected_file_access_path" or
"update_endpoint_access" or
"package_management_endpoint" or
"request_normalization_mismatch"
)
)
and not labels.is_approved_admin_source : true
and (
labels.is_hosting_provider : true or
labels.is_residential_proxy : true or
labels.is_suspicious_asn : true or
labels.source_reputation : ("low" or "unknown") or
labels.source_not_in_unifi_admin_baseline : true
)
and not labels.is_approved_change : true
and not labels.is_security_testing : true
sequence by source.ip, destination.ip with maxspan=ENV_UNIFI_MANAGEMENT_ACCESS_WINDOW
[network where labels.is_unifi_asset == true and labels.is_unifi_exploit_path_category == true and labels.is_approved_admin_source != true]
[network where labels.is_unifi_asset == true and (
http.response.status_code >= 500 or
http.response.status_code in (401, 403, 404) or
labels.response_anomaly == true or
labels.repeated_path_variation == true
)]
[any where labels.is_unifi_asset == true and (
labels.unifi_followon_activity == true or
labels.update_endpoint_activity == true or
labels.admin_state_anomaly == true or
labels.configuration_change == true or
labels.outbound_followon_activity == true
)]
Rule
UniFi OS Update or Package Activity Followed by Endpoint or Network Follow-On Behavior
Rule Format
Elastic transform-backed EQL and KQL detection rule template suitable for UniFi OS web and application logs, update-service logs where available, package-management logs where available, endpoint telemetry where available, firewall telemetry, DNS telemetry, proxy telemetry, administrator activity logs, configuration-change records, and change-management records after data-view validation, local index validation, ECS mapping validation, field normalization, enrichment validation, transform validation, exception-list validation, timing-window tuning, and environment-specific allowlisting.
Detection Purpose
· Detect UniFi OS update-endpoint, package-management, or application-update activity followed by suspicious endpoint, outbound, administrator, configuration, or downstream management behavior.
· Identify cases where update or package activity becomes higher risk because it is followed by shell execution, interpreter execution, file retrieval, archive extraction, sudo usage, root-context activity, outbound communication, administrator-state change, configuration change, or internal management access.
· Prioritize behavior where update context appears near abnormal management-plane access or suspicious source context.
· Support escalation when update/package activity links to process execution, outbound communication, backup export activity, device-adoption changes, gateway policy changes, VPN changes, DNS changes, wireless changes, or downstream network-control activity.
· Preserve separation between suspicious follow-on behavior and confirmed compromise by requiring supporting host, system, administrator, configuration, or incident-response evidence.
· This rule does not prove successful command injection, root compromise, credential theft, data exfiltration, downstream infrastructure compromise, or actor attribution without supporting evidence.
Detection Logic
· Identify UniFi OS update-endpoint, package-management, application-update, or update-service activity from verified UniFi OS assets and write normalized candidates to a transform-backed candidate data stream.
· Identify endpoint follow-on behavior where available, including shell execution, interpreter execution, package-manager execution, file retrieval, archive extraction, sudo usage, service modification, scheduled job creation, local user change, SSH configuration change, or root-context activity.
· Identify outbound or downstream follow-on behavior involving newly observed, rare, low-reputation, unusual, role-inconsistent, or unexpected destinations, internal scanning, device enumeration, additional management-interface access, or downstream management activity.
· Correlate update candidates with endpoint, outbound, administrator, configuration, and downstream candidates using bounded windows and shared UniFi OS asset identifiers.
· Increase confidence when update or package activity occurs after abnormal source access, traversal-style request behavior, authentication-validation anomalies, response anomalies, or management-plane access from a non-standard source.
· Reduce severity when activity aligns with approved firmware updates, package operations, controller upgrades, backup jobs, vendor support, monitoring, security testing, incident response, or documented maintenance.
· Do not treat ordinary update checks, vendor repository access, expected package operations, backup jobs, service restarts, or routine administrator maintenance as malicious by themselves.
· Do not infer root compromise or data exfiltration unless supporting process, sudo, effective-user, file, network, administrator, configuration, or incident-response evidence exists.
Required Telemetry
· ECS-aligned or locally mapped UniFi OS management-plane logs where available.
· UniFi OS update-service logs where available.
· Package-management logs where available.
· Web or reverse-proxy telemetry.
· Endpoint process telemetry where available.
· Endpoint file telemetry where available.
· Sudo or effective-user telemetry where available.
· Firewall telemetry.
· DNS telemetry.
· Proxy telemetry where available.
· Administrator activity logs where available.
· Configuration-change logs where available.
· Change-management records.
· source.ip.
· destination.ip.
· destination.domain where available.
· host.name.
· url.path where available.
· event.action.
· event.category.
· process.name where available.
· process.parent.name where available.
· process.command_line where available.
· user.name where available.
· Configuration object where locally mapped.
· Change type where locally mapped.
· UniFi OS asset enrichment.
· Approved update value list.
· Approved destination value list.
· Approved administrator value list.
· Approved change exception list.
Engineering Implementation Instructions
· Validate Elastic data views, indices, data streams, ECS mappings, local field aliases, endpoint field mappings, UniFi OS field mappings, network field mappings, administrator-audit field mappings, configuration-change field mappings, and timestamp normalization before deployment.
· Build or validate a UniFi update activity transform or enrichment policy that identifies update endpoints, package-management paths, package repository access, application-update paths, update-service events, and locally observed UniFi OS update workflows.
· Build or validate a host follow-on behavior transform or enrichment policy covering shell execution, interpreter execution, file retrieval, archive extraction, package-manager execution, sudo usage, root-context activity, service modification, scheduled job creation, local user changes, SSH configuration changes, and outbound process-network activity.
· Build or validate an outbound-risk enrichment policy covering newly observed external destinations, rare domains, rare IP addresses, low-reputation destinations, unexpected ASNs, unusual geographies, tunnel-like traffic, unusual package repositories, and destinations inconsistent with the deployed UniFi OS role.
· Build or validate a configuration follow-on transform or enrichment policy covering administrator changes, API token activity, backup exports, device adoption, gateway policy changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, and managed-device configuration changes.
· Use transform-backed candidate data streams for high-volume endpoint, web, firewall, DNS, proxy, and network telemetry before running production EQL sequence rules.
· Use bounded windows between update candidates and follow-on candidates instead of broad raw cross-index EQL over high-volume datasets.
· Prefer transforms, enrichment policies, runtime fields with caution, and scheduled detection dependencies over expensive ad hoc cross-index correlation.
· Avoid broad raw cross-index sequences, expensive wildcard-heavy KQL, unbounded event windows, and field comparisons that are not supported by the deployed Elastic rule type.
· Use exception lists for approved update windows, approved package operations, approved vendor destinations, approved monitoring destinations, approved backup destinations, approved administrator sources, approved security testing, and approved incident-response activity.
· Validate false-positive baselines for firmware updates, package operations, controller upgrades, backup jobs, service restarts, monitoring traffic, vendor support, vulnerability management, security testing, and incident-response workflows.
· Do not enable alert mode until endpoint coverage, update-path quality, outbound baseline quality, administrator-context quality, configuration telemetry, transform quality, query performance, false-positive rate, exception behavior, SOC triage workflow, and incident-response escalation requirements are validated.
DRI Assessment
DRI
8.2 / 10
· The rule is behaviorally anchored to UniFi OS update or package activity followed by endpoint, outbound, administrator, configuration, or downstream behavior rather than static CVE identifiers, exploit strings, proof-of-concept names, hashes, IP addresses, user agents, or known infrastructure.
· The rule remains useful if an adversary changes command syntax, file names, outbound destinations, tool names, staging paths, timing, or downstream target order.
· The score is supported by durable update-path interaction followed by child-process behavior, file retrieval, archive extraction, sudo activity, outbound communication, administrator-state change, configuration changes, or downstream management activity.
· The score is constrained by legitimate update behavior, weak update baselines, incomplete endpoint telemetry, missing package logs, noisy outbound traffic, incomplete administrator logs, incomplete configuration-change records, and transform quality.
· The rule is durable as a cross-telemetry follow-on detector but should not be treated as standalone proof of command injection, root compromise, data exfiltration, or actor attribution.
TCR Assessment
Operational TCR
7.4 / 10
Full-Telemetry TCR
8.7 / 10
· Operational confidence depends on UniFi OS update-path visibility, endpoint telemetry availability, process-lineage quality, command-line visibility, outbound telemetry, administrator logs, configuration telemetry, transform quality, and change-management integration.
· Operational confidence is reduced where update behavior is poorly baselined, package logs are unavailable, endpoint visibility is absent, or approved update destinations are not documented.
· Operational confidence is reduced where monitoring tools, backup workflows, vendor services, vulnerability management, security testing, or incident response produce similar follow-on behavior.
· Full-telemetry confidence improves when Elastic correlates UniFi OS logs, endpoint process and file telemetry, sudo logs, firewall logs, DNS logs, proxy logs, administrator activity, configuration-change records, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support escalation and scoping rather than standalone confirmation of exploit success, root compromise, or data exfiltration.
Limitations
· This rule detects suspicious follow-on behavior after UniFi OS update or package activity, not confirmed exploitation by itself.
· Endpoint-specific portions apply only where process, command-line, sudo, file, or service telemetry exists.
· Approved vendor updates, monitoring tools, backup workflows, administrator actions, vulnerability management, security testing, incident response, and remote-management activity can produce similar follow-on patterns.
· Missing endpoint telemetry, DNS telemetry, proxy telemetry, destination reputation, administrator logs, configuration records, source baselines, or change records can reduce confidence.
· The rule may miss activity that uses approved destinations, expected update workflows, approved parent-child process patterns, or delayed follow-on activity outside configured correlation windows.
· The rule should not be used for actor attribution without incident-specific intelligence, validated behavioral correlation, or confirmed victim-environment evidence.
Detection Query Pattern
Elastic transform-backed KQL and EQL pattern for UniFi OS update or package activity followed by endpoint or network follow-on behavior. Configure Elastic rule data views to include transform-backed UniFi update, endpoint-follow-on, network-follow-on, and configuration-follow-on candidate data streams. Local ECS field, value-list, enrichment-policy, exception-list, transform, threshold, and timing-window validation are required before production deployment.
labels.is_unifi_asset : true
and (
labels.unifi_update_activity : true or
labels.unifi_update_activity_type : (
"update_endpoint_access" or
"package_management_endpoint" or
"package_repository_access" or
"application_update_path" or
"update_service_activity"
)
)
and not labels.is_approved_change : true
labels.is_unifi_asset : true
and (
labels.endpoint_followon_behavior : true or
labels.network_followon_behavior : true or
labels.config_followon_behavior : true or
process.name : ("sh" or "bash" or "python" or "python3" or "curl" or "wget" or "tar" or "unzip" or "dpkg" or "apt" or "apt-get" or "systemctl" or "service" or "sudo") or
labels.rare_outbound_destination : true or
labels.downstream_management_activity : true
)
and not labels.is_approved_change : true
sequence by labels.unifi_asset_id with maxspan=ENV_UNIFI_UPDATE_FOLLOWON_WINDOW
[any where labels.is_unifi_asset == true and labels.unifi_update_activity == true and labels.is_approved_change != true]
[any where labels.is_unifi_asset == true and (
labels.endpoint_followon_behavior == true or
labels.network_followon_behavior == true or
labels.config_followon_behavior == true or
process.name in ("sh", "bash", "python", "python3", "curl", "wget", "tar", "unzip", "dpkg", "apt", "apt-get", "systemctl", "service", "sudo") or
labels.rare_outbound_destination == true or
labels.downstream_management_activity == true
)]
Rule
UniFi OS Exploit-Path Activity Followed by Downstream Configuration Change
Rule Format
Elastic transform-backed EQL and KQL detection rule template suitable for UniFi OS management-plane telemetry, web or reverse-proxy logs, firewall telemetry, administrator activity logs, configuration-change records, downstream device logs, DNS telemetry, endpoint telemetry where available, and change-management records after data-view validation, local index validation, ECS mapping validation, field normalization, configuration-event mapping, administrator-context mapping, enrichment validation, transform validation, exception-list validation, timing-window tuning, and environment-specific allowlisting.
Detection Purpose
· Detect suspected UniFi OS exploit-path activity followed by downstream configuration changes affecting gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless configuration, device adoption, recorder behavior, storage access, or managed-device trust.
· Identify cases where UniFi OS management-plane compromise may create operational risk through network-control changes, access-path expansion, segmentation changes, remote-access modification, traffic-handling changes, or device-trust manipulation.
· Prioritize downstream changes that occur near abnormal UniFi OS management-plane access, suspicious source context, update-endpoint activity, administrator-state anomalies, outbound communication, or endpoint evidence where available.
· Support escalation when downstream changes are not explained by approved change records, known administrators, expected maintenance windows, device onboarding, vendor support, security testing, or incident response.
· Preserve separation between suspicious downstream changes and confirmed compromise by requiring linkage to UniFi OS exploit-path activity, administrator anomalies, configuration evidence, or incident-response validation.
· This rule does not prove command execution, root compromise, credential theft, data exfiltration, downstream compromise, or actor attribution without supporting host, administrator, system, configuration, or incident-response evidence.
Detection Logic
· Identify abnormal UniFi OS management-plane access, exploit-path request behavior, update-endpoint activity, suspicious source context, or related endpoint/network follow-on behavior involving verified UniFi OS assets and write normalized upstream candidates to a transform-backed data stream.
· Identify downstream configuration changes affecting gateway policy, firewall rules, routing, VPN access, DNS settings, wireless settings, device adoption, recorder behavior, storage access, or managed-device trust and write normalized downstream candidates to a transform-backed data stream.
· Prioritize changes involving remote-access expansion, firewall weakening, new inbound exposure, segmentation changes, route changes, DNS forwarding changes, VPN access changes, wireless security changes, unexpected device adoption, backup export behavior, or management-access expansion.
· Correlate upstream UniFi OS candidates with downstream configuration candidates using bounded windows, shared UniFi OS asset identifiers, related controller identifiers, administrator context, and change-window context.
· Increase confidence when the downstream change is performed by a newly created administrator, rarely used administrator, unfamiliar source, unusual geography, suspicious ASN, API token, or administrative session created near suspected exploit-path activity.
· Increase confidence when downstream changes are followed by unusual outbound communication, internal scanning, additional management-interface access, high-value system access, monitoring disruption, logging gaps, or defensive visibility reduction.
· Reduce severity when downstream changes align with approved network maintenance, device replacement, site onboarding, firewall policy updates, VPN changes, DNS changes, wireless changes, vendor support, security testing, incident response, or documented change-control activity.
· Do not classify downstream network-control changes as UniFi OS compromise without upstream UniFi OS exploit-path activity, administrator-state anomaly, suspicious source context, or incident-response validation.
· Do not treat legitimate network maintenance or expected device-adoption workflows as compromise indicators solely because UniFi OS is vulnerable or exposed.
Required Telemetry
· ECS-aligned or locally mapped UniFi OS management-plane telemetry where available.
· Web telemetry where available.
· Reverse-proxy telemetry where available.
· Firewall telemetry.
· Administrator activity logs where available.
· Configuration-change telemetry where available.
· Downstream network-device logs where available.
· DNS telemetry where available.
· Endpoint telemetry where available.
· Change-management records.
· source.ip.
· destination.ip.
· destination.address or destination.domain where available.
· host.name or observer.hostname.
· url.path where available.
· event.action.
· event.category.
· event.dataset.
· user.name where available.
· session.id where available.
· Configuration object where locally mapped.
· Configuration action where locally mapped.
· Change type where locally mapped.
· Device identifier where locally mapped.
· Device role where locally mapped.
· Network segment where locally mapped.
· UniFi OS asset enrichment.
· Downstream device inventory enrichment.
· Approved administrator value list.
· Approved change exception list.
· High-risk change enrichment.
· Incident-response exception list.
Engineering Implementation Instructions
· Validate Elastic data views, indices, data streams, ECS mappings, local field aliases, timestamp consistency, configuration-event parsing, administrator-context parsing, downstream device identifiers, and change-record identifiers before deployment.
· Build or validate an upstream UniFi suspicious activity transform that identifies abnormal management-plane access, exploit-path request categories, update-endpoint activity, suspicious source context, response anomalies, endpoint follow-on behavior where available, and outbound follow-on behavior.
· Build or validate a downstream configuration-change transform covering gateway policy changes, firewall rule changes, route changes, VPN changes, DNS changes, wireless changes, device-adoption changes, recorder changes, storage changes, and managed-device configuration changes.
· Build or validate high-risk configuration-change enrichment for remote-access expansion, firewall weakening, new inbound exposure, segmentation change, default route change, DNS forwarding change, VPN access change, wireless security weakening, unexpected device adoption, backup export, and management-access expansion.
· Build or validate administrator-risk enrichment for newly created administrators, rarely used administrators, unusual source geographies, suspicious ASNs, unfamiliar devices, API token use, session anomalies, and administrator activity outside approved windows.
· Build or validate exception lists for network maintenance, device onboarding, firewall policy updates, route changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, security testing, and incident response.
· Use transform-backed candidate data streams when raw upstream and downstream correlation is too expensive.
· Use bounded correlation windows for downstream changes occurring after suspected UniFi OS activity and separate immediate, moderate, and delayed follow-on windows.
· Avoid broad raw cross-index EQL sequences, expensive wildcard-heavy KQL, unbounded event windows, and unsupported field-to-field comparisons for the deployed Elastic rule type.
· Use enrich processors, transforms, value lists, and exception lists for upstream UniFi OS activity, downstream configuration change, high-risk change type, administrator-risk context, approved change context, and incident-response exception context.
· Validate false-positive baselines for frequent network maintenance, firewall policy changes, VPN changes, DNS changes, wireless changes, device onboarding, storage changes, vendor support, security testing, and incident-response workflows.
· Do not enable alert mode until downstream inventory, configuration telemetry, administrator context, change-record quality, transform quality, false-positive rate, query performance, SOC triage workflow, enrichment availability, exception handling, and incident-response escalation paths are validated.
DRI Assessment
DRI
8.1 / 10
· The rule is behaviorally anchored to UniFi OS exploit-path activity followed by downstream configuration change rather than static CVE identifiers, exploit strings, proof-of-concept names, scanner labels, file artifacts, IP addresses, or known infrastructure.
· The rule remains useful if an adversary changes source infrastructure, request timing, administrator account, command syntax, outbound destination, downstream target order, or configuration-change sequence.
· The score is supported by the durability of suspected management-plane compromise followed by gateway, firewall, routing, VPN, DNS, wireless, device-adoption, recorder, storage, or managed-device configuration changes.
· The score is constrained by legitimate network maintenance, broad administrator workflows, incomplete configuration telemetry, weak change records, appliance-only visibility, incomplete downstream inventory, and transform quality.
· The rule is durable as a downstream impact detector but should not be treated as standalone proof of command execution, root compromise, credential theft, or actor attribution.
TCR Assessment
Operational TCR
7.5 / 10
Full-Telemetry TCR
8.7 / 10
· Operational confidence depends on reliable upstream UniFi OS activity detection, downstream configuration telemetry, administrator context, change-management records, asset inventory, downstream inventory, transform quality, and Elastic correlation quality.
· Operational confidence is reduced where network teams perform frequent configuration changes, device onboarding is common, administrator sources are broad, or configuration-change records are incomplete.
· Operational confidence is reduced where downstream device inventories, gateway roles, firewall policy ownership, VPN workflows, DNS change records, wireless change records, recorder records, or storage records are poorly documented.
· Full-telemetry confidence improves when Elastic correlates downstream changes with UniFi OS logs, administrator activity logs, endpoint telemetry where available, system logs, firewall logs, DNS logs, proxy logs, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support downstream impact triage and escalation rather than standalone confirmation of root compromise or actor attribution.
Limitations
· This rule detects suspicious downstream configuration changes after suspected UniFi OS exploit-path activity, not confirmed exploitation by itself.
· Legitimate network maintenance, device onboarding, firewall policy updates, VPN changes, DNS changes, wireless changes, storage changes, vendor support, security testing, and incident response can produce similar downstream signals.
· Missing downstream configuration telemetry, incomplete administrator context, weak change records, broad administrator source paths, or incomplete asset inventory can reduce confidence.
· The rule may miss activity that does not produce observable downstream changes, uses approved administrators, aligns with normal maintenance windows, or occurs outside configured correlation windows.
· The rule should not be used to infer command execution, root compromise, credential theft, or actor attribution without supporting host, system, administrator, configuration, or incident-response evidence.
· The rule requires local Elastic data-view validation, ECS validation, enrichment validation, exception-list validation, transform validation, and query-performance testing before alert promotion.
Detection Query Pattern
Elastic transform-backed KQL and EQL pattern for UniFi OS exploit-path activity followed by downstream configuration change. Configure Elastic rule data views to include transform-backed upstream suspicious activity and downstream configuration-change candidate data streams. Local ECS field, value-list, enrichment-policy, exception-list, transform, threshold, and timing-window validation are required before production deployment.
labels.is_unifi_asset : true
and (
labels.is_unifi_exploit_path_category : true or
labels.upstream_event_type : (
"abnormal_management_plane_access" or
"update_endpoint_activity" or
"suspicious_source_to_unifi_management"
) or
labels.upstream_suspicious : true
)
and not labels.is_approved_change : true
labels.is_unifi_asset : true
and labels.is_downstream_device : true
and labels.is_high_risk_change : true
and not labels.is_approved_change : true
sequence by labels.unifi_asset_id with maxspan=ENV_UNIFI_DOWNSTREAM_CHANGE_WINDOW
[any where labels.is_unifi_asset == true and (
labels.is_unifi_exploit_path_category == true or
labels.upstream_event_type in ("abnormal_management_plane_access", "update_endpoint_activity", "suspicious_source_to_unifi_management") or
labels.upstream_suspicious == true
)]
[any where labels.is_unifi_asset == true and labels.is_downstream_device == true and labels.is_high_risk_change == true and labels.is_approved_change != true]
QRadar
Detection Viability Assessment
QRadar has three rules for this EXP report.
· QRadar is viable for detecting UniFi OS control-plane compromise behavior where UniFi OS management-plane logs, web or reverse-proxy logs, firewall logs, DNS logs, endpoint telemetry where available, administrator activity logs, downstream configuration-change logs, asset inventory, and change-management context are parsed into QRadar events and enriched through reference sets, reference maps, building blocks, and CRE rules.
· QRadar is strongest when DSM parsing and custom properties identify UniFi OS assets, management interfaces, request paths, source context, update-endpoint activity, administrator activity, endpoint follow-on behavior where available, outbound communication, and downstream configuration changes.
· QRadar should use building blocks to separate UniFi OS asset identification, suspicious source context, exploit-path request behavior, update activity, endpoint follow-on behavior, downstream configuration change, approved maintenance, approved security testing, and incident-response context before offense escalation.
· QRadar can support offense-driven triage when multiple weak signals combine into a higher-confidence UniFi OS management-plane compromise candidate.
· QRadar should not treat exposed management interfaces, scanner output, patch state, isolated denied requests, single web errors, ordinary update checks, or normal administrator access as exploitation evidence by themselves.
· QRadar should not infer command execution, sudo-assisted privilege escalation, root compromise, credential theft, data exfiltration, downstream compromise, or actor attribution without supporting host, system, administrator, configuration, or incident-response evidence.
· QRadar AQL should be used as bounded supporting hunt, validation, and retrospective review logic rather than the primary production correlation method when CRE rules, building blocks, reference sets, reference maps, and offense correlation can express the detection more efficiently.
Rule
UniFi OS Management-Plane Exploit-Path Access With Suspicious Source Context
Rule Format
QRadar CRE rule and building-block correlation template suitable for DSM-parsed web, reverse-proxy, firewall, secure access, load-balancer, DNS, and network telemetry after log-source validation, DSM parsing validation, custom-property validation, UniFi OS asset reference-set validation, approved administrator reference-set validation, suspicious source enrichment validation, exploit-path reference-map validation, offense rule tuning, and environment-specific allowlisting.
Detection Purpose
· Detect abnormal UniFi OS management-plane access involving authentication-validation paths, traversal-style request behavior, update endpoints, unexpected file-access paths, request-normalization mismatch indicators, or access patterns inconsistent with approved administration.
· Identify suspicious source context involving unfamiliar internet sources, newly observed sources, hosting providers, residential proxy ranges, suspicious ASNs, unusual geographies, VPN ingress paths, unmanaged internal hosts, or sources outside approved administrator baselines.
· Prioritize cases where exploit-path request behavior and source-path deviation occur together rather than treating exposure or scanning as compromise evidence.
· Support QRadar offense creation when suspicious management-plane access is followed by update-endpoint activity, administrator-state changes, configuration changes, outbound communication, or downstream management activity.
· Preserve separation between suspicious management-plane access and confirmed compromise by requiring supporting UniFi OS, endpoint, system, administrator, configuration, or incident-response evidence before classifying activity as probable compromise.
· This rule does not prove successful command execution, sudo-assisted escalation, root compromise, credential theft, downstream infrastructure compromise, or actor attribution without supporting telemetry and investigation evidence.
Detection Logic
· Use QRadar building blocks to identify verified UniFi OS assets and management interfaces from destination IP, destination hostname, log source, asset profile, or local asset reference sets.
· Use DSM-parsed custom properties to identify request path, normalized path where available, HTTP method, response status, response size, user agent, source IP, destination IP, destination hostname, and destination interface.
· Match request paths or locally classified request categories against reference sets or reference maps for authentication-validation behavior, traversal-style path construction, encoded path variation, update-endpoint access, package-management endpoints, unexpected file-access paths, or request-normalization mismatch indicators.
· Enrich source context using reference sets, reference maps, threat intelligence enrichment, ASN enrichment, geolocation enrichment, approved administrator references, VPN administration ranges, management network references, jump-host references, privileged access workstation references, and newly observed source context where available.
· Increase offense relevance when repeated request attempts, path variations, unusual request ordering, HTTP 5xx patterns, abnormal response sizes, redirect anomalies, or abnormal status-code sequences occur within a bounded CRE window.
· Increase offense relevance when suspicious management-plane access is followed by update-endpoint activity, administrator-session anomalies, API token activity, administrator-account changes, backup export activity, device-adoption activity, configuration changes, outbound communication, or downstream management activity.
· Suppress or reduce severity when activity aligns with approved administration, vulnerability scanning, exposure assessment, monitoring, security testing, vendor support, incident response, or documented maintenance.
· Do not generate a high-confidence offense from vulnerable-state findings, exposed interfaces, scanner labels, isolated denied requests, ordinary login failures, or single web errors by themselves.
· Do not treat network-visible exploit-path behavior as proof of command execution or root compromise without supporting host, administrator, configuration, or incident-response evidence.
Required Telemetry
· QRadar events from web telemetry.
· Reverse-proxy telemetry where available.
· Firewall telemetry.
· Secure access telemetry where available.
· Load-balancer telemetry where available.
· DNS telemetry where available.
· Network telemetry where available.
· Source IP.
· Destination IP.
· Destination hostname.
· Destination interface where available.
· Destination port.
· Protocol.
· HTTP method where available.
· Request path custom property where available.
· Normalized request path custom property where available.
· Raw request path custom property where available.
· Response status custom property where available.
· Response size custom property where available.
· User agent custom property where available.
· Event timestamp.
· UniFi OS asset reference set.
· UniFi OS management-interface reference set.
· Approved administrator source reference set.
· VPN administration range reference set.
· Management network reference set.
· Jump-host reference set.
· Privileged access workstation reference set.
· Exploit-path category reference map.
· Source-reputation enrichment.
· ASN enrichment.
· Geolocation enrichment.
· Newly observed source context.
· Approved change reference map.
· Approved scanning and security-testing reference sets.
· Incident-response exception reference set.
Engineering Implementation Instructions
· Validate QRadar log sources, DSM parsing, custom properties, event categories, QIDs, timestamps, source IP fields, destination IP fields, destination hostname fields, request-path fields, response-code fields, and asset identifiers before deployment.
· Build a UniFi OS asset reference set covering UniFi OS Server deployments, consoles, cloud gateways, dream machines, cloud keys, gateways, recorders, storage appliances, controller hosts, exposed management interfaces, and management-plane IP addresses.
· Build a UniFi OS management-interface reference set covering externally exposed management interfaces, internal administration interfaces, reverse-proxy destinations, secure access destinations, VPN-accessible management paths, and controller administration paths.
· Build approved administrator reference sets covering administrator IPs, VPN ranges, jump hosts, privileged access workstations, management networks, monitoring systems, vendor-support paths, vulnerability management systems, security-testing systems, and incident-response systems.
· Build exploit-path reference maps that classify request paths, normalized paths, raw paths, web classifications, and reverse-proxy classifications into authentication-validation paths, traversal-style paths, encoded path variations, update endpoints, package-management endpoints, unexpected file-access paths, and request-normalization mismatch indicators.
· Build suspicious source reference sets or enrichment maps for hosting-provider sources, residential proxy ranges, suspicious ASNs, unusual geographies, newly observed internal hosts, unmanaged systems, and sources outside the approved administrator baseline.
· Create building blocks for UniFi OS asset targeting, exploit-path request behavior, suspicious source context, repeated request variation, response anomalies, approved administrator activity, approved scanning, approved security testing, approved maintenance, and incident-response exceptions.
· Configure CRE rule tests to require UniFi OS management targeting, exploit-path request behavior, and suspicious or non-approved source context before offense escalation.
· Use bounded CRE windows for request bursts, path variation, response anomalies, source-baseline deviation, and follow-on activity.
· Use offense relevance and magnitude adjustments for source novelty, suspicious ASN, hosting-provider source, residential-proxy source, exploit-path category, repeated path variation, response anomaly, and follow-on behavior.
· Use QRadar reference sets and building blocks for suppression rather than broad AQL exclusion logic.
· Validate false-positive baselines for vulnerability scanning, exposure assessment, administrator troubleshooting, vendor support, security testing, monitoring, firmware updates, package operations, and incident-response workflows.
· Do not enable offense-generating mode until log-source coverage, custom-property quality, reference-set quality, enrichment reliability, CRE performance, offense volume, suppression logic, SOC triage fields, and escalation paths are validated.
DRI Assessment
DRI
8.4 / 10
· The rule is behaviorally anchored to UniFi OS management-plane exploit-path access, suspicious source context, request-path anomaly, and follow-on control-plane activity rather than static CVE identifiers, proof-of-concept names, scanner labels, fixed user agents, IP addresses, hashes, or actor infrastructure.
· The rule remains useful if an adversary changes request pacing, user agent, source infrastructure, path encoding, request ordering, or post-access timing.
· The score is supported by durable management-plane access anomalies, source-path deviation, request-normalization mismatch indicators, update-endpoint interaction, response anomalies, and follow-on correlation.
· The score is constrained by missing request paths, incomplete DSM parsing, incomplete custom properties, reverse-proxy normalization, weak reference sets, high internet scanning volume, and incomplete change-management data.
· The rule is durable as an early exploit-path detector but should not be treated as standalone proof of command execution, root compromise, or actor attribution.
TCR Assessment
Operational TCR
7.5 / 10
Full-Telemetry TCR
8.5 / 10
· Operational confidence depends on reliable QRadar log-source coverage, DSM parsing quality, custom-property quality, UniFi OS asset reference sets, approved administrator reference sets, source enrichment, response-code visibility, and offense-tuning maturity.
· Operational confidence is reduced where reverse proxies strip useful request details, exposed management interfaces receive heavy scanning, approved administrator paths are broad, or source reputation enrichment is unavailable.
· Operational confidence is reduced where vulnerability scanning, exposure assessment, monitoring, security testing, vendor support, or incident-response workflows generate similar request behavior.
· Full-telemetry confidence improves when QRadar correlates suspicious access with UniFi OS logs, administrator audit logs, update-service logs, endpoint telemetry where available, configuration-change records, DNS telemetry, network telemetry, change-management records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support offense-driven escalation and scoping rather than standalone confirmation of exploit success or root compromise.
Limitations
· This rule detects suspicious UniFi OS management-plane access and exploit-path request behavior, not confirmed exploitation by itself.
· Missing request paths, normalized paths, response status, response size, user agent, source enrichment, or asset enrichment can reduce confidence.
· Internet scanning, vulnerability assessment, penetration testing, monitoring, vendor support, administrator troubleshooting, and incident-response activity may produce similar management-plane request patterns.
· The rule may miss exploitation that originates from approved administrator sources, uses expected management paths, blends into normal access patterns, or occurs outside configured CRE windows.
· The rule should not be used to infer command execution, root compromise, data exfiltration, or actor attribution without supporting evidence.
· The rule requires QRadar log-source validation, DSM validation, custom-property validation, reference-set validation, offense-tuning validation, suppression validation, and CRE performance testing before alert promotion.
Detection Query Pattern
QRadar production CRE logic for UniFi OS management-plane exploit-path access with suspicious source context, followed by bounded supporting AQL hunt logic. The CRE logic is the production detection authority. The AQL block is supporting hunt and validation logic only and requires local log-source, DSM, custom-property, reference-set, and timing-window validation before operational use.
WHEN event matches BB:Device Is UniFi OS Management Interface
AND event matches BB:Request Path Matches UniFi OS Exploit Path Category
AND source IP is NOT contained in REF:Approved UniFi Administrator Sources
AND event matches BB:Suspicious Source Context For UniFi OS Management
AND at least ENV_UNIFI_REQUEST_THRESHOLD events are seen with the same source IP and destination IP in ENV_UNIFI_REQUEST_WINDOW
AND event does NOT match BB:Approved UniFi Maintenance Or Security Testing
THEN create or contribute to offense UniFi OS Management-Plane Exploit-Path Access With Suspicious Source Context.
SELECT
DATEFORMAT(starttime, 'YYYY-MM-dd HH:mm:ss') AS event_time,
sourceip,
destinationip,
destinationport,
UTF8(payload) AS payload_sample,
"Request Path" AS request_path,
"HTTP Status" AS http_status,
"User Agent" AS user_agent,
QIDNAME(qid) AS event_name,
LOGSOURCENAME(logsourceid) AS log_source
FROM events
WHERE
destinationip IN REFERENCESET('REF:UniFi OS Management Interfaces')
AND NOT REFERENCESETCONTAINS('REF:Approved UniFi Administrator Sources', sourceip)
AND (
"UniFi Exploit Path Category" IS NOT NULL
OR "Request Path" ILIKE '%update%'
OR "Request Path" ILIKE '%package%'
OR "Request Path" ILIKE '%auth%'
OR "Request Path" ILIKE '%validate%'
OR "Request Path" ILIKE '%../%'
OR "Request Path" ILIKE '%2e%2e%'
OR "Request Path" ILIKE '%traversal%'
)
AND NOT REFERENCESETCONTAINS('REF:Approved Security Testing Sources', sourceip)
AND NOT REFERENCESETCONTAINS('REF:Approved Vulnerability Scanners', sourceip)
LAST ENV_UNIFI_REQUEST_WINDOW
Rule
UniFi OS Update or Package Activity Followed by Endpoint or Network Follow-On Behavior
Rule Format
QRadar CRE rule and building-block correlation template suitable for UniFi OS web and application logs, update-service logs where available, package-management logs where available, endpoint telemetry where available, firewall telemetry, DNS telemetry, proxy telemetry, administrator activity logs, configuration-change records, and change-management records after log-source validation, DSM parsing validation, custom-property validation, reference-set validation, reference-map validation, offense rule tuning, and environment-specific allowlisting.
Detection Purpose
· Detect UniFi OS update-endpoint, package-management, or application-update activity followed by suspicious endpoint, outbound, administrator, configuration, or downstream management behavior.
· Identify cases where update or package activity becomes higher risk because it is followed by shell execution, interpreter execution, file retrieval, archive extraction, sudo usage, root-context activity, outbound communication, administrator-state change, configuration change, or internal management access.
· Prioritize behavior where update context appears near abnormal management-plane access or suspicious source context.
· Support offense escalation when update or package activity links to process execution, outbound communication, backup export activity, device-adoption changes, gateway policy changes, VPN changes, DNS changes, wireless changes, or downstream network-control activity.
· Preserve separation between suspicious follow-on behavior and confirmed compromise by requiring supporting host, system, administrator, configuration, or incident-response evidence.
· This rule does not prove successful command injection, root compromise, credential theft, data exfiltration, downstream infrastructure compromise, or actor attribution without supporting evidence.
Detection Logic
· Use QRadar building blocks to identify verified UniFi OS assets and update or package activity from UniFi OS management-plane logs, web logs, update-service logs, package-management logs, or locally mapped event categories.
· Identify endpoint follow-on behavior where available, including shell execution, interpreter execution, package-manager execution, file retrieval, archive extraction, sudo usage, service modification, scheduled job creation, local user change, SSH configuration change, or root-context activity.
· Identify outbound or downstream follow-on behavior involving newly observed, rare, low-reputation, unusual, role-inconsistent, or unexpected destinations, internal scanning, device enumeration, additional management-interface access, or downstream management activity.
· Correlate update or package activity with endpoint, outbound, administrator, configuration, and downstream building blocks using bounded CRE windows and shared UniFi OS asset identifiers.
· Increase offense relevance when update or package activity occurs after abnormal source access, traversal-style request behavior, authentication-validation anomalies, response anomalies, or management-plane access from a non-standard source.
· Reduce severity when activity aligns with approved firmware updates, package operations, controller upgrades, backup jobs, vendor support, monitoring, security testing, incident response, or documented maintenance.
· Do not treat ordinary update checks, vendor repository access, expected package operations, backup jobs, service restarts, or routine administrator maintenance as malicious by themselves.
· Do not infer root compromise or data exfiltration unless supporting process, sudo, effective-user, file, network, administrator, configuration, or incident-response evidence exists.
Required Telemetry
· QRadar events from UniFi OS management-plane logs where available.
· UniFi OS update-service logs where available.
· Package-management logs where available.
· Web or reverse-proxy telemetry.
· Endpoint process telemetry where available.
· Endpoint file telemetry where available.
· Sudo or effective-user telemetry where available.
· Firewall telemetry.
· DNS telemetry.
· Proxy telemetry where available.
· Administrator activity logs where available.
· Configuration-change logs where available.
· Change-management records.
· Source IP.
· Destination IP.
· Destination hostname.
· Asset role.
· Request path custom property where available.
· Event timestamp.
· Process name custom property where available.
· Parent process custom property where available.
· Command line custom property where available.
· Process user custom property where available.
· Destination domain custom property where available.
· External destination reputation where available.
· Configuration object custom property where available.
· Change type custom property where available.
· UniFi OS asset reference set.
· Approved update reference map.
· Approved destination reference map.
· Approved administrator reference set.
· Approved change reference map.
Engineering Implementation Instructions
· Validate QRadar log sources, DSM parsing, custom properties, QIDs, event categories, timestamps, endpoint field mappings, UniFi OS field mappings, network field mappings, administrator-audit field mappings, configuration-change field mappings, and asset identifiers before deployment.
· Build update-activity building blocks that identify update endpoints, package-management paths, package repository access, application-update paths, update-service events, and locally observed UniFi OS update workflows.
· Build host-follow-on building blocks covering shell execution, interpreter execution, file retrieval, archive extraction, package-manager execution, sudo usage, root-context activity, service modification, scheduled job creation, local user changes, SSH configuration changes, and outbound process-network activity.
· Build outbound-risk building blocks covering newly observed external destinations, rare domains, rare IP addresses, low-reputation destinations, unexpected ASNs, unusual geographies, tunnel-like traffic, unusual package repositories, and destinations inconsistent with the deployed UniFi OS role.
· Build configuration-follow-on building blocks covering administrator changes, API token activity, backup exports, device adoption, gateway policy changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, and managed-device configuration changes.
· Build approved-activity reference sets and reference maps covering approved update windows, package operations, vendor destinations, monitoring destinations, backup destinations, administrator sources, security testing, and incident-response activity.
· Use CRE rules to correlate update activity with endpoint follow-on, network follow-on, and configuration follow-on building blocks within bounded windows.
· Avoid broad raw AQL joins, unbounded historical searches, and high-cardinality negative matching in production offense rules.
· Use AQL only for supporting hunt, validation, and retrospective review when CRE building blocks and offenses identify candidate assets or time windows.
· Validate false-positive baselines for firmware updates, package operations, controller upgrades, backup jobs, service restarts, monitoring traffic, vendor support, vulnerability management, security testing, and incident-response workflows.
· Do not enable offense-generating mode until endpoint coverage, update-path quality, outbound baseline quality, administrator-context quality, configuration telemetry, reference-set quality, CRE performance, false-positive rate, suppression behavior, SOC triage workflow, and incident-response escalation requirements are validated.
DRI Assessment
DRI
8.1 / 10
· The rule is behaviorally anchored to UniFi OS update or package activity followed by endpoint, outbound, administrator, configuration, or downstream behavior rather than static CVE identifiers, exploit strings, proof-of-concept names, hashes, IP addresses, user agents, or known infrastructure.
· The rule remains useful if an adversary changes command syntax, file names, outbound destinations, tool names, staging paths, timing, or downstream target order.
· The score is supported by durable update-path interaction followed by child-process behavior, file retrieval, archive extraction, sudo activity, outbound communication, administrator-state change, configuration changes, or downstream management activity.
· The score is constrained by legitimate update behavior, weak update baselines, incomplete endpoint telemetry, missing package logs, noisy outbound traffic, incomplete administrator logs, incomplete configuration-change records, and custom-property quality.
· The rule is durable as a cross-telemetry follow-on detector but should not be treated as standalone proof of command injection, root compromise, data exfiltration, or actor attribution.
TCR Assessment
Operational TCR
7.3 / 10
Full-Telemetry TCR
8.5 / 10
· Operational confidence depends on UniFi OS update-path visibility, endpoint telemetry availability, process-lineage quality, command-line visibility, outbound telemetry, administrator logs, configuration telemetry, QRadar custom-property quality, and change-management integration.
· Operational confidence is reduced where update behavior is poorly baselined, package logs are unavailable, endpoint visibility is absent, or approved update destinations are not documented.
· Operational confidence is reduced where monitoring tools, backup workflows, vendor services, vulnerability management, security testing, or incident response produce similar follow-on behavior.
· Full-telemetry confidence improves when QRadar correlates UniFi OS logs, endpoint process and file telemetry, sudo logs, firewall logs, DNS logs, proxy logs, administrator activity, configuration-change records, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support offense escalation and scoping rather than standalone confirmation of exploit success, root compromise, or data exfiltration.
Limitations
· This rule detects suspicious follow-on behavior after UniFi OS update or package activity, not confirmed exploitation by itself.
· Endpoint-specific portions apply only where process, command-line, sudo, file, or service telemetry exists.
· Approved vendor updates, monitoring tools, backup workflows, administrator actions, vulnerability management, security testing, incident response, and remote-management activity can produce similar follow-on patterns.
· Missing endpoint telemetry, DNS telemetry, proxy telemetry, destination reputation, administrator logs, configuration records, source baselines, change records, or custom properties can reduce confidence.
· The rule may miss activity that uses approved destinations, expected update workflows, approved parent-child process patterns, or delayed follow-on activity outside configured CRE windows.
· The rule should not be used for actor attribution without incident-specific intelligence, validated behavioral correlation, or confirmed victim-environment evidence.
Detection Query Pattern
QRadar production CRE logic for UniFi OS update or package activity followed by endpoint or network follow-on behavior, followed by bounded supporting AQL hunt logic. The CRE logic is the production detection authority. The AQL block is supporting hunt and validation logic only and requires local log-source, DSM, custom-property, reference-set, and timing-window validation before operational use.
WHEN event matches BB:Device Is UniFi OS Asset
AND event matches BB:UniFi OS Update Or Package Activity
AND event does NOT match BB:Approved UniFi Update Or Maintenance
AND within ENV_UNIFI_UPDATE_FOLLOWON_WINDOW the same UniFi OS asset matches BB:Suspicious Endpoint Network Or Configuration Follow-On Activity
AND event does NOT match BB:Approved Security Testing Or Incident Response
THEN create or contribute to offense UniFi OS Update Or Package Activity Followed By Suspicious Follow-On Behavior.
SELECT
DATEFORMAT(starttime, 'YYYY-MM-dd HH:mm:ss') AS event_time,
sourceip,
destinationip,
destinationport,
"UniFi Asset ID" AS unifi_asset_id,
"UniFi Update Activity Type" AS update_activity_type,
"Process Name" AS process_name,
"Command Line" AS command_line,
"Destination Domain" AS destination_domain,
QIDNAME(qid) AS event_name,
LOGSOURCENAME(logsourceid) AS log_source
FROM events
WHERE
"UniFi Asset ID" IS NOT NULL
AND (
"UniFi Update Activity Type" IS NOT NULL
OR "Request Path" ILIKE '%update%'
OR "Request Path" ILIKE '%package%'
OR "Request Path" ILIKE '%repository%'
OR "Request Path" ILIKE '%upgrade%'
)
AND NOT (
"Change Context" ILIKE '%approved%'
OR REFERENCESETCONTAINS('REF:Approved Security Testing Sources', sourceip)
)
LAST ENV_UNIFI_UPDATE_FOLLOWON_WINDOW
Rule
UniFi OS Exploit-Path Activity Followed by Downstream Configuration Change
Rule Format
QRadar CRE rule and building-block correlation template suitable for UniFi OS management-plane telemetry, web or reverse-proxy logs, firewall telemetry, administrator activity logs, configuration-change records, downstream device logs, DNS telemetry, endpoint telemetry where available, and change-management records after log-source validation, DSM parsing validation, custom-property validation, configuration-event mapping, administrator-context mapping, reference-set validation, reference-map validation, offense rule tuning, and environment-specific allowlisting.
Detection Purpose
· Detect suspected UniFi OS exploit-path activity followed by downstream configuration changes affecting gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless configuration, device adoption, recorder behavior, storage access, or managed-device trust.
· Identify cases where UniFi OS management-plane compromise may create operational risk through network-control changes, access-path expansion, segmentation changes, remote-access modification, traffic-handling changes, or device-trust manipulation.
· Prioritize downstream changes that occur near abnormal UniFi OS management-plane access, suspicious source context, update-endpoint activity, administrator-state anomalies, outbound communication, or endpoint evidence where available.
· Support offense escalation when downstream changes are not explained by approved change records, known administrators, expected maintenance windows, device onboarding, vendor support, security testing, or incident response.
· Preserve separation between suspicious downstream changes and confirmed compromise by requiring linkage to UniFi OS exploit-path activity, administrator anomalies, configuration evidence, or incident-response validation.
· This rule does not prove command execution, root compromise, credential theft, data exfiltration, downstream compromise, or actor attribution without supporting host, administrator, system, configuration, or incident-response evidence.
Detection Logic
· Use QRadar building blocks to identify abnormal UniFi OS management-plane access, exploit-path request behavior, update-endpoint activity, suspicious source context, or related endpoint/network follow-on behavior involving verified UniFi OS assets.
· Use downstream configuration-change building blocks to identify gateway policy changes, firewall rule changes, routing changes, VPN changes, DNS changes, wireless changes, device-adoption changes, recorder changes, storage changes, or managed-device trust changes.
· Prioritize changes involving remote-access expansion, firewall weakening, new inbound exposure, segmentation changes, route changes, DNS forwarding changes, VPN access changes, wireless security changes, unexpected device adoption, backup export behavior, or management-access expansion.
· Correlate upstream UniFi OS building blocks with downstream configuration-change building blocks using bounded CRE windows, shared UniFi OS asset identifiers, related controller identifiers, administrator context, and change-window context.
· Increase offense relevance when the downstream change is performed by a newly created administrator, rarely used administrator, unfamiliar source, unusual geography, suspicious ASN, API token, or administrative session created near suspected exploit-path activity.
· Increase offense relevance when downstream changes are followed by unusual outbound communication, internal scanning, additional management-interface access, high-value system access, monitoring disruption, logging gaps, or defensive visibility reduction.
· Reduce severity when downstream changes align with approved network maintenance, device replacement, site onboarding, firewall policy updates, VPN changes, DNS changes, wireless changes, vendor support, security testing, incident response, or documented change-control activity.
· Do not classify downstream network-control changes as UniFi OS compromise without upstream UniFi OS exploit-path activity, administrator-state anomaly, suspicious source context, or incident-response validation.
· Do not treat legitimate network maintenance or expected device-adoption workflows as compromise indicators solely because UniFi OS is vulnerable or exposed.
Required Telemetry
· QRadar events from UniFi OS management-plane telemetry where available.
· Web telemetry where available.
· Reverse-proxy telemetry where available.
· Firewall telemetry.
· Administrator activity logs where available.
· Configuration-change telemetry where available.
· Downstream network-device logs where available.
· DNS telemetry where available.
· Endpoint telemetry where available.
· Change-management records.
· Source IP.
· Destination IP.
· Destination hostname.
· Asset role.
· Request path custom property where available.
· Event timestamp.
· Administrator identity custom property where available.
· Session context custom property where available.
· API token context custom property where available.
· Configuration object custom property.
· Configuration action custom property.
· Change type custom property.
· Device identifier custom property.
· Device role custom property.
· Network segment custom property.
· UniFi OS asset reference set.
· Downstream device inventory reference set.
· Approved administrator reference set.
· Approved change reference map.
· High-risk change reference map.
· Incident-response exception reference set.
Engineering Implementation Instructions
· Validate QRadar log sources, DSM parsing, custom properties, event categories, QIDs, timestamps, configuration-event parsing, administrator-context parsing, downstream device identifiers, and change-record identifiers before deployment.
· Build upstream UniFi suspicious activity building blocks that identify abnormal management-plane access, exploit-path request categories, update-endpoint activity, suspicious source context, response anomalies, endpoint follow-on behavior where available, and outbound follow-on behavior.
· Build downstream configuration-change building blocks covering gateway policy changes, firewall rule changes, route changes, VPN changes, DNS changes, wireless changes, device-adoption changes, recorder changes, storage changes, and managed-device configuration changes.
· Build high-risk configuration-change reference maps for remote-access expansion, firewall weakening, new inbound exposure, segmentation change, default route change, DNS forwarding change, VPN access change, wireless security weakening, unexpected device adoption, backup export, and management-access expansion.
· Build administrator-risk reference maps for newly created administrators, rarely used administrators, unusual source geographies, suspicious ASNs, unfamiliar devices, API token use, session anomalies, and administrator activity outside approved windows.
· Build approved-change reference sets and reference maps for network maintenance, device onboarding, firewall policy updates, route changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, security testing, and incident response.
· Use CRE rules to correlate upstream UniFi OS activity with downstream configuration-change building blocks within bounded windows.
· Use offense relevance and magnitude adjustments for high-risk change type, administrator-risk context, abnormal source context, update-endpoint activity, outbound follow-on behavior, missing change record, and impact on remote access, segmentation, firewall policy, VPN access, or managed-device trust.
· Avoid broad raw AQL joins, unbounded historical searches, broad negative matching, and high-cardinality raw exclusions in production offense rules.
· Use AQL only for supporting hunt, validation, and retrospective review when CRE building blocks and offenses identify candidate assets or time windows.
· Validate false-positive baselines for frequent network maintenance, firewall policy changes, VPN changes, DNS changes, wireless changes, device onboarding, storage changes, vendor support, security testing, and incident-response workflows.
· Do not enable offense-generating mode until downstream inventory, configuration telemetry, administrator context, change-record quality, reference-set quality, CRE performance, false-positive rate, query performance, SOC triage workflow, enrichment availability, exception handling, and incident-response escalation paths are validated.
DRI Assessment
DRI
8.0 / 10
· The rule is behaviorally anchored to UniFi OS exploit-path activity followed by downstream configuration change rather than static CVE identifiers, exploit strings, proof-of-concept names, scanner labels, file artifacts, IP addresses, or known infrastructure.
· The rule remains useful if an adversary changes source infrastructure, request timing, administrator account, command syntax, outbound destination, downstream target order, or configuration-change sequence.
· The score is supported by the durability of suspected management-plane compromise followed by gateway, firewall, routing, VPN, DNS, wireless, device-adoption, recorder, storage, or managed-device configuration changes.
· The score is constrained by legitimate network maintenance, broad administrator workflows, incomplete configuration telemetry, weak change records, appliance-only visibility, incomplete downstream inventory, and custom-property quality.
· The rule is durable as a downstream impact detector but should not be treated as standalone proof of command execution, root compromise, credential theft, or actor attribution.
TCR Assessment
Operational TCR
7.4 / 10
Full-Telemetry TCR
8.5 / 10
· Operational confidence depends on reliable upstream UniFi OS activity detection, downstream configuration telemetry, administrator context, change-management records, asset inventory, downstream inventory, QRadar custom-property quality, and offense-rule tuning.
· Operational confidence is reduced where network teams perform frequent configuration changes, device onboarding is common, administrator sources are broad, or configuration-change records are incomplete.
· Operational confidence is reduced where downstream device inventories, gateway roles, firewall policy ownership, VPN workflows, DNS change records, wireless change records, recorder records, or storage records are poorly documented.
· Full-telemetry confidence improves when QRadar correlates downstream changes with UniFi OS logs, administrator activity logs, endpoint telemetry where available, system logs, firewall logs, DNS logs, proxy logs, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support downstream impact triage and offense escalation rather than standalone confirmation of root compromise or actor attribution.
Limitations
· This rule detects suspicious downstream configuration changes after suspected UniFi OS exploit-path activity, not confirmed exploitation by itself.
· Legitimate network maintenance, device onboarding, firewall policy updates, VPN changes, DNS changes, wireless changes, storage changes, vendor support, security testing, and incident response can produce similar downstream signals.
· Missing downstream configuration telemetry, incomplete administrator context, weak change records, broad administrator source paths, incomplete asset inventory, or weak custom-property parsing can reduce confidence.
· The rule may miss activity that does not produce observable downstream changes, uses approved administrators, aligns with normal maintenance windows, or occurs outside configured CRE windows.
· The rule should not be used to infer command execution, root compromise, credential theft, or actor attribution without supporting host, system, administrator, configuration, or incident-response evidence.
· The rule requires QRadar log-source validation, DSM validation, custom-property validation, reference-set validation, offense-tuning validation, suppression validation, and CRE performance testing before alert promotion.
Detection Query Pattern
QRadar production CRE logic for UniFi OS exploit-path activity followed by downstream configuration change, followed by bounded supporting AQL hunt logic. The CRE logic is the production detection authority. The AQL block is supporting hunt and validation logic only and requires local log-source, DSM, custom-property, reference-set, and timing-window validation before operational use.
WHEN event matches BB:Upstream UniFi OS Suspicious Activity
AND within ENV_UNIFI_DOWNSTREAM_CHANGE_WINDOW the same UniFi OS asset, related controller, or related administrator matches BB:Downstream High-Risk Configuration Change
AND downstream change does NOT match BB:Approved Network Maintenance Or Device Onboarding
AND event matches BB:Suspicious UniFi Downstream Change Context
THEN create or contribute to offense UniFi OS Exploit-Path Activity Followed By Downstream Configuration Change.
SELECT
DATEFORMAT(starttime, 'YYYY-MM-dd HH:mm:ss') AS event_time,
sourceip,
destinationip,
"UniFi Asset ID" AS unifi_asset_id,
"Related Controller" AS related_controller,
"Administrator" AS administrator,
"Configuration Object" AS configuration_object,
"Change Type" AS change_type,
"High Risk Change Type" AS high_risk_change_type,
QIDNAME(qid) AS event_name,
LOGSOURCENAME(logsourceid) AS log_source
FROM events
WHERE
"UniFi Asset ID" IS NOT NULL
AND (
"Upstream UniFi Suspicious Activity" = 'true'
OR "Downstream High Risk Configuration Change" = 'true'
)
AND NOT (
"Change Context" ILIKE '%approved%'
OR REFERENCESETCONTAINS('REF:Approved Security Testing Sources', sourceip)
)
LAST ENV_UNIFI_DOWNSTREAM_CHANGE_WINDOW
SIGMA
Detection Viability Assessment
SIGMA has three rules for this EXP report.
· SIGMA is viable for expressing portable event-rule templates for UniFi OS control-plane compromise behavior where web, reverse-proxy, firewall, endpoint, Linux system, administrator activity, and downstream configuration-change telemetry can be mapped into a SIEM or backend detection engine.
· SIGMA is strongest as a portable rule-template layer for suspicious UniFi OS management-plane requests, suspicious source context, update-endpoint activity, service-context process execution, package or update follow-on behavior, and downstream configuration-change signals.
· SIGMA should not be treated as a complete correlation engine for this report because multi-stage timing, asset enrichment, approved-source baselines, downstream configuration correlation, and offense-style logic must be implemented in the target SIEM, SOAR, or detection backend.
· SIGMA rules in this report should be implemented as backend-converted event rules, enrichment-dependent templates, or supporting detections that feed SIEM-native correlation rules.
· SIGMA should not treat exposed management interfaces, scanner output, patch state, isolated denied requests, single web errors, ordinary update checks, or normal administrator access as exploitation evidence by themselves.
· SIGMA should not infer command execution, sudo-assisted privilege escalation, root compromise, credential theft, data exfiltration, downstream compromise, or actor attribution without supporting host, system, administrator, configuration, or incident-response evidence.
· SIGMA detections require local field mapping, backend conversion, local enrichment-field creation, approved-source exception handling, change-management suppression, and SIEM-native correlation before production alerting.
Rule
UniFi OS Management-Plane Exploit-Path Request Event
Rule Format
SIGMA event-rule template for web, reverse-proxy, firewall, secure access, load-balancer, or network telemetry after backend conversion, local field mapping, UniFi OS asset enrichment, request-path mapping, approved administrator exception validation, suspicious source enrichment, and SIEM-native correlation with follow-on behavior.
Detection Purpose
· Detect UniFi OS management-plane request events involving authentication-validation paths, traversal-style path behavior, update endpoints, package-management endpoints, unexpected file-access paths, encoded path variation, or request-normalization mismatch indicators.
· Identify events that should feed SIEM-native correlation with suspicious source context, request bursts, response anomalies, administrator activity, update activity, endpoint behavior, outbound communication, or downstream configuration changes.
· Support early identification of attempted or suspected UniFi OS exploit-path activity without claiming exploitation success from request telemetry alone.
· Preserve separation between suspicious request behavior and confirmed compromise by requiring supporting UniFi OS, endpoint, administrator, configuration, or incident-response evidence before escalation.
· This rule does not prove successful command execution, sudo-assisted escalation, root compromise, credential theft, downstream infrastructure compromise, or actor attribution without supporting telemetry and investigation evidence.
Detection Logic
· Match web, reverse-proxy, firewall, secure access, load-balancer, or network events targeting verified UniFi OS management interfaces.
· Match request paths or locally normalized path fields containing authentication-validation, traversal-style, encoded traversal, update-endpoint, package-management, unexpected file-access, or request-normalization mismatch indicators.
· Increase relevance when the source is outside approved administrator baselines, originates from suspicious infrastructure, appears newly observed, or accesses UniFi OS management interfaces from a non-standard path.
· Use this SIGMA rule as an event-level input to SIEM-native correlation rather than a standalone compromise rule.
· Suppress or reduce severity for approved vulnerability scanning, exposure assessment, monitoring, security testing, vendor support, incident response, or documented maintenance activity.
· Do not classify vulnerable-state findings, exposed interfaces, scanner labels, isolated denied requests, ordinary login failures, or single web errors as exploitation evidence by themselves.
Required Telemetry
· Web access logs.
· Reverse-proxy logs where available.
· Firewall or secure access logs where available.
· Load-balancer logs where available.
· Network telemetry where available.
· Source IP.
· Destination IP.
· Destination hostname.
· Destination port.
· HTTP method where available.
· Request path.
· Raw request path where available.
· Normalized request path where available.
· Response status where available.
· Response size where available.
· User agent where available.
· Event timestamp.
· UniFi OS asset enrichment.
· UniFi OS management-interface enrichment.
· Approved administrator source enrichment.
· Approved scanning or security-testing enrichment.
· Approved maintenance or change-window enrichment.
· Source reputation, ASN, geolocation, or newly observed source enrichment where available.
Engineering Implementation Instructions
· Convert this SIGMA rule through the customer’s target backend converter and validate field mappings before deployment.
· Map request path fields to the customer’s web, reverse-proxy, firewall, secure access, load-balancer, or network schema.
· Map source and destination fields to the customer’s normalized source IP, destination IP, destination hostname, and destination port fields.
· Create local enrichment fields that identify UniFi OS assets, management interfaces, approved administrator sources, VPN administration ranges, jump hosts, privileged access workstations, approved scanners, security-testing sources, vendor-support sources, and incident-response sources.
· Create local path categories for authentication-validation behavior, traversal-style path construction, encoded path variation, update-endpoint access, package-management endpoints, unexpected file-access paths, and request-normalization mismatch indicators.
· Treat local.unifi.*, local.source.*, and local.change.* fields in this template as backend-dependent enrichment placeholders that must be created, mapped, or renamed during conversion.
· Use backend SIEM correlation to combine this rule with request-burst thresholds, response anomalies, update activity, endpoint behavior, administrator-state changes, outbound communication, downstream configuration changes, and change-management context.
· Use exception handling for approved maintenance, firmware updates, package operations, vulnerability scanning, security testing, vendor support, monitoring, and incident response.
· Validate false-positive behavior against normal UniFi OS updates, administrator access, device onboarding, monitoring, scanning, and troubleshooting workflows.
· Do not enable high-severity alerting from this SIGMA event rule alone.
· Promote to alert only after the converted rule is correlated with suspicious source context or follow-on behavior in the target SIEM.
DRI Assessment
DRI
8.3 / 10
· The rule is behaviorally anchored to UniFi OS management-plane exploit-path request behavior rather than static CVE identifiers, proof-of-concept names, scanner labels, hashes, IP addresses, or actor infrastructure.
· The rule remains useful if an adversary changes user agent, source infrastructure, request pacing, path encoding, or follow-on timing.
· The score is supported by durable request-path categories, source-path deviation, traversal-style behavior, update-endpoint access, and request-normalization mismatch indicators.
· The score is constrained by missing request paths, reverse-proxy normalization, incomplete source baselines, heavy internet scanning, field-mapping variation, local enrichment quality, and backend conversion quality.
· The rule is durable as an event-level exploit-path detector but should not be treated as standalone proof of compromise.
TCR Assessment
Operational TCR
7.2 / 10
Full-Telemetry TCR
8.4 / 10
· Operational confidence depends on request-path visibility, backend field mapping, UniFi OS asset enrichment, approved-source enrichment, response-code visibility, local enrichment quality, and exception quality.
· Operational confidence is reduced where reverse proxies strip request details, management interfaces receive heavy scanning, approved administrator paths are broad, or source reputation enrichment is unavailable.
· Operational confidence is reduced where vulnerability scanning, exposure assessment, monitoring, vendor support, security testing, or incident-response workflows generate similar request behavior.
· Full-telemetry confidence improves when the converted SIGMA rule feeds SIEM-native correlation with UniFi OS logs, administrator audit logs, update-service logs, endpoint telemetry where available, configuration-change records, DNS telemetry, network telemetry, change-management records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support escalation and scoping rather than standalone confirmation of exploit success.
Limitations
· This rule detects suspicious UniFi OS management-plane request behavior, not confirmed exploitation by itself.
· Missing request paths, normalized paths, response status, response size, user agent, source enrichment, or asset enrichment can reduce confidence.
· Internet scanning, vulnerability assessment, penetration testing, monitoring, vendor support, administrator troubleshooting, and incident-response activity may produce similar request patterns.
· SIGMA does not provide the full multi-stage correlation required to prove command execution, root compromise, downstream configuration impact, or actor attribution.
· Non-standard enrichment fields in this rule are placeholders and must be locally mapped or replaced during backend conversion.
· The rule requires backend conversion, local field mapping, enrichment-field creation, exception validation, SIEM-native correlation, and query-performance testing before production alerting.
Detection Query Pattern
SIGMA event-rule template for UniFi OS management-plane exploit-path request behavior. This template requires backend conversion, local field mapping, local enrichment-field creation, exception handling, and SIEM-native correlation before production deployment.
title: UniFi OS Management-Plane Exploit-Path Request Event
id: unifi-os-management-plane-exploit-path-request-event
status: test
description: Detects suspicious UniFi OS management-plane request paths associated with authentication-validation anomalies, traversal-style path behavior, update endpoints, package-management endpoints, unexpected file-access paths, or request-normalization mismatch indicators. This rule is an event-level template and must be correlated with suspicious source context or follow-on behavior in the target SIEM.
references:
· Local UniFi OS asset inventory
· Local UniFi OS management-plane telemetry
author: CyberDax
date: 2026/06/24
logsource:
category: webserver
detection:
selection_unifi_target:
destination.ip|exists: true
selection_unifi_enrichment:
local.unifi.is_asset: true
selection_path_keywords:
url.path|contains:
o 'update'
o 'package'
o 'auth'
o 'validate'
o '../'
o '%2e%2e'
o 'traversal'
selection_path_category:
local.unifi.request_category:
o 'authentication_validation_path'
o 'traversal_style_path'
o 'encoded_path_variation'
o 'unexpected_file_access_path'
o 'update_endpoint_access'
o 'package_management_endpoint'
o 'request_normalization_mismatch'
filter_approved_admin_source:
local.source.is_approved_unifi_admin: true
filter_approved_activity:
local.change.context:
o 'approved_security_testing'
o 'approved_vulnerability_scanning'
o 'approved_unifi_maintenance'
o 'approved_vendor_support'
o 'approved_incident_response'
condition: selection_unifi_target and selection_unifi_enrichment and (selection_path_keywords or selection_path_category) and not 1 of filter_*
fields:
· source.ip
· destination.ip
· destination.port
· url.path
· url.original
· http.request.method
· http.response.status_code
· user_agent.original
· event.dataset
· local.unifi.request_category
falsepositives:
· Approved UniFi OS administration
· Approved firmware updates
· Approved package operations
· Vulnerability scanning
· Exposure assessment
· Security testing
· Vendor support
· Incident response
level: medium
tags:
· attack.initial_access
· attack.t1190
Rule
UniFi OS Service Context Process Execution or Update Follow-On Event
Rule Format
SIGMA event-rule template for endpoint, Linux system, EDR, process, file, sudo, or package-management telemetry after backend conversion, local field mapping, UniFi OS service-process enrichment, endpoint-visible asset validation, approved maintenance exception validation, and SIEM-native correlation with management-plane request activity.
Detection Purpose
· Detect suspicious process execution, shell execution, interpreter execution, file retrieval, archive extraction, package-manager execution, sudo usage, root-context execution, service modification, scheduled job creation, local user modification, SSH configuration change, or outbound process-network activity from UniFi OS service or update contexts.
· Identify endpoint-visible behavior that may represent command execution or post-exploitation follow-on behavior after UniFi OS management-plane exploit-path activity.
· Support backend correlation between UniFi OS update/package activity and host follow-on behavior.
· Preserve separation between suspicious host behavior and confirmed compromise by requiring process lineage, asset role, user context, maintenance context, and incident-response validation.
· This rule does not apply to UniFi OS appliance deployments that do not expose endpoint, process, file, sudo, system, or package-management telemetry to the customer.
Detection Logic
· Match process or system events from verified endpoint-visible UniFi OS Server, controller-host, or supporting Linux-host assets.
· Match parent process names or service contexts associated with UniFi OS web, application, controller, update, package-management, Java, Node.js, Nginx, service-wrapper, or locally mapped UniFi OS service processes.
· Match suspicious child process, command-line, file, sudo, service, or package-management behavior commonly associated with command execution, file staging, privilege activity, persistence preparation, or outbound follow-on activity.
· Increase relevance when activity occurs near UniFi OS management-plane exploit-path request behavior or update-endpoint activity in the target SIEM.
· Suppress or reduce severity for approved updates, package operations, controller upgrades, backup jobs, service restarts, administrator troubleshooting, vulnerability management, security testing, vendor support, or incident-response activity.
· Do not classify ordinary Linux administration or expected UniFi maintenance as exploitation without suspicious UniFi OS service lineage or management-plane correlation.
Required Telemetry
· Endpoint process telemetry.
· Linux system logs where available.
· EDR telemetry where available.
· Process creation events.
· Parent process name.
· Parent process path.
· Child process name.
· Child process path.
· Process command line.
· Process user.
· Effective user where available.
· Sudo events where available.
· File creation events where available.
· File modification events where available.
· Service modification events where available.
· Scheduled job events where available.
· Local user modification events where available.
· SSH configuration events where available.
· Process network events where available.
· Endpoint hostname.
· Endpoint IP address.
· UniFi OS endpoint-visible asset enrichment.
· UniFi OS service-process enrichment.
· Approved update and maintenance enrichment.
· Approved administrator or incident-response enrichment.
Engineering Implementation Instructions
· Convert this SIGMA rule through the customer’s target backend converter and validate backend-specific process, file, sudo, service, and system field mappings.
· Map UniFi OS endpoint-visible assets through local asset inventory or enrichment fields.
· Build UniFi OS service-process enrichment covering locally observed UniFi OS application processes, controller processes, update-service processes, Java processes, Node.js processes, Nginx or reverse-proxy processes, package-management processes, service wrappers, and approved maintenance scripts.
· Build suspicious child-process enrichment covering shells, interpreters, package managers, file-retrieval utilities, archive utilities, network utilities, service-management commands, user-management commands, SSH configuration commands, permission-changing commands, and sudo execution.
· Treat process field names in this template as backend-normalized field placeholders. Map them to ECS, Sysmon-for-Linux, EDR, auditd, osquery, or customer-specific endpoint fields during conversion.
· Use backend SIEM correlation to link this event rule with UniFi OS management-plane exploit-path request behavior, update-endpoint activity, suspicious source context, outbound communication, administrator-state changes, or downstream configuration changes.
· Use exceptions for approved firmware updates, package operations, controller upgrades, backup jobs, service restarts, administrator troubleshooting, vendor support, security testing, vulnerability management, and incident response.
· Do not claim coverage for appliance-only UniFi OS environments where endpoint telemetry is not available.
· Do not enable alert mode until process-lineage quality, command-line visibility, endpoint coverage, false-positive rate, exception logic, backend conversion quality, and SOC triage workflow are validated.
DRI Assessment
DRI
8.4 / 10
· The rule is behaviorally anchored to UniFi OS service-context process execution, suspicious child-process activity, sudo usage, update-context file staging, and host follow-on behavior rather than static CVE identifiers, exploit strings, proof-of-concept names, hashes, IP addresses, or known infrastructure.
· The rule remains useful if an adversary changes command syntax, file names, tool names, staging paths, outbound destinations, request paths, or execution timing.
· The score is supported by the durability of web or application service processes spawning shells, interpreters, package managers, file-retrieval utilities, sudo commands, service-management tools, or root-context processes.
· The score is constrained by endpoint-visibility gaps, incomplete command-line capture, weak process lineage, incomplete sudo telemetry, legitimate update behavior, and backend field-mapping variation.
· The rule is durable for endpoint-visible UniFi OS deployments but should not be treated as coverage for appliance-only deployments without host telemetry.
TCR Assessment
Operational TCR
7.4 / 10
Full-Telemetry TCR
8.6 / 10
· Operational confidence depends on endpoint telemetry coverage, process-lineage completeness, command-line visibility, service-process enrichment, asset-role accuracy, and approved-maintenance context.
· Operational confidence is reduced where UniFi OS maintenance frequently spawns package managers, service-management tools, shell scripts, backup jobs, or update workflows from service contexts.
· Operational confidence is reduced where endpoint telemetry exists but cannot reliably capture sudo usage, effective user context, command-line arguments, or process-network activity.
· Full-telemetry confidence improves when the converted SIGMA rule feeds SIEM-native correlation with UniFi OS logs, reverse-proxy logs, firewall logs, NDR telemetry, DNS telemetry, administrator activity, configuration changes, change-management records, and incident-response evidence.
· Even under full telemetry conditions, this rule should classify observed host behavior and escalation likelihood rather than infer actor attribution.
Limitations
· This rule applies only to endpoint-visible UniFi OS deployments and does not provide direct coverage for appliance deployments without endpoint telemetry.
· Legitimate updates, package operations, controller upgrades, backup jobs, service restarts, troubleshooting, vendor support, security testing, and incident response can produce similar child-process or privileged-execution behavior.
· Missing command-line capture, weak process lineage, incomplete sudo telemetry, limited file telemetry, or poor asset-role tagging can reduce confidence.
· SIGMA cannot express the full multi-stage timing and enrichment requirements by itself; backend SIEM correlation is required.
· Backend process field names vary significantly; every process, parent, command-line, user, and enrichment field must be validated during conversion.
· The rule should not be used to infer root compromise unless sudo, effective-user, root-context, system, or incident-response evidence supports that conclusion.
Detection Query Pattern
SIGMA event-rule template for UniFi OS service-context process execution or update follow-on behavior. This template requires backend conversion, local endpoint field mapping, UniFi OS service-process enrichment, exception handling, and SIEM-native correlation before production deployment.
title: UniFi OS Service Context Process Execution Or Update Follow-On Event
id: unifi-os-service-context-process-execution-or-update-followon-event
status: test
description: Detects suspicious child process, command-line, sudo, package-management, or service behavior from UniFi OS service or update contexts on endpoint-visible deployments. This rule is an event-level template and must be correlated with UniFi OS management-plane or update activity in the target SIEM.
references:
· Local UniFi OS endpoint-visible asset inventory
· Local endpoint telemetry
author: CyberDax
date: 2026/06/24
logsource:
product: linux
category: process_creation
detection:
selection_unifi_endpoint:
local.unifi.endpoint_visible: true
selection_unifi_parent_name:
process.parent.name|contains:
o 'unifi'
o 'java'
o 'node'
o 'nginx'
o 'systemd'
o 'service-wrapper'
selection_unifi_parent_path:
process.parent.executable|contains:
o '/unifi'
o '/UniFi'
o '/opt/'
o '/usr/lib/'
o '/var/lib/'
selection_suspicious_child:
process.name:
o 'sh'
o 'bash'
o 'dash'
o 'zsh'
o 'python'
o 'python3'
o 'perl'
o 'ruby'
o 'curl'
o 'wget'
o 'scp'
o 'ssh'
o 'nc'
o 'ncat'
o 'socat'
o 'tar'
o 'gzip'
o 'gunzip'
o 'unzip'
o 'dpkg'
o 'apt'
o 'apt-get'
o 'systemctl'
o 'service'
o 'chmod'
o 'chown'
o 'useradd'
o 'usermod'
o 'sudo'
selection_suspicious_command:
process.command_line|contains:
o 'curl '
o 'wget '
o 'bash -c'
o 'sh -c'
o '/tmp/'
o '/var/tmp/'
o '/dev/shm/'
o 'chmod +x'
o 'base64'
o 'python -c'
o 'python3 -c'
o 'systemctl'
o 'service '
o 'useradd'
o 'usermod'
o 'authorized_keys'
o 'sudo '
filter_approved_context:
local.change.context:
o 'approved_unifi_update'
o 'approved_package_operation'
o 'approved_controller_upgrade'
o 'approved_backup_job'
o 'approved_service_restart'
o 'approved_security_testing'
o 'approved_vendor_support'
o 'approved_incident_response'
condition: selection_unifi_endpoint and (selection_unifi_parent_name or selection_unifi_parent_path) and (selection_suspicious_child or selection_suspicious_command) and not filter_approved_context
fields:
· process.parent.executable
· process.parent.command_line
· process.executable
· process.command_line
· local.unifi.endpoint_visible
falsepositives:
· Approved UniFi OS updates
· Package operations
· Controller upgrades
· Backup jobs
· Service restarts
· Administrator troubleshooting
· Security testing
· Vendor support
· Incident response
level: high
tags:
· attack.execution
· attack.t1059
· attack.privilege_escalation
· attack.t1548
Rule
UniFi OS Downstream Configuration Change Event After Suspicious Management Activity
Rule Format
SIGMA event-rule template for administrator activity, configuration-change, network-device, firewall, VPN, DNS, wireless, gateway, recorder, storage, or managed-device telemetry after backend conversion, local field mapping, UniFi OS asset enrichment, downstream device enrichment, high-risk change mapping, approved change exception validation, and SIEM-native correlation with upstream UniFi OS suspicious activity.
Detection Purpose
· Detect downstream configuration-change events that may represent network-control impact after suspected UniFi OS exploit-path activity.
· Identify high-risk changes affecting gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless configuration, device adoption, recorder behavior, storage access, or managed-device trust.
· Support backend correlation where downstream changes occur near suspicious UniFi OS management-plane access, update-endpoint activity, administrator-state anomalies, outbound communication, or endpoint evidence.
· Preserve separation between suspicious downstream configuration change and confirmed compromise by requiring linkage to upstream UniFi OS suspicious activity, administrator anomalies, configuration evidence, or incident-response validation.
· This rule does not prove command execution, root compromise, credential theft, data exfiltration, downstream compromise, or actor attribution without supporting evidence.
Detection Logic
· Match configuration-change or administrator activity events involving downstream devices, gateway policy, firewall policy, routing, VPN, DNS, wireless, device adoption, recorder, storage, or managed-device trust.
· Match locally mapped high-risk change categories such as remote-access expansion, firewall weakening, new inbound exposure, segmentation change, default route change, DNS forwarding change, VPN access change, wireless security weakening, unexpected device adoption, backup export, or management-access expansion.
· Increase relevance when the event involves a newly created administrator, rarely used administrator, unfamiliar source, suspicious source, API token, unusual session, or missing approved change record.
· Use this SIGMA rule as an event-level input to backend SIEM correlation with upstream UniFi OS suspicious activity.
· Suppress or reduce severity for approved network maintenance, device replacement, site onboarding, firewall policy updates, VPN changes, DNS changes, wireless changes, vendor support, security testing, or incident response.
· Do not classify downstream configuration changes as UniFi OS compromise without upstream UniFi OS exploit-path activity, administrator-state anomaly, suspicious source context, or incident-response validation.
Required Telemetry
· Administrator activity logs.
· Configuration-change logs.
· Downstream network-device logs where available.
· Firewall change logs where available.
· Gateway policy logs where available.
· VPN configuration logs where available.
· DNS configuration logs where available.
· Wireless configuration logs where available.
· Recorder or storage logs where available.
· Event timestamp.
· Administrator identity where available.
· Source IP where available.
· Destination device where available.
· Configuration object.
· Configuration action.
· Change type.
· Device identifier.
· Device role.
· Network segment where available.
· UniFi OS asset enrichment.
· Downstream device inventory enrichment.
· High-risk change enrichment.
· Approved change enrichment.
· Approved administrator enrichment.
· Incident-response exception enrichment.
Engineering Implementation Instructions
· Convert this SIGMA rule through the customer’s target backend converter and validate administrator, configuration, network-device, firewall, VPN, DNS, wireless, recorder, and storage field mappings.
· Build downstream device enrichment covering gateways, firewalls, routes, VPN systems, DNS services, wireless infrastructure, recorders, storage systems, and managed devices.
· Build high-risk configuration-change enrichment for remote-access expansion, firewall weakening, new inbound exposure, segmentation changes, default route changes, DNS forwarding changes, VPN access changes, wireless security weakening, unexpected device adoption, backup exports, and management-access expansion.
· Build administrator-risk enrichment for newly created administrators, rarely used administrators, unusual source geographies, suspicious ASNs, unfamiliar devices, API token use, session anomalies, and administrator activity outside approved windows.
· Treat local.config.*, local.downstream.*, local.change.*, and local.unifi.* fields in this template as backend-dependent enrichment placeholders that must be created, mapped, or renamed during conversion.
· Use backend SIEM correlation to link this event rule with upstream UniFi OS suspicious activity, management-plane exploit-path access, update-endpoint activity, endpoint follow-on behavior, outbound communication, and change-management context.
· Use exceptions for approved network maintenance, device onboarding, firewall policy updates, route changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, security testing, and incident response.
· Do not enable alert mode until downstream inventory, configuration telemetry, administrator context, change-record quality, backend conversion quality, exception behavior, and SOC triage workflow are validated.
DRI Assessment
DRI
8.0 / 10
· The rule is behaviorally anchored to downstream configuration-change behavior after suspected UniFi OS suspicious activity rather than static CVE identifiers, exploit strings, proof-of-concept names, scanner labels, file artifacts, IP addresses, or known infrastructure.
· The rule remains useful if an adversary changes source infrastructure, administrator account, command syntax, outbound destination, downstream target order, or configuration-change sequence.
· The score is supported by the durability of gateway, firewall, routing, VPN, DNS, wireless, device-adoption, recorder, storage, or managed-device configuration changes after suspected management-plane compromise.
· The score is constrained by legitimate network maintenance, broad administrator workflows, incomplete configuration telemetry, weak change records, appliance-only visibility, incomplete downstream inventory, and backend field-mapping variation.
· The rule is durable as a downstream impact event detector but should not be treated as standalone proof of command execution, root compromise, credential theft, or actor attribution.
TCR Assessment
Operational TCR
7.2 / 10
Full-Telemetry TCR
8.4 / 10
· Operational confidence depends on downstream configuration telemetry, administrator context, change-management records, asset inventory, downstream inventory, backend conversion quality, enrichment quality, and SIEM-native correlation with upstream UniFi OS suspicious activity.
· Operational confidence is reduced where network teams perform frequent configuration changes, device onboarding is common, administrator sources are broad, or configuration-change records are incomplete.
· Operational confidence is reduced where downstream device inventories, gateway roles, firewall policy ownership, VPN workflows, DNS change records, wireless change records, recorder records, or storage records are poorly documented.
· Full-telemetry confidence improves when the converted SIGMA rule feeds SIEM-native correlation with UniFi OS logs, administrator activity logs, endpoint telemetry where available, system logs, firewall logs, DNS logs, proxy logs, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support downstream impact triage rather than standalone confirmation of root compromise or actor attribution.
Limitations
· This rule detects high-risk downstream configuration-change events that require correlation with suspected UniFi OS activity; it does not confirm exploitation by itself.
· Legitimate network maintenance, device onboarding, firewall policy updates, VPN changes, DNS changes, wireless changes, storage changes, vendor support, security testing, and incident response can produce similar downstream signals.
· Missing downstream configuration telemetry, incomplete administrator context, weak change records, broad administrator source paths, or incomplete asset inventory can reduce confidence.
· SIGMA cannot express full upstream-to-downstream timing logic by itself; SIEM-native correlation is required.
· Non-standard enrichment fields in this rule are placeholders and must be locally mapped or replaced during backend conversion.
· The rule should not be used to infer command execution, root compromise, credential theft, or actor attribution without supporting host, system, administrator, configuration, or incident-response evidence.
Detection Query Pattern
SIGMA event-rule template for downstream configuration-change events that may indicate UniFi OS network-control impact after suspicious management activity. This template requires backend conversion, local field mapping, high-risk change enrichment, exception handling, and SIEM-native correlation with upstream UniFi OS suspicious activity before production deployment.
title: UniFi OS Downstream Configuration Change Event After Suspicious Management Activity
id: unifi-os-downstream-configuration-change-event-after-suspicious-management-activity
status: test
description: Detects high-risk downstream configuration changes that may indicate network-control impact after suspected UniFi OS management-plane suspicious activity. This rule is an event-level template and must be correlated with upstream UniFi OS suspicious activity in the target SIEM.
references:
· Local UniFi OS asset inventory
· Local downstream configuration-change telemetry
author: CyberDax
date: 2026/06/24
logsource:
category: application
detection:
selection_configuration_event:
event.category|contains:
o 'configuration'
o 'iam'
o 'network'
selection_downstream_change:
event.action|contains:
o 'firewall'
o 'routing'
o 'route'
o 'vpn'
o 'dns'
o 'wireless'
o 'device_adoption'
o 'gateway'
o 'policy'
o 'configuration'
selection_high_risk_change:
local.config.high_risk_change_type:
o 'remote_access_expansion'
o 'firewall_weakening'
o 'new_inbound_exposure'
o 'segmentation_change'
o 'default_route_change'
o 'dns_forwarding_change'
o 'vpn_access_change'
o 'wireless_security_weakening'
o 'unexpected_device_adoption'
o 'backup_export'
o 'management_access_expansion'
filter_approved_change:
local.change.context:
o 'approved_network_maintenance'
o 'approved_device_onboarding'
o 'approved_firewall_policy_update'
o 'approved_route_change'
o 'approved_vpn_change'
o 'approved_dns_change'
o 'approved_wireless_change'
o 'approved_vendor_support'
o 'approved_security_testing'
o 'approved_incident_response'
condition: selection_configuration_event and selection_downstream_change and selection_high_risk_change and not filter_approved_change
fields:
· event.action
· event.category
· source.ip
· destination.ip
· local.config.high_risk_change_type
· local.change.context
falsepositives:
· Approved network maintenance
· Device onboarding
· Firewall policy updates
· VPN changes
· DNS changes
· Wireless changes
· Vendor support
· Security testing
· Incident response
level: medium
tags:
· attack.impact
· attack.defense_evasion
· attack.persistence
AWS
Detection Viability Assessment
AWS has two rules for this EXP report.
· AWS is conditionally viable for detecting downstream cloud-impact behavior related to UniFi OS control-plane compromise when the affected environment uses AWS-hosted UniFi OS Server infrastructure, AWS-hosted reverse proxies, AWS-hosted management access paths, AWS identity services, AWS network controls, AWS logging services, AWS backup workflows, or AWS-connected downstream infrastructure.
· AWS does not provide direct native visibility into UniFi OS appliance exploit-path behavior unless UniFi OS management-plane logs, reverse-proxy logs, endpoint telemetry, firewall telemetry, DNS telemetry, or configuration-change telemetry are collected from AWS-hosted systems or forwarded into AWS logging or detection services.
· AWS detection should focus on cloud-observable follow-on behavior, including suspicious access to AWS-hosted UniFi management infrastructure, security group changes, route changes, DNS changes, WAF changes, IAM activity, Systems Manager activity, secrets access, backup or storage access, and outbound communication from AWS-hosted UniFi systems.
· AWS detection must not claim direct proof of UniFi OS exploitation from AWS-native telemetry alone unless upstream UniFi OS exploit-path activity, endpoint evidence, administrator activity, configuration evidence, or incident-response evidence is also present.
· AWS rules must separate direct AWS visibility from conditional downstream correlation so that cloud-only anomalies are not incorrectly attributed to UniFi OS compromise.
· AWS detection is strongest when CloudTrail, VPC Flow Logs, Route 53 Resolver logs, ALB or NLB logs, WAF logs, CloudWatch logs, GuardDuty findings, IAM Access Analyzer context, AWS Config, Systems Manager telemetry, EC2 endpoint telemetry where available, and forwarded UniFi OS logs can be correlated.
· AWS should not infer command execution, root compromise, downstream network compromise, credential theft, data exfiltration, or actor attribution without supporting UniFi OS, endpoint, identity, network, configuration, or incident-response evidence.
Rule
AWS-Hosted UniFi OS Management Access Followed by Suspicious Cloud or Network Follow-On Behavior
Rule Format
AWS conditional correlation rule template suitable for CloudTrail, VPC Flow Logs, Route 53 Resolver logs, ALB or NLB access logs, AWS WAF logs, CloudWatch logs, GuardDuty findings, Systems Manager telemetry where available, EC2 endpoint telemetry where available, forwarded UniFi OS logs where available, and AWS Config after local log-source validation, resource-tag validation, management-path validation, identity mapping, network mapping, exception validation, and SIEM or cloud-native correlation.
Detection Purpose
· Detect suspicious access to AWS-hosted or AWS-fronted UniFi OS management infrastructure followed by cloud-observable follow-on behavior.
· Identify cases where AWS-hosted management paths, reverse proxies, EC2-hosted UniFi OS Server deployments, ALB or NLB front ends, WAF-protected paths, security groups, Route 53, IAM, Systems Manager, or AWS network controls show behavior consistent with attempted or suspected UniFi OS control-plane compromise.
· Support correlation between upstream UniFi OS exploit-path activity and downstream AWS activity such as security group modification, network exposure changes, unusual IAM use, secrets access, DNS changes, backup access, outbound communication, or access from newly observed sources.
· Preserve separation between AWS-observed suspicious behavior and confirmed UniFi OS compromise by requiring supporting UniFi OS, endpoint, administrator, network, configuration, or incident-response evidence.
· This rule does not prove successful UniFi OS exploitation, command execution, root compromise, credential theft, data exfiltration, downstream infrastructure compromise, or actor attribution without supporting telemetry and investigation evidence.
Detection Logic
· Identify AWS-hosted UniFi OS assets, reverse proxies, management interfaces, ALB or NLB listeners, WAF-protected management paths, EC2 instances, security groups, Route 53 records, and related AWS network components using asset tags, CMDB records, AWS Config relationships, resource names, or local enrichment.
· Detect management-plane access to AWS-hosted or AWS-fronted UniFi infrastructure from unfamiliar source IPs, suspicious ASNs, hosting providers, residential proxy ranges, unusual geographies, VPN paths outside approved administration baselines, newly observed internal sources, or unmanaged systems.
· Detect request-path or WAF-visible behavior involving authentication-validation paths, traversal-style path construction, encoded path variations, update endpoints, package-management endpoints, unexpected file-access paths, or request-normalization mismatch indicators where AWS-hosted ingress telemetry exposes those fields.
· Detect follow-on AWS activity involving security group rule changes, route changes, DNS changes, WAF rule changes, unusual IAM activity, Systems Manager command use, secrets access, backup access, snapshot access, storage access, configuration export behavior, or abnormal outbound communication from AWS-hosted UniFi systems.
· Increase confidence when suspicious management-plane access is followed by AWS Config changes, CloudTrail management events, GuardDuty findings, unusual DNS queries, rare outbound VPC Flow Log destinations, or endpoint-visible process behavior on EC2-hosted UniFi systems.
· Reduce severity when activity aligns with approved administrator access, approved maintenance windows, approved deployment automation, patching, backup workflows, vulnerability scanning, security testing, vendor support, monitoring, or incident-response activity.
· Do not attribute AWS-only events to UniFi OS exploitation unless there is reliable linkage to UniFi OS management-plane activity, UniFi OS assets, administrator context, endpoint evidence, configuration-change evidence, or incident-response validation.
· Do not treat internet exposure, scanner output, isolated ALB or WAF events, ordinary CloudTrail activity, or expected AWS automation as UniFi OS compromise evidence by itself.
Required Telemetry
· CloudTrail management events.
· CloudTrail data events where applicable.
· VPC Flow Logs.
· Route 53 Resolver query logs where available.
· ALB or NLB access logs where available.
· AWS WAF logs where available.
· CloudWatch logs from AWS-hosted UniFi OS systems where available.
· Forwarded UniFi OS logs where available.
· Systems Manager command telemetry where available.
· EC2 endpoint telemetry where available.
· GuardDuty findings.
· AWS Config resource history.
· Security group change events.
· Route table change events.
· Network ACL change events.
· IAM activity events.
· Secrets Manager or Parameter Store access logs where applicable.
· Backup, snapshot, or storage access logs where applicable.
· Source IP.
· Destination IP.
· Destination hostname.
· AWS account ID.
· AWS region.
· VPC ID.
· Subnet ID.
· Instance ID.
· Load balancer ARN where applicable.
· Security group ID.
· IAM principal.
· User agent where available.
· Request path where available.
· Response status where available.
· Event timestamp.
· UniFi OS AWS asset tags or local enrichment.
· Approved administrator source enrichment.
· Approved AWS automation enrichment.
· Approved change-window enrichment.
· Incident-response exception enrichment.
Engineering Implementation Instructions
· Validate which UniFi OS components are AWS-hosted, AWS-fronted, or forwarding telemetry into AWS before enabling this rule.
· Build or validate asset tags, AWS Config relationships, CMDB records, or enrichment fields that identify AWS-hosted UniFi OS Server deployments, reverse proxies, management interfaces, EC2 instances, load balancers, WAF web ACLs, security groups, Route 53 records, and related VPC components.
· Validate CloudTrail organization trails, CloudTrail management-event coverage, relevant data-event coverage, VPC Flow Log scope, Route 53 Resolver query-log scope, ALB or NLB logging, WAF logging, CloudWatch log forwarding, Systems Manager telemetry, GuardDuty coverage, AWS Config coverage, and endpoint telemetry on EC2-hosted UniFi systems where available.
· Build approved administrator source baselines covering administrator IPs, VPN ranges, jump hosts, privileged access workstations, management networks, vendor-support paths, vulnerability management systems, security-testing systems, and incident-response systems.
· Build approved AWS automation baselines covering infrastructure-as-code pipelines, deployment roles, patch-management roles, backup roles, monitoring roles, incident-response roles, and expected service-linked roles.
· Build enrichment that maps AWS resource identifiers to UniFi OS asset roles and management-plane functions.
· Treat EventBridge patterns as candidate-event selectors for AWS control-plane activity, not as complete UniFi OS compromise correlation by themselves.
· Use SIEM, Security Lake, CloudWatch Logs Insights over normalized log groups, Athena over normalized S3 data, OpenSearch, or a cloud-native workflow to correlate suspicious AWS-hosted UniFi management access with follow-on AWS activity.
· Use bounded correlation windows between suspicious AWS-hosted UniFi management access and follow-on AWS activity.
· Use separate analytic outcomes for suspicious AWS-hosted management access, suspected UniFi OS exploit-path activity, suspicious AWS network-control change, suspicious IAM or secrets activity, suspicious outbound communication, and confirmed compromise.
· Use AWS Config and CloudTrail to validate whether security group, route, DNS, IAM, WAF, backup, or storage changes align with approved change records.
· Use VPC Flow Logs, DNS logs, ALB or WAF logs, forwarded UniFi OS logs, and endpoint telemetry to determine whether outbound or follow-on behavior is tied to AWS-hosted UniFi systems.
· Do not enable alert mode until AWS account scope, region coverage, log delivery, resource tagging, identity mapping, source baselines, automation exceptions, change-management integration, normalized correlation data, and query performance are validated.
DRI Assessment
DRI
7.7 / 10
· The rule is behaviorally anchored to suspicious access to AWS-hosted or AWS-fronted UniFi management infrastructure followed by AWS-observable network, identity, configuration, or outbound behavior rather than static CVE identifiers, proof-of-concept names, IP addresses, hashes, or actor infrastructure.
· The rule remains useful if an adversary changes source infrastructure, request timing, user agent, AWS resource target, outbound destination, or follow-on sequence.
· The score is supported by durable cloud-observable signals such as management access anomalies, security group changes, IAM activity, DNS changes, VPC Flow Log anomalies, AWS Config changes, GuardDuty findings, and EC2 endpoint behavior where available.
· The score is constrained by AWS-only visibility, incomplete UniFi OS log forwarding, missing request paths, weak resource tagging, legitimate automation noise, cross-account complexity, and incomplete change-management context.
· The rule is durable as a conditional downstream cloud-impact detector but should not be treated as direct proof of UniFi OS exploitation.
TCR Assessment
Operational TCR
7.0 / 10
Full-Telemetry TCR
8.3 / 10
· Operational confidence depends on whether UniFi OS management infrastructure is AWS-hosted or AWS-fronted, whether relevant logs are enabled, whether AWS resources are correctly tagged, and whether identity and change-management context is available.
· Operational confidence is reduced where UniFi OS is appliance-only, not AWS-hosted, not AWS-fronted, or not forwarding logs into AWS or the detection backend.
· Operational confidence is reduced where AWS automation frequently modifies security groups, DNS records, WAF policies, routes, backups, storage objects, or IAM permissions.
· Full-telemetry confidence improves when AWS telemetry correlates with UniFi OS logs, endpoint telemetry on EC2, administrator activity, forwarded application logs, reverse-proxy logs, change-management records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support conditional cloud-impact triage rather than standalone confirmation of UniFi OS exploit success.
Limitations
· This rule applies only when UniFi OS infrastructure is AWS-hosted, AWS-fronted, or meaningfully integrated with AWS logging and identity workflows.
· AWS-native telemetry does not directly prove UniFi OS exploitation unless linked to UniFi OS management-plane activity, endpoint behavior, administrator activity, configuration evidence, or incident-response findings.
· Missing CloudTrail, VPC Flow Logs, Route 53 Resolver logs, ALB or WAF logs, CloudWatch logs, endpoint telemetry, Config history, or resource tags can reduce confidence.
· Approved AWS automation, infrastructure-as-code deployments, backup workflows, patching, security testing, vendor support, monitoring, and incident response can produce similar cloud-side changes.
· The rule may miss exploitation that affects UniFi OS appliances outside AWS visibility or does not produce AWS-observable follow-on behavior.
· The rule should not be used to infer root compromise, credential theft, data exfiltration, downstream compromise, or actor attribution without supporting evidence.
Detection Query Pattern
AWS conditional detection pattern for AWS-hosted UniFi OS management access followed by suspicious cloud or network follow-on behavior. The EventBridge pattern identifies high-risk AWS control-plane candidate events only. Final correlation requires local AWS account, region, log-source, resource-tag, identity, enrichment, exception, normalized-log, and timing-window validation.
{
"source": ["aws.ec2", "aws.route53", "aws.wafv2", "aws.iam", "aws.ssm", "aws.secretsmanager", "aws.backup", "aws.s3"],
"detail-type": ["AWS API Call via CloudTrail"],
"detail": {
"eventSource": [
"ec2.amazonaws.com",
"route53.amazonaws.com",
"wafv2.amazonaws.com",
"iam.amazonaws.com",
"ssm.amazonaws.com",
"secretsmanager.amazonaws.com",
"backup.amazonaws.com",
"s3.amazonaws.com"
],
"eventName": [
"AuthorizeSecurityGroupIngress",
"AuthorizeSecurityGroupEgress",
"RevokeSecurityGroupIngress",
"RevokeSecurityGroupEgress",
"CreateRoute",
"ReplaceRoute",
"DeleteRoute",
"ChangeResourceRecordSets",
"UpdateWebACL",
"PutRolePolicy",
"AttachRolePolicy",
"CreatePolicyVersion",
"CreateAccessKey",
"StartSession",
"SendCommand",
"GetSecretValue",
"GetParameter",
"StartBackupJob",
"StartRestoreJob",
"GetObject",
"PutObject"
]
}
}
CloudWatch Logs Insights supporting hunt pattern for normalized AWS-hosted UniFi management ingress and AWS follow-on activity. This pattern assumes ALB, WAF, reverse-proxy, VPC Flow Log, CloudTrail, CloudWatch, or forwarded UniFi OS events have been normalized into a common schema with local enrichment fields. The traversal condition must be implemented using escaped literal dot-dot matching so that dot-dot traversal is not interpreted as any two characters.
fields @timestamp, src_ip, dst_ip, host, request_path, eventName, eventSource, user_arn, awsRegion, resource_id, local_unifi_asset, local_unifi_management_path, local_approved_admin_source, local_approved_change
| filter local_unifi_asset = "true"
| filter local_approved_change != "true"
| filter (
local_unifi_management_path = "true"
or request_path like /update|package|auth|validate|traversal|%2e%2e/
or request_path like /\.\./
or eventName in [
"AuthorizeSecurityGroupIngress",
"AuthorizeSecurityGroupEgress",
"RevokeSecurityGroupIngress",
"RevokeSecurityGroupEgress",
"CreateRoute",
"ReplaceRoute",
"DeleteRoute",
"ChangeResourceRecordSets",
"UpdateWebACL",
"StartSession",
"SendCommand",
"GetSecretValue",
"GetParameter",
"StartBackupJob",
"StartRestoreJob",
"GetObject",
"PutObject"
]
)
| filter local_approved_admin_source != "true"
| stats count(*) as event_count, count_distinct(request_path) as distinct_paths, count_distinct(eventName) as distinct_aws_actions by bin(10m), src_ip, dst_ip, host, user_arn, awsRegion, resource_id
| filter event_count >= ENV_UNIFI_AWS_EVENT_THRESHOLD or distinct_aws_actions >= ENV_UNIFI_AWS_ACTION_THRESHOLD
| sort event_count desc
Rule
AWS IAM, Secrets, or Network Control Activity Near Suspected UniFi OS Compromise
Rule Format
AWS conditional correlation rule template suitable for CloudTrail, IAM activity, Secrets Manager, Systems Manager, AWS Config, GuardDuty, VPC Flow Logs, Route 53 Resolver logs, CloudWatch logs, and forwarded UniFi OS or reverse-proxy telemetry after local log-source validation, identity mapping, resource-tag validation, UniFi OS asset correlation, exception validation, and SIEM or cloud-native correlation.
Detection Purpose
· Detect AWS IAM, secrets, Systems Manager, backup, storage, DNS, WAF, security group, route, or network-control activity occurring near suspected UniFi OS compromise activity.
· Identify cases where access to AWS-connected infrastructure may be affected by compromised UniFi management paths, exposed management hosts, administrator credential misuse, or downstream network-control changes.
· Support conditional cloud-impact triage when suspected UniFi OS compromise overlaps with AWS identity, secrets, network, backup, storage, or management-control events.
· Preserve separation between AWS activity and UniFi OS compromise by requiring reliable upstream linkage to UniFi OS suspicious activity, AWS-hosted UniFi assets, administrator context, or incident-response evidence.
· This rule does not prove UniFi OS exploitation, AWS compromise, credential theft, data exfiltration, root compromise, or actor attribution without supporting evidence.
Detection Logic
· Identify suspected UniFi OS compromise candidates from forwarded UniFi OS logs, reverse-proxy logs, WAF logs, ALB logs, CloudWatch logs, SIEM detections, endpoint telemetry, incident-response tags, or locally enriched suspect asset markers.
· Identify AWS activity involving IAM policy changes, access key creation, unusual role assumption, Systems Manager sessions or commands, Secrets Manager access, Parameter Store access, AWS Backup activity, S3 object access, Route 53 changes, WAF changes, security group changes, route changes, or network ACL changes.
· Correlate AWS activity with suspected UniFi OS compromise candidates using shared asset tags, source IPs, administrator identities, IAM principals, management jump hosts, VPC context, subnet context, reverse-proxy paths, forwarded UniFi OS logs, or incident-response case identifiers.
· Increase confidence when AWS activity occurs from newly observed sources, unfamiliar administrators, suspicious user agents, unusual geographies, unusual ASNs, non-standard access paths, or roles not normally associated with UniFi administration.
· Increase confidence when AWS activity expands remote access, weakens network controls, accesses secrets, exports backups, modifies DNS, modifies WAF rules, creates access keys, starts Systems Manager sessions, sends commands, or accesses sensitive storage near suspected UniFi OS activity.
· Reduce severity when activity aligns with approved infrastructure-as-code, approved deployment automation, scheduled backups, patching, disaster recovery tests, security testing, vendor support, monitoring, or incident response.
· Do not attribute AWS IAM, secrets, backup, storage, or network-control activity to UniFi OS compromise without upstream UniFi OS suspicious activity, AWS-hosted UniFi asset context, shared administrator context, or incident-response validation.
· Do not treat ordinary CloudTrail noise or expected AWS automation as cloud-impact evidence.
Required Telemetry
· CloudTrail management events.
· CloudTrail data events where applicable.
· IAM activity logs.
· STS AssumeRole activity.
· Secrets Manager access logs.
· Systems Manager session and command telemetry.
· AWS Config resource history.
· GuardDuty findings.
· VPC Flow Logs.
· Route 53 Resolver query logs where available.
· ALB or WAF logs where available.
· CloudWatch logs from AWS-hosted UniFi systems where available.
· Forwarded UniFi OS or reverse-proxy logs where available.
· S3 data events where applicable.
· AWS Backup events where applicable.
· AWS account ID.
· AWS region.
· IAM principal.
· Source IP.
· User agent.
· Resource ARN.
· Instance ID where applicable.
· VPC ID.
· Subnet ID.
· Security group ID.
· Route table ID.
· Secret ARN where applicable.
· Parameter name where applicable.
· Bucket name where applicable.
· Event timestamp.
· UniFi OS suspected compromise enrichment.
· UniFi OS AWS asset enrichment.
· Administrator identity mapping.
· Approved automation enrichment.
· Approved change enrichment.
· Incident-response case enrichment.
Engineering Implementation Instructions
· Validate whether AWS is in scope for the UniFi OS deployment before enabling this rule.
· Build suspected UniFi OS compromise enrichment from upstream S25 detections, forwarded UniFi OS logs, reverse-proxy logs, WAF logs, ALB logs, EC2 endpoint telemetry, SIEM case tags, or incident-response tags.
· Build AWS resource enrichment linking EC2 instances, load balancers, WAF web ACLs, Route 53 records, security groups, VPCs, subnets, IAM roles, secrets, backups, storage resources, and monitoring resources to UniFi OS management-plane functions where applicable.
· Build identity mapping between UniFi administrators, IAM principals, federated identities, privileged access workstations, jump hosts, VPN users, Systems Manager users, and incident-response users.
· Build approved automation exceptions for infrastructure-as-code, deployment pipelines, patch-management roles, backup jobs, monitoring systems, security testing, disaster recovery tests, vendor support, and incident-response roles.
· Use bounded time windows around suspected UniFi OS activity to correlate AWS identity, secrets, backup, storage, network, DNS, WAF, and Systems Manager actions.
· Treat EventBridge patterns as high-risk AWS activity selectors, not as proof that AWS activity is related to UniFi OS compromise.
· Use SIEM, Security Lake, CloudWatch Logs Insights over normalized log groups, Athena over normalized S3 data, OpenSearch, Security Hub automation, or cloud-native workflow logic to perform final correlation.
· Use AWS Config to validate whether AWS resource changes occurred, persisted, or were reverted.
· Use CloudTrail, GuardDuty, VPC Flow Logs, Route 53 Resolver logs, and CloudWatch logs to separate suspicious cloud activity from expected automation.
· Use separate analytic outcomes for suspected UniFi OS compromise, suspected AWS identity impact, suspected secrets exposure, suspected network-control change, suspected backup or storage access, and confirmed cloud impact.
· Do not enable alert mode until AWS account scope, organization trail coverage, CloudTrail data-event coverage, identity mapping, resource enrichment, source baselines, automation exceptions, change-management integration, normalized correlation data, and query performance are validated.
DRI Assessment
DRI
7.5 / 10
· The rule is behaviorally anchored to AWS IAM, secrets, network-control, backup, storage, DNS, WAF, Systems Manager, and cloud-management behavior occurring near suspected UniFi OS compromise rather than static CVE identifiers, IP addresses, hashes, tool names, or actor infrastructure.
· The rule remains useful if an adversary changes source infrastructure, IAM principal, user agent, AWS service target, access method, or timing.
· The score is supported by durable cloud-control-plane behaviors such as security group changes, IAM changes, access key creation, secrets access, Systems Manager use, DNS changes, WAF changes, backup activity, and storage access.
· The score is constrained by the conditional nature of AWS visibility, legitimate automation, incomplete linkage to UniFi OS assets, cross-account complexity, incomplete CloudTrail data events, and weak identity mapping.
· The rule is durable as conditional cloud-impact correlation but should not be treated as direct UniFi OS exploit detection.
TCR Assessment
Operational TCR
6.8 / 10
Full-Telemetry TCR
8.2 / 10
· Operational confidence depends on upstream UniFi OS suspicion quality, AWS logging completeness, resource tagging, identity mapping, change-management context, GuardDuty coverage, CloudTrail data-event coverage, and automation exception quality.
· Operational confidence is reduced where UniFi OS is not AWS-hosted, not AWS-fronted, or not connected to AWS identity, logging, backup, storage, or network-control workflows.
· Operational confidence is reduced where AWS automation, infrastructure-as-code, scheduled backup workflows, patching, monitoring, and security testing frequently produce similar events.
· Full-telemetry confidence improves when AWS telemetry is correlated with UniFi OS logs, reverse-proxy logs, endpoint telemetry, administrator activity, network telemetry, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support conditional cloud-impact triage rather than standalone confirmation of AWS compromise or UniFi OS exploit success.
Limitations
· This rule is conditional and applies only when AWS services are relevant to the UniFi OS deployment, management path, logging path, identity path, backup path, or downstream infrastructure.
· AWS activity near suspected UniFi OS compromise does not automatically mean AWS was compromised.
· AWS-native telemetry cannot prove UniFi OS exploitation without upstream UniFi OS, endpoint, administrator, network, configuration, or incident-response evidence.
· Missing CloudTrail data events, incomplete VPC Flow Logs, missing Route 53 Resolver logs, weak resource tagging, weak identity mapping, and incomplete change-management records can reduce confidence.
· Approved infrastructure-as-code, automation, backup jobs, security testing, monitoring, vendor support, and incident response can produce similar cloud-side activity.
· The rule should not be used to infer credential theft, data exfiltration, root compromise, downstream compromise, or actor attribution without supporting evidence.
Detection Query Pattern
AWS conditional correlation pattern for IAM, secrets, Systems Manager, backup, storage, DNS, WAF, or network-control activity near suspected UniFi OS compromise. The EventBridge pattern identifies high-risk AWS control-plane candidate events only. Final correlation requires local AWS account, region, log-source, resource-tag, identity, enrichment, exception, normalized-log, and timing-window validation.
{
"source": ["aws.ec2", "aws.route53", "aws.wafv2", "aws.iam", "aws.sts", "aws.ssm", "aws.secretsmanager", "aws.backup", "aws.s3"],
"detail-type": ["AWS API Call via CloudTrail"],
"detail": {
"eventSource": [
"ec2.amazonaws.com",
"route53.amazonaws.com",
"wafv2.amazonaws.com",
"iam.amazonaws.com",
"sts.amazonaws.com",
"secretsmanager.amazonaws.com",
"backup.amazonaws.com",
"s3.amazonaws.com"
],
"eventName": [
"AuthorizeSecurityGroupIngress",
"AuthorizeSecurityGroupEgress",
"CreateRoute",
"ReplaceRoute",
"DeleteRoute",
"ChangeResourceRecordSets",
"UpdateWebACL",
"PutRolePolicy",
"AttachRolePolicy",
"CreatePolicyVersion",
"CreateAccessKey",
"AssumeRole",
"StartSession",
"SendCommand",
"GetSecretValue",
"GetParameter",
"StartBackupJob",
"StartRestoreJob",
"GetObject",
"PutObject"
]
}
}
CloudWatch Logs Insights supporting hunt pattern for normalized AWS IAM, secrets, network-control, backup, storage, DNS, WAF, or Systems Manager activity near suspected UniFi OS compromise. This pattern assumes CloudTrail, Config, GuardDuty, VPC Flow Log, CloudWatch, ALB, WAF, reverse-proxy, or forwarded UniFi OS events have been normalized into a common schema with local enrichment fields.
fields @timestamp, eventName, eventSource, user_arn, source_ip, user_agent, awsRegion, resource_id, local_unifi_suspect_asset, local_approved_change
| filter local_unifi_suspect_asset = "true"
| filter local_approved_change != "true"
| filter eventName in [
"AuthorizeSecurityGroupIngress",
"AuthorizeSecurityGroupEgress",
"CreateRoute",
"ReplaceRoute",
"ChangeResourceRecordSets",
"UpdateWebACL",
"PutRolePolicy",
"AttachRolePolicy",
"CreatePolicyVersion",
"CreateAccessKey",
"AssumeRole",
"StartSession",
"SendCommand",
"GetSecretValue",
"GetParameter",
"StartBackupJob",
"StartRestoreJob",
"GetObject",
"PutObject"
]
| stats count(*) as aws_action_count, count_distinct(eventName) as distinct_aws_actions, count_distinct(user_arn) as distinct_principals by bin(10m), source_ip, user_arn, awsRegion, resource_id
| filter aws_action_count >= ENV_UNIFI_AWS_ACTION_THRESHOLD or distinct_aws_actions >= ENV_UNIFI_AWS_DISTINCT_ACTION_THRESHOLD
| sort aws_action_count desc
Azure
Detection Viability Assessment
Azure has two rules for this EXP report.
· Azure is conditionally viable for detecting downstream cloud-impact behavior related to UniFi OS control-plane compromise when the affected environment uses Azure-hosted UniFi OS Server infrastructure, Azure-hosted reverse proxies, Azure Application Gateway, Azure Front Door, Azure Firewall, Azure identity services, Azure networking controls, Azure logging services, Azure backup workflows, or Azure-connected downstream infrastructure.
· Azure does not provide direct native visibility into UniFi OS appliance exploit-path behavior unless UniFi OS management-plane logs, reverse-proxy logs, endpoint telemetry, firewall telemetry, DNS telemetry, or configuration-change telemetry are collected from Azure-hosted systems or forwarded into Microsoft Sentinel, Log Analytics, Microsoft Defender, Azure Monitor, or another detection backend.
· Azure detection should focus on cloud-observable follow-on behavior, including suspicious access to Azure-hosted UniFi management infrastructure, network security group changes, route changes, DNS changes, WAF changes, Entra ID activity, managed identity activity, Key Vault access, Azure VM command execution, backup or storage access, and outbound communication from Azure-hosted UniFi systems.
· Azure detection must not claim direct proof of UniFi OS exploitation from Azure-native telemetry alone unless upstream UniFi OS exploit-path activity, endpoint evidence, administrator activity, configuration evidence, or incident-response evidence is also present.
· Azure rules must separate direct Azure visibility from conditional downstream correlation so that cloud-only anomalies are not incorrectly attributed to UniFi OS compromise.
· Azure detection is strongest when Azure Activity logs, Entra ID sign-in logs, Entra ID audit logs, NSG flow logs, Azure Firewall logs, Application Gateway logs, Front Door logs, WAF logs, Azure Monitor logs, Microsoft Defender for Cloud alerts, Defender for Endpoint telemetry on Azure VMs, Azure Resource Graph context, Key Vault diagnostic logs, Azure DNS logs where available, storage logs, backup logs, and forwarded UniFi OS logs can be correlated.
· Azure should not infer command execution, root compromise, downstream network compromise, credential theft, data exfiltration, or actor attribution without supporting UniFi OS, endpoint, identity, network, configuration, or incident-response evidence.
Rule
Azure-Hosted UniFi OS Management Access Followed by Suspicious Cloud or Network Follow-On Behavior
Rule Format
Azure conditional correlation rule template suitable for Microsoft Sentinel, Log Analytics, Azure Activity logs, Entra ID sign-in logs, Entra ID audit logs, NSG flow logs, Azure Firewall logs, Application Gateway logs, Front Door logs, WAF logs, Azure Monitor logs, Microsoft Defender alerts, Defender for Endpoint telemetry where available, Key Vault logs, storage logs, backup logs, forwarded UniFi OS logs where available, and Azure Resource Graph context after local workspace validation, resource-tag validation, management-path validation, identity mapping, network mapping, exception validation, and Sentinel or backend correlation.
Detection Purpose
· Detect suspicious access to Azure-hosted or Azure-fronted UniFi OS management infrastructure followed by cloud-observable follow-on behavior.
· Identify cases where Azure-hosted management paths, reverse proxies, Azure VM-hosted UniFi OS Server deployments, Application Gateway front ends, Front Door paths, WAF-protected paths, network security groups, Azure Firewall, Azure DNS, Entra ID, managed identities, Key Vault, or Azure network controls show behavior consistent with attempted or suspected UniFi OS control-plane compromise.
· Support correlation between upstream UniFi OS exploit-path activity and downstream Azure activity such as network security group modification, route modification, firewall or WAF change, DNS change, unusual identity use, Key Vault access, VM command execution, backup access, storage access, outbound communication, or access from newly observed sources.
· Preserve separation between Azure-observed suspicious behavior and confirmed UniFi OS compromise by requiring supporting UniFi OS, endpoint, administrator, network, configuration, or incident-response evidence.
· This rule does not prove successful UniFi OS exploitation, command execution, root compromise, credential theft, data exfiltration, downstream infrastructure compromise, or actor attribution without supporting telemetry and investigation evidence.
Detection Logic
· Identify Azure-hosted UniFi OS assets, reverse proxies, management interfaces, Application Gateway listeners, Front Door routes, WAF-protected paths, Azure VMs, network security groups, route tables, Azure DNS records, storage accounts, Key Vaults, and related Azure network components using resource tags, CMDB records, Azure Resource Graph, resource names, or local enrichment.
· Detect management-plane access to Azure-hosted or Azure-fronted UniFi infrastructure from unfamiliar source IPs, suspicious ASNs, hosting providers, residential proxy ranges, unusual geographies, VPN paths outside approved administration baselines, newly observed internal sources, or unmanaged systems.
· Detect request-path or WAF-visible behavior involving authentication-validation paths, traversal-style path construction, encoded path variations, update endpoints, package-management endpoints, unexpected file-access paths, or request-normalization mismatch indicators where Azure-hosted ingress telemetry exposes those fields.
· Detect follow-on Azure activity involving network security group rule changes, route changes, DNS changes, Azure Firewall changes, WAF policy changes, unusual Entra ID activity, managed identity activity, VM Run Command use, Key Vault access, backup access, snapshot access, storage access, configuration export behavior, or abnormal outbound communication from Azure-hosted UniFi systems.
· Increase confidence when suspicious management-plane access is followed by Azure Activity events, Defender alerts, unusual DNS queries, rare outbound NSG flow destinations, Key Vault access, VM command execution, or endpoint-visible process behavior on Azure VM-hosted UniFi systems.
· Reduce severity when activity aligns with approved administrator access, approved maintenance windows, approved deployment automation, patching, backup workflows, vulnerability scanning, security testing, vendor support, monitoring, or incident-response activity.
· Do not attribute Azure-only events to UniFi OS exploitation unless there is reliable linkage to UniFi OS management-plane activity, UniFi OS assets, administrator context, endpoint evidence, configuration-change evidence, or incident-response validation.
· Do not treat internet exposure, scanner output, isolated Application Gateway or WAF events, ordinary Azure Activity events, or expected Azure automation as UniFi OS compromise evidence by itself.
Required Telemetry
· Azure Activity logs.
· Entra ID sign-in logs.
· Entra ID audit logs.
· NSG flow logs where available.
· Azure Firewall logs where available.
· Application Gateway access logs where available.
· Azure Front Door logs where available.
· WAF logs where available.
· Azure Monitor logs.
· Microsoft Sentinel incidents or analytics output where applicable.
· Microsoft Defender for Cloud alerts.
· Defender for Endpoint telemetry on Azure-hosted UniFi systems where available.
· Azure VM Run Command or guest-management telemetry where available.
· Key Vault diagnostic logs where applicable.
· Storage access logs where applicable.
· Backup or Recovery Services Vault logs where applicable.
· Forwarded UniFi OS logs where available.
· Source IP.
· Destination IP.
· Destination hostname.
· Azure tenant ID.
· Azure subscription ID.
· Azure resource group.
· Azure region.
· Virtual network ID.
· Subnet ID.
· VM resource ID.
· Network security group ID.
· Route table ID.
· Firewall policy ID where applicable.
· Application Gateway or Front Door resource ID where applicable.
· Managed identity or service principal.
· User principal name where available.
· User agent where available.
· Request path where available.
· Response status where available.
· Event timestamp.
· UniFi OS Azure asset tags or local enrichment.
· Approved administrator source enrichment.
· Approved Azure automation enrichment.
· Approved change-window enrichment.
· Incident-response exception enrichment.
Engineering Implementation Instructions
· Validate which UniFi OS components are Azure-hosted, Azure-fronted, or forwarding telemetry into Azure or Microsoft Sentinel before enabling this rule.
· Build or validate resource tags, Azure Resource Graph queries, CMDB records, or enrichment fields that identify Azure-hosted UniFi OS Server deployments, reverse proxies, management interfaces, Azure VMs, Application Gateway resources, Front Door resources, WAF policies, network security groups, route tables, Azure DNS records, Key Vaults, storage accounts, and related virtual network components.
· Validate Azure Activity log collection, Entra ID sign-in and audit log collection, NSG flow log scope, Azure Firewall logging, Application Gateway logging, Front Door logging, WAF logging, Azure Monitor workspace coverage, Microsoft Defender for Cloud coverage, Defender for Endpoint telemetry on Azure VMs where available, Key Vault diagnostic logging, storage logging, backup logging, and forwarded UniFi OS log availability.
· Build approved administrator source baselines covering administrator IPs, VPN ranges, jump hosts, privileged access workstations, management networks, vendor-support paths, vulnerability management systems, security-testing systems, and incident-response systems.
· Build approved Azure automation baselines covering infrastructure-as-code pipelines, deployment identities, automation accounts, managed identities, patch-management workflows, backup roles, monitoring identities, incident-response roles, and expected service principals.
· Build enrichment that maps Azure resource identifiers to UniFi OS asset roles and management-plane functions.
· Treat Azure Activity and Defender detections as candidate-event sources for Azure control-plane activity, not as complete UniFi OS compromise correlation by themselves.
· Use Microsoft Sentinel, Log Analytics, Defender XDR, Azure Monitor, Azure Resource Graph, or another backend workflow to correlate suspicious Azure-hosted UniFi management access with follow-on Azure activity.
· Use bounded correlation windows between suspicious Azure-hosted UniFi management access and follow-on Azure activity.
· Use separate analytic outcomes for suspicious Azure-hosted management access, suspected UniFi OS exploit-path activity, suspicious Azure network-control change, suspicious identity or Key Vault activity, suspicious outbound communication, and confirmed compromise.
· Use Azure Activity, Entra ID audit logs, Azure Resource Graph, Defender alerts, and change-management records to validate whether NSG, route, DNS, identity, WAF, backup, storage, or Key Vault changes align with approved change records.
· Use NSG flow logs, DNS logs, Application Gateway logs, WAF logs, forwarded UniFi OS logs, and endpoint telemetry to determine whether outbound or follow-on behavior is tied to Azure-hosted UniFi systems.
· Confirm local normalized-table field mappings for ResourceId, request path, source IP, destination IP, hostname, caller identity, approved-source status, approved-change status, UniFi asset status, and suspected UniFi asset status before enabling the KQL pattern.
· Do not enable alert mode until tenant scope, subscription scope, workspace coverage, log delivery, resource tagging, identity mapping, source baselines, automation exceptions, change-management integration, normalized correlation data, and query performance are validated.
DRI Assessment
DRI
7.7 / 10
· The rule is behaviorally anchored to suspicious access to Azure-hosted or Azure-fronted UniFi management infrastructure followed by Azure-observable network, identity, configuration, or outbound behavior rather than static CVE identifiers, proof-of-concept names, IP addresses, hashes, or actor infrastructure.
· The rule remains useful if an adversary changes source infrastructure, request timing, user agent, Azure resource target, outbound destination, or follow-on sequence.
· The score is supported by durable cloud-observable signals such as management access anomalies, network security group changes, route changes, Entra ID activity, Key Vault access, DNS changes, NSG flow anomalies, Azure Activity events, Defender alerts, and Azure VM endpoint behavior where available.
· The score is constrained by Azure-only visibility, incomplete UniFi OS log forwarding, missing request paths, weak resource tagging, legitimate automation noise, cross-subscription complexity, and incomplete change-management context.
· The rule is durable as a conditional downstream cloud-impact detector but should not be treated as direct proof of UniFi OS exploitation.
TCR Assessment
Operational TCR
7.0 / 10
Full-Telemetry TCR
8.3 / 10
· Operational confidence depends on whether UniFi OS management infrastructure is Azure-hosted or Azure-fronted, whether relevant logs are enabled, whether Azure resources are correctly tagged, and whether identity and change-management context is available.
· Operational confidence is reduced where UniFi OS is appliance-only, not Azure-hosted, not Azure-fronted, or not forwarding logs into Azure or the detection backend.
· Operational confidence is reduced where Azure automation frequently modifies network security groups, DNS records, WAF policies, routes, backups, storage objects, Key Vault access policies, or identity permissions.
· Full-telemetry confidence improves when Azure telemetry correlates with UniFi OS logs, endpoint telemetry on Azure VMs, administrator activity, forwarded application logs, reverse-proxy logs, change-management records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support conditional cloud-impact triage rather than standalone confirmation of UniFi OS exploit success.
Limitations
· This rule applies only when UniFi OS infrastructure is Azure-hosted, Azure-fronted, or meaningfully integrated with Azure logging and identity workflows.
· Azure-native telemetry does not directly prove UniFi OS exploitation unless linked to UniFi OS management-plane activity, endpoint behavior, administrator activity, configuration evidence, or incident-response findings.
· Missing Azure Activity logs, Entra ID logs, NSG flow logs, Azure Firewall logs, Application Gateway logs, WAF logs, Azure Monitor logs, Defender telemetry, Key Vault logs, storage logs, backup logs, endpoint telemetry, resource graph context, or resource tags can reduce confidence.
· Approved Azure automation, infrastructure-as-code deployments, backup workflows, patching, security testing, vendor support, monitoring, and incident response can produce similar cloud-side changes.
· The rule may miss exploitation that affects UniFi OS appliances outside Azure visibility or does not produce Azure-observable follow-on behavior.
· The KQL pattern assumes local normalization or enrichment fields exist; customers must map or replace those fields before deployment.
· The rule should not be used to infer root compromise, credential theft, data exfiltration, downstream compromise, or actor attribution without supporting evidence.
Detection Query Pattern
Azure conditional detection pattern for Azure-hosted UniFi OS management access followed by suspicious cloud or network follow-on behavior. The Log Analytics pattern identifies normalized Azure-hosted UniFi management-ingress events and high-risk Azure control-plane candidate events. Final correlation requires local tenant, subscription, workspace, log-source, resource-tag, identity, enrichment, exception, normalized-log, and timing-window validation.
let timeframe = 24h;
let suspicious_window = 10m;
let AzureHighRiskActions = dynamic([
"Microsoft.Network/networkSecurityGroups/securityRules/write",
"Microsoft.Network/networkSecurityGroups/securityRules/delete",
"Microsoft.Network/routeTables/routes/write",
"Microsoft.Network/routeTables/routes/delete",
"Microsoft.Network/dnsZones/write",
"Microsoft.Network/dnsZones/delete",
"Microsoft.Network/applicationGateways/write",
"Microsoft.Network/frontDoors/write",
"Microsoft.Network/frontdoorWebApplicationFirewallPolicies/write",
"Microsoft.KeyVault/vaults/secrets/read",
"Microsoft.KeyVault/vaults/accessPolicies/write",
"Microsoft.Compute/virtualMachines/runCommand/action",
"Microsoft.Authorization/roleAssignments/write",
"Microsoft.Authorization/roleDefinitions/write",
"Microsoft.Storage/storageAccounts/listKeys/action",
"Microsoft.RecoveryServices/vaults/backupJobs/write"
]);
let UniFiIngressEvents =
NormalizedNetworkEvents
| where TimeGenerated > ago(timeframe)
| extend CorrelationResourceId = tostring(column_ifexists("ResourceId", column_ifexists("resource_id", "")))
| extend request_path = tostring(column_ifexists("request_path", ""))
| extend src_ip = tostring(column_ifexists("src_ip", column_ifexists("SourceIp", "")))
| extend dst_ip = tostring(column_ifexists("dst_ip", column_ifexists("DestinationIp", "")))
| extend host = tostring(column_ifexists("host", column_ifexists("HostName", "")))
| extend local_unifi_asset = tostring(column_ifexists("local_unifi_asset", "false"))
| extend local_unifi_management_path = tostring(column_ifexists("local_unifi_management_path", "false"))
| extend local_approved_change = tostring(column_ifexists("local_approved_change", "false"))
| extend local_approved_admin_source = tostring(column_ifexists("local_approved_admin_source", "false"))
| where isnotempty(CorrelationResourceId)
| where local_unifi_asset =~ "true"
| where local_approved_change !~ "true"
| where local_approved_admin_source !~ "true"
| where local_unifi_management_path =~ "true"
or request_path has_any ("update", "package", "auth", "validate", "traversal", "%2e%2e")
or request_path matches regex @"\.\."
| project IngressTime = TimeGenerated, CorrelationResourceId, src_ip, dst_ip, host, request_path;
let AzureFollowOnEvents =
AzureActivity
| where TimeGenerated > ago(timeframe)
| extend CorrelationResourceId = tostring(ResourceId)
| extend local_unifi_asset = tostring(column_ifexists("local_unifi_asset", "false"))
| extend local_unifi_suspect_asset = tostring(column_ifexists("local_unifi_suspect_asset", "false"))
| extend local_approved_change = tostring(column_ifexists("local_approved_change", "false"))
| where isnotempty(CorrelationResourceId)
| where OperationNameValue in~ (AzureHighRiskActions)
| where local_approved_change !~ "true"
| where local_unifi_asset =~ "true" or local_unifi_suspect_asset =~ "true"
| project FollowOnTime = TimeGenerated, CorrelationResourceId, OperationNameValue, Caller, CallerIpAddress, SubscriptionId, ResourceGroup, ResourceId;
UniFiIngressEvents
| join kind=inner AzureFollowOnEvents on CorrelationResourceId
| where FollowOnTime between (IngressTime .. IngressTime + suspicious_window)
| summarize event_count=count(), distinct_azure_actions=dcount(OperationNameValue), distinct_callers=dcount(Caller) by bin(IngressTime, 10m), src_ip, dst_ip, host, Caller, CallerIpAddress, SubscriptionId, ResourceGroup, ResourceId
| where event_count >= ENV_UNIFI_AZURE_EVENT_THRESHOLD or distinct_azure_actions >= ENV_UNIFI_AZURE_ACTION_THRESHOLD
| sort by event_count desc
Rule
Azure Identity, Key Vault, or Network Control Activity Near Suspected UniFi OS Compromise
Rule Format
Azure conditional correlation rule template suitable for Azure Activity logs, Entra ID sign-in logs, Entra ID audit logs, Key Vault diagnostic logs, Defender alerts, NSG flow logs, Azure Firewall logs, Azure Monitor logs, storage logs, backup logs, and forwarded UniFi OS or reverse-proxy telemetry after local workspace validation, identity mapping, resource-tag validation, UniFi OS asset correlation, exception validation, and Sentinel or backend correlation.
Detection Purpose
· Detect Azure identity, Key Vault, VM command, backup, storage, DNS, WAF, network security group, route, or network-control activity occurring near suspected UniFi OS compromise activity.
· Identify cases where access to Azure-connected infrastructure may be affected by compromised UniFi management paths, exposed management hosts, administrator credential misuse, or downstream network-control changes.
· Support conditional cloud-impact triage when suspected UniFi OS compromise overlaps with Azure identity, Key Vault, network, backup, storage, or management-control events.
· Preserve separation between Azure activity and UniFi OS compromise by requiring reliable upstream linkage to UniFi OS suspicious activity, Azure-hosted UniFi assets, administrator context, or incident-response evidence.
· This rule does not prove UniFi OS exploitation, Azure compromise, credential theft, data exfiltration, root compromise, or actor attribution without supporting evidence.
Detection Logic
· Identify suspected UniFi OS compromise candidates from forwarded UniFi OS logs, reverse-proxy logs, WAF logs, Application Gateway logs, Front Door logs, Azure Monitor logs, Sentinel detections, endpoint telemetry, incident-response tags, or locally enriched suspect asset markers.
· Identify Azure activity involving role assignment changes, role definition changes, unusual sign-ins, managed identity activity, Key Vault secret access, Key Vault access policy changes, VM Run Command use, backup activity, storage key access, storage object access, DNS changes, WAF changes, NSG changes, route changes, or Azure Firewall policy changes.
· Correlate Azure activity with suspected UniFi OS compromise candidates using shared resource tags, source IPs, administrator identities, Entra ID users, service principals, managed identities, management jump hosts, virtual network context, subnet context, reverse-proxy paths, forwarded UniFi OS logs, or incident-response case identifiers.
· Increase confidence when Azure activity occurs from newly observed sources, unfamiliar administrators, suspicious user agents, unusual geographies, unusual ASNs, non-standard access paths, or identities not normally associated with UniFi administration.
· Increase confidence when Azure activity expands remote access, weakens network controls, accesses Key Vault secrets, exports backups, modifies DNS, modifies WAF policies, creates or modifies role assignments, uses VM Run Command, accesses storage keys, or accesses sensitive storage near suspected UniFi OS activity.
· Reduce severity when activity aligns with approved infrastructure-as-code, approved deployment automation, scheduled backups, patching, disaster recovery tests, security testing, vendor support, monitoring, or incident response.
· Do not attribute Azure identity, Key Vault, backup, storage, or network-control activity to UniFi OS compromise without upstream UniFi OS suspicious activity, Azure-hosted UniFi asset context, shared administrator context, or incident-response validation.
· Do not treat ordinary Azure Activity noise or expected Azure automation as cloud-impact evidence.
Required Telemetry
· Azure Activity logs.
· Entra ID sign-in logs.
· Entra ID audit logs.
· Managed identity activity where available.
· Key Vault diagnostic logs.
· Azure VM Run Command telemetry where available.
· Microsoft Defender for Cloud alerts.
· Defender for Endpoint telemetry where available.
· NSG flow logs.
· Azure Firewall logs where available.
· Application Gateway logs where available.
· Front Door logs where available.
· WAF logs where available.
· Azure Monitor logs.
· Storage access logs where applicable.
· Backup or Recovery Services Vault logs where applicable.
· Forwarded UniFi OS or reverse-proxy logs where available.
· Azure tenant ID.
· Azure subscription ID.
· Azure resource group.
· Azure region.
· User principal name.
· Service principal ID where applicable.
· Managed identity ID where applicable.
· Source IP.
· User agent.
· Resource ID.
· VM resource ID where applicable.
· Virtual network ID.
· Subnet ID.
· Network security group ID.
· Route table ID.
· Key Vault name where applicable.
· Secret name where applicable.
· Storage account where applicable.
· Event timestamp.
· UniFi OS suspected compromise enrichment.
· UniFi OS Azure asset enrichment.
· Administrator identity mapping.
· Approved automation enrichment.
· Approved change enrichment.
· Incident-response case enrichment.
Engineering Implementation Instructions
· Validate whether Azure is in scope for the UniFi OS deployment before enabling this rule.
· Build suspected UniFi OS compromise enrichment from upstream S25 detections, forwarded UniFi OS logs, reverse-proxy logs, WAF logs, Application Gateway logs, Front Door logs, Azure VM endpoint telemetry, Sentinel case tags, or incident-response tags.
· Build Azure resource enrichment linking Azure VMs, Application Gateway resources, Front Door routes, WAF policies, DNS zones, NSGs, route tables, virtual networks, subnets, managed identities, Key Vaults, storage accounts, backup vaults, and monitoring resources to UniFi OS management-plane functions where applicable.
· Build identity mapping between UniFi administrators, Entra ID users, service principals, managed identities, privileged access workstations, jump hosts, VPN users, VM Run Command users, and incident-response users.
· Build approved automation exceptions for infrastructure-as-code, deployment pipelines, patch-management workflows, backup jobs, monitoring systems, security testing, disaster recovery tests, vendor support, and incident-response roles.
· Use bounded time windows around suspected UniFi OS activity to correlate Azure identity, Key Vault, backup, storage, network, DNS, WAF, and VM command actions.
· Treat Azure Activity and Defender detections as high-risk Azure activity selectors, not as proof that Azure activity is related to UniFi OS compromise.
· Use Microsoft Sentinel, Log Analytics over normalized tables, Defender XDR, Azure Monitor, Azure Resource Graph, or backend workflow logic to perform final correlation.
· Use Azure Activity, Entra ID audit logs, Defender alerts, NSG flow logs, Azure Firewall logs, Azure Monitor logs, and Key Vault logs to separate suspicious cloud activity from expected automation.
· Use separate analytic outcomes for suspected UniFi OS compromise, suspected Azure identity impact, suspected Key Vault exposure, suspected network-control change, suspected backup or storage access, and confirmed cloud impact.
· Validate local operation names because Azure provider operation strings and diagnostic-table mappings may vary by tenant, resource provider, connector, and logging path.
· Do not enable alert mode until tenant scope, subscription scope, workspace coverage, Azure Activity coverage, Entra ID log coverage, identity mapping, resource enrichment, source baselines, automation exceptions, change-management integration, normalized correlation data, and query performance are validated.
DRI Assessment
DRI
7.5 / 10
· The rule is behaviorally anchored to Azure identity, Key Vault, network-control, backup, storage, DNS, WAF, VM command, and cloud-management behavior occurring near suspected UniFi OS compromise rather than static CVE identifiers, IP addresses, hashes, tool names, or actor infrastructure.
· The rule remains useful if an adversary changes source infrastructure, identity, user agent, Azure service target, access method, or timing.
· The score is supported by durable cloud-control-plane behaviors such as NSG changes, route changes, role assignments, Key Vault access, VM Run Command use, DNS changes, WAF changes, backup activity, and storage access.
· The score is constrained by the conditional nature of Azure visibility, legitimate automation, incomplete linkage to UniFi OS assets, cross-subscription complexity, incomplete diagnostic logging, and weak identity mapping.
· The rule is durable as conditional cloud-impact correlation but should not be treated as direct UniFi OS exploit detection.
TCR Assessment
Operational TCR
6.8 / 10
Full-Telemetry TCR
8.2 / 10
· Operational confidence depends on upstream UniFi OS suspicion quality, Azure logging completeness, resource tagging, identity mapping, change-management context, Defender coverage, diagnostic log coverage, and automation exception quality.
· Operational confidence is reduced where UniFi OS is not Azure-hosted, not Azure-fronted, or not connected to Azure identity, logging, backup, storage, or network-control workflows.
· Operational confidence is reduced where Azure automation, infrastructure-as-code, scheduled backup workflows, patching, monitoring, and security testing frequently produce similar events.
· Full-telemetry confidence improves when Azure telemetry is correlated with UniFi OS logs, reverse-proxy logs, endpoint telemetry, administrator activity, network telemetry, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support conditional cloud-impact triage rather than standalone confirmation of Azure compromise or UniFi OS exploit success.
Limitations
· This rule is conditional and applies only when Azure services are relevant to the UniFi OS deployment, management path, logging path, identity path, backup path, or downstream infrastructure.
· Azure activity near suspected UniFi OS compromise does not automatically mean Azure was compromised.
· Azure-native telemetry cannot prove UniFi OS exploitation without upstream UniFi OS, endpoint, administrator, network, configuration, or incident-response evidence.
· Missing Entra ID logs, Azure Activity logs, diagnostic logs, NSG flow logs, Azure Firewall logs, Application Gateway logs, WAF logs, Key Vault logs, weak resource tagging, weak identity mapping, and incomplete change-management records can reduce confidence.
· Approved infrastructure-as-code, automation, backup jobs, security testing, monitoring, vendor support, and incident response can produce similar cloud-side activity.
· Azure operation names and local enrichment fields must be validated before production deployment because tenant schemas, Sentinel connectors, diagnostic settings, and normalized tables may differ.
· The rule should not be used to infer credential theft, data exfiltration, root compromise, downstream compromise, or actor attribution without supporting evidence.
Detection Query Pattern
Azure conditional correlation pattern for identity, Key Vault, VM command, backup, storage, DNS, WAF, or network-control activity near suspected UniFi OS compromise. The Log Analytics pattern identifies high-risk Azure control-plane candidate events only. Final correlation requires local tenant, subscription, workspace, log-source, resource-tag, identity, enrichment, exception, normalized-log, and timing-window validation.
let timeframe = 24h;
let AzureHighRiskActions = dynamic([
"Microsoft.Network/networkSecurityGroups/securityRules/write",
"Microsoft.Network/networkSecurityGroups/securityRules/delete",
"Microsoft.Network/routeTables/routes/write",
"Microsoft.Network/routeTables/routes/delete",
"Microsoft.Network/dnsZones/write",
"Microsoft.Network/dnsZones/delete",
"Microsoft.Network/applicationGateways/write",
"Microsoft.Network/frontDoors/write",
"Microsoft.Network/frontdoorWebApplicationFirewallPolicies/write",
"Microsoft.KeyVault/vaults/secrets/read",
"Microsoft.KeyVault/vaults/accessPolicies/write",
"Microsoft.Compute/virtualMachines/runCommand/action",
"Microsoft.Authorization/roleAssignments/write",
"Microsoft.Authorization/roleDefinitions/write",
"Microsoft.Storage/storageAccounts/listKeys/action",
"Microsoft.RecoveryServices/vaults/backupJobs/write"
]);
AzureActivity
| where TimeGenerated > ago(timeframe)
| extend local_unifi_suspect_asset = tostring(column_ifexists("local_unifi_suspect_asset", "false"))
| extend local_approved_change = tostring(column_ifexists("local_approved_change", "false"))
| where OperationNameValue in~ (AzureHighRiskActions)
| where local_unifi_suspect_asset =~ "true"
| where local_approved_change !~ "true"
| summarize azure_action_count=count(), distinct_azure_actions=dcount(OperationNameValue), distinct_callers=dcount(Caller) by bin(TimeGenerated, 10m), Caller, CallerIpAddress, SubscriptionId, ResourceGroup, ResourceId
| where azure_action_count >= ENV_UNIFI_AZURE_ACTION_THRESHOLD or distinct_azure_actions >= ENV_UNIFI_AZURE_DISTINCT_ACTION_THRESHOLD
| sort by azure_action_count desc
GCP
Detection Viability Assessment
GCP has two rules for this EXP report.
· GCP is conditionally viable for detecting downstream cloud-impact behavior related to UniFi OS control-plane compromise when the affected environment uses GCP-hosted UniFi OS Server infrastructure, GCP-hosted reverse proxies, Google Cloud Load Balancing, Cloud Armor, Cloud DNS, Cloud IAM, Google Cloud networking controls, Google Cloud logging services, backup workflows, storage workflows, or GCP-connected downstream infrastructure.
· GCP does not provide direct native visibility into UniFi OS appliance exploit-path behavior unless UniFi OS management-plane logs, reverse-proxy logs, endpoint telemetry, firewall telemetry, DNS telemetry, or configuration-change telemetry are collected from GCP-hosted systems or forwarded into Cloud Logging, Security Command Center, Chronicle, BigQuery, or another detection backend.
· GCP detection should focus on cloud-observable follow-on behavior, including suspicious access to GCP-hosted UniFi management infrastructure, firewall rule changes, route changes, DNS changes, Cloud Armor changes, IAM activity, service account activity, Secret Manager access, Compute Engine guest-management activity, backup or storage access, and outbound communication from GCP-hosted UniFi systems.
· GCP detection must not claim direct proof of UniFi OS exploitation from GCP-native telemetry alone unless upstream UniFi OS exploit-path activity, endpoint evidence, administrator activity, configuration evidence, or incident-response evidence is also present.
· GCP rules must separate direct GCP visibility from conditional downstream correlation so that cloud-only anomalies are not incorrectly attributed to UniFi OS compromise.
· GCP detection is strongest when Cloud Audit Logs, VPC Flow Logs, Cloud DNS logs, Cloud Load Balancing logs, Cloud Armor logs, Cloud Logging, Security Command Center findings, Compute Engine guest telemetry where available, Secret Manager audit logs, Cloud Storage audit logs, backup logs, IAM policy-change telemetry, service account activity, and forwarded UniFi OS logs can be correlated.
· GCP should not infer command execution, root compromise, downstream network compromise, credential theft, data exfiltration, or actor attribution without supporting UniFi OS, endpoint, identity, network, configuration, or incident-response evidence.
Rule
GCP-Hosted UniFi OS Management Access Followed by Suspicious Cloud or Network Follow-On Behavior
Rule Format
GCP conditional correlation rule template suitable for Cloud Audit Logs, VPC Flow Logs, Cloud DNS logs, Cloud Load Balancing logs, Cloud Armor logs, Cloud Logging, Security Command Center findings, Compute Engine telemetry where available, Secret Manager audit logs, Cloud Storage audit logs, backup logs, forwarded UniFi OS logs where available, and BigQuery, Chronicle, Cloud Logging, or SIEM correlation after local project validation, normalized-table validation, resource-label validation, management-path validation, identity mapping, network mapping, exception validation, and backend correlation.
Detection Purpose
· Detect suspicious access to GCP-hosted or GCP-fronted UniFi OS management infrastructure followed by cloud-observable follow-on behavior.
· Identify cases where GCP-hosted management paths, reverse proxies, Compute Engine-hosted UniFi OS Server deployments, external load balancer front ends, Cloud Armor-protected paths, firewall rules, routes, Cloud DNS, Cloud IAM, service accounts, Secret Manager, Cloud Storage, or GCP network controls show behavior consistent with attempted or suspected UniFi OS control-plane compromise.
· Support correlation between upstream UniFi OS exploit-path activity and downstream GCP activity such as firewall rule modification, route modification, Cloud Armor policy change, DNS change, unusual IAM use, service account activity, Secret Manager access, storage access, backup access, outbound communication, or access from newly observed sources.
· Preserve separation between GCP-observed suspicious behavior and confirmed UniFi OS compromise by requiring supporting UniFi OS, endpoint, administrator, network, configuration, or incident-response evidence.
· This rule does not prove successful UniFi OS exploitation, command execution, root compromise, credential theft, data exfiltration, downstream infrastructure compromise, or actor attribution without supporting telemetry and investigation evidence.
Detection Logic
· Identify GCP-hosted UniFi OS assets, reverse proxies, management interfaces, load balancers, Cloud Armor-protected paths, Compute Engine instances, firewall rules, routes, Cloud DNS records, Cloud Storage buckets, Secret Manager secrets, and related GCP network components using resource labels, asset inventory, CMDB records, resource names, or local enrichment.
· Detect management-plane access to GCP-hosted or GCP-fronted UniFi infrastructure from unfamiliar source IPs, suspicious ASNs, hosting providers, residential proxy ranges, unusual geographies, VPN paths outside approved administration baselines, newly observed internal sources, or unmanaged systems.
· Detect request-path or Cloud Armor-visible behavior involving authentication-validation paths, traversal-style path construction, encoded path variations, update endpoints, package-management endpoints, unexpected file-access paths, or request-normalization mismatch indicators where GCP-hosted ingress telemetry exposes those fields.
· Detect follow-on GCP activity involving firewall rule changes, route changes, DNS changes, Cloud Armor changes, unusual IAM activity, service account key activity, service account impersonation, Secret Manager access, storage access, backup access, snapshot access, configuration export behavior, or abnormal outbound communication from GCP-hosted UniFi systems.
· Increase confidence when suspicious management-plane access is followed by Cloud Audit Logs events, Security Command Center findings, unusual DNS queries, rare outbound VPC Flow Log destinations, Secret Manager access, service account activity, or endpoint-visible process behavior on Compute Engine-hosted UniFi systems.
· Reduce severity when activity aligns with approved administrator access, approved maintenance windows, approved deployment automation, patching, backup workflows, vulnerability scanning, security testing, vendor support, monitoring, or incident-response activity.
· Do not attribute GCP-only events to UniFi OS exploitation unless there is reliable linkage to UniFi OS management-plane activity, UniFi OS assets, administrator context, endpoint evidence, configuration-change evidence, or incident-response validation.
· Do not treat internet exposure, scanner output, isolated load balancer or Cloud Armor events, ordinary Cloud Audit Logs activity, or expected GCP automation as UniFi OS compromise evidence by itself.
Required Telemetry
· Cloud Audit Logs.
· IAM policy-change audit events.
· Service account activity events.
· Service account key activity events.
· VPC Flow Logs where available.
· Cloud DNS logs where available.
· Cloud Load Balancing logs where available.
· Cloud Armor logs where available.
· Cloud Logging events.
· Security Command Center findings.
· Compute Engine guest or endpoint telemetry where available.
· OS Config or VM Manager telemetry where available.
· Secret Manager audit logs where applicable.
· Cloud Storage data access logs where applicable.
· Backup and disaster-recovery logs where applicable.
· Forwarded UniFi OS logs where available.
· Source IP.
· Destination IP.
· Destination hostname.
· GCP organization ID.
· GCP folder ID where applicable.
· GCP project ID.
· GCP region.
· GCP zone.
· VPC network.
· Subnet.
· Compute Engine instance ID.
· Load balancer resource ID where applicable.
· Firewall rule ID.
· Route ID.
· Cloud Armor policy ID where applicable.
· IAM principal.
· Service account.
· User agent where available.
· Request path where available.
· Response status where available.
· Event timestamp.
· UniFi OS GCP asset labels or local enrichment.
· Approved administrator source enrichment.
· Approved GCP automation enrichment.
· Approved change-window enrichment.
· Incident-response exception enrichment.
Engineering Implementation Instructions
· Validate which UniFi OS components are GCP-hosted, GCP-fronted, or forwarding telemetry into Cloud Logging, Chronicle, BigQuery, SIEM, or another detection backend before enabling this rule.
· Build or validate resource labels, asset inventory, CMDB records, or enrichment fields that identify GCP-hosted UniFi OS Server deployments, reverse proxies, management interfaces, Compute Engine instances, load balancers, Cloud Armor policies, firewall rules, routes, Cloud DNS records, Secret Manager secrets, Cloud Storage buckets, and related VPC components.
· Validate Cloud Audit Logs collection, data access log scope, VPC Flow Log scope, Cloud DNS logging, Cloud Load Balancing logging, Cloud Armor logging, Cloud Logging routing, Security Command Center coverage, Compute Engine guest telemetry where available, OS Config or VM Manager telemetry where available, Secret Manager audit logging, Cloud Storage audit logging, backup logging, and forwarded UniFi OS log availability.
· Build approved administrator source baselines covering administrator IPs, VPN ranges, jump hosts, privileged access workstations, management networks, vendor-support paths, vulnerability management systems, security-testing systems, and incident-response systems.
· Build approved GCP automation baselines covering infrastructure-as-code pipelines, deployment identities, service accounts, workload identities, patch-management workflows, backup roles, monitoring identities, incident-response roles, and expected Google-managed service accounts.
· Build enrichment that maps GCP resource identifiers to UniFi OS asset roles and management-plane functions.
· Normalize GCP-hosted management-ingress events and GCP follow-on control-plane events into stable correlation fields before enabling the BigQuery pattern.
· Treat Cloud Audit Logs, Cloud Armor logs, Security Command Center findings, and Cloud Logging detections as candidate-event sources for GCP control-plane activity, not as complete UniFi OS compromise correlation by themselves.
· Use Chronicle, BigQuery, Cloud Logging, Security Command Center, SIEM, or another backend workflow to correlate suspicious GCP-hosted UniFi management access with follow-on GCP activity.
· Use bounded correlation windows between suspicious GCP-hosted UniFi management access and follow-on GCP activity.
· Use separate analytic outcomes for suspicious GCP-hosted management access, suspected UniFi OS exploit-path activity, suspicious GCP network-control change, suspicious IAM or Secret Manager activity, suspicious outbound communication, and confirmed compromise.
· Use Cloud Audit Logs, IAM audit events, asset inventory, Security Command Center findings, and change-management records to validate whether firewall, route, DNS, IAM, Cloud Armor, backup, storage, or Secret Manager changes align with approved change records.
· Use VPC Flow Logs, DNS logs, load balancer logs, Cloud Armor logs, forwarded UniFi OS logs, and endpoint telemetry to determine whether outbound or follow-on behavior is tied to GCP-hosted UniFi systems.
· Confirm local normalized-table field mappings for correlation resource ID, request path, source IP, destination IP, hostname, caller identity, approved-source status, approved-change status, UniFi asset status, and suspected UniFi asset status before enabling the query pattern.
· Validate local method names because GCP audit method names and log-export table mappings may vary by organization, project, service, connector, and logging path.
· Do not enable alert mode until organization scope, folder scope, project scope, log routing, log delivery, resource labels, identity mapping, source baselines, automation exceptions, change-management integration, normalized correlation data, method-name validation, and query performance are validated.
DRI Assessment
DRI
7.7 / 10
· The rule is behaviorally anchored to suspicious access to GCP-hosted or GCP-fronted UniFi management infrastructure followed by GCP-observable network, identity, configuration, or outbound behavior rather than static CVE identifiers, proof-of-concept names, IP addresses, hashes, or actor infrastructure.
· The rule remains useful if an adversary changes source infrastructure, request timing, user agent, GCP resource target, outbound destination, or follow-on sequence.
· The score is supported by durable cloud-observable signals such as management access anomalies, firewall rule changes, route changes, IAM activity, service account activity, Secret Manager access, DNS changes, VPC Flow Log anomalies, Cloud Audit Logs events, Security Command Center findings, and Compute Engine endpoint behavior where available.
· The score is constrained by GCP-only visibility, incomplete UniFi OS log forwarding, missing request paths, weak resource labeling, legitimate automation noise, cross-project complexity, and incomplete change-management context.
· The rule is durable as a conditional downstream cloud-impact detector but should not be treated as direct proof of UniFi OS exploitation.
TCR Assessment
Operational TCR
7.0 / 10
Full-Telemetry TCR
8.3 / 10
· Operational confidence depends on whether UniFi OS management infrastructure is GCP-hosted or GCP-fronted, whether relevant logs are enabled, whether GCP resources are correctly labeled, and whether identity and change-management context is available.
· Operational confidence is reduced where UniFi OS is appliance-only, not GCP-hosted, not GCP-fronted, or not forwarding logs into GCP or the detection backend.
· Operational confidence is reduced where GCP automation frequently modifies firewall rules, DNS records, Cloud Armor policies, routes, backups, storage objects, Secret Manager permissions, or IAM permissions.
· Full-telemetry confidence improves when GCP telemetry correlates with UniFi OS logs, endpoint telemetry on Compute Engine instances, administrator activity, forwarded application logs, reverse-proxy logs, change-management records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support conditional cloud-impact triage rather than standalone confirmation of UniFi OS exploit success.
Limitations
· This rule applies only when UniFi OS infrastructure is GCP-hosted, GCP-fronted, or meaningfully integrated with GCP logging and identity workflows.
· GCP-native telemetry does not directly prove UniFi OS exploitation unless linked to UniFi OS management-plane activity, endpoint behavior, administrator activity, configuration evidence, or incident-response findings.
· Missing Cloud Audit Logs, VPC Flow Logs, Cloud DNS logs, Cloud Load Balancing logs, Cloud Armor logs, Cloud Logging events, Security Command Center findings, Compute Engine endpoint telemetry, Secret Manager logs, Cloud Storage logs, backup logs, asset inventory context, or resource labels can reduce confidence.
· Approved GCP automation, infrastructure-as-code deployments, backup workflows, patching, security testing, vendor support, monitoring, and incident response can produce similar cloud-side changes.
· The rule may miss exploitation that affects UniFi OS appliances outside GCP visibility or does not produce GCP-observable follow-on behavior.
· The BigQuery pattern assumes local normalization or enrichment fields exist; customers must map or replace those fields before deployment.
· GCP method names and local enrichment fields must be validated before production deployment because organization schemas, log exports, Chronicle parsers, diagnostic settings, and normalized tables may differ.
· The rule should not be used to infer root compromise, credential theft, data exfiltration, downstream compromise, or actor attribution without supporting evidence.
Detection Query Pattern
GCP conditional detection pattern for GCP-hosted UniFi OS management access followed by suspicious cloud or network follow-on behavior. The BigQuery pattern identifies normalized GCP-hosted UniFi management-ingress events and normalized high-risk GCP control-plane candidate events. Final correlation requires local organization, folder, project, dataset, log-source, resource-label, identity, enrichment, exception, normalized-log, method-name, and timing-window validation.
DECLARE timeframe_hours INT64 DEFAULT 24;
DECLARE suspicious_window_minutes INT64 DEFAULT 10;
WITH gcp_high_risk_actions AS (
SELECT action FROM UNNEST([
"compute.firewalls.insert",
"compute.firewalls.patch",
"compute.firewalls.update",
"compute.firewalls.delete",
"compute.routes.insert",
"compute.routes.patch",
"compute.routes.delete",
"dns.changes.create",
"compute.securityPolicies.insert",
"compute.securityPolicies.patch",
"compute.securityPolicies.update",
"compute.securityPolicies.delete",
"setIamPolicy",
"iam.serviceAccounts.actAs",
"iam.serviceAccountKeys.create",
"iam.serviceAccountKeys.delete",
"secretmanager.versions.access",
"storage.objects.get",
"storage.objects.create",
"compute.instances.setMetadata"
]) AS action
),
unifi_ingress_events AS (
SELECT
event_timestamp AS ingress_time,
correlation_resource_id,
src_ip,
dst_ip,
host,
request_path
FROM `ENV_PROJECT.ENV_DATASET.normalized_unifi_gcp_ingress_events`
WHERE event_timestamp >= TIMESTAMP_SUB(CURRENT_TIMESTAMP(), INTERVAL timeframe_hours HOUR)
AND correlation_resource_id IS NOT NULL
AND correlation_resource_id != ""
AND local_unifi_asset = TRUE
AND local_approved_change != TRUE
AND local_approved_admin_source != TRUE
AND (
local_unifi_management_path = TRUE
OR REGEXP_CONTAINS(LOWER(request_path), r"(update|package|auth|validate|traversal|%2e%2e)")
OR REGEXP_CONTAINS(request_path, r"\.\.")
)
),
gcp_follow_on_events AS (
SELECT
event_timestamp AS follow_on_time,
correlation_resource_id,
method_name,
principal_email,
caller_ip,
project_id,
resource_name
FROM `ENV_PROJECT.ENV_DATASET.normalized_gcp_control_plane_events`
WHERE event_timestamp >= TIMESTAMP_SUB(CURRENT_TIMESTAMP(), INTERVAL timeframe_hours HOUR)
AND correlation_resource_id IS NOT NULL
AND correlation_resource_id != ""
AND method_name IN (SELECT action FROM gcp_high_risk_actions)
AND local_approved_change != TRUE
AND (
local_unifi_asset = TRUE
OR local_unifi_suspect_asset = TRUE
)
)
SELECT
TIMESTAMP_TRUNC(ingress_time, MINUTE) AS detection_window,
src_ip,
dst_ip,
host,
principal_email,
caller_ip,
project_id,
resource_name,
COUNT(*) AS event_count,
COUNT(DISTINCT method_name) AS distinct_gcp_actions
FROM unifi_ingress_events
JOIN gcp_follow_on_events
USING (correlation_resource_id)
WHERE follow_on_time BETWEEN ingress_time AND TIMESTAMP_ADD(ingress_time, INTERVAL suspicious_window_minutes MINUTE)
GROUP BY detection_window, src_ip, dst_ip, host, principal_email, caller_ip, project_id, resource_name
HAVING event_count >= ENV_UNIFI_GCP_EVENT_THRESHOLD
OR distinct_gcp_actions >= ENV_UNIFI_GCP_ACTION_THRESHOLD
ORDER BY event_count DESC;
Rule
GCP IAM, Secret Manager, or Network Control Activity Near Suspected UniFi OS Compromise
Rule Format
GCP conditional correlation rule template suitable for Cloud Audit Logs, IAM audit events, service account activity, Secret Manager audit logs, Security Command Center findings, VPC Flow Logs, Cloud DNS logs, Cloud Armor logs, Cloud Logging events, Cloud Storage audit logs, backup logs, and forwarded UniFi OS or reverse-proxy telemetry after local project validation, identity mapping, resource-label validation, UniFi OS asset correlation, exception validation, and BigQuery, Chronicle, Cloud Logging, SIEM, or backend correlation.
Detection Purpose
· Detect GCP IAM, service account, Secret Manager, storage, backup, DNS, Cloud Armor, firewall, route, or network-control activity occurring near suspected UniFi OS compromise activity.
· Identify cases where access to GCP-connected infrastructure may be affected by compromised UniFi management paths, exposed management hosts, administrator credential misuse, or downstream network-control changes.
· Support conditional cloud-impact triage when suspected UniFi OS compromise overlaps with GCP identity, Secret Manager, network, backup, storage, or management-control events.
· Preserve separation between GCP activity and UniFi OS compromise by requiring reliable upstream linkage to UniFi OS suspicious activity, GCP-hosted UniFi assets, administrator context, or incident-response evidence.
· This rule does not prove UniFi OS exploitation, GCP compromise, credential theft, data exfiltration, root compromise, or actor attribution without supporting evidence.
Detection Logic
· Identify suspected UniFi OS compromise candidates from forwarded UniFi OS logs, reverse-proxy logs, Cloud Armor logs, load balancer logs, Cloud Logging events, Chronicle detections, Security Command Center findings, endpoint telemetry, incident-response tags, or locally enriched suspect asset markers.
· Identify GCP activity involving IAM policy changes, service account impersonation, service account key creation, service account key deletion, Secret Manager access, backup activity, storage object access, Cloud DNS changes, Cloud Armor changes, firewall rule changes, route changes, or Compute Engine metadata and guest-management changes.
· Correlate GCP activity with suspected UniFi OS compromise candidates using shared resource labels, source IPs, administrator identities, IAM principals, service accounts, management jump hosts, VPC context, subnet context, reverse-proxy paths, forwarded UniFi OS logs, or incident-response case identifiers.
· Increase confidence when GCP activity occurs from newly observed sources, unfamiliar administrators, suspicious user agents, unusual geographies, unusual ASNs, non-standard access paths, or identities not normally associated with UniFi administration.
· Increase confidence when GCP activity expands remote access, weakens network controls, accesses Secret Manager secrets, exports backups, modifies DNS, modifies Cloud Armor policies, changes IAM policy, creates service account keys, impersonates service accounts, accesses storage objects, or accesses sensitive storage near suspected UniFi OS activity.
· Reduce severity when activity aligns with approved infrastructure-as-code, approved deployment automation, scheduled backups, patching, disaster recovery tests, security testing, vendor support, monitoring, or incident response.
· Do not attribute GCP IAM, Secret Manager, backup, storage, or network-control activity to UniFi OS compromise without upstream UniFi OS suspicious activity, GCP-hosted UniFi asset context, shared administrator context, or incident-response validation.
· Do not treat ordinary Cloud Audit Logs noise or expected GCP automation as cloud-impact evidence.
Required Telemetry
· Cloud Audit Logs.
· IAM policy-change audit events.
· Service account activity.
· Service account key activity.
· Secret Manager audit logs.
· Security Command Center findings.
· VPC Flow Logs.
· Cloud DNS logs where available.
· Cloud Load Balancing logs where available.
· Cloud Armor logs where available.
· Cloud Logging events.
· Compute Engine guest telemetry where available.
· OS Config or VM Manager telemetry where available.
· Cloud Storage data access logs where applicable.
· Backup and disaster-recovery logs where applicable.
· Forwarded UniFi OS or reverse-proxy logs where available.
· GCP organization ID.
· GCP folder ID where applicable.
· GCP project ID.
· GCP region.
· GCP zone.
· IAM principal.
· Service account.
· Source IP.
· User agent.
· Resource ID.
· Compute Engine instance ID where applicable.
· VPC network.
· Subnet.
· Firewall rule ID.
· Route ID.
· Secret Manager secret name where applicable.
· Cloud Storage bucket where applicable.
· Event timestamp.
· UniFi OS suspected compromise enrichment.
· UniFi OS GCP asset enrichment.
· Administrator identity mapping.
· Approved automation enrichment.
· Approved change enrichment.
· Incident-response case enrichment.
Engineering Implementation Instructions
· Validate whether GCP is in scope for the UniFi OS deployment before enabling this rule.
· Build suspected UniFi OS compromise enrichment from upstream S25 detections, forwarded UniFi OS logs, reverse-proxy logs, Cloud Armor logs, load balancer logs, Compute Engine endpoint telemetry, Chronicle case tags, Security Command Center findings, or incident-response tags.
· Build GCP resource enrichment linking Compute Engine instances, load balancers, Cloud Armor policies, Cloud DNS zones, firewall rules, routes, VPCs, subnets, service accounts, Secret Manager secrets, Cloud Storage buckets, backup resources, and monitoring resources to UniFi OS management-plane functions where applicable.
· Build identity mapping between UniFi administrators, Google identities, IAM principals, service accounts, workload identities, privileged access workstations, jump hosts, VPN users, Compute Engine guest-management users, and incident-response users.
· Build approved automation exceptions for infrastructure-as-code, deployment pipelines, patch-management workflows, backup jobs, monitoring systems, security testing, disaster recovery tests, vendor support, and incident-response roles.
· Use bounded time windows around suspected UniFi OS activity to correlate GCP identity, Secret Manager, backup, storage, network, DNS, Cloud Armor, and Compute Engine management actions.
· Treat Cloud Audit Logs, Cloud Armor events, Security Command Center findings, and Chronicle detections as high-risk GCP activity selectors, not as proof that GCP activity is related to UniFi OS compromise.
· Use Chronicle, BigQuery over normalized log exports, Cloud Logging, Security Command Center, or backend workflow logic to perform final correlation.
· Use Cloud Audit Logs, IAM audit events, Security Command Center findings, VPC Flow Logs, Cloud DNS logs, Cloud Armor logs, Cloud Logging events, and Secret Manager logs to separate suspicious cloud activity from expected automation.
· Use separate analytic outcomes for suspected UniFi OS compromise, suspected GCP identity impact, suspected Secret Manager exposure, suspected network-control change, suspected backup or storage access, and confirmed cloud impact.
· Validate local method names because GCP audit method names and log-export table mappings may vary by project, organization, service, connector, and logging path.
· Do not enable alert mode until organization scope, folder scope, project scope, Cloud Audit Logs coverage, identity mapping, resource enrichment, source baselines, automation exceptions, change-management integration, normalized correlation data, and query performance are validated.
DRI Assessment
DRI
7.5 / 10
· The rule is behaviorally anchored to GCP identity, service account, Secret Manager, network-control, backup, storage, DNS, Cloud Armor, Compute Engine management, and cloud-management behavior occurring near suspected UniFi OS compromise rather than static CVE identifiers, IP addresses, hashes, tool names, or actor infrastructure.
· The rule remains useful if an adversary changes source infrastructure, identity, user agent, GCP service target, access method, or timing.
· The score is supported by durable cloud-control-plane behaviors such as firewall changes, route changes, IAM policy changes, service account impersonation, service account key activity, Secret Manager access, DNS changes, Cloud Armor changes, backup activity, and storage access.
· The score is constrained by the conditional nature of GCP visibility, legitimate automation, incomplete linkage to UniFi OS assets, cross-project complexity, incomplete audit/data-access logging, and weak identity mapping.
· The rule is durable as conditional cloud-impact correlation but should not be treated as direct UniFi OS exploit detection.
TCR Assessment
Operational TCR
6.8 / 10
Full-Telemetry TCR
8.2 / 10
· Operational confidence depends on upstream UniFi OS suspicion quality, GCP logging completeness, resource labeling, identity mapping, change-management context, Security Command Center coverage, audit log coverage, data access log coverage, and automation exception quality.
· Operational confidence is reduced where UniFi OS is not GCP-hosted, not GCP-fronted, or not connected to GCP identity, logging, backup, storage, or network-control workflows.
· Operational confidence is reduced where GCP automation, infrastructure-as-code, scheduled backup workflows, patching, monitoring, and security testing frequently produce similar events.
· Full-telemetry confidence improves when GCP telemetry is correlated with UniFi OS logs, reverse-proxy logs, endpoint telemetry, administrator activity, network telemetry, change-control records, and incident-response evidence.
· Even under full telemetry conditions, this rule should support conditional cloud-impact triage rather than standalone confirmation of GCP compromise or UniFi OS exploit success.
Limitations
· This rule is conditional and applies only when GCP services are relevant to the UniFi OS deployment, management path, logging path, identity path, backup path, or downstream infrastructure.
· GCP activity near suspected UniFi OS compromise does not automatically mean GCP was compromised.
· GCP-native telemetry cannot prove UniFi OS exploitation without upstream UniFi OS, endpoint, administrator, network, configuration, or incident-response evidence.
· Missing Cloud Audit Logs, data access logs, VPC Flow Logs, Cloud DNS logs, Cloud Armor logs, load balancer logs, Security Command Center findings, Secret Manager logs, weak resource labeling, weak identity mapping, and incomplete change-management records can reduce confidence.
· Approved infrastructure-as-code, automation, backup jobs, security testing, monitoring, vendor support, and incident response can produce similar cloud-side activity.
· GCP method names and local enrichment fields must be validated before production deployment because organization schemas, log exports, Chronicle parsers, diagnostic settings, and normalized tables may differ.
· The rule should not be used to infer credential theft, data exfiltration, root compromise, downstream compromise, or actor attribution without supporting evidence.
Detection Query Pattern
GCP conditional correlation pattern for IAM, service account, Secret Manager, backup, storage, DNS, Cloud Armor, or network-control activity near suspected UniFi OS compromise. The BigQuery pattern identifies high-risk GCP control-plane candidate events only. Final correlation requires local organization, folder, project, dataset, log-source, resource-label, identity, enrichment, exception, normalized-log, method-name, and timing-window validation.
DECLARE timeframe_hours INT64 DEFAULT 24;
WITH gcp_high_risk_actions AS (
SELECT action FROM UNNEST([
"compute.firewalls.insert",
"compute.firewalls.patch",
"compute.firewalls.update",
"compute.firewalls.delete",
"compute.routes.insert",
"compute.routes.patch",
"compute.routes.delete",
"dns.changes.create",
"compute.securityPolicies.insert",
"compute.securityPolicies.patch",
"compute.securityPolicies.update",
"compute.securityPolicies.delete",
"setIamPolicy",
"iam.serviceAccounts.actAs",
"iam.serviceAccountKeys.create",
"iam.serviceAccountKeys.delete",
"secretmanager.versions.access",
"storage.objects.get",
"storage.objects.create",
"compute.instances.setMetadata"
]) AS action
)
SELECT
TIMESTAMP_TRUNC(event_timestamp, MINUTE) AS detection_window,
principal_email,
caller_ip,
project_id,
resource_name,
COUNT(*) AS gcp_action_count,
COUNT(DISTINCT method_name) AS distinct_gcp_actions
FROM `ENV_PROJECT.ENV_DATASET.normalized_gcp_control_plane_events`
WHERE event_timestamp >= TIMESTAMP_SUB(CURRENT_TIMESTAMP(), INTERVAL timeframe_hours HOUR)
AND method_name IN (SELECT action FROM gcp_high_risk_actions)
AND local_unifi_suspect_asset = TRUE
AND local_approved_change != TRUE
GROUP BY detection_window, principal_email, caller_ip, project_id, resource_name
HAVING gcp_action_count >= ENV_UNIFI_GCP_ACTION_THRESHOLD
OR distinct_gcp_actions >= ENV_UNIFI_GCP_DISTINCT_ACTION_THRESHOLD
ORDER BY gcp_action_count DESC;
S26 Threat-to-Rule Traceability Matrix
Traceability Purpose
This section maps the UniFi OS control-plane compromise behavior model to the finalized S25 detection-rule inventory. The traceability model is behavior-led and separates suspicious access, suspected exploitation, post-access behavior, downstream control-plane impact, conditional cloud impact, and confirmed compromise. CVE identifiers, proof-of-concept labels, scanner output, internet exposure, isolated WAF events, isolated cloud-control events, and actor naming are not treated as standalone confirmation of compromise.
Primary Threat Behaviors Covered
· Suspicious access to UniFi OS management paths from unfamiliar, newly observed, non-baselined, or suspicious source context.
· Authentication-gateway bypass or management-path access behavior exposed through reverse proxy, ingress, WAF, firewall, web, NDR, SIEM, or forwarded UniFi OS telemetry.
· Traversal-style request construction, encoded traversal indicators, authentication-validation path access, update-path access, package-management path access, unexpected file-access paths, or request-normalization mismatch behavior where telemetry exposes those fields.
· UniFi OS update, package, or service-context activity followed by suspicious process, file, network, configuration, or downstream-control behavior.
· Privileged or service-context execution on UniFi OS Server hosts where endpoint telemetry is available.
· File staging, persistence-oriented host behavior, package-update anomalies, or suspicious local modification activity near UniFi OS service context.
· Downstream network-control change following suspected UniFi OS management-plane exploit-path activity.
· Conditional cloud-control-plane activity near suspected UniFi OS compromise when UniFi infrastructure is cloud-hosted, cloud-fronted, cloud-logged, or meaningfully integrated with cloud identity, logging, backup, storage, or network-control workflows.
· Identity, secret, storage, backup, firewall, route, DNS, WAF, load-balancer, service-account, or network-control activity that requires upstream UniFi OS linkage before being treated as related downstream impact.
NDR / Network Behavioral Analytics Traceability
Rule
Suspicious UniFi OS Management-Plane Access With Exploit-Path Request Behavior
Mapped Threat Behavior
· Suspicious access to UniFi OS management interfaces.
· Exploit-path request behavior involving authentication, validation, traversal, update, package, or file-access paths.
· Newly observed, unfamiliar, non-baselined, or suspicious source context accessing UniFi management infrastructure.
· Request-normalization mismatch or traversal-style path behavior where visible to NDR, reverse proxy, web, WAF, or network analytics telemetry.
Coverage Role
This rule provides direct network-side behavioral coverage for suspicious UniFi OS management-plane access attempts when management ingress telemetry is available.
Coverage Boundary
This rule does not prove successful exploitation, command execution, root compromise, downstream network compromise, credential theft, data exfiltration, or actor attribution by itself. Confirmation requires correlation with host, identity, configuration, cloud, administrative, or incident-response evidence.
Rule
UniFi OS Update or Package Activity Followed by Suspicious Outbound or Downstream Management Behavior
Mapped Threat Behavior
· Suspicious update or package-management activity associated with UniFi OS infrastructure.
· Outbound communication from UniFi systems following management-plane or update-path activity.
· Downstream administrative or management behavior occurring after suspected UniFi OS access.
· Post-access behavior that may indicate attempted expansion from the UniFi control plane.
Coverage Role
This rule provides network-side follow-on behavior coverage after suspected UniFi OS management or update-path activity.
Coverage Boundary
This rule depends on visibility into UniFi OS update paths, outbound communication, and downstream management flows. It should not infer payload execution or compromise success without supporting endpoint, application, configuration, administrative, or incident-response evidence.
Rule
UniFi OS Exploit-Path Activity Followed by Downstream Network-Control Change
Mapped Threat Behavior
· Suspected UniFi OS exploit-path access followed by downstream network-control behavior.
· Configuration, routing, firewall, VLAN, device-management, or network-control changes following suspicious management activity.
· Control-plane trust exposure affecting network infrastructure managed through UniFi.
Coverage Role
This rule provides network-behavior traceability between suspicious UniFi OS management activity and downstream network-control consequences.
Coverage Boundary
This rule requires reliable linkage between suspicious UniFi OS activity and downstream control changes. It does not treat ordinary administrative change, maintenance, automation, scanning, or isolated network-control events as compromise evidence by itself.
SentinelOne Traceability
Rule
UniFi OS Service Context Child Process and Privileged Execution Behavior
Mapped Threat Behavior
· UniFi OS Server service-context process execution.
· Unexpected child process behavior from UniFi-related services.
· Privileged execution activity occurring near suspected management-plane, update-path, or service-context compromise.
· Endpoint-visible behavior consistent with command execution or post-exploitation activity on UniFi OS Server hosts.
Coverage Role
This rule provides endpoint-side behavioral coverage where UniFi OS Server infrastructure is hosted on systems monitored by SentinelOne.
Coverage Boundary
This rule does not apply to appliance-only deployments without endpoint telemetry. It requires local process, service, user, command-line, parent-child, and host-role mapping before alert promotion.
Rule
UniFi OS Update Context File Staging and Persistence-Oriented Host Behavior
Mapped Threat Behavior
· Suspicious file staging near UniFi OS update or package activity.
· Persistence-oriented file or service behavior associated with UniFi OS Server hosts.
· Modification activity that may follow exploitation of update, package, or management-plane paths.
· Endpoint-visible host changes requiring investigation for compromise or unauthorized maintenance.
Coverage Role
This rule provides endpoint-side follow-on behavior coverage for update-path abuse, file staging, persistence-oriented activity, and suspicious local modification around UniFi OS Server infrastructure.
Coverage Boundary
This rule requires local baseline validation for approved updates, maintenance, automation, vendor support, backup workflows, and incident-response activity. It should not infer compromise without supporting UniFi OS, endpoint, network, administrative, or incident-response evidence.
Splunk Traceability
Rule
UniFi OS Management-Plane Exploit-Path Access With Suspicious Source Context
Mapped Threat Behavior
· Suspicious access to UniFi OS management infrastructure.
· Authentication, validation, traversal, update, package, file-access, or management-path request indicators.
· Suspicious source context based on administrator baselines, source reputation, new-source behavior, geolocation, ASN, VPN, hosting-provider, or unmanaged-source enrichment.
· Ingress activity requiring correlation against local management-path and asset inventories.
Coverage Role
This rule provides SIEM-side correlation coverage for suspicious UniFi OS management-plane access using normalized web, proxy, WAF, firewall, forwarded UniFi OS, and enrichment telemetry.
Coverage Boundary
This rule is a correlation-search pattern pending local Splunk index, sourcetype, CIM or local field mapping, macro, lookup, threshold, summary-index, schedule, and exception validation.
Rule
UniFi OS Update or Package Activity Followed by Endpoint or Network Follow-On Behavior
Mapped Threat Behavior
· UniFi OS update or package-path activity.
· Endpoint, network, or outbound follow-on behavior occurring after suspicious UniFi OS activity.
· Correlation between management activity and possible post-exploitation behavior across network and host telemetry.
Coverage Role
This rule provides cross-domain correlation between UniFi OS management or update-path signals and endpoint or network follow-on behavior.
Coverage Boundary
This rule depends on local summary indexes, normalized fields, host-role mapping, endpoint telemetry, network telemetry, and approved-maintenance exceptions.
Rule
UniFi OS Exploit-Path Activity Followed by Downstream Configuration Change
Mapped Threat Behavior
· Suspicious UniFi OS management-plane activity followed by network or infrastructure configuration change.
· Downstream control-plane impact affecting managed devices, firewall policies, routing, DNS, VLANs, access controls, or other network-control artifacts.
· Potential management-plane trust collapse requiring SOC escalation.
Coverage Role
This rule provides Splunk correlation coverage for linking exploit-path activity to downstream configuration or control-plane change.
Coverage Boundary
This rule requires change-management integration, asset-role enrichment, administrator mapping, and local suppression for approved automation, maintenance, scanning, backup, monitoring, vendor support, and incident-response activity.
Elastic Traceability
Rule
UniFi OS Management-Plane Exploit-Path Access With Suspicious Source Context
Mapped Threat Behavior
· Suspicious UniFi OS management-plane access.
· Request-path behavior involving authentication, validation, traversal, update, package, or file-access indicators.
· Suspicious source context based on local enrichments, value lists, transforms, exception lists, and source baselines.
Coverage Role
This rule provides Elastic KQL or EQL detection-template coverage for management-plane exploit-path access when relevant logs are mapped into ECS or local schema.
Coverage Boundary
This rule depends on local Elastic data views, ECS mapping, transforms, enrich policies, value lists, exception lists, and rule-type validation.
Rule
UniFi OS Update or Package Activity Followed by Endpoint or Network Follow-On Behavior
Mapped Threat Behavior
· UniFi OS update or package-path access.
· Endpoint process, file, service, or network follow-on behavior.
· Cross-source sequencing between application, endpoint, network, and enrichment data.
Coverage Role
This rule provides Elastic sequence or transform-backed correlation coverage for suspected update-path abuse followed by suspicious host or network activity.
Coverage Boundary
This rule should not be treated as direct compromise proof without endpoint, UniFi OS, network, administrative, or incident-response evidence. It requires tuning for approved maintenance, vendor support, and automation.
Rule
UniFi OS Exploit-Path Activity Followed by Downstream Configuration Change
Mapped Threat Behavior
· Suspicious UniFi OS access followed by downstream network, identity, DNS, firewall, routing, or control-plane configuration activity.
· Potential transition from management-plane access to infrastructure-control impact.
Coverage Role
This rule provides Elastic correlation coverage for linking suspected UniFi OS exploit-path activity to downstream configuration-change behavior.
Coverage Boundary
This rule requires reliable local correlation identifiers, asset enrichment, configuration-change telemetry, change-management context, and validated exception handling.
QRadar Traceability
Rule
UniFi OS Management-Plane Exploit-Path Access With Suspicious Source Context
Mapped Threat Behavior
· Suspicious access to UniFi OS management paths.
· Exploit-path request indicators visible in web, proxy, WAF, firewall, forwarded UniFi OS, or normalized events.
· Non-baselined source behavior, unusual source context, or suspicious administrative access patterns.
Coverage Role
This rule provides QRadar CRE and building-block coverage for suspicious UniFi OS management-plane access.
Coverage Boundary
This rule requires DSM parsing, custom property validation, reference sets or maps, building blocks, offense tuning, and approved-source exceptions before production use.
Rule
UniFi OS Update or Package Activity Followed by Endpoint or Network Follow-On Behavior
Mapped Threat Behavior
· UniFi OS update or package-path activity.
· Follow-on endpoint or network behavior from UniFi OS Server hosts or management infrastructure.
· Correlation between management-path activity and suspected post-access behavior.
Coverage Role
This rule provides QRadar CRE correlation coverage for UniFi update-path behavior followed by endpoint or network follow-on activity.
Coverage Boundary
This rule depends on parsed custom properties, relevant log sources, endpoint or network telemetry, reference data, and local baseline validation.
Rule
UniFi OS Exploit-Path Activity Followed by Downstream Configuration Change
Mapped Threat Behavior
· UniFi OS exploit-path activity followed by downstream configuration or control-plane change.
· Suspicious changes to network controls, firewall rules, routes, DNS, managed devices, or administrative access paths.
Coverage Role
This rule provides QRadar offense-correlation coverage for potential downstream control-plane impact.
Coverage Boundary
This rule should be tuned against approved change windows, automation accounts, administrative workflows, security testing, monitoring, vendor support, and incident-response actions.
SIGMA Traceability
Rule
UniFi OS Management-Plane Exploit-Path Request Event
Mapped Threat Behavior
· Suspicious UniFi OS management-path request behavior.
· Authentication, validation, traversal, update, package, or file-access request indicators.
· Event-level detection of potentially suspicious management-plane access.
Coverage Role
This rule provides portable event-rule template coverage for backend conversion into supported SIEMs.
Coverage Boundary
This rule does not perform full multi-stage correlation in SIGMA alone. Backend SIEM conversion, local field mapping, enrichment creation, exception handling, and SIEM-native correlation are required.
Rule
UniFi OS Service Context Process Execution or Update Follow-On Event
Mapped Threat Behavior
· UniFi OS service-context process execution.
· Update-path follow-on behavior.
· Endpoint-visible process, file, or service activity associated with suspected UniFi OS Server compromise.
Coverage Role
This rule provides portable SIGMA event-template coverage for host-side follow-on behavior.
Coverage Boundary
This rule requires backend-specific conversion, local field mapping, enrichment creation, exceptions, and SIEM-native correlation to avoid overclaiming compromise based on isolated endpoint events.
Rule
UniFi OS Downstream Configuration Change Event After Suspicious Management Activity
Mapped Threat Behavior
· Downstream configuration change occurring after suspicious UniFi OS management activity.
· Network-control or infrastructure-control events that may indicate downstream impact.
Coverage Role
This rule provides portable event-template coverage for downstream configuration-change events requiring backend correlation.
Coverage Boundary
This rule requires SIEM-native correlation with upstream suspicious UniFi OS activity and local approved-change exceptions.
AWS Traceability
Rule
AWS-Hosted UniFi OS Management Access Followed by Suspicious Cloud or Network Follow-On Behavior
Mapped Threat Behavior
· Suspicious access to AWS-hosted or AWS-fronted UniFi OS management infrastructure.
· AWS-observable follow-on behavior involving security groups, routes, DNS, IAM, secrets, storage, backup, WAF, load balancer, or outbound network activity.
· Conditional downstream cloud-impact behavior requiring upstream UniFi OS linkage.
Coverage Role
This rule provides AWS conditional correlation coverage when UniFi OS infrastructure is AWS-hosted, AWS-fronted, AWS-logged, or integrated with AWS identity, networking, logging, backup, or storage workflows.
Coverage Boundary
This rule does not provide direct UniFi OS appliance exploitation visibility. AWS-only events must not be attributed to UniFi OS compromise without upstream UniFi OS, endpoint, administrator, configuration, change-management, or incident-response evidence.
Rule
AWS IAM, Secrets, or Network Control Activity Near Suspected UniFi OS Compromise
Mapped Threat Behavior
· AWS IAM, Secrets Manager, network-control, storage, backup, DNS, WAF, or management activity occurring near suspected UniFi OS compromise.
· Cloud-control activity that may represent downstream impact from compromised management paths, exposed management hosts, or administrator context.
Coverage Role
This rule provides conditional AWS cloud-impact triage for high-risk AWS activity near suspected UniFi OS compromise.
Coverage Boundary
This rule requires reliable linkage to suspected UniFi OS activity, AWS-hosted UniFi asset context, administrator context, change-management context, or incident-response validation. It should not treat cloud-only anomalies as UniFi OS compromise.
Azure Traceability
Rule
Azure-Hosted UniFi OS Management Access Followed by Suspicious Cloud or Network Follow-On Behavior
Mapped Threat Behavior
· Suspicious access to Azure-hosted or Azure-fronted UniFi OS management infrastructure.
· Azure-observable follow-on behavior involving NSGs, routes, DNS, WAF, Front Door, Application Gateway, Entra ID, managed identities, Key Vault, VM Run Command, storage, backup, or outbound network activity.
· Conditional downstream cloud-impact behavior requiring upstream UniFi OS linkage.
Coverage Role
This rule provides Azure conditional correlation coverage when UniFi OS infrastructure is Azure-hosted, Azure-fronted, Azure-logged, or integrated with Azure identity, networking, logging, backup, storage, or management workflows.
Coverage Boundary
This rule does not provide direct UniFi OS appliance exploitation visibility. Azure-only events must not be attributed to UniFi OS compromise without upstream UniFi OS, endpoint, administrator, configuration, change-management, or incident-response evidence.
Rule
Azure Identity, Key Vault, or Network Control Activity Near Suspected UniFi OS Compromise
Mapped Threat Behavior
· Azure identity, Key Vault, VM command, backup, storage, DNS, WAF, NSG, route, or network-control activity near suspected UniFi OS compromise.
· Cloud-control activity that may represent downstream impact from compromised management paths, exposed management hosts, or administrator credential misuse.
Coverage Role
This rule provides conditional Azure cloud-impact triage for high-risk Azure activity near suspected UniFi OS compromise.
Coverage Boundary
This rule requires upstream UniFi OS suspicious activity, Azure-hosted UniFi asset context, shared administrator context, change-management context, or incident-response validation before attributing activity to UniFi OS compromise.
GCP Traceability
Rule
GCP-Hosted UniFi OS Management Access Followed by Suspicious Cloud or Network Follow-On Behavior
Mapped Threat Behavior
· Suspicious access to GCP-hosted or GCP-fronted UniFi OS management infrastructure.
· GCP-observable follow-on behavior involving firewall rules, routes, DNS, Cloud Armor, IAM, service accounts, Secret Manager, Cloud Storage, backup, Compute Engine metadata, or outbound network activity.
· Conditional downstream cloud-impact behavior requiring upstream UniFi OS linkage.
Coverage Role
This rule provides GCP conditional correlation coverage when UniFi OS infrastructure is GCP-hosted, GCP-fronted, GCP-logged, or integrated with GCP identity, networking, logging, backup, storage, or management workflows.
Coverage Boundary
This rule does not provide direct UniFi OS appliance exploitation visibility. GCP-only events must not be attributed to UniFi OS compromise without upstream UniFi OS, endpoint, administrator, configuration, change-management, or incident-response evidence.
Rule
GCP IAM, Secret Manager, or Network Control Activity Near Suspected UniFi OS Compromise
Mapped Threat Behavior
· GCP IAM, service account, Secret Manager, storage, backup, DNS, Cloud Armor, firewall, route, or network-control activity near suspected UniFi OS compromise.
· Cloud-control activity that may represent downstream impact from compromised management paths, exposed management hosts, or administrator credential misuse.
Coverage Role
This rule provides conditional GCP cloud-impact triage for high-risk GCP activity near suspected UniFi OS compromise.
Coverage Boundary
This rule requires upstream UniFi OS suspicious activity, GCP-hosted UniFi asset context, shared administrator context, change-management context, or incident-response validation before attributing activity to UniFi OS compromise.
Coverage Consolidation
The S25 rule inventory provides direct or conditional traceability across network, endpoint, SIEM, event-template, and cloud-control-plane telemetry. The strongest direct coverage appears in NDR, Splunk, Elastic, QRadar, SentinelOne, and SIGMA where UniFi OS management, endpoint, web, proxy, WAF, network, forwarded application, or configuration telemetry is available. AWS, Azure, and GCP provide conditional downstream cloud-impact coverage only when UniFi OS infrastructure is cloud-hosted, cloud-fronted, cloud-logged, or otherwise integrated with cloud identity, logging, backup, storage, or network-control workflows.
Non-Coverage Conditions
· Appliance-only UniFi OS deployments without forwarded management-plane, network, reverse-proxy, WAF, endpoint, or configuration telemetry may have limited detection coverage.
· Cloud-only identity, storage, network, backup, DNS, WAF, route, firewall, secret-access, or service-account events are not treated as UniFi OS compromise without upstream UniFi OS linkage.
· Scanner output, internet exposure, benign WAF events, isolated failed requests, or isolated administrative changes are not treated as compromise confirmation.
· The rule set does not attribute activity to a specific actor, campaign, tool, exploit kit, or malware family without external evidence.
· The rule set does not prove root compromise, credential theft, data exfiltration, downstream device compromise, durable persistence, or successful exploitation without supporting telemetry and investigation evidence.
Traceability Conclusion
The finalized S25 rule inventory provides broad, behavior-led coverage for the UniFi OS control-plane compromise model. The rules trace suspicious management-plane access, update or package-path behavior, host-side service-context execution, suspicious file or persistence behavior, downstream network-control change, and conditional cloud-control-plane activity to the appropriate telemetry sources. The traceability model preserves a strict distinction between suspicious access, suspected exploitation, post-access behavior, downstream control-plane impact, conditional cloud exposure, and confirmed compromise.
S27 Behavior & Log Artifacts
Purpose
This section identifies the primary behavior and log artifacts that support detection, investigation, triage, and validation for UniFi OS control-plane compromise, authentication-bypass activity, path traversal behavior, package or update-path command execution, service-context execution, privileged host activity, downstream network-control change, and conditional downstream cloud-impact activity.
The artifacts below are behavior-led. They should not be treated as proof of UniFi OS exploitation, command execution, root compromise, credential theft, persistence, data exfiltration, downstream network compromise, AWS compromise, Azure compromise, GCP compromise, or actor attribution unless they are correlated into a coherent sequence.
Primary Artifact Categories
· UniFi OS management-plane access artifacts.
· Authentication, validation, traversal, update, package, and file-access request artifacts.
· Reverse proxy, ingress, WAF, web, firewall, DNS, VPN, proxy, and NDR artifacts.
· UniFi OS Server endpoint, process, service, package, file, outbound communication, and persistence artifacts.
· Downstream network-control, configuration-change, routing, firewall, DNS, VLAN, device-management, and administrative artifacts.
· Cloud-hosted or cloud-fronted UniFi OS artifacts across AWS, Azure, and GCP.
· Conditional cloud-control-plane artifacts involving identity, secrets, storage, backup, network controls, WAF, DNS, routing, load balancing, and administrative configuration.
· Asset, source, session, administrator, resource, change-management, SOAR, incident-response, and enrichment artifacts used for correlation.
UniFi OS Management-Plane Access Artifacts
Relevant Artifacts
Management interface access, source IP, destination IP, destination hostname, virtual host, request path, request method, response status, user agent, session identifier where available, authenticated user where available, administrator identity where available, management path, reverse-proxy route, load balancer route, WAF policy, source ASN, geography, VPN context, administrator source baseline, newly observed source status, approved administrator source status, device or asset role, UniFi OS asset tag, and event timestamp.
Useful Log Sources
· UniFi OS logs where available.
· Reverse proxy logs.
· Web access logs.
· WAF logs.
· Load balancer logs.
· Firewall logs.
· NDR telemetry.
· DNS logs.
· VPN logs.
· Proxy logs.
· SIEM-normalized network telemetry.
· Asset inventory or CMDB records.
· Change-management systems.
· SOAR systems.
· Incident-response case-management systems.
Detection Use
These artifacts support detection when UniFi OS management-plane access is joined with suspicious source context, unusual management-path access, traversal-style request construction, authentication-validation path access, update-path access, package-path access, unexpected file-access paths, non-baselined administrator context, downstream network-control change, endpoint follow-on behavior, or cloud-control-plane activity.
Investigation Use
Investigators should determine whether the management access is expected for the source, administrator, asset, route, VPN path, maintenance window, change ticket, source geography, ASN, user agent, and business context. They should also review whether the access is followed by update activity, package activity, service-context execution, file staging, outbound communication, configuration change, downstream device change, or cloud-control-plane activity.
Non-Coverage Conditions
Management-plane access alone does not prove exploitation. Internet exposure alone does not prove compromise. Scanner traffic alone does not prove compromise. WAF events alone do not prove compromise. These artifacts require correlation with suspicious request behavior, source anomalies, endpoint evidence, configuration-change evidence, administrator context, downstream activity, or incident-response validation before they become compromise-oriented detection evidence.
Authentication, Traversal, Update, Package, and Request-Path Artifacts
Relevant Artifacts
Authentication path, validation path, traversal-style path construction, encoded traversal indicator, decoded path, normalized path, raw path, request-normalization mismatch, update endpoint, package-management endpoint, file-access path, API route, HTTP method, response code, response size, request count, request burst, source IP, destination host, user agent, authenticated user where available, session identifier where available, reverse-proxy header, forwarded-for header, and timestamp.
Useful Log Sources
· UniFi OS application logs where available.
· Reverse proxy logs.
· Web server logs.
· WAF logs.
· Load balancer logs.
· Application Gateway, Front Door, CloudFront, ALB, NLB, or equivalent ingress logs where applicable.
· Cloud Armor logs where applicable.
· Firewall logs.
· NDR telemetry.
· SIEM-normalized web and application telemetry.
Detection Use
These artifacts support detection when traversal-style request construction, encoded traversal, authentication-validation path activity, update-path activity, package-path activity, or unexpected file-access behavior occurs from suspicious sources or is followed by endpoint, outbound, downstream network-control, or cloud-control-plane behavior.
Investigation Use
Investigators should determine whether the request path is expected for legitimate UniFi OS administration, upgrade activity, package management, monitoring, vendor support, vulnerability scanning, or security testing. They should compare raw and normalized request paths where available and determine whether follow-on behavior occurred on the UniFi OS host, downstream network infrastructure, or connected cloud environment.
Non-Coverage Conditions
Traversal-like strings alone are not sufficient. Update-path access alone is not sufficient. Package-path access alone is not sufficient. Authentication-validation path access alone is not sufficient. These artifacts must be correlated with suspicious source context, abnormal request sequence, endpoint behavior, configuration changes, administrator activity, or incident-response evidence.
Endpoint, Process, Service, Package, and File Artifacts
Relevant Artifacts
UniFi OS Server host role, process name, parent process, child process, command line, executable path, service account, service context, privilege context, package manager activity, update process, file creation, file modification, file rename, file permission change, new service, scheduled task or timer where applicable, persistence location, temporary file path, download location, script interpreter, outbound connection, DNS query, destination IP, destination port, binary reputation where available, endpoint detection event, and timestamp.
Useful Log Sources
· EDR telemetry.
· SentinelOne Deep Visibility or STAR telemetry where deployed.
· Defender for Endpoint where deployed.
· Linux audit logs where available.
· Sysmon for Linux where deployed.
· System logs.
· Package manager logs.
· Service manager logs.
· File integrity monitoring.
· Process telemetry.
· Network connection telemetry.
· DNS telemetry.
· SIEM-normalized endpoint telemetry.
Detection Use
These artifacts support detection when UniFi OS service-context activity spawns unexpected child processes, performs suspicious package or update activity, stages files, modifies service or persistence locations, initiates abnormal outbound communication, or coincides with suspicious management-plane access.
Investigation Use
Investigators should determine whether the process, package, service, command line, file path, and outbound behavior align with normal UniFi OS operation, approved upgrade workflows, vendor support, administrator maintenance, backup activity, monitoring, vulnerability management, or incident-response work. They should also review whether host activity occurred after suspicious request-path, management-plane, or downstream-control activity.
Non-Coverage Conditions
Endpoint process activity alone is not sufficient. Package manager activity alone is not sufficient. File staging alone is not sufficient. Service modification alone is not sufficient. These artifacts require correlation with UniFi OS asset role, management-plane activity, update context, administrator context, baseline deviation, or incident-response findings.
Outbound Communication and Network Follow-On Artifacts
Relevant Artifacts
Outbound destination IP, destination domain, destination port, protocol, connection count, connection duration, byte count, DNS query, DNS response, first-seen destination, rare destination status, newly observed egress path, source host, source interface, NAT context, proxy context, firewall decision, NDR risk score where available, and timestamp.
Useful Log Sources
· NDR telemetry.
· Firewall logs.
· Proxy logs.
· DNS logs.
· EDR network telemetry.
· VPC Flow Logs where applicable.
· NSG flow logs where applicable.
· Cloud VPC flow logs where applicable.
· SIEM-normalized network telemetry.
Detection Use
These artifacts support detection when outbound communication from UniFi OS infrastructure follows suspicious management-plane access, traversal-path activity, update or package activity, endpoint process activity, or downstream network-control change.
Investigation Use
Investigators should determine whether outbound destinations, protocols, timing, and volume align with expected UniFi OS operations, updates, telemetry, backup, monitoring, vendor support, or administrative workflows. They should verify whether the outbound activity is tied to UniFi OS service context or another local process.
Non-Coverage Conditions
Outbound communication alone is not sufficient. Rare destination access alone is not sufficient. DNS anomaly alone is not sufficient. These artifacts require correlation with UniFi OS asset context, management-plane activity, endpoint behavior, configuration change, or incident-response evidence.
Downstream Network-Control and Configuration Artifacts
Relevant Artifacts
Configuration change, firewall rule change, route change, DNS change, VLAN change, device adoption change, device management action, administrative account change, controller setting change, backup export, configuration export, device inventory change, managed device state, affected network segment, administrator identity, source IP, change ticket, change window, automation identity, and timestamp.
Useful Log Sources
· UniFi OS configuration logs where available.
· Network device logs.
· Firewall logs.
· DNS logs.
· NAC logs where available.
· Change-management systems.
· Administrator activity logs.
· SIEM-normalized configuration telemetry.
· NDR telemetry.
· Cloud network-control logs where applicable.
Detection Use
These artifacts support detection when downstream network-control changes occur after suspicious UniFi OS management-plane activity, update-path activity, endpoint follow-on behavior, or administrator-source deviation.
Investigation Use
Investigators should determine whether the change was approved, expected, and attributable to a known administrator, automation workflow, vendor-support workflow, maintenance window, or incident-response action. They should also review whether the change expanded access, weakened controls, altered routing, modified DNS, exposed management paths, changed backup behavior, or affected downstream managed devices.
Non-Coverage Conditions
Configuration change alone is not sufficient. Firewall change alone is not sufficient. Route change alone is not sufficient. DNS change alone is not sufficient. These artifacts require upstream UniFi OS suspicious activity, administrator context, change-management context, or incident-response validation.
AWS Downstream Cloud Artifacts
Relevant Artifacts
AWS-hosted UniFi asset context, AWS-fronted management path, ALB or CloudFront request context, WAF event, security group change, route table change, Route 53 change, IAM activity, role assumption, Secrets Manager access, S3 access, snapshot activity, backup activity, CloudTrail event, GuardDuty finding, Security Hub finding, VPC Flow Log entry, principal ARN, account ID, source IP, user agent, resource ARN, and timestamp.
Useful Log Sources
· AWS CloudTrail management events.
· AWS CloudTrail data events where enabled.
· AWS WAF logs.
· ALB or CloudFront logs where applicable.
· VPC Flow Logs.
· Route 53 logs.
· GuardDuty.
· Security Hub.
· AWS Config.
· Secrets Manager logs.
· S3 data events where applicable.
· Backup logs where applicable.
· SIEM-normalized AWS telemetry.
· Forwarded UniFi OS or reverse-proxy telemetry.
Detection Use
These artifacts support downstream AWS cloud-impact detection only when UniFi OS infrastructure is AWS-hosted, AWS-fronted, AWS-logged, or correlated with upstream UniFi OS suspicious activity.
Investigation Use
Investigators should determine whether AWS activity aligns to the same UniFi OS asset, source IP, administrator identity, cloud principal, route, security group, WAF path, load balancer, incident-response case, or change-management record.
Non-Coverage Conditions
AWS activity alone is not sufficient. AWS console access alone is not sufficient. IAM activity alone is not sufficient. Cloud-only anomalies must not be attributed to UniFi OS compromise unless reliable upstream UniFi OS context and resource linkage exist.
Azure Downstream Cloud Artifacts
Relevant Artifacts
Azure-hosted UniFi asset context, Azure-fronted management path, Application Gateway event, Front Door event, WAF event, NSG change, route change, Azure DNS change, Entra ID activity, managed identity activity, Key Vault access, VM Run Command use, Storage access, backup activity, Azure Activity event, Defender for Cloud alert, NSG flow event, resource ID, tenant ID, subscription ID, caller identity, source IP, user agent, and timestamp.
Useful Log Sources
· Azure Activity logs.
· Entra ID sign-in logs.
· Entra ID audit logs.
· Application Gateway logs.
· Front Door logs.
· WAF logs.
· NSG flow logs.
· Azure Firewall logs.
· Key Vault diagnostic logs.
· Storage logs.
· Backup or Recovery Services Vault logs.
· Defender for Cloud.
· Defender for Endpoint where applicable.
· Microsoft Sentinel.
· SIEM-normalized Azure telemetry.
· Forwarded UniFi OS or reverse-proxy telemetry.
Detection Use
These artifacts support downstream Azure cloud-impact detection only when UniFi OS infrastructure is Azure-hosted, Azure-fronted, Azure-logged, or correlated with upstream UniFi OS suspicious activity.
Investigation Use
Investigators should determine whether Azure activity aligns to the same UniFi OS asset, source IP, administrator identity, managed identity, resource ID, subscription, network path, incident-response case, or change-management record.
Non-Coverage Conditions
Azure activity alone is not sufficient. Azure portal access alone is not sufficient. Key Vault access alone is not sufficient. Role assignment alone is not sufficient. Cloud-only anomalies must not be attributed to UniFi OS compromise unless reliable upstream UniFi OS context and resource linkage exist.
GCP Downstream Cloud Artifacts
Relevant Artifacts
GCP-hosted UniFi asset context, GCP-fronted management path, load balancer event, Cloud Armor event, firewall rule change, route change, Cloud DNS change, IAM policy change, service account activity, service account key activity, Secret Manager access, Cloud Storage access, backup activity, Compute Engine metadata change, Cloud Audit Logs event, Security Command Center finding, VPC Flow Log entry, principal email, caller IP, project ID, resource name, organization ID, and timestamp.
Useful Log Sources
· Google Cloud Admin Activity audit logs.
· Google Cloud Data Access audit logs where enabled.
· Cloud IAM logs.
· Service account logs.
· Cloud Armor logs.
· Cloud Load Balancing logs.
· VPC Flow Logs.
· Cloud DNS logs where available.
· Secret Manager logs.
· Cloud Storage logs.
· Security Command Center.
· Cloud Logging.
· Chronicle or SIEM-normalized Google Cloud telemetry.
· Forwarded UniFi OS or reverse-proxy telemetry.
Detection Use
These artifacts support downstream GCP cloud-impact detection only when UniFi OS infrastructure is GCP-hosted, GCP-fronted, GCP-logged, or correlated with upstream UniFi OS suspicious activity.
Investigation Use
Investigators should determine whether GCP activity aligns to the same UniFi OS asset, source IP, administrator identity, service account, resource name, project, network path, incident-response case, or change-management record.
Non-Coverage Conditions
GCP activity alone is not sufficient. GCP console access alone is not sufficient. Service-account activity alone is not sufficient. Cloud-only anomalies must not be attributed to UniFi OS compromise unless reliable upstream UniFi OS context and resource linkage exist.
YARA Artifact Disposition
YARA has no deployable primary-rule artifact set for this EXP report.
YARA is not viable as a primary artifact model because the report’s detection surface is management-plane behavior, request-path behavior, network-control behavior, endpoint service-context behavior, cloud-control-plane correlation, and configuration-change activity rather than static-file or malware-signature detection.
YARA may become useful only if a validated malicious artifact, script, loader, dropper, binary payload, memory artifact, credential-theft component, webshell, post-exploitation tool, or reusable malware family is recovered and independently validated.
Final YARA Outcome
No YARA rules survive.
S28 Detection Strategy and SOC Implementation Guidance

Figure 5
Purpose
This section provides implementation guidance for operationalizing the S25 rule set and S26 traceability model across UniFi OS management-plane telemetry, reverse proxy, WAF, firewall, DNS, VPN, proxy, NDR, endpoint, SIEM, QRadar, Elastic, Splunk, SIGMA-converted backends, AWS, Azure, GCP, change-management, SOAR, and incident-response environments.
The detection strategy is sequence-based. It prioritizes correlated behavior over single-event alerting and avoids treating internet exposure, scanner output, isolated WAF events, traversal-like strings, update-path access, package-path access, endpoint process activity, outbound traffic, cloud-control activity, source IP, user agent, or static indicator as proof of compromise.
Implementation Strategy
Deploy the detection model in layered stages:
· UniFi OS asset and management-path inventory first.
· Reverse proxy, WAF, web, firewall, DNS, VPN, proxy, and NDR telemetry second.
· Management-plane request-path and suspicious source-context detection third.
· Endpoint service-context, process, package, file, outbound communication, and persistence telemetry fourth.
· Downstream network-control and configuration-change correlation fifth.
· Conditional AWS, Azure, and GCP cloud-impact correlation sixth.
· Alert promotion only after local telemetry validation, false-positive baselining, suppression governance, and triage playbook alignment.
Telemetry Normalization Requirements
Implementation requires normalized entity and time correlation across UniFi OS, reverse proxy, WAF, firewall, load balancer, DNS, VPN, proxy, NDR, EDR, endpoint, Splunk, Elastic, QRadar, SIGMA-converted backends, AWS, Azure, GCP, change-management, SOAR, incident-response, and SIEM telemetry.
Minimum Normalization Requirements
· UniFi OS asset identifier.
· UniFi OS asset role.
· Management interface hostname.
· Management path.
· Source IP.
· Destination IP.
· Destination hostname.
· Request path.
· Request method.
· Response status.
· User agent.
· Session identifier where available.
· Authenticated administrator where available.
· Administrator identity.
· Administrator source baseline.
· Source ASN.
· Geography.
· VPN context.
· Proxy context.
· Reverse-proxy route.
· WAF policy or rule.
· Firewall decision.
· DNS query and response where available.
· Endpoint hostname.
· Endpoint process name.
· Parent process.
· Child process.
· Command line.
· Service account.
· Package or update process.
· File path.
· Outbound destination.
· Network device or managed-device identifier.
· Configuration-change type.
· Change ticket ID.
· Change window.
· Automation identity.
· AWS principal, account, resource, and region where applicable.
· Azure tenant, subscription, resource, caller, and region where applicable.
· GCP principal, project, resource, and region where applicable.
· SOAR case ID.
· Incident-response case ID.
· Event timestamp.
· Event source.
· Approved workflow context.
Correlation Requirements
Rules should use bounded correlation windows that reflect the relationship between UniFi OS management-plane risk and follow-on behavior.
Recommended Starting Windows
· Suspicious UniFi OS management-plane access to traversal, authentication-validation, update, package, or file-access request behavior within 30 minutes.
· Suspicious UniFi OS management-plane access to endpoint process or service-context behavior within 60 minutes.
· Suspicious UniFi OS update or package activity to endpoint file staging, process execution, outbound communication, or persistence-oriented behavior within 2 hours.
· Suspicious UniFi OS exploit-path activity to downstream network-control or configuration change within 4 hours.
· Suspicious UniFi OS management activity to unusual outbound communication from UniFi OS infrastructure within 4 hours.
· Suspicious UniFi OS activity to AWS, Azure, or GCP cloud-control-plane activity within 24 hours when the UniFi OS deployment is cloud-hosted, cloud-fronted, cloud-logged, or otherwise integrated with cloud identity, logging, backup, storage, or network-control workflows.
These windows should be tightened in high-volume environments and extended only when session continuity, administrator activity, source-device context, VPN logs, reverse-proxy logs, endpoint evidence, change-management evidence, SOAR evidence, or incident-response evidence supports continuity.
Alert Promotion Guidance
Do not promote a hunt or correlation search into alert mode until the following conditions are met:
· Required telemetry is present and normalized.
· Required field mappings are validated.
· Entity resolution is reliable.
· Event timing and ordering are reliable.
· UniFi OS asset roles and management paths are mapped.
· Reverse proxy, WAF, firewall, DNS, NDR, endpoint, SIEM, and cloud context are mapped.
· Approved administrator source baselines are defined.
· Approved maintenance, update, package, backup, vendor-support, monitoring, vulnerability-scanning, security-testing, and incident-response workflows are defined.
· False-positive sources are reviewed.
· High-volume expected workflows are suppressed or downgraded.
· Query performance is tested.
· Triage guidance is documented.
· Analyst review criteria are established.
· Local severity logic is calibrated.
· Alert-routing ownership is assigned.
False-Positive Control
False-positive control should use allowlists, reference sets, approved workflow baselines, known administrator source ranges, expected VPN paths, approved jump hosts, expected device context, expected management routes, approved maintenance windows, approved update workflows, approved package workflows, approved backup workflows, approved vulnerability scanning, approved security testing, approved monitoring, approved vendor-support activity, approved cloud automation identities, approved infrastructure-as-code identities, and incident-response exceptions.
Common False-Positive Sources
· Approved administrator access.
· Approved maintenance windows.
· Approved UniFi OS upgrades.
· Approved package updates.
· Approved backup workflows.
· Approved configuration exports.
· Approved monitoring.
· Approved vulnerability scanning.
· Approved penetration testing.
· Approved vendor support.
· Approved incident-response collection.
· Approved firewall, DNS, route, VLAN, or device-management changes.
· Approved automation identities.
· Infrastructure-as-code workflows.
· CI/CD workflows.
· Cloud load-balancer or WAF testing.
· WAF false positives.
· Scanner traffic.
· VPN egress changes.
· Managed-service provider activity.
· Break-glass administration.
· AWS automation.
· Azure automation.
· GCP automation.
Triage Guidance
Initial triage should determine whether suspicious activity forms a coherent sequence rather than a single-event anomaly.
Triage Questions
· Was suspicious UniFi OS management-plane access observed?
· Was access from a newly observed, unfamiliar, suspicious, or non-baselined source?
· Was traversal-style, authentication-validation, update-path, package-path, or unexpected file-access behavior observed?
· Was the activity visible in UniFi OS logs, reverse proxy logs, WAF logs, web logs, firewall logs, NDR telemetry, or SIEM-normalized telemetry?
· Did endpoint process, service-context, package, file, persistence, or outbound behavior occur after the management-plane activity?
· Did downstream network-control activity occur after suspected UniFi OS exploit-path activity?
· Did configuration changes affect firewall rules, routes, DNS, VLANs, managed devices, device adoption, backup behavior, or management exposure?
· Did AWS, Azure, or GCP administrative, secret, storage, backup, identity, WAF, DNS, firewall, route, or network-control activity follow?
· Can the activity be linked by UniFi OS asset, source IP, administrator identity, session, host, resource, change ticket, cloud principal, SOAR case, incident-response case, or equivalent normalized identity and asset lineage?
· Is the activity explained by approved administration, automation, vendor support, monitoring, vulnerability scanning, security testing, maintenance, backup, cloud automation, or incident response?
Escalation Guidance
Escalate when multiple behavior classes align in sequence, especially when suspicious UniFi OS management-plane access is followed by traversal-like request behavior, update or package-path behavior, endpoint service-context execution, file staging, abnormal outbound communication, downstream network-control change, or cloud-control-plane activity.
Higher-Priority Escalation Conditions
· The affected UniFi OS system manages business-critical network infrastructure.
· The affected UniFi OS system is internet-exposed or accessible from untrusted sources.
· The activity used a newly observed, suspicious, unmanaged, non-baselined, or high-risk source.
· Traversal, authentication-validation, update, package, or unexpected file-access behavior occurred.
· Endpoint service-context child process activity occurred.
· File staging, service modification, package anomaly, or persistence-oriented behavior occurred.
· Abnormal outbound communication occurred from UniFi OS infrastructure.
· Firewall, route, DNS, VLAN, device-management, or other downstream network-control changes occurred.
· Backup, configuration export, or sensitive management-data access occurred.
· AWS, Azure, or GCP activity involved privileged roles, secrets, keys, storage, logging changes, security-control suppression, WAF changes, DNS changes, firewall changes, route changes, or administrative configuration.
· Multiple systems independently show aligned behavior.
· Activity is not explained by approved change records, maintenance, automation, vendor support, monitoring, vulnerability scanning, security testing, or incident response.
Deployment Guardrails
Do not deploy these detections as fully automated blocking or containment logic without local validation.
Do not treat a single management-plane event, traversal-like string, update-path event, package-path event, endpoint process event, outbound connection, configuration change, WAF event, firewall event, DNS event, AWS event, Azure event, GCP event, source IP, user agent, or static indicator as proof of compromise.
Do not attribute cloud-only, endpoint-only, network-only, WAF-only, proxy-only, configuration-only, or SIEM-only anomalies to UniFi OS compromise without prior UniFi OS risk context and reliable asset, administrator, source, host, resource, change-management, or incident-response correlation.
Do not enable high-confidence alerting until platform-specific schemas, index names, sourcetypes, DSM fields, custom properties, ECS mappings, CloudTrail fields, Azure Activity fields, GCP audit fields, WAF fields, proxy fields, firewall fields, UniFi OS fields, endpoint fields, network fields, identity mappings, cloud identity mappings, enrichment sources, exception lists, false-positive baselines, query performance, triage readiness, and escalation criteria have been validated.
S29 Detection Coverage Summary
Coverage Summary
The S25 detection set provides broad behavior-led coverage for UniFi OS control-plane compromise, authentication-bypass activity, traversal-style request behavior, update or package-path abuse, service-context execution, host-side follow-on behavior, downstream network-control change, and conditional cloud-impact activity.
Coverage is strongest when UniFi OS, reverse proxy, WAF, firewall, DNS, NDR, endpoint, SIEM, Splunk, Elastic, QRadar, SIGMA-converted backend, AWS, Azure, GCP, change-management, SOAR, and incident-response telemetry are normalized and correlated into bounded sequences.
The report’s detection model intentionally avoids exploit names, proof-of-concept labels, static indicators, source IPs, user-agent values, actor branding, and single-event conclusions. It focuses on durable activity patterns that remain useful across authentication-bypass attempts, traversal behavior, management-plane abuse, package or update-path execution, endpoint follow-on behavior, network-control change, and conditional cloud activity.
Strong Coverage Areas
· Suspicious UniFi OS management-plane access from unusual, non-baselined, or suspicious source context.
· Authentication, validation, traversal, update, package, and file-access path behavior when visible through UniFi OS logs, reverse proxy logs, WAF logs, web logs, firewall logs, NDR telemetry, or SIEM-normalized telemetry.
· UniFi OS update or package activity followed by endpoint, outbound, or downstream management behavior.
· Service-context child process and privileged execution behavior on monitored UniFi OS Server hosts.
· File staging, package anomalies, service modification, and persistence-oriented host behavior around UniFi OS Server infrastructure.
· Downstream configuration, firewall, DNS, route, VLAN, device-management, or network-control changes following suspicious UniFi OS activity.
· AWS, Azure, and GCP activity when correlated with UniFi OS cloud-hosted, cloud-fronted, cloud-logged, or cloud-integrated risk context.
Moderate Coverage Areas
· Appliance-only UniFi OS deployments that forward partial management-plane telemetry into SIEM or NDR.
· Reverse-proxy or WAF-only visibility where backend UniFi OS logs are unavailable.
· Endpoint detection where UniFi OS Server deployment architecture varies.
· SIGMA portability across SIEM backends.
· QRadar coverage where DSM parsing and custom properties differ.
· Elastic coverage where ECS mapping, transforms, and enrich policies differ.
· Splunk coverage where CIM mapping, macros, lookups, summary indexes, and sourcetypes differ.
· Cloud detection where UniFi-to-cloud asset linkage is partial.
· Downstream configuration detection where change-management context is incomplete.
Limited Coverage Areas
· UniFi OS appliances with no forwarded logs, no reverse-proxy visibility, no WAF telemetry, no NDR coverage, and no configuration telemetry.
· Exploitation that succeeds without visible request-path, endpoint, network, or downstream-control artifacts.
· Command execution on appliances without endpoint visibility.
· Update or package-path activity that blends into approved maintenance.
· Downstream device changes that mirror legitimate administrator workflows.
· Cloud-hosted or cloud-fronted deployments without reliable resource labels, identity mapping, or normalized correlation fields.
· Environments without AWS CloudTrail data events, Azure Key Vault logs, Azure Storage logs, GCP Data Access logs, Secret Manager logs, Cloud Storage logs, or equivalent sensitive-service visibility.
· Environments without reliable change-management, SOAR, or incident-response integration.
Non-Covered Areas
The S25 rule set does not directly prove:
· Successful UniFi OS exploitation.
· Root compromise.
· Command execution.
· Credential theft.
· Data exfiltration.
· Persistent access.
· Downstream device compromise.
· AWS compromise.
· Azure compromise.
· GCP compromise.
· Actor attribution.
· Campaign attribution.
· Malware-family attribution.
These outcomes require investigation, corroborating telemetry, and incident-specific validation.
System Coverage Summary
NDR / Network Behavioral Analytics
NDR provides strong supporting coverage for suspicious management-plane access, request-path anomalies, traversal-style behavior where visible, unusual source context, outbound communication, and downstream management behavior.
NDR does not independently prove successful UniFi OS exploitation, command execution, root compromise, downstream compromise, cloud compromise, or data theft without endpoint, application, configuration, administrator, SIEM, or incident-response context.
SentinelOne
SentinelOne provides endpoint coverage where UniFi OS Server infrastructure is monitored and where service-context process behavior, privileged execution, file staging, package activity, outbound communication, and persistence-oriented host changes are visible.
SentinelOne does not cover appliance-only UniFi OS deployments without endpoint telemetry.
Splunk
Splunk provides strong correlation coverage when UniFi OS, reverse proxy, WAF, firewall, DNS, NDR, endpoint, change-management, AWS, Azure, and GCP telemetry are normalized into searchable indexes with reliable field mappings, sourcetypes, macros, lookups, summary datasets, and sequence logic.
Elastic
Elastic provides strong endpoint and SIEM correlation coverage when UniFi OS, web, proxy, WAF, endpoint, network, configuration, AWS, Azure, and GCP data are normalized into ECS-compatible or locally mapped fields with reliable sequencing, enrichment, transforms, value lists, and exception handling.
QRadar
QRadar provides strong correlation coverage when DSM parsing, custom properties, reference sets, reference maps, building blocks, event ordering, and offense grouping are validated across UniFi OS, reverse proxy, WAF, firewall, endpoint, network, configuration, AWS, Azure, and GCP telemetry.
SIGMA
SIGMA provides portable event-rule template logic for suspicious UniFi OS management-path requests, service-context process behavior, update follow-on activity, and downstream configuration-change events.
SIGMA production value depends on SIEM translation quality, field mappings, enrichment-field creation, sequence support, wildcard behavior, case handling, backend-native correlation, and local event-source coverage.
YARA
YARA has zero deployable rules for this EXP report because no stable malicious artifact, payload family, dropper, loader, script artifact, memory artifact, credential-theft component, webshell, post-exploitation tool, or reusable malware family is available.
AWS
AWS provides conditional downstream cloud-impact coverage when suspicious AWS activity is correlated with UniFi OS infrastructure that is AWS-hosted, AWS-fronted, AWS-logged, or integrated with AWS identity, networking, logging, backup, storage, or network-control workflows.
AWS does not independently prove UniFi OS compromise without upstream UniFi OS context and reliable asset, identity, resource, or incident-response linkage.
Azure
Azure provides conditional downstream cloud-impact coverage when suspicious Azure activity is correlated with UniFi OS infrastructure that is Azure-hosted, Azure-fronted, Azure-logged, or integrated with Azure identity, networking, logging, backup, storage, or network-control workflows.
Azure does not independently prove UniFi OS compromise without upstream UniFi OS context and reliable asset, identity, resource, or incident-response linkage.
GCP
GCP provides conditional downstream cloud-impact coverage when suspicious GCP activity is correlated with UniFi OS infrastructure that is GCP-hosted, GCP-fronted, GCP-logged, or integrated with GCP identity, networking, logging, backup, storage, or network-control workflows.
GCP does not independently prove UniFi OS compromise without upstream UniFi OS context and reliable asset, identity, resource, or incident-response linkage.
Coverage Conclusion
The detection set provides strong practical coverage for observable enterprise behavior associated with UniFi OS control-plane compromise, suspicious management-plane access, traversal-style request behavior, update or package-path activity, service-context execution, host-side follow-on behavior, downstream network-control change, and conditional cloud-control-plane activity.
It is strongest when multiple telemetry classes align in sequence and weakest where UniFi OS is appliance-only, telemetry is not forwarded, endpoint visibility is unavailable, request-path visibility is missing, configuration-change context is incomplete, or downstream cloud activity cannot be correlated to UniFi OS asset and incident context.
S30 Intelligence Maturity Assessment
Maturity Assessment Summary
The intelligence maturity level for this report is high for behavior-led detection strategy and moderate for direct exploitation confirmation.
The detection model is mature because it focuses on durable behavioral relationships: suspicious UniFi OS management-plane access, authentication-validation behavior, traversal-style request construction, update or package-path activity, endpoint service-context execution, file staging, outbound communication, downstream network-control change, and conditional cloud-control-plane activity.
Direct exploit-success attribution remains limited because many environments do not expose the full UniFi OS application, appliance, endpoint, and configuration telemetry needed to prove exploitation or root compromise from detection telemetry alone. Most environments infer suspected compromise through suspicious management access, request-path behavior, endpoint behavior, network behavior, configuration changes, cloud-control-plane activity, and incident-response validation.
Behavioral Intelligence Maturity
Behavioral maturity is high.
The report identifies repeatable post-access and downstream-control behaviors that can be detected across UniFi OS logs, reverse proxy logs, WAF telemetry, firewall logs, NDR telemetry, endpoint telemetry, SIEM platforms, Splunk, Elastic, QRadar, SIGMA-converted backends, AWS, Azure, and GCP platforms.
The behaviors are durable across exploit naming, proof-of-concept labels, scanner infrastructure, source IPs, user-agent values, actor branding, campaign names, cloud-provider variation, and deployment architecture differences.
Strong Behavioral Anchors
· Suspicious UniFi OS management-plane access.
· Traversal-style, authentication-validation, update-path, package-path, or unexpected file-access behavior.
· Suspicious source context, including newly observed, unfamiliar, unmanaged, high-risk, non-baselined, or suspicious administrator sources.
· UniFi OS update or package activity followed by endpoint, network, outbound, or downstream management behavior.
· UniFi OS service-context child process or privileged execution behavior.
· File staging, service modification, package anomalies, or persistence-oriented host behavior.
· Downstream firewall, route, DNS, VLAN, device-management, or configuration-change activity.
· AWS, Azure, or GCP control-plane activity following UniFi OS risk context.
Telemetry Maturity
Telemetry maturity is moderate to high.
UniFi OS logs, reverse proxy logs, WAF telemetry, firewall logs, NDR telemetry, endpoint telemetry, SIEM telemetry, change-management data, SOAR data, incident-response data, and cloud-control-plane telemetry provide strong coverage where asset, source, request, administrator, endpoint, configuration, resource, case, and timestamp fields are available and normalized.
Telemetry maturity decreases when UniFi OS logs are unavailable, management paths are not logged, WAF telemetry is incomplete, reverse-proxy data is unavailable, endpoint telemetry is missing, request paths are not captured, configuration-change logging is incomplete, cloud-resource labeling is weak, or change-management context is not integrated.
Cloud and Infrastructure Maturity
Cloud and infrastructure maturity is moderate.
AWS, Azure, and GCP provide useful downstream cloud-impact visibility when UniFi OS infrastructure is cloud-hosted, cloud-fronted, cloud-logged, or meaningfully integrated with cloud identity, logging, backup, storage, WAF, DNS, or network-control workflows.
Cloud telemetry does not independently prove UniFi OS exploitation. Its strongest value comes from correlation with prior UniFi OS management-plane risk context, asset lineage, administrator identity, network path, endpoint evidence, change-management records, SOAR context, or incident-response validation.
Maturity increases when cloud asset labels, resource identifiers, administrator identities, service accounts, source IPs, VPC or VNet context, WAF events, load balancer logs, CloudTrail, Azure Activity Logs, GCP Cloud Audit Logs, sensitive data-event logs, and SIEM-forwarded UniFi OS context are normalized and validated.
Adversary-Resilience Maturity
Adversary-resilience maturity is high for behavior-led detection and moderate for high-confidence exploitation attribution.
The detection model is resilient because it avoids brittle indicators and focuses on behavior an adversary must often produce when converting UniFi OS control-plane access into command execution, host activity, outbound communication, downstream configuration change, or cloud-control-plane impact.
The model is less resilient when adversaries use expected administrator sources, expected maintenance windows, expected update paths, expected package workflows, approved cloud automation, normal outbound destinations, or subtle downstream changes that blend into legitimate network administration. It is also less resilient when exploitation occurs on appliance-only deployments with limited telemetry forwarding.
Operationalization Maturity
Operationalization maturity is moderate.
The S25 rules are implementation-ready detection patterns, but production deployment requires local validation of schemas, index names, sourcetypes, DSM fields, custom properties, ECS mappings, UniFi OS fields, reverse-proxy fields, WAF fields, firewall fields, endpoint fields, CloudTrail fields, Azure Activity fields, GCP audit fields, identity mappings, administrator mappings, cloud identity mappings, asset mappings, enrichment, exception lists, false-positive baselines, query performance, triage logic, and alert-routing decisions.
Operational maturity increases when detection owners validate each platform’s field mappings, confirm telemetry quality, baseline approved UniFi OS administrative workflows, baseline approved update and package workflows, baseline approved network-control changes, baseline approved cloud administrative workflows, and test sequence logic using realistic benign and suspicious event data.
Attribution Maturity
Attribution maturity is low to moderate.
The rule set supports detection of behavior consistent with UniFi OS control-plane compromise, authentication-bypass activity, traversal-style request behavior, update or package-path abuse, post-access host behavior, downstream network-control change, and conditional cloud-control-plane activity. It should not be used by itself to attribute activity to a specific adversary, campaign, exploit developer, infrastructure provider, tool, malware family, or named threat group without external evidence and incident-specific validation.
Attribution requires corroborating evidence such as exploit timeline, source infrastructure, request sequence, host evidence, payload evidence, credential or session evidence, configuration changes, downstream device impact, cloud activity, victimology, actor tradecraft, and threat-intelligence reporting.
Maturity Limitations
Primary Maturity Limitations
· Limited direct visibility into exploit success.
· Limited direct visibility into root compromise on appliance-only deployments.
· Variable UniFi OS log availability.
· Variable reverse-proxy and WAF visibility.
· Variable request-path capture.
· Variable endpoint coverage for UniFi OS Server deployments.
· Variable configuration-change logging.
· Variable administrator identity mapping.
· Variable change-management integration.
· Variable SOAR and incident-response integration.
· Variable source IP stability.
· Variable cloud-hosted or cloud-fronted deployment context.
· Variable AWS, Azure, and GCP data-event logging.
· Variable approved workflow baselines.
· High false-positive potential when detections are deployed without local tuning.
Maturity Improvement Priorities
Priority Improvements
· Improve UniFi OS management-plane log collection.
· Improve reverse-proxy, WAF, and load-balancer logging.
· Improve request-path normalization and retention.
· Improve firewall, DNS, proxy, VPN, and NDR coverage for management paths.
· Improve endpoint telemetry for UniFi OS Server deployments.
· Improve service-context process, package, file, and outbound communication monitoring.
· Improve downstream configuration-change logging for firewall, DNS, routing, VLAN, and managed-device changes.
· Improve asset inventory and UniFi OS role tagging.
· Improve administrator identity mapping and privileged access workflow baselining.
· Improve change-management, SOAR, and incident-response integration.
· Improve cloud resource labeling and asset-to-cloud linkage for AWS, Azure, and GCP.
· Enable relevant cloud data-event logging for sensitive AWS, Azure, and GCP services.
· Build approved workflow baselines for UniFi OS administration, updates, packages, backups, configuration exports, monitoring, vulnerability scanning, vendor support, cloud administration, infrastructure-as-code, managed-service access, break-glass use, security tooling, and incident-response activity.
· Test detection logic against realistic benign and suspicious sequences before alert promotion.
Final Intelligence Maturity Assessment
The report’s intelligence maturity is strong for behavior-led detection engineering, strong for executive risk framing, moderate to strong for telemetry-driven operational detection, moderate to strong for SIEM and network-control correlation, moderate for AWS, Azure, and GCP downstream cloud correlation, and low to moderate for direct exploit-success attribution.
The S25 through S30 detection model is best used as an implementation-ready threat-to-detection framework that identifies suspicious UniFi OS management-plane, request-path, endpoint, configuration, downstream network-control, and cloud-impact patterns. It should not be used as a standalone proof model for successful exploitation, command execution, root compromise, credential theft, data exfiltration, downstream device compromise, cloud compromise, or actor attribution without corroborating telemetry and incident-specific validation.
S31 — Telemetry Dependencies
UniFi OS control-plane compromise through authentication bypass and command injection requires telemetry that can prove whether suspicious management-plane access, authentication-bypass behavior, traversal-like request activity, protected functionality reachability, update or package abuse, command execution, sudo or root-context behavior, administrator-state change, configuration modification, outbound communication, downstream discovery, or network-control impact stayed within approved UniFi administration or created material infrastructure-trust risk. The central dependency is the ability to correlate UniFi OS asset inventory, management-interface exposure records, reverse-proxy logs, firewall telemetry, web or application logs where available, update-service logs, system logs, sudo logs, package-management records, endpoint or appliance telemetry, administrator audit records, API token activity, device-adoption records, configuration-change telemetry, gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, and managed-device records, change-control evidence, vulnerability management records, incident-response records, and approved administration baselines into one management-plane access-to-impact investigation model.
UniFi OS Asset, Exposure, and Management-Plane Telemetry
· UniFi OS asset telemetry must identify UniFi OS Server deployments, consoles, cloud gateways, dream machines, cloud keys, gateways, controller hosts, recorders, storage appliances, management interfaces, exposed administration paths, reverse-proxy destinations, VPN-accessible administration paths, firmware versions, fixed-version status, and approved management paths.
· Exposure telemetry must capture whether UniFi OS management interfaces are internet-reachable, VPN-reachable, internally reachable, reverse-proxied, protected by secure access controls, restricted to management networks, or reachable from non-administrative segments.
· Required fields include asset name, asset type, asset role, device model where available, UniFi OS version, management IP, public exposure status, management interface, destination host, destination port, interface path, exposure source, administrative owner, business owner, site, network segment, fixed-version status, and last validation time.
· This telemetry is required to determine whether suspicious UniFi OS activity affected a low-impact controller, management server, gateway, firewall-control path, VPN-control path, recorder, storage appliance, remote-site controller, or privileged network-management system.
· Asset and exposure telemetry must be interpreted conservatively because vulnerability scans, patch dashboards, asset discovery tools, vendor inventory, and network-management records may identify exposure but cannot prove exploitation by themselves..
Management-Plane Access, Reverse-Proxy, Firewall, and Web Telemetry
· Management-plane access telemetry must capture source IP, destination IP, destination host, destination interface, HTTP method, request path where available, normalized path where available, raw path where available, response status, response size, user agent, session context where available, request timestamp, connection frequency, and management-interface exposure path.
· Reverse-proxy, firewall, load-balancer, secure access, VPN, and web telemetry must capture UniFi OS management access, suspicious source context, unfamiliar geographies, suspicious ASNs, hosting-provider sources, residential proxy sources, newly observed internal hosts, unmanaged systems, approved administrator-source deviations, and abnormal request sequences.
· Required fields include source IP, source ASN, source geography, source device, source network, destination asset, destination interface, protocol, port, request path, response status, response size, user agent, request count, connection count, timestamp, session identifier where available, administrator identity where available, and approved-source status.
· This telemetry is required to determine whether authentication-bypass behavior, traversal-like request activity, update-endpoint probing, protected path access, or abnormal management-plane activity occurred near suspicious source context or follow-on infrastructure behavior.
· Management-plane telemetry must be interpreted against approved administration, vulnerability scanning, exposure assessment, vendor support, monitoring, security testing, incident-response activity, and documented maintenance because those workflows can produce overlapping request behavior.
UniFi OS Application, Update-Service, and Package-Management Telemetry
· UniFi OS application telemetry should capture administrative sessions, API activity, update-endpoint access, package-management activity, application-update workflows, device-adoption events, backup actions, configuration changes, service instability, application errors, and update-triggered behavior where exposed by the deployment.
· Update-service and package-management telemetry should capture update checks, package retrieval, package installation, package validation, update failures, package-management errors, service restarts, package-script activity, and update behavior occurring outside approved maintenance windows.
· Required fields include asset, service name, update action, package action, package name where available, process or service context where available, administrator identity where available, API token context where available, event result, error code, timestamp, maintenance-window status, and change-ticket reference where available.
· This telemetry is required to determine whether suspected authentication bypass or protected functionality access moved into update or package abuse, service instability, command-execution opportunity, or post-exploitation workflow.
· Update and package telemetry must be interpreted conservatively because approved firmware updates, vendor-guided remediation, controller upgrades, package operations, emergency patching, backup workflows, and incident-response actions may produce similar signals.
Endpoint, Process, Sudo, System, and File Telemetry
· Endpoint and process telemetry should be collected from self-hosted UniFi OS Server deployments, controller hosts, supporting Linux hosts, management servers, and appliance environments that expose host-level visibility.
· Process telemetry should capture process creation, parent-child lineage, command line, working directory, user context, service context, shell execution, interpreter execution, package-manager execution, network utility execution, file retrieval, archive extraction, service-management commands, and execution from temporary, update, package, application-writable, or staging paths.
· Sudo, system, file, and persistence telemetry should capture sudo usage, effective-user context, root-context execution, service modification, permission changes, package changes, local user changes, SSH configuration changes, scheduled jobs, file creation, file modification, script placement, archive extraction, backup access, configuration export, and credential-material access where technically available.
· Required fields include host, process name, parent process, command line, process path, process user, effective user, sudo command, working directory, file path, file action, package action, service action, event timestamp, hash where available, and relationship to UniFi OS service context.
· This telemetry is required to determine whether suspicious management-plane activity progressed into command execution, sudo-assisted activity, root-context behavior, file staging, tool retrieval, service modification, or persistence-relevant changes.
· Host-level telemetry must not be assumed available for all UniFi OS appliance deployments. Where it is unavailable, confidence should be reduced and detections should rely on management-plane logs, system diagnostics, administrator activity, configuration records, network telemetry, and incident-response evidence.
Administrator, API Token, Device-Adoption, and Configuration Telemetry
· Administrator telemetry must capture administrative session creation, administrator login activity, account creation, account modification, permission changes, API token activity, local user changes, SSH access changes, device-adoption events, backup actions, configuration exports, and management-plane permission changes.
· Configuration telemetry must capture gateway policy changes, firewall rule changes, routing changes, VPN changes, DNS changes, wireless changes, SSID changes, device-adoption changes, recorder configuration changes, storage configuration changes, backup changes, and managed-device configuration changes where those UniFi OS roles are deployed.
· Required fields include administrator identity, administrator role, source IP, source device, session ID where available, API token identifier where available, action, configuration object, prior value where available, new value where available, device identifier, device role, site, network segment, timestamp, approving change ticket, and change owner where available.
· This telemetry is required to determine whether suspicious UniFi OS access affected administrative trust, device trust, configuration integrity, remote access, segmentation, firewall policy, VPN access, DNS behavior, wireless security, recorder operations, storage access, or downstream infrastructure state.
· Administrator and configuration telemetry must be interpreted against approved maintenance, device onboarding, vendor support, incident response, network-change records, site onboarding, firewall-policy updates, VPN changes, wireless changes, and DNS changes before being treated as malicious.
Network, DNS, Proxy, NDR, and Outbound Communication Telemetry
· Network telemetry must capture public ingress, VPN ingress, reverse-proxy traffic, management-interface traffic, controller-to-device communication, east-west management traffic, outbound communication, internal scanning, device enumeration, and access to additional management interfaces.
· DNS, proxy, firewall, secure web gateway, and NDR telemetry should capture newly observed destinations, rare domains, rare IPs, unusual ASNs, low-reputation destinations, unexpected geographies, role-inconsistent traffic, HTTP or HTTPS access, SSH traffic, SMB traffic, tunnel-like traffic, file retrieval, package-repository access, and abnormal byte volume.
· Required fields include source IP, source host, destination IP, destination host, destination port, protocol, directionality, byte count, DNS query, URL where available, application classification, connection count, first-seen context, ASN, geography, reputation, asset role, and event timestamp.
· This telemetry is required to determine whether suspected UniFi OS compromise produced outbound staging, tool retrieval, rare external communication, internal scanning, device enumeration, or downstream network-management access.
· Network telemetry must not be used as standalone proof of command execution, root compromise, credential exposure, downstream compromise, or actor attribution without supporting UniFi OS, administrator, system, configuration, or incident-response evidence.
Change-Control, Vulnerability Management, Incident Response, and Business Context
· Change-control telemetry must capture approved firmware updates, package operations, controller upgrades, device adoption, backup activity, gateway changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, security testing, monitoring, vulnerability management, and incident-response actions.
· Vulnerability management records must capture affected UniFi OS assets, vulnerable versions, fixed versions, exposure state, KEV-driven remediation status, remediation date, compensating controls, retest status, and pre-patch compromise assessment status.
· Incident-response records must capture triage owner, investigation window, suspected exploit-path evidence, log sources reviewed, administrator actions reviewed, command-execution assessment, sudo or root-context assessment, configuration review status, downstream impact assessment, containment actions, and closure evidence.
· Required fields include ticket ID, change ID, asset owner, business owner, action owner, approving authority, maintenance window, affected asset, affected site, event timestamp, remediation timestamp, validation outcome, rollback status, and business justification where available.
· This telemetry is required to determine whether observed UniFi OS activity aligned with approved operations or represented suspicious exploitation, unauthorized administration, post-exploitation behavior, or unresolved control-plane trust risk.
S32 — Detection Limitations
Detection of UniFi OS control-plane compromise through authentication bypass and command injection is limited by whether the organization can reconstruct the relationship between management-plane exposure, exploit-path request behavior, protected functionality reachability, update or package activity, command execution, sudo or root-context behavior, administrator-state changes, configuration changes, outbound communication, downstream discovery, network-control impact, and approved UniFi administration workflows. Environments that rely only on vulnerable-version state, exposed-interface findings, scanner output, isolated denied requests, single web errors, ordinary update checks, or public exploit reporting will not have enough evidence for high-confidence compromise or impact determination.
Primary Limitations
· Missing UniFi OS asset inventory may prevent identification of affected servers, consoles, gateways, cloud keys, dream machines, recorders, storage appliances, controller hosts, exposed management interfaces, firmware versions, approved management paths, and downstream infrastructure roles.
· Missing exposure records may prevent determination of whether UniFi OS management interfaces were internet-reachable, VPN-reachable, internally reachable, reverse-proxied, restricted to management networks, or reachable from non-administrative segments.
· Missing reverse-proxy, firewall, secure access, load-balancer, or web telemetry may prevent reliable assessment of management-plane source context, request paths, response behavior, traversal-like activity, update-endpoint access, or protected path reachability.
· Missing raw request path, normalized request path, HTTP method, response status, response size, user agent, source context, or session context may prevent high-confidence exploit-path reconstruction.
· Missing UniFi OS application logs may reduce visibility into authentication-gateway behavior, administrative sessions, API token use, update-service activity, package-management behavior, device adoption, backup actions, and configuration changes.
· Missing endpoint, process, sudo, package-management, file, memory, or system telemetry may prevent direct confirmation of command execution, sudo-assisted activity, root-context execution, service modification, file staging, or persistence-relevant changes.
· Missing administrator audit logs may reduce confidence when assessing administrator creation, API token activity, session anomalies, device adoption, backup export, SSH changes, permission changes, or configuration manipulation.
· Missing downstream configuration telemetry may prevent assessment of gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless configuration, recorder behavior, storage access, segmentation boundaries, or managed-device trust after suspected compromise.
· Missing DNS, proxy, firewall, NDR, or network-flow telemetry may prevent assessment of outbound communication, file retrieval, rare destinations, internal scanning, device enumeration, or access to adjacent management interfaces.
· Missing change-management and incident-response records may prevent differentiation between approved firmware updates, package operations, device adoption, backups, gateway changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, vendor support, monitoring, security testing, remediation, and suspicious control-plane behavior.
· Short log retention may prevent reconstruction of the period between exploitation, emergency remediation, administrator review, configuration validation, downstream impact assessment, and post-remediation monitoring.
· Poor timestamp normalization can break sequence logic between management-plane requests, update-service activity, process execution, sudo usage, administrator activity, configuration changes, network traffic, and incident-response actions.
Detection Boundary
· A vulnerable UniFi OS version, exposed management interface, scanner result, KEV listing, public proof-of-concept, isolated denied request, single web error, ordinary update check, or single administrative action is not proof of compromise by itself.
· Suspicious management-plane access should not be treated as successful exploitation without protected functionality access, update or package activity, command-execution evidence, administrator anomaly, configuration change, outbound communication, or incident-response validation.
· Update-endpoint or package-management activity should not be treated as malicious without suspicious source context, exploit-path behavior, unusual timing, service instability, command execution, administrator anomaly, or change-management mismatch.
· Command execution should not be inferred from management-plane request behavior alone without supporting process, system, endpoint, package-management, network, sudo, or incident-response evidence.
· Sudo or root-context activity should not be treated as exploit-related unless it occurs near suspicious UniFi OS activity, update or package abuse, unexpected service-context execution, administrator anomaly, or incident-response evidence.
· Administrator changes, API token use, device adoption, backup export, or configuration changes should not be attributed to UniFi OS exploitation unless tied to suspicious management-plane access, command execution, sudo activity, unusual source context, or missing change-control evidence.
· Downstream gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, or managed-device changes should not be treated as UniFi compromise evidence unless linked to suspected UniFi OS exploit-path activity, administrator-state anomaly, suspicious source context, or incident-response validation.
· Network telemetry should not be used as the primary basis for confirming command execution, root compromise, credential exposure, downstream compromise, or actor attribution by itself.
· Detection logic must not rely on prior alert state, another rule’s output, analyst judgment after alert generation, DRI, or TCR as an input.
· High-confidence alerting should require validated multi-signal correlation across UniFi OS management-plane activity, update or package behavior, host or system telemetry where available, administrator activity, configuration records, network telemetry, change-control records, and incident-response evidence.
Operational Impact of Limitations
Detection coverage should be reduced, scoped down, converted to hunt-only logic, or withheld when required telemetry is unavailable, incomplete, delayed, sampled, inconsistently normalized, or unable to support bounded sequence correlation. Suspicious UniFi OS access or network activity may be analytically important but unsuitable for high-confidence alerting if the organization cannot validate asset role, management-interface exposure, source context, request behavior, update or package activity, administrator context, command execution, sudo activity, configuration changes, downstream network-control impact, and approved business workflow evidence within locally validated correlation windows.
S33 — Defensive Control & Hardening Improvements
Defensive improvement should focus on making UniFi OS management-plane exposure, administrative access, update and package behavior, command execution, privileged activity, configuration integrity, downstream network-control state, and post-remediation assurance measurable, governed, and resilient under active exploitation pressure. The objective is not only to patch one vulnerable version, block one source, close one management interface, or detect one request pattern, but to prove that UniFi OS activity can be scoped, correlated, contained, and separated from legitimate network administration when control-plane compromise is suspected.
UniFi OS Asset, Exposure, and Patch Governance
· Maintain a complete inventory of UniFi OS Server deployments, consoles, cloud gateways, dream machines, cloud keys, gateways, controller hosts, network video recorders, storage appliances, exposed management interfaces, management IPs, firmware versions, fixed-version status, administrative owners, business owners, sites, and network segments.
· Identify which UniFi OS systems control gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless networks, device adoption, recorder functions, storage access, segmentation boundaries, remote sites, customer-facing locations, or privileged management networks.
· Restrict UniFi OS management interfaces to approved management networks, privileged access workstations, jump hosts, VPN administration paths, secure access paths, or other controlled administrative channels.
· Prioritize KEV-driven remediation, fixed-version deployment, compensating controls, emergency exposure reduction, and pre-patch compromise assessment for internet-reachable or broadly reachable UniFi OS systems.
· Require auditable change-control for UniFi OS upgrades, package operations, controller upgrades, gateway changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, device adoption, recorder changes, storage changes, backup actions, and emergency remediation.
Management-Plane Access and Administrator Governance
· Maintain approved administrator source baselines covering known administrator IPs, VPN ranges, jump hosts, privileged access workstations, management networks, monitoring systems, vendor-support paths, vulnerability management systems, security-testing systems, and incident-response systems.
· Monitor access to UniFi OS management interfaces from unfamiliar internet sources, unusual geographies, suspicious ASNs, hosting-provider sources, residential proxy ranges, VPN ingress paths, newly observed internal hosts, unmanaged systems, and sources outside approved administration paths.
· Govern administrator accounts, local users, API tokens, administrative sessions, SSH access, device-adoption permissions, backup permissions, configuration permissions, and role-specific management privileges.
· Review newly created, rarely used, unusual-source, geographically unusual, API-token-based, or privilege-changing administrative activity near exploit-path behavior, command execution, sudo activity, outbound communication, or configuration changes.
· Require rapid administrator and API-token review when suspected UniFi OS exploitation affects systems that manage gateways, firewalls, VPN access, DNS behavior, wireless networks, recorder infrastructure, storage appliances, or privileged management networks.
Update, Package, Command Execution, and Privileged Activity Hardening
· Baseline normal UniFi OS update checks, package operations, controller upgrades, firmware updates, package-management behavior, service restarts, maintenance scripts, and vendor-guided remediation activity.
· Monitor update-endpoint activity, package-management behavior, application-update workflows, update-triggered service activity, package failures, and service instability near suspicious management-plane access.
· Monitor unexpected child processes from UniFi OS web, application, controller, update, package-management, or service-wrapper contexts where host-level telemetry exists.
· Monitor shell execution, interpreter execution, package-manager execution, command chaining, file retrieval, archive extraction, network utility execution, service-management commands, sudo usage, root-context execution, service modification, permission changes, local user changes, and SSH configuration changes.
· Treat command execution and sudo or root-context behavior near suspicious UniFi OS access as high-priority infrastructure-trust evidence requiring incident-response validation.
Configuration, Downstream Control, and Network-Trust Hardening
· Monitor gateway policy, firewall rules, routing configuration, VPN access, DNS behavior, wireless configuration, SSID security, device adoption, recorder behavior, storage access, backup actions, and managed-device configuration where those UniFi OS roles are deployed.
· Require change records for firewall rule changes, routing changes, VPN changes, DNS changes, wireless changes, device adoption, recorder changes, storage changes, backup exports, and management-plane permission changes.
· Prioritize review of changes that expand remote access, weaken firewall policy, alter segmentation, change default routes, modify DNS forwarding, weaken wireless security, add unexpected devices, affect recorder visibility, expose storage, or reduce monitoring.
· Validate downstream configuration integrity after suspected UniFi OS exploitation, especially where affected systems support executive sites, branch offices, regulated environments, customer-facing locations, production networks, remote-site connectivity, surveillance systems, or privileged management networks.
· Treat unexplained downstream configuration changes near exploit-path activity as control-plane impact risk until approved maintenance or incident-response evidence proves otherwise.
Network, Outbound Communication, and Discovery Hardening
· Monitor outbound communication from UniFi OS systems to newly observed, rare, low-reputation, unusual ASN, unexpected geographic, tunnel-like, role-inconsistent, or unapproved destinations.
· Monitor file retrieval, package-repository access, HTTP or HTTPS activity, DNS activity, SSH traffic, SMB traffic, tunnel-like traffic, abnormal byte volume, and process-network connections after suspected exploit-path behavior.
· Monitor internal scanning, device enumeration, management-interface discovery, SNMP activity, SSH access, web-admin access, API probing, and access to additional gateways, switches, access points, firewalls, VPN systems, DNS services, recorder systems, storage systems, backup systems, monitoring systems, and high-value management targets.
· Validate outbound communication against approved vendor services, update destinations, monitoring tools, backup systems, remote-management platforms, vulnerability management, security testing, vendor support, and incident-response infrastructure.
· Treat outbound and downstream network activity as supporting context rather than standalone confirmation of command execution, root compromise, credential exposure, or actor attribution.
Telemetry, Baseline, and Correlation Hardening
· Enable and retain UniFi OS logs, reverse-proxy logs, firewall logs, secure access logs, load-balancer logs, web logs where available, update-service logs, system logs, sudo logs, package-management logs, endpoint telemetry where available, DNS logs, proxy logs, NDR telemetry, administrator audit logs, configuration-change records, change-management records, vulnerability management records, and incident-response records.
· Normalize asset identifiers, source identifiers, administrator identifiers, API token identifiers, session identifiers, request paths, normalized paths, raw paths where available, response codes, service names, process lineage, command lines, sudo activity, package events, configuration objects, device identifiers, network segments, sites, timestamps, and change-window context.
· Baseline approved management paths, administrator sources, update workflows, package operations, firmware updates, device adoption, backup actions, gateway changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, monitoring, vulnerability management, security testing, and incident-response activity.
· Require multi-signal correlation before high-severity alerting or compromise determination.
· Build incident timelines that join suspicious management-plane access, exploit-path request behavior, update or package activity, command execution, sudo activity, administrator changes, configuration changes, outbound communication, downstream network-control activity, change-control records, and incident-response evidence.
Incident Response and Containment Hardening
· Create response procedures for suspicious UniFi OS management-plane access, authentication-bypass indicators, traversal-like request behavior, update-endpoint abuse, package-management anomalies, command execution, sudo activity, root-context behavior, administrator changes, API token activity, device-adoption anomalies, configuration changes, outbound communication, internal scanning, and downstream network-control impact.
· Require rapid validation of affected asset, affected site, asset role, exposure path, source context, request behavior, update or package activity, administrator context, command-execution evidence, sudo activity, configuration state, downstream device impact, and post-remediation activity.
· Prepare decision paths for emergency management-interface isolation, fixed-version deployment, administrator credential rotation, API token revocation, SSH access review, configuration rollback, gateway and firewall policy review, VPN review, DNS review, wireless review, device readoption review, recorder and storage assurance, segmentation validation, legal review, cyber-insurance coordination, communications planning, and executive reporting.
· Treat suspected UniFi OS exploitation as a network-management control-plane trust incident, not a routine patch ticket, isolated scanner finding, single denied request, ordinary update event, or standard administrator troubleshooting issue.
· Require post-event validation to distinguish approved firmware updates, package operations, controller upgrades, backups, device adoption, gateway changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, monitoring, security testing, and incident response from attacker-driven behavior.
S34 — Defensive Control & Hardening Architecture

Figure 6
UniFi OS control-plane compromise defensive architecture showing asset and exposure governance, management-plane access control, update and package monitoring, command-execution visibility, administrator and API-token governance, configuration integrity validation, downstream network-control assurance, SOC correlation, and executive infrastructure-trust restoration.
The defensive architecture should treat UniFi OS as governed network-management trust infrastructure rather than an isolated web service or patch-management issue. The architecture must connect UniFi OS asset inventory, exposure control, management-interface restriction, fixed-version deployment, administrator governance, update and package monitoring, command-execution visibility, sudo and root-context validation, configuration integrity, downstream network-control assurance, network telemetry, SOC correlation, incident-response containment, and executive infrastructure-trust decisioning into one management-plane access-to-impact assurance model.
Architecture Layer One — UniFi OS Asset and Exposure Governance
UniFi OS asset and exposure governance establishes which UniFi OS systems exist, where they are reachable, what roles they perform, which firmware versions are deployed, which management paths are approved, and which downstream infrastructure functions depend on them. This layer captures UniFi OS Server deployments, consoles, gateways, cloud keys, dream machines, recorders, storage appliances, controller hosts, exposed management interfaces, management IPs, public exposure, VPN exposure, internal reachability, fixed-version status, site context, owner context, and business dependency.
Architecture Layer Two — Management-Plane Access Control
Management-plane access control determines whether UniFi OS administrative access is restricted to approved paths and whether suspicious source access can be identified quickly. This layer captures approved administrator sources, VPN ranges, jump hosts, privileged access workstations, management networks, secure access paths, reverse-proxy destinations, monitoring systems, vendor-support paths, source reputation, source geography, ASN context, newly observed sources, unmanaged systems, and access outside approved baselines.
Architecture Layer Three — Exploit-Path and Request Visibility
Exploit-path and request visibility determines whether suspicious management-plane activity remained scanning or reached behavior consistent with authentication bypass, traversal-like access, protected functionality reachability, or update-endpoint interaction. This layer captures request paths, normalized paths, raw paths where available, HTTP methods, response codes, response sizes, request timing, request bursts, encoded path variations, repeated path changes, response anomalies, update endpoints, and protected path activity.
Architecture Layer Four — Update, Package, and Service Behavior
Update, package, and service behavior determines whether protected functionality access moved into update or package-related abuse. This layer captures update checks, package retrieval, package installation, update validation, package-management errors, update-service failures, application errors, service restarts, package-script behavior, maintenance-window context, vendor-update context, and change-ticket linkage.
Architecture Layer Five — Command Execution and Privileged Activity Visibility
Command execution and privileged activity visibility determines whether management-plane exploitation created host-level or appliance-level execution risk. This layer captures process creation, parent-child process lineage, command lines, shell execution, interpreter execution, package-manager execution, file retrieval, archive extraction, network utility execution, sudo usage, effective-user context, root-context execution, service modification, permission changes, local user changes, SSH configuration changes, and file activity where technically available.
Architecture Layer Six — Administrator, API Token, and Device-Trust Governance
Administrator, API token, and device-trust governance determines whether adversaries modified or misused control-plane trust relationships. This layer captures administrator accounts, local users, administrative sessions, API tokens, permissions, SSH access, device adoption, backup actions, configuration exports, administrator source context, administrator timing, newly created administrators, rarely used administrators, and privilege changes.
Architecture Layer Seven — Configuration Integrity and Downstream Network-Control Assurance
Configuration integrity and downstream network-control assurance determines whether suspected UniFi OS compromise affected the infrastructure managed by UniFi OS. This layer captures gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless configuration, SSID security, device-adoption state, recorder behavior, storage access, backup state, segmentation boundaries, managed-device configuration, site impact, and rollback validation.
Architecture Layer Eight — Network, Outbound, and Discovery Context
Network, outbound, and discovery context determines whether suspected compromise produced external communication, tool staging, internal scanning, or movement toward additional management surfaces. This layer captures DNS, proxy, firewall, NDR, network-flow, secure web, and management-network telemetry, including rare outbound destinations, newly observed destinations, low-reputation destinations, unusual ASNs, unexpected geographies, tunnel-like traffic, internal scanning, device enumeration, SNMP activity, SSH access, web-admin access, API probing, and additional management-interface access.
Architecture Layer Nine — SOC Correlation and False-Positive Control
SOC correlation joins UniFi OS asset context, management-plane access, request behavior, update-service activity, process telemetry, sudo activity, administrator events, API token activity, configuration records, outbound communication, network discovery, downstream device changes, vulnerability management records, change-control records, incident-response records, and approved workflow baselines. This layer validates whether activity is attacker-driven, administrator-driven, vendor-support-related, monitoring-related, vulnerability-management-related, security-testing-related, maintenance-related, device-onboarding-related, or incident-response-related.
Architecture Layer Ten — Incident Response and Executive Infrastructure-Trust Workflow
Incident response and executive infrastructure-trust workflow connects technical validation to business decisions. This layer captures incident severity, affected assets, affected sites, exposed management paths, affected administrators, affected API tokens, affected devices, affected gateway policies, affected firewall rules, affected VPN paths, affected DNS behavior, affected wireless networks, affected recorder infrastructure, affected storage systems, affected business workflows, containment actions, configuration rollback, credential rotation, legal review, cyber-insurance coordination, communications planning, executive reporting, board-level assurance, and validation that infrastructure control-plane trust can safely resume.
Architecture Outcome
The architecture should enable the organization to answer seven questions during a UniFi OS exploitation incident:
· Which UniFi OS asset, management interface, source system, administrator, API token, session, update path, process, sudo event, configuration object, gateway, firewall rule, VPN path, DNS setting, wireless network, recorder, storage appliance, managed device, site, or business workflow was affected?
· Did the activity align with approved administration, firmware updates, package operations, controller upgrades, device adoption, backups, gateway changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, monitoring, vulnerability management, security testing, or incident response?
· Did suspicious management-plane activity transition into protected functionality reachability, update or package abuse, command execution, sudo or root-context activity, administrator-state change, configuration change, outbound communication, internal scanning, or downstream network-control activity?
· Did the activity affect gateways, firewalls, routing, VPN access, DNS behavior, wireless networks, segmentation boundaries, remote sites, customer-facing locations, regulated environments, surveillance infrastructure, storage systems, or privileged management networks?
· Can the organization contain affected UniFi OS systems, isolate management interfaces, deploy fixed versions, rotate administrator credentials, revoke API tokens, review SSH access, validate configuration integrity, roll back unauthorized changes, review downstream devices, and preserve business continuity without over-attributing unrelated network or administration anomalies to UniFi OS compromise?
· Can the organization prove that UniFi OS management-plane access, update activity, administrator actions, configuration changes, outbound communication, and downstream management activity were approved operational activity rather than suspicious follow-on behavior?
· Can leadership make defensible decisions about network-control trust, site operations, remote access, segmentation, customer or workforce impact, legal review, cyber-insurance coordination, communications response, and infrastructure trust restoration?
S35 — Defensive Control Mapping Matrix
Preventive Controls
· Maintain complete UniFi OS asset inventory, including UniFi OS Server deployments, consoles, cloud gateways, dream machines, cloud keys, gateways, recorders, storage appliances, controller hosts, exposed management interfaces, firmware versions, approved administration paths, administrative owners, business owners, sites, and downstream infrastructure roles.
· Restrict UniFi OS management interfaces to approved management networks, VPN administration paths, jump hosts, privileged access workstations, secure access paths, and controlled administrator sources.
· Enforce fixed-version deployment, KEV-driven remediation, emergency exposure reduction, compensating controls, and pre-patch compromise assessment for vulnerable or broadly reachable UniFi OS systems.
· Govern administrator accounts, local users, API tokens, administrative sessions, SSH access, device-adoption permissions, backup permissions, configuration permissions, and role-specific management privileges.
· Require change control for UniFi OS upgrades, package operations, controller upgrades, gateway changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, device adoption, backups, vendor support, security testing, and incident-response changes.
· Prioritize preventive controls for systems managing gateways, firewalls, routing, VPN access, DNS behavior, wireless networks, segmentation boundaries, remote sites, customer-facing locations, regulated environments, surveillance infrastructure, storage appliances, and privileged management networks.
Detective Controls
· Monitor UniFi OS management-plane access from unfamiliar internet sources, unusual geographies, suspicious ASNs, hosting providers, residential proxy ranges, VPN ingress paths, newly observed internal hosts, unmanaged systems, and sources outside approved administration paths.
· Monitor authentication-gateway anomalies, traversal-like request behavior, encoded path variations, unexpected file-access paths, update-endpoint access, request-normalization mismatches, abnormal response-code patterns, and management-plane request bursts.
· Monitor update-endpoint activity, package-management behavior, application-update workflows, package failures, update-service instability, service restarts, and update activity outside approved maintenance windows.
· Monitor unexpected child processes from UniFi OS web, application, controller, update, package-management, backup, or service-wrapper contexts where host telemetry exists.
· Monitor shell execution, interpreter execution, command chaining, file retrieval, archive extraction, network utility execution, package-manager execution, sudo usage, root-context execution, service modification, permission changes, local user changes, and SSH configuration changes.
· Monitor administrator creation, administrator modification, API token activity, administrative session anomalies, device-adoption changes, backup exports, configuration exports, permission changes, and unusual administrator-source activity.
· Monitor gateway policy changes, firewall rule changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, segmentation changes, and managed-device configuration changes after suspicious UniFi OS activity.
· Monitor outbound communication, rare destinations, newly observed destinations, low-reputation destinations, unusual ASNs, unexpected geographies, tunnel-like traffic, internal scanning, device enumeration, and additional management-interface access after suspected exploit-path activity.
Responsive Controls
· Isolate affected UniFi OS management interfaces where appropriate, restrict public exposure, disable nonessential administration paths, and validate fixed-version deployment.
· Review suspected exploit-path activity, protected functionality reachability, update or package behavior, command execution, sudo activity, root-context activity, file activity, service changes, and outbound communication.
· Rotate or review administrator credentials, revoke suspicious API tokens, review local users, inspect SSH access, validate administrative sessions, and confirm authorized management paths.
· Review and restore gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless configuration, device-adoption state, recorder settings, storage configuration, backup state, and managed-device trust.
· Validate downstream infrastructure integrity across gateways, switches, access points, firewalls, VPN systems, DNS services, recorder systems, storage systems, backup systems, monitoring systems, and other management targets.
· Perform legal and compliance review, cyber-insurance coordination, communications planning, customer or workforce impact assessment, executive reporting, and board-level infrastructure-trust assurance where control-plane impact or business disruption is suspected.
· Confirm that UniFi OS management-plane access, update activity, administrator activity, configuration changes, outbound communication, and downstream device activity were approved operational activity before closing the incident.
Governance Controls
· Maintain approved inventories for UniFi OS assets, management interfaces, firmware versions, approved administrator sources, VPN administration paths, jump hosts, privileged access workstations, management networks, administrator accounts, API tokens, device-adoption workflows, backup workflows, and downstream infrastructure roles.
· Maintain approved workflows for firmware updates, package operations, controller upgrades, device adoption, backups, gateway changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, monitoring, vulnerability management, security testing, and incident response.
· Require change-control records for UniFi OS upgrades, package changes, administrator changes, API token changes, device adoption, configuration exports, gateway policy changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, and emergency remediation.
· Maintain escalation criteria for suspicious management-plane access, authentication-bypass behavior, traversal-like request activity, update-endpoint abuse, package-management anomalies, command execution, sudo activity, root-context behavior, administrator changes, configuration changes, outbound communication, internal scanning, and downstream network-control impact.
· Track UniFi OS control-plane compromise and network-infrastructure trust exposure in the risk register when telemetry, asset inventory, exposure control, administrator governance, configuration integrity, or response gaps create unresolved enterprise risk.
Control Mapping Summary
The strongest control posture combines prevention of unnecessary UniFi OS management-plane exposure, detection of suspicious management-plane access-to-impact behavior, and response workflows that restore infrastructure trust, administrator integrity, configuration confidence, network-control assurance, and business continuity. Controls should be prioritized for UniFi OS environments supporting gateways, firewalls, routing, VPN access, DNS behavior, wireless networks, segmentation boundaries, remote sites, customer-facing locations, regulated environments, surveillance infrastructure, storage appliances, and privileged management networks.
S36 — CyberDax Intelligence Maturity Assessment
Current Intelligence Maturity
Moderate
Maturity Rationale
UniFi OS control-plane compromise through authentication bypass and command injection is a well-defined exploit-path behavior class, but organization-specific maturity depends on whether suspicious management-plane access, protected functionality reachability, update or package activity, command execution, sudo or root-context behavior, administrator-state changes, configuration changes, outbound communication, downstream discovery, network-control impact, remediation actions, and approved UniFi administration workflows can be correlated. Many environments can identify vulnerable UniFi OS versions, exposed management interfaces, patch status, firewall traffic, or administrative changes, but fewer can prove whether suspected exploit-path activity resulted in command execution, root-level compromise, configuration manipulation, downstream network-control impact, or containment failure.
Strengths
· The behavior pattern is durable because it focuses on management-plane access-to-impact tradecraft rather than one CVE identifier, proof-of-concept name, request string, user agent, source IP, file hash, tool name, actor name, malware family, or static IOC.
· The core sequence is analytically clear: management-plane exposure, authentication-bypass or traversal-like access behavior, protected functionality reachability, update or package interaction, command execution, privileged or root-context activity, administrator or configuration impact, and downstream discovery or network-control exposure.
· Detection opportunities are strong where UniFi OS asset inventory, exposure records, reverse-proxy logs, firewall telemetry, web logs, update-service logs, system logs, sudo logs, package-management logs, endpoint telemetry where available, administrator audit logs, configuration records, DNS logs, NDR telemetry, change-control records, and incident-response evidence can be correlated.
· Defensive controls can be mapped directly to asset inventory, exposure reduction, fixed-version deployment, administrator governance, API token review, management-interface restriction, update monitoring, process telemetry, sudo visibility, configuration integrity, outbound communication review, downstream device assurance, SOC triage, and incident-response containment.
· The executive risk model, attack-path narrative, detection strategy, and defensive hardening model remain aligned while preserving a behavior-led approach and avoiding CVE-only, actor-only, proof-of-concept-only, scanner-only, exploit-string-only, or IOC-only overreach.
Maturity Gaps
· UniFi OS asset inventory may not reliably identify all UniFi OS Server deployments, consoles, gateways, cloud keys, dream machines, recorders, storage appliances, controller hosts, exposed management interfaces, firmware versions, approved administration paths, or downstream infrastructure roles.
· Exposure management may not reliably identify whether UniFi OS systems are internet-reachable, VPN-reachable, internally reachable, reverse-proxied, or accessible from non-administrative segments.
· Reverse-proxy, firewall, secure access, load-balancer, or web telemetry may not preserve enough request path, normalized path, raw path, response status, response size, user agent, source context, or session detail for complete exploit-path reconstruction.
· UniFi OS application telemetry may not preserve sufficient authentication-gateway behavior, protected functionality access, update-endpoint activity, package-management behavior, administrator-session context, API token context, device adoption, backup action, or configuration-change detail.
· Appliance deployments may not expose full process, sudo, package-management, file, memory, or endpoint telemetry to confirm command execution or root-context behavior.
· Administrator audit telemetry may be limited, making it difficult to assess administrator creation, API token activity, session anomalies, device adoption, backup exports, SSH changes, permission changes, or configuration manipulation.
· Downstream configuration telemetry may be limited, making it difficult to validate gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, segmentation, or managed-device impact after suspected compromise.
· DNS, proxy, firewall, NDR, and network-flow telemetry may not reliably connect outbound communication, internal scanning, device enumeration, or additional management-interface access to upstream UniFi OS exploit-path behavior.
· Change-management and incident-response records may not consistently document firmware updates, package operations, controller upgrades, device adoption, backups, gateway changes, firewall changes, VPN changes, DNS changes, wireless changes, vendor support, monitoring, security testing, emergency remediation, or post-remediation validation.
· Organizations may over-rely on vulnerable-version state, KEV status, exposed-interface findings, scanner output, public exploit reporting, suspicious source IPs, or isolated administrative events rather than validating the full UniFi OS management-plane access-to-impact sequence.
Maturity Improvement Priorities
· Normalize UniFi OS asset inventory, exposed management-interface inventory, firmware version records, fixed-version status, approved administration paths, administrator ownership, business ownership, site context, and downstream infrastructure roles.
· Improve management-plane logging across UniFi OS logs, reverse-proxy logs, firewall logs, secure access logs, load-balancer logs, web logs, VPN logs, and request-path visibility.
· Improve UniFi OS application, update-service, package-management, administrator, API token, device-adoption, backup, and configuration-change visibility.
· Improve host-level process, sudo, package-management, file, system, and endpoint telemetry for self-hosted UniFi OS Server deployments and appliance environments that expose those signals.
· Improve downstream configuration telemetry for gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless settings, recorder behavior, storage configuration, segmentation boundaries, and managed-device trust.
· Improve DNS, proxy, firewall, NDR, and network-flow correlation for outbound communication, rare destinations, internal scanning, device enumeration, and access to additional management interfaces.
· Improve change-management and incident-response evidence capture for fixed-version deployment, pre-patch compromise assessment, management-interface isolation, administrator review, API token review, configuration validation, downstream device assurance, and post-remediation monitoring.
· Add UniFi OS control-plane compromise validation steps to SOC, network engineering, firewall administration, wireless operations, infrastructure, identity, legal, compliance, cyber-insurance, communications, business-continuity, and executive reporting workflows.
Maturity Outlook
Maturity can improve quickly if the organization prioritizes UniFi OS asset inventory completeness, management-interface exposure control, fixed-version deployment, administrator-source baselining, request-path logging, update and package telemetry, process and sudo visibility where available, configuration-change logging, downstream device assurance, outbound communication review, change-management discipline, and SOC workflows that connect management-plane access to command execution and network-control impact evidence. The highest-value improvements are exposed management-interface reduction, KEV-driven remediation validation, approved administrator source mapping, update-endpoint monitoring, API token review, configuration integrity validation, downstream gateway and firewall review, VPN and DNS review, wireless review, and post-remediation access correlation.
S37 — Strategic Defensive Improvements
Strategic improvement should reduce the likelihood that attackers can use vulnerable UniFi OS management-plane exposure, authentication bypass, protected functionality access, update or package abuse, command execution, or privileged system behavior to create infrastructure-control uncertainty without detection, and reduce the response burden when UniFi OS compromise cannot be validated quickly. The objective is measurable management-plane-to-network-control resilience and infrastructure trust governance, not patching response alone.
Priority One — Establish Network-Management Trust as a Security Metric
· Define measurable assurance metrics for UniFi OS asset inventory completeness, management-interface exposure control, fixed-version deployment, approved administrator-source coverage, API token governance, update and package visibility, command-execution visibility, sudo and root-context visibility, configuration-change coverage, downstream network-control validation, and post-remediation assurance.
· Track resilience completeness for UniFi OS environments supporting gateways, firewalls, routing, VPN access, DNS behavior, wireless networks, segmentation boundaries, remote sites, customer-facing locations, regulated environments, surveillance infrastructure, storage appliances, and privileged management networks.
· Report unresolved exposed management interfaces, delayed fixed-version deployment, incomplete logging, weak administrator baselines, API token governance gaps, limited configuration visibility, missing downstream device assurance, and post-remediation uncertainty as enterprise risk.
· Treat unexplained UniFi OS management-plane activity, update-path anomalies, command execution, sudo activity, administrator changes, configuration changes, or downstream network-control changes affecting high-value sites as executive-relevant infrastructure trust issues.
Priority Two — Harden UniFi OS Exposure, Patch, and Administrative Access Governance
· Maintain live inventory of UniFi OS systems, exposed management interfaces, firmware versions, fixed-version status, approved management paths, approved administrator sources, VPN administration paths, jump hosts, privileged access workstations, management networks, API tokens, local users, device-adoption workflows, and downstream infrastructure roles.
· Restrict UniFi OS management-plane access to controlled administrative paths and remove unnecessary public exposure, broad VPN reachability, unmanaged source access, and non-administrative network reachability.
· Enforce fixed-version deployment, KEV-driven remediation, emergency exposure reduction, compensating controls, and pre-patch compromise assessment for vulnerable or broadly reachable UniFi OS systems.
· Validate that UniFi OS administration can distinguish approved firmware updates, package operations, controller upgrades, device adoption, backups, gateway changes, firewall changes, routing changes, VPN changes, DNS changes, wireless changes, recorder changes, storage changes, vendor support, monitoring, security testing, and incident response from unmanaged control-plane exposure or attacker-relevant access.
· Reduce broad or informal exceptions that allow high-value UniFi OS systems or sensitive management networks to remain exposed to unnecessary management-plane reachability, weak administrator governance, uncontrolled API token use, or incomplete logging.
Priority Three — Improve Management-Plane, Update, Command, and Privilege Visibility
· Centralize UniFi OS logs, reverse-proxy logs, firewall logs, secure access logs, load-balancer logs, web logs where available, update-service logs, package-management logs, system logs, sudo logs, endpoint telemetry where available, administrator audit records, configuration records, DNS logs, proxy logs, NDR telemetry, change-control records, and incident-response evidence.
· Improve telemetry that links suspicious management-plane access to protected functionality reachability, update-endpoint activity, package behavior, command execution, sudo activity, root-context behavior, administrator-state change, configuration change, outbound communication, and downstream network-control activity.
· Prioritize detection for suspicious management-plane exploit-path activity followed by update or package behavior, unexpected child processes, sudo usage, administrator changes, configuration changes, outbound communication, internal scanning, or downstream infrastructure activity.
· Validate timestamp normalization, field mapping, schema mapping, lookup accuracy, enrichment quality, exception logic, asset tagging, administrator-source mapping, change-window tagging, and SIEM correlation before promoting hunt logic into high-severity alerting.
· Require staged containment review for UniFi OS systems with unresolved command-execution evidence, sudo activity, administrator anomalies, API token anomalies, configuration changes, outbound communication, or downstream network-control uncertainty.
Priority Four — Strengthen Configuration Integrity and Downstream Infrastructure Assurance
· Improve configuration visibility for gateway policy, firewall rules, routing, VPN access, DNS behavior, wireless configuration, SSID security, device adoption, recorder behavior, storage configuration, backup state, segmentation boundaries, and managed-device trust.
· Define rapid response paths for downstream configuration review, gateway and firewall policy validation, VPN access review, DNS review, wireless review, device-adoption review, recorder and storage assurance, backup validation, segmentation review, legal review, cyber-insurance coordination, communications planning, and executive reporting.
· Require correlation between downstream configuration changes and upstream suspicious management-plane activity, administrator anomalies, command-execution evidence, source-context deviation, or missing change records before determining infrastructure-impact confidence.
· Prioritize systems and workflows involving remote-site connectivity, customer-facing operations, regulated environments, executive facilities, production networks, surveillance infrastructure, storage systems, VPN access, DNS control, wireless access, and privileged management networks.
· Maintain rollback procedures for gateway policy, firewall rules, routing, VPN changes, DNS changes, wireless changes, device adoption, recorder settings, storage configuration, and managed-device configuration when suspicious UniFi OS activity is confirmed or strongly suspected.
Priority Five — Improve Network, Outbound, and Post-Remediation Correlation
· Enrich DNS, proxy, firewall, secure web gateway, NDR, endpoint, and network-flow telemetry with UniFi OS asset identity, management-interface context, source context, administrator context, asset role, destination reputation, first-seen context, downstream device role, configuration object, and approved business workflow.
· Monitor suspicious outbound communication after management-plane activity, update-endpoint access, package behavior, command execution, sudo activity, administrator changes, configuration changes, or device-adoption activity.
· Monitor internal scanning, device enumeration, management-interface discovery, SNMP activity, SSH access, web-admin access, API probing, and access to adjacent network-management, security-management, backup, monitoring, recorder, or storage systems after suspected UniFi OS compromise.
· Prevent network-only detections from asserting UniFi OS compromise, root-level access, credential exposure, downstream compromise, or actor attribution without management-plane, host, administrator, configuration, change-management, or incident-response correlation.
· Require post-remediation monitoring to confirm that suspicious UniFi OS management-plane access, administrator activity, API token use, update behavior, outbound communication, and downstream network-control activity have stopped.
Priority Six — Strengthen SOC, Network, Infrastructure, Legal, and Executive Response
· Create or update playbooks for suspicious UniFi OS management-plane access, authentication-bypass indicators, traversal-like request behavior, update-endpoint abuse, package-management anomalies, command execution, sudo activity, root-context behavior, administrator changes, API token activity, device-adoption anomalies, configuration changes, outbound communication, internal scanning, and downstream network-control impact.
· Require responders to validate affected asset, site, role, exposure path, source IP, ASN, geography, management interface, request path, update activity, package activity, process context, sudo activity, administrator identity, API token context, configuration object, downstream device role, change record, and remediation status.
· Require rapid decision paths for management-interface isolation, fixed-version deployment, administrator credential rotation, API token revocation, SSH access review, configuration rollback, gateway and firewall validation, routing review, VPN review, DNS review, wireless review, device readoption review, recorder and storage assurance, segmentation validation, legal and compliance escalation, cyber-insurance coordination, communications planning, affected-operation analysis, and executive reporting.
· Require UniFi OS control-plane compromise validation before affected systems resume unrestricted administration of gateways, firewalls, routing, VPN access, DNS behavior, wireless networks, recorder systems, storage systems, segmentation boundaries, remote sites, customer-facing networks, regulated environments, or privileged management networks.
Strategic Outcome
The organization should be able to prove whether suspicious UniFi OS management-plane activity affected protected functionality, update or package behavior, command execution, sudo or root-context activity, administrator accounts, API tokens, device adoption, configuration integrity, outbound communication, downstream network-control state, or business-critical workflows. It should also be able to scope exposure across asset, site, management interface, source, administrator, API token, session, update path, process, sudo event, configuration object, gateway, firewall rule, VPN path, DNS setting, wireless network, recorder, storage appliance, managed device, change record, remediation action, and business workflow context, then restore infrastructure trust, administrator integrity, configuration confidence, network-control assurance, and business continuity before UniFi OS compromise becomes broad operational disruption.
S38 — Attack Economics & Organizational Impact Model

Figure 7
UniFi OS control-plane compromise through authentication bypass and command injection creates economic exposure because the affected platform may function as a trusted network-management layer rather than an isolated server application. The economic risk is driven by the organization’s need to determine whether suspicious management-plane access moved into protected functionality, update or package abuse, command execution, sudo-assisted or root-context activity, administrator-state changes, configuration manipulation, outbound communication, downstream discovery, or modification of infrastructure controls that support site connectivity, segmentation, remote access, wireless operations, DNS behavior, recorder infrastructure, storage access, and managed-device trust.
UniFi OS control-plane compromise economic impact model showing management-plane exposure, authentication bypass, update or package abuse, command execution, privileged activity, administrator and configuration impact, downstream network-control exposure, business disruption, and executive assurance cost.
The highest economic burden does not come from applying the fixed UniFi OS version alone. It comes from proving whether the organization can still trust affected UniFi OS systems, administrator accounts, API tokens, device-adoption workflows, gateway policies, firewall rules, VPN access, DNS behavior, wireless configuration, recorder functions, storage access, and managed-device state after suspected exploitation. If telemetry is incomplete, response teams may need to expand the investigation across network engineering, firewall administration, wireless operations, infrastructure, SOC, incident response, legal, compliance, cyber insurance, communications, business continuity, and business owners responsible for affected sites or network-dependent workflows.
Primary Economic Drivers
· Emergency fixed-version deployment, management-interface isolation, exposure reduction, and compensating control implementation for vulnerable or broadly reachable UniFi OS systems.
· Investigation of management-plane requests, authentication-validation behavior, traversal-like request activity, update-endpoint access, package-management behavior, system instability, and protected functionality reachability.
· Review of process execution, service-context child processes, sudo usage, root-context activity, local user changes, SSH configuration changes, package changes, file staging, and service modification where host-level telemetry exists.
· Administrator and API-token review, including newly created accounts, rarely used accounts, unusual-source sessions, privilege changes, device-adoption activity, backup exports, configuration exports, and management-plane permission changes.
· Gateway, firewall, routing, VPN, DNS, wireless, recorder, storage, segmentation, and managed-device configuration validation where affected UniFi OS systems administer downstream infrastructure.
· Review of outbound communication, rare destinations, file retrieval, package-repository access, internal scanning, device enumeration, management-interface discovery, and access to adjacent infrastructure.
· Business disruption from emergency management restrictions, site connectivity review, network downtime, firewall or VPN rollback, wireless revalidation, device readoption, help desk surge, administrator lockouts, monitoring gaps, or delayed operations.
· Legal, regulatory, cyber-insurance, communications, customer, workforce, partner, executive, or board-level costs when suspected infrastructure-control compromise affects regulated environments, customer-facing locations, workforce access, physical-security infrastructure, surveillance systems, or critical network services.
Low Impact Economic Pattern
The low impact pattern applies when vulnerable or exposed UniFi OS systems are rapidly updated or isolated, investigation confirms scanning or failed exploit-path activity, and available logs show no command execution, sudo activity, root-context behavior, administrator-state change, configuration export, downstream network-control change, suspicious outbound communication, persistence, credential access, or continued activity after remediation. Economic impact is driven by emergency patch validation, targeted log review, management-interface exposure reduction, administrator baseline validation, limited gateway and VPN confirmation, short-term monitoring, and executive assurance that network-control trust was not materially affected.
Moderate Impact Economic Pattern
The moderate impact pattern applies when exploit-path activity is confirmed or strongly suspected, but downstream business impact remains uncertain or bounded. The organization may need to reconstruct management-plane activity, validate update and package behavior, review endpoint or system telemetry where available, assess administrator and API-token changes, inspect firewall and VPN policy, review routing, DNS, wireless, recorder, and storage state, validate configuration integrity, coordinate cyber-insurance and legal review, and strengthen post-remediation monitoring. Cost increases when telemetry gaps prevent rapid confirmation that command execution, root-context behavior, configuration manipulation, or downstream network-control impact did not occur.
High Impact Economic Pattern
The high impact pattern applies when suspected or confirmed UniFi OS compromise creates uncertainty over root-level control, unauthorized administrator creation, firewall or routing modification, VPN exposure changes, DNS manipulation, wireless trust changes, device-adoption abuse, configuration export, credential exposure, backup tampering, monitoring disruption, recorder or storage compromise, remote-site outage, segmentation weakening, or business-critical network workflows. The organization may need to assume that network-management trust and downstream infrastructure configuration were exposed until technical evidence proves otherwise. Economic exposure can include extended forensics, broad credential and API-token review, configuration rollback, network segmentation validation, outage coordination, legal and privacy review, cyber-insurance engagement, customer or workforce communications, executive reporting, and board-level infrastructure-trust assurance.
Estimated Organizational Impact
· Estimated impact remains consistent with the Block 1 high scenario of $75M to $300M or higher.
· Cost concentration is driven by broad server isolation, tenant-by-tenant validation, customer notification analysis, customer assurance, abuse-infrastructure takedown, DNS and mail remediation, credential rotation at scale, forensic preservation, rebuild or migration activity, legal and regulatory review, insurance engagement, revenue-impact management, and board-level incident governance.
· Business disruption becomes severe when affected hosting-control systems support many customers, high-revenue sites, regulated content, authentication portals, ecommerce workflows, or reseller-managed environments.
Economic Amplification Factors
· Number of exposed hosting-control assets.
· Number of hosted accounts, customer domains, reseller accounts, mailboxes, databases, DNS zones, and webroots administered by affected systems.
· Whether unauthorized administrative access occurred before patch validation.
· Whether suspicious access was followed by privileged execution, account manipulation, hosted-content modification, outbound communication, or tenant-spanning behavior.
· Whether telemetry can support historical compromise review.
· Whether tenant mapping can support confident customer-impact scoping.
· Whether affected infrastructure was used for phishing, malware delivery, spam, redirector infrastructure, credential harvesting, or other abuse operations.
· Whether customer assurance, legal review, regulatory analysis, insurance reporting, or board-level governance is required.
· Whether clean rebuild, migration, backup validation, credential rotation, or restoration gates are needed before returning systems to normal operation.
Organizational Impact Model
The organizational impact model should treat this threat as a control-plane trust problem. When hosting-control trust is weakened, the organization must validate not only software patch status, but also administrative access integrity, hosted-content integrity, credential exposure, tenant impact, outbound abuse, recovery trust, and customer assurance. The cost curve rises sharply when telemetry gaps prevent confident scoping, because uncertainty forces broader containment and more conservative customer-impact assumptions.
S39 — Economic Impact & Organizational Exposure
Estimated Economic Exposure
Enterprise management control-plane compromise, anchored in the direct UniFi OS and UniFi Connect behavior model and extended through validated Coverage With Adaptation mappings, creates an estimated economic exposure range of $450K–$95M+ depending on exposure state, affected asset role, downstream infrastructure dependency, telemetry maturity, configuration-change visibility, incident-response complexity, business disruption, legal review, and executive assurance requirements.
Splunk Enterprise CVE-2026-76264 through CVE-2026-76285 do not change the existing economic-impact ranges. The 22 Coverage With Adaptation vulnerabilities expand the applicable enterprise security-monitoring and management-control-plane exposure to authorization and access-control failures, missing authentication, privilege escalation, operating-system command execution, SQL injection, server-side request forgery, log injection, information disclosure, input-validation weaknesses, denial-of-service conditions, and product-specific security-hardening failures under their respective prerequisites.
Reliable conclusions require Splunk Enterprise product, deployment, and version inventory; management-interface, REST API, Patroni REST API, search-job, SPL2 Module Catalog, and Secure Gateway applicability where relevant; administrator and application-role context; request and authentication telemetry; search and application activity; process and command execution; filesystem and configuration state; security-monitoring and audit-record integrity; remediation status; and incident-response validation. The vulnerabilities should not be represented as one mandatory exploit chain because their affected components, configuration prerequisites, authentication conditions, required privileges, and resulting consequences differ materially.
Splunk documents corrected Enterprise releases 10.4.3, 10.2.7, 10.0.10, and 9.4.15 for the applicable affected branches. Additional remediation requirements apply to CVE-2026-76264, CVE-2026-76265, CVE-2026-76272, and CVE-2026-76280. Available authoritative evidence reviewed for this amendment does not establish confirmed in-the-wild exploitation or CISA Known Exploited Vulnerabilities Catalog status for the 22 identifiers.
Cisco's October 7, 2026 NX-OS and Nexus, Application Policy Infrastructure Controller, License On-Prem, Meraki, and Finesse 35-CVE cohort does not change the existing economic-impact ranges. The cohort expands the applicable enterprise network-management and control-plane exposure to NX-OS and Nexus remote-code-execution conditions, NX-API exploitation, network-policy bypass, control-plane denial of service, Python sandbox escape, APIC command execution and sensitive-file access, License On-Prem authentication, authorization, credential, file, database, code-execution, and management-interface weaknesses, Meraki platform hardening weaknesses, and Cisco Finesse server-side request forgery under vulnerability-specific prerequisites.
Reliable conclusions require affected Cisco product, model, software, and version inventory; feature and service enablement; management-interface, API, web, and network exposure; authentication, authorization, administrator, and privilege context; request, process, command, filesystem, database, configuration, and service telemetry where applicable; control-plane and downstream network effects; remediation state; and incident-response validation. The individual vulnerabilities must not be represented as one mandatory exploit chain because their prerequisites, affected components, required privileges, network position, and security consequences differ materially.
Available authoritative evidence does not establish CISA Known Exploited Vulnerabilities Catalog status for any of the 35 October 7 identifiers. Cisco states that the internally discovered hardening-release vulnerabilities are not known to be actively exploited, and the applicable specific advisories reviewed do not establish confirmed malicious use.
Brocade Fabric OS CVE-2026-94575 through the applicable CVE-2026-94587 identifiers and CVE-2026-87659 through the applicable CVE-2026-87688 identifiers represented in this report do not change the existing economic-impact ranges. The 37 qualifying Coverage With Adaptation vulnerabilities expand the applicable enterprise switching, storage-fabric, and management-control-plane exposure to REST API and WebTools command execution, authentication and authorization bypass, RBAC failure, AAA and federated-authentication weakness, administrative-session abuse, arbitrary file access or manipulation, configuration and firmware-management abuse, certificate-management command injection, Virtual Fabric and fabric-control authorization failure, inter-switch administrative trust abuse, privilege escalation, and privileged or root-context command execution under CVE-specific prerequisites.
Reliable conclusions require affected Brocade Fabric OS switch and version inventory; REST API, WebTools, web-management, and CLI reachability; authentication, AAA, RADIUS, LDAP, TACACS+, SSO, administrator, and privilege context; RBAC and Virtual Fabric state; configuration, firmware, certificate, SNMP, zoning, and fabric-management activity; switch-to-switch and inter-switch administrative relationships; privileged command or process telemetry where available; downstream fabric effects; remediation state; and incident-response validation. The individual vulnerabilities must not be represented as one mandatory exploit chain because their prerequisites, affected functions, privilege requirements, network position, and resulting security effects differ materially.
Available authoritative evidence reviewed for this amendment does not establish CISA Known Exploited Vulnerabilities Catalog status for the 37 qualifying Brocade identifiers.
Cloud Foundry UAA CVE-2026-59357 and CVE-2026-59358 do not change the existing economic-impact ranges. They expand the applicable identity and platform-control-plane exposure to unauthorized authenticated session establishment through the documented self-UAA OIDC trust condition and to privilege-bearing OAuth client-credentials token issuance through reuse of a valid user access token under the documented client configuration.
Reliable conclusions require affected UAA and cf-deployment version inventory; OAuth-client, grant-type, and client-authority configuration; OIDC identity-provider and self-UAA configuration; user and client token issuance; external-OIDC callback and browser-session activity; shadow-account and group-membership state; administrative-scope and downstream platform-access evidence; remediation state; and incident-response validation. Available authoritative evidence reviewed for this amendment does not establish CISA KEV status for either identifier.
Arista CloudVision Portal, CloudVision Sensor, and CloudVision-CUE on-premises CVE-2026-101149 through CVE-2026-101158 and CVE-2026-102155 through CVE-2026-102161 do not change the existing economic-impact ranges. The 17-vulnerability cohort expands the applicable enterprise network-management control-plane exposure to OIDC and SSO request-trust failures, server-side request forgery, authentication-material redirection, stored cross-site scripting and authenticated-session compromise, path traversal and unauthorized file access, XML external entity injection, insecure direct object reference, SQL injection, missing authentication for backend functionality, operating-system command injection, source-address trust and authentication bypass, and LDAP injection under CVE-specific prerequisites.
Reliable conclusions require affected CloudVision Portal, CloudVision Sensor, or CloudVision-CUE asset and version inventory; OIDC, SSO, LDAP, CV-CUE backend, CV-CUE UI, reverse-proxy, authentication, privilege, and network-position context where applicable; API and management-interface activity; identity-provider and session evidence; filesystem, database, directory-service, process, command-execution, and configuration telemetry where available; managed-network and wireless-control effects; remediation state; and incident-response validation. Arista states that it is not aware of malicious exploitation of these vulnerabilities in customer deployments, and available authoritative evidence does not establish CISA KEV status for the 17 identifiers.
Arista's advisories confirm that the prerequisites differ materially across the cohort, including OIDC configuration, external SSO, CV-CUE backend/UI enablement, authenticated administrative privileges, and adjacent-network access depending on the CVE.
VeloCloud Orchestrator On-Prem CVE-2026-93952 does not change the existing economic-impact ranges. It expands the applicable management-control-plane exposure to unauthenticated remote access to privileged internal VCO functionality and potential compromise of the VCO host and data managed by the orchestrator under the documented exposure conditions.
Arista states that exploitation requires certificate-based authentication from VeloCloud Edge to VeloCloud Orchestrator to be configured, access to the public portion of the VeloCloud Edge authentication certificate, and network access to the VCO web interface; VCO tenant or operator credentials are not required. Affected VCO On-Prem releases include 5.2.3.15 and below in the 5.2.x train, 6.1.3.7 and below in the 6.1.x train, 6.4.2.7 and below in the 6.4.x train, and 7.0.0.2 and below in the 7.0.x train. Arista identifies VCO 5.2.3.16 and later in the 5.2.3 train and VCO 6.4.2.8 and later in the 6.4.2 train as fixed, with additional supported-train fixes to be added as available.
Arista states that the issue was discovered externally and is known to be actively exploited. Hosted, including Dedicated, VCO versions were impacted and have already been patched. Reliable conclusions require VCO deployment and version inventory, Edge-to-VCO certificate-authentication configuration, VCO web-interface exposure, web and nginx access logs, backend application logs, system and database logs, filesystem and service state, administrator activity, outbound network behavior, managed Edge state, remediation status, and incident-response validation. Arista-confirmed active exploitation materially increases remediation and retrospective-hunting urgency. CISA added CVE-2026-93952 to the Known Exploited Vulnerabilities Catalog on September 22, 2026, with a remediation due date of September 25, 2026.
Check Point Security Management CVE-2026-93616 does not change the existing economic-impact ranges. It expands the applicable enterprise security-management control-plane exposure to pre-authentication path traversal in the Check Point Management web service, arbitrary-path script execution, and arbitrary Java class loading on affected Security Management systems.
Check Point identifies CVE-2026-93616 as Critical with a CVSS score of 9.8. Affected Security Management releases include R82.20; R82.10 with Jumbo Hotfix Take 44 or lower; R82 with Jumbo Hotfix Take 126 or lower; R81.20 with Jumbo Hotfix Take 166 or lower; R81.10 with Jumbo Hotfix Take 190 or lower; and the documented R80, R80.10, R80.20, R80.30, R80.40, and R81 end-of-support releases. Check Point states that LivePatch Take 28/29 does not address this issue and directs customers to sk1000171 for remediation, mitigation, hunting, indicators of compromise, validation, and upgrade guidance.
Check Point Research reports a handful of pinpointed attacks involving CVE-2026-93616 observed on July 23, 2026. Reliable conclusions require affected Security Management asset and version inventory, management-web service exposure, HTTP request and path telemetry where available, file-upload and script-execution evidence, Java class-loading and process activity, administrator and configuration or security-policy records, managed-gateway and downstream firewall effects, network behavior, remediation state, and incident-response validation. Check Point-confirmed exploitation materially increases remediation and retrospective-hunting urgency. CISA added CVE-2026-93616 to the Known Exploited Vulnerabilities Catalog on September 22, 2026, with a remediation due date of September 25, 2026.
SUSE Rancher CVE-2026-88804 and CVE-2026-88805 do not change the existing economic-impact ranges. They expand the applicable management-control-plane exposure to unauthenticated modification of public UI settings with login-page browser-context script execution and potential administrator bootstrap-password or active-session exposure, and to continued validity of previously obtained public API session tokens after browser logout where server-side token revocation does not occur as expected.
Reliable conclusions require Rancher asset and version inventory, public and authenticated API exposure, public UI settings, login-page and browser-session context, public API session-token state, logout and revocation events, OIDC and identity-provider configuration, administrator activity, RBAC and cluster-management changes, downstream managed-cluster activity, remediation state, and incident-response validation. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for either identifier.
SailPoint IdentityIQ CVE-2026-12342 does not change the existing economic-impact ranges. It expands the applicable identity-governance and enterprise management-control-plane exposure to unauthenticated remote code execution through improper input validation of submitted web-service API content on affected IdentityIQ servers. Affected releases include IdentityIQ 8.3 through 8.3p5, 8.4 through 8.4p4, and 8.5 through 8.5p2.
Reliable conclusions require IdentityIQ asset and version inventory, web-service API reachability, request context where available, authentication and authorization state, application and service process activity, identity-governance workflows, roles and entitlements, connector and configuration state, filesystem or process changes where observable, network behavior, remediation state, and incident-response validation. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status.
FreePBX CVE-2026-54675, CVE-2026-54710, and CVE-2026-75600 do not change the existing economic-impact ranges. They expand the applicable PBX, unified-communications, and management-control-plane exposure to authenticated Soundlang arbitrary file write and follow-on PHP execution, authenticated Superfecta unsafe PHP file inclusion and code execution, and authenticated GraphQL API generatedocs host-command injection with shell-command execution in the FreePBX service context.
Reliable conclusions require FreePBX asset, module, and version inventory, authenticated identity and authorization context, Soundlang upload and conversion activity, Superfecta configuration and source-processing activity, GraphQL and API management activity, file creation or modification, PHP and web-server process activity, Asterisk service and child-process behavior, command execution, telephony configuration, network behavior, remediation state, and incident-response validation. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for these three identifiers.
Zammad CVE-2026-102489 and CVE-2026-102490 do not change the existing economic-impact ranges. They expand the applicable enterprise application and management-control-plane exposure to remote code execution in the Zammad application-user context with potential session leakage, and, under DIVD's findings for CVE-2026-102490, local privilege escalation from the zammad user to root.
DIVD states that its September 21, 2026 breach involved the two Zammad zero-day vulnerabilities. CVE-2026-102489 affects Zammad 6.3.0 through 6.5.4 under DIVD's published record. DIVD also identifies the vulnerability as present in Zammad 7.0.0 through 7.1.3 but not practically exploitable there because of environmental conditions. Zammad states that practical exploitation is limited to Zammad 6.5 and older, that Zammad 7.0 and later are not affected in practice, and that the relevant code was additionally hardened in Zammad 7.2.0.
DIVD identifies CVE-2026-102490 as a local privilege-escalation vulnerability affecting Zammad from 1.5.0 through versions before 7.1.0-alpha and permitting the local zammad user to escalate to root. Zammad states that it had not received sufficient technical detail to independently verify CVE-2026-102490, its scope, or its affected-version range as of October 1, 2026.
Reliable conclusions require Zammad asset and version inventory, application exposure, authentication and session activity, Zammad application-user and service activity, process and child-process telemetry, filesystem and configuration state, privilege-transition and root-context evidence where available, network behavior, remediation state, and incident-response validation. DIVD's reported exploitation materially increases remediation and retrospective-hunting urgency, but vulnerable-version state or ordinary Zammad activity should not by themselves be treated as proof that a specific deployment was compromised.
Kiteworks Core CVE-2026-102132 does not change the existing economic-impact ranges. It expands the applicable enterprise management and secure file-transfer control-plane exposure to authenticated delegated-administrator privilege escalation through improper access control in the administrative import function, creation of a privileged integration credential beyond the intended authorization scope, and consequential elevation to full system-administrator privileges.
Affected Kiteworks Core versions are earlier than 9.5.1; version 9.5.1 is the documented corrected boundary. Reliable conclusions require Kiteworks Core asset and version inventory, delegated-administrator identity and assigned-permission state, administrative import activity, privileged integration-credential creation and use, administrator-role and privilege changes, configuration and audit records, managed-content or connector activity where relevant, remediation state, and incident-response validation. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for CVE-2026-102132.
The lower end reflects contained exposure or failed exploitation with strong telemetry and rapid remediation. The upper end reflects suspected or confirmed control-plane compromise affecting gateway policy, firewall rules, VPN access, DNS behavior, wireless networks, public Wi-Fi gateways, connected-user traffic, recorder infrastructure, storage access, segmentation boundaries, remote sites, regulated environments, customer-facing operations, privileged management networks, enterprise identity infrastructure, directory services, application-host trust, infrastructure-monitoring systems, service-discovery infrastructure, or service-mesh authorization.
kcp CVE-2026-61682 does not change the existing economic-impact ranges. It expands the applicable multi-tenant management-control-plane exposure to authenticated identity-header injection at the kcp front-proxy trust boundary, forged delegated identity and scope data, assertion of system authority, cross-workspace authorization bypass, and unauthorized read, write, or delete access to secrets, RBAC objects, APIExports, APIBindings, LogicalClusters, and other tenant resources.
Affected versions are earlier than 0.31.4 and 0.32.0 through 0.32.1; 0.31.4 and 0.32.2 are fixed. An external proxy that strips all inbound X-Remote-* identity headers can reduce interim exposure, but upgrading is the complete remediation. Reliable conclusions require kcp version and topology inventory, front-proxy and shard request telemetry, raw identity-header visibility where available, authenticated tenant and credential context, delegated-identity and scope data, RBAC and workspace authorization state, secret and object access, APIExport, APIBinding, and LogicalCluster changes, configuration activity, downstream effects, and incident-response validation. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status.
IBM Guardium Data Protection CVE-2026-85542, CVE-2026-84893, CVE-2026-84884, CVE-2026-84882, CVE-2026-84842, CVE-2026-84440, CVE-2026-84278, CVE-2026-84275, CVE-2026-84271, CVE-2026-84250, CVE-2026-84247, CVE-2026-84245, CVE-2026-84244, CVE-2026-84241, CVE-2026-84239, CVE-2026-84108, CVE-2026-84106, CVE-2026-84105, CVE-2026-84089, CVE-2026-84086, CVE-2026-84085, CVE-2026-84084, CVE-2026-84083, CVE-2026-84081, CVE-2026-84077, CVE-2026-84076, CVE-2026-84074, CVE-2026-84070, CVE-2026-84036, CVE-2026-82967, CVE-2026-82896, CVE-2026-82893, CVE-2026-82892, CVE-2026-82890, CVE-2026-82887, CVE-2026-82885, and CVE-2026-82832 do not change the existing economic-impact ranges.
The Guardium cohort expands the applicable enterprise security-management, database-security, appliance-management, and Linux-backed control-plane exposure to command injection with elevated or root execution, SQL injection and sensitive database access, recoverable privileged credentials, arbitrary file writes and deletes, path traversal, local SUID-root privilege escalation, improper authorization, REST privilege escalation, authentication bypass, CSRF, stored and reflected web-input execution, certificate-validation weakness, patch-signature bypass, management-interface access-control failure, and other Guardium-specific privileged appliance behaviors.
The applicable prerequisites and consequences are identifier-specific. They include authenticated GIM bundle import on the Central Manager, authenticated PESI access, authenticated access to reversibly protected internal REST credentials, authenticated Universal Connector Oracle Wallet upload, authenticated Datasource REST operations, authenticated SNMP alert-policy influence, authenticated access to SUID-root wrapper paths, unauthenticated GIM Collector upload, local patch-installer access, local access to weakly protected root-recovery material, local low-privilege access to SUID-root wrappers, authenticated and unauthenticated web paths, and authentication or authorization failures affecting REST or management interfaces.
IBM identifies Guardium Data Protection 12.2 as affected and directs customers to the 12.0p233 update. No workaround is provided.
Reliable conclusions require Guardium Data Protection, Central Manager, Collector, Guardium Installation Manager, appliance-management, REST, import, update, patch, SUID-wrapper, PESI, SNMP, database, filesystem, credential, process, administrator, certificate, and network telemetry appropriate to the specific CVE together with affected-version, remediation-state, and incident-response validation. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for this cohort.
Check Point Security Management and Log Server CVE-2026-91843 does not change the existing economic-impact ranges. It expands the applicable enterprise security-management and logging control-plane exposure to unauthenticated remote code execution with root privileges through the affected login process. Successful exploitation could undermine confidence in centralized security-management policy, administrative trust, management logging, configuration state, or downstream managed-gateway and firewall controls.
Check Point identifies the vulnerability as Critical with a CVSS score of 9.8 and states that there is currently no indication that the vulnerability has been exploited in the wild. The documented remediation is the LivePatch fix in sk1000155; customers with automatic updates enabled are already protected. Check Point further states that Smart-1 Cloud is not affected because the fix has already been implemented there.
Reliable conclusions require Check Point Security Management or Log Server asset and version inventory, deployment and management-interface exposure, login and authentication telemetry, FWM process and child-process activity where available, root-context execution evidence, administrator-session and configuration-change records, downstream managed-gateway and security-policy effects, network behavior, remediation state, and incident-response validation.
WSO2 API Manager, API Control Plane, Traffic Manager, and Universal Gateway CVE-2026-5430 do not change the existing economic-impact ranges. The vulnerability expands the applicable API-management and enterprise control-plane exposure to unauthenticated JWT authentication bypass, unauthorized administrative access, administrative-account compromise, and consequential access to APIs, backend services, configuration, credentials, or data reachable through the affected WSO2 control plane.
WSO2 identifies the vulnerability as Critical, and public reporting confirms malicious exploitation activity. CISA added CVE-2026-5430 to the Known Exploited Vulnerabilities Catalog on September 24, 2026, based on evidence of active exploitation. The KEV designation materially increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification, coverage-register count, or Directly Covered KEV / Exploited Anchor-Product Entry count because WSO2 remains an adapted-coverage platform rather than a UniFi OS / UniFi Connect anchor product. Reliable conclusions require WSO2 product and version inventory, API and management-interface exposure, JWT and token-validation evidence where available, authentication and administrator-session records, API and gateway request telemetry, administrative-state and configuration changes, backend-service activity, credential or sensitive-data access where observable, network telemetry, and incident-response validation.
Issabel Framework CVE-2026-89026 does not change the existing economic-impact ranges. It expands the applicable PBX, unified-communications, and management-control-plane exposure to unauthenticated forged JWT bearer-token access and arbitrary operating-system command execution through the pbxapi manager originate endpoint.
Issabel Framework before commit b97dbaf0b71c1c36f841e672b664afbeb02773bd is affected. Public exploitation evidence was first observed by the Shadowserver Foundation on September 9, 2026.
Reliable conclusions require Issabel Framework and PBX asset and version inventory, pbxapi exposure, JWT and bearer-token evidence where available, API request telemetry, manager-originate parameters, Asterisk application and process telemetry, command and child-process evidence, filesystem and configuration state, network behavior, telephony-service records, and incident-response validation.
Fortinet FortiMail CVE-2026-104286 does not change the existing economic-impact ranges. It expands the applicable email-security-appliance and management-control-plane exposure to unauthenticated path traversal through crafted HTTP or HTTPS requests and arbitrary file write on the underlying FortiMail system.
CISA added CVE-2026-104286 to the Known Exploited Vulnerabilities Catalog on October 1, 2026, based on evidence of active exploitation. Reliable conclusions require FortiMail asset and version inventory, HTTP and HTTPS interface exposure, request and path activity, filesystem and file-write evidence, configuration state, administrator activity, process and service behavior where available, network communication, email-security policy and mail-system state, remediation state, and incident-response validation. The KEV designation materially increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification or establish compromise of a specific local appliance.
Cisco Secure Email Gateway CVE-2026-76461 does not change the existing economic-impact ranges. It expands the applicable email-security-appliance and management-control-plane exposure to unauthenticated crafted-email delivery, SQL injection in Cisco AsyncOS email parsing, arbitrary SQL-statement execution, and consequential command execution with root privileges on the underlying operating system.
CISA added CVE-2026-76461 to the Known Exploited Vulnerabilities Catalog on September 14, 2026, based on evidence of active exploitation. Cisco identifies 15.5.5-014, 16.0.4-302, and 16.5.0-780 as the first fixed releases for the affected release trains, strongly recommends migration to 16.5.0-780, and states that no workaround addresses the vulnerability.
Local impact conclusions require affected-product and version validation, email-message and connection context, Cisco AsyncOS email-processing and mail_logs evidence, database activity where available, process and root-context evidence, filesystem and configuration telemetry, external network and firewall telemetry, administrator-state evidence, and incident-response findings.
CISA Malcolm CVE-2026-90443 through CVE-2026-90457 do not change the existing economic-impact ranges. They expand the applicable security-monitoring and management-control-plane exposure to analyst-session hijacking, reflected cross-site scripting, authenticated command injection, archive path traversal and arbitrary file write, server-side request forgery using elevated service credentials, role and authorization bypass, unauthorized writes in read-only deployments, reverse-proxy authentication-boundary failure, fail-open authorization, default or weak secrets, identity-provider certificate-validation failure, open redirect, security-record tampering, a constrained dependency issue, and weakly protected administrator-password material.
Malcolm releases before v26.06.0 are affected; v26.06.0 or later is the documented remediation boundary. Available authoritative evidence does not establish known public exploitation or CISA KEV status for these fifteen vulnerabilities.
Reliable conclusions require Malcolm asset and version inventory, deployment and interface exposure, analyst identity and session context, request route, method and header context, reverse-proxy and identity-provider configuration, RBAC and role state, certificate-validation state, signing-secret and administrator-secret provenance, upload and archive activity, backend service requests, container and service-process activity, security-record creation or modification, configuration access, and incident-response validation.
The compromised public Wi-Fi gateway activity does not change the existing economic-impact ranges. It expands the applicable downstream exposure to include unauthorized gateway DNS changes, redirection of connected users to attacker-controlled Microsoft 365 credential-harvesting infrastructure, and uncertainty over whether affected users disclosed authentication information.
Cisco IOS XE CVE-2026-20272 does not change the existing economic-impact ranges. It expands the applicable management-platform and network-control exposure to include Cisco IOS XE deployments operating in autonomous or controller-managed modes, device-management services, privileged operating-system functions, network-device configuration activity, and downstream routing, switching, segmentation, VPN, and network-control infrastructure. CVE-2026-20272 represents a Cisco CWE-74 vulnerability-class grouping rather than one uniform exploit path across every affected deployment.
Cisco Unified Intelligence Center CVE-2026-20327 does not change the existing economic-impact ranges. It expands the applicable management-platform exposure to authenticated blind SQL injection through the web-based management interface and unauthorized read access to the affected device's internal database. The vulnerability requires Cisco Unified Intelligence Center-specific asset, authentication, request, database, management-interface, and application telemetry adaptation and should not be treated as evidence that database contents were accessed without local telemetry and investigation findings.
Cisco Unity Connection CVE-2026-20034 and CVE-2026-20035 do not change the existing economic-impact ranges. They expand the applicable application-host exposure to authenticated API-driven root-level code execution and unauthenticated Web Inbox server-side request forgery that may cause arbitrary network requests to originate from an affected device. The vulnerabilities require Cisco Unity Connection-specific validation and engineering adaptation and should not be treated as evidence of successful exploitation or downstream impact without local telemetry and investigation findings.
Tenable Security Center CVE-2026-19626 does not change the existing economic-impact ranges. It expands the applicable management-platform exposure to authenticated non-administrative report-generation access, trusted server-side report rendering, service-account execution, and security-management-platform compromise risk. The vulnerability requires Tenable Security Center-specific validation and engineering adaptation and should not be treated as evidence of successful exploitation or downstream impact without local telemetry and investigation findings.
TrueConf Server CVE-2026-72529 and CVE-2026-72530 do not change the existing economic-impact ranges. They expand the applicable application-host and trusted-software-distribution exposure to unauthorized critical-function access, arbitrary script or code execution, privileged server compromise, web-shell placement, privileged database access, and replacement of legitimate TrueConf client installers with attacker-controlled versions. Public reporting confirms active exploitation, but successful exploitation and downstream impact still require local telemetry and incident-response validation.
MikroTik RouterOS CVE-2026-67276, CVE-2026-67277, CVE-2026-67278, CVE-2026-67279, CVE-2026-67281, and CVE-2026-86060 do not change the existing economic-impact ranges. They expand the applicable network-device and management-plane exposure to SSH authentication bypass, SSH session privilege manipulation, bandwidth-test memory disclosure or remote restart, X.509 validation weakness, unauthenticated SSH command-channel file access, and unauthenticated WebFig file disclosure.
CERT Polska confirms that CVE-2026-67276 and CVE-2026-86060 are combined as the MikroTrick chain to take full control of internet-reachable RouterOS devices with exposed SSH. CISA separately added CVE-2026-67277 and CVE-2026-86060 to the Known Exploited Vulnerabilities Catalog on September 10, 2026, and added CVE-2026-67279 on September 25, 2026 based on evidence of active exploitation. CVE-2026-67277, CVE-2026-67279, and CVE-2026-86060 are CISA KEV-listed. The observed MikroTrick chain and CISA KEV identifier set therefore overlap at CVE-2026-86060 but are not identical.
Fixed RouterOS releases include 6.49.21, 7.23.4, 7.24.2, and 7.25beta3.
Zyxel GS1900 CVE-2026-7273 does not change the existing economic-impact ranges. It expands the applicable network-device and management-plane exposure to a stack-based buffer overflow in the GS1900 CGI management component where a LAN-based unauthenticated attacker can send a crafted HTTP request and potentially execute operating-system commands. Consequential effects may include abnormal device or process behavior, configuration or administrative-state change, unexpected outbound communication, or downstream switching and network-control impact.
Zyxel identifies ten supported GS1900 models with affected 2.90 firmware builds and provides model-specific 2.90 patched builds. CISA has added CVE-2026-7273 to the Known Exploited Vulnerabilities Catalog based on evidence of active exploitation. The vendor-documented prerequisite remains LAN-based access to the affected management plane and should not be generalized to Internet-reachable exploitation without local architecture and exposure evidence.
Reliable conclusions require GS1900 model and firmware inventory, management-interface reachability, source-network context, HTTP and CGI request telemetry where available, device and process behavior, command-execution evidence where observable, administrator and configuration-change records, outbound network activity, switching and downstream network-control state, remediation status, and incident-response validation.
Advantech WISE-6610 and WISE-6610P CVE-2026-79697 and CVE-2026-79698 do not change the existing economic-impact ranges. They expand the applicable network-device and management-plane exposure to authenticated remote command injection through Basic Station certificate-management and Node-RED library administrative functions. The affected firmware identified in the validated disclosure is 1.2.1_20251110, and Advantech firmware 1.2.4_20260821 provides the fixed boundary. Public exploit details are available, but neither vulnerability is currently treated as CISA KEV or as confirmed in-the-wild exploitation.
SonicWall Network Security Manager On-Prem CVE-2026-78327, CVE-2026-78328, and CVE-2026-81939 do not change the existing economic-impact ranges. They expand the applicable management-platform exposure to authenticated SuperAdmin OS command injection and underlying-host command execution, Admin-to-SuperAdmin privilege escalation, and Zip Slip archive-processing behavior capable of extracting files outside the intended destination directory. Affected NSM On-Prem versions are earlier than 4.3.1-R4. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation for these three vulnerabilities.
ASUS Control Center Enterprise CVE-2026-75754 does not change the existing economic-impact ranges. It expands the applicable management-platform exposure to unauthenticated retrieval of an encryption key through an HTTP request, local service-driven enablement of SSH on TCP port 2222, use of hard-coded credentials to obtain a root shell, direct access to or modification of ACC data, and potential remote control of managed servers, PCs, and workstations. ASUS identifies Control Center Enterprise 4.0.0.2 and earlier as affected. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation.
NEC UNIVERGE IX-R/IX-V CVE-2026-16876 does not change the existing economic-impact ranges. It expands the applicable router and management-plane exposure to unauthenticated WebGUI message tampering capable of bypassing authentication and executing arbitrary CLI commands on affected devices. NEC identifies Ver1.1 through Ver1.3, Ver1.4.21 through Ver1.4.28, and Ver1.5.23 as affected and recommends updating to a fixed release or disabling the WebGUI. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation.
Red Hat 389 Directory Server and Cockpit 389 Console CVE-2026-76560, CVE-2026-19843, CVE-2026-19404, CVE-2026-18922, CVE-2026-18651, CVE-2026-18355, and CVE-2026-11770 do not change the existing economic-impact ranges. They expand the applicable enterprise management and identity-control-plane exposure to anonymous or low-privilege authorization bypass, stale or incorrectly retained authentication state, unauthorized Directory Manager authority, unauthorized replication-maintenance operations, LDAP-filter injection and configuration disclosure, authenticated SASL heap corruption with potential remote code execution, and delegated directory-object manipulation that can trigger root-level command execution when a privileged Cockpit 389 Console operator views a crafted entry.
Reliable conclusions require 389 Directory Server or Red Hat Directory Server asset and version inventory, LDAP and LDAPS exposure context, SASL mechanism and bind evidence, ACI and account-lock state, replication extended-operation activity, directory-object and DN change history, Cockpit 389 Console presence and administrator activity, process and root-context execution evidence, configuration and audit records, and incident-response validation. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation for these seven vulnerabilities.
FreeIPA CVE-2026-76578 and CVE-2026-79678 do not change the existing economic-impact ranges. They expand the applicable identity-control-plane exposure above the underlying 389 Directory Server layer to FreeIPA administrator membership, Kerberos principal creation, self-managed OTP token workflows, identity-provider configuration, server-process environment disclosure, and service availability.
CVE-2026-76578 can combine FreeIPA's self-managed-token ACI with the underlying 389 Directory Server authorization flaw to let an unauthenticated LDAP client create an attacker-controlled Kerberos principal and obtain genuine FreeIPA administrators-group membership.
CVE-2026-79678 allows any authenticated IPA principal to cause attacker-controlled identity-provider template values to reach constrained eval() processing before the intended access-control check, permitting server-process environment-variable disclosure and memory-exhaustion denial of service.
FreeIPA 4.13.4 contains the documented fixes. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation for either vulnerability.
Ivanti Neurons for ITSM CVE-2026-12744, CVE-2026-12745, CVE-2026-12645, CVE-2026-12646, CVE-2026-12647, CVE-2026-12650, CVE-2026-12648, and CVE-2026-12651, Ivanti Sentry CVE-2026-83527, and Ivanti Endpoint Manager Mobile CVE-2026-18851 do not change the existing economic-impact ranges. They expand the applicable enterprise management-control-plane exposure to unauthenticated and authenticated server-side remote code execution in Ivanti Neurons for ITSM, unauthenticated administrative access in Ivanti Sentry, and authenticated privilege escalation to administrator in Ivanti Endpoint Manager Mobile.
Reliable conclusions require Ivanti product and branch inventory, cloud-versus-on-premises deployment state, affected and fixed-version validation, management-interface and web/API exposure, session and identity context, authentication requirement, deserialization or protected-function activity, service and child-process lineage, administrator-state change, configuration and managed-device activity, outbound behavior, downstream enterprise-workflow effects, and incident-response validation.
Ivanti states that Neurons for ITSM cloud landscapes were fixed on August 9 and require no customer action. Affected on-premises branches are 2025.2, 2025.3, 2025.4, and 2026.1, with September 2026 security patches available; the on-premises 2026.2 release scheduled for September 21 includes the fixes. Sentry fixed versions are R10.8.2, R10.7.3, and R10.6.4. Endpoint Manager Mobile fixed versions are 12.10.0.0, 12.9.0.2, and 12.8.0.4. Ivanti reports no known customer exploitation at disclosure, and no CISA KEV listing is established for these ten vulnerabilities.
Schneider Electric EcoStruxure IT Data Center Expert CVE-2026-19233 and CVE-2026-8044 do not change the existing economic-impact ranges. They expand the applicable infrastructure-management and application-host exposure to server-side request forgery and argument-injection behavior affecting a centralized data-center infrastructure management platform. Schneider Electric identifies EcoStruxure IT Data Center Expert, formerly StruxureWare Data Center Expert, versions 9.1.2 and prior as affected.
CVE-2026-19233 is an SSRF vulnerability in which a privileged user can provide crafted, unvalidated parameters to an affected server endpoint, potentially causing unauthorized server-side requests, command execution, or disclosure of server data under the documented conditions.
CVE-2026-8044 is an argument-injection vulnerability affecting backup-configuration parameters that may permit a privileged user to achieve remote code execution.
Reliable conclusions require affected-product and version inventory, privileged user and session context, relevant request or backup-configuration activity, process and command telemetry, data-access evidence, configuration state, network behavior, and incident-response validation.
HashiCorp Consul CVE-2026-88021, CVE-2026-87107, CVE-2026-87106, and CVE-2026-87090 do not change the existing economic-impact ranges. They expand the applicable infrastructure-control-plane exposure to service-mesh authorization bypass, unauthorized removal of peer-imported catalog objects, native RPC resource exhaustion before ACL authorization, and catalog node-write authorization bypass capable of deleting another node's registration and taking over its node identity.
CVE-2026-88021 affects Consul Connect intention enforcement where certain characters in service names, namespaces, or partitions may cause generated Envoy RBAC rules to match more broadly than intended.
CVE-2026-87107 affects deployments using cluster peering and may allow a local token with service-write or node-write permission to remove peer-imported services, health checks, or nodes without authority over the peer origin.
CVE-2026-87106 affects the native RPC listener and may allow a client that can complete the internal RPC mTLS handshake to exhaust server memory before ACL authorization is evaluated.
CVE-2026-87090 may allow a token with node-write permission over one node to delete another node's catalog registration and take over its node identity when the target node ID is known.
Consul 2.0.4 and Consul Enterprise 1.21.18, 1.22.12, and 2.0.4 contain the documented fixes for these vulnerabilities.
Reliable conclusions require Consul version inventory, ACL and token configuration, node and service identity, catalog registration and deregistration activity, cluster-peering state, Connect intentions, SPIFFE identities, generated Envoy authorization state, RPC reachability, mTLS client identity, server memory and process telemetry, and downstream service-discovery evidence.
Low Impact Scenario
Estimated Impact
$450K–$2.8M.
Rapid investigation confirms vulnerable or exposed enterprise management-control-plane conditions without evidence of successful command execution, sudo activity, root-context behavior, privileged device activity, unauthorized Directory Manager authority, administrator-state change, privileged directory-object manipulation, unauthorized service-catalog manipulation, service-mesh authorization bypass, configuration export, downstream network-control change, suspicious outbound communication, persistence, credential access, or continued activity after remediation.
Response is limited to emergency fixed-version validation, management-interface or directory-service exposure reduction, targeted log review, administrator and privileged-identity baseline validation, configuration review, Consul catalog and authorization-state validation where applicable, limited downstream control validation, short-term monitoring, and executive assurance that management-plane, network-control, identity-control, and service-control trust were not materially affected.
Moderate Impact Scenario
Estimated Impact
$3.5M–$18M.
Confirmed or strongly suspected control-plane exploit-path activity affects one or more systems that manage business-relevant gateways, network devices, routing, switching, VPN access, DNS behavior, wireless networks, recorder infrastructure, storage appliances, application hosts, enterprise identity services, directory infrastructure, infrastructure-monitoring platforms, service-discovery infrastructure, service meshes, segmentation boundaries, or remote-site connectivity.
The organization cannot immediately determine whether authentication bypass, authorization bypass, stale session identity, improper access control, traversal-like access, update-package command injection, host command injection, privileged directory-service access, replication-control abuse, SQL injection, server-side request forgery, deserialization, argument injection, service-catalog authorization bypass, service-mesh authorization bypass, RPC resource exhaustion, protected-function authorization failure, or operating-system command injection resulted in command execution, privileged device activity, root-context activity, unauthorized Directory Manager authority, administrator changes, privileged directory-object modification, service-identity manipulation, API-token activity, configuration export, credential access, outbound communication, or downstream control-plane modification.
Response requires management-plane and identity-control-plane investigation, affected-service and fixed-version validation, exposed-interface review, LDAP and LDAPS review where applicable, Consul ACL, catalog, peering, RPC, and Connect review where applicable, reverse-proxy and firewall reconstruction where applicable, endpoint, server, application, directory-service, system, or device telemetry review, administrator and privileged-identity review, configuration-integrity validation, downstream device and service assurance, legal and compliance review, cyber-insurance coordination, executive reporting, and strengthened monitoring for post-remediation activity.
High Impact Scenario
Estimated Impact
$22M–$95M+.
Enterprise management control-plane compromise becomes an enterprise-impact event when suspected or confirmed compromise results in host-level command execution, root-level control, privileged network-device control, unauthorized administrator creation, unauthorized Directory Manager authority, directory-service control, privileged directory-object manipulation, replication-control abuse, unauthorized service-catalog or node-identity manipulation, service-mesh authorization bypass affecting protected services, firewall or routing modification, switching or segmentation changes, VPN exposure changes, DNS manipulation, wireless trust changes, configuration export, credential exposure, backup tampering, monitoring disruption, recorder or storage compromise, remote-site outage, identity-service disruption, service-discovery disruption, enterprise-management workflow compromise, managed-device manipulation, or uncertainty over multiple business-critical workflows.
Response may require emergency management-interface or directory-service isolation, service-discovery control-plane isolation, broad platform remediation, root-compromise or privileged-device forensics, privileged identity and Directory Manager credential rotation, gateway and firewall rollback, routing and switching validation, VPN and DNS review, directory-object and replication-state validation, service-catalog reconstruction, service-mesh authorization review, administrator credential rotation, API-token revocation, configuration restore, downstream device or service revalidation, segmentation validation, legal and privacy notification analysis, cyber-insurance engagement, customer or workforce communications planning, executive and board reporting, and formal validation that control-plane and identity trust can safely resume.
Customer, Workforce, and Regulatory Exposure
Customer, workforce, and regulatory exposure should be driven by local evidence of unauthorized control-plane access, authentication or authorization bypass, stale privileged identity, command execution, root-level activity, privileged network-device activity, unauthorized administrator changes, unauthorized Directory Manager authority, privileged directory-object modification, unauthorized service-catalog or node-identity changes, service-mesh authorization bypass, configuration export, firewall, routing, switching, segmentation, VPN, DNS, wireless or directory-service manipulation, ITSM workflow manipulation, mobile endpoint-management actions, public Wi-Fi traffic redirection, credential-harvesting exposure, recorder or storage exposure, infrastructure-monitoring compromise, service-discovery disruption, credential access, downstream device modification, identity-service disruption, application-host compromise, unauthorized management-database access, monitored-database or security-monitoring compromise, or inability to validate containment.
For Splunk Enterprise environments affected by CVE-2026-76264 through CVE-2026-76285, exposure may additionally include unauthorized access to protected REST API or management functionality, misuse of search-job or application permissions, unauthorized information disclosure, SQL injection against applicable SPL2 functionality, server-side requests to internal resources, operating-system command execution through affected Patroni REST API functionality, elevated activity during vulnerable package-upgrade operations, log injection, disruption of management or monitoring services, and reduced confidence in security-monitoring evidence where local telemetry confirms consequential activity. Customer, workforce, privacy, or regulatory impact should be determined from locally validated access, execution, data, monitoring-integrity, and downstream-control evidence rather than vulnerable-version state alone.
For Cisco NX-OS and Nexus, Application Policy Infrastructure Controller, License On-Prem, Meraki, and Finesse environments affected by the October 7 cohort, exposure may additionally include unauthorized management-plane or API access, remote or privileged command execution, root-context activity, unauthorized network-policy bypass, control-plane disruption, unauthorized file or database access, credential or authentication-material exposure, arbitrary file modification, management-interface compromise, unauthorized server-side requests, administrator or configuration changes, service disruption, unexpected outbound communication, and downstream routing, switching, segmentation, application, licensing, wireless, or communications effects where local evidence confirms consequential activity. Customer, workforce, privacy, or regulatory impact should be determined from locally validated access, execution, data, configuration, and downstream-control evidence rather than vulnerability presence alone.
For Brocade Fabric OS environments affected by the qualifying October 6 cohort, exposure may additionally include unauthorized REST API, WebTools, web-management, or CLI activity; authentication or authorization bypass; unauthorized RBAC or administrative privilege; AAA or federated-authentication abuse; arbitrary file access or modification; firmware, configuration, certificate, zoning, Virtual Fabric, or SNMP manipulation; privileged or root-context command execution; inter-switch administrative abuse; unauthorized fabric-control activity; service disruption; unexpected outbound communication; and consequential switching, storage-fabric, segmentation, or downstream infrastructure effects where local evidence confirms consequential activity.
For Cloud Foundry UAA environments affected by CVE-2026-59357 or CVE-2026-59358, exposure may additionally include unauthorized authenticated browser sessions, misuse of OIDC identity relationships, anomalous shadow-account or group mappings, unauthorized OAuth token issuance, privilege-bearing client-only tokens, misuse of client authorities or administrative scopes, unauthorized platform access, and consequential identity or application-control activity where local evidence confirms consequential activity.
For Arista CloudVision Portal, CloudVision Sensor, and CloudVision-CUE on-premises environments, exposure may additionally include unauthorized identity-provider or SSO request redirection, disclosure or misuse of authentication material, unauthorized browser-session activity, access to or modification of files outside intended repository boundaries, unauthorized backend functionality, disclosure of local files or transient user data, database or directory-service manipulation, operating-system command execution, unauthorized administrative sessions, managed wireless or network-configuration changes, service disruption, and loss of confidence in CloudVision management-plane integrity where local evidence confirms consequential activity.
For VeloCloud Orchestrator environments, exposure may additionally include unauthorized access to privileged internal orchestrator functionality, VCO host or data compromise, persistence through unexpected services or files, administrator or configuration changes, credential or trust-material exposure, unexpected outbound communication, and potential downstream access to or manipulation of managed VeloCloud Edge devices where local evidence confirms consequential activity.
For Check Point Security Management environments affected by CVE-2026-93616, exposure may additionally include unauthenticated management-web access leading to arbitrary-path script execution or Java class loading, Management Server compromise, unauthorized administrator or security-policy changes, credential or sensitive configuration exposure, persistence, unexpected outbound communication, and downstream effects on managed Security Gateways or firewall controls where local evidence confirms consequential activity.
For SUSE Rancher environments, exposure may additionally include attacker-controlled modification of public UI settings, script execution in the Rancher login-page browser context, exposure of bootstrap administrator credentials or active administrator sessions, continued use of previously obtained public API session tokens after logout, unauthorized RBAC or cluster-management activity, secret or configuration access, and downstream managed-cluster effects where local evidence confirms consequential activity.
For SailPoint IdentityIQ environments, exposure may additionally include unauthenticated server-side code execution through the web-service API, compromise of the IdentityIQ application-service context, identity-governance workflow manipulation, role or entitlement changes, connector or configuration compromise, credential or sensitive identity-data exposure, persistence, outbound communication, and downstream effects on enterprise systems governed through IdentityIQ.
For FreePBX environments, exposure may additionally include authenticated arbitrary file write, malicious PHP placement or inclusion, shell-command execution in the FreePBX or Asterisk service context, unauthorized telephony or PBX configuration changes, credential or sensitive-data access, persistence, outbound communication, call-control or communications disruption, and uncertainty over downstream communications operations while PBX trust was impaired.
For Zammad environments, exposure may additionally include unauthorized application-context code execution, exposure or misuse of session material, unauthorized activity under the Zammad application-user context, and, where CVE-2026-102490 applies under DIVD's findings, escalation to root-level host control. Consequential exposure may include unauthorized access to or modification of data, configuration, application state, credentials or session material available to the affected application or host, persistence, unexpected outbound communication, and loss of confidence in application-host integrity. Customer, workforce, privacy, or regulatory impact should be determined from locally validated access and data-impact evidence rather than vulnerability presence alone.
For Guardium environments, exposure may additionally include unauthorized access to Guardium internal database information, recovery of administrative REST credentials, arbitrary file modification or deletion, root-level execution, compromised security alerts, modified monitoring or database-security configuration, unauthorized management-interface access, and uncertainty over whether monitored database-security evidence or controls remained trustworthy during the exposure period.
For Issabel Framework environments, exposure may also include unauthenticated forged-token access to PBX administrative functionality, arbitrary operating-system command execution in the Asterisk service context, unauthorized PBX or telephony-service configuration changes, credential or sensitive-data access, persistence, outbound communication, call-control or communications disruption, and uncertainty over downstream communications operations while PBX trust was impaired.
For Fortinet FortiMail environments affected by CVE-2026-104286, exposure may additionally include unauthorized filesystem modification through crafted HTTP or HTTPS requests, arbitrary file placement on the underlying appliance, configuration or security-policy modification, credential or sensitive-data exposure where consequential access occurred, persistence, unexpected outbound communication, disruption or manipulation of email-security functions, and uncertainty over messages, policies, or downstream systems processed while appliance trust was impaired.
For Cisco Secure Email Gateway environments, exposure may also include root-level appliance compromise initiated through malicious email content, unauthorized database activity, security-configuration modification, credential or sensitive-data access, persistence, outbound communication, disruption or manipulation of email-security functions, and uncertainty over messages or downstream systems processed while appliance trust was impaired.
For Malcolm environments, exposure may also include analyst-session compromise, unauthorized access to internal services or administrative functions, command execution in affected containers, arbitrary file writes, fabricated or modified security-monitoring records, configuration tampering, credential or secret exposure, and reduced confidence in monitoring evidence used for incident investigation or regulatory response.
For Logsign SIEM CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926, control-plane and monitoring-data trust are reduced when authentication and administrator sessions, process or child-process execution, file or configuration changes, credential or secret access, outbound activity, administrator changes, connector or ingestion changes, alerting or logging gaps, or SIEM-record modification cannot be reconciled with expected users, approved configuration, and authorized security-monitoring activity. Trust restoration requires deployment of Logsign SIEM 6.4.117 or later, validation that default administrative credentials are no longer present, review of pre-remediation authentication and administrator activity, process and child-process evidence, files and configuration, credential and secret state, network activity, connector and ingestion configuration, alerting and logging continuity, and independent validation of SIEM-record integrity, followed by post-remediation monitoring.
For FreeIPA, exposure may also include unauthorized creation of attacker-controlled Kerberos principals, unauthorized administrators-group membership, privileged directory and identity operations, exposure of server-process environment variables, possible disclosure of administrator or Directory Manager credentials where deployment context places those secrets in the affected process environment, and downstream use of identity-control-plane trust.
For Ivanti environments, exposure may also include unauthorized service-management execution, administrator-level Sentry access, EPMM administrator privilege, enterprise workflow modification, managed-device actions, sensitive management-data access, configuration changes, or downstream use of centralized management authority.
For EcoStruxure IT Data Center Expert environments, exposure may also include unauthorized server-side requests, command execution, disclosure of server data, backup-workflow abuse, or loss of trust in centralized infrastructure-monitoring operations.
For Consul environments, exposure may also include unauthorized deletion or takeover of node identity, removal of peer-imported services or health checks, control-plane denial of service, unintended service-to-service access, service-discovery disruption, or application-routing effects.
For Zyxel GS1900 environments, exposure may also include unauthorized command execution on the affected switch, configuration or administrative-state modification, switching or segmentation changes, unexpected outbound communication, loss of confidence in port or VLAN state, and downstream network-control effects where local telemetry confirms consequential activity.
Vulnerable version state, internet exposure, LDAP or LDAPS reachability, management-interface reachability, Consul control-plane reachability, maximum CVSS score, CISA KEV status, or ordinary administrative activity should increase urgency but should not by themselves be treated as proof of reportable compromise without environment-specific evidence.
Residual Economic Risk
Residual economic risk remains when vulnerable management platforms or directory services were exposed before remediation, when request-path or LDAP telemetry is incomplete, when host-level process or sudo visibility is unavailable, when effective bind identity cannot be reconstructed, when administrator-state or privileged directory-object changes cannot be fully reviewed, when replication activity cannot be reconstructed, when authorization or role-state evidence is incomplete, when configuration-change records are incomplete, when Consul catalog, peering, or Connect state cannot be fully reconstructed, when downstream systems lack reliable configuration or managed-device telemetry, or when post-remediation monitoring cannot prove that suspicious access stopped.
For Splunk Enterprise CVE-2026-76264 through CVE-2026-76285, deployment of the applicable corrected Enterprise release and completion of any CVE-specific additional remediation reduce future exposure but do not independently prove that affected management functions, REST API endpoints, search jobs, applications, SPL2 functionality, Secure Gateway components, package-upgrade workflows, or Patroni REST API functionality were not accessed, manipulated, or exploited before remediation.
Where pre-remediation exposure existed, organizations should review affected Splunk Enterprise versions, enabled services, management and REST API reachability, authentication and authorization activity, administrator and application-role state, search-job access, SPL2 and Secure Gateway activity where applicable, Patroni REST API exposure and requests, process and command execution, package-upgrade activity, filesystem and configuration changes, logging continuity, security-monitoring evidence integrity, unexpected outbound communication, remediation state, and incident-response findings. Residual risk should remain open where the organization cannot reconstruct the relevant pre-remediation period or independently validate that unauthorized access, execution, privilege escalation, information disclosure, monitoring manipulation, or service disruption did not occur.
For the Cisco October 7, 2026 35-CVE cohort, deployment of the applicable Cisco-fixed release reduces future risk but does not independently prove that an affected NX-OS, Nexus, APIC, License On-Prem, Meraki, or Finesse system was not accessed, exploited, modified, disrupted, or used to affect downstream infrastructure before remediation.
Where pre-remediation exposure existed, organizations should review affected-product and software inventory, enabled features and services, management-interface and API activity, authentication and administrator sessions, privilege and role state, HTTP and application requests where applicable, command and process execution, filesystem and database activity, configuration changes, control-plane state, service availability, unexpected outbound requests, routing, switching, segmentation, wireless, licensing, and communications effects, remediation state, and incident-response findings. Residual risk should remain open where the organization cannot reconstruct the applicable pre-remediation period or independently validate that unauthorized execution, policy bypass, file or database access, administrative control, service disruption, or downstream network-control effects did not occur.
For the qualifying Brocade Fabric OS October 6 cohort, deployment of the applicable vendor-fixed Fabric OS release reduces future risk but does not independently prove that a previously affected switch, management interface, administrative session, or fabric relationship was not accessed, manipulated, or used for privileged activity before remediation.
Where pre-remediation exposure existed, organizations should review Fabric OS version and switch inventory, REST API and WebTools activity, CLI and administrative sessions, authentication and AAA events, RADIUS, LDAP, TACACS+, and SSO activity, RBAC and privilege changes, configuration and firmware operations, certificate and SNMP management, zoning and Virtual Fabric changes, inter-switch administrative communications, privileged command and process activity where available, downstream fabric state, remediation evidence, and incident-response findings. Residual risk should remain open where the organization cannot reconstruct the applicable pre-remediation period or independently validate that unauthorized access, privilege escalation, command execution, configuration manipulation, or consequential fabric-control effects did not occur.
For Cloud Foundry UAA CVE-2026-59357 and CVE-2026-59358, deployment of UAA v79.7.0 or later and, where applicable, cf-deployment v60.5.0 or later reduces future risk but does not independently prove that unauthorized session establishment or privilege-bearing token issuance did not occur before remediation.
Where pre-remediation exposure existed, organizations should review UAA and cf-deployment versions, OAuth-client configuration, supported grant types, client authorities, OIDC identity-provider and self-UAA relationships, token issuance, external-OIDC callback activity, browser sessions, shadow-account and group mappings, administrative scopes, downstream platform access, remediation state, and incident-response findings. Residual risk should remain open where the organization cannot reconstruct the affected authentication and token-issuance period or independently validate that unauthorized sessions, tokens, identity mappings, or consequential platform activity did not occur.
For the Arista CloudVision Portal, CloudVision Sensor, and CloudVision-CUE on-premises 17-CVE cohort, deployment of the applicable Arista-fixed release reduces future risk but does not independently prove that a previously affected management platform, Sensor, CV-CUE backend, or CV-CUE UI was not accessed or manipulated before remediation.
Where pre-remediation exposure existed, organizations should review CloudVision and CV-CUE authentication and administrator activity, OIDC and SSO provider configuration, identity-provider redirects and session evidence, API and management-interface requests, CV-CUE backend and UI state, reverse-proxy or source-address handling where applicable, file and repository activity, Sensor data access, database and LDAP activity, process and command-execution evidence, configuration and wireless-management changes, network behavior, remediation state, and incident-response findings. Residual risk should remain open where the organization cannot reconstruct the applicable pre-remediation period or independently validate that unauthorized access, session compromise, file manipulation, command execution, administrative control, or downstream management effects did not occur.
For VeloCloud Orchestrator On-Prem CVE-2026-93952, deployment of an applicable fixed VCO release reduces future risk but does not independently prove that a previously exposed orchestrator was not exploited before remediation.
Where pre-remediation exposure existed, organizations should preserve and review VCO web access logs, backend application logs, system logs, database logs, relevant filesystem timestamps, service and process state, administrator activity, outbound network behavior, and managed Edge state; evaluate credential rotation and restoration or replacement of affected orchestrator instances from trusted sources where compromise is suspected; and validate that suspicious activity did not continue after remediation.
For Check Point Security Management CVE-2026-93616, deployment of the applicable sk1000171 remediation or a later vendor-fixed release reduces future risk but does not independently prove that a previously affected Management Server was not exploited before remediation.
Where pre-remediation exposure existed, organizations should review management-web requests and path activity, file-upload and filesystem state, unexpected script execution, Java class loading, process activity, administrator sessions, configuration and security-policy changes, managed-gateway and downstream firewall effects, outbound network behavior, remediation state, and incident-response evidence. Residual risk should remain open where the organization cannot reconstruct the pre-remediation management-web and host-execution period or independently validate that unexpected execution, policy manipulation, persistence, or downstream security-control effects did not occur.
For SUSE Rancher CVE-2026-88804 and CVE-2026-88805, deployment of an applicable vendor-fixed Rancher release reduces future risk but does not independently prove that public UI settings were not modified, browser-context script execution did not occur, administrator sessions or bootstrap credentials were not exposed, or previously obtained public API session tokens were not used after logout before remediation.
Where pre-remediation exposure existed, organizations should review Rancher public UI setting changes, login-page content, browser and administrator-session evidence, public API session-token issuance and use, logout and revocation events, OIDC and identity-provider activity, RBAC and cluster-management changes, secret and configuration access, downstream managed-cluster activity, and incident-response findings.
For SailPoint IdentityIQ CVE-2026-12342, deployment of the applicable vendor-fixed IdentityIQ patch level reduces future risk but does not independently prove that the vulnerable web-service API was not used for unauthenticated server-side execution before remediation.
Where pre-remediation exposure existed, organizations should review web-service API activity, application and service process behavior, filesystem and configuration changes, identity-governance workflow activity, role and entitlement changes, connector activity, outbound communication, credential or sensitive-data access where observable, and incident-response evidence.
For FreePBX CVE-2026-54675, CVE-2026-54710, and CVE-2026-75600, deployment of the applicable fixed Soundlang, Superfecta, or API module version reduces future risk but does not independently prove that authenticated administrative access was not used for arbitrary file write, PHP execution, or shell-command execution before remediation.
Where pre-remediation exposure existed, organizations should review authenticated sessions, Soundlang upload and conversion activity, Superfecta configuration and source-processing activity, GraphQL API generatedocs requests, file creation and modification, PHP and web-server process behavior, Asterisk process and child-process activity, operating-system commands, telephony configuration changes, outbound network behavior, and incident-response evidence.
For kcp CVE-2026-61682, upgrading to 0.31.4, 0.32.2, or a later applicable fixed version reduces future risk but does not independently prove that a previously affected authenticated tenant did not inject trusted identity headers or cross workspace boundaries before remediation.
External proxy stripping of inbound X-Remote-* headers is an interim mitigation and should not replace version remediation.
Where pre-remediation exposure existed, organizations should review effective identity, group and scope data, workspace and RBAC activity, secret and object access, APIExport, APIBinding, LogicalCluster changes, and downstream effects.
For the IBM Guardium Data Protection 37-CVE cohort, deployment of 12.0p233 or a later applicable fixed update reduces future risk but does not independently prove that a previously affected Guardium appliance was not accessed, modified, or used to reach privileged functions before remediation.
Because IBM provides no workaround for the cohort, organizations with pre-remediation exposure should review the specific affected management, GIM, REST, PESI, SNMP, SUID-wrapper, patch, import, file, credential, database, web, certificate, or privilege path applicable to the CVE; the associated authentication or authorization evidence; privileged process activity; filesystem and database state; credential use; Central Manager and Collector activity; network behavior; and downstream security-monitoring integrity.
For Check Point Security Management and Log Server CVE-2026-91843, application of the LivePatch fix in sk1000155, automatic-update protection, or other applicable vendor remediation reduces future exposure but does not independently prove that a previously vulnerable Security Management or Log Server was not exploited before remediation.
Where pre-remediation exposure existed, organizations should review login and authentication activity, FWM and related process behavior, unexpected child processes, root-context execution, administrator sessions, configuration and security-policy changes, managed-gateway and downstream firewall effects, outbound network activity, remediation state, and incident-response evidence.
Residual risk should remain open until the organization can establish that suspicious pre-remediation activity did not result in root-level execution or downstream security-control manipulation.
For Issabel Framework CVE-2026-89026, deployment of code at or after commit b97dbaf0b71c1c36f841e672b664afbeb02773bd or an applicable vendor-fixed release reduces future risk but does not independently prove that a vulnerable PBX was not exploited before remediation.
Where pre-remediation exposure existed, organizations should review pbxapi access, JWT and bearer-token activity where available, manager-originate requests, Asterisk application and process behavior, operating-system command execution, filesystem and configuration changes, outbound network activity, telephony-service effects, and incident-response evidence.
Residual risk should be carried forward into the risk register until management-plane exposure, directory-service exposure, affected-service scope, fixed-version deployment, administrator trust, privileged-identity trust, directory-object integrity, service-catalog integrity, service-mesh authorization integrity, application-host or device trust, downstream state, and monitoring coverage are validated.
For Zammad CVE-2026-102489, migration from affected Zammad 6.5-and-older deployments to a currently supported Zammad 7 release reduces future exposure to the documented remote-code-execution condition. Zammad states that 7.0 and later are not practically affected by CVE-2026-102489 and that the relevant code was additionally hardened in Zammad 7.2.0. Remediation does not independently prove that a previously vulnerable deployment was not exploited before upgrade.
CVE-2026-102490 requires separate treatment. DIVD identifies a local zammad-user-to-root privilege-escalation condition, while Zammad states that it had not received sufficient technical detail to independently verify the vulnerability, its mechanism, or its affected-version range as of October 1, 2026. Organizations should therefore follow current Zammad security guidance and subsequent vendor updates rather than treating CVE-2026-102489 remediation as proof that CVE-2026-102490 has also been resolved.
Where pre-remediation exposure existed, organizations should review Zammad authentication and session activity, application and service-user activity, process and child-process execution, filesystem and configuration changes, privilege-transition and root-context evidence where available, network activity, persistence indicators, remediation state, and incident-response findings. Residual risk should remain open where the organization cannot reconstruct the pre-remediation period or independently validate that unauthorized application execution, session exposure, privilege escalation, or consequential host activity did not occur.
For Fortinet FortiMail CVE-2026-104286, vendor remediation reduces future exposure but does not independently prove that a previously vulnerable or reachable FortiMail appliance was not exploited before remediation.
Where pre-remediation exposure existed, organizations should review HTTP and HTTPS request and path activity, filesystem and file-write evidence, configuration and email-security policy state, administrator activity, process and service behavior where available, network communication, mail-system state, persistence indicators, remediation state, and incident-response evidence. Residual risk should remain open where the organization cannot reconstruct the pre-remediation exposure period or independently validate that unauthorized file writes or consequential appliance activity did not occur.
For Cisco Secure Email Gateway CVE-2026-76461, deployment of Cisco AsyncOS 15.5.5-014, 16.0.4-302, 16.5.0-780, or a later applicable fixed release reduces future risk but does not independently prove that a vulnerable appliance was not exploited before remediation.
Cisco strongly recommends migration to 16.5.0-780 and states that no workaround addresses the vulnerability.
Where pre-remediation exposure existed, organizations should review relevant message and connection activity, mail_logs for suspicious SQL statements, email-processing behavior, database evidence where available, process and root-context activity, filesystem and configuration changes, administrator state, external network and firewall telemetry, outbound communication, persistence indicators, and incident-response evidence.
For CISA Malcolm CVE-2026-90443 through CVE-2026-90457, deployment of v26.06.0 or later reduces future risk but does not independently prove that pre-remediation analyst sessions, administrative functions, internal service requests, container activity, file or archive workflows, security-monitoring records, configuration state, or credential material were not affected.
Where pre-remediation exposure existed, organizations should validate session integrity, proxy and identity-provider state, record integrity, affected containers and services, credential and secret state, and post-remediation activity.
For Logsign SIEM CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926, deployment of Logsign SIEM 6.4.117 or later reduces future risk but does not independently prove that a previously affected SIEM was not accessed through default administrative credentials, traversed through the vulnerable path, or used for code injection before remediation. Where pre-remediation exposure existed, organizations should review authentication and administrator sessions, process and child-process activity, file and configuration changes, credential and secret access, outbound network activity, connector and ingestion changes, alerting and logging continuity, and the integrity of security-monitoring records. Default or exposed administrative credentials and other affected secrets should be rotated where local evidence supports possible access, and residual risk should remain open where the organization cannot independently validate the integrity of SIEM evidence used for detection, investigation, or regulatory response.
For CVE-2026-76578, upgrading to FreeIPA 4.13.4 or an applicable vendor-fixed package and restricting LDAP exposure reduce future risk but do not independently prove that an unauthenticated client did not create an attacker-controlled OTP token or Kerberos principal, obtain administrators-group membership, perform privileged directory operations, or alter downstream identity state before remediation.
For CVE-2026-79678, upgrading to FreeIPA 4.13.4 or an applicable vendor-fixed package reduces future risk but does not independently prove that an authenticated low-privilege principal did not use idp-add template processing to disclose server-process environment variables or cause memory exhaustion before remediation.
Where a containerized deployment may have retained administrator or Directory Manager credentials in the affected process environment, credential exposure should be evaluated and affected secrets rotated when local evidence supports disclosure.
For the eight Ivanti Neurons for ITSM vulnerabilities, deployment of the September 2026 security patches or an applicable fixed release reduces future risk but does not independently prove that an affected on-premises system was not accessed through an unauthenticated or authenticated RCE path before remediation.
Where pre-remediation exposure existed, organizations should validate web/API activity, application-service and child-process behavior, file and configuration changes, outbound communication, privileged follow-on, and downstream workflow effects.
For Ivanti Sentry CVE-2026-83527 and Ivanti Endpoint Manager Mobile CVE-2026-18851, deployment of the fixed versions reduces future risk but does not independently prove that unauthorized administrator access or privilege escalation did not occur before remediation.
Administrator sessions, role changes, configuration activity, managed-device actions, and downstream effects should be reviewed where local exposure warrants.
For EcoStruxure IT Data Center Expert CVE-2026-19233 and CVE-2026-8044, deployment of an applicable vendor-fixed version reduces future risk but does not independently prove that crafted privileged requests or backup-configuration parameters were not used before remediation.
Pre-remediation privileged activity, server-side requests, process execution, data access, configuration changes, and downstream monitoring effects should be reviewed where local exposure warrants.
For Consul CVE-2026-88021, CVE-2026-87107, CVE-2026-87106, and CVE-2026-87090, deployment of Consul 2.0.4 or the applicable Consul Enterprise fixed release reduces future risk but does not independently prove that unauthorized catalog manipulation, peer-object deletion, RPC resource exhaustion, or unintended Connect service access did not occur before remediation.
Catalog history, ACL token use, node identity, peering state, Connect policy, RPC activity, service availability, and downstream service effects should be reviewed where local exposure warrants.
For Zyxel GS1900 CVE-2026-7273, deployment of the applicable model-specific patched 2.90 firmware reduces future risk but does not independently prove that a previously vulnerable switch was not exploited before remediation.
Where pre-remediation LAN-based management access existed, organizations should review management-interface reachability, HTTP and CGI activity where available, source-network context, device and process anomalies, administrator and configuration changes, outbound network behavior, switch configuration, VLAN and segmentation state where applicable, downstream network effects, and incident-response evidence.
Residual risk should remain open where the organization cannot reconstruct pre-remediation management activity or independently validate that unexpected command execution, configuration change, or downstream switching impact did not occur.
Proof-of-Concept / KEV Behavioral Coverage Assessment
Splunk Enterprise SVD-2026-1001 and SVD-2026-1002, published October 7, 2026, comprise 22 distinct Coverage With Adaptation CVEs.
SVD-2026-1001 comprises CVE-2026-76264, CVE-2026-76265, CVE-2026-76266, CVE-2026-76267, CVE-2026-76268, CVE-2026-76269, CVE-2026-76270, CVE-2026-76271, CVE-2026-76272, CVE-2026-76273, CVE-2026-76274, CVE-2026-76275, CVE-2026-76276, CVE-2026-76277, CVE-2026-76278, CVE-2026-76279, and CVE-2026-76280. The advisory spans REST API authorization and access-control failures, Linux package-upgrade privilege escalation, log injection, missing authentication in the Patroni REST API with potential operating-system command execution, search-job access-control failures, SPL2 Module Catalog SQL injection, denial of service, server-side request forgery, information disclosure, input-validation weaknesses, SPL2 module-permission authorization bypass, and incorrect permission assignment in Splunk Secure Gateway.
SVD-2026-1002 comprises CVE-2026-76281, CVE-2026-76282, CVE-2026-76283, CVE-2026-76284, and CVE-2026-76285. The advisory documents five grouped hardening findings associated with improper access control, improper resource-lifecycle control, protection-mechanism failure, improper neutralization, and improper adherence to coding standards. These identifiers should not be assigned more specific exploitation consequences without CVE-specific supporting evidence.
The 22 identifiers remain Coverage With Adaptation because reliable attribution requires Splunk-specific asset and version inventory, affected component and feature applicability, authentication and authorization context, management and REST API activity, Patroni REST API exposure, application and search-job permissions, SPL2 and Secure Gateway state, package-management activity, process and command telemetry, filesystem and configuration evidence, security-monitoring integrity, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
The cohort adds 22 Coverage With Adaptation CVEs and 0 Direct Coverage CVEs. Coverage With Adaptation increases from 395 to 417 and the total CVE register increases from 407 to 429. Available authoritative evidence reviewed for this amendment does not establish CISA KEV status or confirmed in-the-wild exploitation for the 22 identifiers. The Directly Covered KEV / Exploited Anchor-Product Entry count remains 3.
Cisco's October 7, 2026 security-advisory package adds 35 Coverage With Adaptation entries across Cisco NX-OS Software and Nexus platforms, Cisco Application Policy Infrastructure Controller, Cisco License On-Prem, Cisco Meraki platforms, and Cisco Finesse.
The NX-OS and Nexus portion comprises 14 identifiers: CVE-2026-76453, CVE-2026-76455, CVE-2026-76456, CVE-2026-76457, CVE-2026-76458, CVE-2026-76459, CVE-2026-76465, CVE-2026-76485, CVE-2026-76486, CVE-2026-76501, CVE-2026-76471, CVE-2026-20038, CVE-2026-20173, and CVE-2026-20032. The cohort spans NX-OS hardening weaknesses, MPLS OAM and NGOAM remote-code-execution conditions, NX-API remote code execution, ACI endpoint-group contract bypass, control-plane denial of service, and Python sandbox escape.
The Cisco Application Policy Infrastructure Controller portion comprises five identifiers: CVE-2026-76498, CVE-2026-76499, CVE-2026-76500, CVE-2026-20321, and CVE-2026-76488. The cohort includes APIC hardening weaknesses, authenticated API command injection capable of root-context execution, and authenticated unauthorized sensitive-file access.
The Cisco License On-Prem portion comprises eight identifiers: CVE-2026-76480, CVE-2026-76482, CVE-2026-76483, CVE-2026-76484, CVE-2026-20328, CVE-2026-76437, CVE-2026-76452, and CVE-2026-76454. The cohort includes authentication, authorization, credential-protection, code-execution, SQL-injection, arbitrary-file-write, availability, password-reset, and management-interface weaknesses.
The Cisco Meraki portion comprises seven identifiers: CVE-2026-76463, CVE-2026-76464, CVE-2026-76467, CVE-2026-76468, CVE-2026-76469, CVE-2026-76470, and CVE-2026-76472. These remain product-specific adapted coverage because reliable attribution requires affected Meraki product and firmware inventory, network position, device and cloud-management telemetry, configuration state, administrator activity, traffic evidence, remediation state, and downstream network effects beyond the UniFi OS / UniFi Connect anchor model.
Cisco Finesse CVE-2026-20362 is a Coverage With Adaptation entry mapping unauthenticated server-side request forgery in the Finesse web-based management interface to attacker-influenced server-side requests and potential limited sensitive-information exposure from services reachable by the affected system.
All 35 identifiers remain Coverage With Adaptation because reliable attribution requires Cisco product-specific assets, versions, feature state, exposure conditions, identity and privilege context, management-interface and API evidence, process, command, filesystem, database, configuration, service, and network telemetry appropriate to the applicable vulnerability beyond the UniFi OS / UniFi Connect anchor model.
The cohort adds 35 Coverage With Adaptation CVEs and 0 Direct Coverage CVEs. Available authoritative evidence does not establish CISA KEV status for any of the 35 identifiers. The Directly Covered CVE count remains 12, Coverage With Adaptation increases from 321 to 356, and the total CVE register increases from 333 to 368.
Broadcom's October 6, 2026 Brocade Fabric OS disclosure package contains 48 CVEs. Thirty-seven identifiers are represented in this report as Coverage With Adaptation because their documented behaviors align with the existing enterprise management-control-plane compromise model while requiring Brocade-specific asset, version, management-interface, authentication, authorization, fabric, and remediation context.
The qualifying Brocade identifiers are CVE-2026-94587, CVE-2026-94586, CVE-2026-94585, CVE-2026-94584, CVE-2026-94583, CVE-2026-94581, CVE-2026-94580, CVE-2026-94579, CVE-2026-94578, CVE-2026-94577, CVE-2026-94576, CVE-2026-94575, CVE-2026-87688, CVE-2026-87687, CVE-2026-87686, CVE-2026-87685, CVE-2026-87684, CVE-2026-87683, CVE-2026-87682, CVE-2026-87681, CVE-2026-87680, CVE-2026-87679, CVE-2026-87678, CVE-2026-87677, CVE-2026-87675, CVE-2026-87674, CVE-2026-87673, CVE-2026-87672, CVE-2026-87670, CVE-2026-87669, CVE-2026-87667, CVE-2026-87666, CVE-2026-87664, CVE-2026-87663, CVE-2026-87662, CVE-2026-87660, and CVE-2026-87659.
The cohort spans REST API and WebTools management-plane command execution, authentication and authorization bypass, RBAC failure, AAA and federated-authentication weaknesses, administrative-session and identity-context abuse, arbitrary file access or manipulation, firmware and configuration-management abuse, certificate-management command injection, management-interface code-execution paths, Virtual Fabric and fabric-management authorization failures, inter-switch administrative trust abuse, privilege escalation, and privileged or root-context command execution.
The remaining 11 identifiers in the governing October 6 disclosure are not added to the production CVE register because their validated conditions are denial-of-service-only, underlying third-party or operating-system component issues, or otherwise lack sufficient management-control-plane relevance under the current production threshold.
Available authoritative evidence reviewed for this amendment does not establish CISA KEV status for the 37 qualifying Brocade identifiers. The Brocade cohort adds 37 Coverage With Adaptation CVEs and 0 Direct Coverage CVEs, increasing Coverage With Adaptation from 356 to 393 and the total CVE register from 368 to 405.
Cloud Foundry UAA CVE-2026-59357 and CVE-2026-59358 are Coverage With Adaptation entries.
CVE-2026-59357 maps the documented self-UAA OIDC trust condition to unauthorized authenticated external-OIDC browser-session establishment. CVE-2026-59358 maps reuse of a valid user access token in the affected client-credentials path to issuance of a client-only token carrying the OAuth client's configured authorities.
The two identifiers remain Coverage With Adaptation because reliable attribution depends on UAA and cf-deployment asset and version inventory, OAuth-client and grant-type configuration, client-authority state, OIDC identity-provider and self-UAA configuration, token issuance, browser-session state, shadow-account and group-membership context, administrative-scope activity, downstream platform access, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
Available authoritative evidence reviewed for this amendment does not establish CISA KEV status for either identifier. The Cloud Foundry cohort adds two Coverage With Adaptation CVEs and 0 Direct Coverage CVEs, increasing Coverage With Adaptation from 393 to 395 and the total CVE register from 405 to 407.
Arista CloudVision Portal, CloudVision Sensor, and CloudVision-CUE on-premises CVE-2026-101149 through CVE-2026-101158 and CVE-2026-102155 through CVE-2026-102161 are 17 Coverage With Adaptation entries.
The identifiers represent distinct management-control-plane weaknesses and should not be represented as one mandatory exploit chain. The cohort includes OIDC and SSO request-trust failures and server-side request forgery, open-redirection and authentication-material redirection, stored cross-site scripting, path traversal and unauthorized file access, XML external entity injection, insecure direct object reference, SQL injection, missing authentication for internal backend functionality, operating-system command injection, source-address trust and authentication bypass, and LDAP injection.
The cohort remains Coverage With Adaptation because reliable attribution depends on Arista-specific asset and version inventory, affected CloudVision component, OIDC or SSO configuration, authentication and privilege context, CV-CUE backend or UI state, source-network or reverse-proxy conditions where applicable, API and management-interface telemetry, identity-provider and session evidence, filesystem and repository activity, Sensor data access, database and directory-service telemetry, process and command activity, administrator and configuration state, managed-network and wireless-control effects, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
Arista states that it is not aware of malicious exploitation of these vulnerabilities in customer deployments. The cohort adds 17 Coverage With Adaptation CVEs and 0 CISA KEV entries to this report.
HPE Integrated Lights-Out 7 CVE-2026-79820 is a Coverage With Adaptation entry.
The vulnerability maps a remote user-validation failure affecting the HPE iLO 7 management control plane to potential unauthorized management-plane access under the documented affected conditions.
CVE-2026-79820 remains Coverage With Adaptation because reliable attribution depends on HPE iLO 7-specific asset and firmware inventory, management-interface reachability, authentication and session context, administrator activity, configuration and firmware state, managed-server activity, network behavior, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
CVE-2026-79820 adds 0 CISA KEV entries to this report. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status.
HPE Networking ClearPass Policy Manager HPESBNW05158 documents 28 vulnerabilities that are Coverage With Adaptation entries.
The ClearPass cohort includes remote code execution, authentication and access-control failure, SQL injection, command execution, privilege escalation, file and path manipulation, client and agent integrity weaknesses, information disclosure, web-interface compromise, and availability-impacting behavior under vulnerability-specific prerequisites.
Affected applicability includes ClearPass Policy Manager 6.14.0 and earlier and the 6.11 branch through 6.11.15 under the applicable vulnerability-specific conditions.
The cohort remains Coverage With Adaptation because reliable attribution depends on ClearPass-specific asset and version inventory, management-interface and API exposure, authentication and session context, administrator and role state, OnGuard and client-agent activity, request and database telemetry, filesystem evidence, process and command execution, privilege context, configuration state, endpoint effects, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
The HPE ClearPass cohort adds 0 CISA KEV entries to this report. Available authoritative evidence does not establish CISA KEV status for the 28 identifiers.
HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 are Coverage With Adaptation entries.
The nine-CVE cohort includes authenticated denial of service, unauthenticated management-interface authentication bypass, remote and adjacent memory-corruption and buffer-overflow conditions producing code-execution or information-disclosure consequences, authenticated API privilege escalation, and unauthenticated sensitive-information disclosure.
AOS-S 16.11.0031 and earlier are affected. AOS-S 16.11.0032 is the corrected release. Available authoritative evidence does not establish CISA KEV status for the nine identifiers.
The cohort remains Coverage With Adaptation because reliable attribution depends on AOS-S-specific switch and version inventory, management-interface reachability, authentication and session context, API activity, source-network and adjacent-network conditions where applicable, device and process behavior, crash or memory-corruption evidence where observable, administrator and privilege state, configuration changes, network behavior, remediation state, and downstream switching or network-control effects beyond the UniFi OS / UniFi Connect anchor model.
The HPE AOS-Switch cohort adds 0 CISA KEV entries to this report.
HPE Networking Analytics and Location Engine CVE-2026-76708 through CVE-2026-76717 are Coverage With Adaptation entries.
The ten-CVE cohort spans the following vendor-described behavior families: default hard-coded administrative and operating-system credentials; unauthenticated arbitrary file write; unauthenticated sensitive-information disclosure; unauthenticated socket data injection; unauthorized access; denial of service; authenticated maintenance-restore filesystem access with root privileges; authenticated web-interface command execution as root; root code execution under the documented man-in-the-middle condition; and API disclosure of user information and password hashes.
ALE 5.0.0.0 and earlier are affected. ALE 5.1.0.0 is the corrected release. HPE reported no known public discussion or exploit code targeting the package at publication.
The cohort remains Coverage With Adaptation because reliable attribution depends on ALE-specific asset and version inventory, account and credential state, management-interface and API exposure, authentication and session context, maintenance-restore activity, filesystem and file-write evidence, socket and service telemetry, process and root-context evidence, network-path and man-in-the-middle conditions where applicable, sensitive-data access, configuration state, and downstream effects beyond the UniFi OS / UniFi Connect anchor model.
The HPE ALE cohort adds 0 CISA KEV entries to this report. Available authoritative evidence does not establish CISA KEV status for CVE-2026-76708 through CVE-2026-76717.
Zammad CVE-2026-102489 and CVE-2026-102490 are Coverage With Adaptation entries.
CVE-2026-102489 maps unauthenticated network-reachable exploitation to remote code execution in the Zammad application-user context and potential session leakage under affected version and runtime conditions. DIVD identifies Zammad 6.3.0 through 6.5.4 as affected and states that the vulnerability is also present in Zammad 7.0.0 through 7.1.3 but not practically exploitable there because of environmental conditions. Zammad states that practical exploitation applies to Zammad 6.5 and older, that Zammad 7.0 and later are not affected in practice, and that the affected code was additionally hardened in Zammad 7.2.0.
CVE-2026-102490 maps local low-privilege access in the zammad user context to root privilege escalation under DIVD's published analysis. DIVD identifies Zammad 1.5.0 through versions before 7.1.0-alpha as affected. Zammad states that it had not received sufficient technical information to independently verify the vulnerability, its scope, or its affected-version range as of October 1, 2026.
DIVD states that its September 21, 2026 breach occurred through the two Zammad zero-day vulnerabilities. The two identifiers can form a progression from remote application-context execution to consequential root-level host control where both conditions apply, but they should not be represented as a universally required exploit chain because their prerequisites, practical exploitability, and vendor-confirmed scope differ.
The identifiers remain Coverage With Adaptation because reliable attribution depends on Zammad-specific asset and version inventory, application exposure, authentication and session state, application-user and service activity, process and child-process execution, filesystem and configuration state, privilege-transition and root-context evidence where available, network behavior, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
CISA added CVE-2026-102489 and CVE-2026-102490 to the Known Exploited Vulnerabilities Catalog on October 2, 2026, with remediation due dates of October 5, 2026. The KEV designations confirm known exploitation and materially increase remediation and retrospective-hunting urgency without changing either identifier's Coverage With Adaptation classification or establishing compromise of any other Zammad deployment.
Kiteworks Core CVE-2026-102132 is a Coverage With Adaptation entry.
The vulnerability maps improper access control in the Kiteworks Core administrative import function to authenticated delegated-administrator privilege escalation. Under the documented prerequisite, a delegated administrator holding the required administrative permission can create a privileged integration credential beyond the intended authorization scope and obtain full system-administrator privileges.
Kiteworks Core versions before 9.5.1 are affected; version 9.5.1 is the documented corrected boundary.
The vulnerability remains Coverage With Adaptation because reliable attribution depends on Kiteworks-specific asset and version inventory, delegated-administrator identity and assigned-permission state, administrative import activity, privileged integration-credential creation and use, administrator-role and privilege changes, configuration and audit records, managed-content or connector activity where consequential access is suspected, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for CVE-2026-102132.
VeloCloud Orchestrator On-Prem CVE-2026-93952 is a Coverage With Adaptation entry.
Arista documents a VCO On-Prem improper-input-validation issue that may allow a remote attacker to access privileged internal functionality and impact the VCO host. Successful exploitation may compromise the confidentiality, integrity, and availability of the orchestrator and data managed by the orchestrator.
The documented exposure requires certificate-based authentication from VeloCloud Edge to VCO, access to the public portion of the VeloCloud Edge authentication certificate, and network access to the VCO web interface; VCO tenant or operator credentials are not required.
Arista states that the issue was discovered externally and is known to be actively exploited. Active exploitation materially increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification or establish compromise of a specific local deployment.
CISA added CVE-2026-93952 to the Known Exploited Vulnerabilities Catalog on September 22, 2026, with a remediation due date of September 25, 2026.
Check Point Security Management CVE-2026-93616 is a Coverage With Adaptation entry.
Check Point documents a pre-authentication path traversal vulnerability in the Security Management web service that can allow an attacker to execute a script from an arbitrary path and load an arbitrary Java class. The vulnerability is Critical with a CVSS score of 9.8.
Affected Security Management releases include R82.20; R82.10 with Jumbo Hotfix Take 44 or lower; R82 with Jumbo Hotfix Take 126 or lower; R81.20 with Jumbo Hotfix Take 166 or lower; R81.10 with Jumbo Hotfix Take 190 or lower; and the documented R80, R80.10, R80.20, R80.30, R80.40, and R81 end-of-support releases. Check Point states that LivePatch Take 28/29 does not address the issue and provides sk1000171 as the remediation and response reference.
Check Point Research reports a handful of pinpointed attacks involving CVE-2026-93616 observed on July 23, 2026. Confirmed exploitation materially increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification or establish compromise of a specific local deployment.
CISA added CVE-2026-93616 to the Known Exploited Vulnerabilities Catalog on September 22, 2026, with a remediation due date of September 25, 2026.
SUSE Rancher CVE-2026-88804 and CVE-2026-88805 are Coverage With Adaptation entries.
CVE-2026-88804 maps unauthenticated modification of Rancher public UI settings to login-page browser-context script execution and potential administrator bootstrap-password or active-session exposure. CVE-2026-88805 maps a failure to invalidate corresponding public API session tokens after browser logout, allowing a previously obtained token to remain valid until expiration.
The two identifiers remain Coverage With Adaptation because reliable attribution requires Rancher-specific asset and version inventory, public and authenticated API exposure, public UI settings, browser and session-token state, logout and revocation events, identity-provider and OIDC configuration, administrator and RBAC activity, cluster-management state, downstream managed-cluster activity, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for either identifier.
CVE-2026-87688, CVE-2026-87687, CVE-2026-87686, CVE-2026-87685, CVE-2026-87684, CVE-2026-87683, CVE-2026-87682, CVE-2026-87681, CVE-2026-87680, CVE-2026-87679, CVE-2026-87678, CVE-2026-87677, CVE-2026-87675, CVE-2026-87674, CVE-2026-87673, CVE-2026-87672, CVE-2026-87670, CVE-2026-87669, CVE-2026-87667, CVE-2026-87666, CVE-2026-87664, CVE-2026-87663, CVE-2026-87662, CVE-2026-87660, and CVE-2026-87659 — Brocade Fabric OS management-control-plane vulnerabilities — Covered with adaptation where the applicable CVE-specific condition produces REST API or WebTools abuse, authentication or authorization failure, RBAC bypass, AAA or federated-authentication abuse, administrative-session manipulation, configuration or firmware-management abuse, arbitrary file activity, privileged command execution, privilege escalation, Virtual Fabric or fabric-management authorization failure, inter-switch administrative trust abuse, or consequential fabric-control effects. Reliable implementation depends on Brocade Fabric OS asset and version inventory, enabled management functions, authentication and privilege context, REST API, WebTools, CLI, AAA, RADIUS, LDAP, TACACS+, SSO, RBAC, configuration, firmware, certificate, SNMP, zoning, Virtual Fabric, inter-switch, process, command, remediation, and incident-response evidence appropriate to the applicable CVE. Available authoritative evidence reviewed for this amendment does not establish CISA KEV status for these identifiers.
FreePBX CVE-2026-75600, CVE-2026-54710, and CVE-2026-54675 are Coverage With Adaptation entries.
The three identifiers represent distinct authenticated PBX management-plane execution paths: GraphQL API generatedocs host-command injection, Superfecta unsafe PHP file inclusion, and Soundlang arbitrary file write with follow-on PHP execution.
The cohort remains Coverage With Adaptation because reliable attribution depends on FreePBX-specific asset, module, and version inventory, authenticated identity and authorization context, relevant administrative or API activity, file and PHP evidence, Asterisk and web-server process telemetry, command execution, telephony configuration, network behavior, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for these three identifiers.
SailPoint IdentityIQ CVE-2026-12342 is a Coverage With Adaptation entry.
The vulnerability maps unauthenticated web-service API improper input validation to remote code execution on the IdentityIQ server.
The identifier remains Coverage With Adaptation because reliable attribution depends on IdentityIQ-specific asset and version inventory, web-service API exposure, request context where available, application and service process activity, identity-governance workflow state, role and entitlement changes, connector and configuration evidence, filesystem and network behavior, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status.
kcp CVE-2026-61682 is a Coverage With Adaptation entry.
The kcp front proxy fails to remove caller-supplied X-Remote-* identity headers before forwarding authenticated requests to shards, allowing an authenticated tenant to inject group and extra identity values, assert system, forge delegated identity or scope data, escape workspace boundaries, and read, write, or delete secrets, RBAC objects, APIExports, APIBindings, LogicalClusters, and other resources across workspaces.
Affected versions are earlier than 0.31.4 and 0.32.0 through 0.32.1; 0.31.4 and 0.32.2 are fixed. An external proxy that strips all inbound X-Remote-* identity headers is an interim mitigation rather than the complete remediation.
The vulnerability remains Coverage With Adaptation because reliable attribution depends on kcp-specific front-proxy, shard, workspace, request-header authentication, credential, RBAC, delegated-identity, scope, secret, policy, configuration, and downstream telemetry beyond the UniFi OS / UniFi Connect anchor model.
Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status.
The 37 IBM Guardium Data Protection identifiers are Coverage With Adaptation entries.
The cohort includes distinct command injection, OS command injection, SQL injection, recoverable credential, path traversal, arbitrary file-write and file-delete, local privilege-escalation, SUID-root wrapper, authentication-bypass, improper-authorization, REST authorization, CSRF, cross-site scripting or web-input execution, certificate-validation, patch-signature-validation, and management-interface access-control weaknesses.
Guardium Data Protection 12.2 is affected. IBM directs customers to the 12.0p233 update.
The cohort remains Coverage With Adaptation because reliable attribution requires the CVE-specific Guardium appliance role, prerequisite, affected function, authentication or authorization context, process, SUID, file, credential, database, REST, PESI, GIM, SNMP, web, certificate, configuration, and downstream telemetry appropriate to that CVE beyond the UniFi OS / UniFi Connect anchor model.
Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for this cohort.
Check Point Security Management and Log Server CVE-2026-91843 is a Coverage With Adaptation entry.
Check Point states that the vulnerability affects Security Management and Log Servers and may allow an unauthenticated remote attacker to execute arbitrary code with root privileges through the login process.
Check Point identifies the issue as Critical with a CVSS score of 9.8 and states that there is currently no indication of exploitation in the wild.
The documented remediation is the LivePatch fix described in sk1000155; customers with automatic updates enabled are already protected. Check Point states that Smart-1 Cloud is not affected because the fix has already been implemented there.
The vulnerability remains Coverage With Adaptation because reliable attribution requires Check Point-specific management or Log Server inventory, deployment context, login and authentication evidence, FWM process telemetry where available, root-context execution evidence, administrator and configuration activity, managed-gateway or policy effects, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor telemetry.
Available authoritative evidence does not establish CISA KEV status as of September 17, 2026.
Logsign SIEM CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926 are Coverage With Adaptation entries.
TR-CERT identifies all three vulnerabilities as affecting Logsign SIEM 6.4.101 through versions before 6.4.117. CVE-2026-90924 is a default-credential weakness that may permit unauthenticated administrative access; CVE-2026-90925 is a low-privilege authenticated path-traversal vulnerability; and CVE-2026-90926 is a low-privilege authenticated code-injection vulnerability reachable over the network. The CNA-assigned CVSS v3.1 scores are 9.8, 7.1, and 8.8 respectively.
The cohort remains Coverage With Adaptation because reliable attribution requires Logsign-specific asset and version inventory, management and application-path reachability, authentication and privilege context, request and path telemetry where available, process and child-process activity, filesystem and configuration evidence, credential and secret state, administrator activity, connector and ingestion configuration, alerting and logging state, security-record integrity, network behavior, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
Logsign SIEM 6.4.117 or later is the documented correction boundary. The three identifiers add 0 CISA KEV entries to this report. The validated CISA ADP exploitation state is none for CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926.
UTMStack CVE-2026-82039 through CVE-2026-82045 are Coverage With Adaptation entries.
The seven identifiers represent distinct UTMStack security-monitoring and management-control-plane weaknesses and should not be represented as one mandatory exploit chain.
CVE-2026-82039 maps authenticated manipulation of UTMStack asset-group search functionality to SQL injection against the underlying database, with potential unauthorized access to or modification of database information.
CVE-2026-82040 maps authenticated manipulation of identity-provider metadata input to server-side request forgery capable of reaching internal network resources or cloud instance-metadata services.
CVE-2026-82041 maps insufficient authorization on the STOMP command WebSocket to authenticated delivery of attacker-controlled operating-system commands through the UTMStack control plane to connected agents.
CVE-2026-82042 maps possession or misuse of a valid UTMStack internal key to access to privileged API functionality without completing the normal user-account or JWT-authentication path.
CVE-2026-82043 maps unauthenticated password-reset response differences to enumeration of valid UTMStack accounts. Account enumeration alone does not establish account compromise.
CVE-2026-82044 maps authenticated manipulation of the UTMStack PDF-reporting service to server-side request forgery capable of retrieving information from internal resources, OpenSearch services, or cloud instance-metadata services.
CVE-2026-82045 maps authenticated manipulation of network-scan property-value search input to JPQL injection and consequential unauthorized access to sensitive entity information, including credential-related records.
UTMStack versions before 11.2.16 are affected under the applicable vulnerability-specific prerequisites. UTMStack 11.2.16 provides the documented corrected-version boundary.
The seven identifiers remain Coverage With Adaptation because reliable attribution requires UTMStack-specific asset and version inventory, authentication and role context where applicable, administrative-interface and API exposure, internal-key state, identity-provider configuration, STOMP command-WebSocket activity, connected-agent identity and command telemetry, database-query activity, credential and sensitive-record access, password-reset activity, PDF-reporting requests, internal-service or cloud-metadata network access, managed-endpoint process and command telemetry, configuration and security-rule changes, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for CVE-2026-82039 through CVE-2026-82045.
Zyxel GS1900 CVE-2026-7273 is a Coverage With Adaptation entry.
Zyxel documents a stack-based buffer overflow in the GS1900 CGI management component that can allow a LAN-based unauthenticated attacker to send a crafted HTTP request and potentially execute operating-system commands on an affected switch.
CISA has added CVE-2026-7273 to the Known Exploited Vulnerabilities Catalog based on evidence of active exploitation.
The KEV designation materially increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification or the Directly Covered KEV / Exploited Anchor-Product Entry count because Zyxel GS1900 remains an adapted-coverage platform rather than a UniFi OS / UniFi Connect anchor product.
The vulnerability remains Coverage With Adaptation because reliable attribution depends on Zyxel-specific model and firmware inventory, LAN and management-interface reachability, HTTP and CGI request telemetry where available, device or process behavior, command-execution evidence, administrator and configuration state, network activity, switching behavior, downstream network-control effects, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
WSO2 CVE-2026-5430 is a Coverage With Adaptation entry.
WSO2 documents a Critical JWT authentication-bypass vulnerability affecting API Manager, API Control Plane, Traffic Manager, and Universal Gateway, with potential unauthorized administrative access, administrative-account compromise, and full account takeover.
Public reporting confirms malicious exploitation activity.
CISA added CVE-2026-5430 to the Known Exploited Vulnerabilities Catalog on September 24, 2026, based on evidence of active exploitation.
Active exploitation and the CISA KEV designation materially increase remediation and retrospective-hunting urgency but do not change the Coverage With Adaptation classification, coverage-register count, or Directly Covered KEV / Exploited Anchor-Product Entry count because WSO2 remains an adapted-coverage platform rather than a UniFi OS / UniFi Connect anchor product.
Issabel Framework CVE-2026-89026 is a Coverage With Adaptation entry.
The vulnerability permits an unauthenticated remote attacker to forge a valid HS256 bearer token using a hard-coded JWT signing key and invoke the pbxapi manager originate endpoint with the System application parameter, resulting in arbitrary operating-system command execution as the Asterisk user.
Public exploitation evidence was first observed by the Shadowserver Foundation on September 9, 2026.
Active exploitation materially increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification or establish compromise of a specific local deployment.
Available authoritative evidence does not establish CISA KEV status as of September 17, 2026.
Fortinet FortiMail CVE-2026-104286 is a Coverage With Adaptation entry.
The vulnerability maps unauthenticated crafted HTTP or HTTPS request activity and path traversal to arbitrary file write on the underlying FortiMail system.
The identifier remains Coverage With Adaptation because reliable attribution depends on FortiMail-specific asset and version inventory, HTTP and HTTPS interface exposure, request and path activity, filesystem and file-write evidence, configuration state, administrator activity, process and service behavior where available, network communication, email-security policy and mail-system state, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
CISA added CVE-2026-104286 to the Known Exploited Vulnerabilities Catalog on October 1, 2026, based on evidence of active exploitation.
The KEV designation materially increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification or establish compromise of a specific local appliance.
Cisco Secure Email Gateway CVE-2026-76461 is a Coverage With Adaptation entry.
CISA added the vulnerability to the Known Exploited Vulnerabilities Catalog on September 14, 2026, based on evidence of active exploitation.
The KEV designation materially increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification or establish compromise of a specific local appliance.
Cisco Secure Email Gateway and Cisco Secure Email and Web Manager CVE-2026-76440, CVE-2026-76441, CVE-2026-20353, CVE-2026-76443, and CVE-2026-76442 are Coverage With Adaptation entries.
Cisco groups each identifier by its highest-level CWE class.
Available authoritative evidence does not establish any of these five identifiers as CISA KEV-listed or confirmed in-the-wild exploitation. Cisco's separate exploitation notice for CVE-2026-76461 must not be generalized to these five hardening CVEs.
Cisco's September 16, 2026 publication set adds 62 Coverage With Adaptation CVEs to this report: 42 Cisco Identity Services Engine / ISE-PIC CVEs, 12 Cisco Secure Firewall Management Center CVEs, six Cisco Nexus Dashboard CVEs, one Cisco BroadWorks CommPilot CVE, and one Cisco ThousandEyes Virtual Appliance CVE.
These additions remain adapted coverage because reliable detection requires product-specific asset, interface, authentication, authorization, service, process, database, filesystem, configuration, peer, and downstream-control telemetry beyond the UniFi OS / UniFi Connect anchor model.
Cisco ISE / ISE-PIC CVE-2026-76460 is a Coverage With Adaptation entry.
Cisco states that it has observed attempted exploitation of this vulnerability in the wild.
The vulnerability permits an unauthenticated remote attacker to bypass authentication to the web-based management interface through a crafted API request.
CISA added CVE-2026-76460 to the Known Exploited Vulnerabilities Catalog on September 16, 2026, based on evidence of active exploitation.
The vendor exploitation evidence and KEV designation materially increase remediation and retrospective-hunting urgency but do not change the Coverage With Adaptation classification or establish compromise of a specific local deployment.
CISA Malcolm CVE-2026-90443 through CVE-2026-90457 are Coverage With Adaptation entries.
Available authoritative evidence does not establish known public exploitation or CISA KEV status for these fifteen identifiers.
Vulnerable-version state or advisory publication should increase remediation urgency but should not be treated as proof of compromise.
The detection model provides direct behavioral coverage for the UniFi OS and UniFi Connect anchor behavior when telemetry exposes management-plane access, authentication-validation or traversal-like request behavior, improper access-control reachability, update or package activity, application-host command injection, service-context execution, sudo or root-context behavior, administrator-state changes, configuration changes, outbound communication, internal scanning, or downstream network-control activity.
Detection should remain behavior-led and should not depend on proof-of-concept names, static exploit strings, user-agent values, source IPs, scanner labels, or actor attribution.
Direct Behavioral Coverage — UniFi OS and UniFi Connect Anchor CVEs, Listed Newest to Oldest by CVE Identifier
· CVE-2026-77550 — Ubiquiti UniFi OS improper neutralization of CRLF sequences allowing authentication-bypass behavior under the documented affected conditions.
· CVE-2026-77549 — Ubiquiti UniFi OS improper neutralization of CRLF sequences allowing authentication-bypass behavior under specific conditions.
· CVE-2026-77545 — Ubiquiti UniFi OS active-debug-code behavior allowing privilege escalation within affected UniFi OS devices or instances.
· CVE-2026-77540 — Ubiquiti UniFi OS Server improper input validation and command-injection behavior requiring high privileges.
· CVE-2026-77539 — Ubiquiti UniFi OS Server improper input validation and command-injection behavior requiring high privileges.
· CVE-2026-77538 — Ubiquiti UniFi Connect Application improper access-control and privilege-escalation behavior.
· CVE-2026-77536 — Ubiquiti UniFi OS improper access-control and privilege-escalation behavior.
· CVE-2026-77534 — Ubiquiti UniFi OS improper access-control and privilege-escalation behavior.
· CVE-2026-50746 — Ubiquiti UniFi Connect Application improper access control leading to command injection on the host device.
· CVE-2026-34910 — Ubiquiti UniFi OS improper input validation and command-injection behavior.
· CVE-2026-34909 — Ubiquiti UniFi OS path-traversal behavior.
· CVE-2026-34908 — Ubiquiti UniFi OS improper access-control and authentication-bypass behavior.
Coverage With Adaptation
· CVE-2026-76285 — Splunk Enterprise SVD-2026-1002 security-hardening vulnerability — Covered with adaptation where locally validated activity involving the affected Splunk component demonstrates the applicable vendor-documented hardening failure. Reliable implementation depends on the CVE-specific affected function, Enterprise version, authentication and authorization state, relevant activity and telemetry, remediation status, and incident-response findings.
· CVE-2026-76284 — Splunk Enterprise SVD-2026-1002 security-hardening vulnerability — Covered with adaptation where locally validated activity involving the affected Splunk component demonstrates the applicable vendor-documented hardening failure. Reliable implementation depends on the CVE-specific affected function, Enterprise version, authentication and authorization state, relevant activity and telemetry, remediation status, and incident-response findings.
· CVE-2026-76283 — Splunk Enterprise SVD-2026-1002 security-hardening vulnerability — Covered with adaptation where locally validated activity involving the affected Splunk component demonstrates the applicable vendor-documented hardening failure. Reliable implementation depends on the CVE-specific affected function, Enterprise version, authentication and authorization state, relevant activity and telemetry, remediation status, and incident-response findings.
· CVE-2026-76282 — Splunk Enterprise SVD-2026-1002 security-hardening vulnerability — Covered with adaptation where locally validated activity involving the affected Splunk component demonstrates the applicable vendor-documented hardening failure. Reliable implementation depends on the CVE-specific affected function, Enterprise version, authentication and authorization state, relevant activity and telemetry, remediation status, and incident-response findings.
· CVE-2026-76281 — Splunk Enterprise SVD-2026-1002 security-hardening vulnerability — Covered with adaptation where locally validated activity involving the affected Splunk component demonstrates the applicable vendor-documented hardening failure. Reliable implementation depends on the CVE-specific affected function, Enterprise version, authentication and authorization state, relevant activity and telemetry, remediation status, and incident-response findings.
· CVE-2026-76280 — Splunk Enterprise SVD-2026-1001 vulnerability requiring additional vendor remediation — Covered with adaptation where applicable Splunk Enterprise activity demonstrates the CVE-specific affected-function behavior. Reliable implementation depends on affected product and version state, applicable permissions and service configuration, supporting telemetry, completion of the vendor's additional remediation requirements, and incident-response findings.
· CVE-2026-76279 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76278 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76277 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76276 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76275 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76274 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76273 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76272 — Splunk Enterprise SVD-2026-1001 vulnerability requiring additional vendor remediation — Covered with adaptation where applicable Splunk Enterprise activity demonstrates the CVE-specific affected-function behavior. Reliable implementation depends on affected product and version state, applicable permissions and service configuration, supporting telemetry, completion of the vendor's additional remediation requirements, and incident-response findings.
· CVE-2026-76271 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76270 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76269 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76268 — Splunk Enterprise Patroni REST API missing authentication permitting unauthenticated operating-system command execution under affected conditions — Covered with adaptation where exposed Patroni REST API activity results in unauthorized request handling, unexpected operating-system command execution, abnormal service or child-process activity, filesystem or configuration modification, or consequential Splunk host compromise. Reliable implementation depends on Splunk Enterprise and Patroni applicability, affected versions, REST API reachability, source-network context, request telemetry, service and process activity, command-execution evidence, host configuration, remediation status, and incident-response findings.
· CVE-2026-76267 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76266 — Splunk Enterprise SVD-2026-1001 vulnerability — Covered with adaptation where activity affecting the documented Splunk component produces the applicable authorization, execution, information-disclosure, service, or security-control consequence. Reliable implementation depends on the CVE-specific affected function, Enterprise version, configuration and permission prerequisites, relevant telemetry, remediation status, and incident-response findings.
· CVE-2026-76265 — Splunk Enterprise SVD-2026-1001 vulnerability requiring additional vendor remediation — Covered with adaptation where applicable Splunk Enterprise activity demonstrates the CVE-specific affected-function behavior. Reliable implementation depends on affected product and version state, applicable permissions and service configuration, supporting telemetry, completion of the vendor's additional remediation requirements, and incident-response findings.
· CVE-2026-76264 — Splunk Enterprise SVD-2026-1001 vulnerability requiring additional vendor remediation — Covered with adaptation where applicable Splunk Enterprise activity demonstrates the CVE-specific affected-function behavior. Reliable implementation depends on affected product and version state, applicable permissions and service configuration, supporting telemetry, completion of the vendor's additional remediation requirements, and incident-response findings.
· CVE-2026-104286 — Fortinet FortiMail path traversal permitting unauthenticated arbitrary file write — Covered with adaptation where unauthenticated crafted HTTP or HTTPS request activity against an affected FortiMail deployment produces traversal-like path behavior, arbitrary file write on the underlying system, unexpected filesystem modification, configuration or email-security policy changes, abnormal process or service activity where observable, unexpected outbound communication, persistence, or consequential mail-system effects. Reliable implementation depends on FortiMail asset and version inventory, HTTP and HTTPS interface exposure, request and path activity, filesystem and file-write evidence, configuration state, administrator activity, process and service behavior where available, network communication, email-security policy and mail-system state, remediation status, and incident-response findings. CISA added CVE-2026-104286 to the Known Exploited Vulnerabilities Catalog on October 1, 2026, based on evidence of active exploitation. The Coverage With Adaptation classification is unchanged.
· CVE-2026-103057 — AiSOC missing authentication on realtime internal endpoints — Covered with adaptation where AiSOC realtime internal endpoint activity permits unauthenticated event submission, spoofed tenant identifiers, unauthorized WebSocket or SSE content distribution, or unauthorized notification activity. Reliable implementation depends on AiSOC version inventory, internal-endpoint exposure, source-network context, realtime-service request telemetry, tenant identifiers, event and notification records, WebSocket and SSE activity, configuration state, remediation status, and incident-response findings.
· CVE-2026-103056 — AiSOC authenticated command injection through CrowdStrike Real Time Response action parameters — Covered with adaptation where authenticated AiSOC actions-service activity results in CrowdStrike Real Time Response command injection, unexpected command construction, managed-endpoint command execution, SYSTEM or root-context activity, or consequential endpoint modification. Reliable implementation depends on AiSOC version inventory, authenticated-user and action context, CrowdStrike integration configuration, action parameters, RTR activity, managed-endpoint process and command telemetry, privilege context, downstream endpoint state, remediation status, and incident-response findings.
· CVE-2026-103055 — AiSOC hard-coded JWT verification secret in the realtime service — Covered with adaptation where AiSOC realtime authentication permits forged JWT-backed subscription tickets, arbitrary tenant identifiers, or unauthorized cross-tenant access to live alerts, cases, agent events, or graph updates. Reliable implementation depends on AiSOC version and configuration state, realtime-service exposure, JWT-secret configuration, subscription-ticket and tenant context, WebSocket and SSE activity, accessed security data, remediation status, and incident-response findings.
· CVE-2026-103054 — AiSOC authenticated MSSP portfolio tenant authorization failure — Covered with adaptation where authenticated AiSOC MSSP activity permits unauthorized addition of tenant UUIDs to a user-controlled portfolio or consequential access to another tenant's alerts, incidents, or posture information. Reliable implementation depends on AiSOC version inventory, authenticated identity and role context, MSSP portfolio ownership and membership state, tenant-addition events, tenant identifiers, security-data access records, remediation status, and incident-response findings.
· CVE-2026-103053 — AiSOC response-action API authentication failure — Covered with adaptation where AiSOC response-action API activity occurs without the expected authentication controls and results in unauthorized integration enumeration, action submission or approval, arbitrary-principal activity, or dispatch of containment actions using configured vendor credentials. Reliable implementation depends on AiSOC version and deployment configuration, development-mode and actions-service-token state, response-action API reachability, authentication context, integration inventory, action-submission and approval records, vendor-credential use, downstream containment activity, remediation status, and incident-response findings.
· CVE-2026-102490 — Zammad local privilege escalation from the zammad user to root — Covered with adaptation where local activity in the Zammad application-user context progresses to unauthorized root privileges, root-context process or command execution, privileged filesystem or configuration changes, persistence, unexpected service activity, or consequential host-level effects under DIVD's published findings. Reliable implementation depends on Zammad asset and version inventory, local zammad user and service context, process and child-process activity, privilege-transition evidence, sudo or equivalent privilege-use records where available, root-context execution, filesystem and configuration state, network behavior, remediation status, and incident-response findings. DIVD identifies Zammad 1.5.0 through versions before 7.1.0-alpha as affected. Zammad states that it had not received sufficient technical detail to independently verify CVE-2026-102490, its mechanism, scope, or affected-version range as of October 1, 2026. CISA added CVE-2026-102490 to the Known Exploited Vulnerabilities Catalog on October 2, 2026, with an October 5, 2026 remediation due date. The KEV designation increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification.
· CVE-2026-102489 — Zammad remote code execution in the application-user context with potential session leakage — Covered with adaptation where unauthenticated network activity against an affected Zammad deployment results in execution in the Zammad application-user context, abnormal application or service processes, potential session leakage, unexpected filesystem or configuration changes, outbound communication, persistence, or consequential application-host activity. Reliable implementation depends on Zammad asset and version inventory, application exposure, request and authentication context where available, session activity, application-user and service-process telemetry, child-process and command execution, filesystem and configuration state, network behavior, remediation status, and incident-response findings. DIVD identifies Zammad 6.3.0 through 6.5.4 as affected and identifies the vulnerability as present but not practically exploitable in Zammad 7.0.0 through 7.1.3 because of environmental conditions. Zammad states that practical exploitation applies to Zammad 6.5 and older, that Zammad 7.0 and later are not affected in practice, and that the affected code was additionally hardened in Zammad 7.2.0. DIVD states that the vulnerability was involved in its September 21, 2026 breach. CISA added CVE-2026-102489 to the Known Exploited Vulnerabilities Catalog on October 2, 2026, with an October 5, 2026 remediation due date. The KEV designation increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification.
· CVE-2026-102161 — Arista CloudVision-CUE on-premises source-address trust and authentication bypass — Covered with adaptation where an unauthenticated attacker with adjacent-network access, or an attacker routed through a reverse proxy or load balancer that forwards client headers, forges source-address information and obtains administrative session privileges on the CV-CUE backend. Reliable implementation depends on CV-CUE asset and version inventory, backend enablement, source-network context, reverse-proxy and forwarded-header handling, authentication and session telemetry, administrator activity, configuration changes, remediation status, and incident-response findings.
· CVE-2026-102160 — Arista CloudVision-CUE on-premises authenticated operating-system command injection through backup management — Covered with adaptation where an authenticated Super User submits a crafted backup-management request that results in arbitrary command execution with the privileges of the affected CV-CUE service. Reliable implementation depends on CV-CUE version inventory, authenticated administrator context, backup-management activity, request parameters, db_ops_ui.log or equivalent telemetry, process and command execution, privilege context, configuration state, remediation status, and incident-response findings.
· CVE-2026-102159 — Arista CloudVision-CUE on-premises missing authentication for internal backend functionality — Covered with adaptation where unauthenticated network activity reaches functionality intended only for internal CV-CUE backend services and results in sensitive-location-data exposure, unauthorized backend access, service disruption, or consequential administrative effects. Reliable implementation depends on CV-CUE backend enablement, asset and version inventory, request and source-network context, backend-service telemetry, sensitive-data access, service availability, administrator activity, remediation status, and incident-response findings.
· CVE-2026-102158 — Arista CloudVision-CUE on-premises authenticated SQL injection — Covered with adaptation where an authenticated network user supplies crafted API request parameters that reach backend database processing and produce SQL-injection behavior or service-availability impact. Reliable implementation depends on CV-CUE version inventory, authenticated identity, API request telemetry, backend database activity, slow or abnormal API requests, HTTP response behavior, service availability, remediation status, and incident-response findings.
· CVE-2026-102157 — Arista CloudVision-CUE on-premises insecure direct object reference — Covered with adaptation where an authenticated network user abuses the affected file-serving interface under the documented attack conditions to access another user's transient data. Reliable implementation depends on CV-CUE asset and version inventory, authenticated-user context, file-serving requests, object and user identifiers, transient-data access, authorization state, remediation status, and incident-response findings.
· CVE-2026-102156 — Arista CloudVision-CUE on-premises LDAP injection — Covered with adaptation where an unauthenticated network attacker under the documented high-complexity conditions manipulates LDAP authentication input and injects queries against the configured directory service. Reliable implementation depends on CV-CUE version inventory, LDAP authentication configuration, network reachability, submitted authentication input, LDAP query and bind telemetry where available, directory-service behavior, remediation status, and incident-response findings.
· CVE-2026-102155 — Arista CloudVision-CUE on-premises XML external entity injection — Covered with adaptation where an authenticated user submits malicious XML to the WiFi-server Spectralight application and obtains arbitrary local-file disclosure or produces partial denial of service. Reliable implementation depends on CV-CUE version inventory, authenticated-user context, Spectralight request activity, XML-processing evidence, filesystem access, service availability, remediation status, and incident-response findings.
· These six 0190 vulnerabilities require the CV-CUE backend to be enabled, while CVE-2026-102156 has its separate LDAP-authentication condition; Arista reports no known malicious exploitation.
· CVE-2026-102132 — Kiteworks Core improper access control in the administrative import function enabling delegated-administrator privilege escalation — Covered with adaptation where an authenticated delegated administrator holding the documented administrative permission uses the affected import function to create a privileged integration credential beyond the intended authorization scope and obtain full system-administrator privileges. Reliable implementation depends on Kiteworks Core asset and version inventory, delegated-administrator identity and assigned-permission state, administrative import activity, privileged integration-credential creation and use, administrator-role and privilege changes, configuration and audit records, managed-content or connector activity where consequential access is suspected, remediation status, and incident-response findings. Kiteworks Core versions before 9.5.1 are affected; version 9.5.1 is the documented corrected boundary. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status.
· CVE-2026-101158 — Arista CloudVision stored cross-site scripting through the Fileserver upload path — Covered with adaptation where an authenticated user with the required file-upload privileges stores malicious content that executes in another CloudVision user's browser and results in session compromise, sensitive-data access, administrative activity, configuration changes, or consequential management-plane effects. Reliable implementation depends on affected CloudVision asset and version inventory, authenticated identity and privilege state, Fileserver upload activity, browser-session and administrator evidence, configuration changes, remediation status, and incident-response findings.
· CVE-2026-101157 — Arista CloudVision-CUE on-premises adjacent-network stored cross-site scripting — Covered with adaptation where an unauthenticated attacker with adjacent-network access injects malicious content that executes when an authenticated user views affected content, potentially compromising the victim's browser session, accessing sensitive data, modifying system state, or disrupting services. Reliable implementation depends on CV-CUE UI enablement, asset and version inventory, source-network context, affected-content activity, authenticated-user session evidence, configuration and service state, remediation status, and incident-response findings.
· CVE-2026-101156 — Arista CloudVision-CUE on-premises authenticated stored cross-site scripting — Covered with adaptation where a high-privilege administrator stores malicious content in an affected configuration and the content executes when another authenticated user views or compares that configuration, permitting activity through the victim's authenticated browser session. Reliable implementation depends on CV-CUE UI enablement, asset and version inventory, administrator identity and privilege context, configuration activity, browser-session telemetry, sensitive-data and configuration access, remediation status, and incident-response findings.
· CVE-2026-101155 — Arista CloudVision Portal Software Management Studio Software Repository path traversal — Covered with adaptation where an authenticated remote attacker with the required permissions submits crafted requests or file uploads and reads or writes files outside the intended repository scope. Reliable implementation depends on CloudVision Portal asset and version inventory, authenticated identity and repository permissions, Software Management Studio activity, submitted paths and uploads, filesystem evidence, configuration state, remediation status, and incident-response findings.
· CVE-2026-101154 — Arista CloudVision Portal Network Provisioning Image Repository path traversal — Covered with adaptation where an authenticated remote attacker with the required permissions submits crafted requests or file uploads and reads or writes files outside the intended repository scope. Reliable implementation depends on CloudVision Portal asset and version inventory, authenticated identity and repository permissions, Network Provisioning Image Repository activity, submitted paths and uploads, filesystem evidence, configuration state, remediation status, and incident-response findings.
· CVE-2026-101153 — Arista CloudVision Portal and CloudVision Sensor authenticated path traversal — Covered with adaptation where a sufficiently privileged authenticated user exploits path traversal to extract unintended data from an affected CloudVision Sensor. Reliable implementation depends on CloudVision Portal or Sensor asset and version inventory, authenticated identity and privilege context, request and path telemetry, Sensor data access, filesystem evidence, certificate and remediation state, and incident-response findings.
· CVE-2026-101152 — Arista CloudVision Portal SSO authentication-material redirection — Covered with adaptation where an unauthenticated attacker crafts a URL that, after user interaction in an affected deployment using an external SSO identity provider, causes authentication material to be delivered to an attacker-controlled URL rather than CloudVision. Reliable implementation depends on CloudVision version inventory, SSO and identity-provider configuration, user interaction, authentication redirects, session and token evidence, destination context, remediation status, and incident-response findings.
· CVE-2026-101151 — Arista CloudVision Portal login-flow open redirection — Covered with adaptation where an unauthenticated attacker crafts a URL that, when used by a victim, causes the browser to redirect to an arbitrary external destination after authentication. Reliable implementation depends on CloudVision version inventory, login and redirect activity, user interaction, destination context, authentication and session evidence, remediation status, and incident-response findings.
· CVE-2026-101150 — Arista CloudVision Portal OIDC bearer-token configuration server-side request forgery — Covered with adaptation where a high-privilege user in an affected OIDC deployment with bearer-token login enabled manipulates OIDC bearer-token configuration to direct server requests to arbitrary destinations. Reliable implementation depends on CloudVision version inventory, OIDC provider configuration, Allow Bearer Token Login state, privileged administrator activity, outbound requests, destination context, remediation status, and incident-response findings.
· CVE-2026-101149 — Arista CloudVision Portal OIDC SSO provider-configuration server-side request forgery — Covered with adaptation where a high-privilege user in an affected OIDC SSO deployment manipulates provider configuration and causes CloudVision to direct requests to arbitrary destinations. Reliable implementation depends on CloudVision version inventory, OIDC and OAuth SSO configuration, privileged administrator activity, provider-setting changes, outbound requests, destination context, remediation status, and incident-response findings.
· CVE-2026-94587, CVE-2026-94586, CVE-2026-94585, CVE-2026-94584, CVE-2026-94583, CVE-2026-94581, CVE-2026-94580, CVE-2026-94579, CVE-2026-94578, CVE-2026-94577, CVE-2026-94576, and CVE-2026-94575 — Brocade Fabric OS management-control-plane vulnerabilities — Covered with adaptation where the applicable CVE-specific condition produces unauthorized management access, authentication or authorization bypass, administrative privilege, management-interface command execution, file or configuration manipulation, AAA or federated-authentication abuse, firmware or certificate-management abuse, Virtual Fabric or fabric-control authorization failure, inter-switch administrative abuse, privileged process or command execution, or consequential fabric-control effects. Reliable implementation depends on the affected Fabric OS product and version, enabled feature and management interface, authentication and privilege prerequisite, REST API, WebTools, CLI, AAA, RBAC, configuration, firmware, certificate, SNMP, zoning, Virtual Fabric, fabric relationship, process, command, remediation, and incident-response evidence appropriate to the individual identifier. Available authoritative evidence reviewed for this amendment does not establish CISA KEV status for these identifiers.
· CVE-2026-93952 — VeloCloud Orchestrator On-Prem improper input validation permitting remote access to privileged internal functionality and potential VCO host and managed-data compromise — Covered with adaptation where VeloCloud Orchestrator On-Prem activity consistent with unauthorized access to privileged internal VCO functionality produces abnormal web or backend behavior, host-level process or service activity, unexpected file creation or modification, administrator or configuration changes, outbound communication, persistence, or downstream managed-edge effects. Reliable implementation depends on VCO deployment and version inventory, certificate-based Edge-to-VCO authentication state, access to the public portion of the Edge authentication certificate as an exposure prerequisite, VCO web-interface reachability, nginx and web access logs, backend application logs, system and database logs, filesystem and service state, administrator activity, network telemetry, managed Edge state, remediation status, and incident-response findings. Arista states that the issue is known to be actively exploited. CISA added CVE-2026-93952 to the Known Exploited Vulnerabilities Catalog on September 22, 2026, with a remediation due date of September 25, 2026. The Coverage With Adaptation classification is unchanged.
· CVE-2026-93616 — Check Point Security Management pre-authentication path traversal in the management web service permitting arbitrary-path script execution and Java class loading — Covered with adaptation where unauthenticated activity against an affected Check Point Security Management web service produces traversal-like path access, arbitrary-path script execution, Java class loading, unexpected file or filesystem activity, Management Server process anomalies, administrator or configuration changes, security-policy modification, outbound communication, or downstream managed-gateway effects. Reliable implementation depends on Check Point Security Management asset and version inventory, management-web service exposure, HTTP request and path telemetry where available, file-upload and script-execution evidence, Java class-loading and process telemetry, filesystem state, administrator and security-policy records, managed-gateway and downstream firewall activity, network telemetry, sk1000171 remediation state, and incident-response findings. Check Point identifies CVE-2026-93616 as Critical with CVSS 9.8 and reports a handful of pinpointed attacks observed on July 23, 2026. Affected releases include R82.20; R82.10 with Jumbo Hotfix Take 44 or lower; R82 with Jumbo Hotfix Take 126 or lower; R81.20 with Jumbo Hotfix Take 166 or lower; R81.10 with Jumbo Hotfix Take 190 or lower; and the documented R80, R80.10, R80.20, R80.30, R80.40, and R81 end-of-support releases. Check Point states that LivePatch Take 28/29 does not address the issue and directs customers to sk1000171. CISA added CVE-2026-93616 to the Known Exploited Vulnerabilities Catalog on September 22, 2026, with a remediation due date of September 25, 2026. The Coverage With Adaptation classification is unchanged.
· CVE-2026-91843 — Check Point Security Management and Log Server unauthenticated remote code execution with root privileges through the login process — Covered with adaptation where unauthenticated activity against an affected Check Point Security Management or Log Server reaches the login process and produces arbitrary code execution with root privileges, abnormal FWM or related process behavior, unexpected child-process execution, administrator-session anomalies, configuration or policy changes, outbound communication, or downstream managed-gateway effects. Reliable implementation depends on Check Point Security Management or Log Server asset and version inventory, deployment and management-interface exposure, login and authentication telemetry, FWM process and child-process evidence where available, root-context execution evidence, administrator and configuration records, managed-gateway and policy activity, network telemetry, remediation state, and incident-response findings. Check Point identifies the vulnerability as Critical with a CVSS score of 9.8 and states that there is currently no indication of exploitation in the wild. The documented remediation is the LivePatch fix in sk1000155; customers with automatic updates enabled are already protected. Check Point states that Smart-1 Cloud is not affected because the fix has already been implemented there. Available authoritative evidence does not establish CISA KEV status as of September 17, 2026.
· CVE-2026-90926 — Logsign SIEM low-privilege authenticated network-reachable code injection — Covered with adaptation where low-privilege authenticated activity against Logsign SIEM 6.4.101 through versions before 6.4.117 reaches the network-accessible vulnerable application path and produces code injection or arbitrary code execution, abnormal parent or child processes, unexpected service activity, filesystem or configuration changes, credential or secret access, outbound communication, administrator-state changes, connector or ingestion changes, alerting or logging gaps, or loss of confidence in SIEM-record integrity. Reliable implementation depends on Logsign SIEM asset and version inventory, authenticated-user and privilege context, management and application-path reachability, request and application telemetry where available, process and child-process evidence, filesystem and configuration state, credential and secret use, network behavior, administrator changes, connector and ingestion configuration, alerting and logging state, security-record integrity, remediation state, and incident-response findings. TR-CERT identifies CVE-2026-90926 as CWE-94 code injection with CVSS 8.8 and identifies Logsign SIEM 6.4.101 through versions before 6.4.117 as affected.
· CVE-2026-90925 — Logsign SIEM low-privilege authenticated path traversal — Covered with adaptation where low-privilege authenticated activity against Logsign SIEM 6.4.101 through versions before 6.4.117 reaches the network-accessible vulnerable application path and produces path-traversal behavior, unauthorized file or directory modification, filesystem or configuration changes, service degradation, connector or ingestion changes, alerting or logging gaps, or consequential loss of confidence in SIEM-record integrity. Reliable implementation depends on Logsign SIEM asset and version inventory, authenticated-user and privilege context, management and application-path reachability, request and path telemetry where available, file and filesystem evidence, configuration state, service behavior, administrator activity, connector and ingestion state, security-record integrity, remediation state, and incident-response findings. TR-CERT identifies CVE-2026-90925 as CWE-22 path traversal with CVSS 7.1 and identifies Logsign SIEM 6.4.101 through versions before 6.4.117 as affected.
· CVE-2026-90924 — Logsign SIEM use of default administrative credentials — Covered with adaptation where network-reachable Logsign SIEM 6.4.101 through versions before 6.4.117 retains default administrative credentials and unauthenticated activity uses common or default usernames and passwords to obtain unauthorized administrative access, followed by configuration changes, credential or secret access, process or service activity, connector or ingestion changes, alerting or logging gaps, security-record modification, outbound communication, or downstream security-monitoring effects. Reliable implementation depends on Logsign SIEM asset and version inventory, management-interface reachability, authentication and administrator-session telemetry, credential-change state, process and service evidence, filesystem and configuration state, credential and secret use, connector and ingestion configuration, alerting and logging state, security-record integrity, network behavior, remediation state, and incident-response findings. TR-CERT identifies CVE-2026-90924 as CWE-1392 use of default credentials with CVSS 9.8 and identifies Logsign SIEM 6.4.101 through versions before 6.4.117 as affected. The Logsign SIEM cohort is product-specific security-monitoring coverage. CVE-2026-90924 represents unauthenticated default-credential administrative access, CVE-2026-90925 represents low-privilege authenticated path traversal, and CVE-2026-90926 represents low-privilege authenticated network-reachable code injection. Successful exploitation may affect process and child-process execution, files and configuration, credentials and secrets, outbound activity, administrator state, connectors and ingestion, alerting and logging, and the integrity of SIEM records. Logsign SIEM 6.4.117 or later is the correction boundary for the affected 6.4.101-through-before-6.4.117 range.
· CVE-2026-90457 — CISA Malcolm weakly protected administrator-password material stored in a world-readable local file — Covered with adaptation where weakly protected administrator-password material stored in a world-readable local file is accessed, recovered offline, or used to obtain unauthorized administrative authority. Reliable implementation depends on Malcolm asset and version inventory, filesystem permissions, file-access evidence, backup or local-access context, credential-use evidence, administrator activity, and incident-response findings.
· CVE-2026-90456 — CISA Malcolm default administrator password from sample inventory configuration — Covered with adaptation where a default administrator password from sample inventory configuration remains in a deployed Malcolm administrative interface and is used to obtain unauthorized privileged access. Reliable implementation depends on deployment provenance, administrator-interface exposure, authentication records, credential-change history, administrator activity, and incident-response evidence.
· CVE-2026-90455 — CISA Malcolm reintroduced vulnerable HTTP-library path under the documented trusted-vendor URL condition — Covered with adaptation where the affected Malcolm implementation reaches the documented trusted-vendor URL path through a reintroduced vulnerable HTTP library and produces abnormal request, response, or dependency behavior under the constrained documented conditions. Reliable implementation depends on Malcolm version, affected dependency state, request path and destination evidence, application behavior, and incident-response findings.
· CVE-2026-90454 — CISA Malcolm authenticated modification of session-record tags in read-only deployments — Covered with adaptation where an authenticated user modifies session-record tags despite read-only deployment expectations, producing unauthorized monitoring-record modification or loss of evidence integrity. Reliable implementation depends on deployment mode, authenticated identity, session-record history, tag modification records, authorization state, and independent evidence integrity.
· CVE-2026-88007 — Traefik HTTP/3 backend connection reuse affecting NTLM or Negotiate authentication identity — Covered with adaptation where Traefik's HTTP/3 request path reuses a shared backend connection already authenticated through connection-bound NTLM or Negotiate authentication, allowing an unrelated client to inherit the victim's backend identity, access protected data, or perform actions as the victim. Reliable implementation depends on Traefik asset and version inventory, HTTP/3 exposure, backend NTLM or Negotiate use, frontend connection attribution, backend connection and transport identity, keep-alive and reuse state, authentication context, downstream application access, and incident-response evidence.
· CVE-2026-88004 — Traefik request-trailer header sanitization failure — Covered with adaptation where Traefik v3 entrypoint header-name protections inspect request headers but fail to apply equivalent sanitization to request trailers, allowing attacker-controlled trusted or aliased header names to reach a downstream component and potentially influence identity or forwarding context. Reliable implementation depends on Traefik v3 asset and version inventory, request-trailer visibility, entrypoint header-protection configuration, downstream trailer handling, effective application identity or routing behavior, and incident-response evidence.
· CVE-2026-87107 — HashiCorp Consul unauthorized deregistration of peer-imported catalog objects — Covered with adaptation where a Consul ACL token with service-write or node-write permission causes unauthorized deregistration of peer-imported nodes, services, or health checks, producing catalog-state loss, service-discovery changes, routing effects, or downstream availability impact. Reliable implementation depends on active cluster peering, local token permissions, peer-imported object inventory, catalog deregistration activity, replication state, service and health-check history, and incident-response evidence. Fixed versions are Consul 2.0.4 and Consul Enterprise 1.21.18, 1.22.12, and 2.0.4.
· CVE-2026-87106 — HashiCorp Consul native RPC pre-authorization memory exhaustion denial of service — Covered with adaptation where a client capable of completing the Consul native RPC mTLS handshake sends crafted request-header data that produces excessive memory consumption, process termination, control-plane instability, or service-discovery interruption before ACL authorization is evaluated. Reliable implementation depends on Consul server inventory, RPC reachability, mTLS client identity, connection telemetry where available, server-memory behavior, process termination or restart records, cluster state, and service-discovery availability. Fixed versions are Consul 2.0.4 and Consul Enterprise 1.21.18, 1.22.12, and 2.0.4.
· CVE-2026-87090 — HashiCorp Consul catalog node-write authorization bypass and node-identity takeover — Covered with adaptation where a Consul ACL token with node-write permission on one authorized node submits crafted catalog registration activity affecting another node, resulting in unauthorized deletion of the target node's catalog registration, node-identity takeover, service or health-check reassignment, or downstream service-discovery effects. Reliable implementation depends on ACL use, token scope, catalog registration activity, node IDs, node names, service and health-check state, and incident-response evidence. Fixed versions are Consul 2.0.4 and Consul Enterprise 1.21.18, 1.22.12, and 2.0.4.
· CVE-2026-86060 — MikroTik RouterOS SSH session privilege manipulation — Covered with adaptation where MikroTik RouterOS SSH session privilege manipulation produces unauthorized full-administrator sessions, abnormal privilege state, administrator changes, configuration changes, tunnel or proxy creation, or downstream network-control effects. CERT Polska confirms this vulnerability is used with CVE-2026-67276 in the actively exploited MikroTrick chain. CISA added CVE-2026-86060 to the Known Exploited Vulnerabilities Catalog on September 10, 2026.
· CVE-2026-85542 — IBM Guardium Data Protection authenticated GIM bundle-import command injection affecting Central Manager — Covered with adaptation where an authenticated Guardium user imports a crafted Guardium Installation Manager bundle whose attacker-controlled arguments are passed to tar, resulting in arbitrary command execution with elevated privileges on the Central Manager. Reliable implementation depends on GIM bundle-import records, authenticated identity, Central Manager role, archive metadata, process ancestry, tar invocation, privilege context, filesystem activity, configuration state, and downstream Guardium effects. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84893 — IBM Guardium Data Protection authenticated PESI SQL injection and internal-database information access — Covered with adaptation where an authenticated attacker abuses SQL injection in the Guardium PESI service to access sensitive information in the internal database. Reliable implementation depends on PESI exposure, authenticated-session context, affected requests, SQL and database-access telemetry, sensitive-record access, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84884 — IBM Guardium Data Protection reversibly protected internal REST service-account credential enabling recovery of administrative REST authority — Covered with adaptation where an authenticated attacker accesses an internal REST service-account password stored in reversibly protected or plaintext-equivalent form, recovers the credential, and uses it to obtain an administrative REST access token. Reliable implementation depends on credential-store access, authenticated identity, REST service-account use, administrative-token issuance, privileged REST actions, configuration changes, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84882 — IBM Guardium Data Protection authenticated Universal Connector Oracle Wallet upload path traversal and arbitrary file write — Covered with adaptation where an authenticated remote attacker abuses path traversal in the Universal Connector Oracle Wallet upload component to write arbitrary files to the Guardium system. Reliable implementation depends on authenticated session context, Universal Connector activity, Oracle Wallet uploads, submitted paths and filenames, filesystem writes, service or process follow-on, configuration effects, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84842 — IBM Guardium Data Protection authenticated Datasource REST path traversal and arbitrary file deletion — Covered with adaptation where an authenticated remote attacker exploits path traversal in the Datasource REST component to delete files outside the intended path, potentially causing denial of service or system-integrity impact. Reliable implementation depends on REST identity and request context, Datasource operations, path arguments, filesystem deletion evidence, service availability, configuration state, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84440 — IBM Guardium Data Protection authenticated SNMP alert-policy command injection with root-context execution — Covered with adaptation where an authenticated attacker able to influence Guardium policy-alert text causes attacker-controlled data to reach the SNMP alert-notification path and execute as operating-system commands through the SNMP alerter service running with root privileges. Reliable implementation depends on policy-alert modification, authenticated identity, SNMP notification configuration, process and command telemetry, root-context execution, configuration changes, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84278 — IBM Guardium Data Protection authenticated high-privilege SUID-root ssh_config_wrapper command injection — Covered with adaptation where an authenticated high-privilege user supplies attacker-controlled arguments to the SUID-root ssh_config_wrapper component and obtains arbitrary command execution with root privileges. Reliable implementation depends on local or administrative identity, ssh_config_wrapper invocation, argument values, SUID execution state, root-context process activity, filesystem and configuration changes, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84275 — IBM Guardium Data Protection unauthenticated GIM file-upload path traversal and arbitrary file write to Collector — Covered with adaptation where an unauthenticated remote attacker abuses path traversal in Guardium Installation Manager file-upload functionality to write arbitrary files to a Collector. Reliable implementation depends on GIM exposure, file-upload request telemetry, Collector role, path and filename data, resulting filesystem writes, process or service follow-on, configuration effects, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84271 — IBM Guardium Data Protection local patch-installer signature-verification bypass and root code execution — Covered with adaptation where a local attacker abuses insufficient signature validation in the Guardium patch installer and causes attacker-controlled code to execute with root privileges. Reliable implementation depends on local-access context, patch-installation activity, package or signature validation evidence, installer process activity, root-context execution, filesystem changes, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84250 — IBM Guardium Data Protection weak cryptographic protection and hard-coded recovery key allowing recovery of the root password — Covered with adaptation where a local attacker exploits weak cryptographic protection and a hard-coded recovery key in the pkcrypto passkey component to recover the root password and obtain root privileges. Reliable implementation depends on local-access context, pkcrypto or passkey artifact access, root credential use, authentication records, privileged process activity, configuration changes, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84247 — IBM Guardium Data Protection authenticated remote path traversal with denial-of-service impact — Covered with adaptation where an authenticated remote attacker exploits a Guardium path-traversal flaw and causes denial-of-service effects. Reliable implementation depends on affected request and path context, authenticated identity, filesystem or resource effects, service degradation or restart evidence, configuration state, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84245 — IBM Guardium Data Protection local cpwrapper privilege escalation to root — Covered with adaptation where a low-privileged local user abuses the Guardium cpwrapper component to escalate privileges to root and access or modify sensitive system files. Reliable implementation depends on local-account context, cpwrapper invocation, SUID or privilege state, root-context activity, filesystem access or modification, configuration changes, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84244 — IBM Guardium Data Protection stored web-input execution in Quick Search through attacker-influenced monitored database traffic — Covered with adaptation where an unauthenticated attacker able to influence monitored database traffic injects content that is rendered unsafely in the Guardium Quick Search results grid and executes script in the browser of an authenticated Guardium user. Reliable implementation depends on monitored database traffic, Quick Search usage, authenticated user and browser context, rendered content, subsequent session actions, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84241 — IBM Guardium Data Protection remote improper-authorization security bypass — Covered with adaptation where an unauthenticated remote attacker bypasses expected Guardium authorization controls and reaches functionality or data outside the intended security boundary. Reliable implementation depends on affected interface or service context, request telemetry, authentication and authorization state, resulting privileged or protected-function activity, configuration or data changes, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84239 — IBM Guardium Data Protection high-privilege authenticated SQL injection and sensitive-information access — Covered with adaptation where a high-privilege authenticated remote attacker exploits SQL injection in Guardium to obtain sensitive information. Reliable implementation depends on authenticated administrator or privileged-session context, affected request telemetry, SQL and database activity, sensitive-data access, service effects, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84108 — IBM Guardium Data Protection unauthenticated web-input-neutralization weakness producing attacker-controlled execution — Covered with adaptation where an unauthenticated remote attacker supplies web input that is improperly neutralized during page generation and produces attacker-controlled execution or consequential application behavior under the documented Guardium conditions. Reliable implementation depends on affected web endpoint, request and response data, browser or application execution context, resulting privileged or sensitive actions, configuration changes, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84106 — IBM Guardium Data Protection authenticated web-input-neutralization weakness producing attacker-controlled execution — Covered with adaptation where an authenticated remote attacker supplies input that is improperly neutralized during web-page generation and produces attacker-controlled execution in the affected Guardium web context. Reliable implementation depends on authenticated-session context, affected page or request parameters, browser or application execution evidence, resulting privileged activity, configuration effects, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84105 — IBM Guardium Data Protection authenticated SQL injection and sensitive-information access — Covered with adaptation where an authenticated remote attacker exploits SQL injection to obtain sensitive information from Guardium. Reliable implementation depends on authenticated-session context, affected requests, SQL and database telemetry, data-access evidence, authorization context, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84089 — IBM Guardium Data Protection local improper privilege management and privilege escalation — Covered with adaptation where a low-privileged local Guardium user abuses improper privilege management and gains elevated privileges. Reliable implementation depends on local-account and session context, privilege state, process and command activity, root-context evidence, filesystem and configuration effects, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84086 — IBM Guardium Data Protection high-privilege authenticated pathname-restriction weakness with arbitrary-code-execution impact — Covered with adaptation where a high-privilege authenticated remote attacker exploits insufficient pathname restriction and achieves arbitrary-code execution under the documented Guardium path-traversal condition. Reliable implementation depends on authenticated administrator context, affected request and path data, filesystem access or modification, process execution, configuration state, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84085 — IBM Guardium Data Protection remote unauthenticated OS-command injection under the documented high-complexity condition — Covered with adaptation where an unauthenticated remote attacker reaches a Guardium OS-command-injection path and executes arbitrary operating-system commands under the documented high-complexity condition. Reliable implementation depends on affected interface exposure, request and argument telemetry, process and command execution, privilege context, filesystem or configuration effects, outbound communication, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84084 — IBM Guardium Data Protection remote CSRF security bypass — Covered with adaptation where an unauthenticated remote attacker uses a Guardium cross-site-request-forgery condition and causes an authenticated user to perform security-sensitive actions without intended authorization. Reliable implementation depends on affected web function, victim authenticated-session context, request origin and referrer evidence where available, resulting administrative or configuration changes, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84083 — IBM Guardium Data Protection local Collector nmap_wrapper SUID-root privilege escalation — Covered with adaptation where a low-privileged local user abuses the Collector nmap_wrapper component to execute with root privileges and obtain unauthorized elevated access. Reliable implementation depends on Collector role, local account and session context, nmap_wrapper invocation, SUID and privilege state, process and command activity, root-context evidence, filesystem and configuration changes, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84081 — IBM Guardium Data Protection improper certificate validation — Covered with adaptation where affected Guardium communications accept or trust a certificate that should fail validation and the condition enables interception, impersonation, or other trust-boundary effects. Reliable implementation depends on affected communication path, certificate and TLS evidence, peer identity, network context, consequential access or configuration effects, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84077 — IBM Guardium Data Protection remote CSRF security bypass — Covered with adaptation where a victim's authenticated Guardium session is used to perform an unauthorized state-changing action. Reliable implementation depends on administrator-session evidence, request origin and route, resulting state or configuration changes, browser or proxy telemetry where available, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84076 — IBM Guardium Data Protection authenticated improper-authorization security bypass — Covered with adaptation where authenticated Guardium activity reaches functionality beyond the user's intended authorization and results in unauthorized access, modification, or privileged behavior. Reliable implementation depends on authenticated identity, role and privilege state, affected function, authorization decisions, downstream activity, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84074 — IBM Guardium Data Protection authenticated web-input-neutralization weakness with user interaction — Covered with adaptation where authenticated attacker-controlled input is rendered in a victim user's Guardium browser context and produces active-content execution under the documented conditions. Reliable implementation depends on authenticated attacker context, affected route, stored or reflected values, victim browser and session evidence, resulting application actions, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84070 — IBM Guardium Data Protection authenticated web-input-neutralization weakness with user interaction — Covered with adaptation where authenticated attacker-controlled input is rendered in a victim user's Guardium browser context and produces active-content execution under the documented conditions. Reliable implementation depends on authenticated attacker context, affected route, stored or reflected values, victim browser and session evidence, resulting application actions, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-84036 — IBM Guardium Data Protection authenticated improper-authorization security bypass — Covered with adaptation where authenticated Guardium activity reaches functionality beyond the user's intended authority and produces unauthorized access, modification, or privileged behavior. Reliable implementation depends on authenticated identity, role and privilege state, affected function, authorization decisions, resulting activity, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-82967 — IBM Guardium Data Protection unauthenticated bypass of IP-based management-interface access controls — Covered with adaptation where a remote unauthenticated source reaches Guardium management functionality despite configured source-IP restrictions and performs access or actions that should have been denied. Reliable implementation depends on source network, management-interface exposure, configured IP restrictions, request telemetry, authentication state, resulting activity, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-82896 — IBM Guardium Data Protection authenticated path traversal — Covered with adaptation where authenticated Guardium activity escapes an intended filesystem path and produces unauthorized file access, modification, or consequential service effects under the documented conditions. Reliable implementation depends on authenticated identity, affected request or workflow, path values, filesystem evidence, service state, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-82893 — IBM Guardium Data Protection local improper privilege management and privilege escalation — Covered with adaptation where local activity abuses an affected privilege boundary and results in unauthorized elevated access or execution. Reliable implementation depends on local identity, affected component, privilege state, process behavior, filesystem or configuration effects, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-82892 — IBM Guardium Data Protection remote unauthenticated OS-command injection under the documented high-complexity condition — Covered with adaptation where unauthenticated remote activity reaches the affected Guardium function under the required prerequisite and results in operating-system command execution. Reliable implementation depends on affected interface exposure, request evidence, prerequisite state, process and command telemetry, filesystem or configuration effects, network behavior, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-82890 — IBM Guardium Data Protection authenticated arbitrary JavaScript execution through improper web-input neutralization — Covered with adaptation where a remote authenticated attacker causes attacker-controlled JavaScript execution because Guardium fails to neutralize web input correctly during page generation. Reliable implementation depends on authenticated-session context, affected web input and rendered output, browser or session behavior, resulting privileged or sensitive actions, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-82887 — IBM Guardium Data Protection authenticated OS-command injection — Covered with adaptation where a remote authenticated attacker exploits Guardium OS-command injection and executes arbitrary commands. Reliable implementation depends on authenticated-session context, affected request or argument values, command and process telemetry, privilege context, filesystem and configuration effects, outbound behavior, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-82885 — IBM Guardium Data Protection authenticated REST API missing authorization and elevated privileges — Covered with adaptation where a remote authenticated attacker exploits missing authorization in the Guardium REST API and gains elevated privileges. Reliable implementation depends on authenticated identity and role, REST request telemetry, authorization outcomes, administrative-token or privilege state, resulting configuration or protected-resource activity, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-82832 — IBM Guardium Data Protection authenticated web-input-neutralization weakness producing attacker-controlled execution — Covered with adaptation where a remote authenticated attacker supplies web input that is improperly neutralized during Guardium page generation and produces attacker-controlled execution under the documented affected conditions. Reliable implementation depends on authenticated-session context, affected web request and rendered content, resulting browser or application execution, sensitive or privileged follow-on activity, and incident-response findings. Guardium Data Protection 12.2 is affected and IBM directs customers to 12.0p233. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-82045 — UTMStack authenticated JPQL injection affecting network-scan property-value search — Covered with adaptation where authenticated manipulation of affected UTMStack network-scan property-value search input alters JPQL processing and results in unauthorized access to sensitive entity information, including credential-related records. Reliable implementation depends on UTMStack asset and version inventory, authenticated identity and role context, affected search activity, query and database evidence, sensitive-record and credential access, subsequent authentication or administrative activity, remediation status, and incident-response findings. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· CVE-2026-82044 — UTMStack authenticated PDF-reporting server-side request forgery — Covered with adaptation where authenticated UTMStack PDF-reporting activity using an attacker-controlled URL causes server-side retrieval of internal resources, OpenSearch services, cloud instance-metadata services, or other resources reachable from the UTMStack server. Reliable implementation depends on UTMStack asset and version inventory, authenticated identity and role context, PDF-reporting requests, requested destinations, internal-service or cloud-metadata network activity, resulting report content, credential or sensitive-data access, remediation status, and incident-response findings. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· CVE-2026-82043 — UTMStack unauthenticated password-reset account enumeration — Covered with adaptation where unauthenticated password-reset activity produces distinguishable responses that permit identification of valid UTMStack accounts and supports consequential credential targeting, phishing, or authentication attacks. Reliable implementation depends on UTMStack asset and version inventory, password-reset request and response activity, account state, source context, subsequent authentication or credential-targeting activity, remediation status, and incident-response findings. Account enumeration alone should not be treated as evidence of account compromise. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· CVE-2026-82042 — UTMStack internal-key authentication-path bypass permitting privileged API access — Covered with adaptation where possession or misuse of a valid UTMStack internal key permits access to privileged API functionality without completion of the normal user-account or JWT-authentication path and results in unauthorized privileged management activity. Reliable implementation depends on UTMStack asset and version inventory, internal-key state and provenance, API reachability, authentication context, account and administrator activity, configuration and security-rule changes, credential access, remediation status, and incident-response findings. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· CVE-2026-82041 — UTMStack STOMP command-WebSocket missing authorization permitting operating-system command delivery to connected agents — Covered with adaptation where authenticated access to the affected STOMP command WebSocket without sufficient authorization results in attacker-controlled operating-system commands being forwarded through the UTMStack control plane to connected agents or managed systems. Reliable implementation depends on UTMStack asset and version inventory, authenticated identity and role context, STOMP command-WebSocket activity, connected-agent identity, submitted command data, managed-endpoint process and command telemetry, privilege context, downstream endpoint state, remediation status, and incident-response findings. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· CVE-2026-82040 — UTMStack authenticated identity-provider server-side request forgery — Covered with adaptation where authenticated manipulation of UTMStack identity-provider metadata input causes the UTMStack server to issue requests to internal network resources or cloud instance-metadata services that are not directly reachable by the attacker. Reliable implementation depends on UTMStack asset and version inventory, authenticated identity and role context, identity-provider configuration, metadata URL activity, server-originated network requests, internal-service or cloud-metadata destinations, consequential information access, remediation status, and incident-response findings. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· CVE-2026-82039 — UTMStack authenticated SQL injection affecting asset-group search — Covered with adaptation where authenticated manipulation of UTMStack asset-group search input reaches the underlying database query and results in unauthorized SQL execution, database access, or modification of information maintained by the security-management platform. Reliable implementation depends on UTMStack asset and version inventory, authenticated identity and role context, asset-group search activity, request and query evidence, database activity, sensitive-record access or modification, remediation status, and incident-response findings. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· CVE-2026-81939 — SonicWall Network Security Manager On-Prem Zip Slip archive path traversal — Covered with adaptation where SonicWall Network Security Manager On-Prem file-upload or archive-processing activity produces Zip Slip path traversal, extraction outside the intended destination directory, unauthorized file placement or modification, service-context effects, configuration changes, or downstream network-security-management impact.
· CVE-2026-79820 — HPE Integrated Lights-Out 7 remote user-validation failure — Covered with adaptation where activity against affected HPE iLO 7 firmware produces unauthorized management-plane access, abnormal authentication or session behavior, unexpected administrator activity, configuration or firmware changes, managed-server control activity, unexpected outbound communication, or consequential server-management effects. Reliable implementation depends on HPE iLO 7 asset and firmware inventory, management-interface reachability, authentication and session context, administrator and configuration records, firmware and remediation state, managed-server activity, network telemetry, and incident-response findings. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status.
· CVE-2026-79818 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79817 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79816 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79815 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79814 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79813 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79812 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79811 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79810 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79809 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79808 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79807 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79806 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79805 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79803 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79802 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79801 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79800 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79799 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79798 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79797 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79796 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79794 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-79698 — Advantech WISE-6610 / WISE-6610P Node-RED Library command injection — Covered with adaptation where authenticated Advantech WISE-6610 or WISE-6610P Node-RED Library administration reaches nodered_lib_apply and manipulation of the act argument produces command injection, unexpected process execution, configuration change, file activity, outbound communication, or downstream network-control effects.
· CVE-2026-79697 — Advantech WISE-6610 / WISE-6610P Basic Station certificate-management command injection — Covered with adaptation where authenticated Advantech WISE-6610 or WISE-6610P Basic Station certificate administration reaches basicstation_apply and manipulation of the act argument produces command injection, unexpected process execution, configuration or certificate-related change, file activity, outbound communication, or downstream network-control effects.
· CVE-2026-79678 — FreeIPA authenticated identity-provider template evaluation causing environment-variable disclosure and denial of service — Covered with adaptation where an authenticated FreeIPA principal invokes idp-add with attacker-controlled organization or base-URL values that reach identity-provider template evaluation before the intended authorization check, resulting in server-process environment-variable disclosure, abnormal memory consumption, service degradation, or denial of service. Reliable implementation depends on FreeIPA asset and version inventory, authenticated principal and session context, idp-add activity, IdP provider and template parameters, API and audit logs, process-environment sensitivity, service memory and health telemetry, container or RPM deployment context, and incident-response evidence. The flaw does not permit arbitrary code execution. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-78328 — SonicWall Network Security Manager On-Prem Admin-to-SuperAdmin privilege escalation — Covered with adaptation where SonicWall Network Security Manager On-Prem Admin activity produces unauthorized elevation to SuperAdmin, abnormal role or permission state, privileged administrative activity, configuration changes, security-policy changes, or downstream managed-firewall effects.
· CVE-2026-78327 — SonicWall Network Security Manager On-Prem authenticated SuperAdmin OS command injection — Covered with adaptation where authenticated SonicWall Network Security Manager On-Prem SuperAdmin activity, crafted management-interface input, OS command injection, underlying-host command execution, process activity, configuration changes, outbound communication, or downstream network-security-management effects can be mapped into the report's management-plane-to-host-control model.
· CVE-2026-77557 — Ubiquiti UniFi Protect AI Key improper access control and privilege escalation — Covered with adaptation where UniFi Protect AI Key improper access control, unauthorized privilege escalation, abnormal administrative activity, configuration effects, or device-level behavior can be mapped into the report's access-control and privileged-device model.
· CVE-2026-77554 — Ubiquiti UniFi Talk Application command injection — Covered with adaptation where UniFi Talk Application command injection produces service-context execution, child-process creation, elevated host activity, configuration changes, outbound communication, or communications-service impact.
· CVE-2026-77553 — Ubiquiti UniFi Access Application improper access control — Covered with adaptation where UniFi Access Application improper access control produces privilege escalation, abnormal administrative activity, host-device effects, configuration changes, or physical-access-system impact.
· CVE-2026-77552 — Ubiquiti UniFi Enterprise Audio/Video Bridge command injection — Covered with adaptation where UniFi Enterprise Audio/Video Bridge command injection produces device-level execution, privileged activity, configuration changes, outbound communication, or audio/video infrastructure impact.
· CVE-2026-77551 — Ubiquiti UniFi Connect Display Cast Pro improper access control — Covered with adaptation where UniFi Connect Display Cast Pro improper access control produces unauthorized privilege escalation, abnormal management activity, configuration change, or device-level effects.
· CVE-2026-77548 — Ubiquiti UniFi Protect Application command injection — Covered with adaptation where UniFi Protect Application command injection produces service-context execution, child-process activity, elevated host behavior, filesystem modification, configuration effects, recorder or storage impact, or outbound communication.
· CVE-2026-77547 — Ubiquiti UniFi Access Application command injection — Covered with adaptation where UniFi Access Application command injection produces service-context execution, elevated host activity, configuration changes, administrative effects, or physical-access-system impact.
· CVE-2026-77546 — Ubiquiti UniFi Access Application command injection — Covered with adaptation where UniFi Access Application command injection produces service-context execution, elevated host activity, configuration changes, administrative effects, or physical-access-system impact.
· CVE-2026-77543 — Ubiquiti UniFi Access Application command injection — Covered with adaptation where UniFi Access Application command injection produces service-context execution, elevated host activity, configuration changes, administrative effects, or physical-access-system impact.
· CVE-2026-77542 — Ubiquiti UID Enterprise Agent command injection — Covered with adaptation where UID Enterprise Agent command injection produces host-level command execution, service-context activity, privilege use, configuration changes, identity-system effects, or outbound communication.
· CVE-2026-77541 — Ubiquiti UniFi Network Application improper access control — Covered with adaptation where UniFi Network Application improper access control produces privilege escalation, role anomalies, unauthorized administrative activity, configuration changes, or downstream managed-device effects.
· CVE-2026-77537 — Ubiquiti UniFi Protect Application unauthenticated command injection — Covered with adaptation where unauthenticated UniFi Protect Application command injection produces service-context execution, elevated host activity, filesystem modification, configuration effects, recorder or storage impact, or outbound communication.
· CVE-2026-77535 — Ubiquiti UniFi Network Application command injection against an adopted device — Covered with adaptation where UniFi Network Application command injection against an adopted device produces device-command execution, privileged device activity, administrator anomalies, configuration changes, outbound communication, or downstream network-control impact.
· CVE-2026-77533 — Ubiquiti UniFi Protect Application command injection — Covered with adaptation where UniFi Protect Application command injection produces service-context execution, child-process activity, elevated host behavior, filesystem modification, configuration effects, recorder or storage impact, or outbound communication.
· CVE-2026-76754 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-76753 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-76752 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-76751 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-76750 — HPE Networking ClearPass Policy Manager vulnerability documented in HPESBNW05158 Rev. 1 — Covered with adaptation for the HPE Networking ClearPass Policy Manager 28-vulnerability cohort
· CVE-2026-76749 — HPE Networking AOS-Switch vulnerability documented in HPESBNW05156 Rev. 1 — Covered with adaptation for the HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 vulnerability cohort
· CVE-2026-76748 — HPE Networking AOS-Switch vulnerability documented in HPESBNW05156 Rev. 1 — Covered with adaptation for the HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 vulnerability cohort
· CVE-2026-76747 — HPE Networking AOS-Switch vulnerability documented in HPESBNW05156 Rev. 1 — Covered with adaptation for the HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 vulnerability cohort
· CVE-2026-76746 — HPE Networking AOS-Switch vulnerability documented in HPESBNW05156 Rev. 1 — Covered with adaptation for the HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 vulnerability cohort
· CVE-2026-76745 — HPE Networking AOS-Switch vulnerability documented in HPESBNW05156 Rev. 1 — Covered with adaptation for the HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 vulnerability cohort
· CVE-2026-76744 — HPE Networking AOS-Switch vulnerability documented in HPESBNW05156 Rev. 1 — Covered with adaptation for the HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 vulnerability cohort
· CVE-2026-76743 — HPE Networking AOS-Switch vulnerability documented in HPESBNW05156 Rev. 1 — Covered with adaptation for the HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 vulnerability cohort
· CVE-2026-76742 — HPE Networking AOS-Switch vulnerability documented in HPESBNW05156 Rev. 1 — Covered with adaptation for the HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 vulnerability cohort
· CVE-2026-76741 — HPE Networking AOS-Switch vulnerability documented in HPESBNW05156 Rev. 1 — Covered with adaptation for the HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 vulnerability cohort
· CVE-2026-76717 — HPE Networking Analytics and Location Engine vulnerability documented in HPESBNW05137 Rev. 1 — Covered with adaptation for the HPE Networking Analytics and Location Engine CVE-2026-76708 through CVE-2026-76717 vulnerability cohort. Reliable implementation depends on ALE asset and version inventory, affected interface or service reachability, authentication and session context where applicable, request and API telemetry, sensitive-data, filesystem, process, service, configuration, credential, availability, and downstream evidence appropriate to the documented ALE behavior. ALE 5.0.0.0 and earlier are affected; ALE 5.1.0.0 is corrected. Available authoritative evidence does not establish CISA KEV status.
· CVE-2026-76716 — HPE Networking Analytics and Location Engine vulnerability documented in HPESBNW05137 Rev. 1 — Covered with adaptation for the HPE Networking Analytics and Location Engine CVE-2026-76708 through CVE-2026-76717 vulnerability cohort. Reliable implementation depends on ALE asset and version inventory, affected interface or service reachability, authentication and session context where applicable, request and API telemetry, sensitive-data, filesystem, process, service, configuration, credential, availability, and downstream evidence appropriate to the documented ALE behavior. ALE 5.0.0.0 and earlier are affected; ALE 5.1.0.0 is corrected. Available authoritative evidence does not establish CISA KEV status.
· CVE-2026-76715 — HPE Networking Analytics and Location Engine documented man-in-the-middle condition associated with root code execution — Covered with adaptation where the documented man-in-the-middle condition affecting ALE is present and activity results in root code execution or consequential privileged system effects. This entry must not be generalized to arbitrary unauthenticated direct remote code execution because exploitation depends on the documented man-in-the-middle condition. Reliable implementation depends on ALE asset and version inventory, network-path and interception evidence, affected component activity, process and root-context telemetry, filesystem and configuration state, remediation status, and incident-response findings. ALE 5.0.0.0 and earlier are affected; ALE 5.1.0.0 is corrected. Available authoritative evidence does not establish CISA KEV status.
· CVE-2026-76714 — HPE Networking Analytics and Location Engine authenticated web-interface command execution with root privileges — Covered with adaptation where an authenticated remote user abuses the affected ALE web interface and executes commands with root privileges, producing abnormal privileged process activity, filesystem or configuration changes, outbound communication, or consequential appliance effects. Reliable implementation depends on ALE asset and version inventory, authenticated identity and session context, web-interface request activity, command and process telemetry, root-context execution, filesystem and configuration state, remediation status, and incident-response findings. This is an authenticated path and must not be represented as unauthenticated RCE. ALE 5.0.0.0 and earlier are affected; ALE 5.1.0.0 is corrected. Available authoritative evidence does not establish CISA KEV status.
· CVE-2026-76713 — HPE Networking Analytics and Location Engine authenticated maintenance-restore filesystem access with root privileges — Covered with adaptation where an authenticated remote user abuses ALE maintenance-restore functionality and gains filesystem access with root privileges, producing file access or modification, configuration changes, privileged follow-on activity, or consequential system effects. Reliable implementation depends on ALE asset and version inventory, authenticated identity and session context, maintenance-restore activity, filesystem access and modification evidence, root-context behavior, configuration state, remediation status, and incident-response findings. This is an authenticated path and must not be represented as unauthenticated root filesystem access. ALE 5.0.0.0 and earlier are affected; ALE 5.1.0.0 is corrected. Available authoritative evidence does not establish CISA KEV status.
· CVE-2026-76712 — HPE Networking Analytics and Location Engine vulnerability documented in HPESBNW05137 Rev. 1 — Covered with adaptation for the HPE Networking Analytics and Location Engine CVE-2026-76708 through CVE-2026-76717 vulnerability cohort. Reliable implementation depends on ALE asset and version inventory, affected interface or service reachability, authentication and session context where applicable, request and API telemetry, sensitive-data, filesystem, process, service, configuration, credential, availability, and downstream evidence appropriate to the documented ALE behavior. ALE 5.0.0.0 and earlier are affected; ALE 5.1.0.0 is corrected. Available authoritative evidence does not establish CISA KEV status.
· CVE-2026-76711 — HPE Networking Analytics and Location Engine vulnerability documented in HPESBNW05137 Rev. 1 — Covered with adaptation for the HPE Networking Analytics and Location Engine vulnerability cohort. Reliable implementation depends on ALE asset and version inventory, affected interface or service reachability, authentication and session context where applicable, request and API telemetry, sensitive-data, filesystem, process, service, configuration, credential, availability, and downstream evidence appropriate to the documented ALE behavior. ALE 5.0.0.0 and earlier are affected; ALE 5.1.0.0 is corrected. Available authoritative evidence does not establish CISA KEV status.
· CVE-2026-76710 — HPE Networking Analytics and Location Engine vulnerability documented in HPESBNW05137 Rev. 1 — Covered with adaptation for the HPE Networking Analytics and Location Engine vulnerability cohort. Reliable implementation depends on ALE asset and version inventory, affected interface or service reachability, authentication and session context where applicable, request and API telemetry, sensitive-data, filesystem, process, service, configuration, credential, availability, and downstream evidence appropriate to the documented ALE behavior. ALE 5.0.0.0 and earlier are affected; ALE 5.1.0.0 is corrected. Available authoritative evidence does not establish CISA KEV status.
· CVE-2026-76709 — HPE Networking Analytics and Location Engine vulnerability documented in HPESBNW05137 Rev. 1 — Covered with adaptation for the HPE Networking Analytics and Location Engine vulnerability cohort. Reliable implementation depends on ALE asset and version inventory, affected interface or service reachability, authentication and session context where applicable, request and API telemetry, sensitive-data, filesystem, process, service, configuration, credential, availability, and downstream evidence appropriate to the documented ALE behavior. ALE 5.0.0.0 and earlier are affected; ALE 5.1.0.0 is corrected. Available authoritative evidence does not establish CISA KEV status.
· CVE-2026-76708 — HPE Networking Analytics and Location Engine vulnerability documented in HPESBNW05137 Rev. 1 — Covered with adaptation for the HPE Networking Analytics and Location Engine vulnerability cohort. Reliable implementation depends on ALE asset and version inventory, affected interface or service reachability, authentication and session context where applicable, request and API telemetry, sensitive-data, filesystem, process, service, configuration, credential, availability, and downstream evidence appropriate to the documented ALE behavior. ALE 5.0.0.0 and earlier are affected; ALE 5.1.0.0 is corrected. Available authoritative evidence does not establish CISA KEV status.
· CVE-2026-76578 — FreeIPA unauthenticated LDAP authorization abuse enabling attacker-controlled Kerberos principal creation and administrators-group membership — Covered with adaptation where an unauthenticated FreeIPA LDAP client combines the self-managed OTP-token ACI with the underlying 389 Directory Server authorization weakness to create an attacker-controlled Kerberos principal, obtain genuine administrators-group membership, perform privileged FreeIPA or LDAP operations, modify identity state, or affect downstream IdM services. Reliable implementation depends on FreeIPA and 389 Directory Server asset and version inventory, LDAP or LDAPS exposure, anonymous-bind state, self-managed OTP-token creation, ipaTokenOwner and managedBy attribute state, Kerberos-principal creation, administrators-group membership changes, FreeIPA API and LDAP administrative activity, ticket or authentication activity, and incident-response evidence. Red Hat describes the flaw as Critical and confirms the attack against a default FreeIPA installation. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-76560 — 389 Directory Server anonymous authorization bypass through empty bind-DN ACI matching — Covered with adaptation where an anonymous LDAP client satisfies a 389 Directory Server SELFDN or USERDN ACI bind-rule check because an empty bind DN matches an explicitly empty stored attribute value, resulting in otherwise unauthorized directory-entry addition or modification. Reliable implementation depends on 389 Directory Server or Red Hat Directory Server asset and version inventory, ACI configuration, attribute-value state, anonymous-access configuration, bind identity, LDAP operation and target-object telemetry, directory-change records, authorization evidence, and incident-response findings. Red Hat states that the vulnerable ACI shape is not shipped by default and impact depends on deployment-specific ACI configuration. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-76501 — Cisco Nexus 3000 and 9000 Series Switches NGOAM remote code execution — Covered with adaptation where affected NGOAM processing permits crafted network input to produce unauthorized code execution, abnormal process or device behavior, configuration effects, service disruption, outbound activity, or downstream switching and routing effects. Reliable implementation depends on affected Nexus model and NX-OS version, NGOAM feature state, network reachability, packet and control-plane evidence, process and device telemetry, configuration state, remediation status, and incident-response findings.
· CVE-2026-76500 — Cisco Application Policy Infrastructure Controller October 2026 hardening vulnerability — Covered with adaptation where APIC-specific behavior documented in Cisco's October 2026 hardening release produces unauthorized management-plane access, application or service effects, privilege consequences, sensitive-data exposure, configuration effects, or control-plane impact. Reliable implementation depends on APIC asset and version inventory, affected service context, authentication and privilege state, API and management-interface telemetry, configuration evidence, remediation status, and incident-response findings.
· CVE-2026-76499 — Cisco Application Policy Infrastructure Controller October 2026 hardening vulnerability — Covered with adaptation where APIC-specific behavior documented in Cisco's October 2026 hardening release produces unauthorized management-plane access, application or service effects, privilege consequences, sensitive-data exposure, configuration effects, or control-plane impact. Reliable implementation depends on APIC asset and version inventory, affected service context, authentication and privilege state, API and management-interface telemetry, configuration evidence, remediation status, and incident-response findings.
· CVE-2026-76498 — Cisco Application Policy Infrastructure Controller October 2026 hardening vulnerability — Covered with adaptation where APIC-specific behavior documented in Cisco's October 2026 hardening release produces unauthorized management-plane access, application or service effects, privilege consequences, sensitive-data exposure, configuration effects, or control-plane impact. Reliable implementation depends on APIC asset and version inventory, affected service context, authentication and privilege state, API and management-interface telemetry, configuration evidence, remediation status, and incident-response findings.
· CVE-2026-76488 — Cisco Application Policy Infrastructure Controller unauthorized file access — Covered with adaptation where authenticated APIC activity permits access to sensitive files outside intended authorization boundaries, resulting in unauthorized data exposure, filesystem access, management-data disclosure, or consequential administrative activity. Reliable implementation depends on APIC asset and version inventory, authenticated identity and privilege context, file-access activity, management-interface and API telemetry, filesystem evidence, remediation status, and incident-response findings.
· CVE-2026-76486 — Cisco Nexus 3000 and 9000 Series Switches NGOAM remote code execution — Covered with adaptation where affected NGOAM processing permits crafted network input to produce unauthorized code execution, abnormal process or device behavior, configuration effects, service disruption, outbound activity, or downstream switching and routing effects.
· CVE-2026-76485 — Cisco Nexus 3000 and 9000 Series Switches NGOAM remote code execution — Covered with adaptation where affected NGOAM processing permits crafted network input to produce unauthorized code execution, abnormal process or device behavior, configuration effects, service disruption, outbound activity, or downstream switching and routing effects.
· CVE-2026-76484 — Cisco License On-Prem October 2026 hardening vulnerability — Covered with adaptation where affected License On-Prem management behavior produces authentication, authorization, credential, management-interface, application, configuration, or service effects outside expected administrative boundaries.
· CVE-2026-76483 — Cisco License On-Prem October 2026 hardening vulnerability — Covered with adaptation where affected License On-Prem management behavior produces authentication, authorization, credential, management-interface, application, configuration, or service effects outside expected administrative boundaries.
· CVE-2026-76482 — Cisco License On-Prem October 2026 hardening vulnerability — Covered with adaptation where affected License On-Prem management behavior produces authentication, authorization, credential, management-interface, application, configuration, or service effects outside expected administrative boundaries.
· CVE-2026-76480 — Cisco License On-Prem October 2026 hardening vulnerability — Covered with adaptation where affected License On-Prem management behavior produces authentication, authorization, credential, management-interface, application, configuration, or service effects outside expected administrative boundaries.
· CVE-2026-76472 — Cisco Meraki October 2026 security-hardening vulnerability — Covered with adaptation where affected Meraki platform behavior produces unauthorized network or management activity, configuration effects, service disruption, data exposure, device instability, or downstream network-control consequences.
· CVE-2026-76471 — Cisco NX-OS Software NX-API remote code execution — Covered with adaptation where network activity against an affected NX-API service results in unauthorized code execution, abnormal NX-OS process activity, configuration or administrator-state changes, outbound communication, persistence, or downstream network-control effects. Reliable implementation depends on NX-OS version, NX-API enablement and exposure, request telemetry, process and command evidence, configuration state, remediation status, and incident-response findings.
· CVE-2026-76470 — Cisco Meraki October 2026 security-hardening vulnerability — Covered with adaptation where affected Meraki platform behavior produces unauthorized network or management activity, configuration effects, service disruption, data exposure, device instability, or downstream network-control consequences.
· CVE-2026-76469 — Cisco Meraki October 2026 security-hardening vulnerability — Covered with adaptation where affected Meraki platform behavior produces unauthorized network or management activity, configuration effects, service disruption, data exposure, device instability, or downstream network-control consequences.
· CVE-2026-76468 — Cisco Meraki October 2026 security-hardening vulnerability — Covered with adaptation where affected Meraki platform behavior produces unauthorized network or management activity, configuration effects, service disruption, data exposure, device instability, or downstream network-control consequences.
· CVE-2026-76467 — Cisco Meraki October 2026 security-hardening vulnerability — Covered with adaptation where affected Meraki platform behavior produces unauthorized network or management activity, configuration effects, service disruption, data exposure, device instability, or downstream network-control consequences.
· CVE-2026-76465 — Cisco Nexus 3000 and 9000 Series Switches MPLS OAM remote code execution — Covered with adaptation where affected MPLS OAM processing permits crafted network input to produce unauthorized code execution, abnormal device or process behavior, configuration effects, service disruption, outbound activity, or downstream routing and switching consequences.
· CVE-2026-76464 — Cisco Meraki October 2026 security-hardening vulnerability — Covered with adaptation where affected Meraki platform behavior produces unauthorized network or management activity, configuration effects, service disruption, data exposure, device instability, or downstream network-control consequences.
· CVE-2026-76463 — Cisco Meraki October 2026 security-hardening vulnerability — Covered with adaptation where affected Meraki platform behavior produces unauthorized network or management activity, configuration effects, service disruption, data exposure, device instability, or downstream network-control consequences.
· CVE-2026-76461 — Cisco Secure Email Gateway SQL injection leading to command execution with root privileges — Covered with adaptation where unauthenticated Cisco Secure Email Gateway email-processing activity involving a crafted email containing malicious SQL statements produces abnormal database interaction, arbitrary SQL-statement execution, appliance service-context execution, command execution, root-context activity, filesystem or configuration changes, credential or sensitive-data access, outbound communication, persistence, or downstream mail-security impact. Reliable implementation depends on Cisco Secure Email Gateway asset and affected-version inventory, Cisco AsyncOS email-processing telemetry, message and connection context, mail_logs review for suspicious SQL statements, database activity where available, process and root-context evidence, filesystem and configuration telemetry, external network and firewall telemetry, administrator-state evidence, and incident-response findings. Cisco identifies 15.5.5-014, 16.0.4-302, and 16.5.0-780 as the first fixed releases for the affected release trains, strongly recommends migration to 16.5.0-780, and states that no workaround addresses the vulnerability. CISA added CVE-2026-76461 to the Known Exploited Vulnerabilities Catalog on September 14, 2026, based on evidence of active exploitation. The KEV designation increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification.
· CVE-2026-76460 — Cisco ISE / ISE-PIC unauthenticated API authentication bypass — Covered with adaptation where an unauthenticated remote attacker sends a crafted request to an affected Cisco ISE / ISE-PIC API endpoint and bypasses authentication to the web-based management interface, producing unauthorized management access or consequential privileged activity. Cisco states that it has observed attempted exploitation of this vulnerability in the wild. Reliable implementation requires affected-product and version inventory, management-interface and API exposure, request telemetry, authentication results, administrator-state and configuration changes, downstream access-control effects, and incident-response findings. CISA added CVE-2026-76460 to the Known Exploited Vulnerabilities Catalog on September 16, 2026, based on evidence of active exploitation. The KEV designation increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification.
· CVE-2026-76459 — Cisco NX-OS Software October 2026 security-hardening vulnerability — Covered with adaptation where affected NX-OS behavior produces unauthorized access, improper input handling, control-plane or process instability, memory or service effects, configuration effects, or other network-control consequences under the Cisco-documented conditions.
· CVE-2026-76458 — Cisco NX-OS Software October 2026 security-hardening vulnerability — Covered with adaptation where affected NX-OS behavior produces unauthorized access, improper input handling, control-plane or process instability, memory or service effects, configuration effects, or other network-control consequences under the Cisco-documented conditions.
· CVE-2026-76457 — Cisco NX-OS Software October 2026 security-hardening vulnerability — Covered with adaptation where affected NX-OS behavior produces unauthorized access, improper input handling, control-plane or process instability, memory or service effects, configuration effects, or other network-control consequences under the Cisco-documented conditions.
· CVE-2026-76456 — Cisco NX-OS Software October 2026 security-hardening vulnerability — Covered with adaptation where affected NX-OS behavior produces unauthorized access, improper input handling, control-plane or process instability, memory or service effects, configuration effects, or other network-control consequences under the Cisco-documented conditions.
· CVE-2026-76455 — Cisco NX-OS Software October 2026 security-hardening vulnerability — Covered with adaptation where affected NX-OS behavior produces unauthorized access, improper input handling, control-plane or process instability, memory or service effects, configuration effects, or other network-control consequences under the Cisco-documented conditions.
· CVE-2026-76454 — Cisco License On-Prem vulnerability — Covered with adaptation where affected License On-Prem activity produces unauthorized management access, authentication or authorization failure, code or command execution, file or database effects, credential exposure, service disruption, or consequential administrative-state change.
· CVE-2026-76453 — Cisco NX-OS Software October 2026 security-hardening vulnerability — Covered with adaptation where affected NX-OS behavior produces unauthorized access, improper input handling, control-plane or process instability, memory or service effects, configuration effects, or other network-control consequences under the Cisco-documented conditions.
· CVE-2026-76452 — Cisco License On-Prem vulnerability — Covered with adaptation where affected License On-Prem activity produces unauthorized management access, authentication or authorization failure, code or command execution, file or database effects, credential exposure, service disruption, or consequential administrative-state change.
· CVE-2026-76451 — Cisco ISE / ISE-PIC authenticated SQL or HQL injection — Covered with adaptation where authenticated Cisco ISE / ISE-PIC API activity produces SQL or HQL injection, arbitrary database queries, or unauthorized viewing or modification of data. Reliable implementation requires administrative-session context, affected API requests, database query and access evidence, authorization context, and incident-response findings.
· CVE-2026-76450 — Cisco ISE / ISE-PIC authenticated SQL or HQL injection — Covered with adaptation where authenticated Cisco ISE / ISE-PIC API activity produces SQL or HQL injection, arbitrary database queries, or unauthorized viewing or modification of data. Reliable implementation requires administrative-session context, affected API requests, database query and access evidence, authorization context, and incident-response findings.
· CVE-2026-76449 — Cisco ISE / ISE-PIC authenticated SQL or HQL injection — Covered with adaptation where authenticated Cisco ISE / ISE-PIC API activity produces SQL or HQL injection, arbitrary database queries, or unauthorized viewing or modification of data. Reliable implementation requires administrative-session context, affected API requests, database query and access evidence, authorization context, and incident-response findings.
· CVE-2026-76448 — Cisco ISE / ISE-PIC authenticated SQL or HQL injection — Covered with adaptation where authenticated Cisco ISE / ISE-PIC API activity produces SQL or HQL injection, arbitrary database queries, or unauthorized viewing or modification of data. Reliable implementation requires administrative-session context, affected API requests, database query and access evidence, authorization context, and incident-response findings.
· CVE-2026-76447 — Cisco ISE / ISE-PIC authentication-boundary weakness affecting data, certificates, or keys — Covered with adaptation where Cisco ISE / ISE-PIC authentication-boundary weakness permits a remote attacker to access or manipulate data, obtain sensitive information, or affect certificate and key material under the documented advisory conditions. Reliable implementation requires affected endpoint and service context, request telemetry, authentication state, data or certificate activity, configuration history, and incident-response findings.
· CVE-2026-76446 — Cisco ISE / ISE-PIC authentication-boundary weakness affecting data, certificates, or keys — Covered with adaptation where Cisco ISE / ISE-PIC authentication-boundary weakness permits a remote attacker to access or manipulate data, obtain sensitive information, or affect certificate and key material under the documented advisory conditions. Reliable implementation requires affected endpoint and service context, request telemetry, authentication state, data or certificate activity, configuration history, and incident-response findings.
· CVE-2026-76444 — Cisco ISE / ISE-PIC authentication-boundary weakness affecting data, certificates, or keys — Covered with adaptation where Cisco ISE / ISE-PIC authentication-boundary weakness permits a remote attacker to access or manipulate data, obtain sensitive information, or affect certificate and key material under the documented advisory conditions. Reliable implementation requires affected endpoint and service context, request telemetry, authentication state, data or certificate activity, configuration history, and incident-response findings.
· CVE-2026-76443 — Cisco Secure Email Gateway / Secure Email and Web Manager improper-neutralization vulnerability — Covered with adaptation where Cisco Secure Email Gateway or Cisco Secure Email and Web Manager input-handling behavior within the CWE-707 improper-neutralization class produces command, SQL, code or evaluation injection, cross-site scripting, unexpected process or database activity, configuration effects, administrative effects, or appliance impact. Reliable implementation depends on affected product and release inventory, relevant appliance or management-interface context, authentication or exposure preconditions for the specific underlying issue where supported, application and service telemetry, database evidence where applicable, process and filesystem activity, configuration state, and incident-response findings. This grouped hardening identifier is not currently validated as CISA KEV-listed or as confirmed in-the-wild exploitation.
· CVE-2026-76442 — Cisco Secure Email Gateway / Secure Email and Web Manager improper validation of a specified quantity — Covered with adaptation where Cisco Secure Email Gateway or Cisco Secure Email and Web Manager accepts an unbounded or improperly validated numeric quantity and produces abnormal resource consumption, memory or process pressure, service degradation, restart, or availability impact. Reliable implementation depends on affected product and release inventory, relevant appliance or management-interface context, authentication or exposure preconditions for the specific underlying issue where supported, resource and process telemetry, service-health evidence, configuration state, and incident-response findings. This grouped hardening identifier is not currently validated as CISA KEV-listed or as confirmed in-the-wild exploitation.
· CVE-2026-76441 — Cisco Secure Email Gateway / Secure Email and Web Manager improper access control — Covered with adaptation where Cisco Secure Email Gateway or Cisco Secure Email and Web Manager improper access control permits activity inconsistent with expected authentication, authorization, privilege, or protected-function boundaries and produces unauthorized access, administrative-state change, configuration effects, data access, process activity, or appliance impact. Reliable implementation depends on affected product and release inventory, relevant interface exposure, identity, session, authentication and authorization evidence, administrator and role state, configuration records, downstream effects, and incident-response findings. This grouped hardening identifier is not currently validated as CISA KEV-listed or as confirmed in-the-wild exploitation.
· CVE-2026-76440 — Cisco Secure Email Gateway / Secure Email and Web Manager path traversal or improper link-resolution behavior — Covered with adaptation where Cisco Secure Email Gateway or Cisco Secure Email and Web Manager path handling permits traversal beyond an intended directory boundary or improper link resolution before file access, resulting in unexpected file access, file modification, filesystem effects, configuration exposure, process effects, or appliance impact. Reliable implementation depends on affected product and release inventory, relevant interface and request context, filesystem path and link-resolution evidence, file-access telemetry, configuration state, process activity, administrator context, and incident-response findings. This grouped hardening identifier is not currently validated as CISA KEV-listed or as confirmed in-the-wild exploitation.
· CVE-2026-76439 — Cisco ISE / ISE-PIC authentication-boundary weakness — Covered with adaptation where Cisco ISE / ISE-PIC authentication-boundary weakness permits a remote attacker to access or manipulate data, obtain sensitive information, or affect certificate and key material under the documented advisory conditions. Reliable implementation requires affected endpoint and service context, request telemetry, authentication state, data or certificate activity, configuration history, and incident-response findings.
· CVE-2026-76438 — Cisco BroadWorks CommPilot authorization bypass — Covered with adaptation where a low-privilege authenticated Cisco BroadWorks CommPilot user sends a crafted HTTP request and alters configuration on pages outside the intended authorization boundary. Reliable implementation requires authenticated-user and role context, web-management request evidence, authorization state, configuration-change history, and incident-response findings.
· CVE-2026-76437 — Cisco License On-Prem vulnerability — Covered with adaptation where affected License On-Prem management activity produces unauthorized authentication or authorization behavior, credential misuse, privileged administrative activity, code or command execution, file or database modification, service disruption, or other control-plane effects. Reliable implementation depends on License On-Prem version inventory, management-interface and API exposure, identity and administrator context, request and application telemetry, process, filesystem, database, configuration, remediation, and incident-response evidence.
· CVE-2026-76434 — Cisco ISE / ISE-PIC path traversal — Covered with adaptation where Cisco ISE / ISE-PIC path handling permits traversal outside the intended filesystem boundary, producing unauthorized file access, file modification, or related management-plane effects under the documented conditions. Reliable implementation requires affected interface and request context, path and filesystem telemetry, file-access evidence, authentication state where applicable, and incident-response findings.
· CVE-2026-76433 — Cisco ISE / ISE-PIC path traversal — Covered with adaptation where Cisco ISE / ISE-PIC path handling permits traversal outside the intended filesystem boundary, producing unauthorized file access, file modification, or related management-plane effects under the documented conditions. Reliable implementation requires affected interface and request context, path and filesystem telemetry, file-access evidence, authentication state where applicable, and incident-response findings.
· CVE-2026-76432 — Cisco ISE / ISE-PIC path traversal — Covered with adaptation where Cisco ISE / ISE-PIC path handling permits traversal outside the intended filesystem boundary, producing unauthorized file access, file modification, or related management-plane effects under the documented conditions. Reliable implementation requires affected interface and request context, path and filesystem telemetry, file-access evidence, authentication state where applicable, and incident-response findings.
· CVE-2026-76431 — Cisco ISE / ISE-PIC path traversal — Covered with adaptation where Cisco ISE / ISE-PIC path handling permits traversal outside the intended filesystem boundary, producing unauthorized file access, file modification, or related management-plane effects under the documented conditions. Reliable implementation requires affected interface and request context, path and filesystem telemetry, file-access evidence, authentication state where applicable, and incident-response findings.
· CVE-2026-76428 — Cisco ISE / ISE-PIC Profiler REST API SQL injection — Covered with adaptation where authenticated Cisco ISE / ISE-PIC profiler REST API activity produces SQL injection against the session database and unauthorized session-data access. Reliable implementation requires administrative-session context, REST API requests, session-database activity, data-access evidence, and incident-response findings.
· CVE-2026-76427 — Cisco ISE offline-profiler XML external entity injection — Covered with adaptation where authenticated Cisco ISE offline-profiler feed processing permits XML external entity injection, arbitrary local-file reads, or requests to internal systems from the affected device. Reliable implementation requires administrative-session context, offline feed uploads, XML-processing evidence, filesystem access, internal network requests, and incident-response findings.
· CVE-2026-76426 — Cisco ISE / ISE-PIC REST API SQL injection — Covered with adaptation where authenticated Cisco ISE / ISE-PIC REST API activity produces SQL injection against the monitoring database and unauthorized monitoring-data access. Reliable implementation requires administrative-session context, REST API request evidence, monitoring-database activity, data-access records, and incident-response findings.
· CVE-2026-76425 — Cisco ISE authenticated API SQL injection and server-side request forgery — Covered with adaptation where authenticated Cisco ISE API activity produces SQL injection against the backend database, unauthorized database reads, or server-side request forgery. Reliable implementation requires administrative-session context, affected API requests, database query and access evidence, server-side destination activity, configuration state, and incident-response findings.
· CVE-2026-76424 — Cisco ISE authenticated API arbitrary file upload or copy leading to root command execution — Covered with adaptation where authenticated Cisco ISE REST API file operations permit arbitrary file upload or copy to attacker-controlled paths and consequential command execution as root. Reliable implementation requires administrative-session context, REST API and file-operation telemetry, filesystem writes, process lineage, root-context execution, configuration state, and incident-response findings.
· CVE-2026-76423 — Cisco ISE / ISE-PIC unauthenticated REST API authorization bypass — Covered with adaptation where unauthenticated Cisco ISE / ISE-PIC REST API activity bypasses authorization checks and produces administrative access to configuration or identity data. Reliable implementation requires REST API exposure, request context, authentication and authorization evidence, configuration and identity-data access, administrator-state changes, and incident-response findings.
· CVE-2026-76420 — Cisco Secure Firewall Management Center management or trust-boundary vulnerability associated with root access, session forgery, or session impersonation — Covered with adaptation where Cisco Secure FMC management or trust-boundary behavior permits root access, session forgery, or session impersonation under the documented conditions. Reliable implementation requires affected service and interface context, authentication and session evidence, peer or trust state where applicable, process and root-context activity, administrator-state changes, and incident-response findings.
· CVE-2026-76413 — Cisco Secure Firewall Management Center management or trust-boundary vulnerability associated with root access, session forgery, or session impersonation — Covered with adaptation where Cisco Secure FMC management or trust-boundary behavior permits root access, session forgery, or session impersonation under the documented conditions. Reliable implementation requires affected service and interface context, authentication and session evidence, peer or trust state where applicable, process and root-context activity, administrator-state changes, and incident-response findings.
· CVE-2026-76412 — Cisco Secure Firewall Management Center management or trust-boundary vulnerability associated with root access, session forgery, or session impersonation — Covered with adaptation where Cisco Secure FMC management or trust-boundary behavior permits root access, session forgery, or session impersonation under the documented conditions. Reliable implementation requires affected service and interface context, authentication and session evidence, peer or trust state where applicable, process and root-context activity, administrator-state changes, and incident-response findings.
· CVE-2026-76409 — Cisco Nexus Dashboard September 2026 hardening identifier — Covered with adaptation as a Cisco Nexus Dashboard September 2026 hardening identifier where product-specific behavior within Cisco's grouped CWE classes produces sensitive-information exposure, path traversal, improper access control, missing authentication, command injection, or SQL injection effects. Reliable implementation requires Nexus Dashboard asset and version inventory, affected application or service context, authentication and authorization evidence, request and database or filesystem telemetry where applicable, process activity, configuration state, and incident-response findings. Cisco states that these vulnerabilities are not known to be actively exploited.
· CVE-2026-75754 — ASUS Control Center Enterprise unauthenticated encryption-key disclosure and hard-coded credential root access — Covered with adaptation where unauthorized ASUS Control Center Enterprise access results in encryption-key retrieval, local service-driven SSH enablement on TCP port 2222, hard-coded credential use, root-shell or equivalent privileged access, ACC data access or modification, or remote control of managed servers, PCs, or workstations.
· CVE-2026-75600 — FreePBX authenticated GraphQL API generatedocs host-command injection — Covered with adaptation where an authenticated FreePBX user authorized for the GraphQL API interface supplies attacker-controlled host input to the generatedocs path and causes shell-command execution in the FreePBX service context, including Asterisk-context process activity, configuration changes, file activity, outbound communication, or downstream telephony effects. Reliable implementation depends on FreePBX asset and API-module version inventory, authenticated identity and authorization state, GraphQL and generatedocs request activity, submitted host values where available, web-server and Asterisk process telemetry, child-process execution, command activity, configuration state, network behavior, remediation state, and incident-response findings. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation.
· CVE-2026-72530 — TrueConf Server code injection or sandbox escape — Covered with adaptation where TrueConf Server code-injection or sandbox-escape behavior produces arbitrary code execution, privileged server activity, filesystem modification, web-shell-like artifact placement, privileged database access, outbound communication, or trusted client-installer modification. Active exploitation and CISA KEV status increase remediation and retrospective-hunting urgency but do not change the Coverage With Adaptation classification.
· CVE-2026-72529 — TrueConf Server unauthorized critical-function access and arbitrary script execution — Covered with adaptation where unauthorized TrueConf Server access to critical functionality, arbitrary script execution, abnormal application or server activity, privilege escalation, filesystem modification, database access, administrative-state change, outbound communication, or downstream client-distribution effects can be mapped into the report's authentication-bypass, protected-functionality, and application-host behavior model.
· CVE-2026-70416 — Dell ObjectScale unauthenticated deserialization of untrusted data leading to remote code execution — Covered with adaptation where unauthenticated remote input reaches an affected Dell ObjectScale deserialization path and results in deserialization of untrusted data, remote code execution, abnormal service or process activity, filesystem or configuration changes, outbound communication, or consequential storage-management and control-plane effects. Reliable implementation depends on Dell ObjectScale asset and version inventory, management and service exposure, request and application telemetry, serialization or deserialization evidence where available, service and process activity, filesystem and configuration state, network behavior, storage-management activity, and incident-response findings. Dell Security Advisory DSA-2026-393 identifies ObjectScale versions prior to 4.4.0.0 as affected and 4.4.0.0 or later as the remediation boundary.
· CVE-2026-67281 — MikroTik RouterOS WebFig unauthenticated file read — Covered with adaptation where MikroTik RouterOS WebFig unauthenticated file-read behavior produces abnormal WebFig access, traversal-like file requests, unauthorized root-owned file access, configuration-store disclosure, credential exposure, or related management-plane effects.
· CVE-2026-67279 — MikroTik RouterOS unauthenticated SSH connection-protocol file access — Covered with adaptation where MikroTik RouterOS unauthenticated SSH connection-protocol behavior produces unauthorized session-channel activity, exec requests, managed-file creation or overwrite, configuration or diagnostic-file access, or related management-plane effects. CISA added CVE-2026-67279 to the Known Exploited Vulnerabilities Catalog on September 25, 2026 based on evidence of active exploitation. The KEV addition increases remediation and retrospective compromise-assessment urgency but does not change the Coverage With Adaptation classification.
· CVE-2026-67278 — MikroTik RouterOS X.509 validation weakness — Covered with adaptation where MikroTik RouterOS X.509 validation weakness produces abnormal certificate trust, redirected or intercepted outbound TLS activity, unexpected trusted destinations, or related network effects.
· CVE-2026-67277 — MikroTik RouterOS unauthenticated bandwidth-test memory disclosure or restart behavior — Covered with adaptation where MikroTik RouterOS bandwidth-test behavior produces unauthenticated service-state progression, kernel-memory disclosure indicators, anomalous packet behavior, service instability, kernel restart, or downstream network impact. CISA added CVE-2026-67277 to the Known Exploited Vulnerabilities Catalog on September 10, 2026.
· CVE-2026-67276 — MikroTik RouterOS SSH public-key authentication bypass — Covered with adaptation where MikroTik RouterOS SSH public-key authentication bypass produces unauthorized account access, abnormal SSH sessions, privileged device activity, administrator or configuration changes, command execution, tunnel or proxy creation, or downstream network-control effects. CERT Polska confirms this vulnerability is used with CVE-2026-86060 in the actively exploited MikroTrick chain. CVE-2026-67276 is not represented as CISA KEV-listed based on the September 10, 2026 CISA update.
· CVE-2026-61682 — kcp front-proxy identity-header trust failure and multi-tenant authorization bypass — Covered with adaptation where an authenticated kcp tenant supplies X-Remote-Group or X-Remote-Extra-* identity headers to an affected front proxy, the headers are forwarded to shards without being removed, and forged delegated identity or scope data produces system authority, cross-workspace authorization bypass, or unauthorized read, write, or delete access to secrets, RBAC objects, APIExports, APIBindings, LogicalClusters, or other tenant resources. Reliable implementation depends on kcp version inventory, front-proxy and shard topology, authenticated tenant and credential context, raw inbound and forwarded request-header visibility where available, workspace and RBAC state, delegated-identity and scope data, secret and object access, configuration changes, and downstream activity. Versions earlier than 0.31.4 and 0.32.0 through 0.32.1 are affected; 0.31.4 and 0.32.2 are fixed. Stripping all inbound X-Remote-* headers at an external proxy reduces exposure but is an interim mitigation rather than complete remediation. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status.
· CVE-2026-59358 — Cloud Foundry UAA OAuth token-endpoint user-access-token reuse in the client_credentials grant path — Covered with adaptation where a valid user access token associated with an OAuth client supporting the documented public user-facing authorization flow and client_credentials grant configuration is accepted as client authentication and results in issuance of a client-only token carrying configured client authorities. Reliable implementation depends on UAA and cf-deployment version inventory, OAuth-client configuration, enabled grant types, client authorities, user and client token issuance, token-endpoint activity, administrative scopes, downstream platform access, remediation status, and incident-response findings. UAA v3.7.0 through v79.6.0 and cf-deployment through v60.4.0 are affected under the documented conditions; UAA v79.7.0 or later and cf-deployment v60.5.0 or later provide the documented remediation boundaries. Available authoritative evidence reviewed for this amendment does not establish CISA KEV status.
· CVE-2026-59357 — Cloud Foundry UAA self-UAA OIDC trust failure permitting unauthorized authenticated session establishment — Covered with adaptation where the documented self-UAA OIDC configuration permits qualifying attacker-controlled token material to be accepted during the external OIDC login flow and results in unauthorized authenticated browser-session establishment, unexpected shadow-account or group mapping, anomalous identity-provider activity, administrative-scope access, or consequential downstream platform activity. Reliable implementation depends on UAA version inventory, self-UAA OIDC and identity-provider configuration, external-OIDC callback activity, browser-session state, user identity, shadow-account and group-membership mappings, administrative scopes, downstream access, remediation status, and incident-response findings. UAA v4.5.0 through v79.6.0 is affected under the documented self-UAA OIDC condition; UAA v79.7.0 or later provides the documented remediation boundary. Available authoritative evidence reviewed for this amendment does not establish CISA KEV status.
· CVE-2026-57155 — OPNsense GeoIP alias-import path traversal and arbitrary root file write — Covered with adaptation where OPNsense firewall-management telemetry, GeoIP alias-import activity, alias-permission usage, external archive retrieval, traversal-like path behavior, arbitrary root file-write evidence, root-owned file changes, cron or service-triggered execution, administrator changes, firewall policy changes, routing changes, VPN changes, DNS changes, outbound communication, or downstream infrastructure impact can be mapped into the same management-plane-to-root-control behavior model.
· CVE-2026-33000 — UniFi OS Server command-injection or update/package-execution vulnerability under a different prerequisite and access context — Covered with adaptation where the same UniFi OS Server command-injection sink or comparable update or package-execution behavior is monitored, but preconditions and access context differ from the unauthenticated chain.
· CVE-2026-28326 — SolarWinds Access Rights Manager unauthenticated remote code execution — Covered with adaptation where unauthenticated activity against SolarWinds Access Rights Manager reaches the affected management and identity-control-plane path and produces remote code execution, abnormal service or process behavior, administrative-state or configuration changes, credential or access-rights effects, outbound communication, or downstream identity and authorization impact. Reliable implementation depends on SolarWinds Access Rights Manager asset and version inventory, management-interface and service exposure, request and authentication telemetry, service and process activity, administrator and access-rights state, configuration records, network behavior, and incident-response findings. The SolarWinds-assigned CVE record identifies Access Rights Manager 2026.2 and earlier affected versions and recommends upgrading to Access Rights Manager 2026.2.1.
· CVE-2026-28325 — SolarWinds Observability Self-Hosted unauthenticated deserialization of untrusted data leading to remote code execution — Covered with adaptation where unauthenticated activity against SolarWinds Observability Self-Hosted reaches the affected communication path and deserialization of untrusted data produces remote code execution, abnormal SolarWinds service or process behavior, filesystem or configuration changes, outbound communication, persistence, or downstream management-plane effects. Reliable implementation depends on SolarWinds Observability Self-Hosted / SolarWinds Platform asset and version inventory, confirmation that the affected communication mode is configured, interface and service exposure, request or message and application telemetry where available, deserialization and process evidence, filesystem and configuration state, administrator activity, network behavior, remediation state, and incident-response findings. SolarWinds identifies SolarWinds Platform 2026.2.3 as the corrected release. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status.
· CVE-2026-28324 — SolarWinds Observability Self-Hosted unauthenticated remote code execution through insufficient integrity checks under a non-default and non-secure configuration — Covered with adaptation where unauthenticated activity against an affected SolarWinds Observability Self-Hosted deployment operating in the documented non-default and non-secure configuration reaches the insufficient-integrity-check path and produces remote code execution, abnormal SolarWinds service or process behavior, filesystem or configuration changes, outbound communication, persistence, or downstream management-plane effects. Reliable implementation depends on SolarWinds Observability Self-Hosted / SolarWinds Platform asset and version inventory, confirmation of the documented non-default and non-secure configuration prerequisite, interface and service exposure, integrity-validation context where available, process and filesystem telemetry, configuration and administrator state, network behavior, remediation state, and incident-response findings. SolarWinds identifies SolarWinds Platform 2026.2.3 as the corrected release. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status.
· CVE-2026-20361 — Cisco Nexus Dashboard September 2026 hardening identifier — Covered with adaptation as a Cisco Nexus Dashboard September 2026 hardening identifier where product-specific behavior within Cisco's grouped CWE classes produces sensitive-information exposure, path traversal, improper access control, missing authentication, command injection, or SQL injection effects. Reliable implementation requires Nexus Dashboard asset and version inventory, affected application or service context, authentication and authorization evidence, request and database or filesystem telemetry where applicable, process activity, configuration state, and incident-response findings. Cisco states that these vulnerabilities are not known to be actively exploited.
· CVE-2026-20360 — Cisco Nexus Dashboard September 2026 hardening identifier — Covered with adaptation as a Cisco Nexus Dashboard September 2026 hardening identifier where product-specific behavior within Cisco's grouped CWE classes produces sensitive-information exposure, path traversal, improper access control, missing authentication, command injection, or SQL injection effects. Reliable implementation requires Nexus Dashboard asset and version inventory, affected application or service context, authentication and authorization evidence, request and database or filesystem telemetry where applicable, process activity, configuration state, and incident-response findings. Cisco states that these vulnerabilities are not known to be actively exploited.
· CVE-2026-20362 — Cisco Finesse server-side request forgery — Covered with adaptation where unauthenticated requests to the affected Finesse web-based management interface cause the device to issue attacker-influenced server-side requests, reach internal or otherwise inaccessible services, or expose limited sensitive information. Reliable implementation depends on Finesse asset and version inventory, management-interface exposure, HTTP request telemetry, destination and response context, reachable-service inventory, application and system logging, remediation status, and incident-response findings.
· CVE-2026-20359 — Cisco Crosswork insufficiently protected credentials and privileged-object exposure — Covered with adaptation where Cisco Crosswork insufficiently protected credential behavior, privileged-object exposure, abnormal credential access or use, administrator-state anomalies, configuration changes, or downstream network-control effects can be mapped into the report's management-plane and privileged-object model.
· CVE-2026-20358 — Cisco Crosswork externally controlled filesystem-path vulnerability — Covered with adaptation where Cisco Crosswork external filesystem-control behavior, suspicious file-path activity, unauthorized file access or modification, service-context activity, configuration changes, or downstream network-control effects can be mapped into the report's management-plane and filesystem-control model.
· CVE-2026-20357 — Cisco Crosswork missing authentication for critical functionality — Covered with adaptation where Cisco Crosswork critical functionality is reachable without expected authentication, abnormal management sessions occur, unauthorized administrative activity is observed, or configuration and downstream network-control effects can be mapped into the report's authentication-bypass and management-plane model.
· CVE-2026-20353 — Cisco Secure Email Gateway / Secure Email and Web Manager resource-lifetime vulnerability — Covered with adaptation where Cisco Secure Email Gateway or Cisco Secure Email and Web Manager resource-lifetime behavior within the CWE-664 grouping produces uncontrolled resource consumption, algorithmic complexity, recursion or iteration effects, unsafe deserialization, improper resource initialization, service instability, process effects, or appliance availability impact. Reliable implementation depends on affected product and release inventory, relevant appliance or management-interface context, authentication or exposure preconditions for the specific underlying issue where supported, deserialization or initialization evidence where available, process, memory and resource telemetry, service-health records, configuration state, and incident-response findings. This grouped hardening identifier is not currently validated as CISA KEV-listed or as confirmed in-the-wild exploitation.
· CVE-2026-20352 — Cisco ISE crafted RADIUS request denial of service — Covered with adaptation where unauthenticated crafted RADIUS requests to an affected Cisco ISE Policy Service Node cause node unavailability and disrupt authentication for endpoints that have not already authenticated. Reliable implementation requires PSN and Session Services state, RADIUS exposure, request and service-health telemetry, node restart or recovery evidence, authentication failures, and incident-response findings.
· CVE-2026-20350 — Cisco ThousandEyes Virtual Appliance authenticated web-interface command injection — Covered with adaptation where an authenticated Cisco ThousandEyes Virtual Appliance administrator saves malicious web-interface configuration values that produce arbitrary operating-system command execution with root privileges. Reliable implementation requires affected-version inventory, administrator-session context, web-interface configuration activity, submitted parameter evidence where available, process and root-context telemetry, filesystem and configuration state, and incident-response findings.
· CVE-2026-20344 — Cisco Secure Firewall Management Center September 2026 multi-vulnerability advisory entry — Covered with adaptation where Cisco Secure FMC management or service behavior within the September 2026 multi-vulnerability advisory produces root access, sensitive-file download, SQL injection, or denial-of-service effects under the documented conditions. Reliable implementation requires affected-product and version inventory, relevant interface or service context, authentication state, request and database or filesystem evidence where applicable, process and root-context telemetry, service-health records, and incident-response findings.
· CVE-2026-20343 — Cisco Secure Firewall Management Center September 2026 multi-vulnerability advisory entry — Covered with adaptation where Cisco Secure FMC management or service behavior within the September 2026 multi-vulnerability advisory produces root access, sensitive-file download, SQL injection, or denial-of-service effects under the documented conditions. Reliable implementation requires affected-product and version inventory, relevant interface or service context, authentication state, request and database or filesystem evidence where applicable, process and root-context telemetry, service-health records, and incident-response findings.
· CVE-2026-20342 — Cisco Secure Firewall Management Center September 2026 multi-vulnerability advisory entry — Covered with adaptation where Cisco Secure FMC management or service behavior within the September 2026 multi-vulnerability advisory produces root access, sensitive-file download, SQL injection, or denial-of-service effects under the documented conditions. Reliable implementation requires affected-product and version inventory, relevant interface or service context, authentication state, request and database or filesystem evidence where applicable, process and root-context telemetry, service-health records, and incident-response findings.
· CVE-2026-20341 — Cisco Secure Firewall Management Center September 2026 multi-vulnerability advisory entry — Covered with adaptation where Cisco Secure FMC management or service behavior within the September 2026 multi-vulnerability advisory produces root access, sensitive-file download, SQL injection, or denial-of-service effects under the documented conditions. Reliable implementation requires affected-product and version inventory, relevant interface or service context, authentication state, request and database or filesystem evidence where applicable, process and root-context telemetry, service-health records, and incident-response findings.
· CVE-2026-20340 — Cisco Secure Firewall Management Center September 2026 multi-vulnerability advisory entry — Covered with adaptation where Cisco Secure FMC management or service behavior within the September 2026 multi-vulnerability advisory produces root access, sensitive-file download, SQL injection, or denial-of-service effects under the documented conditions. Reliable implementation requires affected-product and version inventory, relevant interface or service context, authentication state, request and database or filesystem evidence where applicable, process and root-context telemetry, service-health records, and incident-response findings.
· CVE-2026-20328 — Cisco License On-Prem vulnerability — Covered with adaptation where affected License On-Prem management behavior results in unauthorized administrative access, code or command execution, SQL or database manipulation, arbitrary file activity, credential or password-management effects, service disruption, or consequential control-plane activity. Reliable implementation depends on affected version and service context, authentication and administrator state, management-interface and API telemetry, process, filesystem, database, configuration, remediation, and incident-response evidence.
· CVE-2026-20327 — Cisco Unified Intelligence Center authenticated blind SQL injection and unauthorized internal-database read access — Covered with adaptation where authenticated Cisco Unified Intelligence Center web-management activity, crafted requests, abnormal database interaction, unauthorized internal-database reads, management-data access, or associated application and configuration effects can be mapped into the report's crafted-request and management-plane model.
· CVE-2026-20326 — Cisco Nexus Dashboard September 2026 hardening identifier — Covered with adaptation as a Cisco Nexus Dashboard September 2026 hardening identifier where product-specific behavior within Cisco's grouped CWE classes produces sensitive-information exposure, path traversal, improper access control, missing authentication, command injection, or SQL injection effects. Reliable implementation requires Nexus Dashboard asset and version inventory, affected application or service context, authentication and authorization evidence, request and database or filesystem telemetry where applicable, process activity, configuration state, and incident-response findings. Cisco states that these vulnerabilities are not known to be actively exploited.
· CVE-2026-20325 — Cisco Nexus Dashboard September 2026 hardening identifier — Covered with adaptation as a Cisco Nexus Dashboard September 2026 hardening identifier where product-specific behavior within Cisco's grouped CWE classes produces sensitive-information exposure, path traversal, improper access control, missing authentication, command injection, or SQL injection effects. Reliable implementation requires Nexus Dashboard asset and version inventory, affected application or service context, authentication and authorization evidence, request and database or filesystem telemetry where applicable, process activity, configuration state, and incident-response findings. Cisco states that these vulnerabilities are not known to be actively exploited.
· CVE-2026-20324 — Cisco Secure Firewall Management Center authenticated sftunnel arbitrary file write — Covered with adaptation where an authenticated or hijacked registered Cisco Secure FMC sftunnel peer writes an arbitrary file to the device and causes that file to execute with root privileges. Reliable implementation requires sftunnel peer and registration state, connection evidence, file-write telemetry, process and root-context activity, configuration changes, and incident-response findings.
· CVE-2026-20323 — Cisco Secure Firewall Management Center / Secure FTD unauthenticated sftunnel authentication bypass or denial of service — Covered with adaptation where unauthenticated Cisco Secure FMC / Secure FTD sftunnel activity produces authentication-bypass or denial-of-service effects under the documented conditions. Reliable implementation requires sftunnel exposure, peer and certificate state, connection and authentication telemetry, resource or service-health evidence, managed-device context, and incident-response findings.
· CVE-2026-20322 — Cisco Nexus Dashboard September 2026 hardening identifier — Covered with adaptation as a Cisco Nexus Dashboard September 2026 hardening identifier where product-specific behavior within Cisco's grouped CWE classes produces sensitive-information exposure, path traversal, improper access control, missing authentication, command injection, or SQL injection effects. Reliable implementation requires Nexus Dashboard asset and version inventory, affected application or service context, authentication and authorization evidence, request and database or filesystem telemetry where applicable, process activity, configuration state, and incident-response findings. Cisco states that these vulnerabilities are not known to be actively exploited.
· CVE-2026-20321 — Cisco Application Policy Infrastructure Controller API command injection — Covered with adaptation where an authenticated APIC user supplies crafted API input that results in operating-system command execution, including root-context execution, abnormal process behavior, filesystem or configuration effects, network-control changes, or other consequential APIC activity. Reliable implementation depends on APIC asset and version inventory, authenticated identity and privilege state, API request activity, command and process telemetry, root-context evidence, configuration state, ACI fabric effects, remediation status, and incident-response findings.
· CVE-2026-20319 — Cisco Secure Workload memory-buffer operation failure — Covered with adaptation where Cisco Secure Workload memory-buffer operation failures produce abnormal service behavior, process instability, crash or memory-corruption evidence, unexpected execution, or associated network and security-control effects.
· CVE-2026-20318 — Cisco Secure Workload improper input validation and externally controlled path behavior — Covered with adaptation where Cisco Secure Workload improper input validation, traversal-like activity, externally controlled path behavior, filesystem activity, application anomalies, or configuration effects can be mapped into the report's request-path, traversal, filesystem, and application-host model.
· CVE-2026-20317 — Cisco Secure Workload missing authentication or authentication bypass — Covered with adaptation where Cisco Secure Workload missing-authentication or authentication-bypass behavior, reliance on untrusted authentication inputs, abnormal sessions, unauthorized protected-function access, or administrator-state anomalies can be mapped into the report's authentication-validation and management-plane model.
· CVE-2026-20316 — Cisco Secure Firewall Management Center static low-privileged account exposure — Covered with adaptation where unauthorized Cisco Secure FMC access through the static low-privileged account, abnormal management sessions, access to sensitive management data, configuration access, administrator-state changes, or downstream managed-firewall activity can be mapped into the report's management-plane access and network-control exposure model. CISA added CVE-2026-20316 to the Known Exploited Vulnerabilities Catalog on July 29, 2026.
· CVE-2026-20315 — Cisco Secure Workload improper access control — Covered with adaptation where Cisco Secure Workload improper access control, authorization or authentication failure, privilege misuse, protected-function bypass, role anomalies, or configuration effects can be mapped into the report's improper-access-control and privileged-object model.
· CVE-2026-20309 — Cisco ISE unauthenticated reflected cross-site scripting — Covered with adaptation where unauthenticated Cisco ISE web-management input produces reflected cross-site scripting and script execution in a user's browser context. Reliable implementation requires management-interface exposure, crafted-link or request evidence, browser and session context, subsequent application activity, and incident-response findings.
· CVE-2026-20307 — Cisco ISE low-privilege authenticated Java deserialization leading to root execution — Covered with adaptation where an authenticated low-privilege Cisco ISE user submits a crafted serialized Java object to the web-based management interface, producing arbitrary code execution and privilege elevation to root. Reliable implementation requires authenticated-session context, web-management requests, Java-deserialization evidence where available, process lineage, root-context activity, service availability, configuration changes, and incident-response findings.
· CVE-2026-20306 — Cisco ISE / ISE-PIC authenticated REST API command execution with root privilege elevation — Covered with adaptation where authenticated Cisco ISE / ISE-PIC REST API activity processes crafted command input and produces arbitrary code execution with privilege elevation to root. Reliable implementation requires administrative-session context, REST API requests, command and process telemetry, root-context activity, service availability, and incident-response findings.
· CVE-2026-20305 — Cisco ISE / ISE-PIC authenticated diagnostic-tool command execution with root privilege elevation — Covered with adaptation where authenticated Cisco ISE / ISE-PIC diagnostic-tool activity processes crafted command input and produces arbitrary code execution with privilege elevation to root. Reliable implementation requires administrative-session context, diagnostic-tool and web-management requests, command and process telemetry, root-context activity, service availability, and incident-response findings.
· CVE-2026-20300 — Cisco ISE low-privilege authenticated SQL injection — Covered with adaptation where a low-privilege Cisco ISE administrator submits crafted requests that produce SQL injection and unauthorized reading or modification of underlying database data. Reliable implementation requires administrative-session context, request telemetry, database activity, authorization context, and incident-response findings.
· CVE-2026-20295 — Cisco Secure Firewall Management Center / Secure FTD unauthenticated sftunnel authentication bypass or denial of service — Covered with adaptation where unauthenticated Cisco Secure FMC / Secure FTD sftunnel activity produces authentication-bypass or denial-of-service effects under the documented conditions. Reliable implementation requires sftunnel exposure, peer and certificate state, connection and authentication telemetry, resource or service-health evidence, managed-device context, and incident-response findings.
· CVE-2026-20287 — Cisco ISE / ISE-PIC September 2026 hardening identifier — Covered with adaptation as a Cisco ISE / ISE-PIC September 2026 hardening identifier where product-specific behavior within Cisco's grouped weakness classes produces unauthorized access, privilege or authorization effects, input-processing abuse, credential or secret exposure, resource-management effects, or other management-control-plane impact. Reliable implementation requires affected-product and version inventory, applicable interface or service context, authentication and authorization evidence, administrator and role state, process and resource telemetry, configuration history, and incident-response findings. Cisco states that these hardening issues were found during internal security review and are not known to be actively exploited.
· CVE-2026-20286 — Cisco ISE / ISE-PIC low-privilege authorization bypass and configuration modification — Covered with adaptation where an authenticated low-privilege Cisco ISE / ISE-PIC user bypasses server-side administrator-permission checks through crafted HTTP requests and modifies configuration outside the intended authorization boundary. Reliable implementation requires authenticated-session context, role and permission state, HTTP request evidence, configuration-change history, and incident-response findings.
· CVE-2026-20285 — Cisco ISE / ISE-PIC low-privilege authorization bypass and configuration modification — Covered with adaptation where an authenticated low-privilege Cisco ISE / ISE-PIC user bypasses server-side administrator-permission checks through crafted HTTP requests and modifies configuration outside the intended authorization boundary. Reliable implementation requires authenticated-session context, role and permission state, HTTP request evidence, configuration-change history, and incident-response findings.
· CVE-2026-20284 — Cisco ISE authenticated SXP REST API SQL injection and service impact — Covered with adaptation where an authenticated Cisco ISE administrator abuses the SXP REST API on a deployment with SXP enabled and an active SXP connection to conduct SQL injection, view or modify database data, or cause service unavailability. Reliable implementation requires SXP state, administrative-session context, REST API request evidence, database activity, service-health telemetry, and incident-response findings.
· CVE-2026-20283 — Cisco ISE authenticated IPsec Open API operating-system command injection — Covered with adaptation where an authenticated Cisco ISE administrator abuses the IPsec Open API on a node with the documented active IPsec-tunnel condition to inject arbitrary operating-system commands. Reliable implementation requires IPsec VTI and interface state, administrative-session context, Open API requests, command and process telemetry, privilege state, and incident-response findings.
· CVE-2026-20282 — Cisco ISE authenticated operating-system write access — Covered with adaptation where an authenticated Cisco ISE administrator submits crafted HTTP input and obtains unauthorized write access to the underlying operating system, creating a path to consequential privileged activity. Reliable implementation requires administrative-session context, HTTP request evidence, filesystem writes, process activity, privilege state, and incident-response findings.
· CVE-2026-20280 — Cisco IOS XR exceptional-condition-handling weakness — Covered with adaptation where an affected Cisco IOS XR exceptional-condition-handling weakness produces abnormal process or service behavior, fault conditions, crash or reload activity, configuration effects, or downstream network-control effects.
· CVE-2026-20279 — Cisco IOS XR access-control weakness — Covered with adaptation where an affected Cisco IOS XR access-control weakness produces certificate-validation anomalies, missing or incorrect authentication or authorization, unauthorized protected-function access, abnormal privileged activity, configuration effects, or downstream network-control effects.
· CVE-2026-20278 — Cisco IOS XR improper-neutralization weakness — Covered with adaptation where an affected Cisco IOS XR improper-neutralization weakness produces suspicious command or input handling, unexpected execution, process activity, configuration changes, service anomalies, or downstream network-control effects.
· CVE-2026-20277 — Cisco IOS XR protection-mechanism weakness — Covered with adaptation where an affected Cisco IOS XR protection-mechanism weakness produces abnormal security-mechanism, authentication, session, protocol, process, or configuration behavior.
· CVE-2026-20276 — Cisco IOS XR control-flow weakness — Covered with adaptation where an affected Cisco IOS XR control-flow weakness produces reachable-assertion behavior, non-terminating processing, process instability, resource consumption, service disruption, crash or reload activity, route or protocol effects, or downstream network-control impact.
· CVE-2026-20275 — Cisco IOS XR calculation weakness — Covered with adaptation where an affected Cisco IOS XR calculation weakness produces abnormal memory, process, input-processing, service-instability, crash, reload, or downstream network-state behavior.
· CVE-2026-20274 — Cisco IOS XR resource-lifetime weakness — Covered with adaptation where an affected Cisco IOS XR resource-lifetime weakness produces memory-safety, resource-management, process-instability, crash, reload, unexpected execution, route or protocol disruption, or downstream network-control effects.
· CVE-2026-20272 — Cisco IOS XE service vulnerability — Covered with adaptation where activity associated with an affected Cisco IOS XE service produces suspicious management-plane access, command or argument-processing behavior, privileged device activity, administrator-state anomalies, configuration changes, outbound communication, or downstream routing, switching, segmentation, VPN, or network-control impact.
· CVE-2026-20247 — Cisco ISE unauthenticated SQL injection — Covered with adaptation where unauthenticated Cisco ISE requests produce SQL injection and unauthorized modification of data in the underlying database. Reliable implementation requires affected-product and version context, crafted request evidence, database queries and changes, application telemetry, and incident-response findings.
· CVE-2026-20242 — Cisco Secure Firewall Management Center External Database Access Java deserialization leading to root execution — Covered with adaptation where a host permitted by Cisco Secure FMC External Database Access sends a crafted serialized Java byte stream to the affected service and produces arbitrary command execution with privilege elevation to root. Reliable implementation requires external-database access-list state, source-host context, TCP service exposure, deserialization and process telemetry, root-context activity, and incident-response findings.
· CVE-2026-20237 — Cisco ISE / ISE-PIC September 2026 hardening identifier — Covered with adaptation as a Cisco ISE / ISE-PIC September 2026 hardening identifier where product-specific behavior within Cisco's grouped weakness classes produces unauthorized access, privilege or authorization effects, input-processing abuse, credential or secret exposure, resource-management effects, or other management-control-plane impact. Reliable implementation requires affected-product and version inventory, applicable interface or service context, authentication and authorization evidence, administrator and role state, process and resource telemetry, configuration history, and incident-response findings. Cisco states that these hardening issues were found during internal security review and are not known to be actively exploited.
· CVE-2026-20235 — Cisco ISE authenticated API sensitive-information disclosure — Covered with adaptation where authenticated Cisco ISE API activity uses crafted parameters to obtain sensitive information from the affected device. Reliable implementation requires administrative-session context, API request evidence, database or data-access telemetry, authorization state, and incident-response findings.
· CVE-2026-20234 — Cisco ISE / ISE-PIC September 2026 hardening identifier — Covered with adaptation as a Cisco ISE / ISE-PIC September 2026 hardening identifier where product-specific behavior within Cisco's grouped weakness classes produces unauthorized access, privilege or authorization effects, input-processing abuse, credential or secret exposure, resource-management effects, or other management-control-plane impact. Reliable implementation requires affected-product and version inventory, applicable interface or service context, authentication and authorization evidence, administrator and role state, process and resource telemetry, configuration history, and incident-response findings. Cisco states that these hardening issues were found during internal security review and are not known to be actively exploited.
· CVE-2026-20231 — Cisco Secure Workload command or argument injection — Covered with adaptation where Cisco Secure Workload command, operating-system command, or argument-injection behavior produces suspicious request or service activity, process execution, privileged execution, configuration changes, outbound communication, or downstream security-control effects.
· CVE-2026-20212 — Cisco Nexus 9000 Silicon One root-context execution path — Covered with adaptation where traffic to TCP ports 43210 or 43211 on an affected Cisco Nexus 9000 Silicon One device, crafted-input activity, root-context execution, S1HAL instability, unexpected device reload, administrator anomalies, configuration change, outbound communication, or downstream routing, switching, segmentation, or network-control impact can be mapped into the report's control-plane-to-root-execution behavior model.
· CVE-2026-20211 — Cisco ISE high-privilege authenticated Java deserialization leading to root execution — Covered with adaptation where a high-privilege Cisco ISE administrator submits crafted serialized Java objects that produce arbitrary operating-system execution and privilege elevation to root. Reliable implementation requires administrative-session context, deserialization and request evidence, process lineage, root-context activity, service availability, and incident-response findings.
· CVE-2026-20194 — Cisco ISE / ISE-PIC September 2026 hardening identifier — Covered with adaptation as a Cisco ISE / ISE-PIC September 2026 hardening identifier where product-specific behavior within Cisco's grouped weakness classes produces unauthorized access, privilege or authorization effects, input-processing abuse, credential or secret exposure, resource-management effects, or other management-control-plane impact. Reliable implementation requires affected-product and version inventory, applicable interface or service context, authentication and authorization evidence, administrator and role state, process and resource telemetry, configuration history, and incident-response findings. Cisco states that these hardening issues were found during internal security review and are not known to be actively exploited.
· CVE-2026-20192 — Cisco ISE / ISE-PIC September 2026 hardening identifier — Covered with adaptation as a Cisco ISE / ISE-PIC September 2026 hardening identifier where product-specific behavior within Cisco's grouped weakness classes produces unauthorized access, privilege or authorization effects, input-processing abuse, credential or secret exposure, resource-management effects, or other management-control-plane impact. Reliable implementation requires affected-product and version inventory, applicable interface or service context, authentication and authorization evidence, administrator and role state, process and resource telemetry, configuration history, and incident-response findings. Cisco states that these hardening issues were found during internal security review and are not known to be actively exploited.
· CVE-2026-20176 — Cisco ISE high-privilege authenticated operating-system command execution — Covered with adaptation where a high-privilege Cisco ISE administrator submits crafted HTTP input that produces operating-system command execution, system-level access, and privilege elevation to root. Reliable implementation requires administrative-session context, HTTP request evidence, process and root-context activity, service availability, configuration state, and incident-response findings.
· CVE-2026-20130 — Cisco ISE / ISE-PIC September 2026 hardening identifier — Covered with adaptation as a Cisco ISE / ISE-PIC September 2026 hardening identifier where product-specific behavior within Cisco's grouped weakness classes produces unauthorized access, privilege or authorization effects, input-processing abuse, credential or secret exposure, resource-management effects, or other management-control-plane impact. Reliable implementation requires affected-product and version inventory, applicable interface or service context, authentication and authorization evidence, administrator and role state, process and resource telemetry, configuration history, and incident-response findings. Cisco states that these hardening issues were found during internal security review and are not known to be actively exploited.
· CVE-2026-20173 — Cisco NX-OS Software control-plane denial of service — Covered with adaptation where crafted or abnormal activity against an affected NX-OS control-plane service produces excessive resource consumption, process or control-plane instability, service degradation, device restart, network-control interruption, or downstream availability impact. Reliable implementation depends on affected NX-OS asset and version, enabled service and feature state, network reachability, control-plane and process telemetry, resource state, device availability, remediation status, and incident-response findings.
· CVE-2026-20097 — Cisco IMC authenticated administrator arbitrary code execution — Covered with adaptation where authenticated Cisco IMC administrator activity, crafted HTTP requests, arbitrary code execution, root-context process activity, configuration or firmware changes, suspicious management-network activity, or downstream server or appliance effects can be mapped into the report's management-plane-to-root-control model.
· CVE-2026-20096 — Cisco IMC authenticated administrator operating-system command execution — Covered with adaptation where authenticated Cisco IMC administrator activity, crafted command submission, arbitrary operating-system command execution, root-context process activity, configuration or firmware changes, suspicious management-network activity, or downstream server or appliance effects can be mapped into the report's management-plane-to-root-control model.
· CVE-2026-20095 — Cisco IMC authenticated administrator operating-system command execution — Covered with adaptation where authenticated Cisco IMC administrator activity, crafted command submission, arbitrary operating-system command execution, root-context process activity, configuration or firmware changes, suspicious management-network activity, or downstream server or appliance effects can be mapped into the report's management-plane-to-root-control model.
· CVE-2026-20094 — Cisco IMC authenticated read-only account command execution — Covered with adaptation where authenticated Cisco IMC read-only account activity, crafted command submission, arbitrary operating-system command execution, root-context process activity, configuration or firmware changes, suspicious management-network activity, or downstream server or appliance effects can be mapped into the report's management-plane-to-root-control model.
· CVE-2026-20079 — Cisco Secure Firewall Management Center unauthenticated web-interface authentication bypass and root execution — Covered with adaptation where unauthenticated Cisco Secure Firewall Management Center web-interface activity, crafted HTTP requests, authentication-bypass behavior, script or command execution, root-context activity, administrator or configuration changes, or downstream managed-firewall effects can be mapped into the report's authentication-bypass, management-plane-to-root-control, privileged-activity, and network-control behavior model. Cisco rates the vulnerability Critical with a CVSS base score of 10.0. CISA added CVE-2026-20079 to the Known Exploited Vulnerabilities Catalog on September 9, 2026. The KEV designation increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification.
· CVE-2026-20072 — Cisco ISE local unauthenticated 802.1X session hijack, authentication bypass, or sensitive-information disclosure — Covered with adaptation where local unauthenticated Cisco ISE 802.1X-related activity results in session hijack, authentication-bypass behavior, or sensitive-information disclosure under the documented conditions. Reliable implementation requires affected ISE asset and version context, 802.1X session and endpoint evidence, authentication state, local network context, information-access evidence, and incident-response findings.
· CVE-2026-20071 — Cisco ISE local unauthenticated 802.1X session hijack, authentication bypass, or sensitive-information disclosure — Covered with adaptation where local unauthenticated Cisco ISE 802.1X-related activity results in session hijack, authentication-bypass behavior, or sensitive-information disclosure under the documented conditions. Reliable implementation requires affected ISE asset and version context, 802.1X session and endpoint evidence, authentication state, local network context, information-access evidence, and incident-response findings.
· CVE-2026-20038 — Cisco Nexus 9000 Series Fabric Switches in ACI Mode endpoint-group contract bypass — Covered with adaptation where affected ACI fabric behavior bypasses expected endpoint-group contract enforcement and permits network communication inconsistent with intended segmentation or policy. Reliable implementation depends on affected Nexus and ACI inventory, endpoint-group and contract configuration, traffic and flow evidence, policy and fabric state, administrator activity, remediation status, and downstream network-security validation.
· CVE-2026-20035 — Cisco Unity Connection Web Inbox unauthenticated arbitrary outbound network requests — Covered with adaptation where unauthenticated Cisco Unity Connection Web Inbox activity, crafted HTTP requests, arbitrary network requests originating from the affected device, suspicious destination patterns, or associated application and network activity can be mapped into the report's management-plane and application-host behavior model.
· CVE-2026-20034 — Cisco Unity Connection authenticated API-driven root-level code execution — Covered with adaptation where authenticated Cisco Unity Connection user activity, crafted API requests, arbitrary code execution, application or service-context execution, root-context process activity, configuration changes, or associated network activity can be mapped into the report's management-plane-to-root-control behavior model.
· CVE-2026-20032 — Cisco NX-OS Software Python sandbox escape — Covered with adaptation where authenticated local Python activity on an affected NX-OS device escapes the intended sandbox or execution restriction and results in unauthorized operating-system functionality, privileged command or process activity, filesystem or configuration modification, persistence, or downstream network-control effects. Reliable implementation depends on NX-OS version, local identity and privilege context, Python execution activity, process and command telemetry, filesystem and configuration evidence, remediation status, and incident-response findings.
· CVE-2026-20030 — Cisco Crosswork SQL injection — Covered with adaptation where Cisco Crosswork SQL-injection behavior produces suspicious application requests, abnormal database interaction, unauthorized management-data access, configuration manipulation, service anomalies, or downstream network-control effects.
· CVE-2026-19843 — 389 Directory Server crafted DN leading to root command execution through Cockpit 389 Console — Covered with adaptation where a delegated LDAP user creates or renames a 389 Directory Server entry with a crafted DN and subsequent viewing through the privileged Cockpit 389 Console causes shell command execution, root-context process activity, filesystem or configuration changes, outbound communication, or host compromise that can be mapped into the report's management-plane-to-root-control and application-host command-execution model. Reliable implementation depends on Red Hat Directory Server deployment context, Cockpit 389 Console presence, delegated LDAP create or rename permissions, DN and directory-object change records, privileged Cockpit operator activity, application and shell execution evidence, process ancestry, root-context activity, filesystem and configuration evidence, network activity, and incident-response findings. Exploitation requires both delegated LDAP write capability and a privileged operator viewing the crafted entry. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-19626 — Tenable Security Center authenticated non-administrative report-generation execution path — Covered with adaptation where authenticated non-administrative Tenable Security Center activity, crafted report-generation input, suspicious report or job execution, server-side rendering activity, unexpected child-process creation, Security Center service-account execution, file or network activity, administrative-state changes, or downstream security-platform effects can be mapped into the report's management-plane access and service-context execution behavior model.
· CVE-2026-19404 — 389 Directory Server CleanAllRUV / Abort CleanAllRUV missing authorization — Covered with adaptation where 389 Directory Server CleanAllRUV or Abort CleanAllRUV replication-maintenance extended operations are invoked without the expected authorization check and produce replica-ID removal, changelog purging, interrupted cleanup, replication inconsistency, or availability effects that can be mapped into the report's protected-functionality and administrative-control model. Reliable implementation depends on directory-server asset and supplier-role context, LDAP listener exposure, anonymous-access configuration, bind identity, extended-operation telemetry, replication metadata, changelog state, administrator workflow, service health, and incident-response evidence. The shipped default anonymous-access configuration can permit unauthenticated exploitation; otherwise any successfully bound low-privileged account can reach the affected handlers. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-19233 — Schneider Electric EcoStruxure IT Data Center Expert privileged SSRF and command-execution path — Covered with adaptation where a privileged EcoStruxure IT Data Center Expert user submits crafted, unvalidated parameters to an affected server endpoint and produces SSRF behavior, unauthorized server-side requests, command execution, server-data disclosure, unexpected process activity, configuration effects, or infrastructure-monitoring impact. Reliable implementation depends on DCE asset and version inventory, privileged account and session context, web/API request telemetry, destination and server-side request evidence, process and command activity, data-access evidence, configuration state, and incident-response findings. Versions 9.1.2 and prior are affected.
· CVE-2026-18922 — 389 Directory Server stale privileged identity after failed SASL PLAIN bind — Covered with adaptation where a failed 389 Directory Server SASL PLAIN bind plants stale privileged identity state and a subsequent successful bind on the same connection results in unauthorized cn=Directory Manager authority, abnormal effective identity, privileged directory operations, configuration changes, credential or object access, or downstream identity-control effects that can be mapped into the report's authentication-bypass, session-state, privileged-object, and control-plane model. Reliable implementation depends on 389 Directory Server or Red Hat Directory Server asset and version inventory, LDAP or LDAPS connection correlation, SASL mechanism, requested bind DN, bind result, effective connection identity, subsequent bind sequence, Directory Manager activity, directory and configuration changes, and incident-response evidence. Red Hat rates the flaw Critical and states that the primary chain can grant full Directory Manager authority remotely without valid credentials, user interaction, or non-default configuration. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-18851 — Ivanti Endpoint Manager Mobile authenticated missing authorization and administrator privilege escalation — Covered with adaptation where an authenticated Ivanti Endpoint Manager Mobile user reaches a missing-authorization path and escalates to administrator, producing abnormal role or permission state, privileged administrative activity, configuration changes, managed-device actions, protected-resource access, or downstream enterprise-management effects. Reliable implementation depends on EPMM asset and version inventory, authenticated user and session context, authorization and role-state evidence, administrative audit logs, configuration-change records, managed-device activity, and incident-response findings. Fixed versions are 12.10.0.0, 12.9.0.2, and 12.8.0.4. Ivanti reports no known customer exploitation at disclosure, and no CISA KEV status is established.
· CVE-2026-18651 — 389 Directory Server account-lock bypass through stale authenticated connection state — Covered with adaptation where a 389 Directory Server SASL PLAIN bind against an administratively locked account installs authenticated connection state before the account-lock check, causing subsequent activity on the same connection to continue with the locked account's existing privileges despite a failed bind result. Reliable implementation depends on account-lock state, SASL PLAIN bind and authentication-result telemetry, connection reuse, requested and effective bind identity, directory access and modification evidence, and incident-response findings. This condition defeats account lock as an access-revocation control but does not grant privileges beyond those already assigned to the affected account. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-18355 — 389 Directory Server authenticated SASL wrapped-record heap buffer overflow — Covered with adaptation where an authenticated 389 Directory Server session using a SASL integrity-protected security layer receives a malformed wrapped record whose lower-bound length handling causes attacker-controlled heap buffer overflow, service failure, unexpected execution, or potential remote code execution that can be mapped into the report's application-host and service-context execution model. Reliable implementation depends on 389 Directory Server asset and version inventory, successful SASL bind and SSF context, wrapped-record or connection anomalies, process and crash evidence, memory-corruption indicators where available, unexpected child-process or execution evidence, privilege context, network activity, and incident-response findings. Red Hat rates the issue Important and states that authenticated exploitation can cause denial of service or potentially remote code execution. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-16876 — NEC UNIVERGE IX-R / IX-V WebGUI authentication bypass and arbitrary CLI command execution — Covered with adaptation where NEC UNIVERGE IX-R/IX-V WebGUI activity bypasses expected authentication through tampered WebGUI messages and results in arbitrary CLI-command execution, privileged device activity, configuration changes, routing, firewall, VPN, DNS, or downstream network-control effects that can be mapped into the report's management-plane-to-command-execution model.
· CVE-2026-16812 — VeloCloud Orchestrator On-Prem OS command injection — Covered with adaptation where VeloCloud Orchestrator On-Prem management-plane access, OS command-injection behavior, application or service-context execution, host-level process activity, file activity, outbound communication, administrator-state anomalies, configuration changes, or downstream network-control impact can be mapped into the same management-plane-to-host-control behavior model. CISA added CVE-2026-16812 to the KEV Catalog on July 27, 2026 based on evidence of active exploitation.
· CVE-2026-12745 — Ivanti Neurons for ITSM unauthenticated deserialization leading to server-side execution — Covered with adaptation where unauthenticated Ivanti Neurons for ITSM deserialization activity reaches a server-side execution path and produces service-context execution, unexpected child processes, file or configuration changes, outbound communication, privileged follow-on activity, or downstream enterprise-workflow effects. Reliable implementation depends on Ivanti Neurons for ITSM on-premises asset and branch inventory, public or restricted management exposure, web/API request context, deserialization-path telemetry where available, service and child-process lineage, file and configuration evidence, network activity, and incident-response findings. Ivanti rates the vulnerability Critical at 9.8.
· CVE-2026-12744 — Ivanti Neurons for ITSM unauthenticated deserialization leading to server-side execution — Covered with adaptation where unauthenticated Ivanti Neurons for ITSM deserialization activity reaches a server-side execution path and produces service-context execution, unexpected child processes, file or configuration changes, outbound communication, privileged follow-on activity, or downstream enterprise-workflow effects. Reliable implementation depends on Ivanti Neurons for ITSM on-premises asset and branch inventory, public or restricted management exposure, web/API request context, deserialization-path telemetry where available, service and child-process lineage, file and configuration evidence, network activity, and incident-response findings. Ivanti rates the vulnerability Critical at 9.8.
· CVE-2026-12651 — Ivanti Neurons for ITSM authenticated deserialization leading to server-side execution — Covered with adaptation where authenticated Ivanti Neurons for ITSM deserialization activity produces server-side execution, unexpected application or service child processes, file or configuration changes, outbound communication, privileged follow-on activity, or downstream enterprise-workflow effects. Reliable implementation depends on affected on-premises branch inventory, authenticated user and session context, web/API and deserialization-path telemetry where available, service and child-process lineage, file and configuration evidence, network activity, and incident-response findings. Ivanti rates the vulnerability High at 8.8.
· CVE-2026-12650 — Ivanti Neurons for ITSM authenticated deserialization leading to server-side execution — Covered with adaptation where authenticated Ivanti Neurons for ITSM deserialization activity produces server-side execution, unexpected application or service child processes, file or configuration changes, outbound communication, privileged follow-on activity, or downstream enterprise-workflow effects. Reliable implementation depends on affected on-premises branch inventory, authenticated user and session context, web/API and deserialization-path telemetry where available, service and child-process lineage, file and configuration evidence, network activity, and incident-response findings. Ivanti rates the vulnerability Critical at 9.9.
· CVE-2026-12648 — Ivanti Neurons for ITSM authenticated deserialization leading to server-side execution — Covered with adaptation where authenticated Ivanti Neurons for ITSM deserialization activity produces server-side execution, unexpected application or service child processes, file or configuration changes, outbound communication, privileged follow-on activity, or downstream enterprise-workflow effects. Reliable implementation depends on affected on-premises branch inventory, authenticated user and session context, web/API and deserialization-path telemetry where available, service and child-process lineage, file and configuration evidence, network activity, and incident-response findings. Ivanti rates the vulnerability High at 8.8.
· CVE-2026-12647 — Ivanti Neurons for ITSM authenticated missing authorization leading to server-side remote code execution — Covered with adaptation where an authenticated Ivanti Neurons for ITSM user reaches a missing-authorization path that permits server-side remote code execution, resulting in unexpected process execution, privileged service activity, file or configuration changes, outbound communication, or downstream enterprise-workflow effects. Reliable implementation depends on affected on-premises branch inventory, authenticated user and session context, authorization and protected-function evidence, service and child-process lineage, file and configuration telemetry, network activity, and incident-response findings. Ivanti rates the vulnerability Critical at 9.9.
· CVE-2026-12646 — Ivanti Neurons for ITSM authenticated missing authorization leading to server-side remote code execution — Covered with adaptation where an authenticated Ivanti Neurons for ITSM user reaches a missing-authorization path that permits server-side remote code execution, resulting in unexpected process execution, privileged service activity, file or configuration changes, outbound communication, or downstream enterprise-workflow effects. Reliable implementation depends on affected on-premises branch inventory, authenticated user and session context, authorization and protected-function evidence, service and child-process lineage, file and configuration telemetry, network activity, and incident-response findings. Ivanti rates the vulnerability Critical at 9.9.
· CVE-2026-12645 — Ivanti Neurons for ITSM authenticated missing authorization leading to server-side remote code execution — Covered with adaptation where an authenticated Ivanti Neurons for ITSM user reaches a missing-authorization path that permits server-side remote code execution, resulting in unexpected process execution, privileged service activity, file or configuration changes, outbound communication, or downstream enterprise-workflow effects. Reliable implementation depends on affected on-premises branch inventory, authenticated user and session context, authorization and protected-function evidence, service and child-process lineage, file and configuration telemetry, network activity, and incident-response findings. Ivanti rates the vulnerability Critical at 9.9. Ivanti states the eight ITSM vulnerabilities affect on-premises 2025.2, 2025.3, 2025.4, and 2026.1; September 2026 security patches are available, cloud landscapes were fixed on August 9, and the on-premises 2026.2 release scheduled for September 21 includes the fixes. No known customer exploitation or CISA KEV status is established for the eight identifiers.
· CVE-2026-12342 — SailPoint IdentityIQ unauthenticated web-service API remote code execution — Covered with adaptation where unauthenticated SailPoint IdentityIQ web-service API content reaches the vulnerable improper-input-validation path and produces remote code execution on the IdentityIQ server, abnormal application or service processes, filesystem or configuration changes, identity-governance workflow manipulation, role or entitlement changes, connector activity, outbound communication, or downstream enterprise-system effects. Reliable implementation depends on IdentityIQ asset and version inventory, web-service API reachability, request telemetry where available, process and service activity, identity-governance state, roles and entitlements, connector and configuration evidence, filesystem and network behavior, remediation state, and incident-response findings. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation.
· CVE-2026-11770 — 389 Directory Server unauthenticated LDAP search-filter injection in CleanAllRUV replication status checking — Covered with adaptation where an unauthenticated remote client injects LDAP search-filter elements into the 389 Directory Server CleanAllRUV replication status-check extended operation and uses the elevated replication-plugin search against cn=config to infer sensitive server configuration metadata, including replication bind DNs or password-storage scheme information. Reliable implementation depends on 389 Directory Server asset and version inventory, LDAP listener exposure, anonymous-access state, extended-operation and LDAP query telemetry, replication context, configuration-access evidence, disclosed-metadata context, and incident-response findings. No confirmed in-the-wild exploitation or CISA KEV status is established.
· CVE-2026-8044 — Schneider Electric EcoStruxure IT Data Center Expert privileged backup-configuration command execution — Covered with adaptation where a privileged EcoStruxure IT Data Center Expert user supplies malicious backup-configuration arguments and produces command execution, unexpected server processes, file or configuration changes, outbound communication, data-access effects, or infrastructure-management compromise. Reliable implementation depends on DCE asset and version inventory, privileged account and session context, backup-configuration activity, parameter evidence where available, process and command telemetry, filesystem and configuration state, network behavior, and incident-response findings. Versions 9.1.2 and prior are affected.
· CVE-2026-7273 — Zyxel GS1900 LAN-based unauthenticated CGI stack buffer overflow — Covered with adaptation where a LAN-based unauthenticated attacker sends a crafted HTTP request to the CGI management component of an affected Zyxel GS1900 series switch and produces stack-based buffer-overflow behavior, potential operating-system command execution, abnormal device or process activity, configuration or administrative-state change, unexpected outbound communication, or downstream switching and network-control effects. Reliable implementation depends on GS1900 model and firmware inventory, LAN and management-interface reachability, source-network context, HTTP and CGI request telemetry where available, device and process behavior, command-execution evidence where observable, administrator and configuration-change records, outbound network activity, switching and downstream network-control state, remediation status, and incident-response findings. Zyxel documents the attacker prerequisite as LAN-based and unauthenticated; Internet-reachable exploitation should not be inferred unless local architecture exposes the affected management interface beyond the expected LAN boundary. CISA has added CVE-2026-7273 to the Known Exploited Vulnerabilities Catalog based on evidence of active exploitation.
· CVE-2026-54710 — FreePBX authenticated Superfecta unsafe PHP file inclusion — Covered with adaptation where authenticated FreePBX Superfecta processing reaches an unsafe PHP file-inclusion path and produces arbitrary PHP execution in the web-server context, unexpected process or child-process activity, filesystem or configuration changes, credential or sensitive-data access, outbound communication, persistence, or downstream telephony effects. Reliable implementation depends on FreePBX asset and Superfecta-module version inventory, authenticated identity and authorization context, Superfecta configuration and source-processing activity, PHP and web-server process telemetry, filesystem and configuration evidence, Asterisk activity, network behavior, remediation state, and incident-response findings. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation.
· CVE-2026-54675 — FreePBX authenticated Soundlang path traversal and arbitrary file write — Covered with adaptation where authenticated FreePBX Soundlang upload or conversion activity abuses insufficient path sanitization to write an attacker-controlled file outside the intended path, including malicious PHP placement in the web root and follow-on code execution. Reliable implementation depends on FreePBX asset and Soundlang-module version inventory, authenticated identity and authorization context, upload and conversion activity, submitted paths and filenames where available, filesystem writes, PHP and web-server process telemetry, Asterisk activity, configuration state, network behavior, remediation state, and incident-response findings. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation.
· CVE-2026-5430 — WSO2 JWT algorithm authentication bypass — Covered with adaptation where an unauthenticated remote attacker supplies a JWT signed using an unsupported algorithm and bypasses authentication to an affected WSO2 API Manager, API Control Plane, Traffic Manager, or Universal Gateway deployment, producing unauthorized administrative access, abnormal privileged sessions, administrative-account takeover, configuration changes, API or backend-service access, credential or sensitive-data access, or consequential downstream activity. Reliable implementation depends on WSO2 product and affected-version inventory, management and API interface exposure, JWT and token-validation telemetry where available, authentication and administrator-session evidence, API and gateway request records, administrator-state and configuration changes, backend-service activity, credential or sensitive-data access where observable, network telemetry, and incident-response findings. Public reporting confirms malicious exploitation. CISA added CVE-2026-5430 to the Known Exploited Vulnerabilities Catalog on September 24, 2026, based on evidence of active exploitation. Active exploitation and the CISA KEV designation increase remediation and retrospective-hunting urgency but do not change the Coverage With Adaptation classification.
· CVE-2024-3400 — PAN-OS GlobalProtect exploitation — Covered with adaptation where PAN-OS GlobalProtect telemetry, management-interface paths, command-execution signals, endpoint or system logs, outbound communication, and configuration-impact records are mapped into equivalent behavior logic.
· CVE-2024-21893 — Ivanti appliance SSRF-adjacent exploitation — Covered with adaptation where Ivanti appliance telemetry, gateway request paths, SSRF-adjacent appliance behavior, follow-on command execution, outbound communication, and administrator or configuration evidence are available.
· CVE-2024-21887 — Ivanti appliance command injection — Covered with adaptation where Ivanti command-injection behavior can be tied to management-plane access, appliance service-context execution, system logs, file activity, outbound communication, and post-access configuration review.
· CVE-2023-20273 — Cisco IOS XE Web UI command-injection or post-access behavior — Covered with adaptation where Cisco IOS XE Web UI command-injection or post-access behavior is visible through management-plane telemetry, device logs, administrator-state changes, configuration changes, or downstream network-control events.
· CVE-2023-20198 — Cisco IOS XE Web UI management-plane compromise — Covered with adaptation where Cisco IOS XE Web UI management-plane compromise, privilege escalation, or unauthorized administrative control can be correlated with source context, administrator anomalies, configuration changes, and network-device impact.
· CVE-2023-3519 — Citrix ADC / Gateway exploitation — Covered with adaptation where Citrix ADC or Gateway exploitation produces management-plane access anomalies, appliance execution signals, outbound communication, credential or configuration access, or downstream infrastructure impact.
· CVE-2023-27997 — Fortinet FortiOS SSL-VPN exploitation — Covered with adaptation where Fortinet FortiOS SSL-VPN exploitation produces edge-appliance access anomalies, service instability, execution indicators, outbound follow-on activity, or firewall or VPN configuration impact.
· CVE-2023-2868 — Barracuda ESG command injection — Covered with adaptation where Barracuda ESG command-injection behavior produces appliance service-context execution, file staging, outbound communication, credential or configuration access, or persistence-oriented activity.
· CVE-2022-40684 — Fortinet authentication bypass — Covered with adaptation where Fortinet authentication-bypass behavior produces unauthorized management-plane access, administrator changes, configuration manipulation, or downstream firewall or VPN impact.
· CVE-2021-22986 — F5 iControl REST exploitation — Covered with adaptation where F5 iControl REST exploitation produces management-plane access anomalies, command execution, administrator or configuration changes, outbound communication, or network-control impact.
· CVE-2020-5902 — F5 BIG-IP TMUI exploitation — Covered with adaptation where F5 BIG-IP TMUI exploitation produces management-interface abuse, command execution, file access, outbound communication, administrator changes, or configuration manipulation.
· Cisco Talos Secure FMC exploitation and post-compromise activity — Covered with adaptation where exploitation of the already-registered Cisco Secure Firewall Management Center vulnerabilities is followed by command execution, root-context activity, credential and configuration theft, tunneling or proxy activity, internal reconnaissance, packet sniffing, persistence, defense impairment, downstream endpoint targeting, malware deployment, or ransomware staging. Cisco Talos documents three intrusion clusters, UAT-12197, UAT-11823, and UAT-11988, including observed Cyclops Blink deployment and Qilin ransomware activity. Reliable local conclusions require Secure FMC asset and version validation, management-interface and authentication evidence, process and root-context telemetry, filesystem and package activity, credential and configuration-access records, tunneling or proxy evidence, downstream network activity, endpoint evidence, and incident-response corroboration. This is a non-CVE Coverage With Adaptation behavior entry and does not add or duplicate CVE-2026-20079 or CVE-2026-20316.
· Compromised public Wi-Fi gateway DNS redirection and Microsoft 365 credential-harvesting activity — Covered with adaptation where unauthorized gateway administration, DNS resolver or forwarding changes, forged or anomalous DNS responses, redirected connected-user traffic, attacker-controlled Microsoft 365 credential-harvesting infrastructure, or related authentication exposure can be mapped into the same management-plane-to-network-control and downstream credential-exposure model.
· MikroTrick RouterOS exploitation activity — Covered with adaptation where CVE-2026-67276 and CVE-2026-86060 are combined against internet-reachable RouterOS SSH services and produce unauthorized administrative control, unknown users, scripts, scheduler tasks, proxy servers, tunnels, configuration changes, or downstream network-control effects.
· Head Mare TrueConf Server exploitation activity — Covered with adaptation where exploitation of vulnerable TrueConf Server deployments, privileged server execution, web-shell placement, infrastructure discovery, privileged database access, client-installer replacement, or downstream malware delivery can be mapped to locally available telemetry.
· PhantomCore and PhantomGraph delivery through compromised TrueConf Server infrastructure — Covered with adaptation where infected TrueConf client installers, downstream execution, persistence, command-and-control, or related endpoint behavior can be identified through locally mapped client-distribution, file, process, endpoint, network, and incident-response telemetry.
· Appliance-focused intrusion tradecraft — Covered with adaptation when local telemetry shows management-plane exploitation, command execution, privileged activity, administrator-state change, outbound communication, internal discovery, or downstream network-control behavior affecting edge or infrastructure appliances.
· Proxy or botnet operator tradecraft — Covered with adaptation when local telemetry shows compromised infrastructure being used for outbound staging, tunnel-like communication, proxy-like behavior, public-STUN-assisted NAT traversal or binding maintenance, back-connect proxy activity, internal discovery, device enumeration, self-propagation, or role-inconsistent external communication after suspected management-plane compromise.
· Ransomware pre-access or staging tradecraft — Covered with adaptation when local telemetry shows management-plane exploitation followed by privileged activity, credential or configuration access, remote-access change, firewall or VPN manipulation, internal discovery, tool staging, or downstream infrastructure preparation.
· State-aligned edge-infrastructure pre-positioning tradecraft — Covered with adaptation when local telemetry shows stealthy management-plane access, administrator or API-token manipulation, configuration review, outbound communication, internal discovery, and long-lived access behavior on edge or network-management infrastructure.
Non-Coverage Conditions
· Splunk Enterprise vulnerable-version state, management-interface or REST API reachability, ordinary administrator or application activity, routine search-job execution, expected SPL2 Module Catalog operations, normal Secure Gateway activity, ordinary package upgrades, authorized Patroni REST API activity, expected process execution, normal service behavior, or routine logging should not by themselves be treated as proof that CVE-2026-76264 through CVE-2026-76285 were successfully exploited. Reliable attribution requires the specific affected function and prerequisite together with unauthorized behavior, consequential execution, access, configuration, service, or security-monitoring evidence.
· Cisco NX-OS or Nexus vulnerable-version state, management-interface or NX-API reachability, enabled OAM or NGOAM functionality, ordinary control-plane traffic, routine Python use, ordinary administrator activity, routine configuration changes, expected device reloads, or normal routing and switching activity should not by themselves be treated as proof that any October 7 NX-OS or Nexus vulnerability was successfully exploited.
· Cisco Application Policy Infrastructure Controller vulnerable-version state, ordinary authenticated API activity, management-interface reachability, expected file access, routine administrator activity, normal configuration change, or ordinary ACI fabric behavior should not by themselves be treated as proof that CVE-2026-76498, CVE-2026-76499, CVE-2026-76500, CVE-2026-20321, or CVE-2026-76488 was successfully exploited.
· Cisco License On-Prem vulnerable-version state, management-interface reachability, ordinary administrator authentication, normal licensing operations, routine password-reset activity, expected database or filesystem activity, or normal service behavior should not by themselves be treated as proof that CVE-2026-76480, CVE-2026-76482, CVE-2026-76483, CVE-2026-76484, CVE-2026-20328, CVE-2026-76437, CVE-2026-76452, or CVE-2026-76454 was successfully exploited.
· Cisco Meraki vulnerable-firmware state, ordinary cloud-management activity, expected network traffic, routine configuration changes, administrator sessions, service restarts, or isolated device instability should not by themselves be treated as proof that CVE-2026-76463, CVE-2026-76464, CVE-2026-76467, CVE-2026-76468, CVE-2026-76469, CVE-2026-76470, or CVE-2026-76472 was successfully exploited.
· Cisco Finesse vulnerable-version state, management-interface reachability, ordinary HTTP requests, expected server-side connections, normal application activity, or isolated service errors should not by themselves be treated as proof that CVE-2026-20362 was successfully exploited.
· HPE Integrated Lights-Out 7 vulnerable-firmware state, management-interface reachability, ordinary authentication failures, expected administrator activity, routine configuration changes, firmware-update activity, or normal managed-server operations should not by themselves be treated as proof that CVE-2026-79820 was successfully exploited.
· HPE Networking Analytics and Location Engine vulnerable-version state, management-interface or API reachability, ordinary administrative activity, routine maintenance-restore operations, normal file writes, expected socket traffic, standard service restarts, or ordinary API responses should not by themselves be treated as proof that CVE-2026-76708 through CVE-2026-76717 was successfully exploited.
· CVE-2026-76713 requires authenticated access to the affected maintenance-restore functionality and should not be represented as unauthenticated root filesystem access.
· CVE-2026-76714 requires authenticated access to the affected ALE web interface and should not be represented as unauthenticated root command execution.
· CVE-2026-76715 requires the documented man-in-the-middle condition and should not be generalized to arbitrary unauthenticated direct remote code execution against an ALE appliance.
· The remaining HPE ALE entries in the ten-CVE cohort should retain their vendor-specific documented prerequisite and effect. A vulnerability's presence in the cohort should not be used to infer a different cohort member's authentication requirement, execution primitive, data-access effect, filesystem effect, socket behavior, denial-of-service condition, credential condition, or API-disclosure consequence.
· Kiteworks Core vulnerable-version state, ordinary delegated-administrator activity, routine administrative imports, legitimate creation or use of integration credentials, ordinary administrator-role changes, expected connector or managed-content activity, or routine configuration changes should not by themselves be treated as proof that CVE-2026-102132 was successfully exploited.
· CVE-2026-102132 should not be represented as an unauthenticated Kiteworks Core compromise. The documented prerequisite is an authenticated delegated administrator holding the required administrative permission whose use of the affected administrative import function permits creation of a privileged integration credential beyond the intended authorization scope and consequential elevation to full system-administrator privileges.
· IBM Guardium Data Protection vulnerable-version state, appliance reachability, ordinary Central Manager or Collector administration, routine Guardium Installation Manager activity, normal patch or import operations, ordinary REST requests, routine PESI activity, normal SNMP alerts, routine database activity, expected file access, normal SUID-wrapper execution, ordinary credential use, certificate-validation events, or normal web-interface use should not by themselves be treated as proof that any of the 37 Guardium vulnerabilities was successfully exploited.
· kcp vulnerable-version state, Kubernetes-compatible API reachability, ordinary authenticated tenant activity, normal X-Remote-* identity-header use generated by trusted infrastructure, routine RBAC changes, normal secret access, expected APIExport or APIBinding activity, or ordinary workspace administration should not by themselves be treated as proof that CVE-2026-61682 was successfully exploited.
· CVE-2026-61682 should not be represented as an unauthenticated control-plane compromise. The documented prerequisite is an authenticated tenant or client whose caller-supplied identity headers reach the affected front proxy.
· External proxy removal of all inbound X-Remote-* identity headers is a mitigation and should not be represented as equivalent to upgrade remediation.
· Check Point Security Management vulnerable-version state, management-web reachability, ordinary web administration, expected file activity, normal Java class loading, routine administrator sessions, or approved security-policy changes should not by themselves be treated as proof that CVE-2026-93616 was successfully exploited.
· Check Point Security Management or Log Server vulnerable-version state, management-interface reachability, ordinary login activity, normal administrator sessions, routine policy changes, ordinary FWM process activity, or the presence or absence of the LivePatch should not by themselves be treated as proof that CVE-2026-91843 was successfully exploited.
· SUSE Rancher vulnerable-version state, public or authenticated API reachability, ordinary public UI settings, routine browser login activity, normal OIDC or identity-provider use, ordinary logout events, routine API-token use, expected RBAC changes, or ordinary cluster administration should not by themselves be treated as proof that CVE-2026-88804 or CVE-2026-88805 was successfully exploited.
· CVE-2026-88805 should not be represented as token creation or authentication bypass. The documented issue is failure to revoke a previously valid public API session token after logout, so proof of exploitation requires evidence that a previously obtained token remained in use after the corresponding logout or revocation point.
· Logsign SIEM vulnerable-version state, management or application-interface reachability, presence of default credentials, ordinary authentication, routine administrator activity, expected file or configuration changes, normal process or service activity, ordinary connector or ingestion changes, routine alerting or logging behavior, or isolated application errors should not by themselves be treated as proof that CVE-2026-90924, CVE-2026-90925, or CVE-2026-90926 was successfully exploited.
· UTMStack vulnerable-version state, management-interface or API reachability, ordinary authenticated administration, normal identity-provider activity, routine STOMP or connected-agent communication, possession or expected use of an internal key, ordinary password-reset activity, routine PDF-report generation, normal database queries, or ordinary network-scan activity should not by themselves be treated as proof that CVE-2026-82039 through CVE-2026-82045 were successfully exploited.
· The seven UTMStack identifiers should not be represented as one mandatory exploit chain. Each identifier retains its documented authentication prerequisite, affected service or function, exploitation mechanic, and consequence. CVE-2026-82043 is unauthenticated account enumeration and should not be represented as account compromise, while the authenticated prerequisites applicable to CVE-2026-82039, CVE-2026-82040, CVE-2026-82041, CVE-2026-82044, and CVE-2026-82045 should not be generalized to unauthenticated exploitation.
· Issabel Framework vulnerable-version state, internet reachability, ordinary JWT use, routine PBX administration, normal pbxapi traffic, ordinary manager originate activity, or ordinary Asterisk process behavior should not by themselves be treated as proof that CVE-2026-89026 was successfully exploited.
· FreePBX vulnerable-version state, ordinary Administrator Control Panel use, routine authenticated administration, normal Soundlang uploads or conversions, ordinary Superfecta configuration, expected GraphQL or API activity, routine PHP or Asterisk process behavior, or ordinary telephony configuration changes should not by themselves be treated as proof that CVE-2026-54675, CVE-2026-54710, or CVE-2026-75600 was successfully exploited.
· The three FreePBX identifiers should not be represented as a mandatory exploit chain. Each retains its own authenticated prerequisite, affected module or API path, and execution primitive.
· WSO2 vulnerable-version state, internet or API-interface exposure, ordinary JWT use, normal administrator sessions, expected API traffic, or routine configuration changes should not by themselves be treated as proof that CVE-2026-5430 was successfully exploited.
· HP Advance vulnerable-version state, ordinary enterprise print-workflow activity, routine administrator activity, expected file creation or modification, normal service or process activity, or ordinary configuration changes should not by themselves be treated as proof that CVE-2026-89082, CVE-2026-89083, or CVE-2026-89084 was successfully exploited.
· Dell ObjectScale vulnerable-version state, ordinary storage management, expected object-storage operations, routine administrator activity, normal service or process behavior, or isolated deserialization-related errors should not by themselves be treated as proof that CVE-2026-70416 was successfully exploited.
· SolarWinds Access Rights Manager vulnerable-version state, ordinary ARM administration, routine identity or access-rights changes, normal service activity, or management-interface reachability should not by themselves be treated as proof that CVE-2026-28326 was successfully exploited.
· SolarWinds Observability Self-Hosted vulnerable-version state, SolarWinds Platform presence, the documented non-default and non-secure configuration relevant to CVE-2026-28324, use of the affected communication mode relevant to CVE-2026-28325, management-interface or service reachability, ordinary SolarWinds administration, normal service or process activity, or isolated application errors should not by themselves be treated as proof that CVE-2026-28324 or CVE-2026-28325 was successfully exploited.
· Malcolm vulnerable-version state, internet or internal reachability, ordinary analyst activity, routine uploads, normal archive processing, standard proxy or identity-provider traffic, read-only deployment state, ordinary record edits, or the presence of sample configuration should not by themselves be treated as proof that CVE-2026-90443 through CVE-2026-90457 was successfully exploited.
· Traefik vulnerable-version state, public exposure, ordinary reverse-proxy traffic, ordinary ForwardAuth use, HTTP/3 enablement, h2c support, or isolated header, trailer, route, or access-log anomalies should not by themselves be treated as proof that CVE-2026-88004, CVE-2026-88007, CVE-2026-88008, CVE-2026-88009, or CVE-2026-88011 was successfully exploited.
· EcoStruxure IT Data Center Expert vulnerable-version state, routine privileged administration, ordinary server-side network activity, ordinary backup configuration, or routine infrastructure-monitoring behavior should not by themselves be treated as proof that CVE-2026-19233 or CVE-2026-8044 was successfully exploited.
· Zyxel GS1900 vulnerable-version state, ordinary LAN management activity, routine HTTP access to the management interface, ordinary switch configuration changes, or the CISA KEV designation should not by themselves be treated as proof that CVE-2026-7273 was successfully exploited in a specific environment.
· Consul vulnerable-version state, ordinary catalog registration or deregistration, routine health-check activity, normal RPC communication, expected peering replication, Connect intention changes, or ordinary Envoy policy enforcement should not by themselves be treated as proof that CVE-2026-87090, CVE-2026-87106, CVE-2026-87107, or CVE-2026-88021 was successfully exploited.
· FreeIPA vulnerable-version state, LDAP or LDAPS reachability, anonymous-bind availability, ordinary OTP self-service activity, normal Kerberos-principal creation, normal administrators-group changes, ordinary idp-add use, routine IdP configuration, or isolated memory growth should not by themselves be treated as proof that CVE-2026-76578 or CVE-2026-79678 was successfully exploited.
· SailPoint IdentityIQ vulnerable-version state, web-service API reachability, ordinary identity-governance activity, routine role or entitlement changes, normal connector activity, ordinary administrative sessions, or isolated application errors should not by themselves be treated as proof that CVE-2026-12342 was successfully exploited.
· 389 Directory Server or Red Hat Directory Server vulnerable-version state, ordinary LDAP or LDAPS traffic, ordinary failed or successful binds, ordinary anonymous access, ordinary ACI matches, routine replication maintenance, ordinary Cockpit administration, or isolated service instability should not by themselves be treated as proof that CVE-2026-76560, CVE-2026-19843, CVE-2026-19404, CVE-2026-18922, CVE-2026-18651, CVE-2026-18355, or CVE-2026-11770 was successfully exploited.
· SonicWall Network Security Manager On-Prem vulnerable-version state, ordinary SuperAdmin or Admin activity, ordinary file uploads, archive processing, configuration changes, or management-interface activity should not by themselves be treated as proof that CVE-2026-78327, CVE-2026-78328, or CVE-2026-81939 was successfully exploited.
· ASUS Control Center Enterprise vulnerable-version state, web-management exposure, TCP port 2222 availability, ordinary SSH activity, or ordinary managed-endpoint administration should not by themselves be treated as proof that CVE-2026-75754 was successfully exploited.
· NEC UNIVERGE IX-R/IX-V vulnerable-version state, enabled WebGUI functionality, internet reachability, ordinary WebGUI access, ordinary administrative sessions, CLI activity, or configuration changes should not by themselves be treated as proof that CVE-2026-16876 was successfully exploited.
· Public reporting confirms that the two TrueConf vulnerabilities were used together in observed Head Mare activity, but they should not be represented as a mandatory exploit chain in every environment.
· Fortinet FortiMail vulnerable-version state, HTTP or HTTPS interface reachability, ordinary web or administrative requests, routine filesystem activity, expected configuration changes, normal mail processing, ordinary administrator activity, or the CISA KEV designation should not by themselves be treated as proof that CVE-2026-104286 was successfully exploited on a specific local appliance. Successful exploitation requires environment-specific evidence connecting the affected request path to unauthorized file-write behavior or consequential appliance activity.
· Cisco Secure Email Gateway vulnerable-version state, ordinary email traffic, routine message scanning, isolated database anomalies, or the CISA KEV designation should not by themselves be treated as proof that CVE-2026-76461 was successfully exploited on a specific local appliance.
· The separate active-exploitation and CISA KEV evidence for CVE-2026-76461 must not be used as evidence that CVE-2026-76440, CVE-2026-76441, CVE-2026-20353, CVE-2026-76443, or CVE-2026-76442 is exploited or CISA KEV-listed.
· Cisco Secure Firewall Management Center vulnerable-version state, internet reachability, ordinary management-interface activity, failed authentication, or routine administrative and firewall-policy changes should not by themselves be treated as proof that CVE-2026-20079 was successfully exploited. CISA KEV status establishes that the vulnerability belongs in the Known Exploited Vulnerabilities Catalog but does not establish compromise of a specific local system.
· VeloCloud Orchestrator-specific command injection should not be treated as directly covered by the current anchor-product detection logic unless the environment separately maps VeloCloud Orchestrator assets, management paths, application and host services, process activity, administrator baselines, configuration records, outbound communication, and downstream network-control telemetry.
· CVE-2026-93952 should not be treated as directly covered by the current anchor-product detection logic or as proof of compromise based solely on vulnerable-version state, VCO web-interface reachability, certificate-based Edge-to-VCO authentication, possession of the public portion of an Edge authentication certificate, or Arista's active-exploitation statement.
· OPNsense-specific GeoIP alias-import exploitation should not be treated as directly covered by the current anchor-product detection logic unless the environment separately maps OPNsense assets, alias permissions, GeoIP import behavior, external archive retrieval, filesystem paths, cron or service-execution paths, firewall configuration records, administrator baselines, and downstream network-control telemetry.
· Public Wi-Fi gateway DNS-redirection activity should not be treated as directly covered by the current anchor-product detection logic unless the affected gateway or management platform, administrator activity, DNS configuration, DNS responses, wireless network, connected-user context, redirected destinations, and downstream authentication activity are separately mapped and correlated.
· Advantech WISE-6610 or WISE-6610P exposure, affected firmware 1.2.1_20251110, ordinary Basic Station or Node-RED administration, management authentication, act-argument use, configuration changes, command execution, service faults, or network activity should not by themselves be treated as proof that CVE-2026-79697 or CVE-2026-79698 was successfully exploited.
· MikroTik RouterOS exposure, vulnerable-version state, exposed SSH, WebFig or bandwidth-test service, ordinary SSH failures, ordinary configuration changes, or the absence of the RouterOS Flagged marker should not by themselves be treated as proof that any of the six September 2026 vulnerabilities was successfully exploited.
· The MikroTrick active-exploitation claim applies to the combined CVE-2026-67276 and CVE-2026-86060 chain documented by CERT Polska.
· CISA KEV status separately applies to CVE-2026-67277, CVE-2026-67279, and CVE-2026-86060. CVE-2026-67277 and CVE-2026-86060 were added on September 10, 2026, and CVE-2026-67279 was added on September 25, 2026 based on evidence of active exploitation. The CISA KEV updates should not be used to replace CVE-2026-67276 with CVE-2026-67277 or CVE-2026-67279 in the documented MikroTrick exploit chain.
· Ivanti Neurons for ITSM, Ivanti Sentry, or Ivanti Endpoint Manager Mobile vulnerable-version state, ordinary management-interface exposure, routine web/API traffic, normal authenticated administration, ordinary configuration changes, service faults, process activity, or managed-device actions should not by themselves be treated as proof that any of the ten September 8 Ivanti vulnerabilities was successfully exploited.
· Cloud-only identity, storage, backup, DNS, WAF, route, firewall, secret-access, service-account, or network-control events are not treated as compromise without upstream management-plane, endpoint, process, application, device, directory-service, service-control-plane, administrator, configuration, change-management, network, database, filesystem, or incident-response linkage.
· Scanner output, internet exposure, patch state, LDAP exposure, enabled Web Inbox functionality, Consul listener exposure, maximum CVSS score, CISA KEV status, benign WAF events, isolated failed requests, isolated binds, isolated administrative actions, ordinary update activity, ordinary database activity, ordinary DNS changes, ordinary wireless administration, ordinary archive activity, ordinary catalog activity, or ordinary replication activity are not treated as compromise confirmation.
· Historical non-anchor-product exploitation examples require engineering adaptation. Product-specific detections must be remapped to the affected platform's asset inventory, log schema, request paths, administrator and user model, directory-service or service-control model where applicable, execution or device telemetry, destination context, database records, DNS records, filesystem records, configuration records, service-catalog records, and change-management context.
Current Coverage Count
Directly Covered CVEs
12
CVEs Covered With Adaptation
417
Total CVEs
429
KEV Accounting Change From This Amendment
0 CISA KEV-listed CVE
Brocade Fabric OS CVE-2026-94575 through the applicable CVE-2026-94587 identifiers and CVE-2026-87659 through the applicable CVE-2026-87688 identifiers add 37 Coverage With Adaptation CVEs and 0 CISA Known Exploited Vulnerabilities Catalog entries to the report's overall KEV accounting. Available authoritative evidence reviewed for this amendment does not establish CISA KEV status for the 37 qualifying identifiers. The Directly Covered KEV / Exploited Anchor-Product Entries count remains 3 because Brocade Fabric OS remains Coverage With Adaptation rather than a UniFi OS / UniFi Connect anchor product.
Cloud Foundry UAA CVE-2026-59357 and CVE-2026-59358 add two Coverage With Adaptation CVEs and 0 CISA Known Exploited Vulnerabilities Catalog entries to the report's overall KEV accounting. Available authoritative evidence reviewed for this amendment does not establish CISA KEV status for either identifier. The Directly Covered KEV / Exploited Anchor-Product Entries count remains 3 because Cloud Foundry UAA remains Coverage With Adaptation rather than a UniFi OS / UniFi Connect anchor product.
Cisco's October 7, 2026 finalized advisory cohort adds 35 Coverage With Adaptation CVEs and 0 CISA Known Exploited Vulnerabilities Catalog entries to the report's overall KEV accounting. The cohort comprises 14 NX-OS and Nexus identifiers, five Application Policy Infrastructure Controller identifiers, eight License On-Prem identifiers, seven Meraki identifiers, and one Cisco Finesse identifier. Available authoritative evidence does not establish CISA KEV status for any of the 35 identifiers. The Directly Covered KEV / Exploited Anchor-Product Entries count remains 3 because all 35 Cisco October 7 identifiers are Coverage With Adaptation rather than UniFi OS / UniFi Connect anchor-product entries.
HPE Integrated Lights-Out 7 CVE-2026-79820 adds 0 CISA Known Exploited
Vulnerabilities Catalog entries to the report's overall KEV accounting. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for CVE-2026-79820. The Directly Covered KEV / Exploited Anchor-Product Entries count remains 3 because HPE Integrated Lights-Out 7 is Coverage With Adaptation, not an anchor product.
SolarWinds Observability Self-Hosted CVE-2026-28324 and CVE-2026-28325 add no CISA Known Exploited Vulnerabilities Catalog entries to the report's overall KEV accounting. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation for either identifier.
HPE Networking Analytics and Location Engine CVE-2026-76708 through CVE-2026-76717 add no CISA Known Exploited Vulnerabilities Catalog entries to the report's overall KEV accounting. Available authoritative evidence does not establish CISA KEV status for these ten identifiers.
HPE Networking ClearPass Policy Manager HPESBNW05158 adds 28 Coverage With Adaptation CVEs and 0 CISA Known Exploited Vulnerabilities Catalog entries to the report's overall KEV accounting. Available authoritative evidence does not establish CISA KEV status for the cohort.
HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 add nine Coverage With Adaptation CVEs and 0 CISA Known Exploited Vulnerabilities Catalog entries to the report's overall KEV accounting. Available authoritative evidence does not establish CISA KEV status for these nine identifiers.
Logsign SIEM CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926 add no CISA Known Exploited Vulnerabilities Catalog entries to the report's overall KEV accounting. The validated CISA ADP exploitation state is none for all three identifiers.
UTMStack CVE-2026-82039 through CVE-2026-82045 add no CISA Known Exploited Vulnerabilities Catalog entries to the report's overall KEV accounting. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for any of the seven identifiers.
SUSE Rancher CVE-2026-88804 and CVE-2026-88805 add no CISA Known Exploited Vulnerabilities Catalog entries to the report's overall KEV accounting. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation for either identifier.
SailPoint IdentityIQ CVE-2026-12342 adds no CISA Known Exploited Vulnerabilities Catalog entry to the report's overall KEV accounting. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation.
FreePBX CVE-2026-54675, CVE-2026-54710, and CVE-2026-75600 add no CISA Known Exploited Vulnerabilities Catalog entries to the report's overall KEV accounting. Available authoritative evidence does not establish CISA KEV status or confirmed in-the-wild exploitation for these three identifiers.
Directly Covered KEV / Exploited Anchor-Product Entries
3
Directly Covered Named Malware Families
1
Directly Covered Named Ransomware Families
1
Directly Covered Named Botnets
1
Directly Covered Named PhaaS Platforms
1
Directly Covered Named APT / Actor Groups
1
The current CVE coverage register is 429 total CVEs: 12 Directly Covered and 417 Covered With Adaptation.
Splunk Enterprise SVD-2026-1001 CVE-2026-76264 through CVE-2026-76280 and SVD-2026-1002 CVE-2026-76281 through CVE-2026-76285 are included as 22 Coverage With Adaptation entries. The Splunk cohort adds 0 Direct Coverage CVEs and 0 CISA KEV-listed CVEs, increasing Coverage With Adaptation from 395 to 417 and the total CVE register from 407 to 429. The Directly Covered CVE count remains 12, and the Directly Covered KEV / Exploited Anchor-Product Entry count remains 3 because Splunk Enterprise is an adapted-coverage platform rather than a UniFi OS / UniFi Connect anchor product.
Brocade Fabric OS CVE-2026-94575 through the applicable CVE-2026-94587 identifiers and CVE-2026-87659 through the applicable CVE-2026-87688 identifiers are included as 37 Coverage With Adaptation entries. The Directly Covered CVE count remains 12, the current register is 12 Direct / 417 Coverage With Adaptation / 429 total, and the Brocade Fabric OS cohort adds 0 CISA KEV-listed CVEs. The Directly Covered KEV / Exploited Anchor-Product Entry count remains 3 because Brocade Fabric OS remains an adapted-coverage platform rather than a UniFi OS / UniFi Connect anchor product.
Cloud Foundry UAA CVE-2026-59357 and CVE-2026-59358 are included as two Coverage With Adaptation entries. The Directly Covered CVE count remains 12, the current register is 12 Direct / 417 Coverage With Adaptation / 429 total, and the Cloud Foundry UAA cohort adds 0 CISA KEV-listed CVEs. The Directly Covered KEV / Exploited Anchor-Product Entry count remains 3 because Cloud Foundry UAA remains an adapted-coverage platform rather than a UniFi OS / UniFi Connect anchor product.
Cisco's October 7, 2026 finalized advisory cohort is included as 35 Coverage With Adaptation entries. The Directly Covered CVE count remains 12, the current register is 12 Direct / 417 Coverage With Adaptation / 429 total, and the Cisco October 7 cohort adds 0 CISA KEV-listed CVEs. The Directly Covered KEV / Exploited Anchor-Product Entry count remains unchanged because NX-OS, Nexus, Application Policy Infrastructure Controller, License On-Prem, Meraki, and Finesse remain adapted-coverage platforms rather than UniFi OS / UniFi Connect anchor products.
Arista CloudVision Portal, CloudVision Sensor, and CloudVision-CUE on-premises CVE-2026-101149 through CVE-2026-101158 and CVE-2026-102155 through CVE-2026-102161 are included as 17 Coverage With Adaptation entries. The Directly Covered CVE count remains 12, the current register is 12 Direct / 417 Coverage With Adaptation / 429 total, and the Arista CloudVision cohort adds 0 CISA KEV-listed CVEs. The Directly Covered KEV / Exploited Anchor-Product Entry count remains unchanged because the Arista CloudVision platforms remain adapted-coverage platforms rather than UniFi OS / UniFi Connect anchor products.
Zammad CVE-2026-102489 and CVE-2026-102490 are included as two Coverage With Adaptation entries. The Directly Covered CVE count remains 12, and the current register remains 12 Direct / 417 Coverage With Adaptation / 429 total. CISA added both Zammad vulnerabilities to the Known Exploited Vulnerabilities Catalog on October 2, 2026, increasing the report's overall KEV accounting by two entries. The Directly Covered KEV / Exploited Anchor-Product Entry count remains 3 because Zammad remains an adapted-coverage platform rather than a UniFi OS / UniFi Connect anchor product.
Fortinet FortiMail CVE-2026-104286 is included as one Coverage With Adaptation entry.
The Directly Covered CVE count remains 12, the current register is 12 Direct / 417 Coverage With Adaptation / 429 total, and the FortiMail addition contributes 1 CISA KEV-listed CVE to the report's overall KEV accounting. The Directly Covered KEV / Exploited Anchor-Product Entry count remains 3 because FortiMail remains an adapted-coverage platform rather than a UniFi OS / UniFi Connect anchor product.
SolarWinds Observability Self-Hosted CVE-2026-28324 and CVE-2026-28325 are included as two Coverage With Adaptation entries. The Directly Covered CVE count remains 12, and the two SolarWinds Observability additions add 0 CISA KEV-listed CVEs.
HPE Integrated Lights-Out 7 CVE-2026-79820 is included as one Coverage With Adaptation entry. The Directly Covered CVE count remains 12, the current register is 12 Direct / 417 Coverage With Adaptation / 429 total, the Directly Covered KEV / Exploited Anchor-Product Entry count remains 3, and CVE-2026-79820 adds 0 CISA KEV-listed CVEs.
HPE Networking Analytics and Location Engine CVE-2026-76708 through CVE-2026-76717 are included as ten Coverage With Adaptation entries. The Directly Covered CVE count remains 12, the Directly Covered KEV / Exploited Anchor-Product Entry count remains 3, and the HPE ALE cohort adds 0 CISA KEV-listed CVEs.
Logsign SIEM CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926 are included as three Coverage With Adaptation entries. The Directly Covered CVE count remains 12, the current register is 12 Direct / 417 Coverage With Adaptation / 429 total, and the Logsign cohort adds 0 CISA KEV-listed CVEs. The validated CISA ADP exploitation state is none for all three identifiers.
UTMStack CVE-2026-82039 through CVE-2026-82045 are included as seven Coverage With Adaptation entries. The Directly Covered CVE count remains 12, the current register is 12 Direct / 417 Coverage With Adaptation / 429 total, and the UTMStack cohort adds 0 CISA KEV-listed CVEs.
SUSE Rancher CVE-2026-88804 and CVE-2026-88805 are included as two Coverage With Adaptation entries. SailPoint IdentityIQ CVE-2026-12342 is included as one Coverage With Adaptation entry. FreePBX CVE-2026-54675, CVE-2026-54710, and CVE-2026-75600 are included as three Coverage With Adaptation entries. Together, these six additions are reflected in the current 417 Coverage With Adaptation / 429 total register while the Directly Covered CVE count remains 12.
The six additions add 0 CISA KEV-listed CVEs, so the Directly Covered KEV / Exploited Anchor-Product Entry count remains unchanged.
CVE-2026-93952 remains Coverage With Adaptation. Its coverage classification is unchanged and it is reflected in the current 12 Direct / 417 Coverage With Adaptation / 429 total register. CISA KEV accounting includes CVE-2026-93952 because CISA added the identifier on September 22, 2026, with a September 25, 2026 remediation due date.
CVE-2026-93616 remains Coverage With Adaptation. Its coverage classification is unchanged and it is reflected in the current 12 Direct / 417 Coverage With Adaptation / 429 total register. CISA KEV accounting includes CVE-2026-93616 because CISA added the identifier on September 22, 2026, with a September 25, 2026 remediation due date.
CVE-2026-5430 remains Coverage With Adaptation. Its coverage classification is unchanged and it is reflected in the current 12 Direct / 417 Coverage With Adaptation / 429 total register. CISA KEV accounting includes CVE-2026-5430 because CISA added the identifier on September 24, 2026, based on evidence of active exploitation. The Directly Covered KEV / Exploited Anchor-Product Entry count remains 3 because WSO2 remains an adapted-coverage platform.
Primary Behavior Families Covered
· JWT authentication bypass, unsupported-algorithm token acceptance, unauthorized API-management access, and administrative-account takeover when locally adapted.
· Hard-coded JWT signing-key abuse, forged bearer-token acceptance, and unauthenticated PBX API command execution when locally adapted.
· Analyst-session hijacking and browser-context abuse when locally adapted.
· Reverse-proxy, identity-provider, RBAC, role, method, route, and header authorization failures when locally adapted.
· Security-monitoring record creation, overwrite, tagging, fabrication, and evidence-integrity loss when locally adapted.
· Authenticated archive path traversal, arbitrary file write, and filename-driven command execution when locally adapted.
· Backend server-side request forgery using elevated service credentials when locally adapted.
· Default or weak administrator credentials, cookie-signing secrets, and identity-provider certificate-validation failures when locally adapted.
· Management-plane exploit-path access.
· Authentication-bypass and protected-functionality reachability.
· Authentication-state and session-identity mismatch leading to unauthorized privileged authority.
· Public API session-token persistence after logout and continued post-logout token use when locally adapted.
· Unauthenticated public UI setting manipulation and browser-context script execution affecting management login workflows when locally adapted.
· Unauthenticated identity-governance web-service API input reaching server-side execution when locally adapted.
· Authenticated PBX file-write, PHP file-inclusion, and GraphQL API host-command injection behavior when locally adapted.
· FreeIPA administrative-privilege takeover through attacker-controlled Kerberos-principal and administrators-group state.
· Identity-provider configuration pre-authorization processing, server-process environment disclosure, and resource-exhaustion denial of service when locally adapted.
· Directory-service authorization bypass, privileged directory-object manipulation, and replication-control abuse.
· Service-catalog authorization bypass, catalog-object manipulation, and node-identity takeover when locally adapted.
· Service-mesh authorization bypass and unintended service reachability when locally adapted.
· Native RPC resource-exhaustion and control-plane availability effects when locally adapted.
· Improper access-control reachability.
· Traversal-like request behavior.
· Arbitrary file write, arbitrary file delete, and path escape through management or upload functions when locally adapted.
· Local SUID-root wrapper abuse and privilege escalation when locally adapted.
· Recoverable privileged credentials, hard-coded recovery material, and REST service-account credential exposure when locally adapted.
· Patch-signature verification bypass and privileged installer abuse when locally adapted.
· Crafted application, API, email-processing, PESI, GIM, REST, SNMP, CGI, or management-interface input behavior when locally adapted.
· SQL-injection, arbitrary SQL execution, abnormal database-interaction, and unauthorized management-data-access behavior when locally adapted.
· Server-side request forgery and arbitrary device-originated or server-originated network-request behavior when locally adapted.
· Backup-configuration argument injection when locally adapted.
· External archive or package retrieval by management-plane services.
· Update or package-path abuse.
· Application-host, email-security-appliance, network-device, Guardium appliance, or management-service command injection.
· LAN-based unauthenticated network-device management-plane exploitation when locally adapted.
· Server-side deserialization leading to remote code execution when locally adapted.
· Authenticated missing-authorization paths leading to server-side execution or administrator privilege when locally adapted.
· Unauthenticated administrative-access paths in enterprise management products when locally adapted.
· Service-context command execution.
· Privileged device, sudo-assisted, SUID-assisted, or root-context activity.
· Administrator, API-token, ACL-token, privileged-directory-identity, service-identity, and device-trust manipulation.
· Configuration export and management-data access.
· Directory-service configuration and privileged-object access.
· Routing, switching, segmentation, firewall, VPN, DNS, wireless, service-discovery, service-mesh, and downstream network-control change.
· DNS resolver or forwarding manipulation.
· Public Wi-Fi gateway traffic redirection.
· Microsoft 365 credential-harvesting exposure following gateway-level DNS manipulation when locally adapted.
· Outbound communication and tool-staging behavior.
· Internal discovery and management-interface reconnaissance.
· Conditional cloud-control-plane activity near suspected management-platform compromise.
· Appliance-focused intrusion tradecraft when locally adapted.
· Proxy, botnet, or tunnel-like infrastructure abuse behavior when locally adapted.
· Ransomware pre-access or infrastructure-staging behavior when locally adapted.
· State-aligned edge-infrastructure pre-positioning tradecraft when locally adapted.
Coverage Qualification
Splunk Enterprise CVE-2026-76264 through CVE-2026-76285 are included only as Coverage With Adaptation because reliable attribution depends on affected Splunk Enterprise components, release branches, management and REST API exposure, administrator and application permissions, Patroni REST API configuration and reachability, search-job and SPL2 functionality, Secure Gateway applicability, package-upgrade activity, process and command execution, filesystem and configuration evidence, security-monitoring integrity, remediation state, and incident-response findings not represented by the UniFi OS / UniFi Connect anchor-product detection logic.
The two Splunk advisories document separate vulnerability groups rather than one mandatory exploit chain. Vulnerability presence, advisory publication, or a high CVSS score should not be treated as proof of successful exploitation. The applicable corrected Enterprise releases are 10.4.3, 10.2.7, 10.0.10, and 9.4.15, with CVE-specific additional remediation required for CVE-2026-76264, CVE-2026-76265, CVE-2026-76272, and CVE-2026-76280.
ClingSTUN is included as Coverage With Adaptation campaign context rather than as a new standalone malware-report requirement. FortiGuard Labs documents exploitation of known vulnerabilities affecting internet-facing routers and IoT devices followed by Linux backdoor deployment, startup-file persistence, termination of competing or interfering processes, watchdog manipulation, remote command execution, self-propagation, and use of compromised devices as back-connect proxy infrastructure.
The campaign's use of public STUN services supports discovery of externally mapped address and port information and maintenance of NAT bindings for proxy communications. Public STUN infrastructure should not by itself be treated as malicious. Reliable attribution depends on affected-device and exposure validation, exploit-path evidence where available, process and filesystem telemetry where supported by the device, startup-file or persistence evidence, unusual or role-inconsistent UDP and STUN activity, proxy or tunnel-like communication, internal discovery or propagation behavior, remediation state, and incident-response findings beyond the UniFi OS and UniFi Connect direct-coverage anchor model.
ClingSTUN remains Coverage With Adaptation because the report already provides durable behavioral coverage for management-plane exploitation, privileged or device-level execution, outbound communication, appliance-focused intrusion activity, tunnel-like or proxy behavior, internal discovery, device enumeration, and role-inconsistent external communication. ClingSTUN does not add a new CVE entry and does not change the current CVE coverage register.
HPE Integrated Lights-Out 7 CVE-2026-79820 is included only as Coverage With Adaptation because reliable attribution depends on HPE iLO 7-specific asset and firmware inventory, management-interface reachability, authentication and session context, administrator activity, configuration and firmware state, managed-server activity, network behavior, remediation state, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The vulnerability aligns with the report's existing authentication, access-control, management-plane, administrator-state, configuration, privileged-control, network-behavior, and downstream infrastructure-control model. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for CVE-2026-79820.
HPE Networking Analytics and Location Engine CVE-2026-76708 through CVE-2026-76717 are included only as Coverage With Adaptation because reliable attribution depends on ALE-specific asset and version inventory, default-credential state, management-interface and API exposure, authentication and session context, maintenance-restore activity, filesystem and file-write evidence, socket and service telemetry, process and root-context evidence, network-path and man-in-the-middle conditions where applicable, sensitive-data access, configuration state, and downstream effects not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The cohort aligns with the report's existing authentication, access-control, sensitive-information, file-write, data-injection, service-availability, privileged-execution, root-control, credential, configuration, and downstream behavior model. ALE 5.0.0.0 and earlier are affected; ALE 5.1.0.0 is corrected. HPE reported no known public discussion or exploit code targeting the package at publication, and available authoritative evidence does not establish CISA KEV status for the ten identifiers.
Kiteworks Core CVE-2026-102132 is included only as Coverage With Adaptation because reliable attribution depends on Kiteworks-specific asset and version inventory, delegated-administrator identity and assigned-permission state, administrative import activity, privileged integration-credential creation and use, administrator-role and privilege changes, configuration and audit records, managed-content and connector context, downstream activity, remediation state, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The vulnerability aligns with the report's existing authenticated management-plane access, improper access control, authorization-boundary failure, privileged-credential creation, administrator-role escalation, configuration-change, privileged-object, and downstream behavior families. Kiteworks Core versions before 9.5.1 are affected; version 9.5.1 is the documented corrected boundary. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for CVE-2026-102132.
The 37 IBM Guardium Data Protection CVEs are included only as Coverage With Adaptation because reliable attribution depends on Guardium-specific appliance role, affected function, authentication and authorization state, local-versus-remote prerequisites, process, SUID, file, credential, database, REST, PESI, GIM, SNMP, web, certificate, configuration, Central Manager, Collector, and downstream telemetry that is not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The cohort aligns with the report's existing management-access, authentication, authorization, process, privileged-execution, file, credential, database, configuration, service-impact, persistence, outbound, and downstream behavior families, but each identifier retains its own documented prerequisite and weakness.
Guardium Data Protection 12.2 is affected. IBM directs customers to the 12.0p233 update. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for the cohort.
kcp CVE-2026-61682 is included only as Coverage With Adaptation because reliable attribution depends on kcp-specific front-proxy, shard, workspace, request-header authentication, X-Remote-* identity propagation, tenant identity, RBAC, delegated-identity, scope, secret, APIExport, APIBinding, LogicalCluster, configuration, and downstream telemetry not represented by the current anchor-product detection logic.
The vulnerability aligns with the report's authentication, authorization, identity, privilege, secret-access, policy, configuration, tenant-boundary, and downstream behavior model.
Affected versions are earlier than 0.31.4 and 0.32.0 through 0.32.1. Fixed versions are 0.31.4 and 0.32.2. External proxy stripping of inbound X-Remote-* identity headers is a mitigation rather than complete remediation. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status.
Check Point Security Management CVE-2026-93616 is included only as Coverage With Adaptation because reliable attribution depends on Check Point-specific Security Management asset and version inventory, management-web service exposure, HTTP request and path telemetry, file-upload and script-execution evidence, Java class-loading and process telemetry, filesystem state, administrator and security-policy activity, managed-gateway and downstream firewall effects, remediation state, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The vulnerability aligns with the report's existing management-access, pre-authentication exploitation, traversal-like access, application-host execution, privileged-process, administrator-state, configuration and security-policy change, outbound communication, and downstream network-control behavior families. Check Point-confirmed limited exploitation increases urgency but does not change the Coverage With Adaptation classification or establish compromise of a specific local deployment. CISA added CVE-2026-93616 to the Known Exploited Vulnerabilities Catalog on September 22, 2026, with a remediation due date of September 25, 2026.
SUSE Rancher CVE-2026-88804 and CVE-2026-88805 are included only as Coverage With Adaptation because reliable attribution depends on Rancher-specific asset and version inventory, public and authenticated API exposure, public UI settings, browser and administrator-session state, public API session-token issuance and reuse, logout and revocation events, identity-provider and OIDC configuration, RBAC and cluster-management activity, downstream managed-cluster state, remediation state, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The two identifiers align with the report's existing management-plane access, authentication and session trust, administrator-state, configuration, privileged-object, downstream-control, and post-compromise behavior families, but they retain distinct product-specific prerequisites and evidence requirements.
SailPoint IdentityIQ CVE-2026-12342 is included only as Coverage With Adaptation because reliable attribution depends on IdentityIQ-specific asset and version inventory, web-service API reachability, request context where available, application and service process activity, identity-governance workflow state, role and entitlement changes, connector and configuration evidence, filesystem and network behavior, remediation state, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The vulnerability aligns with the report's existing unauthenticated management/API access, server-side execution, process, filesystem, configuration, credential, identity-state, outbound-communication, and downstream behavior families.
FreePBX CVE-2026-54675, CVE-2026-54710, and CVE-2026-75600 are included only as Coverage With Adaptation because reliable attribution depends on FreePBX-specific asset, module, and version inventory, authenticated identity and authorization context, Soundlang, Superfecta, GraphQL and API activity, file creation and modification, PHP and web-server process activity, Asterisk process and child-process evidence, command execution, telephony configuration, network behavior, remediation state, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The three identifiers align with the report's existing authenticated management-plane access, arbitrary file write, server-side code execution, command execution, process, filesystem, configuration, credential, outbound-communication, and downstream communications behavior families, but they should not be represented as one mandatory exploit chain.
Check Point Security Management and Log Server CVE-2026-91843 is included only as Coverage With Adaptation because reliable attribution depends on Check Point-specific management or Log Server asset and version inventory, deployment context, login and authentication telemetry, FWM and related process evidence, root-context execution, administrator-session and configuration state, managed-gateway or policy effects, remediation state, network activity, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The vulnerability aligns with the report's management-plane, authentication-boundary, service-context execution, root-control, administrator-state, configuration-change, and downstream security-control behavior model.
Logsign SIEM CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926 are included only as Coverage With Adaptation because reliable attribution depends on Logsign-specific asset and version inventory, management and application-path reachability, authentication and privilege context, request and path context where available, process and child-process execution, filesystem and configuration changes, credential and secret state, administrator activity, connector and ingestion changes, alerting and logging continuity, security-monitoring record integrity, network behavior, remediation state, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The three identifiers align with the report's existing authentication-boundary, management-plane access, path-traversal, code-injection, service-context execution, process, filesystem, credential, configuration, administrator-state, outbound-communication, monitoring-integrity, and downstream behavior families. They should not be represented as one mandatory exploit chain.
Logsign SIEM versions 6.4.101 through versions before 6.4.117 are affected. Logsign SIEM 6.4.117 or later is the documented correction boundary. The Logsign cohort adds 0 CISA KEV-listed CVEs, and the validated CISA ADP exploitation state is none for CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926.
Zyxel GS1900 CVE-2026-7273 is included only as Coverage With Adaptation because reliable attribution depends on Zyxel-specific model and firmware inventory, LAN and management-interface reachability, source-network context, HTTP and CGI request evidence where available, device and process behavior, command-execution evidence, administrator and configuration state, outbound network activity, switching and downstream network-control effects, remediation state, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The vulnerability aligns with the report's management-plane access, crafted HTTP request, command-execution, privileged-device, configuration-change, outbound-communication, switching, and downstream network-control behavior model. Zyxel documents the attack prerequisite as LAN-based and unauthenticated. CISA KEV status materially increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification or establish compromise of a specific local deployment.
WSO2 CVE-2026-5430 is included only as Coverage With Adaptation because reliable attribution depends on WSO2-specific product and affected-version inventory, API and management-interface exposure, JWT signing and validation behavior, authentication and administrator-session telemetry, API and gateway request activity, administrator and configuration state, backend-service access, credential or sensitive-data access where observable, network activity, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The vulnerability aligns with the report's authentication-bypass, protected-functionality, privileged-object, management-control-plane, administrator-state, configuration-change, and downstream-access behavior model. CISA added CVE-2026-5430 to the Known Exploited Vulnerabilities Catalog on September 24, 2026, based on evidence of active exploitation. The KEV designation increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification or establish compromise of a specific local deployment.
Issabel Framework CVE-2026-89026 is included only as Coverage With Adaptation because reliable attribution depends on Issabel-specific asset and version inventory, pbxapi exposure, JWT signing and bearer-token behavior, manager-originate request context, Asterisk service and process telemetry, operating-system command execution, filesystem and configuration activity, network behavior, telephony-service effects, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The vulnerability aligns with the report's authentication-bypass and forged-token, management/API, service-context execution, application-host compromise, configuration-change, outbound-communication, and downstream communications behavior model.
Fortinet FortiMail CVE-2026-104286 is included only as Coverage With Adaptation because reliable attribution depends on FortiMail-specific asset and version inventory, HTTP and HTTPS interface exposure, request and path activity, filesystem and file-write evidence, configuration state, administrator activity, process and service behavior where available, network communication, email-security policy and mail-system state, remediation state, and incident-response findings not represented by the current UniFi OS / UniFi Connect anchor-product detection logic.
The vulnerability aligns with the report's traversal-like request, arbitrary-file-write, management-plane, filesystem, configuration-change, service-context, outbound-communication, and downstream email-security behavior model. CISA KEV status establishes known exploitation and increases remediation and retrospective-hunting urgency without converting the vulnerability to Direct Coverage or establishing compromise of a specific local appliance.
Cisco Secure Email Gateway CVE-2026-76461 is included only as Coverage With Adaptation because reliable attribution depends on Secure Email Gateway-specific asset and affected-version inventory, Cisco AsyncOS email-processing and message context, mail_logs, database activity where available, process and root-context telemetry, filesystem and configuration evidence, external network and firewall telemetry, administrator-state evidence, and incident-response findings not represented by the current anchor-product detection logic.
CISA Malcolm CVE-2026-90443 through CVE-2026-90457 are included only as Coverage With Adaptation because reliable attribution depends on Malcolm-specific product and version inventory, deployment mode, analyst identities and sessions, application routes and methods, request-header context, RBAC and role state, reverse-proxy and identity-provider configuration, certificate-validation state, signing-secret and administrator-secret provenance, upload and archive behavior, backend service requests, container and service-process activity, security-record integrity, configuration state, and incident-response evidence not represented by the current anchor-product detection logic.
Traefik CVE-2026-88004, CVE-2026-88007, CVE-2026-88008, CVE-2026-88009, and CVE-2026-88011 are included only as Coverage With Adaptation because reliable attribution depends on Traefik-specific version inventory, affected protocol and entrypoint state, raw and normalized request context, header and trailer behavior, ForwardAuth and middleware decisions, route selection, backend connection identity, downstream application interpretation, and product-specific security telemetry not represented by the current anchor-product detection logic.
Schneider Electric EcoStruxure IT Data Center Expert CVE-2026-19233 and CVE-2026-8044 are included only as Coverage With Adaptation because reliable attribution depends on product-specific version inventory, privileged-user and session context, server-endpoint or backup-configuration activity, server-side destination evidence, process and command execution, server-data access, filesystem or configuration evidence, and infrastructure-management context not represented by the current anchor-product detection logic.
HashiCorp Consul CVE-2026-88021, CVE-2026-87107, CVE-2026-87106, and CVE-2026-87090 are included only as Coverage With Adaptation because reliable attribution depends on Consul-specific product and version inventory, ACL policy and token scope, catalog state, node and service identities, peering, Connect intentions, SPIFFE identities, generated Envoy RBAC state, RPC and mTLS context, memory and process telemetry, and downstream service-discovery evidence not represented by the current anchor-product detection logic.
Executive Exposure Statement
Enterprise management control-plane compromise is an executive exposure issue because the affected systems may sit between business operations and the administrative, network, security, application, identity, infrastructure-monitoring, service-discovery, or service-mesh controls that enable connectivity, segmentation, routing, switching, VPN access, DNS behavior, wireless operations, public Wi-Fi access, recorder visibility, storage access, application-host trust, identity services, directory-based authentication and authorization, enterprise service-management workflows, managed-device control, application discovery, service routing, and site continuity.
Leadership should treat the risk as unresolved until the organization can prove that vulnerable systems were updated, exposed management interfaces and directory listeners were controlled, suspected pre-patch activity was reviewed, administrator and privileged-directory trust was validated, configuration and directory-object integrity were confirmed, service-catalog and service-mesh integrity were confirmed where applicable, downstream dependencies were assessed, and post-remediation activity did not continue.
The strongest business assurance comes from behavior-led detection coverage that can show whether suspicious access remained exposure noise or became command execution, privileged activity, unauthorized database or directory access, privileged identity takeover, directory-object manipulation, service-catalog manipulation, service-identity takeover, service-mesh authorization bypass, DNS manipulation, control-plane manipulation, workflow manipulation, managed-device action, or downstream infrastructure impact.
Related management-platform, firewall-appliance, device-control, application-host, collaboration-server, gateway-control, identity-control, directory-service, IT-service-management, endpoint-management, infrastructure-monitoring, service-discovery, and service-mesh issues should be handled through adapted coverage rather than expanded direct-coverage claims unless local telemetry, product mappings, server or device evidence, directory-service evidence, service-control evidence, network evidence, database evidence, filesystem evidence, configuration evidence, and incident evidence support the same validated behavior sequence.
Named malware or APT attribution should remain outside the direct executive coverage claim set unless validated source reporting or incident-specific evidence supports it.
S40 — References
The following references support the enterprise management control-plane compromise scope, anchored in the UniFi OS and UniFi Connect direct-coverage model; the AiSOC CVE-2026-103053 through CVE-2026-103057 Coverage With Adaptation mappings, including response-action API authentication failure, authenticated MSSP portfolio tenant authorization failure, hard-coded JWT verification-secret abuse in the realtime service, authenticated CrowdStrike Real Time Response command injection, missing authentication on realtime internal endpoints, CVE-specific affected-version applicability, AiSOC 12.0.0 remediation, and 0-change CISA KEV accounting; Kiteworks Core CVE-2026-102132 Coverage With Adaptation mapping, including improper access control in the administrative import function, delegated-administrator privilege escalation through unauthorized creation of a privileged integration credential, escalation to full system-administrator privileges, the affected-version boundary before 9.5.1, the 9.5.1 corrected boundary, and 0-change CISA KEV accounting; the SUSE Rancher CVE-2026-88804 and CVE-2026-88805 Coverage With Adaptation mappings, including unauthenticated modification of public UI settings, login-page stored-script execution, potential local administrator bootstrap-password or active-session exposure, public API session-token persistence after logout, OIDC-backed session applicability, applicable Rancher fixed-release boundaries, and 0-change CISA KEV accounting; the SailPoint IdentityIQ CVE-2026-12342 Coverage With Adaptation mapping, unauthenticated web-service API improper-input-validation behavior leading to remote code execution, affected IdentityIQ 8.3 through 8.3p5, 8.4 through 8.4p4, and 8.5 through 8.5p2 boundaries, and 0-change CISA KEV accounting; the FreePBX CVE-2026-54675, CVE-2026-54710, and CVE-2026-75600 Coverage With Adaptation mappings, authenticated Soundlang arbitrary-file-write-to-RCE behavior, authenticated Superfecta unsafe PHP file inclusion, authenticated GraphQL API generatedocs host-command injection, applicable fixed module versions, and 0-change CISA KEV accounting; the HPE
Networking Analytics and Location Engine CVE-2026-76708 through CVE-2026-76717
Coverage With Adaptation mapping, ALE 5.0.0.0-and-earlier affected boundary,
ALE 5.1.0.0 corrected release, default-credential, arbitrary-file-write,
information-disclosure, socket-data-injection, unauthorized-access,
denial-of-service, authenticated root-filesystem-access, authenticated
root-command-execution, documented man-in-the-middle root-code-execution, API
password-hash-disclosure behaviors, and 0-change CISA KEV accounting; the HPE
Integrated Lights-Out 7 CVE-2026-79820 Coverage With Adaptation mapping,
remote user-validation failure affecting the iLO management control plane,
affected iLO 7 firmware applicability, HPE remediation guidance, and 0-change
CISA KEV accounting; the HPE Networking AOS-Switch CVE-2026-76741 through CVE-2026-76749 Coverage With Adaptation mappings, including management-interface authentication bypass, remote and adjacent memory-corruption and buffer-overflow conditions, code execution, information disclosure, authenticated API privilege escalation, denial-of-service behavior, the AOS-S 16.11.0031-and-earlier affected boundary, the AOS-S 16.11.0032 corrected boundary, and 0-change CISA KEV accounting; the 28-vulnerability HPE Networking ClearPass Policy Manager HPESBNW05158 Coverage With Adaptation cohort, including remote code execution, authentication bypass, SQL injection, command execution, privilege escalation, access-control and client-software compromise paths, affected ClearPass Policy Manager 6.14.0-and-earlier and 6.11.15-and-earlier applicability, HPE remediation guidance, and 0-change CISA KEV accounting; the Arista CloudVision Portal and CloudVision-CUE on-premises CVE-2026-101149 through CVE-2026-101158 and CVE-2026-102155 through CVE-2026-102161 Coverage With Adaptation cohort, including OIDC and SSO trust failures, authentication-material redirection, stored cross-site scripting and session-hijacking paths, path traversal and unauthorized data access, server-side request forgery, missing authentication for internal backend functionality, XML external entity injection, insecure direct object reference, SQL injection, operating-system command injection, source-address trust and authentication-bypass behavior, LDAP injection, affected CloudVision Portal, CloudVision Sensor, and CloudVision-CUE on-premises applicability, Arista remediation guidance, Arista's statement that it is not aware of malicious exploitation in customer deployments, and 0-change CISA KEV accounting; the VeloCloud Orchestrator On-Prem CVE-2026-93952 Coverage With Adaptation mapping, affected and fixed release boundaries, certificate-based Edge-to-VCO exposure prerequisites, Arista-confirmed active exploitation, VCO host and managed-data consequence, and +1 CISA KEV accounting change; the Check Point Security Management CVE-2026-93616 Coverage With Adaptation mapping, affected release boundaries, pre-authentication path traversal, arbitrary-path script execution, Java class loading, Check Point-confirmed limited exploitation, sk1000171 remediation and response guidance, and +1 CISA KEV accounting change; the Zyxel GS1900 CVE-2026-7273 Coverage With Adaptation and CISA KEV mapping, LAN-based unauthenticated management-plane prerequisite, CGI stack-based buffer-overflow behavior, affected model and firmware boundaries, patched 2.90 builds, and potential OS-command-execution consequence; the kcp CVE-2026-61682 Coverage With Adaptation mapping, affected and fixed version boundaries, identity-header trust failure, and cross-workspace authorization behavior; the IBM Guardium Data Protection 37-CVE Coverage With Adaptation mapping, Guardium Data Protection 12.2 affected boundary, 12.0p233 remediation, and Guardium appliance, GIM, REST, PESI, SNMP, file, credential, database, authorization, web, certificate, patch, and privileged-execution behaviors; the Check Point Security Management and Log Server CVE-2026-91843 Coverage With Adaptation mapping, current non-exploitation statement, and LivePatch remediation guidance; the HP Advance CVE-2026-89082, CVE-2026-89083, and CVE-2026-89084 Coverage With Adaptation mappings; the Dell ObjectScale CVE-2026-70416 Coverage With Adaptation mapping; the SolarWinds Access Rights Manager CVE-2026-28326 Coverage With Adaptation and ARM 2026.2.1 remediation mapping; the Logsign SIEM CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926 Coverage With Adaptation mappings, 6.4.101-through-before-6.4.117 affected range, 6.4.117-or-later correction boundary, default-credential, path-traversal, and code-injection behaviors, security-monitoring evidence-integrity consequences, and 0-change CISA KEV accounting; the UTMStack CVE-2026-82039 through CVE-2026-82045 Coverage With Adaptation mappings, including the UTMStack-before-11.2.16 affected-version boundary and the UTMStack 11.2.16 corrected-version boundary; authenticated SQL injection affecting asset-group search and permitting database-impacting activity; authenticated identity-provider server-side request forgery permitting access to internal services or cloud instance-metadata services; missing authorization on the STOMP command WebSocket permitting authenticated users to deliver operating-system commands to connected agents; misuse of the internal-key authentication path to obtain access to privileged APIs without normal user-account or JWT authentication; unauthenticated password-reset account enumeration; authenticated server-side request forgery through the PDF-reporting service permitting access to internal resources or cloud instance-metadata services; authenticated JPQL injection capable of exposing sensitive entity and credential records; and 0-change CISA KEV accounting; the SolarWinds Observability Self-Hosted CVE-2026-28324 and CVE-2026-28325 Coverage With Adaptation mappings, SolarWinds Observability Self-Hosted 2026.2.3 remediation boundary, configuration-dependent unauthenticated remote-code-execution prerequisites, insufficient-integrity-check and untrusted-deserialization behavior, and 0-change CISA KEV accounting; the WSO2 CVE-2026-5430 Coverage With Adaptation, active-exploitation, and CISA KEV mapping; the Issabel Framework CVE-2026-89026 Coverage With Adaptation and active-exploitation mapping; the September 16, 2026 Cisco ISE / ISE-PIC 42-CVE Coverage With Adaptation mapping, including the CVE-2026-76460 CISA KEV status; the 12-CVE Cisco Secure Firewall Management Center September 16 Coverage With Adaptation mapping; the six-CVE Cisco Nexus Dashboard September 16 hardening mapping; the Cisco BroadWorks CommPilot CVE-2026-76438 mapping; the Cisco ThousandEyes Virtual Appliance CVE-2026-20350 mapping; the Fortinet FortiMail CVE-2026-104286 Coverage With Adaptation and CISA KEV mapping, including unauthenticated HTTP and HTTPS path traversal, arbitrary file write on the underlying system, FortiMail-specific asset and exposure validation, active-exploitation state, and +1 CISA KEV accounting change; the Cisco Secure Email Gateway and Cisco Secure Email and Web Manager CVE-2026-76440, CVE-2026-76441, CVE-2026-20353, CVE-2026-76443, and CVE-2026-76442 hardening Coverage With Adaptation mappings; the Cisco Secure Email Gateway CVE-2026-76461 Coverage With Adaptation and KEV mapping; the CISA Malcolm CVE-2026-90443 through CVE-2026-90457 Coverage With Adaptation mappings; the Traefik CVE-2026-88004, CVE-2026-88007, CVE-2026-88008, CVE-2026-88009, and CVE-2026-88011 Coverage With Adaptation mappings; the HashiCorp Consul CVE-2026-88021, CVE-2026-87107, CVE-2026-87106, and CVE-2026-87090 Coverage With Adaptation mappings; the Schneider Electric EcoStruxure IT Data Center Expert CVE-2026-19233 and CVE-2026-8044 Coverage With Adaptation mappings; the MikroTik RouterOS six-CVE and MikroTrick mapping and current KEV state; the Cisco Secure Firewall Management Center CVE-2026-20079 Coverage With Adaptation and KEV mapping; the Cisco Talos Secure FMC exploitation and post-compromise campaign context; the ten Ivanti September 8 Coverage With Adaptation mappings for Neurons for ITSM, Sentry, and Endpoint Manager Mobile; the FreeIPA CVE-2026-76578 and CVE-2026-79678 Coverage With Adaptation mappings; the Red Hat 389 Directory Server and Cockpit 389 Console CVE-2026-76560, CVE-2026-19843, CVE-2026-19404, CVE-2026-18922, CVE-2026-18651, CVE-2026-18355, and CVE-2026-11770 Coverage With Adaptation mappings; the NEC UNIVERGE IX-R/IX-V CVE-2026-16876, ASUS Control Center Enterprise CVE-2026-75754, SonicWall Network Security Manager On-Prem CVE-2026-78327, CVE-2026-78328, and CVE-2026-81939 mappings; the Advantech WISE-6610 and WISE-6610P CVE-2026-79697 and CVE-2026-79698 mapping; the Zammad CVE-2026-102489 and CVE-2026-102490 Coverage With Adaptation mappings, including DIVD-reported exploitation during the September 21, 2026 breach, CVE-2026-102489 remote-code-execution behavior in the Zammad application context, CVE-2026-102490 local Zammad-user-to-root privilege-escalation behavior, affected-version and practical-exploitability qualifications, the documented disagreement between DIVD and Zammad regarding CVE-2026-102490 validation and affected scope, and the October 2, 2026 CISA KEV designations for CVE-2026-102489 and CVE-2026-102490, adding two KEV-listed CVEs to the report’s overall KEV accounting; Ubiquiti Security Advisory Bulletin 067; TrueConf Server; Cisco Crosswork; Cisco Secure Workload; Cisco Unified Intelligence Center; Cisco Nexus 9000; Cisco IOS XR; Cisco IOS XE; Cisco IMC; Cisco Unity Connection; Cisco Secure Firewall Management Center; Tenable Security Center; compromised public Wi-Fi gateway DNS-redirection activity; ClingSTUN Linux back-connect proxy campaign context, including exploitation of known vulnerabilities in internet-facing IoT and network devices, Linux boot persistence, process-killing and watchdog manipulation, public-STUN-assisted NAT traversal, back-connect proxy behavior, remote command execution, and self-propagation; the Cisco October 7, 2026 finalized 35-CVE Coverage With Adaptation cohort across Cisco NX-OS Software and Nexus platforms, Cisco Application Policy Infrastructure Controller, Cisco License On-Prem, Cisco Meraki platforms, and Cisco Finesse, including NX-OS hardening, MPLS OAM and NGOAM remote-code-execution paths, NX-API remote code execution, ACI endpoint-group contract bypass, control-plane denial of service, Python sandbox escape, APIC access-control, command-injection, and sensitive-file-access weaknesses, License On-Prem authentication, authorization, credential, code-execution, SQL-injection, arbitrary-file-write, and management-interface weaknesses, Meraki hardening vulnerabilities, Cisco Finesse server-side request forgery, Cisco remediation guidance, Cisco's current non-exploitation state, and 0-change CISA KEV accounting; the Cloud Foundry UAA CVE-2026-59357 and CVE-2026-59358 Coverage With Adaptation mappings, including self-UAA OIDC authentication and session-trust failure, unauthorized session establishment, OAuth user-token reuse in the client-credentials grant path, privilege-bearing token issuance, UAA and cf-deployment applicability and remediation boundaries, and 0-change CISA KEV accounting; the Brocade Fabric OS October 6, 2026 37-CVE Coverage With Adaptation cohort, including REST API and WebTools management-plane command injection, authentication and authorization bypass, RBAC failure, AAA and federated-authentication weaknesses, privilege escalation, administrative-session manipulation, configuration and firmware-management abuse, Virtual Fabric and fabric-control authorization effects, inter-switch administrative trust abuse, privileged command execution, affected Fabric OS applicability and remediation guidance, and 0-change CISA KEV accounting; the Splunk Enterprise SVD-2026-1001 and SVD-2026-1002 October 7, 2026 disclosure cohorts, comprising 22 Coverage With Adaptation CVEs (CVE-2026-76264 through CVE-2026-76285), including authorization and access-control failures, missing authentication, privilege escalation, operating-system command execution, SQL injection, server-side request forgery, log injection, information disclosure, input-validation weaknesses, denial-of-service conditions, Splunk Enterprise product and version applicability, REST/API and administrative-role prerequisites, Patroni REST API exposure, application and search-job context, SPL2 and Secure Gateway applicability, vendor remediation requirements, and 0-change CISA KEV accounting; the current 12 Directly Covered, 417 Coverage With Adaptation, and 429 total CVE accounting; KEV accounting; and detection-engineering interpretation in this report.
Vendor / Platform Documentation
· Splunk Product Security — SVD-2026-1002 — Security Hardening in Splunk Enterprise — October 7, 2026 — documenting CVE-2026-76281 through CVE-2026-76285, comprising five internally identified vulnerability groups classified under improper access control (CWE-284), improper control of a resource through its lifetime (CWE-664), protection mechanism failure (CWE-693), improper neutralization (CWE-707), and improper adherence to coding standards (CWE-710). Splunk assigns one CVE identifier to each CWE-grouped set of findings, with the highest applicable CVSS 3.1 scores of 9.8, 8.8, 7.6, 9.0, and 4.4, respectively. Affected Splunk Enterprise release branches are 10.4, 10.2, 10.0, and 9.4, with corrected versions 10.4.3, 10.2.7, 10.0.10, and 9.4.15, respectively
· hxxps://advisory[.]splunk[.]com/advisories/SVD-2026-1002
· Splunk Product Security — SVD-2026-1001 — Security Vulnerabilities in Splunk Enterprise — October 7, 2026 — documenting CVE-2026-76264 through CVE-2026-76280, comprising 17 distinct vulnerabilities involving REST API authorization and access-control failures, Linux package-upgrade privilege escalation, log injection, missing authentication in the Patroni REST API permitting unauthenticated operating-system command execution, search-job access-control failures, SPL2 Module Catalog SQL injection, denial of service, server-side request forgery, information disclosure, input-validation weaknesses, SPL2 module-permission authorization bypass, and incorrect permission assignment in Splunk Secure Gateway. Affected Splunk Enterprise release branches are 10.4, 10.2, 10.0, and 9.4, with corrected versions 10.4.3, 10.2.7, 10.0.10, and 9.4.15, respectively. Splunk identifies additional remediation requirements for CVE-2026-76264, CVE-2026-76265, CVE-2026-76272, and CVE-2026-76280
· hxxps://advisory[.]splunk[.]com/advisories/SVD-2026-1001
· Cisco Security Advisory — Cisco Advance Notification for Publication of October 7, 2026, Security Advisories — finalized October 7, 2026 — documenting Cisco PSIRT publication of the NX-OS, Application Policy Infrastructure Controller, License On-Prem, Meraki, and Finesse advisory set.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-notice-fBn58ELx
· Cisco Security Advisory — Cisco NX-OS Software Security Hardening Release: October 2026 — CVE-2026-76453, CVE-2026-76455, CVE-2026-76456, CVE-2026-76457, CVE-2026-76458, and CVE-2026-76459.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-nxosw1-cWzSbtR
· Cisco Security Advisory — Cisco Nexus 3000 and 9000 Series Switches MPLS OAM Remote Code Execution Vulnerability — CVE-2026-76465.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-moam-rce-uBTzYV7
· Cisco Security Advisory — Cisco Nexus 3000 and 9000 Series Switches NGOAM Remote Code Execution Vulnerabilities — CVE-2026-76485, CVE-2026-76486, and CVE-2026-76501.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ngoam-rce-LWKQ4BU
· Cisco Security Advisory — Cisco NX-OS Software NX-API Remote Code Execution Vulnerability — CVE-2026-76471.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-napi-rce-r2shwu2j
· Cisco Security Advisory — Cisco Nexus 9000 Series Fabric Switches in ACI Mode Endpoint Group Contract Bypass Vulnerability — CVE-2026-20038.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-aci-epgcbp-SfDU7NLf
· Cisco Security Advisory — Cisco NX-OS Software Control Plane Denial of Service Vulnerability — CVE-2026-20173.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-nxos-nscpdos-SnderkC7
· Cisco Security Advisory — Cisco NX-OS Software Python Sandbox Escape Vulnerability — CVE-2026-20032.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-nxos-mppe-dhKZAFgb
· Cisco Security Advisory — Cisco Application Policy Infrastructure Controller Security Hardening Release: October 2026 — CVE-2026-76498, CVE-2026-76499, and CVE-2026-76500.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-apic-UOXWtfh
· Cisco Security Advisory — Cisco Application Policy Infrastructure Controller API Command Injection Vulnerability — CVE-2026-20321.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-apic-cmdinj-L6VR4E7
· Cisco Security Advisory — Cisco Application Policy Infrastructure Controller Unauthorized File Access Vulnerability — CVE-2026-76488.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-apic-info-priv-enAdB5vD
· Cisco Security Advisory — Cisco License (Smart Software Manager) On-Prem Security Hardening Release: October 2026 — CVE-2026-76480, CVE-2026-76482, CVE-2026-76483, and CVE-2026-76484.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-ssm-Ph77wdhf
· Cisco Security Advisory — Cisco License (Smart Software Manager) On-Prem Vulnerabilities — CVE-2026-20328, CVE-2026-76437, CVE-2026-76452, and CVE-2026-76454.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ssm-access-nttb2dhE
· Cisco Security Advisory — Cisco Meraki Security Hardening Release: October 2026 — CVE-2026-76463, CVE-2026-76464, CVE-2026-76467, CVE-2026-76468, CVE-2026-76469, CVE-2026-76470, and CVE-2026-76472.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-meraki-os-drbEX9GH
· Cisco Security Advisory — Cisco Finesse Server-Side Request Forgery Vulnerability — CVE-2026-20362.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-finesse-ssrf-mmSuyugS
· Broadcom / Brocade — Brocade Fabric OS 10.x and 9.2.x Releases Vulnerability Disclosures — updated October 6, 2026 — governing disclosure page for the October 6 Brocade Fabric OS advisory cohort, including the qualifying management-plane, REST API, WebTools, authentication, authorization, RBAC, AAA, configuration, firmware, certificate-management, Virtual Fabric, inter-switch management, privilege-escalation, command-execution, and related vulnerabilities represented as Coverage With Adaptation in this report.
· hxxps://support[.]broadcom[.]com/web/ecx/support-content-notification/-/external/content/SecurityAdvisories/0/25000
· Cloud Foundry Foundation Security Team — CVE-2026-59357 — Self-UAA OIDC Configuration Allows JWT Injection to Establish Unauthorized Sessions — October 5, 2026 — documenting the affected UAA v4.5.0 through v79.6.0 boundary, self-UAA OIDC configuration prerequisite, unauthorized external-OIDC browser-session establishment, and UAA v79.7.0-or-later remediation.
· hxxps://www[.]cloudfoundry[.]org/blog/cve-2026-59357-self-uaa-oidc-configuration-allows-jwt-injection-to-establish-unauthorized-sessions/
· Cloud Foundry Foundation Security Team — CVE-2026-59358 — UAA OAuth Token Endpoint Vulnerability Allows User Access Token Reuse for client_credentials Grant Type — October 5, 2026 — documenting affected UAA v3.7.0 through v79.6.0 and cf-deployment through v60.4.0, the valid-user-access-token prerequisite, privilege-bearing client_credentials token issuance, UAA v79.7.0-or-later remediation, and cf-deployment v60.5.0-or-later remediation.
· hxxps://www[.]cloudfoundry[.]org/blog/cve-2026-59358-uaa-oauth-token-endpoint-vulnerability-allows-user-access-token-reuse-for-client_credentials-grant-type/
· Zammad — Statement on vulnerability reports in DIVD case DIVD-2026-00015 — October 1, 2026 — documenting Zammad's position that CVE-2026-102489 is practically exploitable only on Zammad 6.5 and older, that Zammad 7.0 and later are not affected in practice under the documented runtime conditions, that the affected code was additionally hardened in Zammad 7.2.0, and that Zammad had not received sufficient technical detail to independently verify CVE-2026-102490, its scope, or affected-version range at the time of the statement.
· hxxps://community[.]zammad[.]org/t/take-care-local-privilege-escalation-cve-2026-102490-is-reported-as-being-actively-exploited/21297
· DIVD — DIVD-2026-00015 — Zammad zero-day vulnerabilities identified during investigation of the September 21, 2026 DIVD breach, including DIVD's reported exploitation context for CVE-2026-102489 and CVE-2026-102490.
· hxxps://csirt[.]divd[.]nl/cases/DIVD-2026-00015/
· CISA — Known Exploited Vulnerabilities Catalog — CVE-2026-102489 — Zammad GmbH Zammad Session Fixation Vulnerability — added October 2, 2026 — remediation due October 5, 2026.
· hxxps://www[.]cisa[.]gov/known-exploited-vulnerabilities-catalog
· CISA — Known Exploited Vulnerabilities Catalog — CVE-2026-102490 — Zammad GmbH Zammad Improper Privilege Management Vulnerability — added October 2, 2026 — remediation due October 5, 2026.
· hxxps://www[.]cisa[.]gov/known-exploited-vulnerabilities-catalog
· Kiteworks Security Advisory GHSA-qx8c-x3hv-c25g — CVE-2026-102132 — Kiteworks Core privilege escalation through improper access control in the administrative import function, allowing a delegated administrator with the documented permission prerequisite to create a privileged integration credential and obtain full system-administrator privileges; Kiteworks Core versions before 9.5.1 are affected and 9.5.1 is the corrected boundary.
· hxxps://github[.]com/kiteworks/security-advisories/security/advisories/GHSA-qx8c-x3hv-c25g
· GitHub Security Advisory GHSA-g4h7-p63q-r8r4 — Missing Authentication for Critical Function and Initialization of a Resource with an Insecure Default in aisoc — associated with CVE-2026-103053; fixed in AiSOC 12.0.0.
· hxxps://github[.]com/beenuar/AiSOC/security/advisories/GHSA-g4h7-p63q-r8r4
· GitHub Security Advisory GHSA-mcg9-8pxf-j98v — Improper Access Control and Authorization Bypass Through User-Controlled Key and Incorrect Authorization in aisoc — associated with CVE-2026-103054; fixed in AiSOC 12.0.0.
· hxxps://github[.]com/beenuar/AiSOC/security/advisories/GHSA-mcg9-8pxf-j98v
· GitHub Security Advisory GHSA-4m55-xhcm-wjcr — Use of Hard-coded Credentials and Improper Authentication in aisoc — associated with CVE-2026-103055; fixed in AiSOC 12.0.0.
· hxxps://github[.]com/beenuar/AiSOC/security/advisories/GHSA-4m55-xhcm-wjcr
· GitHub Security Advisory GHSA-7q37-2wfw-xrx7 — Improper Neutralization of Special Elements used in an OS Command ('OS Command Injection') in aisoc — associated with CVE-2026-103056; fixed in AiSOC 12.0.0.
· hxxps://github[.]com/beenuar/AiSOC/security/advisories/GHSA-7q37-2wfw-xrx7
· GitHub Security Advisory GHSA-mqjp-pcpr-7c37 — Missing Authentication for Critical Function and Initialization of a Resource with an Insecure Default in aisoc — associated with CVE-2026-103057; fixed in AiSOC 12.0.0.
· hxxps://github[.]com/beenuar/AiSOC/security/advisories/GHSA-mqjp-pcpr-7c37
· AiSOC — Releases — v12.0.0 — security-hardening release correcting the AiSOC conditions represented by CVE-2026-103053 through CVE-2026-103057.
· hxxps://github[.]com/beenuar/AiSOC/releases
· SUSE Rancher Manager — Security Advisories and CVEs — CVE-2026-88804 and CVE-2026-88805 — September 23, 2026 — documenting unauthenticated modification of public UI settings with login-page script-execution consequences and failure to revoke corresponding public API session tokens on logout.
· hxxps://documentation[.]suse[.]com/cloudnative/rancher-manager/latest/en/security/cves[.]html
· SUSE Security — CVE-2026-88804 — Rancher public UI settings modification and login-page script-execution vulnerability.
· hxxps://www[.]suse[.]com/security/cve/CVE-2026-88804[.]html
· SUSE Security — CVE-2026-88805 — Rancher public API session-token revocation failure after logout.
· hxxps://www[.]suse[.]com/security/cve/CVE-2026-88805[.]html
· SailPoint Technologies — Security Advisories — IdentityIQ CVE-2026-12342.
· hxxps://www[.]sailpoint[.]com/security-advisories/
· NVD / SailPoint CNA — CVE-2026-12342 — IdentityIQ improper input validation of submitted web-service API content permitting unauthenticated remote code execution; CNA CVSS 9.6; affected IdentityIQ 8.3 through 8.3p5, 8.4 through 8.4p4, and 8.5 through 8.5p2.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-12342
· FreePBX Security Advisory GHSA-95gm-cmxf-cv8v — CVE-2026-54675 — Authenticated Remote Code Execution via File Upload and Convert in Soundlang Module.
· hxxps://github[.]com/FreePBX/security-reporting/security/advisories/GHSA-95gm-cmxf-cv8v
· FreePBX Security Advisory GHSA-j53p-5m8r-j3p6 — CVE-2026-54710 — Authenticated Superfecta Arbitrary PHP Code Execution through unsafe file inclusion.
· hxxps://github[.]com/FreePBX/security-reporting/security/advisories/GHSA-j53p-5m8r-j3p6
· FreePBX Security Advisory GHSA-79rg-3xp6-rqq6 — CVE-2026-75600 — Authenticated API generatedocs Host Command Injection affecting FreePBX API module versions before 17.0.9.
· hxxps://github[.]com/FreePBX/security-reporting/security/advisories/GHSA-79rg-3xp6-rqq6
· HPE Security Bulletin HPESBHF05163 — HPE Integrated Lights-Out (iLO) 7 firmware — CVE-2026-79820 — remote user-validation failure affecting the iLO 7 management control plane, with network-reachable exploitation conditions and HPE remediation guidance
· hxxps://support[.]hpe[.]com/hpesc/public/docDisplay?docId=hpesbhf05163en_us&docLocale=en_US
· HPE Networking Security Bulletin HPESBNW05137 Rev. 1 — Multiple Vulnerabilities in HPE Networking Analytics and Location Engine (ALE) — supporting the ten HPE ALE Coverage With Adaptation identifiers, ALE 5.0.0.0-and-earlier affected boundary, ALE 5.1.0.0 corrected release, documented authentication and network-path conditions, and HPE's statement that no known public discussion or exploit code targeted the package at publication
· hxxps://support[.]hpe[.]com/hpesc/public/docDisplay?docId=hpesbnw05137en_us&docLocale=en_US
· HPE Networking Security Bulletin HPESBNW05156 Rev. 1 — Multiple Vulnerabilities in HPE Networking AOS-Switch (AOS-S) — supporting the nine CVE-2026-76741 through CVE-2026-76749 Coverage With Adaptation identifiers, management-interface authentication bypass, remote and adjacent memory-corruption and buffer-overflow conditions, code execution, information disclosure, authenticated API privilege escalation, denial-of-service behavior, the AOS-S 16.11.0031-and-earlier affected boundary, the AOS-S 16.11.0032 corrected boundary, and HPE's statement that no known public discussion or exploit code targeted the package at publication
· hxxps://support[.]hpe[.]com/hpesc/public/docDisplay?docId=hpesbnw05156en_us&docLocale=en_US
· HPE Networking Security Bulletin HPESBNW05158 Rev. 1 — Multiple Vulnerabilities in HPE Networking ClearPass Policy Manager (CPPM) — supporting the 28-vulnerability ClearPass Coverage With Adaptation cohort, including remote code execution, authentication bypass, SQL injection, command execution, privilege escalation, access-control and client-software compromise paths, affected ClearPass Policy Manager 6.14.0-and-earlier and 6.11.15-and-earlier applicability, and HPE remediation guidance
· hxxps://support[.]hpe[.]com/hpesc/public/docDisplay?docId=hpesbnw05158en_us&docLocale=en_US
· Zyxel Security Advisory — Zyxel security advisory for stack-based buffer overflow vulnerability in GS1900 series switches — CVE-2026-7273.
· hxxps://www[.]zyxel[.]com/global/en/support/security-advisories/zyxel-security-advisory-for-stack-based-buffer-overflow-vulnerability-in-gs1900-series-switches-06-16-2026
· CISA — Known Exploited Vulnerabilities Catalog — CVE-2026-7273 — Zyxel GS1900 Series Switches stack-based buffer overflow vulnerability.
· hxxps://www[.]cisa[.]gov/known-exploited-vulnerabilities-catalog
· IBM Security Bulletin — IBM Guardium Data Protection is affected by multiple vulnerabilities — September 17, 2026.
· hxxps://www[.]ibm[.]com/support/pages/security-bulletin-ibm-guardium-data-protection-affected-multiple-vulnerabilities-17
· IBM — Guardium Data Protection 12.0p233 Release Notes.
· hxxps://www[.]ibm[.]com/support/pages/node/7285635
· GitHub Reviewed Advisory — GHSA-c8w2-fgvx-vhv4 — kcp CVE-2026-61682.
· hxxps://github[.]com/advisories/GHSA-c8w2-fgvx-vhv4
· HP Security Bulletin HPSBPI04149 Rev. 1 — HP Advance – Potential Elevation of Privilege, Remote Code Execution & Arbitrary File Write — September 16, 2026.
· hxxps://support[.]hp[.]com/us-en/document/ish_15646496-15646518-16/hpsbpi04149
· Dell Security Advisory DSA-2026-393 — Security Update for Dell ObjectScale Multiple Vulnerabilities.
· hxxps://www[.]dell[.]com/support/kbdoc/en-us/000505935/dsa-2026-393-security-update-for-dell-objectscale-multiple-vulnerabilities
· SolarWinds-assigned CVE record — CVE-2026-28326 — Access Rights Manager unauthenticated remote code execution.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-28326
· TR-CERT / USOM — TR-26-1202 — Logsign SIEM security advisory bundle — CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926 — default administrative credentials, path traversal, and code injection affecting Logsign SIEM 6.4.101 through versions before 6.4.117.
· hxxps://siberguvenlik[.]gov[.]tr/guvenlik-bildirimleri/detay/tr-26-1202
· CVE Program / TR-CERT CNA record — CVE-2026-90924 — Logsign SIEM use of default credentials; CVSS 9.8; affected versions 6.4.101 through versions before 6.4.117.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-90924
· CVE Program / TR-CERT CNA record — CVE-2026-90925 — Logsign SIEM path traversal; CVSS 7.1; affected versions 6.4.101 through versions before 6.4.117.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-90925
· CVE Program / TR-CERT CNA record — CVE-2026-90926 — Logsign SIEM code injection; CVSS 8.8; affected versions 6.4.101 through versions before 6.4.117.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-90926
· Logsign Support Center — Version 6.4.117 Release Notes — September 7, 2026 — security hardening for integration configuration and file permissions and the release used as the correction boundary identified by the TR-CERT CNA records.
· hxxps://support[.]logsign[.]net/hc/en-us/articles/38722038483730-07-09-2026-Version-6-4-117-Release-Notes
· UTMStack — Release v11.2.16 — October 1, 2026 — documents the UTMStack security release that provides the corrected-version boundary for CVE-2026-82039 through CVE-2026-82045. UTMStack versions before 11.2.16 are affected by the applicable vulnerabilities in this seven-CVE cohort, and version 11.2.16 contains the corresponding security corrections.
· hxxps://github[.]com/UTMStack/UTMStack/releases/tag/v11.2.16
· UTMStack — Security patch commit 4e7a727c3b8d8e2ad020d3b4f982a6d085dbecdd — documents the UTMStack code changes associated with remediation of CVE-2026-82039 through CVE-2026-82045, including changes affecting database-query handling, server-side request behavior, command-WebSocket authorization, authentication handling, password-reset responses, PDF-service request processing, and JPQL-query construction.
· hxxps://github[.]com/utmstack/UTMStack/commit/4e7a727c3b8d8e2ad020d3b4f982a6d085dbecdd
· SolarWinds — SolarWinds Observability Self-Hosted 2026.2.3 Release Notes — September 22, 2026 — CVE-2026-28324 and CVE-2026-28325 — unauthenticated remote-code-execution vulnerabilities caused respectively by insufficient integrity checks under a non-default, non-secure configuration and deserialization of untrusted data when the application uses the affected communication mode.
· hxxps://documentation[.]solarwinds[.]com/en/success_center/orionplatform/content/release_notes/hco_2026-2-3_release_notes[.]htm
· Check Point — Security Advisory – Action Required – Active Exploitation of CVE-2026-85102 and a Management Pre-Authentication Vulnerability CVE-2026-93616 — September 22, 2026.
· hxxps://blog[.]checkpoint[.]com/security/security-advisory-action-required-active-exploitation-of-cve-2026-85102-and-a-management-pre-authentication-vulnerability-cve-2026-93616/
· Check Point Support — sk1000171 — CVE-2026-93616 Security Management remediation, mitigation, hunting, indicators of compromise, validation, and upgrade guidance.
· hxxps://support[.]checkpoint[.]com/results/sk/sk1000171
· Check Point CheckMates — Important Notification: Action required - Critical Security Update CVE-2026-91843 — September 16, 2026.
· hxxps://community[.]checkpoint[.]com/t5/General-Topics/Important-Notification-Action-required-Critical-Security-Update/m-p/282409
· WSO2 — Security Advisory WSO2-2026-5328 — CVE-2026-5430 — Authentication Bypass via JWT Algorithm Mismatch in Multiple WSO2 Products Allows Account Takeover.
· hxxps://security[.]docs[.]wso2[.]com/en/latest/security-announcements/security-advisories/2026/WSO2-2026-5328/
· CISA — Known Exploited Vulnerabilities Catalog — CVE-2026-5430 — WSO2 Products authentication-bypass vulnerability — added September 24, 2026 based on evidence of active exploitation.
· hxxps://www[.]cisa[.]gov/known-exploited-vulnerabilities-catalog
· Issabel Foundation — Framework patch commit b97dbaf0b71c1c36f841e672b664afbeb02773bd.
· hxxps://github[.]com/IssabelFoundation/framework/commit/b97dbaf0b71c1c36f841e672b664afbeb02773bd
· VulnCheck — Issabel Framework Hard-coded JWT Key RCE via pbxapi/manager/originate — CVE-2026-89026.
· hxxps://www[.]vulncheck[.]com/advisories/issabel-pbx-hard-coded-jwt-key-rce-via-pbxapi-manager-originate
· Cisco Security Advisory — Cisco Advance Notification for Publication of September 16, 2026, Security Advisories.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-notice-jfxK98ZP
· Cisco Security Advisory — Cisco Identity Services Engine Hardening Release: September 2026.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-ise-XU5EwX5T
· Cisco Security Advisory — Cisco Identity Services Engine Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-multi-hrP9jQSQ
· Cisco Security Advisory — Cisco Identity Services Engine Authentication Bypass Vulnerability — CVE-2026-76460.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ISE-ABP-VNSW7Tn5
· CISA — Known Exploited Vulnerabilities Catalog — CVE-2026-76460.
· hxxps://www[.]cisa[.]gov/known-exploited-vulnerabilities-catalog
· Cisco Security Advisory — Cisco Identity Services Engine Remote Code Execution Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-rce-se7bYU57
· Cisco Security Advisory — Cisco Identity Services Engine Authenticated Remote Code Execution and API Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-mult-vul-ymSsTLCc
· Cisco Security Advisory — Cisco Identity Services Engine Command Injection Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-cmd-inj-e2CuZCYZ
· Cisco Security Advisory — Cisco Identity Services Engine RADIUS Denial of Service Vulnerability.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-RADIUS-dos-wR3hYPMw
· Cisco Security Advisory — Cisco Identity Services Engine SQL Injection Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-sql-inj-3QTKR947
· Cisco Security Advisory — Cisco Identity Services Engine Cross-Site Scripting Vulnerability.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-xss-Uz9VWRQ
· Cisco Security Advisory — Cisco Identity Services Engine Authentication Bypass Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-multiauth-bypass-sgD2HbL4
· Cisco Security Advisory — Cisco Identity Services Engine Multiple Path Traversal Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-multi-traversal-WDTgYCdn
· Cisco Security Advisory — Cisco Identity Services Engine Information Disclosure Vulnerability.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-inf-disc-LFWvcCu
· Cisco Security Advisory — Cisco Identity Services Engine SQL and HQL Injection Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-multisql-inject-JnHK54Rq
· Cisco Security Advisory — Cisco Identity Services Engine Authorization Bypass Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-auth-bypass-1-MxcTNgwx
· Cisco Security Advisory — Cisco Identity Services Engine 802.1X Session Hijack and Information Disclosure Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-multi-vuln-kWLeNnRD
· Cisco Security Advisory — Cisco Secure Firewall Management Center Software sftunnel Root Arbitrary Code Execution Vulnerability.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmc-sftunn-codex-c3O4Jft2
· Cisco Security Advisory — Cisco Secure Firewall Management Center Software Java Deserialization Remote Code Execution Vulnerability.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmc-javarce-y2NypXwk
· Cisco Security Advisory — Cisco Secure Firewall Management Center Software Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmc-mulivulns-4PsnFwvx
· Cisco Security Advisory — Cisco Secure Firewall Management Center Software Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmc2-multivulns-HXgcqRG
· Cisco Security Advisory — Cisco Secure Firewall Management Center and Secure Firewall Threat Defense Software sftunnel Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmcftd-sftun-multivulns-WGVHOrN3
· Cisco Security Advisory — Cisco Secure Firewall Adaptive Security Appliance, Secure Firewall Threat Defense, and Secure Firewall Management Center Software Hardening Release: September 2026.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-asaftdfmc-uvpPROhN
· Cisco Security Advisory — Cisco Nexus Dashboard Software Security Hardening Release: September 2026.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-ndw1-psFvnrg
· Cisco Security Advisory — Cisco BroadWorks CommPilot Application Software Authorization Bypass Vulnerability.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-auth-bypass-broadwor-57m9dmm5
· Cisco Security Advisory — Cisco ThousandEyes Virtual Appliance Authenticated Web Interface Command Injection Vulnerability.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-teva-os-command-W4GAO6jp
· Fortinet PSIRT — FG-IR-26-175 — CVE-2026-104286 — FortiMail path traversal vulnerability permitting an unauthenticated attacker to write arbitrary files on the underlying system through crafted HTTP or HTTPS requests.
· hxxps://fortiguard[.]fortinet[.]com/psirt/FG-IR-26-175
· CISA — CISA Adds One Known Exploited Vulnerability to Catalog — October 1, 2026 — CVE-2026-104286 — Fortinet FortiMail Path Traversal Vulnerability.
· hxxps://www[.]cisa[.]gov/news-events/alerts/2026/10/01/cisa-adds-one-known-exploited-vulnerability-catalog
· CISA — Known Exploited Vulnerabilities Catalog — CVE-2026-104286 — Fortinet FortiMail Path Traversal Vulnerability — added October 1, 2026 based on evidence of active exploitation.
· hxxps://www[.]cisa[.]gov/known-exploited-vulnerabilities-catalog
· Cisco Security Advisory — Cisco Secure Email Gateway and Secure Email and Web Manager Security Hardening Release: September 2026.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-esa-dfCrfXkm
· Cisco Security Advisory — Cisco Secure Email Gateway SQL Injection Vulnerability — CVE-2026-76461.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-esa-inj-2bLVGmhX
· CISA — Known Exploited Vulnerabilities Catalog — CVE-2026-76461.
· hxxps://www[.]cisa[.]gov/known-exploited-vulnerabilities-catalog
· CISA — ICSA-26-254-01 — Malcolm Multiple Vulnerabilities — September 11, 2026.
· hxxps://raw[.]githubusercontent[.]com/cisagov/CSAF/develop/csaf_files/OT/white/2026/icsa-26-254-01[.]json
· Traefik Labs — New security update for Traefik 2.11.57 and 3.7.13.
· hxxps://community[.]traefik[.]io/t/new-security-update-for-traefik-2-11-2-11-57-and-3-7-3-7-13/30229
· Traefik — GHSA-v67p-phpq-fc8x — CVE-2026-88004.
· hxxps://github[.]com/traefik/traefik/security/advisories/GHSA-v67p-phpq-fc8x
· Traefik — GHSA-qqjf-53cj-pwvv — CVE-2026-88007.
· hxxps://github[.]com/traefik/traefik/security/advisories/GHSA-qqjf-53cj-pwvv
· Traefik — GHSA-w4v4-9rw7-5326 — CVE-2026-88008.
· hxxps://github[.]com/traefik/traefik/security/advisories/GHSA-w4v4-9rw7-5326
· Traefik — GHSA-f52w-8j3h-j724 — CVE-2026-88009.
· hxxps://github[.]com/traefik/traefik/security/advisories/GHSA-f52w-8j3h-j724
· Traefik — GHSA-rf44-j88r-hh8c — CVE-2026-88011.
· hxxps://github[.]com/traefik/traefik/security/advisories/GHSA-rf44-j88r-hh8c
· HashiCorp — HCSEC-2026-37 — CVE-2026-88021.
· hxxps://discuss[.]hashicorp[.]com/t/hcsec-2026-37-consul-vulnerable-to-an-authorization-bypass-in-the-connect-service-mesh/77739
· HashiCorp — HCSEC-2026-36 — CVE-2026-87107.
· hxxps://discuss[.]hashicorp[.]com/t/hcsec-2026-36-consul-vulnerable-to-an-authorization-bypass-in-the-catalog-deregistration-path/77738
· HashiCorp — HCSEC-2026-35 — CVE-2026-87106.
· hxxps://discuss[.]hashicorp[.]com/t/hcsec-2026-35-consul-vulnerable-to-a-denial-of-service-in-the-native-rpc-listener/77737
· HashiCorp — HCSEC-2026-34 — CVE-2026-87090.
· hxxps://discuss[.]hashicorp[.]com/t/hcsec-2026-34-consul-vulnerable-to-an-authorization-bypass-in-the-catalog-node-write-path/77736
· Schneider Electric — SEVD-2026-251-01 — Multiple Vulnerabilities on EcoStruxure IT Data Center Expert.
· hxxps://download[.]se[.]com/files?p_Doc_Ref=SEVD-2026-251-01
· Schneider Electric — Security Notifications.
· hxxps://www[.]se[.]com/ww/en/work/support/cybersecurity/security-notifications/
· CERT-FR — CERTFR-2026-AVI-1132 — Multiple vulnerabilities in Schneider Electric EcoStruxure IT Data Center Expert.
· hxxps://www[.]cert[.]ssi[.]gouv[.]fr/avis/CERTFR-2026-AVI-1132/
· CISA — CISA Adds Two Known Exploited Vulnerabilities to Catalog — September 10, 2026 — CVE-2026-67277 and CVE-2026-86060.
· hxxps://www[.]cisa[.]gov/news-events/alerts/2026/09/10/cisa-adds-two-known-exploited-vulnerabilities-catalog
· CISA — Known Exploited Vulnerabilities Catalog — CVE-2026-67279 — MikroTik RouterOS unauthenticated SSH connection-protocol vulnerability — added September 25, 2026 based on evidence of active exploitation.
· hxxps://www[.]cisa[.]gov/known-exploited-vulnerabilities-catalog
· CERT Polska — Critical vulnerabilities in MikroTik RouterOS are being actively exploited.
· hxxps://cert[.]pl/en/posts/2026/09/vulnerabilities-in-mikrotik-routeros-actively-exploited/
· Cisco Security Advisory — Cisco IOS XR Software Security Hardening Release: September 2026.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-iosxr-qg64NcM
· Cisco Advance Notification for Publication of September 2, 2026, Security Advisories.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-notice-f2SiMFxl
· Ubiquiti Security Advisory Bulletin 067.
· hxxps://community[.]ui[.]com/releases/Security-Advisory-Bulletin-067/fc4a3488-7c43-4628-8bab-f715e96dbfc9
· TrueConf — TrueConf Server Security Updates.
· hxxps://trueconf[.]com/blog/update/
· Cisco Security Advisory — Cisco Crosswork Security Hardening Release: August 2026.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-crosswork-UzDTU9Vh
· Cisco Security Advisory — Cisco Secure Workload Software Security Hardening Release: August 2026.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-csw1-shSvndWP
· Cisco Security Advisory — Cisco Unified Intelligence Center SQL Injection Vulnerability.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-cuic-sql-inject-2qbfWSm5
· Cisco Security Advisory — Cisco IOS XE Software Security Hardening Release: August 2026.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-iosxe-V8NMuMZJ
· Cisco Security Advisory — Cisco Integrated Management Controller Command Injection and Remote Code Execution Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-cimc-cmd-inj-3hKN3bVt
· Cisco Security Advisory — Cisco Unity Connection Remote Code Execution and Server-Side Request Forgery Vulnerabilities.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-unity-rce-ssrf-hENhuASy
· Cisco Security Advisory — Cisco Secure Firewall Management Center Software Static Credential Vulnerability — CVE-2026-20316.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmc-static-cred-BET3Cjh
· Cisco Security Advisory — Cisco Secure Firewall Management Center Software Authentication Bypass Vulnerability — CVE-2026-20079.
· hxxps://sec[.]cloudapps[.]cisco[.]com/security/center/content/CiscoSecurityAdvisory/cisco-sa-onprem-fmc-authbypass-5JPp45V2
· Tenable Security Advisory — Security Center Version 6.9.0 Fixes Multiple Vulnerabilities — TNS-2026-22 — CVE-2026-19626.
· hxxps://www[.]tenable[.]com/security/tns-2026-22
· Arista Security Advisory 0185 — CloudVision Portal and CloudVision-CUE On-Premises — CVE-2026-101158 — stored cross-site scripting through the Fileserver upload API with authenticated file-upload privileges and potential CloudVision user-session hijacking and administrative-account access.
· hxxps://www[.]arista[.]com/en/support/advisories-notices/security-advisory/24801-security-advisory-0185
· Arista Security Advisory 0186 — CloudVision Portal On-Premises — CVE-2026-101149 and CVE-2026-101150 — OIDC single-sign-on configuration and bearer-token server-side request forgery conditions affecting deployments using the documented optional OIDC authentication configuration.
· hxxps://www[.]arista[.]com/en/support/advisories-notices/security-advisory/24802-security-advisory-0186
· Arista Security Advisory 0187 — CloudVision Portal On-Premises — CVE-2026-101151 and CVE-2026-101152 — login-flow and SSO request-validation weaknesses permitting open redirection and, for CVE-2026-101152 under the documented SSO condition, delivery of identity-provider authentication material to an attacker-controlled URL.
· hxxps://www[.]arista[.]com/en/support/advisories-notices/security-advisory/24803-security-advisory-0187
· Arista Security Advisory 0188 — CloudVision Portal On-Premises and CloudVision Sensor — CVE-2026-101153 — authenticated high-privilege path traversal permitting extraction of unintended data from the CloudVision Sensor.
· hxxps://www[.]arista[.]com/en/support/advisories-notices/security-advisory/24804-security-advisory-0188
· Arista Security Advisory 0189 — CloudVision Portal On-Premises — CVE-2026-101154 and CVE-2026-101155 — CloudVision management-plane vulnerabilities corrected in CloudVision Portal 2026.2.1, 2026.1.3, and 2025.3.4.
· hxxps://www[.]arista[.]com/en/support/advisories-notices/security-advisory/24805-security-advisory-0189
· Arista Security Advisory 0190 — CloudVision-CUE On-Premises — CVE-2026-102155, CVE-2026-102157, CVE-2026-102158, CVE-2026-102159, CVE-2026-102160, and CVE-2026-102161 — XML external entity injection, authorization bypass through insecure direct object reference, SQL injection, missing authentication for internal backend functionality, operating-system command injection, and source-address trust or authentication-bypass behavior affecting the CV-CUE management backend.
· hxxps://www[.]arista[.]com/en/support/advisories-notices/security-advisory/24806-security-advisory-0190
· Arista Security Advisory 0191 — CloudVision-CUE On-Premises — CVE-2026-102156 — unauthenticated LDAP injection against the configured directory service under the documented high-complexity and LDAP-authentication conditions.
· hxxps://www[.]arista[.]com/en/support/advisories-notices/security-advisory/24807-security-advisory-0191
· Arista Security Advisory 0192 — CloudVision-CUE On-Premises — CVE-2026-101156 and CVE-2026-101157 — stored cross-site scripting affecting the CV-CUE user-interface context, including authenticated high-privilege configuration injection and adjacent-network unauthenticated injection under the applicable CVE conditions.
· hxxps://www[.]arista[.]com/en/support/advisories-notices/security-advisory/24808-security-advisory-0192
· Arista Security Advisory 0183 — VeloCloud Orchestrator On-Prem — CVE-2026-93952.
· hxxps://www[.]arista[.]com/en/support/advisories-notices/security-advisory/24765-security-advisory-0183
· Ubiquiti Security Advisory Bulletin 064.
· hxxps://community[.]ui[.]com/releases/Security-Advisory-Bulletin-064-064/84811c09-4cf4-42ab-bd61-cc994445963b
· Ubiquiti Security Advisory Bulletin 066.
· hxxps://community[.]ui[.]com/releases/Security-Advisory-Bulletin-066-066/984eceb3-49c8-4227-942d-671c289b3afc
· OPNsense Core Security Advisory — GHSA-wjqq-rfmm-v5h3.
· hxxps://github[.]com/opnsense/core/security/advisories/GHSA-wjqq-rfmm-v5h3
CVE Records
· CVE Records — Arista CloudVision Portal, CloudVision Sensor, and CloudVision-CUE on-premises — CVE-2026-101149, CVE-2026-101150, CVE-2026-101151, CVE-2026-101152, CVE-2026-101153, CVE-2026-101154, CVE-2026-101155, CVE-2026-101156, CVE-2026-101157, CVE-2026-101158, CVE-2026-102155, CVE-2026-102156, CVE-2026-102157, CVE-2026-102158, CVE-2026-102159, CVE-2026-102160, and CVE-2026-102161 — 17 distinct CloudVision management-control-plane vulnerabilities represented as Coverage With Adaptation under their CVE-specific authentication, configuration, affected-product, and network-access prerequisites.
· CVE Record — CVE-2026-102490 — Zammad local privilege-escalation vulnerability affecting the local zammad user under the DIVD-assigned record, permitting escalation to root; DIVD identifies Zammad 1.5.0 through versions before 7.1.0-alpha as affected, while Zammad states that it had not received sufficient technical detail to independently verify the vulnerability or affected scope as of October 1, 2026.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-102490
· CVE Record — CVE-2026-102489 — Zammad remote-code-execution and session-compromise vulnerability affecting Zammad 6.3.0 through 6.5.4 under DIVD's record; the vulnerability is also present in Zammad 7.0.0 through 7.1.3 but DIVD states that it is not practically exploitable there because of environmental conditions.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-102489
· CVE Record — CVE-2026-104286 — Fortinet FortiMail path traversal permitting an unauthenticated remote attacker to write arbitrary files on the underlying system through crafted HTTP or HTTPS requests.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-104286
· CVE Record — CVE-2026-103057 — AiSOC missing authentication on realtime internal endpoints permitting unauthenticated event submission, spoofed tenant identifiers, unauthorized WebSocket or SSE content distribution, or unauthorized notification activity.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-103057
· CVE Record — CVE-2026-102132 — Kiteworks Core privilege escalation through improper access control in the administrative import function, allowing a delegated administrator holding a narrowly scoped administrative permission to create a privileged integration credential and obtain full system-administrator privileges without action by an existing system administrator; Kiteworks Core versions before 9.5.1 are affected and 9.5.1 is unaffected.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-102132
· CVE Record — CVE-2026-103056 — AiSOC authenticated command injection through CrowdStrike Real Time Response action parameters, permitting attacker-controlled command execution on managed endpoints with SYSTEM or root privileges.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-103056
· CVE Record — CVE-2026-103055 — AiSOC hard-coded JWT verification secret in the realtime service permitting forged subscription authority, arbitrary tenant identifiers, or unauthorized cross-tenant access to live security data under the documented configuration condition.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-103055
· CVE Record — CVE-2026-103054 — AiSOC authenticated MSSP portfolio tenant authorization failure permitting unauthorized tenant association and consequential access to another tenant's alerts, incidents, or posture information.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-103054
· CVE Record — CVE-2026-103053 — AiSOC response-action API authentication failure permitting unauthorized response-action functionality under the documented deployment and actions-service-token conditions.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-103053
· CVE Record — CVE-2026-88805 — SUSE Rancher session-token revocation failure after logout affecting public API session-token deployments.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-88805
· CVE Record — CVE-2026-88804 — SUSE Rancher unauthenticated public UI settings modification enabling login-page script execution.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-88804
· CVE Record — CVE-2026-75600 — FreePBX authenticated API generatedocs host command injection.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-75600
· CVE Record — CVE-2026-54710 — FreePBX authenticated Superfecta arbitrary PHP code execution through unsafe file inclusion.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-54710
· CVE Record — CVE-2026-54675 — FreePBX authenticated Soundlang arbitrary file write leading to remote code execution.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-54675
· CVE Record — CVE-2026-12342 — SailPoint IdentityIQ unauthenticated remote code execution through improper input validation of submitted web-service API content.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-12342
· CVE Record — CVE-2026-79820 — HPE Integrated Lights-Out 7 remote user-validation failure affecting iLO 7 firmware
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79820
· CVE Record — CVE-2026-79818 — HPE Networking ClearPass Policy Manager API-interface authentication bypass permitting unauthenticated sensitive-information disclosure
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79818
· CVE Record — CVE-2026-79817 — HPE Networking ClearPass Policy Manager client-software local sensitive-information disclosure
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79817
· CVE Record — CVE-2026-79816 — HPE Networking ClearPass Policy Manager client-interface unauthenticated DOM-based cross-site scripting
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79816
· CVE Record — CVE-2026-79815 — HPE Networking ClearPass Policy Manager OnGuard agent authenticated command injection with elevated-privilege command execution
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79815
· CVE Record — CVE-2026-79814 — HPE Networking ClearPass Policy Manager OnGuard agent local arbitrary file write leading to local privilege escalation
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79814
CVE Record — CVE-2026-79813 — HPE Networking ClearPass Policy Manager client-software local privilege escalation
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79813
· CVE Record — CVE-2026-79812 — HPE Networking ClearPass Policy Manager OnGuard agent authenticated local denial of service
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79812
· CVE Record — CVE-2026-79811 — HPE Networking ClearPass Policy Manager API authenticated SQL injection with arbitrary database-command execution
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79811
· CVE Record — CVE-2026-79810 — HPE Networking ClearPass Policy Manager authenticated remote code execution under the documented high-privilege condition
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79810
· CVE Record — CVE-2026-79809 — HPE Networking ClearPass Policy Manager API-endpoint unauthenticated path traversal leading to authorization bypass
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79809
· CVE Record — CVE-2026-79808 — HPE Networking ClearPass Policy Manager OnGuard agent authenticated local buffer overflow with elevated code-execution or availability impact
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79808
· CVE Record — CVE-2026-79807 — HPE Networking ClearPass Policy Manager Windows client-software local missing-integrity-verification vulnerability leading to privilege escalation
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79807
· CVE Record — CVE-2026-79806 — HPE Networking ClearPass Policy Manager OnGuard Linux agent local privilege escalation to root
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79806
· CVE Record — CVE-2026-79805 — HPE Networking ClearPass Policy Manager path traversal permitting unauthorized file access and modification
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79805
· CVE Record — CVE-2026-79803 — HPE Networking ClearPass Policy Manager API authenticated command injection leading to privilege escalation and administrative control
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79803
· CVE Record — CVE-2026-79802 — HPE Networking ClearPass Policy Manager client-software command injection with elevated command execution
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79802
· CVE Record — CVE-2026-79801 — HPE Networking ClearPass Policy Manager client agent unauthenticated missing-integrity-verification vulnerability permitting remote code execution
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79801
· CVE Record — CVE-2026-79800 — HPE Networking ClearPass Policy Manager authenticated path traversal leading to remote code execution
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79800
· CVE Record — CVE-2026-79799 — HPE Networking ClearPass Policy Manager web-based management-interface unauthenticated stored cross-site scripting
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79799
· CVE Record — CVE-2026-79798 — HPE Networking ClearPass Policy Manager web-based management-interface authenticated SQL injection
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79798
· CVE Record — CVE-2026-79797 — HPE Networking ClearPass Android client application improper access control
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79797
· CVE Record — CVE-2026-79796 — HPE Networking ClearPass Policy Manager unauthenticated authentication bypass permitting unauthorized system access
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79796
· CVE Record — CVE-2026-79794 — HPE Networking ClearPass Policy Manager web-based management-interface authenticated SQL injection
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-79794
· CVE Record — CVE-2026-76754 — HPE Networking ClearPass Policy Manager unauthenticated SQL injection leading to remote code execution
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76754
· CVE Record — CVE-2026-76753 — HPE Networking ClearPass Policy Manager unauthenticated format-string vulnerability
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76753
· CVE Record — CVE-2026-76752 — HPE Networking ClearPass Policy Manager authentication bypass permitting unauthorized administrative access
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76752
· CVE Record — CVE-2026-76751 — HPE Networking ClearPass Policy Manager OnGuard agent missing integrity verification permitting unauthenticated remote code execution
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76751
· CVE Record — CVE-2026-76750 — HPE Networking ClearPass Policy Manager web-interface deserialization of untrusted data permitting unauthenticated remote code execution
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76750
· CVE Record — CVE-2026-76749 — HPE Networking AOS-Switch unauthenticated sensitive-information disclosure
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76749
· CVE Record — CVE-2026-76748 — HPE Networking AOS-Switch API authenticated privilege escalation
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76748
· CVE Record — CVE-2026-76747 — HPE Networking AOS-Switch unauthenticated buffer overflow permitting information disclosure
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76747
· CVE Record — CVE-2026-76746 — HPE Networking AOS-Switch unauthenticated adjacent buffer overflow permitting information disclosure
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76746
· CVE Record — CVE-2026-76745 — HPE Networking AOS-Switch unauthenticated adjacent memory corruption permitting remote code execution
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76745
· CVE Record — CVE-2026-76744 — HPE Networking AOS-Switch unauthenticated buffer overflow permitting remote code execution
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76744
· CVE Record — CVE-2026-76743 — HPE Networking AOS-Switch management-interface authentication bypass
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76743
· CVE Record — CVE-2026-76742 — HPE Networking AOS-Switch web-management-interface authentication bypass
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76742
· CVE Record — CVE-2026-76741 — HPE Networking AOS-Switch authenticated buffer overflow leading to denial of service
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76741
· CVE Record — CVE-2026-76717 — HPE Networking Analytics and Location Engine, one of the ten vulnerabilities documented in HPESBNW05137 Rev. 1.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76717
· CVE Record — CVE-2026-76716 — HPE Networking Analytics and Location Engine, one of the ten vulnerabilities documented in HPESBNW05137 Rev. 1.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76716
· CVE Record — CVE-2026-76715 — HPE Networking Analytics and Location Engine, documented man-in-the-middle condition associated with root code execution; not generalized to arbitrary direct unauthenticated RCE.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76715
· CVE Record — CVE-2026-76714 — HPE Networking Analytics and Location Engine authenticated web-interface command execution with root privileges.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76714
· CVE Record — CVE-2026-76713 — HPE Networking Analytics and Location Engine authenticated maintenance-restore filesystem access with root privileges.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76713
· CVE Record — CVE-2026-76712 — HPE Networking Analytics and Location Engine, one of the ten vulnerabilities documented in HPESBNW05137 Rev. 1.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76712
· CVE Record — CVE-2026-76711 — HPE Networking Analytics and Location Engine, one of the ten vulnerabilities documented in HPESBNW05137 Rev. 1.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76711
· CVE Record — CVE-2026-76710 — HPE Networking Analytics and Location Engine, one of the ten vulnerabilities documented in HPESBNW05137 Rev. 1.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76710
· CVE Record — CVE-2026-76709 — HPE Networking Analytics and Location Engine, one of the ten vulnerabilities documented in HPESBNW05137 Rev. 1.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76709
· CVE Record — CVE-2026-76708 — HPE Networking Analytics and Location Engine, one of the ten vulnerabilities documented in HPESBNW05137 Rev. 1.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-76708
· CVE Record — CVE-2026-93952 — VeloCloud Orchestrator On-Prem improper input validation permitting remote access to privileged internal functionality and potential VCO host and managed-data compromise under the documented exposure conditions.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-93952
· CVE Record — CVE-2026-93616 — Check Point Security Management pre-authentication path traversal in the management web service, permitting arbitrary-path script execution and Java class loading under the documented affected conditions.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-93616
· CVE Record — CVE-2026-90924 — Logsign SIEM use of default administrative credentials affecting versions 6.4.101 through versions before 6.4.117.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-90924
· CVE Record — CVE-2026-90925 — Logsign SIEM low-privilege authenticated path traversal affecting versions 6.4.101 through versions before 6.4.117.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-90925
· CVE Record — CVE-2026-90926 — Logsign SIEM low-privilege authenticated, network-reachable code injection affecting versions 6.4.101 through versions before 6.4.117.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-90926
· CVE Record — CVE-2026-82039 — UTMStack authenticated SQL injection affecting the asset-group search functionality. An authenticated attacker can manipulate affected search parameters so that attacker-controlled input reaches a database query, permitting unauthorized SQL execution and consequential access to or modification of database information. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-82039
· CVE Record — CVE-2026-82040 — UTMStack authenticated server-side request forgery affecting identity-provider metadata processing. An authenticated attacker can supply an attacker-controlled metadata URL and cause the UTMStack server to issue requests to internal network resources or cloud instance-metadata services that would not otherwise be directly reachable by the attacker. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-82040
· CVE Record — CVE-2026-82041 — UTMStack missing authorization affecting the STOMP command WebSocket used for communication with connected agents. An authenticated user who can reach the affected command path can submit operating-system commands without the intended authorization restriction and cause those commands to be forwarded through the UTMStack control plane to connected agents. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-82041
· CVE Record — CVE-2026-82042 — UTMStack authentication bypass affecting the internal-key authentication path. An attacker who possesses or obtains a valid internal key can use that trust path to access privileged API functionality without completing the normal user-account or JWT-authentication process, creating a path to unauthorized privileged management activity. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-82042
· CVE Record — CVE-2026-82043 — UTMStack unauthenticated account-enumeration vulnerability affecting the password-reset workflow. An unauthenticated attacker can distinguish between registered and unregistered email addresses based on password-reset responses, allowing valid UTMStack accounts to be identified for potential follow-on credential attacks, phishing, or other identity-targeting activity. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-82043
· CVE Record — CVE-2026-82044 — UTMStack authenticated server-side request forgery affecting the PDF-reporting service. An authenticated attacker can provide an attacker-controlled URL that causes the reporting service to retrieve content from internal backend resources, OpenSearch services, or cloud instance-metadata services, with the retrieved information potentially exposed through generated report content. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-82044
· CVE Record — CVE-2026-82045 — UTMStack authenticated JPQL injection affecting network-scan property-value search functionality. An authenticated attacker can manipulate affected query input and alter JPQL processing in a manner that permits unauthorized access to sensitive entity information, including credential-related records. UTMStack versions before 11.2.16 are affected, and version 11.2.16 provides the corrected boundary.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-82045
· CVE Record — CVE-2026-7273 — Zyxel GS1900 series switch CGI stack-based buffer overflow with LAN-based unauthenticated crafted-HTTP-request path and potential OS-command-execution impact.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-7273
· CVE-2026-85542 — IBM Guardium Data Protection authenticated GIM bundle-import command injection affecting Central Manager.
· CVE-2026-84893 — IBM Guardium Data Protection authenticated PESI SQL injection and internal-database information access.
· CVE-2026-84884 — IBM Guardium Data Protection reversibly protected internal REST service-account credential enabling recovery of administrative REST authority.
· CVE-2026-84882 — IBM Guardium Data Protection authenticated Universal Connector Oracle Wallet upload path traversal and arbitrary file write.
· CVE-2026-84842 — IBM Guardium Data Protection authenticated Datasource REST path traversal and arbitrary file deletion.
· CVE-2026-84440 — IBM Guardium Data Protection authenticated SNMP alert-policy command injection with root-context execution.
· CVE-2026-84278 — IBM Guardium Data Protection authenticated high-privilege SUID-root ssh_config_wrapper command injection.
· CVE-2026-84275 — IBM Guardium Data Protection unauthenticated GIM file-upload path traversal and arbitrary file write to Collector.
· CVE-2026-84271 — IBM Guardium Data Protection local patch-installer signature-verification bypass and root code execution.
· CVE-2026-84250 — IBM Guardium Data Protection local weak cryptographic protection and hard-coded recovery key allowing recovery of the root password.
· CVE-2026-84247 — IBM Guardium Data Protection authenticated remote path traversal with denial-of-service impact.
· CVE-2026-84245 — IBM Guardium Data Protection local cpwrapper privilege escalation to root.
· CVE-2026-84244 — IBM Guardium Data Protection stored web-input execution in Quick Search through attacker-influenced monitored database traffic.
· CVE-2026-84241 — IBM Guardium Data Protection remote improper-authorization security bypass.
· CVE-2026-84239 — IBM Guardium Data Protection high-privilege authenticated SQL injection and sensitive-information access.
· CVE-2026-84108 — IBM Guardium Data Protection unauthenticated web-input-neutralization weakness producing attacker-controlled execution under the documented affected conditions.
· CVE-2026-84106 — IBM Guardium Data Protection authenticated web-input-neutralization weakness producing attacker-controlled execution under the documented affected conditions.
· CVE-2026-84105 — IBM Guardium Data Protection authenticated SQL injection and sensitive-information access.
· CVE-2026-84089 — IBM Guardium Data Protection local improper privilege management and privilege escalation.
· CVE-2026-84086 — IBM Guardium Data Protection high-privilege authenticated pathname-restriction weakness with arbitrary-code-execution impact.
· CVE-2026-84085 — IBM Guardium Data Protection remote unauthenticated OS-command injection under the documented high-complexity condition.
· CVE-2026-84084 — IBM Guardium Data Protection remote CSRF security bypass.
· CVE-2026-84083 — IBM Guardium Data Protection local Collector nmap_wrapper SUID-root privilege escalation.
· CVE-2026-84081 — IBM Guardium Data Protection remote improper certificate validation.
· CVE-2026-84077 — IBM Guardium Data Protection remote CSRF security bypass.
· CVE-2026-84076 — IBM Guardium Data Protection authenticated improper-authorization security bypass.
· CVE-2026-84074 — IBM Guardium Data Protection authenticated web-input-neutralization weakness with user interaction.
· CVE-2026-84070 — IBM Guardium Data Protection authenticated web-input-neutralization weakness with user interaction.
· CVE-2026-84036 — IBM Guardium Data Protection authenticated improper-authorization security bypass.
· CVE-2026-82967 — IBM Guardium Data Protection unauthenticated bypass of IP-based management-interface access controls.
· CVE-2026-82896 — IBM Guardium Data Protection authenticated path traversal.
· CVE-2026-82893 — IBM Guardium Data Protection local improper privilege management and privilege escalation.
· CVE-2026-82892 — IBM Guardium Data Protection remote unauthenticated OS-command injection under the documented high-complexity condition.
· CVE-2026-82890 — IBM Guardium Data Protection authenticated arbitrary JavaScript or web-input execution.
· CVE-2026-82887 — IBM Guardium Data Protection authenticated OS-command injection.
· CVE-2026-82885 — IBM Guardium Data Protection authenticated REST API missing authorization and elevated privileges.
· CVE-2026-82832 — IBM Guardium Data Protection authenticated web-input-neutralization weakness producing attacker-controlled execution under the documented affected conditions.
· CVE-2026-61682 — kcp front-proxy identity-header trust failure and multi-tenant authorization bypass.
· NVD / CVE records — IBM Guardium Data Protection cohort.
· hxxps://nvd[.]nist[.]gov/
· NVD — CVE-2026-61682.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-61682
· CVE Record — CVE-2026-28326 — SolarWinds Access Rights Manager unauthenticated remote code execution.
· hxxps://www[.]cve[.]org/CVERecord?id=CVE-2026-28326
· NVD / CVE records — HP Advance CVE-2026-89082, CVE-2026-89083, and CVE-2026-89084.
· hxxps://nvd[.]nist[.]gov/
· NVD — CVE-2026-70416.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-70416
· NVD — CVE-2026-91843.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-91843
· NVD — CVE-2026-5430.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-5430
· NVD — CVE-2026-89026.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-89026
· NVD / CVE records — Cisco September 16, 2026 ISE / ISE-PIC cohort.
· hxxps://nvd[.]nist[.]gov/
· NVD / CVE records — Cisco September 16, 2026 Secure FMC cohort.
· hxxps://nvd[.]nist[.]gov/
· NVD / CVE records — Cisco Nexus Dashboard, Cisco BroadWorks CommPilot, and Cisco ThousandEyes Virtual Appliance September 16 cohort.
· hxxps://nvd[.]nist[.]gov/
· NVD — CVE-2026-90457.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90457
· NVD — CVE-2026-90456.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90456
· NVD — CVE-2026-90455.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90455
· NVD — CVE-2026-90454.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90454
· NVD — CVE-2026-90453.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90453
· NVD — CVE-2026-90452.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90452
· NVD — CVE-2026-90451.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90451
· NVD — CVE-2026-90450.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90450
· NVD — CVE-2026-90449.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90449
· NVD — CVE-2026-90448.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90448
· NVD — CVE-2026-90447.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90447
· NVD — CVE-2026-90446.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90446
· NVD — CVE-2026-90445.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90445
· NVD — CVE-2026-90444.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90444
· NVD — CVE-2026-90443.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-90443
· NVD — CVE-2026-88021.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-88021
· NVD — CVE-2026-88011.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-88011
· NVD — CVE-2026-88009.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-88009
· NVD — CVE-2026-88008.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-88008
· NVD — CVE-2026-88007.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-88007
· NVD — CVE-2026-88004.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-88004
· NVD — CVE-2026-87107.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-87107
· NVD — CVE-2026-87106.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-87106
· NVD — CVE-2026-87090.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-87090
· NVD — CVE-2026-86060.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-86060
· NVD — CVE-2026-83527.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-83527
· NVD — CVE-2026-81939.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-81939
· NVD — CVE-2026-8044.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-8044
· NVD — CVE-2026-79698.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-79698
· NVD — CVE-2026-79697.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-79697
· NVD — CVE-2026-79678.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-79678
· NVD — CVE-2026-78328.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-78328
· NVD — CVE-2026-78327.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-78327
· NVD — CVE-2026-75754.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-75754
· NVD — CVE-2026-72530.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-72530
· NVD — CVE-2026-72529.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-72529
· NVD — CVE-2026-67281.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-67281
· NVD — CVE-2026-67279.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-67279
· NVD — CVE-2026-67278.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-67278
· NVD — CVE-2026-67277.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-67277
· NVD — CVE-2026-67276.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-67276
· NVD — CVE-2026-57155.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-57155
· NVD — CVE-2026-50746.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-50746
· NVD — CVE-2026-34910.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-34910
· NVD — CVE-2026-34909.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-34909
· NVD — CVE-2026-34908.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-34908
· NVD — CVE-2026-20359.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20359
· NVD — CVE-2026-20358.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20358
· NVD — CVE-2026-20357.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20357
· NVD — CVE-2026-20353.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20353
· NVD — CVE-2026-20327.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20327
· NVD — CVE-2026-20319.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20319
· NVD — CVE-2026-20318.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20318
· NVD — CVE-2026-20317.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20317
· NVD — CVE-2026-20315.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20315
· NVD — CVE-2026-20231.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20231
· NVD — CVE-2026-20097.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20097
· NVD — CVE-2026-20096.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20096
· NVD — CVE-2026-20095.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20095
· NVD — CVE-2026-20094.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20094
· NVD — CVE-2026-20079.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20079
· NVD — CVE-2026-20035.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20035
· NVD — CVE-2026-20034.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20034
· NVD — CVE-2026-20030.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-20030
· NVD — CVE-2026-19843.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-19843
· NVD — CVE-2026-19626.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-19626
· NVD — CVE-2026-19404.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-19404
· NVD — CVE-2026-19233.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-19233
· NVD — CVE-2026-18922.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-18922
· NVD — CVE-2026-18851.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-18851
· NVD — CVE-2026-18651.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-18651
· NVD — CVE-2026-18355.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-18355
· NVD — CVE-2026-16876.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-16876
· NVD — CVE-2026-16812.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-16812
· NVD — CVE-2026-12745.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-12745
· NVD — CVE-2026-12744.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-12744
· NVD — CVE-2026-12651.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-12651
· NVD — CVE-2026-12650.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-12650
· NVD — CVE-2026-12648.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-12648
· NVD — CVE-2026-12647.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-12647
· NVD — CVE-2026-12646.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-12646
· NVD — CVE-2026-12645.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-12645
· NVD — CVE-2026-11770.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2026-11770
· NVD — CVE-2024-3400.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2024-3400
· NVD — CVE-2024-21893.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2024-21893
· NVD — CVE-2024-21887.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2024-21887
· NVD — CVE-2023-20273.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2023-20273
· NVD — CVE-2023-20198.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2023-20198
· NVD — CVE-2023-3519.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2023-3519
· NVD — CVE-2023-27997.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2023-27997
· NVD — CVE-2023-2868.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2023-2868
· NVD — CVE-2022-40684.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2022-40684
· NVD — CVE-2021-22986.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2021-22986
· NVD — CVE-2020-5902.
· hxxps://nvd[.]nist[.]gov/vuln/detail/CVE-2020-5902
Threat Technique Framework
· MITRE ATT&CK.
· hxxps://attack[.]mitre[.]org/
Security Vendor Analysis
Cisco's finalized October 7, 2026 security-advisory package documents 35 distinct vulnerabilities across Cisco NX-OS Software and Nexus platforms, Cisco Application Policy Infrastructure Controller, Cisco License On-Prem, Cisco Meraki platforms, and Cisco Finesse. The cohort should not be represented as one mandatory exploit chain because affected products, enabled features, authentication prerequisites, privilege requirements, network position, management-interface exposure, and resulting security effects differ materially between identifiers.
The NX-OS and Nexus portion comprises 14 Coverage With Adaptation CVEs: CVE-2026-76453, CVE-2026-76455, CVE-2026-76456, CVE-2026-76457, CVE-2026-76458, CVE-2026-76459, CVE-2026-76465, CVE-2026-76485, CVE-2026-76486, CVE-2026-76501, CVE-2026-76471, CVE-2026-20038, CVE-2026-20173, and CVE-2026-20032. The cohort spans internally discovered NX-OS hardening weaknesses, unauthenticated MPLS OAM and NGOAM remote-code-execution conditions, unauthenticated NX-API remote code execution, ACI endpoint-group contract bypass, control-plane resource exhaustion and denial of service, and authenticated local Python sandbox escape. The product-specific prerequisites and telemetry requirements prevent Direct Coverage classification even though the consequential privileged execution, control-plane disruption, unauthorized policy bypass, management-interface abuse, and downstream network-control effects align with the existing behavior-led model.
The Cisco Application Policy Infrastructure Controller portion comprises five Coverage With Adaptation CVEs: CVE-2026-76498, CVE-2026-76499, CVE-2026-76500, CVE-2026-20321, and CVE-2026-76488. The cohort includes APIC hardening weaknesses, authenticated API command injection capable of root-context command execution, and authenticated unauthorized sensitive-file access. Reliable attribution requires APIC-specific asset and version inventory, API and management-interface telemetry, authenticated identity and privilege context, process and root-context evidence, file-access activity, configuration state, ACI fabric effects, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
The Cisco License On-Prem portion comprises eight Coverage With Adaptation CVEs: CVE-2026-76480, CVE-2026-76482, CVE-2026-76483, CVE-2026-76484, CVE-2026-20328, CVE-2026-76437, CVE-2026-76452, and CVE-2026-76454. The cohort includes authentication, authorization, credential-protection, code-execution, SQL-injection, arbitrary-file-write, denial-of-service, password-reset, and management-interface weaknesses affecting Cisco License On-Prem, formerly Cisco Smart Software Manager On-Prem. Reliable attribution requires License On-Prem-specific version, management-interface, API, authentication, administrator, database, filesystem, process, configuration, remediation, and incident-response evidence.
The Cisco Meraki portion comprises seven Coverage With Adaptation CVEs: CVE-2026-76463, CVE-2026-76464, CVE-2026-76467, CVE-2026-76468, CVE-2026-76469, CVE-2026-76470, and CVE-2026-76472. Cisco groups these internally discovered networking weaknesses in the October 2026 Meraki security-hardening release. Reliable attribution requires affected Meraki product and firmware inventory, network-position and exposure context, device and cloud-management telemetry, configuration state, administrator activity, traffic and downstream network effects, remediation state, and incident-response findings.
Cisco Finesse CVE-2026-20362 is a Coverage With Adaptation entry. Cisco documents an unauthenticated server-side request forgery condition in the Finesse web-based management interface caused by improper validation of specific HTTP requests. Successful exploitation may cause the affected device to issue attacker-influenced requests and may expose limited sensitive information associated with services reachable from the device. Reliable attribution requires Finesse-specific asset and version inventory, management-interface exposure, HTTP request telemetry, effective destination and response context, reachable-service inventory, application and system logging, remediation state, and incident-response findings.
The 35 Cisco October 7 identifiers add 35 Coverage With Adaptation CVEs and 0 Direct Coverage CVEs. The Directly Covered CVE count remains 12, Coverage With Adaptation increases from 321 to 356, and the total CVE register increases from 333 to 368. Available authoritative evidence reviewed for this amendment does not establish CISA Known Exploited Vulnerabilities Catalog status for any of the 35 identifiers. Cisco states that the internally discovered hardening-release vulnerabilities are not known to be actively exploited, and the applicable specific Cisco advisories reviewed do not establish confirmed malicious use. The cohort therefore adds 0 CISA KEV-listed CVEs under the evidence currently validated for this amendment.
Broadcom's October 6, 2026 Brocade Fabric OS vulnerability-disclosure package documents 48 CVEs affecting Fabric OS 10.x and 9.2.x release families under CVE-specific product, version, privilege, feature, authentication, network-position, and configuration prerequisites. The complete vendor cohort should not be represented as a single exploit chain or added wholesale to this report because the disclosure set includes management-control-plane vulnerabilities, denial-of-service-only conditions, and third-party or underlying-component vulnerabilities with materially different relevance to the CyberDax behavior-led coverage model.
Thirty-seven Brocade Fabric OS identifiers qualify as Coverage With Adaptation in this report: CVE-2026-87679, CVE-2026-87680, CVE-2026-87681, CVE-2026-87682, CVE-2026-87683, CVE-2026-87684, CVE-2026-87659, CVE-2026-94578, CVE-2026-87686, CVE-2026-87678, CVE-2026-87669, CVE-2026-87670, CVE-2026-87672, CVE-2026-94583, CVE-2026-94575, CVE-2026-94580, CVE-2026-94584, CVE-2026-87688, CVE-2026-87685, CVE-2026-87687, CVE-2026-87673, CVE-2026-87674, CVE-2026-87675, CVE-2026-87666, CVE-2026-87667, CVE-2026-87660, CVE-2026-87662, CVE-2026-87663, CVE-2026-87664, CVE-2026-94577, CVE-2026-94581, CVE-2026-94586, CVE-2026-87677, CVE-2026-94576, CVE-2026-94579, CVE-2026-94587, and CVE-2026-94585.
The qualifying cohort includes REST API and WebTools management-plane command injection, RBAC and access-control bypass, AAA authorization and federated-identity trust failures, administrative authentication bypass, session and identity-context manipulation, arbitrary file access or manipulation, firmware and configuration-management abuse, certificate-management command injection, management-interface memory-corruption and code-execution paths, Virtual Fabric and fabric-management authorization failures, inter-switch administrative trust abuse, privilege escalation, and privileged or root-context command execution. These behaviors align with the existing enterprise management-control-plane compromise model, but reliable attribution requires Brocade Fabric OS-specific asset and version inventory, enabled management services, REST API and WebTools exposure, authenticated identity and privilege context, AAA and external-authentication configuration, RBAC state, administrative-session evidence, configuration and firmware activity, certificate and SNMP management state, Virtual Fabric and zoning context, switch-to-switch and fabric relationships, privileged process or command telemetry, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect direct-coverage anchor model.
The remaining 11 identifiers in the October 6 vendor disclosure are not added to the production CVE register because their validated conditions are denial-of-service-only, underlying third-party or operating-system component issues, or otherwise lack sufficient management-control-plane relevance under the current production threshold. Their presence in the Broadcom disclosure does not by itself justify Coverage With Adaptation classification.
Available authoritative evidence reviewed for this amendment does not establish CISA Known Exploited Vulnerabilities Catalog status for the 37 qualifying Brocade identifiers. The Brocade cohort therefore adds 37 Coverage With Adaptation CVEs, 0 Direct Coverage CVEs, and 0 CISA KEV-listed CVEs. The Directly Covered CVE count remains 12, Coverage With Adaptation increases from 356 to 393, and the total CVE register increases from 368 to 405.
Arista's October 6, 2026 CloudVision security-advisory package documents 17 distinct management-control-plane vulnerabilities affecting CloudVision Portal on-premises, CloudVision Sensor, and CloudVision-CUE on-premises under CVE-specific prerequisites. The cohort includes OIDC and SSO request-trust weaknesses, authentication-material redirection, stored cross-site scripting and authenticated-session compromise paths, path traversal, server-side request forgery, unauthorized backend-function access, XML external entity injection, insecure direct object reference, SQL injection, operating-system command injection, source-address trust and authentication bypass, and LDAP injection. The vulnerabilities should not be represented as a single mandatory exploit chain because affected components, authentication prerequisites, required configuration, network position, privilege requirements, and resulting security effects differ materially between identifiers. Arista states across the applicable advisories that it is not aware of malicious exploitation of these vulnerabilities in customer deployments. The cohort therefore adds 17 Coverage With Adaptation CVEs and 0 CISA KEV-listed CVEs under the evidence currently validated for this amendment.
The "not one exploit chain" treatment is important because, for example, Advisory 0186 requires OIDC configuration, Advisory 0187 has separate default and SSO-dependent conditions, Advisory 0190 applies specifically to CV-CUE backend functions, and Advisory 0191 requires the applicable LDAP configuration.
Cloud Foundry Foundation security advisories published October 5, 2026 document two distinct UAA identity and authorization-control-plane vulnerabilities represented by CVE-2026-59357 and CVE-2026-59358. The two identifiers should not be represented as a single exploit chain because their configuration prerequisites, authentication state, affected OAuth or OIDC paths, and resulting authorization consequences differ materially.
CVE-2026-59357 affects UAA v4.5.0 through v79.6.0 inclusive under the documented self-UAA OIDC configuration condition, where an OIDC identity provider's issuer matches the UAA zone's own /oauth/token endpoint. Under the affected condition, insufficient authenticity verification in the external OIDC login callback allows an authenticated UAA user to submit qualifying token material in place of the expected OIDC authorization-code exchange and establish an unauthorized authenticated external-OIDC browser session.
CVE-2026-59358 affects UAA v3.7.0 through v79.6.0 inclusive and cf-deployment versions through v60.4.0 inclusive. Exploitation requires a valid user access token associated with an OAuth client configured to support both a public user-facing authorization flow and the client_credentials grant type on the same client identifier. The vulnerable token endpoint can accept the user token as client authentication for a client_credentials request and issue a client-only token carrying the OAuth client's configured authorities, creating a privilege-expansion path whose practical impact depends on those authorities.
Cloud Foundry recommends upgrading UAA to v79.7.0 or later for both vulnerabilities and cf-deployment to v60.5.0 or later where applicable to CVE-2026-59358. Reliable attribution requires Cloud Foundry UAA and cf-deployment asset and version inventory, OAuth-client and grant-type configuration, client-authority state, OIDC identity-provider and self-UAA configuration, user and client token issuance, external-OIDC callback activity, browser-session state, shadow-account and group-membership context, administrative-scope activity, downstream platform access, remediation state, and incident-response evidence beyond the UniFi OS / UniFi Connect direct-coverage anchor model.
Available authoritative evidence reviewed for this amendment does not establish CISA Known Exploited Vulnerabilities Catalog status for CVE-2026-59357 or CVE-2026-59358. The Cloud Foundry cohort therefore adds two Coverage With Adaptation CVEs, 0 Direct Coverage CVEs, and 0 CISA KEV-listed CVEs. The Directly Covered CVE count remains 12, Coverage With Adaptation increases from 393 to 395, and the total CVE register increases from 405 to 407.
DIVD case DIVD-2026-00015 documents CVE-2026-102489 and CVE-2026-102490 as two distinct Zammad vulnerabilities identified during investigation of the September 21, 2026 DIVD breach. DIVD states that its environment was breached through the two Zammad zero-day vulnerabilities and that the vulnerabilities were subsequently analyzed and reproduced during the investigation. Zammad independently confirms the practical exploitability constraints for CVE-2026-102489 but states that it had not received sufficient technical detail to independently verify CVE-2026-102490, its scope, or affected-version range as of October 1, 2026.
CVE-2026-102489 represents a remote application-compromise path affecting Zammad. DIVD identifies Zammad 6.3.0 through 6.5.4 as vulnerable to remote code execution in the Zammad application-user context and states that the condition can contribute to session leakage. DIVD also identifies the issue as present in Zammad 7.0.0 through 7.1.3 but not practically exploitable there because of environmental conditions.
Zammad's October 1, 2026 statement narrows the practical exposure further, stating that exploitation is possible only on Zammad 6.5 and older under the affected runtime environment, that Zammad 7.0 and later are not affected in practice, and that the relevant code was additionally hardened in Zammad 7.2.0.
CVE-2026-102490 represents a separate local privilege-escalation path. DIVD states that an attacker operating as the local zammad user can escalate privileges to root and identifies Zammad versions from 1.5.0 through versions before 7.1.0-alpha as affected.
Zammad states that it had not received technical details sufficient to independently verify CVE-2026-102490, its scope, or the affected-version range as of October 1, 2026. DIVD's exploitation and affected-version assertions therefore remain DIVD-attributed findings and are not independently confirmed by Zammad.
The two identifiers remain Coverage With Adaptation because reliable attribution requires Zammad-specific asset and version inventory, application exposure, session and authentication context, Zammad application-user activity, service and process telemetry, filesystem activity, local privilege state, sudo or root-context evidence where available, network behavior, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
DIVD's reported breach association materially increases retrospective-hunting and remediation urgency, but neither vulnerable-version state nor application exposure alone should be treated as proof that a specific deployment was compromised. CISA added CVE-2026-102489 and CVE-2026-102490 to the Known Exploited Vulnerabilities Catalog on October 2, 2026. The KEV designations confirm known exploitation and increase remediation and retrospective-investigation urgency without changing either identifier’s Coverage With Adaptation classification.
Kiteworks Security Advisory GHSA-qx8c-x3hv-c25g and the CISA-assigned CVE record document CVE-2026-102132 as an improper-access-control vulnerability affecting Kiteworks Core.
The affected administrative import function did not verify that the requesting administrator was authorized to create the privileged integration credential being imported. Under the documented prerequisite, a delegated administrator holding a narrowly scoped administrative permission can create the privileged integration credential and obtain full system-administrator privileges without action by an existing full system administrator.
Kiteworks Core versions before 9.5.1 are affected. Version 9.5.1 is the documented corrected boundary.
CVE-2026-102132 remains Coverage With Adaptation because reliable attribution requires Kiteworks-specific asset and version inventory, delegated-administrator identity and permission state, administrative-import activity, integration-credential creation and use, administrator-role and privilege state, configuration activity, audit evidence, managed-content and connector context, downstream activity, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for CVE-2026-102132.
AiSOC security advisories document five distinct security-orchestration and enterprise management-control-plane weaknesses represented by CVE-2026-103053 through CVE-2026-103057.
CVE-2026-103053 documents an authentication failure affecting AiSOC response-action API functionality under the documented deployment configuration. The affected condition can permit unauthorized integration enumeration, action submission or approval, arbitrary-principal activity, or dispatch of containment actions using configured vendor credentials.
CVE-2026-103054 documents an authenticated MSSP portfolio authorization failure in which an authenticated user can associate unauthorized tenant UUIDs with a user-controlled portfolio and obtain consequential access to another tenant's alerts, incidents, or posture information.
CVE-2026-103055 documents a hard-coded JWT verification-secret condition affecting AiSOC realtime authentication. Under the documented configuration condition, forged JWT-backed subscription authority can permit arbitrary tenant identifiers or unauthorized cross-tenant access to live alerts, cases, agent events, or graph updates through realtime WebSocket or SSE functionality.
CVE-2026-103056 documents authenticated command injection through AiSOC CrowdStrike Real Time Response action parameters. Successful exploitation can produce attacker-controlled command construction and execution on managed endpoints with SYSTEM or root privileges, creating a security-orchestration-to-endpoint-execution path.
CVE-2026-103057 documents missing authentication on AiSOC realtime internal endpoints. Successful exploitation can permit unauthenticated event submission, spoofed tenant identifiers, unauthorized WebSocket or SSE content distribution, or unauthorized notification activity.
AiSOC 12.0.0 is the documented correction boundary for the five-CVE cohort. Affected-version applicability remains CVE-specific and should be validated against the individual advisory or CVE record rather than generalized across all five identifiers.
The five AiSOC identifiers remain Coverage With Adaptation because reliable attribution requires AiSOC-specific asset and version inventory, deployment configuration, response-action API and realtime-service reachability, actions-service-token and development-mode state where applicable, authenticated identity and role context, MSSP portfolio and tenant-association state, JWT-secret configuration, subscription-ticket activity, realtime WebSocket and SSE telemetry, CrowdStrike integration state, response-action and approval records, RTR activity, managed-endpoint process and command telemetry, SYSTEM or root-context execution, event and notification records, configuration state, downstream security-control effects, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
The AiSOC cohort adds five Coverage With Adaptation CVEs and 0 CISA KEV-listed CVEs. The Directly Covered CVE count remains 12.
SUSE Rancher Manager security documentation identifies CVE-2026-88804 and CVE-2026-88805 as distinct Rancher management-plane trust failures.
CVE-2026-88804 allows a remote unauthenticated user to modify public UI settings and can result in attacker-controlled script execution in the browser context of users opening the Rancher login page, with potential exposure of the local administrator bootstrap password or an active administrator session.
CVE-2026-88805 affects deployments using public API session tokens. Logging out clears browser session cookies but does not invalidate the corresponding server-side public API session token, allowing a previously obtained token to remain valid until expiration. The issue applies to public API session-token deployments, including applicable OIDC-backed authentication scenarios.
The two Rancher identifiers remain Coverage With Adaptation because reliable attribution requires Rancher-specific asset and version inventory, public and authenticated API exposure, public UI settings, browser and API session-token state, logout and revocation events, identity-provider and OIDC configuration, administrator activity, RBAC and cluster-management state, downstream cluster activity, remediation state, and incident-response evidence beyond the UniFi OS / UniFi Connect anchor model. Available authoritative evidence reviewed for this amendment does not establish CISA KEV status for either identifier.
SailPoint's CNA record for CVE-2026-12342 documents improper input validation of submitted IdentityIQ web-service API content that allows an unauthenticated user to achieve remote code execution on the IdentityIQ server.
The affected IdentityIQ boundaries are 8.3 through 8.3p5, 8.4 through 8.4p4, and 8.5 through 8.5p2. SailPoint assigns CVSS 9.6.
CVE-2026-12342 remains Coverage With Adaptation because reliable attribution requires IdentityIQ-specific asset and version inventory, reachable web-service API paths, authentication and authorization state, application and service process activity, identity-governance workflow context, role and entitlement state, connector and configuration evidence, filesystem or process changes where observable, network behavior, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model. Available authoritative evidence reviewed for this amendment does not establish CISA KEV status.
FreePBX security advisories document three distinct authenticated PBX management-plane code-execution paths represented by CVE-2026-54675, CVE-2026-54710, and CVE-2026-75600. They should not be represented as one mandatory exploit chain.
CVE-2026-54675 affects vulnerable Soundlang module versions and permits an authenticated attacker to abuse insufficient path sanitization in file-upload and conversion processing to write a malicious PHP file into the web root and obtain remote code execution.
CVE-2026-54710 affects vulnerable Superfecta module versions and permits an authenticated attacker to abuse unsafe PHP file inclusion to execute arbitrary PHP code with the privileges of the web-server context.
CVE-2026-75600 affects vulnerable FreePBX 17 API module versions. An authenticated user authorized for the GraphQL API interface can supply attacker-controlled host input to the generatedocs path and cause arbitrary shell-command execution in the FreePBX service context.
The three FreePBX identifiers remain Coverage With Adaptation because reliable attribution requires FreePBX-specific asset, module, and version inventory, authenticated identity and authorization context, Soundlang, Superfecta, GraphQL or API path activity, file creation and modification, PHP and web-server process activity, Asterisk process and child-process evidence, command execution, telephony configuration, network behavior, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model. Available authoritative evidence reviewed for this amendment does not establish CISA KEV status for these three identifiers.
IBM's September 17, 2026 Guardium Data Protection bulletin documents 37 vulnerabilities affecting Guardium Data Protection 12.2 and directs customers to update to 12.0p233.
The cohort includes distinct security-bypass, authorization, command, privileged-execution, file, credential, database, REST, PESI, GIM, SNMP, certificate-validation, patch-validation, and management-interface weaknesses affecting Guardium appliance functions including Central Manager and Collector roles.
The 37 identifiers should not be collapsed into a single exploit sequence. The authentication prerequisite, local-versus-remote condition, affected function, and specific file, command, credential, database, REST, authorization, certificate, web, or privilege mechanic must be retained for the applicable identifier.
Local conclusions require affected Guardium role and version validation and the product-specific telemetry appropriate to the CVE being investigated. Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for the cohort.
The kcp reviewed advisory for CVE-2026-61682 documents an authorization-boundary failure in which the affected front proxy does not remove caller-supplied X-Remote-* identity headers before forwarding authenticated requests to shards.
An authenticated tenant can inject X-Remote-Group or X-Remote-Extra-* values, assert system:masters or forged delegated identity or scope data, cross workspace boundaries, and access secrets, RBAC objects, APIExports, APIBindings, LogicalClusters, and other resources outside the intended authorization boundary.
Affected versions are earlier than 0.31.4 and 0.32.0 through 0.32.1. Fixed versions are 0.31.4 and 0.32.2. External proxy stripping of inbound X-Remote-* headers can mitigate exposure, but upgrading is the complete remediation.
Local conclusions require kcp asset and version validation, front-proxy and shard topology, authenticated tenant identity, raw and forwarded header context where available, workspace and RBAC state, delegated-identity or scope context, secret and object access, configuration activity, and incident-response evidence.
Check Point's September 22, 2026 advisory for CVE-2026-93616 documents a Critical pre-authentication path-traversal vulnerability in the Security Management web service that can allow an attacker to execute a script from an arbitrary path and load an arbitrary Java class.
Check Point assigns CVSS 9.8 and identifies affected Security Management releases including R82.20; R82.10 with Jumbo Hotfix Take 44 or lower; R82 with Jumbo Hotfix Take 126 or lower; R81.20 with Jumbo Hotfix Take 166 or lower; R81.10 with Jumbo Hotfix Take 190 or lower; and the documented R80, R80.10, R80.20, R80.30, R80.40, and R81 end-of-support releases. Check Point states that LivePatch Take 28/29 does not address the issue and directs customers to sk1000171.
Check Point Research reports a handful of pinpointed attacks involving CVE-2026-93616 observed on July 23, 2026. Confirmed exploitation materially increases remediation and retrospective-hunting urgency but does not change the Coverage With Adaptation classification or establish compromise of a specific local deployment.
CISA added CVE-2026-93616 to the Known Exploited Vulnerabilities Catalog on September 22, 2026, with a remediation due date of September 25, 2026.
Check Point's advisory for CVE-2026-91843 documents a Critical vulnerability affecting Security Management and Log Servers in which an unauthenticated remote attacker may execute arbitrary code with root privileges through the login process.
Check Point assigns a CVSS score of 9.8 and states that there is currently no indication that the vulnerability has been exploited in the wild.
The documented remediation is the LivePatch fix in sk1000155; customers with automatic updates enabled are already protected, and Check Point states that Smart-1 Cloud is not affected because the fix has already been implemented there.
TR-CERT advisory TR-26-1202 and the associated CNA records document three Logsign SIEM vulnerabilities affecting versions 6.4.101 through versions before 6.4.117. CVE-2026-90924 is a default-credential vulnerability that permits trying common or default usernames and passwords and carries a CNA-assigned CVSS v3.1 score of 9.8. CVE-2026-90925 is a path-traversal vulnerability requiring low privileges and carries a CNA-assigned CVSS v3.1 score of 7.1. CVE-2026-90926 is a network-reachable code-injection vulnerability requiring low privileges and carries a CNA-assigned CVSS v3.1 score of 8.8.
Logsign SIEM 6.4.117 or later is the correction boundary for all three identifiers. The Logsign 6.4.117 release notes independently confirm the availability of that release and document security hardening in integration-configuration processing and file permissions.
The three identifiers remain Coverage With Adaptation because reliable attribution requires Logsign-specific authentication and privilege context, management and application-path reachability, process and child-process evidence, files and configuration, credential and secret state, outbound activity, administrator changes, connector and ingestion changes, alerting and logging state, SIEM-record integrity, remediation state, and incident-response evidence beyond the UniFi OS / UniFi Connect anchor model.
The cohort adds 0 CISA KEV entries to this report. The validated CISA ADP exploitation state is none for CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926.
UTMStack security documentation and the associated vulnerability records document seven distinct security-monitoring and management-control-plane vulnerabilities represented by CVE-2026-82039 through CVE-2026-82045. The seven identifiers should be evaluated separately because their authentication prerequisites, affected services, exploitation mechanics, and resulting security consequences are not identical.
CVE-2026-82039 documents authenticated SQL injection affecting UTMStack asset-group search functionality. An authenticated attacker can manipulate the affected search input so that attacker-controlled data reaches the underlying database query. Successful exploitation can permit unauthorized database queries and can affect the confidentiality or integrity of information stored in the UTMStack database.
CVE-2026-82040 documents authenticated server-side request forgery affecting UTMStack identity-provider metadata processing. An authenticated attacker can provide a malicious metadata URL and cause the UTMStack server to initiate requests to internal network resources or cloud instance-metadata services. The resulting access can expose services or information that are reachable by the UTMStack server but not directly reachable by the attacker.
CVE-2026-82041 documents missing authorization affecting the STOMP command WebSocket used by UTMStack to communicate with connected agents. An authenticated user who can access the affected WebSocket path can submit operating-system commands without satisfying the intended authorization restriction. Successful exploitation can cause attacker-controlled commands to be delivered through the UTMStack management plane to connected agents, creating a security-management-control-plane-to-managed-endpoint execution path.
CVE-2026-82042 documents an authentication bypass involving the UTMStack internal-key authentication mechanism. An attacker who possesses or obtains a valid internal key can use that trusted path to reach privileged API functionality without completing the normal user-account or JWT-authentication process. Successful abuse can therefore create unauthorized privileged access to management functions, configuration, security data, account functions, or other APIs protected by that internal trust mechanism.
CVE-2026-82043 documents unauthenticated account enumeration in the UTMStack password-reset workflow. An unauthenticated remote attacker can distinguish between registered and unregistered email addresses based on differences in password-reset responses. The weakness can therefore disclose valid UTMStack user identities and support subsequent credential attacks, phishing activity, or other targeted identity abuse, but account enumeration by itself does not establish account compromise.
CVE-2026-82044 documents authenticated server-side request forgery affecting the UTMStack PDF-reporting service. An authenticated attacker can supply an attacker-controlled URL that causes the service to retrieve content from internal backend resources, OpenSearch services, cloud instance-metadata services, or other resources reachable from the UTMStack server. Retrieved information can then be exposed through the resulting report content, creating an internal-resource-access and sensitive-information-disclosure path.
CVE-2026-82045 documents authenticated JPQL injection affecting UTMStack network-scan property-value search functionality. An authenticated attacker can manipulate the affected query input and alter JPQL processing in a manner that permits unauthorized access to sensitive entity information. The exposed information can include credential-related records and other sensitive data maintained within the UTMStack environment.
UTMStack versions before 11.2.16 are affected by the applicable vulnerabilities in this seven-CVE cohort. UTMStack version 11.2.16, released on October 1, 2026, provides the documented corrected-version boundary for CVE-2026-82039 through CVE-2026-82045.
The seven UTMStack identifiers remain Coverage With Adaptation because reliable local attribution requires UTMStack-specific asset and version inventory, authenticated identity and role context where applicable, administrative-interface and API exposure, internal-key state, identity-provider configuration, STOMP command-WebSocket activity, connected-agent identity and command telemetry, database-query activity, credential and sensitive-record access, password-reset activity, PDF-reporting requests, internal-service or cloud-metadata network access, managed-endpoint process and command telemetry, configuration and security-rule changes, remediation state, and incident-response evidence beyond the UniFi OS and UniFi Connect direct-coverage anchor model.
Available authoritative evidence reviewed for this amendment does not establish confirmed in-the-wild exploitation or CISA Known Exploited Vulnerabilities Catalog status for CVE-2026-82039 through CVE-2026-82045. The UTMStack cohort therefore adds seven Coverage With Adaptation CVEs and 0 CISA KEV-listed CVEs to this report. The Directly Covered CVE count remains 12.
SolarWinds Observability Self-Hosted 2026.2.3 documents CVE-2026-28324 and CVE-2026-28325 as two distinct unauthenticated remote-code-execution vulnerabilities.
CVE-2026-28324 is associated with insufficient integrity checks and applies where affected installations are configured in a non-default and non-secure configuration.
CVE-2026-28325 involves deserialization of untrusted data and applies where the application is configured to use the affected communication mode.
SolarWinds Observability Self-Hosted 2026.2.3 is the documented remediation boundary for both vulnerabilities.
The two identifiers remain Coverage With Adaptation because reliable attribution requires SolarWinds Observability Self-Hosted asset and version inventory, configuration state, affected communication-mode context, request and service telemetry, application and process activity, privilege context, filesystem and configuration effects, outbound network behavior, downstream monitoring or management effects, remediation state, and incident-response evidence beyond the UniFi OS / UniFi Connect anchor model.
Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for CVE-2026-28324 or CVE-2026-28325.
Zyxel's advisory for CVE-2026-7273 documents a stack-based buffer overflow in the CGI management component of affected GS1900 series switches.
The documented attack prerequisite is a LAN-based unauthenticated attacker capable of reaching the affected management path and sending a crafted HTTP request.
Successful exploitation may permit operating-system command execution on the affected switch.
CISA's Known Exploited Vulnerabilities Catalog establishes CVE-2026-7273 as a known exploited vulnerability.
WSO2 Security Advisory WSO2-2026-5328 documents CVE-2026-5430 as a Critical JWT authentication-bypass vulnerability affecting WSO2 API Manager, API Control Plane, Traffic Manager, and Universal Gateway.
Public reporting confirms malicious exploitation activity involving CVE-2026-5430. CISA added CVE-2026-5430 to the Known Exploited Vulnerabilities Catalog on September 24, 2026, based on evidence of active exploitation.
The CVE record for CVE-2026-89026 identifies Issabel Framework before commit b97dbaf0b71c1c36f841e672b664afbeb02773bd as affected.
The vulnerability is a hard-coded HS256 JWT signing-key weakness in pbxapi/index.php that allows an unauthenticated remote attacker to forge valid bearer tokens.
A forged token can call the manager originate endpoint with the System application parameter and cause Asterisk to execute arbitrary operating-system commands as the Asterisk user.
Fortinet PSIRT FG-IR-26-175 documents CVE-2026-104286 as a Critical path-traversal vulnerability affecting FortiMail. Under the documented affected conditions, an unauthenticated remote attacker can send crafted HTTP or HTTPS requests and write arbitrary files on the underlying FortiMail system.
CVE-2026-104286 remains Coverage With Adaptation because reliable attribution requires FortiMail-specific asset and version inventory, HTTP and HTTPS interface exposure, request and path activity, filesystem and file-write evidence, configuration state, administrator activity, process and service behavior where available, network communication, email-security policy and mail-system state, remediation state, and incident-response findings beyond the UniFi OS / UniFi Connect anchor model.
CISA added CVE-2026-104286 to the Known Exploited Vulnerabilities Catalog on October 1, 2026 based on evidence of active exploitation. The identifier adds one Coverage With Adaptation CVE and one CISA KEV-listed CVE to this report. The Directly Covered CVE count remains 12.
Cisco's September 14, 2026 advisory for CVE-2026-76461 describes a vulnerability in Cisco AsyncOS Software email parsing for Cisco Secure Email Gateway.
An unauthenticated remote attacker can send a crafted email containing malicious SQL statements through an affected device.
Successful exploitation can permit arbitrary SQL-statement execution and lead to command execution with root privileges on the underlying operating system.
CISA added CVE-2026-76461 to the Known Exploited Vulnerabilities Catalog on September 14, 2026, based on evidence of active exploitation.
CISA ICSA-26-254-01 documents fifteen vulnerabilities affecting Malcolm before v26.06.0.
The documented consequences include command execution in containers, forgery or overwriting of security-monitoring data, analyst-session theft or hijacking, RBAC bypass to administrative functions, unauthorized access to internal service data, insecure default or sample secrets, certificate-validation weakness, and related management and evidence-integrity effects.
Malcolm v26.06.0 or later provides the remediation boundary identified by the advisory.
Available authoritative evidence does not establish known public exploitation or CISA KEV status for CVE-2026-90443 through CVE-2026-90457.
· FortiGuard Labs — ClingSTUN Linux backdoor campaign analysis — documents exploitation of known vulnerabilities affecting internet-facing routers and IoT devices to deploy a Linux backdoor with startup-file persistence, process-killing and watchdog manipulation, public-STUN-assisted discovery of externally mapped address and port information, NAT-binding maintenance, back-connect proxy capability, remote command execution, and self-propagation. The public STUN services used by the malware are legitimate infrastructure and should not be treated by themselves as malicious indicators. Local assessment should correlate unexpected STUN or UDP activity, role-inconsistent outbound communication, persistence or startup-file changes where observable, process suppression, proxy or tunnel-like behavior, exploit-path evidence, device inventory, and incident-response findings before attributing activity to ClingSTUN.
· hxxps://www[.]fortinet[.]com/blog/threat-research/clingstun-linux-backdoor-abuses-public-stun-infrastructure
· SecurityWeek — Enterprises Warned of Attacks Exploiting WSO2 Vulnerability — September 16, 2026.
· hxxps://www[.]securityweek[.]com/enterprises-warned-of-attacks-exploiting-wso2-vulnerability/
· Tenable — CVE-2026-89026.
· hxxps://www[.]tenable[.]com/cve/CVE-2026-89026
· Cisco Talos — Active exploitation of Cisco Secure Firewall Management Center vulnerabilities — September 9, 2026.
· hxxps://blog[.]talosintelligence[.]com/fmc-ongoing-exploitation/
· Kaspersky — Organizations Face New Attacks via Unpatched TrueConf Videoconferencing Servers — Head Mare / PhantomCore / PhantomGraph.
· hxxps://www[.]kaspersky[.]com/about/press-releases/kaspersky-organizations-face-new-attacks-via-unpatched-trueconf-videoconferencing-servers
· Bishop Fox — Popping Root on UniFi OS Server: Unauthenticated RCE Chain Detection Analysis.
· hxxps://bishopfox[.]com/blog/popping-root-on-unifi-os-server-unauthenticated-rce-chain-detection-analysis
· ReliaQuest Threat Research — DNS Poisoning Tactics Expand to Hospitality Wi-Fi — July 23, 2026.
· hxxps://reliaquest[.]com/blog/threat-spotlight-dns-poisoning-tactics-expand-to-hospitality/
· CERT Polska — MikroTrick active RouterOS exploitation, compromise indicators, Flagged-state guidance, and remediation recommendations.
· hxxps://cert[.]pl/en/posts/2026/09/vulnerabilities-in-mikrotik-routeros-actively-exploited/
· Bishop Fox — CVE-2026-34908 Safe Detection Utility.
· hxxps://github[.]com/BishopFox/CVE-2026-34908-check
· Ampferl Security Disclosure — OPNsense RCE File Write GeoIP.
· hxxps://github[.]com/Ampferl/security/blob/main/disclosures/001_opnsense-rce-file-write-geoip/README[.]md
Threat Tradecraft and Intrusion Patterns
Arista CloudVision Portal and CloudVision-CUE CVE-2026-101149 through CVE-2026-101158 and CVE-2026-102155 through CVE-2026-102161 should be treated as 17 distinct adapted enterprise network-management control-plane weaknesses rather than as one generic CloudVision compromise chain.
Local conclusions require affected CloudVision Portal, CloudVision Sensor, or CloudVision-CUE asset and version validation; CVE-specific OIDC, SSO, LDAP, backend-service, UI, reverse-proxy, or privilege prerequisites where applicable; authentication and administrative context; API and management-interface activity; session and identity-provider evidence; file, database, directory-service, and command-execution telemetry where available; managed-network or wireless configuration effects; remediation state; and incident-response corroboration.
Vulnerable-version state or ordinary CloudVision administrative activity should not by themselves be treated as evidence that any of the 17 vulnerabilities was successfully exploited. Arista's current advisories do not report known malicious exploitation in customer deployments.
Zammad CVE-2026-102489 and CVE-2026-102490 should be treated as two related but distinct adapted application and host-compromise paths rather than as one mandatory exploit chain.
CVE-2026-102489 maps Zammad application and session compromise to remote code execution in the Zammad application-user context under affected runtime and version conditions. DIVD identifies Zammad 6.3.0 through 6.5.4 as vulnerable and identifies the condition as present but not practically exploitable in Zammad 7.0.0 through 7.1.3 because of environmental conditions. Zammad separately states that practical exploitation applies to Zammad 6.5 and older and that Zammad 7.0 and later are not affected in practice.
CVE-2026-102490 maps a separate local privilege-boundary failure from the zammad service-user context to root privileges under DIVD's published analysis. Zammad had not independently verified the vulnerability, technical mechanism, or affected-version scope as of October 1, 2026, so those details should remain attributed to DIVD.
The documented incident context supports a potential progression from application or session compromise into Zammad-user execution and, where CVE-2026-102490 applies, consequential root-level host control. The two vulnerabilities should not be represented as a universally required chain because the applicability, practical exploitability, and vendor-confirmed scope differ between the identifiers.
Local conclusions require affected-product and version validation, application and session activity, authenticated-user and administrative context, Zammad service-user process activity, child-process and command-execution evidence, filesystem changes, privilege-transition evidence, sudo or root-context activity where available, network behavior, persistence or configuration changes, remediation state, and incident-response corroboration.
DIVD's reported exploitation during its September 21 breach increases retrospective-hunting urgency. Vulnerable-version state, ordinary Zammad service activity, or presence of the local zammad account should not by themselves be treated as proof of successful exploitation.
Kiteworks Core CVE-2026-102132 should be treated as an adapted administrative authorization and privilege-escalation path rather than as unauthenticated compromise of the Kiteworks platform.
The documented prerequisite is an already authenticated delegated administrator holding the required narrowly scoped administrative permission. The relevant security boundary failure occurs when the administrative import function permits that administrator to create a privileged integration credential beyond the intended authorization scope and obtain full system-administrator privileges.
Local conclusions require Kiteworks Core asset and version validation, delegated-administrator identity and permission context, administrative-import activity, integration-credential creation and subsequent use, administrator-role changes, configuration and audit records, managed-content or connector activity where consequential access is suspected, and incident-response corroboration.
Vulnerable-version state or ordinary delegated-administrator activity should not by themselves be treated as proof that CVE-2026-102132 was exploited.
AiSOC CVE-2026-103053 through CVE-2026-103057 should be treated as five distinct adapted security-orchestration and enterprise management-control-plane weaknesses rather than as a single AiSOC exploit chain.
CVE-2026-103053 maps missing authentication on response-action functionality to unauthorized integration enumeration, action submission or approval, arbitrary-principal activity, vendor-credential-backed containment actions, and consequential downstream security-control changes under the documented deployment prerequisites.
CVE-2026-103054 maps authenticated MSSP portfolio manipulation to unauthorized tenant association and cross-tenant access to alerts, incidents, or posture information. It should not be represented as an unauthenticated tenant-compromise path.
CVE-2026-103055 maps the documented hard-coded JWT verification-secret condition to forged realtime subscription authority, arbitrary tenant identifiers, and unauthorized cross-tenant access to live alerts, cases, agent events, or graph updates.
CVE-2026-103056 maps authenticated security-orchestration action abuse to CrowdStrike Real Time Response command injection and consequential managed-endpoint execution with SYSTEM or root privileges. It should not be represented as unauthenticated direct endpoint compromise.
CVE-2026-103057 maps missing authentication on realtime internal endpoints to unauthenticated event submission, spoofed tenant identifiers, unauthorized realtime content distribution through WebSocket or SSE, and unauthorized notification activity. Exploitation requires network reachability to the affected internal endpoints.
Local conclusions for the AiSOC cohort require affected-product and version validation, deployment configuration, response-action API and realtime-service exposure, authentication and authorization context, tenant and MSSP portfolio state, actions-service-token and development-mode state where applicable, JWT-secret and subscription-ticket state, CrowdStrike integration and RTR activity, action-submission and approval records, managed-endpoint process and command telemetry, privilege context, event and notification records, WebSocket and SSE activity, downstream security-control effects, remediation state, and incident-response corroboration.
AiSOC 12.0.0 is the documented correction boundary for the cohort, but affected-version applicability remains CVE-specific. The five identifiers add five Coverage With Adaptation CVEs and 0 CISA KEV-listed CVEs.
SUSE Rancher CVE-2026-88804 and CVE-2026-88805 should be treated as two distinct adapted management-control-plane trust failures rather than as one exploit chain.
CVE-2026-88804 begins with unauthenticated modification of Rancher public UI settings and may progress to script execution in the login-page browser context, bootstrap-password exposure, active administrator-session exposure, or consequential privileged management activity.
CVE-2026-88805 requires prior acquisition of a valid public API session token. The relevant trust failure is continued server-side token validity after the associated browser logout event, so vulnerable-version state, ordinary session use, or logout activity alone should not be treated as proof of exploitation.
SailPoint IdentityIQ CVE-2026-12342 should be treated as an adapted unauthenticated identity-governance web-service API-to-server-execution path.
Local conclusions require affected-product and version validation, API exposure, request context where available, process and service activity, identity-governance changes, connector or configuration activity, filesystem and network effects, and incident-response corroboration.
FreePBX CVE-2026-54675, CVE-2026-54710, and CVE-2026-75600 should be treated as three distinct authenticated PBX management-plane execution paths rather than as one generic FreePBX RCE chain.
CVE-2026-54675 maps authenticated Soundlang upload and conversion activity to path traversal, arbitrary file write, malicious PHP placement, and follow-on web-server execution.
CVE-2026-54710 maps authenticated Superfecta processing to unsafe PHP inclusion and code execution in the web-server context.
CVE-2026-75600 maps authenticated GraphQL API generatedocs activity to attacker-controlled host input and arbitrary shell-command execution in the FreePBX service context.
Local conclusions for the FreePBX cohort require affected module and version validation, authenticated identity and privilege context, relevant management or API path activity, file and PHP evidence where applicable, Asterisk and web-server process telemetry, command execution, telephony configuration, network behavior, remediation state, and incident-response corroboration.
IBM Guardium Data Protection 12.2 should be treated as an adapted enterprise security-management and database-security control plane.
The 37 identifiers are not represented as a single exploit chain.
Local assessment should retain each identifier's actual prerequisite and mechanic while correlating resulting behavior to the report's existing authentication, authorization, privileged-execution, process, file, credential, database, configuration, service-impact, persistence, outbound, and downstream coverage families.
kcp CVE-2026-61682 should be treated as an adapted multi-tenant control-plane identity and authorization-boundary failure rather than as generic unauthenticated Kubernetes compromise.
The documented prerequisite is an authenticated tenant or client capable of reaching the affected front proxy.
The consequential risk arises because caller-supplied X-Remote-* identity data is trusted downstream by shards, allowing forged group or scope state, system:masters impersonation, and cross-workspace access.
Logsign SIEM CVE-2026-90924, CVE-2026-90925, and CVE-2026-90926 should be treated as three adapted security-monitoring control-plane paths rather than as one generic SIEM compromise.
CVE-2026-90924 represents unauthenticated administrative access through default credentials. CVE-2026-90925 represents low-privilege authenticated path traversal. CVE-2026-90926 represents low-privilege authenticated, network-reachable code injection. All three affect Logsign SIEM 6.4.101 through versions before 6.4.117.
Successful exploitation may produce unauthorized administrative access, path traversal, file or configuration effects, code execution, abnormal process or child-process activity, credential or secret access, outbound communication, administrator-state changes, connector or ingestion changes, alerting or logging gaps, and loss of confidence in SIEM-record integrity.
Local conclusions require affected-product and version validation, authentication and privilege context, management and application-path reachability, request and path context where available, process and child-process telemetry, filesystem and configuration evidence, credential and secret state, network behavior, administrator activity, connector and ingestion state, alerting and logging continuity, remediation state, SIEM-record integrity, and incident-response corroboration.
The validated CISA ADP exploitation state is none for all three identifiers, and the Logsign cohort adds 0 CISA KEV entries to this report.
UTMStack CVE-2026-82039 through CVE-2026-82045 should be treated as seven distinct adapted security-monitoring and agent-control-plane vulnerabilities rather than as a single generic UTMStack exploit chain. The authentication prerequisites, vulnerable services, attack mechanics, and resulting security effects differ materially between the seven identifiers and should be preserved during detection, hunting, and incident-response analysis.
CVE-2026-82039 maps authenticated manipulation of the UTMStack asset-group search functionality to SQL injection against the underlying database. Successful exploitation can result in unauthorized database queries and consequential access to or modification of data maintained by the security-management platform.
CVE-2026-82040 maps authenticated modification of identity-provider metadata input to server-side requests against internal network resources or cloud instance-metadata services. Local assessment should distinguish this server-originated request activity from ordinary identity-provider communications and should correlate suspicious destinations with administrative activity and configuration changes.
CVE-2026-82041 maps authenticated access to the affected STOMP command WebSocket without sufficient authorization to attacker-controlled operating-system command delivery through the UTMStack control plane. Successful exploitation can result in command execution on connected agents and managed systems. The vulnerability should therefore be represented as management-control-plane abuse leading to downstream agent execution, rather than as unauthenticated direct compromise of the managed endpoint.
CVE-2026-82042 maps possession or misuse of a valid UTMStack internal key to bypass of the normal user-account or JWT-authentication path and consequential privileged API access. Local analysis should correlate internal-key use with API requests, account activity, configuration changes, security-rule modifications, credential access, and other privileged management actions that would not be expected from the associated source or service.
CVE-2026-82043 maps unauthenticated password-reset requests and distinguishable application responses to enumeration of valid UTMStack accounts. The resulting account information can support follow-on phishing, password attacks, or credential targeting, but successful enumeration alone should not be treated as evidence that an enumerated account was subsequently compromised.
CVE-2026-82044 maps authenticated PDF-report generation using an attacker-controlled URL to server-side retrieval of internal resources or cloud instance-metadata information. Local analysis should correlate unusual report-generation activity with unexpected internal destinations, OpenSearch access, cloud-metadata requests, resulting report content, and subsequent credential, configuration, or network activity.
CVE-2026-82045 maps authenticated manipulation of network-scan property-value search input to JPQL injection and consequential unauthorized access to sensitive entity information. Credential-related records exposed through the affected query path can support additional privilege, access, persistence, or downstream compromise activity and should therefore be correlated with subsequent authentication and administrative behavior.
Local conclusions for the UTMStack cohort require validation of the affected UTMStack product and version, authentication and role context where applicable, administrative-interface and API reachability, internal-key state, identity-provider configuration, STOMP command-WebSocket activity, connected-agent identity and command telemetry, database and query evidence, password-reset activity, PDF-reporting requests, internal-service and cloud-metadata network access, credential and security-record access, configuration and security-rule changes, downstream managed-endpoint activity, remediation state, and incident-response corroboration.
All seven identifiers affect UTMStack versions before 11.2.16 under their applicable prerequisites, and UTMStack 11.2.16 provides the documented corrected-version boundary. Available authoritative evidence reviewed for this amendment does not establish confirmed in-the-wild exploitation or CISA KEV status for the UTMStack cohort. Vulnerable-version state, product presence, ordinary agent communication, ordinary report generation, or normal administrative activity should not by themselves be treated as proof that any of the seven vulnerabilities was successfully exploited.
SolarWinds Observability Self-Hosted CVE-2026-28324 and CVE-2026-28325 should be treated as two distinct adapted enterprise management and infrastructure-monitoring control-plane remote-code-execution paths rather than as a single generic SolarWinds exploit chain.
CVE-2026-28324 retains its documented prerequisite that the affected installation is configured in a non-default and non-secure configuration.
CVE-2026-28325 retains its documented prerequisite that the application is configured to use the affected communication mode.
Successful exploitation can produce application or service-context execution, process anomalies, privilege effects, filesystem or configuration changes, outbound communication, and downstream management or monitoring impact. Local conclusions require affected-product, version, configuration, communication-mode, service, process, network, administrative-state, remediation-state, and incident-response evidence.
Available authoritative evidence does not establish confirmed in-the-wild exploitation or CISA KEV status for either CVE, and vulnerable-version or configuration state alone should not be treated as proof of compromise.
Zyxel GS1900 CVE-2026-7273 should be treated as an adapted LAN-based unauthenticated network-device management-plane exploitation path rather than as a generic Internet-reachable switch RCE condition.
The documented sequence is LAN-based access to the affected GS1900 management plane, delivery of a crafted HTTP request to the CGI component, stack-based buffer-overflow behavior, and potential operating-system command execution.
CISA KEV status establishes known exploitation and increases remediation and retrospective-hunting urgency. It does not establish local compromise and does not remove the vendor-documented LAN-based prerequisite.
WSO2 CVE-2026-5430 represents an unauthenticated JWT authentication-bypass path affecting API-management and gateway control-plane functions. CISA KEV status confirms known exploitation and increases remediation and retrospective-hunting urgency without changing the Coverage With Adaptation classification or establishing compromise of a specific local deployment.
Issabel Framework CVE-2026-89026 represents an unauthenticated forged-token-to-operating-system-command-execution path affecting PBX and unified-communications infrastructure.
Fortinet FortiMail CVE-2026-104286 represents an unauthenticated HTTP-and-HTTPS-request-to-arbitrary-file-write path affecting email-security-appliance infrastructure.
CISA KEV status establishes known exploitation and increases remediation and retrospective-hunting urgency. Vulnerable FortiMail version or interface exposure alone should not be treated as proof that CVE-2026-104286 was successfully exploited or that a specific appliance was compromised.
Cisco Secure Email Gateway CVE-2026-76461 represents an unauthenticated email-processing-to-root-execution path.
Traefik's September 2026 advisories document five distinct reverse-proxy, gateway, request-interpretation, and identity-boundary weaknesses and should not be represented as one mandatory exploit chain.
HashiCorp's September 10, 2026 Consul advisories document four distinct control-plane weaknesses and should not be represented as one mandatory exploit chain.
CISA added MikroTik RouterOS CVE-2026-67277 and CVE-2026-86060 to the Known Exploited Vulnerabilities Catalog on September 10, 2026.
CERT Polska separately documents active exploitation of the MikroTrick chain combining CVE-2026-67276 and CVE-2026-86060 against internet-reachable RouterOS SSH services.
Cisco Secure Firewall Management Center CVE-2026-20079 is a critical unauthenticated management-plane authentication-bypass path.
Cisco Talos documents active Secure FMC exploitation across UAT-12197, UAT-11823, and UAT-11988, with observed post-compromise behavior including command execution, credential and configuration theft, reverse-shell and proxy activity, tunneling, internal reconnaissance, packet sniffing, persistence, defense impairment, Cyclops Blink deployment, downstream endpoint targeting, and Qilin ransomware activity.
The September 8 Ivanti package represents three distinct management-control-plane vulnerability groups and should not be treated as one mandatory exploit chain.
FreeIPA CVE-2026-76578 and CVE-2026-79678 represent two distinct higher-layer identity-control-plane weaknesses and should not be treated as one exploit chain.
Red Hat 389 Directory Server and Cockpit 389 Console CVE-2026-76560, CVE-2026-19843, CVE-2026-19404, CVE-2026-18922, CVE-2026-18651, CVE-2026-18355, and CVE-2026-11770 represent distinct but behaviorally related enterprise identity and directory-control-plane weaknesses. They should not be treated as one mandatory exploit chain.
SonicWall Network Security Manager On-Prem CVE-2026-78327, CVE-2026-78328, and CVE-2026-81939 represent three distinct but related management-platform weaknesses in affected NSM On-Prem deployments.
ASUS Control Center Enterprise CVE-2026-75754 represents an unauthenticated management-platform compromise path involving missing authentication for a critical function, server-side request forgery, and hard-coded credentials.
NEC UNIVERGE IX-R/IX-V CVE-2026-16876 represents an unauthenticated WebGUI-to-CLI command-execution path.
Advantech WISE-6610 and WISE-6610P CVE-2026-79697 and CVE-2026-79698 represent authenticated command-injection paths in firmware 1.2.1_20251110.
ClingSTUN should be treated as adapted appliance-focused intrusion and proxy or botnet operator tradecraft rather than as a new standalone malware-report requirement. FortiGuard Labs documents exploitation of known vulnerabilities affecting internet-facing routers and IoT devices followed by Linux backdoor deployment, persistence through startup files, termination of competing or interfering processes, watchdog manipulation, remote command execution, self-propagation, and use of compromised devices as back-connect proxy infrastructure.
The campaign's use of public STUN services supports discovery of externally mapped address and port information and maintenance of NAT bindings for proxy communications. Those legitimate STUN services should not be treated as malicious infrastructure by themselves. Local conclusions require affected-device and exposure validation, exploit-path evidence where available, process and filesystem telemetry where supported by the device, startup-file or persistence evidence, unusual or role-inconsistent UDP and STUN activity, proxy or tunnel-like communication, internal discovery or propagation behavior, remediation state, and incident-response corroboration.
ClingSTUN remains Coverage With Adaptation because the report already provides durable behavioral coverage for management-plane exploitation, privileged or device-level execution, outbound communication, appliance-focused intrusion activity, tunnel-like or proxy behavior, internal discovery, device enumeration, and role-inconsistent external communication. Campaign attribution requires ClingSTUN-specific device, persistence, process, STUN, proxy, propagation, and incident-response evidence beyond the UniFi OS and UniFi Connect direct-coverage anchor model.
ReliaQuest reporting on compromised public Wi-Fi gateways documents unauthorized DNS changes used to redirect connected-user traffic to attacker-controlled Microsoft 365 credential-harvesting infrastructure.
Local conclusions require affected-gateway and management-platform evidence, administrator activity, DNS configuration and response data, connected-user context, destination evidence, authentication evidence, and incident-response corroboration.
